Fortinet IPSec VPN NAT Traversal Technical Tips and Best Practices
Technical Tip
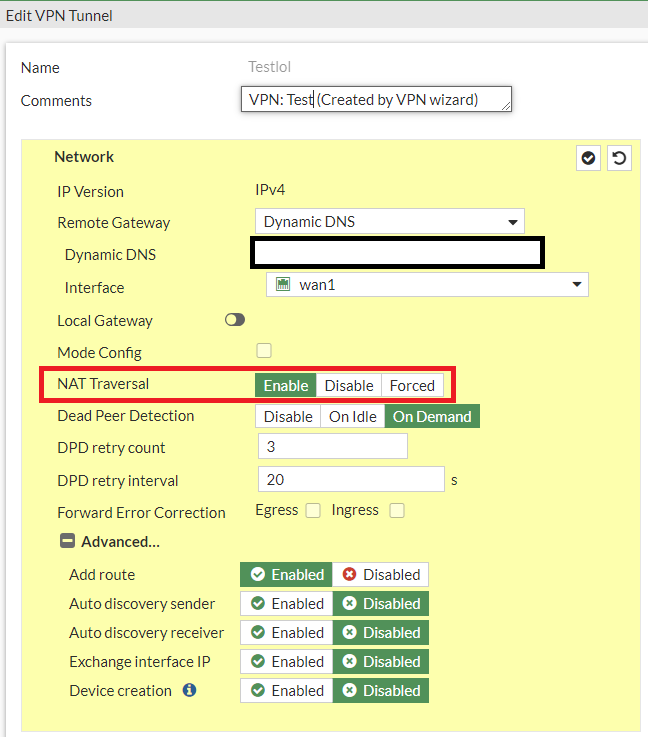
DescriptionThis article describes the NAT traversal options available under the phase 1 settings of an IPsec tunnel.ScopeFortiGate.SolutionNetwork Address Translation ( NAT ) is a way to convert private IP addresses to publicly routable Internet addresses and vice versa. When an IP packet passes throu...
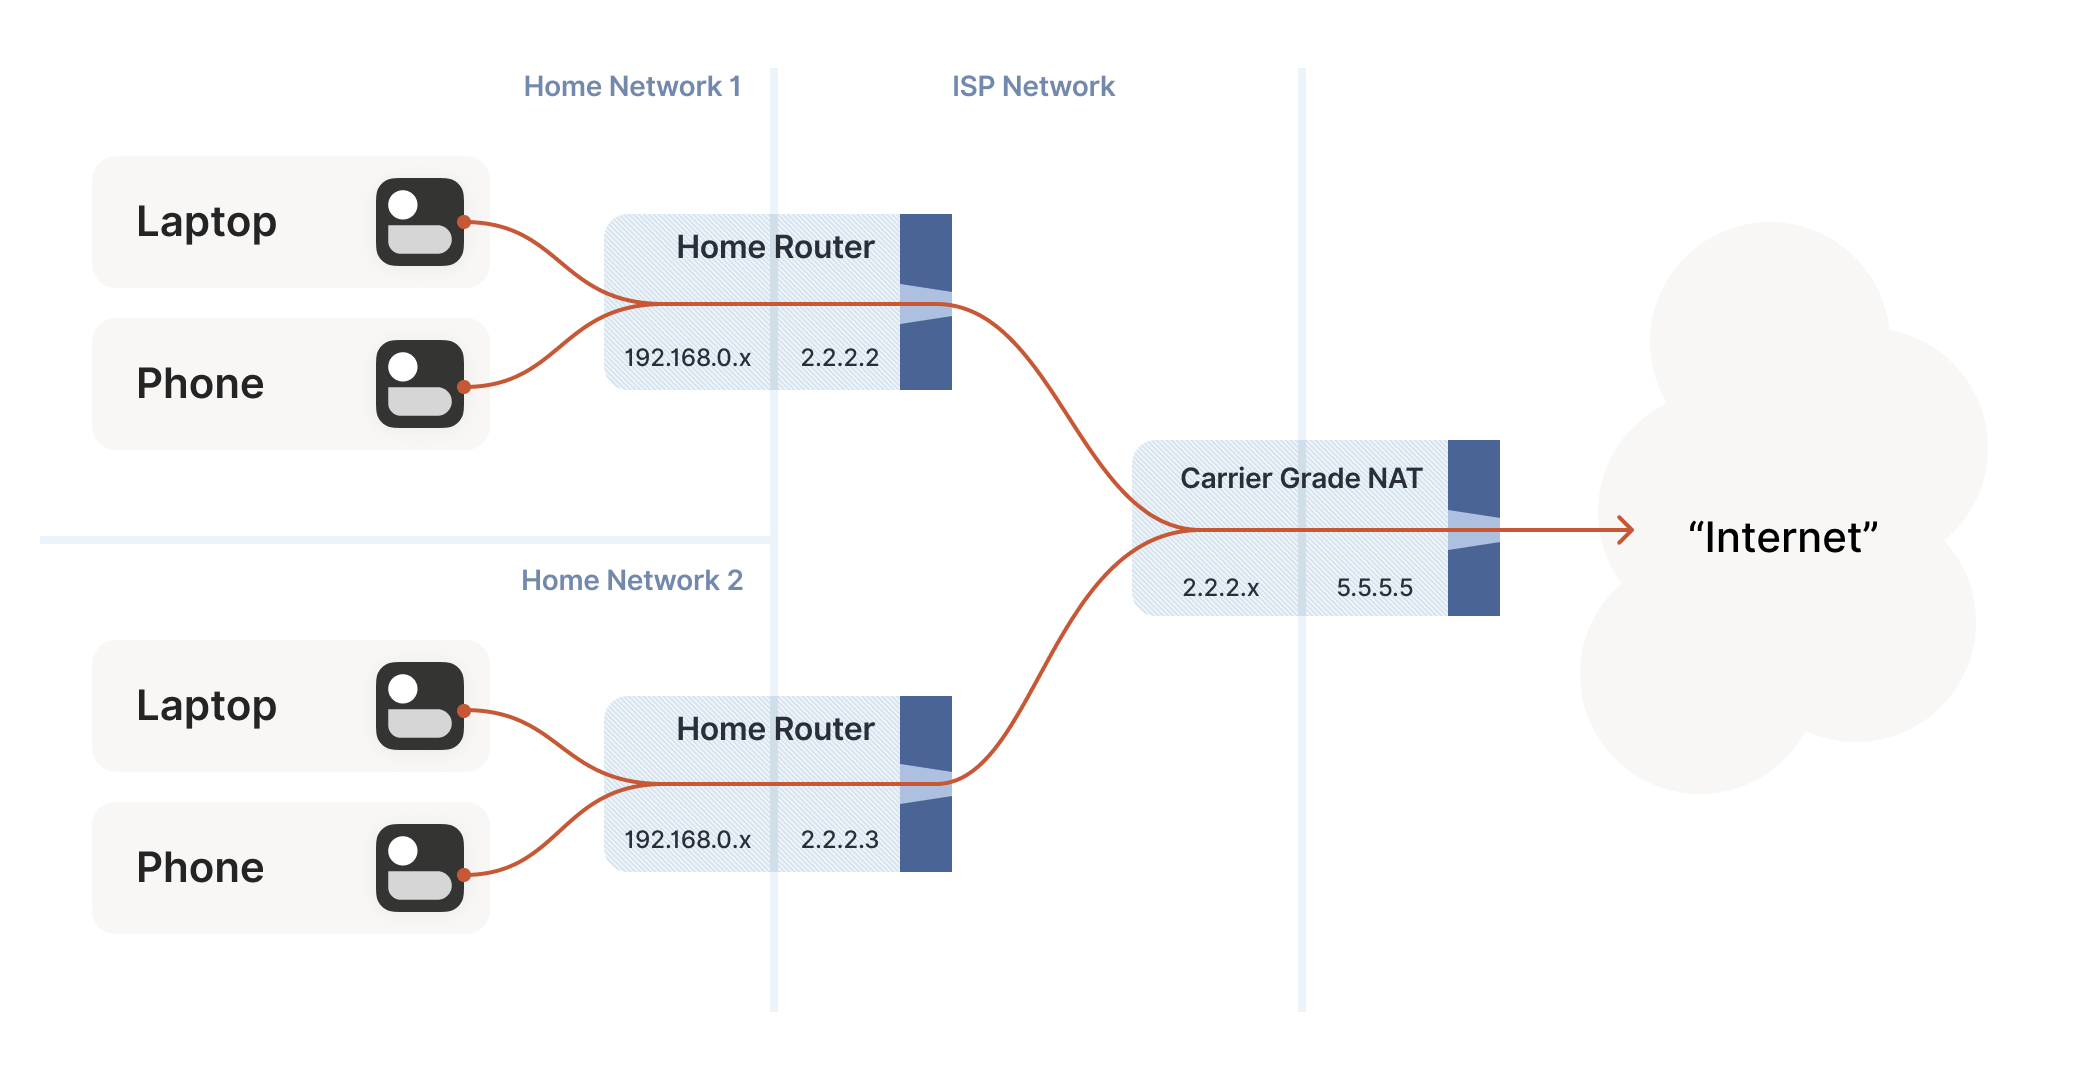
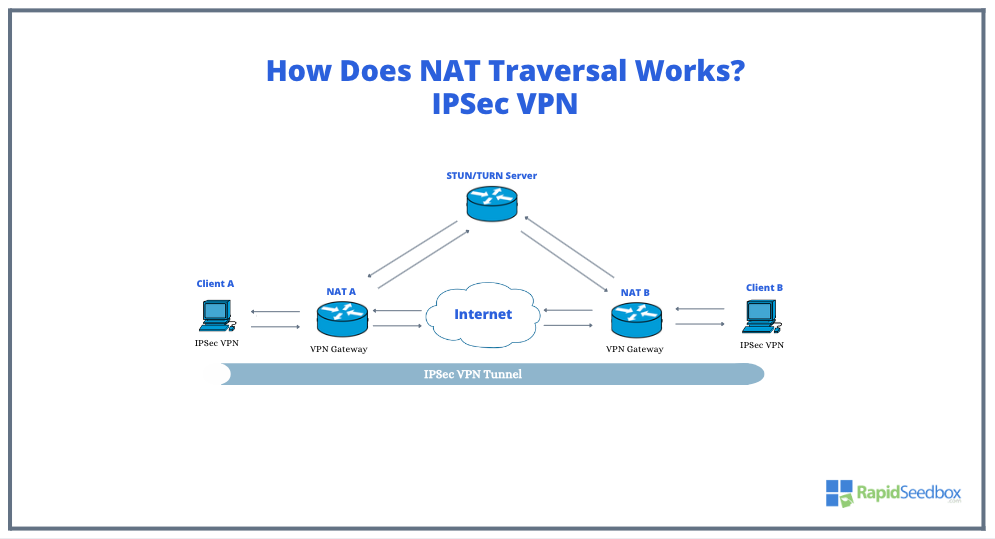
This extra encapsulation allows NAT devices to change the port number without modifying the IPsec packet directly. To provide the extra layer of encapsulation on IPsec packets, the Nat-traversal option must be enabled whenever a NAT device exists between two FortiGate VPN peers or a FortiGate unit and a DialUP client such as FortiClient.
IPSec Over NAT
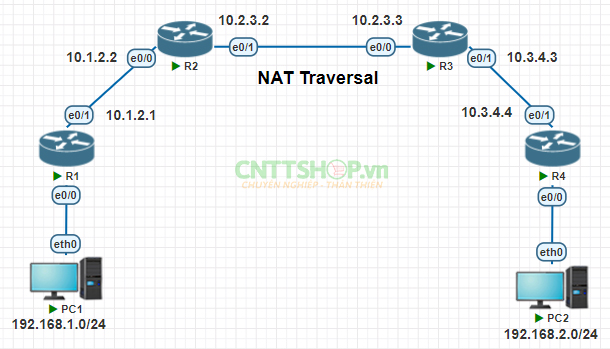
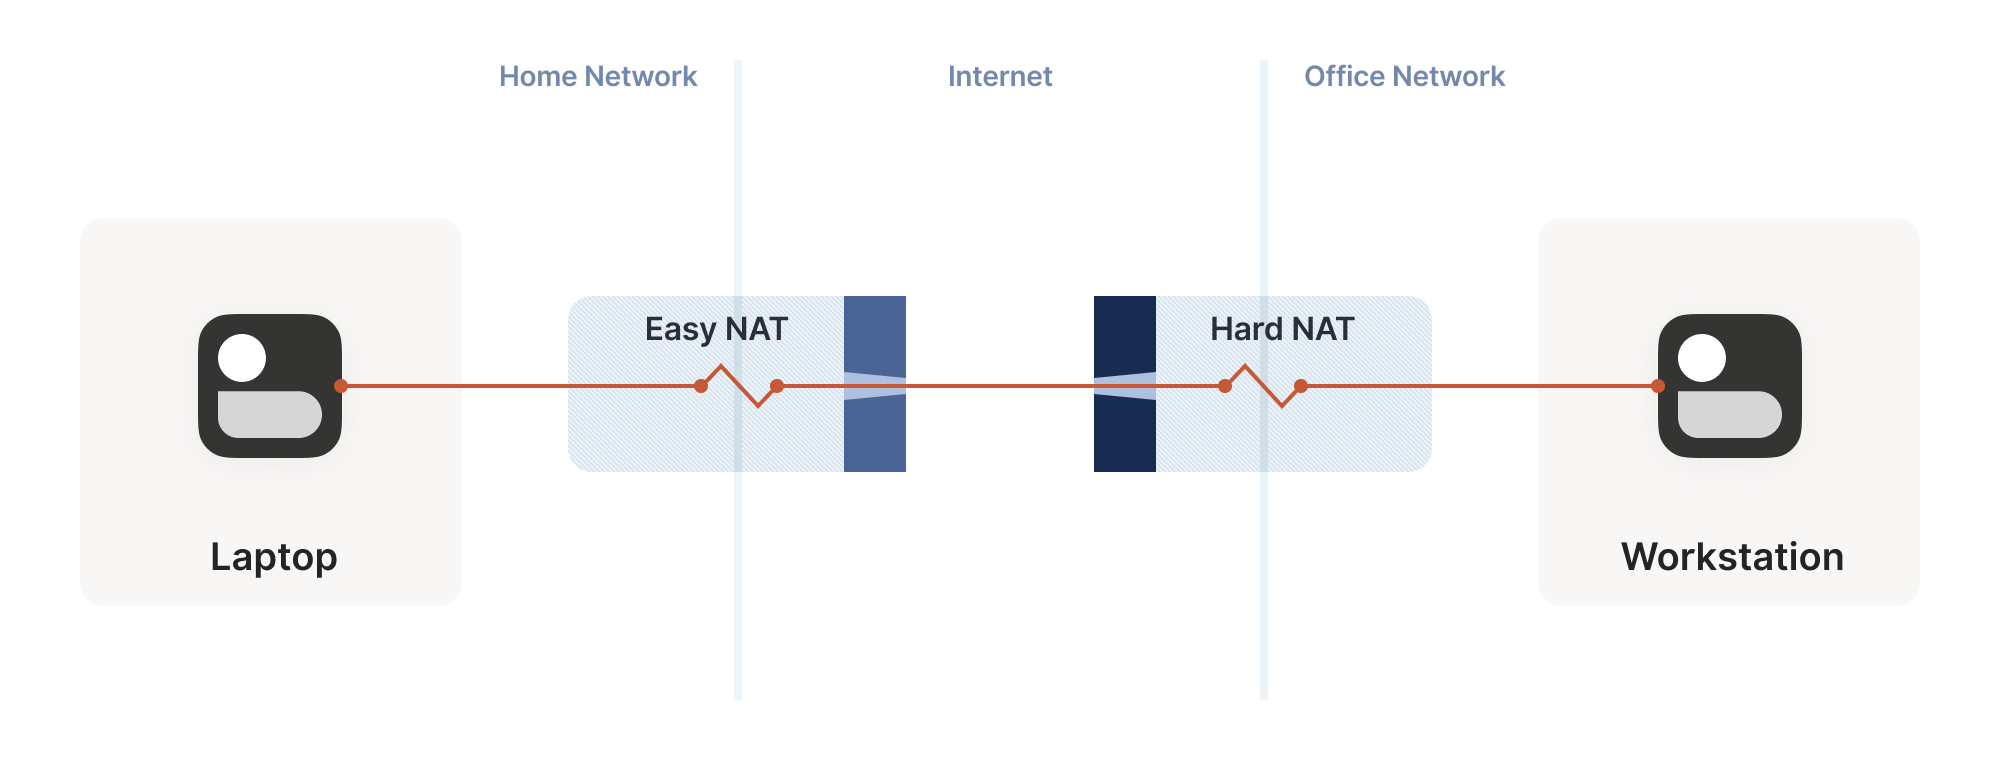
Generally speaking as long as NAT gateway out of your control (e.g. the ISP's) has a ESP ALG enabled, this should be good. If not, you might have difficulty if more than one client tries to establish an IPSec VPN behind the same network. If SSL VPN dial-in is an option, it tends to be a lot more NAT friendly.
So, they are expecting us to NAT our traffic and hide the private addresses behind our public IP addresses. I basically need to accomplish this setup: Private IP --> NAT --> Public IP --> TUNNEL --> Public IPSec Gateway --> Public Endpoint I feel like I am misunderstanding the policy that the VPN wizards created.

Fixing IPSec Tunnels with NAT Traversal (NAT
Conclusion NAT Traversal (NAT-T) is essential in modern IPSec VPNs , especially when NAT or PAT is involved between peers. By encapsulating ESP in UDP packets, NAT-T ensures tunnel reliability, even when public addresses are being translated. Understanding how to troubleshoot and configure NAT-T can save hours of frustration and restore full routing and VPN functionality across your IPSec ...
This creates a routing conflict, making a standard IPSec VPN unusable without additional design. On FortiGate Firewall, the recommended approach is to use IPSec VPN with NAT (IP Pool / Virtual IP) to translate one side of the network into a non-overlapping subnet.

How to Integrate IPSec VPN with NAT on FortiGate
Learn how to configure, test, and troubleshoot IPSec VPN with NAT on FortiGate, a network security appliance that encrypts and translates your network traffic.
Here the remote gateway is the Fortigate unit in Site A - VPN -GW-Site-A (10.10.50.2/24). And the IPSec phase is configured as the picture below which is exactly same as Site A with difference in IP address configuration only.

FortiGate Site
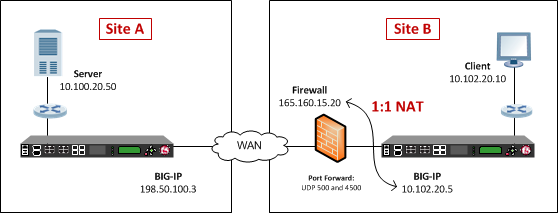
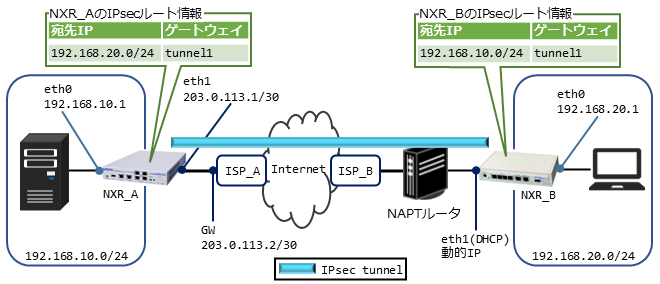
Learn how to configure site-to-site IPsec VPN between two FortiGate firewalls, where one FortiGate is behind a NAT device.


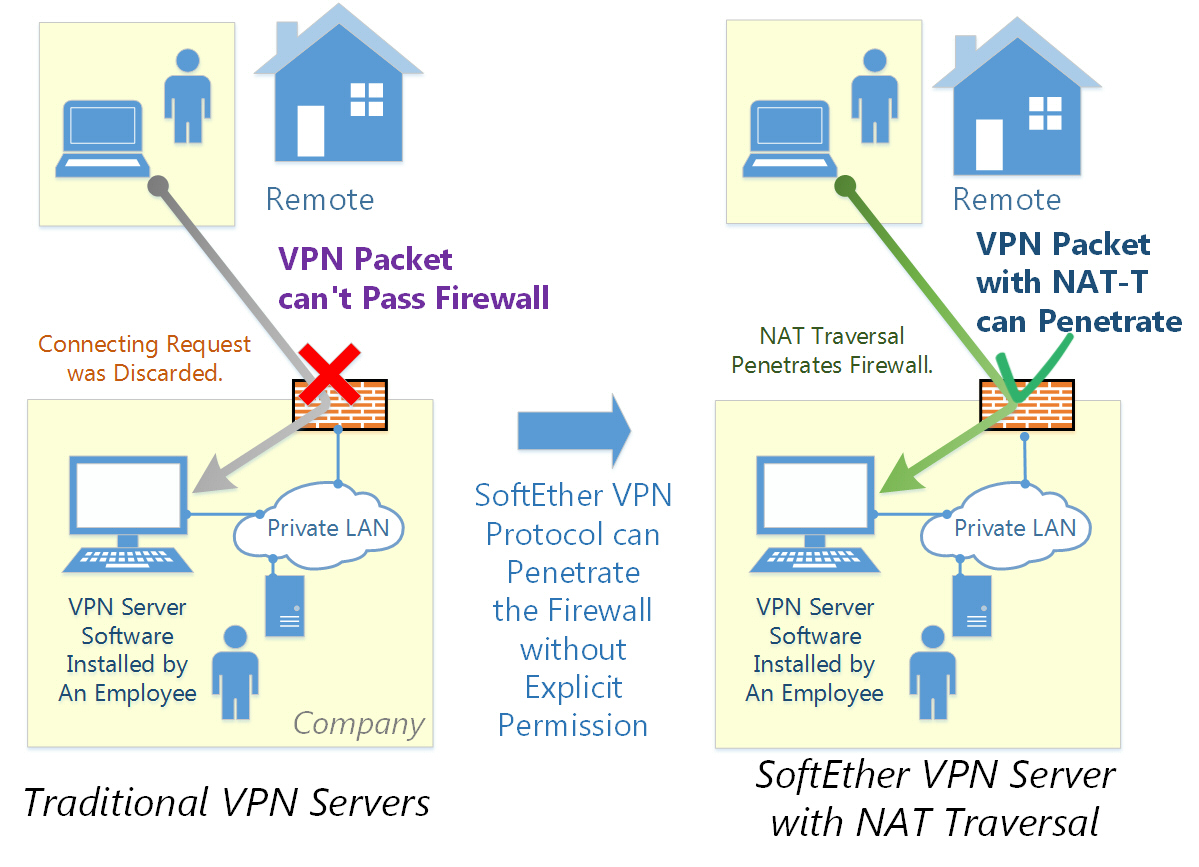


Learn how to configure a secure IPsec VPN on FortiGate for remote users using FortiClient. Includes users, groups, IP pools, Phase 1/2 settings, policies, and split/full tunnel options.