More advanced tools have additional detection capabilities such as statistical anomaly detection or stateful protocol inspection. Both of these capabilities use algorithms to detect intrusions. This allows detection of intrusions that don't yet have signatures created for them.
Linux Intrusion Detection and Response (IDS), Linux Endpoint Detection and Response (EDR) and Cloud Detection and Response (CDR) are different security techniques for the analysis and identification of unusual behavior patterns or actions in a system.

Furthermore, visual representations like the one above help us fully grasp the concept of Linux Intrusion Detection Techniques.
Protect your Linux server by consistently conducting assessments and validations employing robust security techniques and instruments.Intrusion detection, or monitoring a network or system for malicious activity or policy violations, is a critical part of maintaining a secure Linux server.

Moving forward, it's essential to keep these visual contexts in mind when discussing Linux Intrusion Detection Techniques.
Network Intrusion Detection Systems (NIDS) provide an effective technique to detect and prevent intrusions.This Linux Intrusion Detection System with Figure 2 shows the typical sensor-based network GRANT tool serves for the following purposes: intrusion detection architecture.
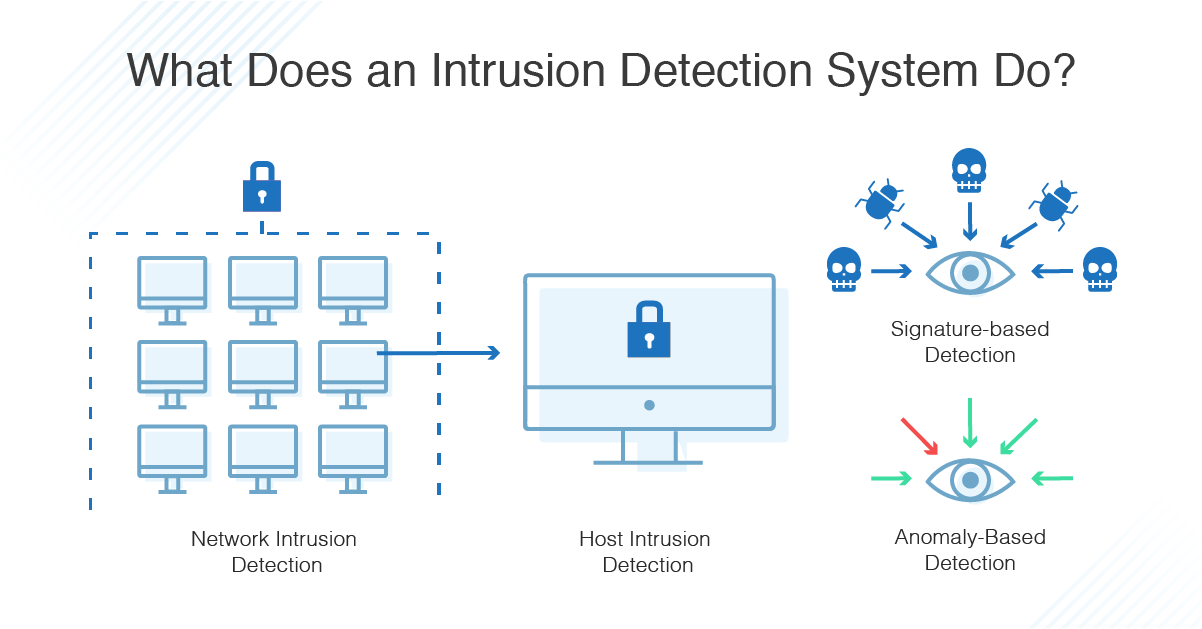
This particular example perfectly highlights why Linux Intrusion Detection Techniques is so captivating.
techniques have been developed to protect Linux hosts. and mitigate the risk posed by intruders [9]. The tool. GRANT (Global Real-time Analysis of Network. Traffic) being a Linux based Intrusion Detection.
Network-based Intrusion Detection Systems (NIDS): NIDS monitors traffic on a network segment. It acts as a guardian for the entire network, analyzing packets in real-time. When an anomaly is detected, it generates alerts, informing administrators of potential threats.
How to build a basic Linux intrusion detection system using BashHow to discover devices on your local network using ARP