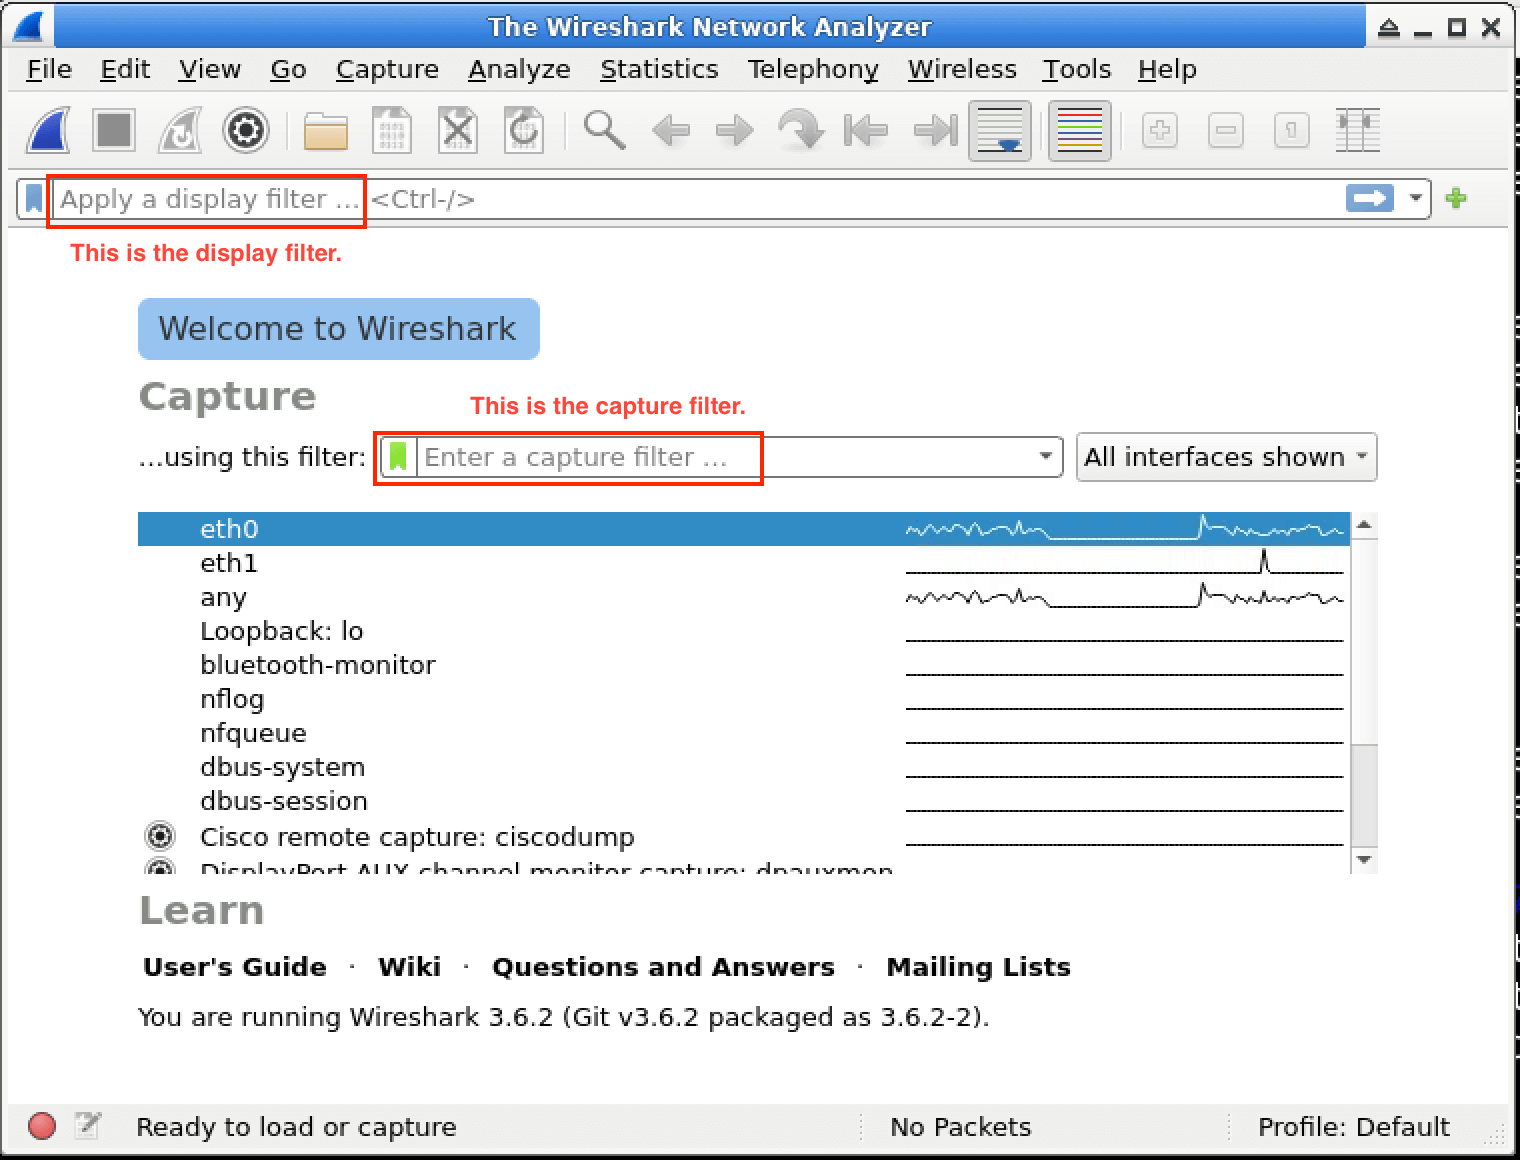
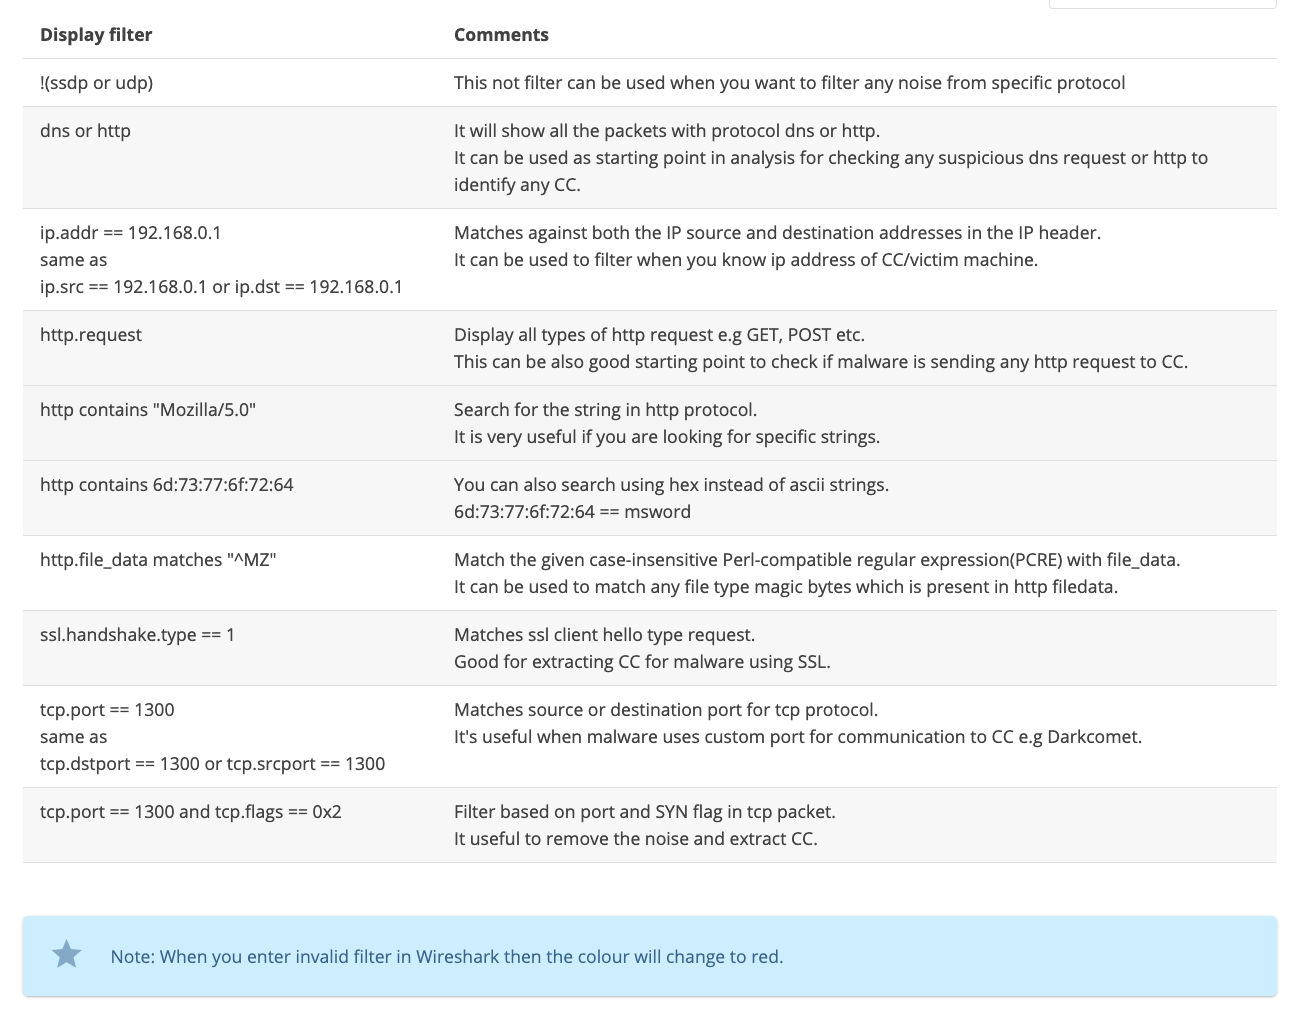
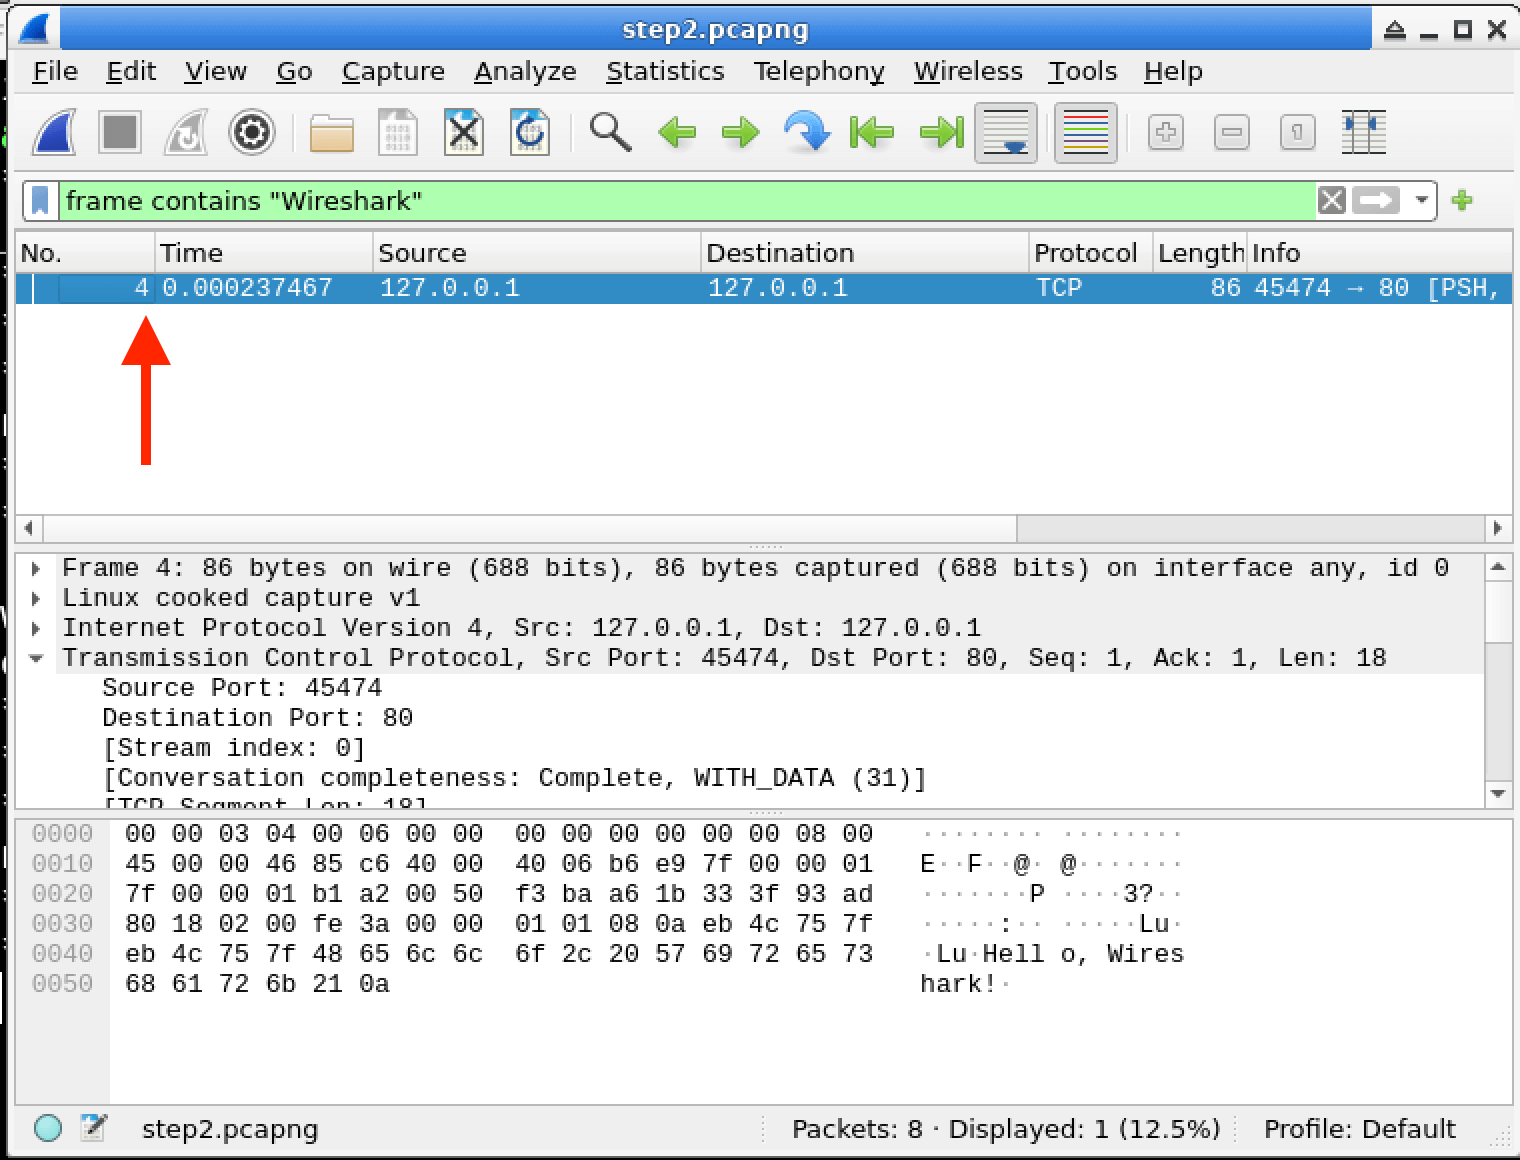
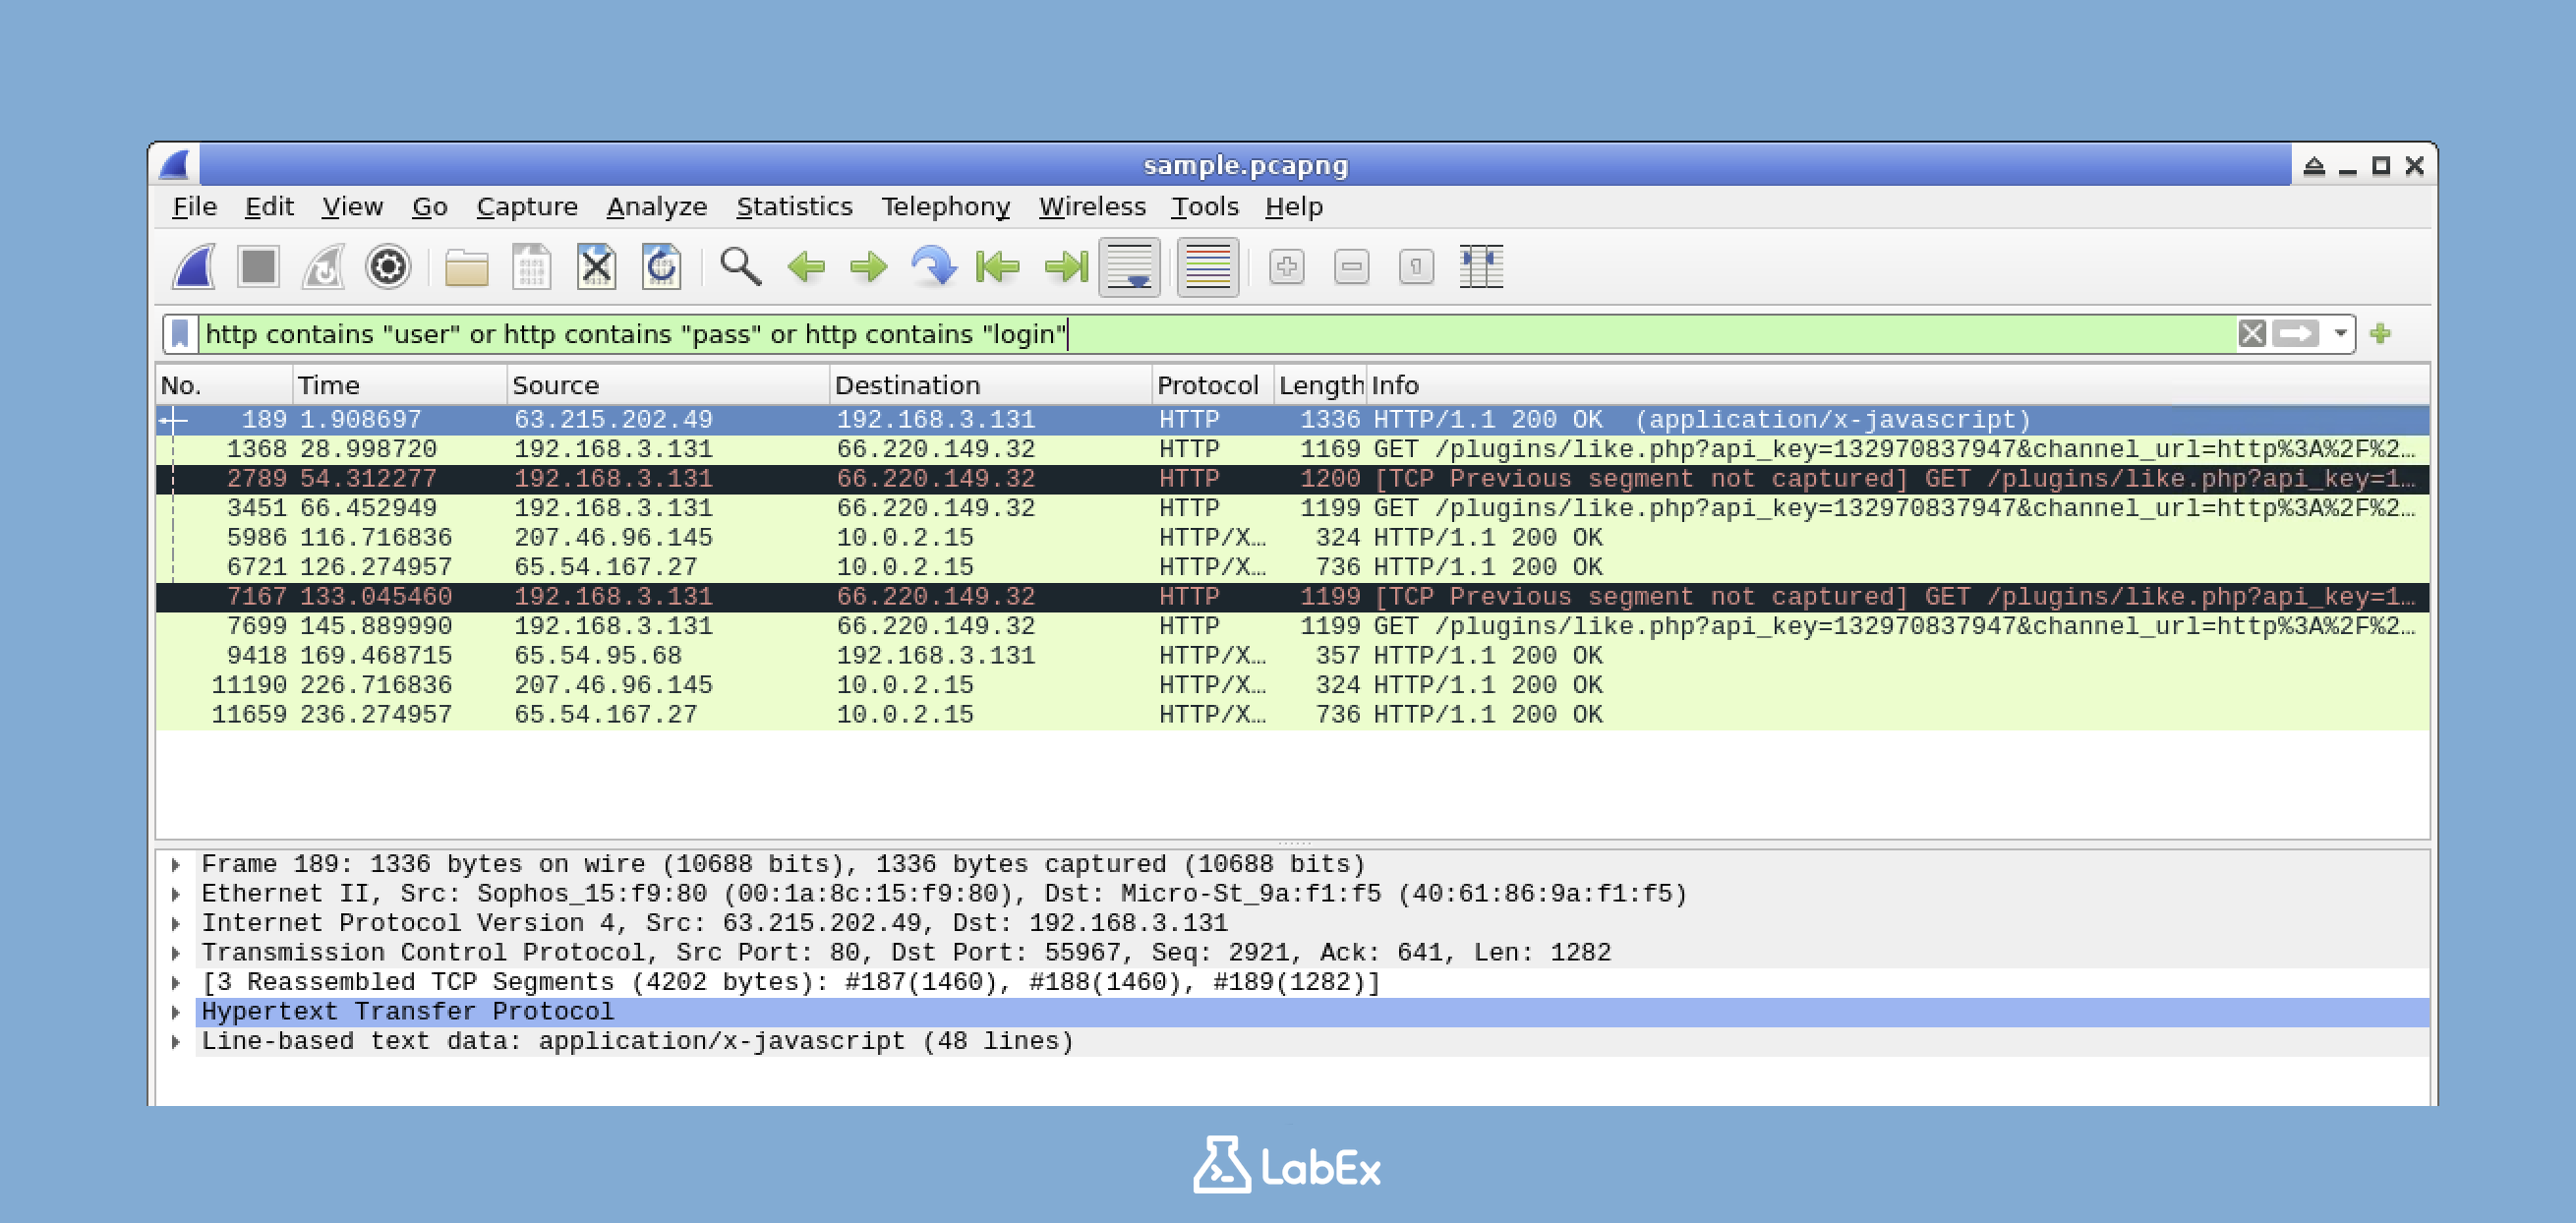
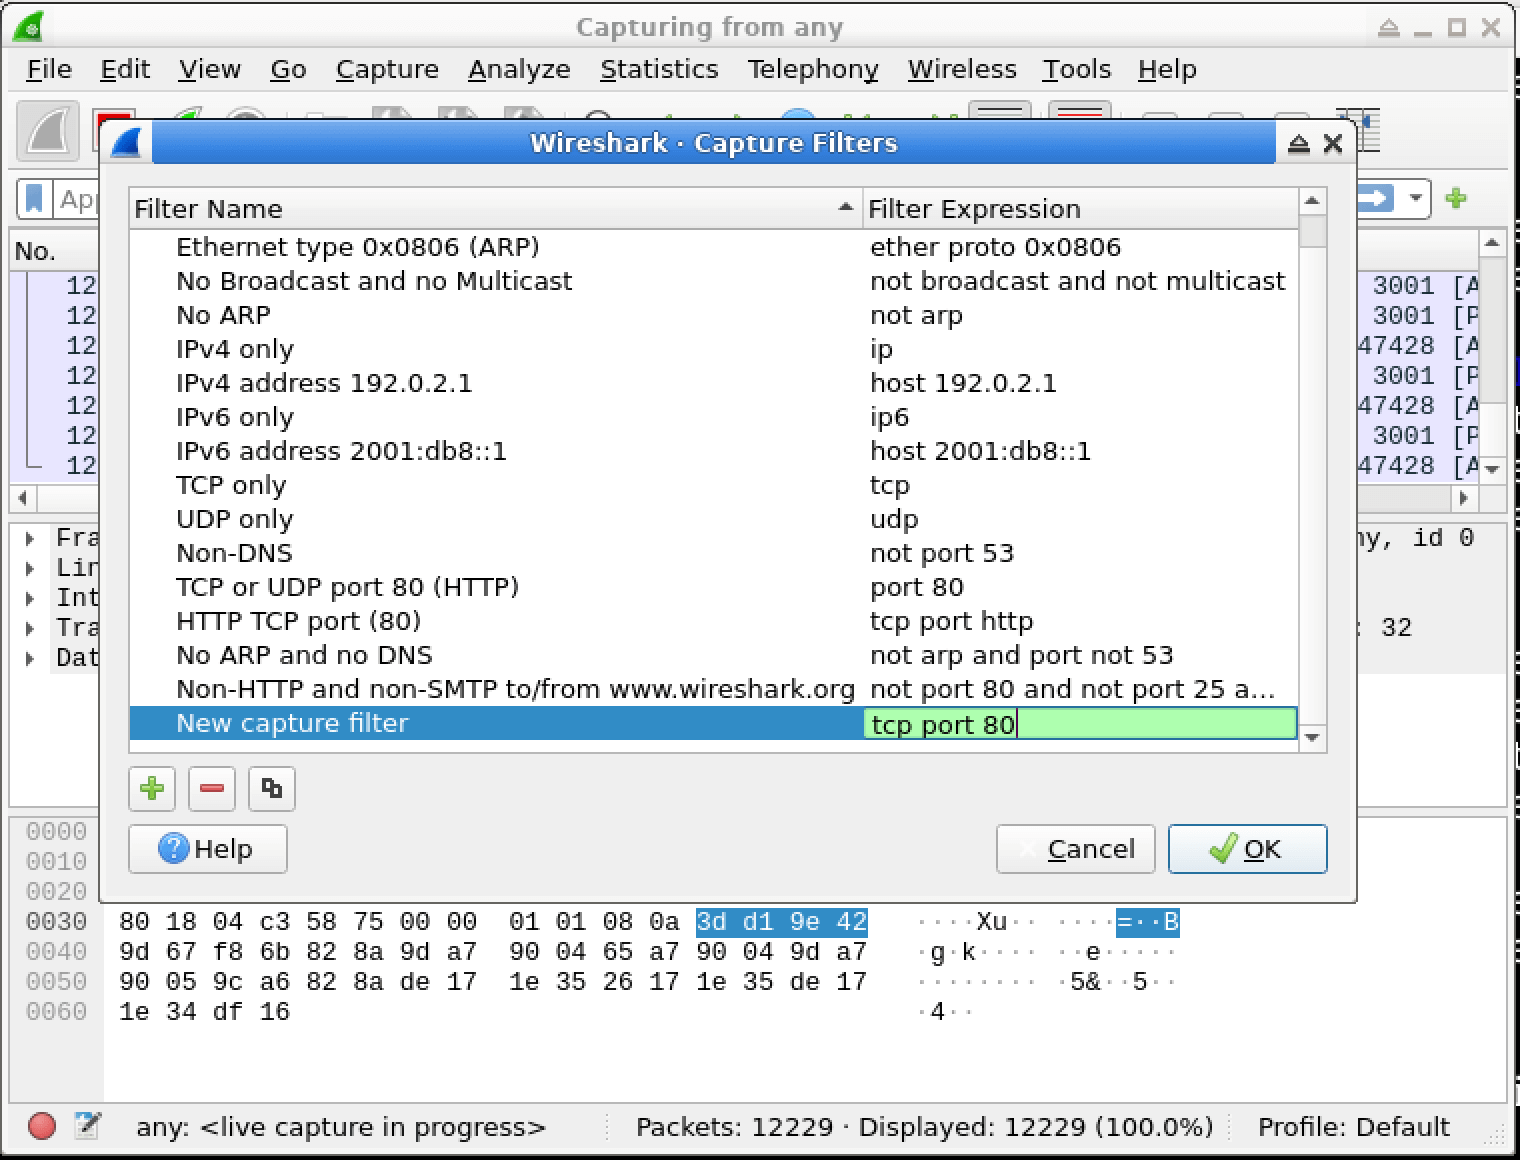
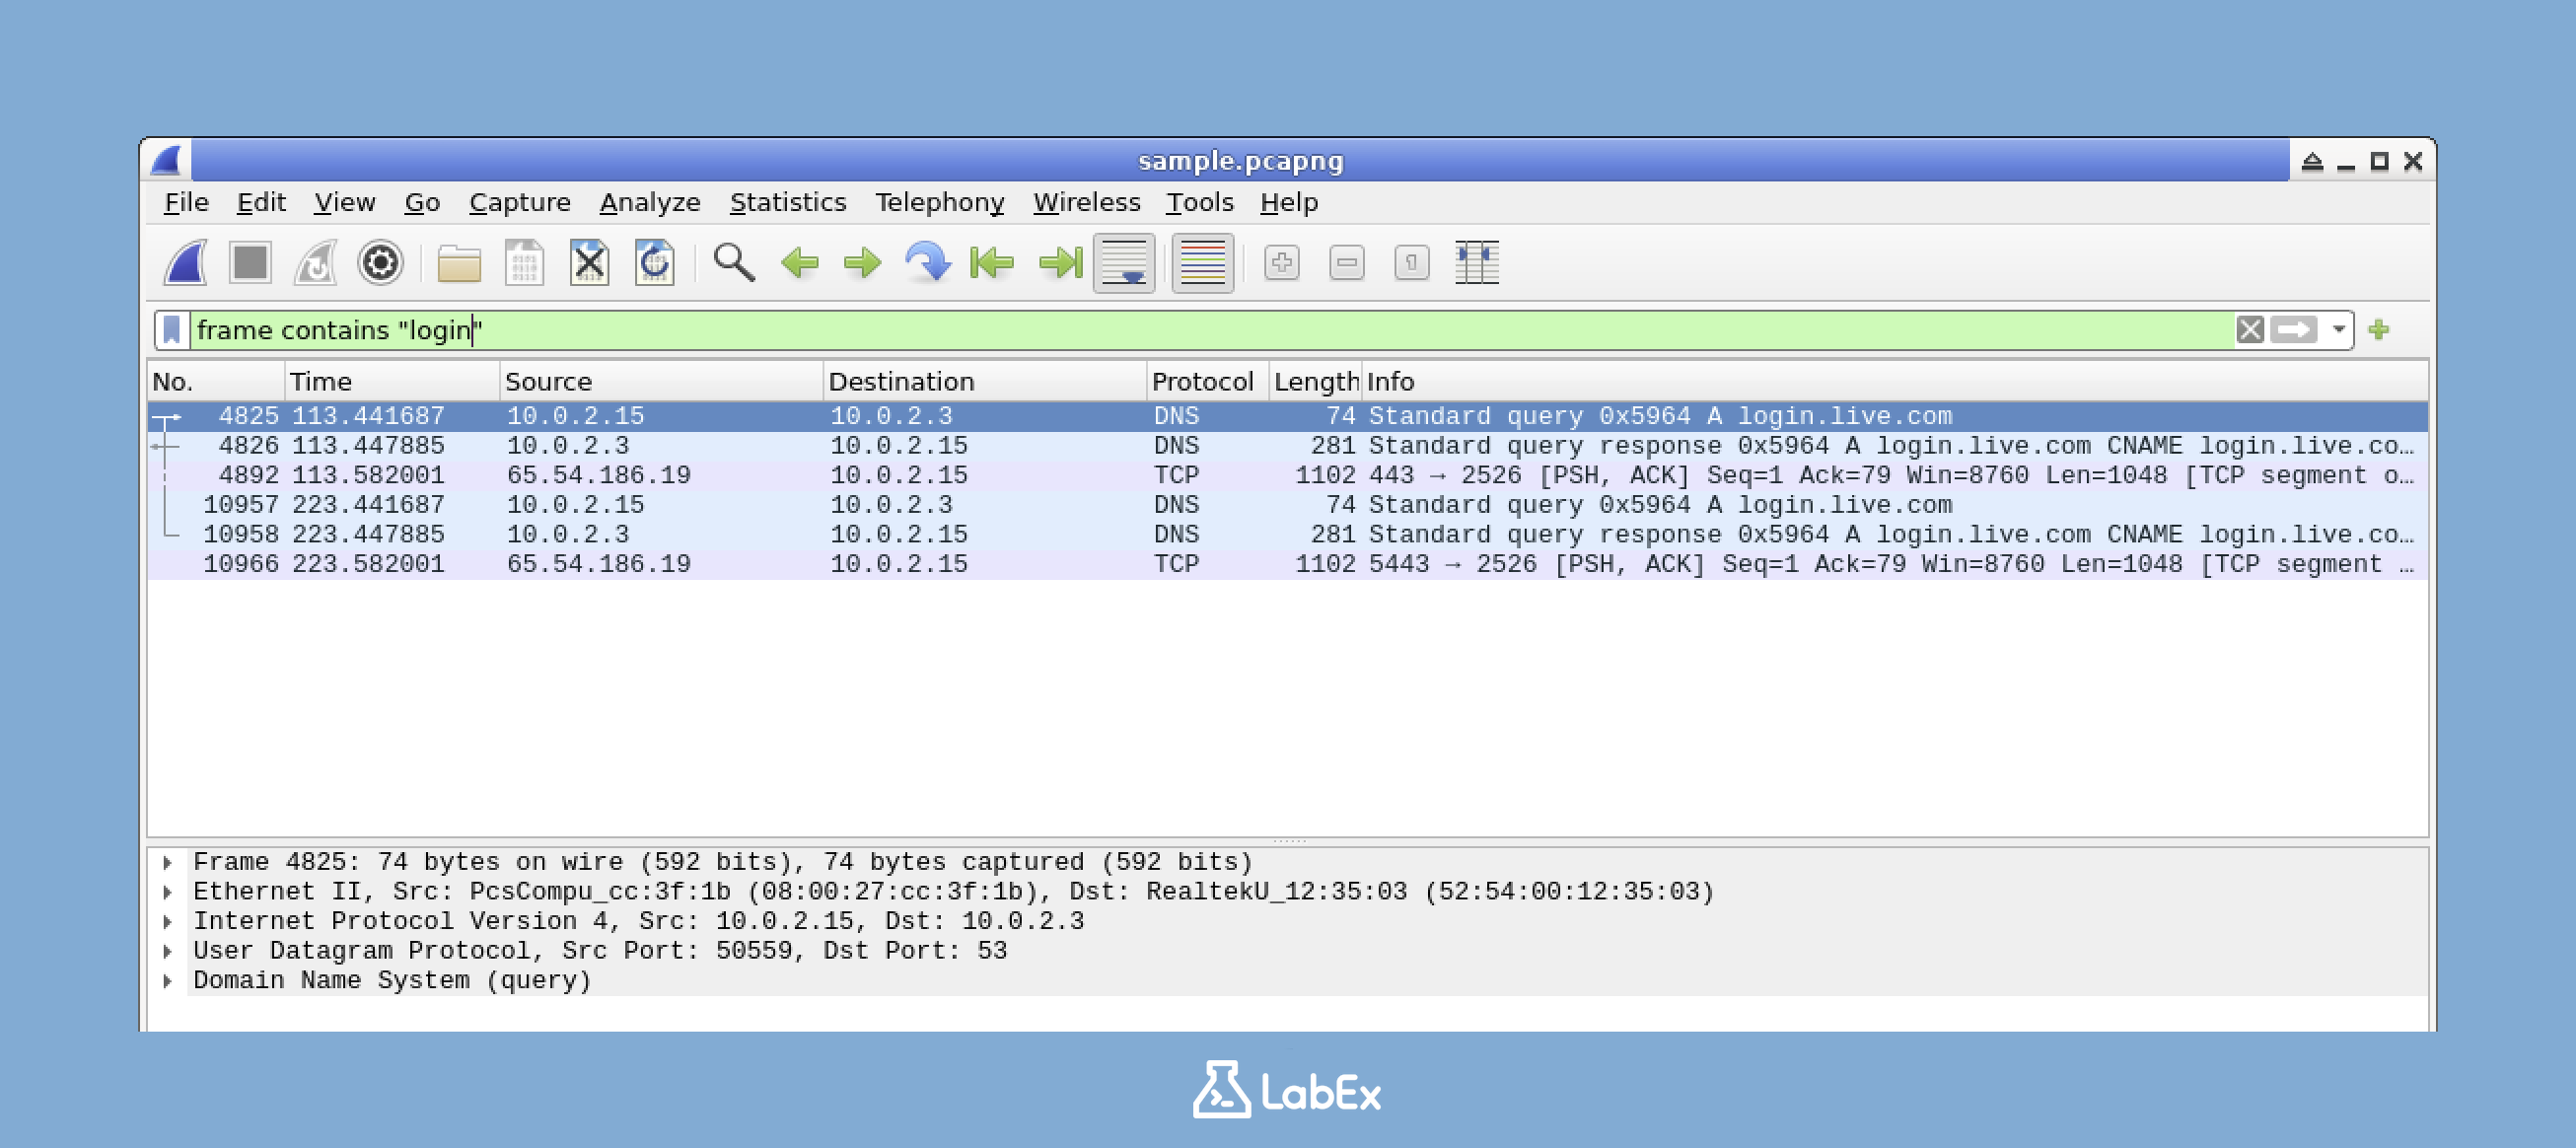
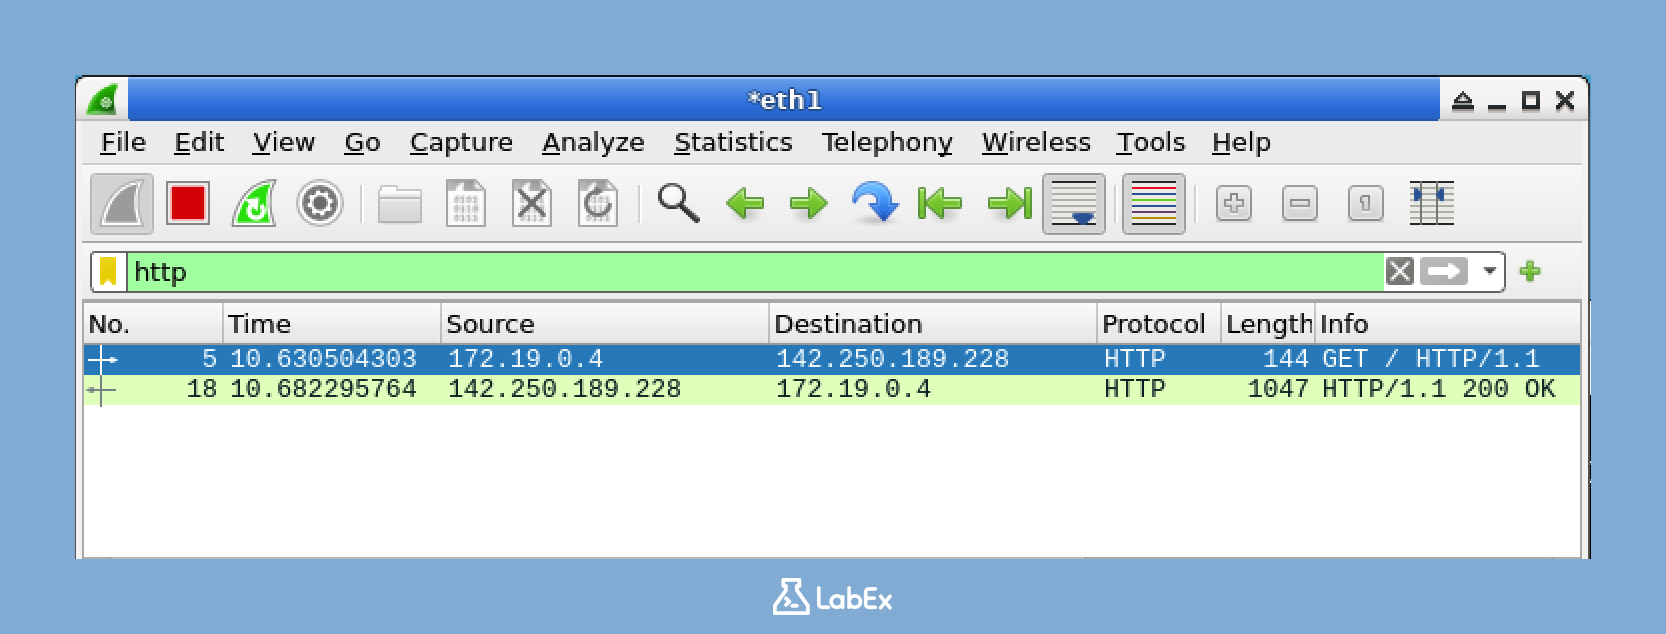
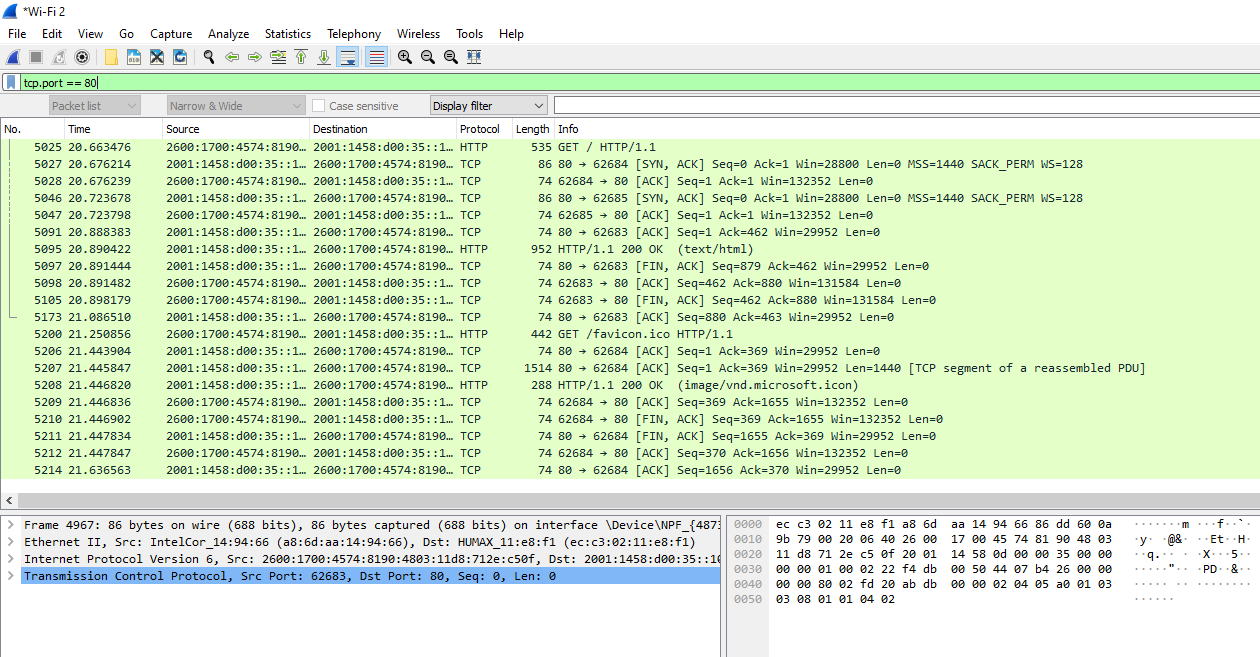
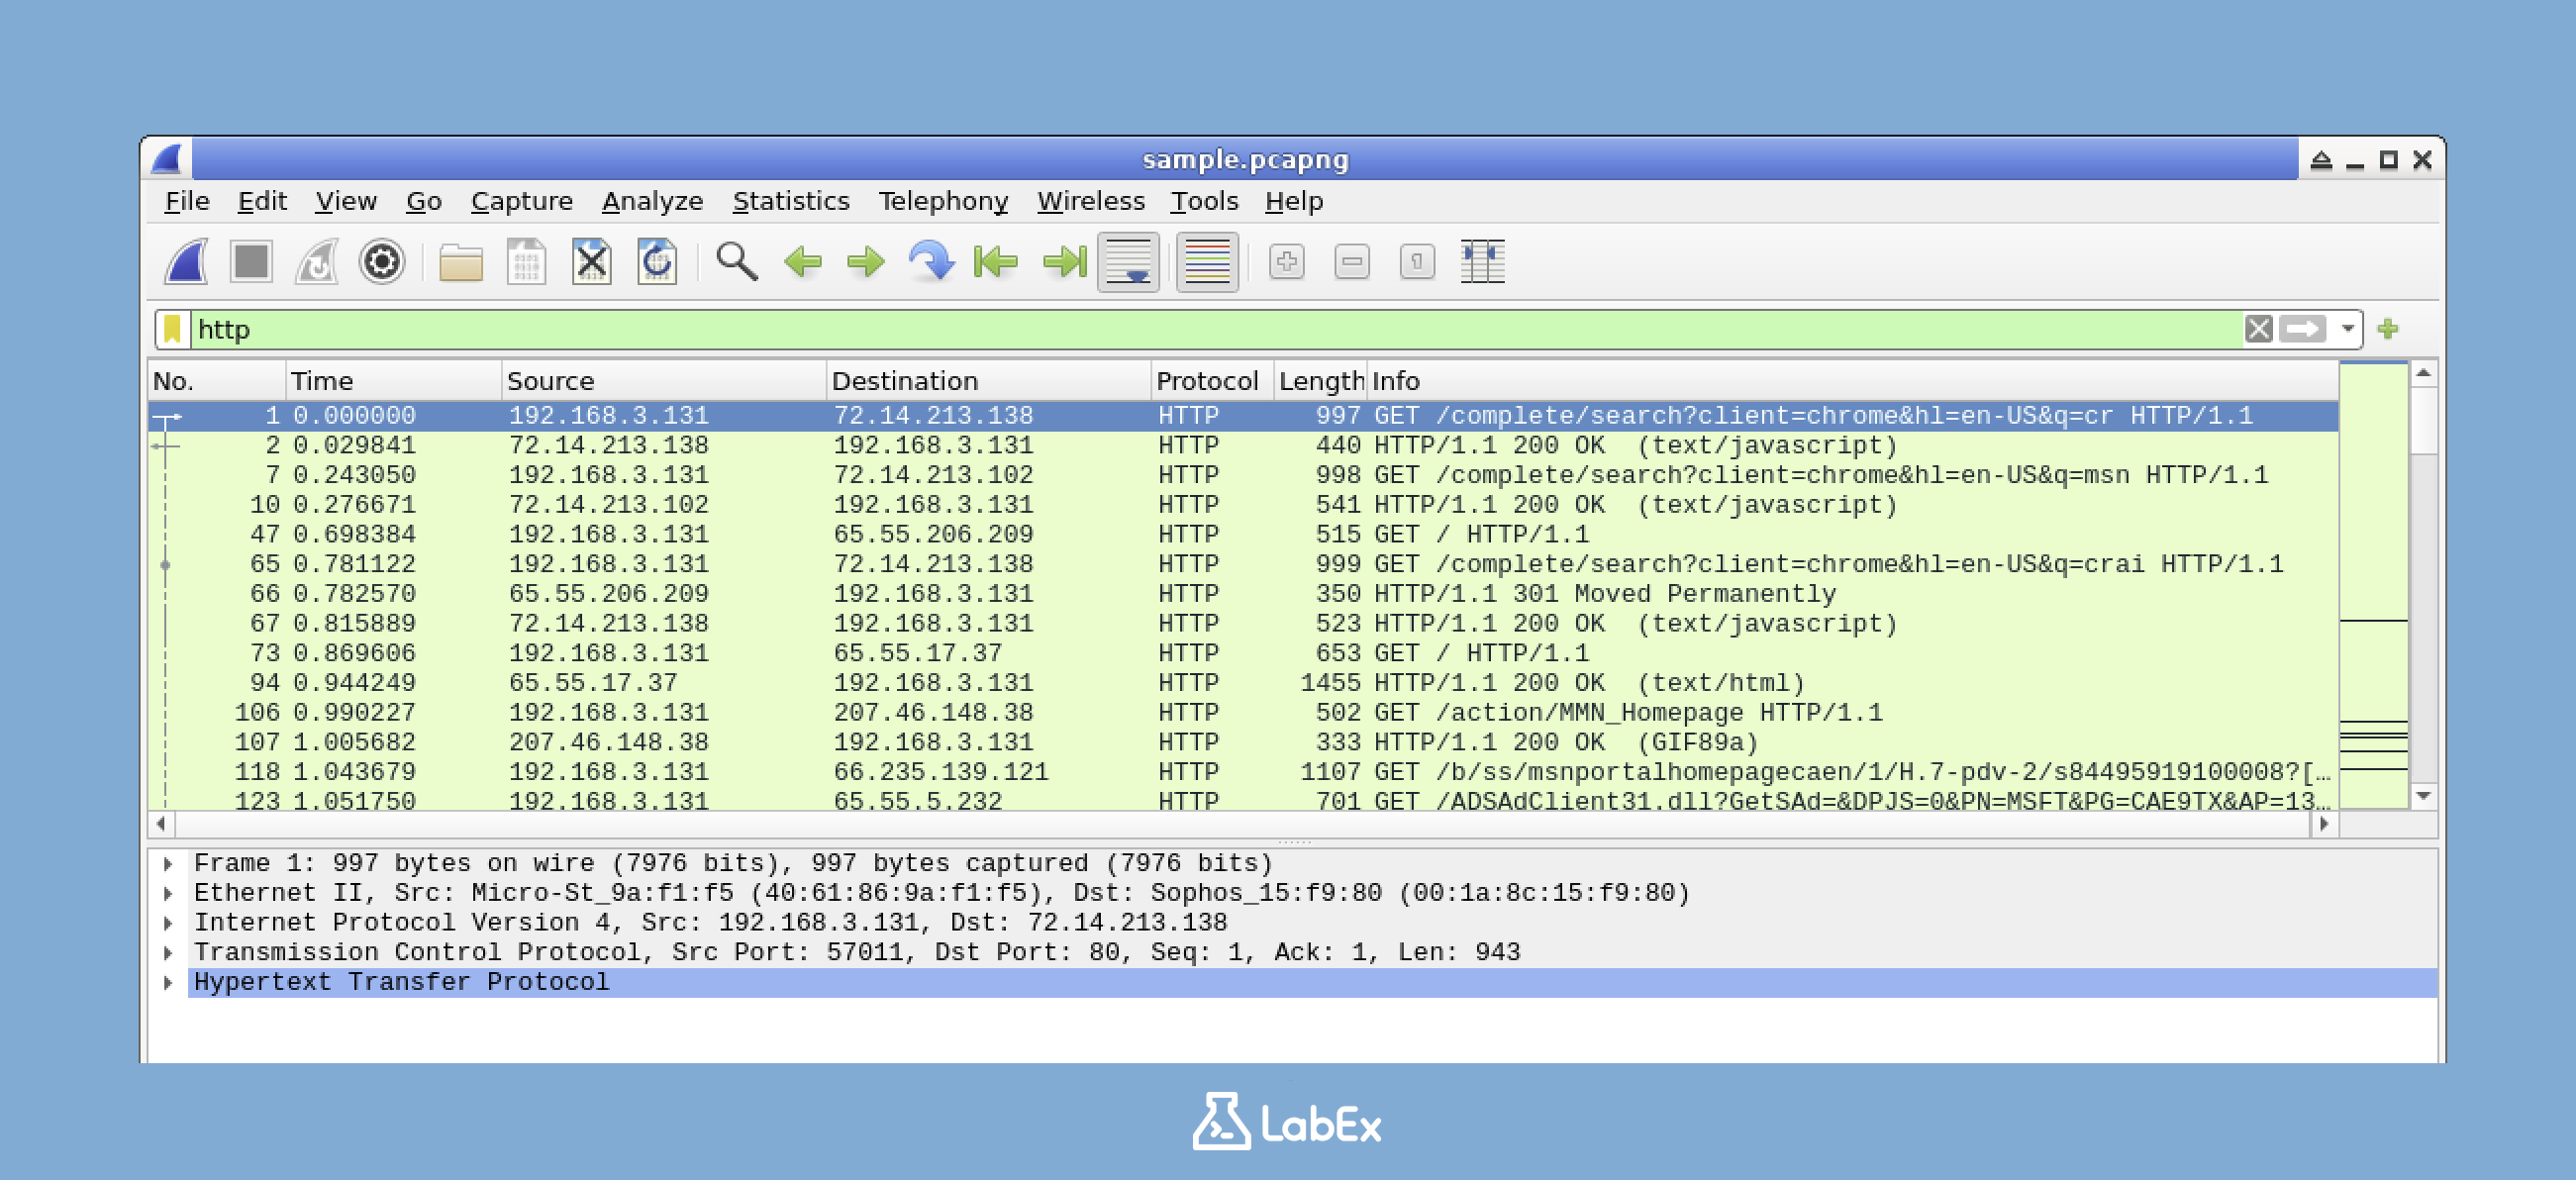
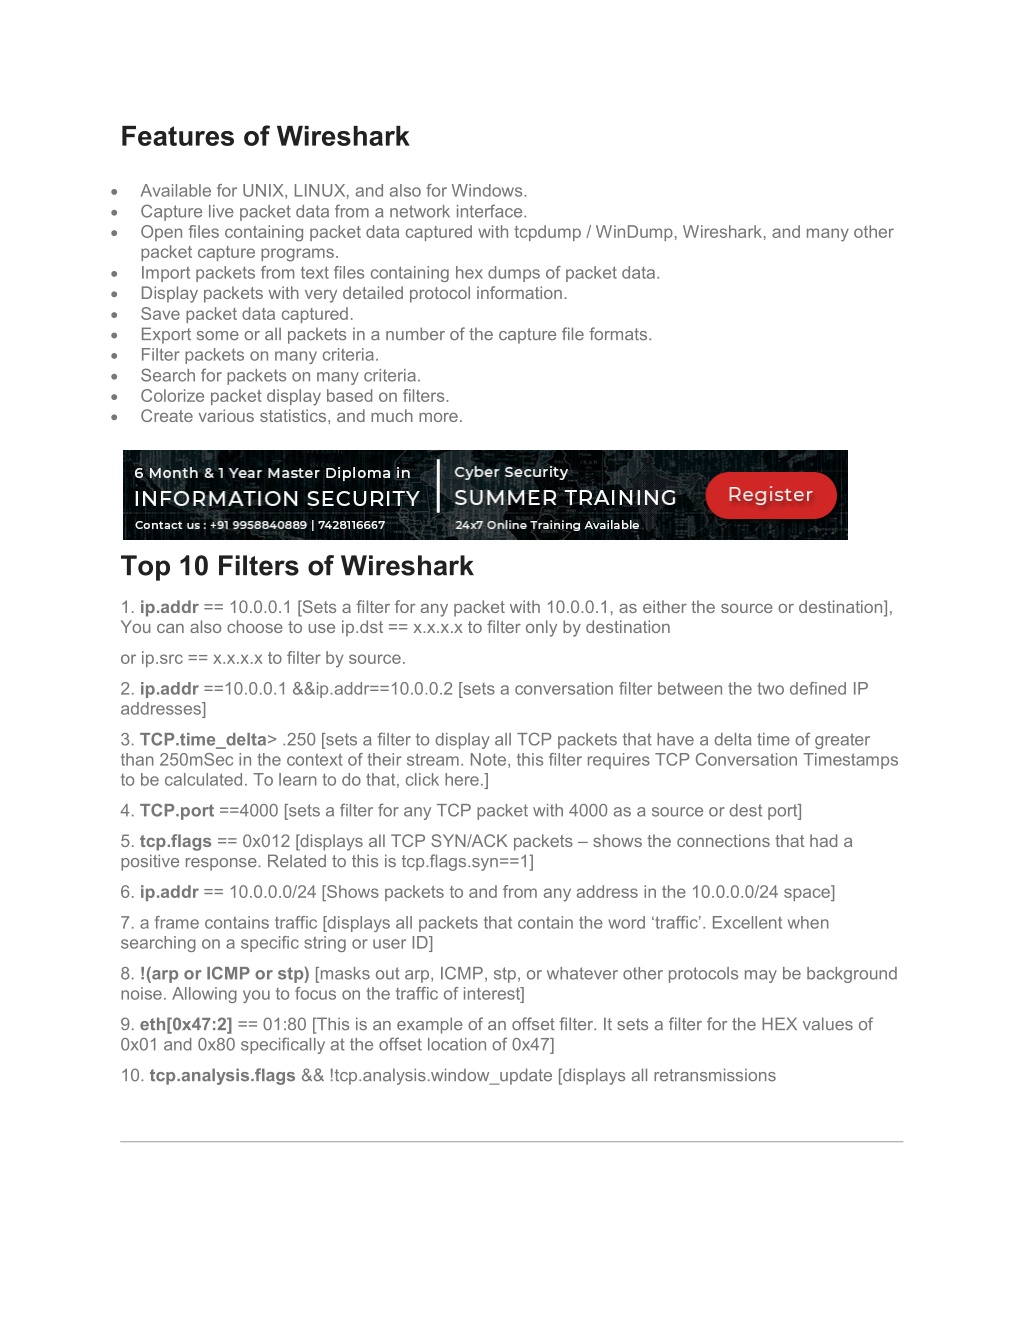
Display Filters: Filters applied to already captured data for more focused analysis. Essential Wireshark Filters and Their Use Cases. Here is a categorized list of Wireshark filters, along with examples of their application
Wireshark is a go-to tool for network administrators, used daily to analyze traffic for various purposes. In this article, weve highlighted key filters to streamline your analysis and make troubleshooting faster and more effective.
Chapter 2: Networking for Packet Analysts. The OSI model why it matters. IP networks and subnets.You can also analyze a the effects of TCP issues on network throughput by applying TCP analysis display filter strings to Wireshark's IO Graph, such as
Wireshark can analyze network traffic in real time or inspect previously captured packet data. This makes it a valuable tool for reviewing network behavior, troubleshooting, and identifying potential security threats.
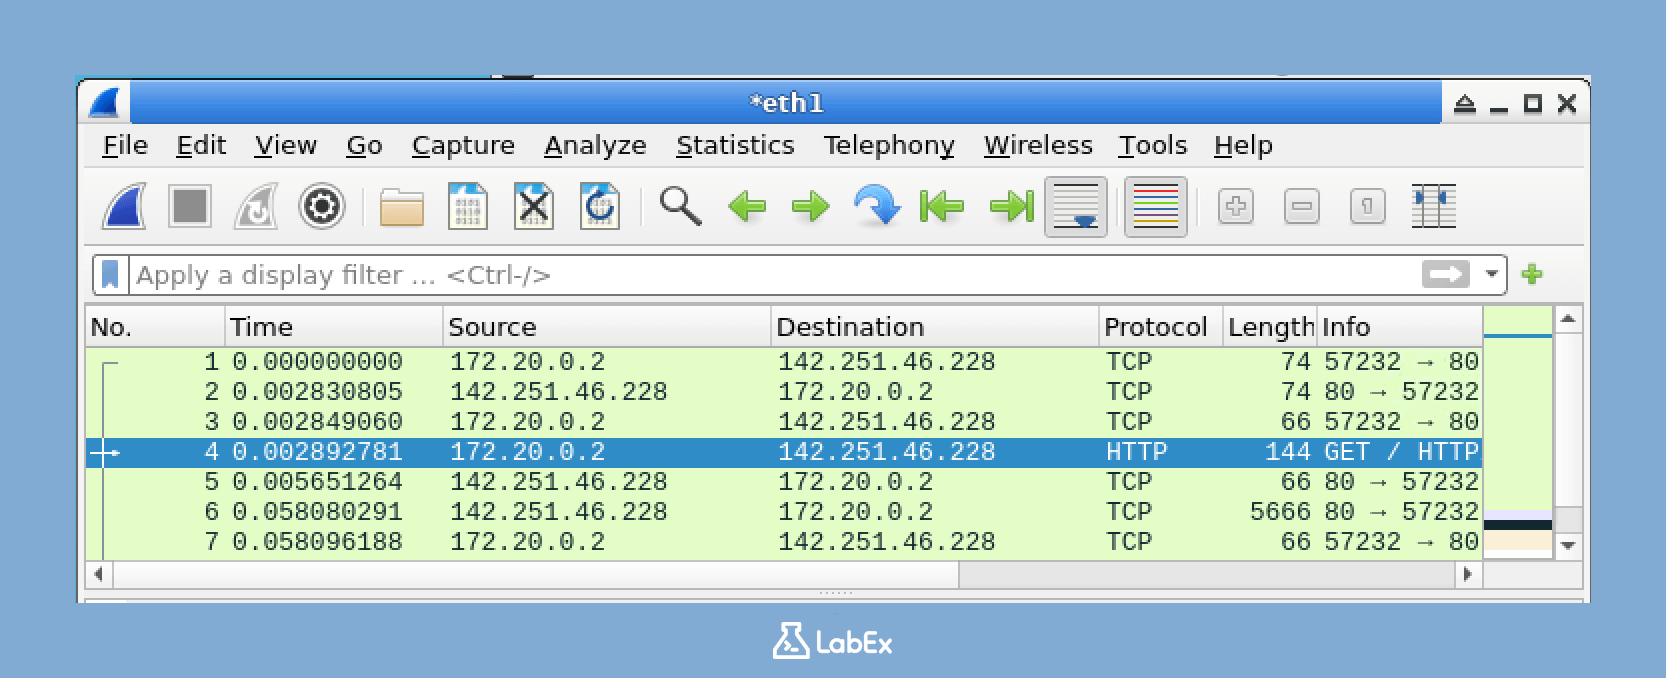
As we can see from the illustration, Wireshark Essential Filters For Network Analysis has many fascinating aspects to explore.
In this article, Ill show you how to analyze a PCAP file using Wireshark filters step by step. Whether youre new to packet analysis or sharpening your threat-hunting workflow, this guide will help you spot the meaningful signals inside the chaos.
Helps troubleshoot network issues and analyze performance. Essential for security investigations and protocol debugging. Key Features. Wireshark analyzes network packets in detail, similar to how a voltmeter inspects electrical signals.
Learn how to use Wireshark to track network activity, view specific frame, tcp, ip and http information, view specific packets being sent and received on the...
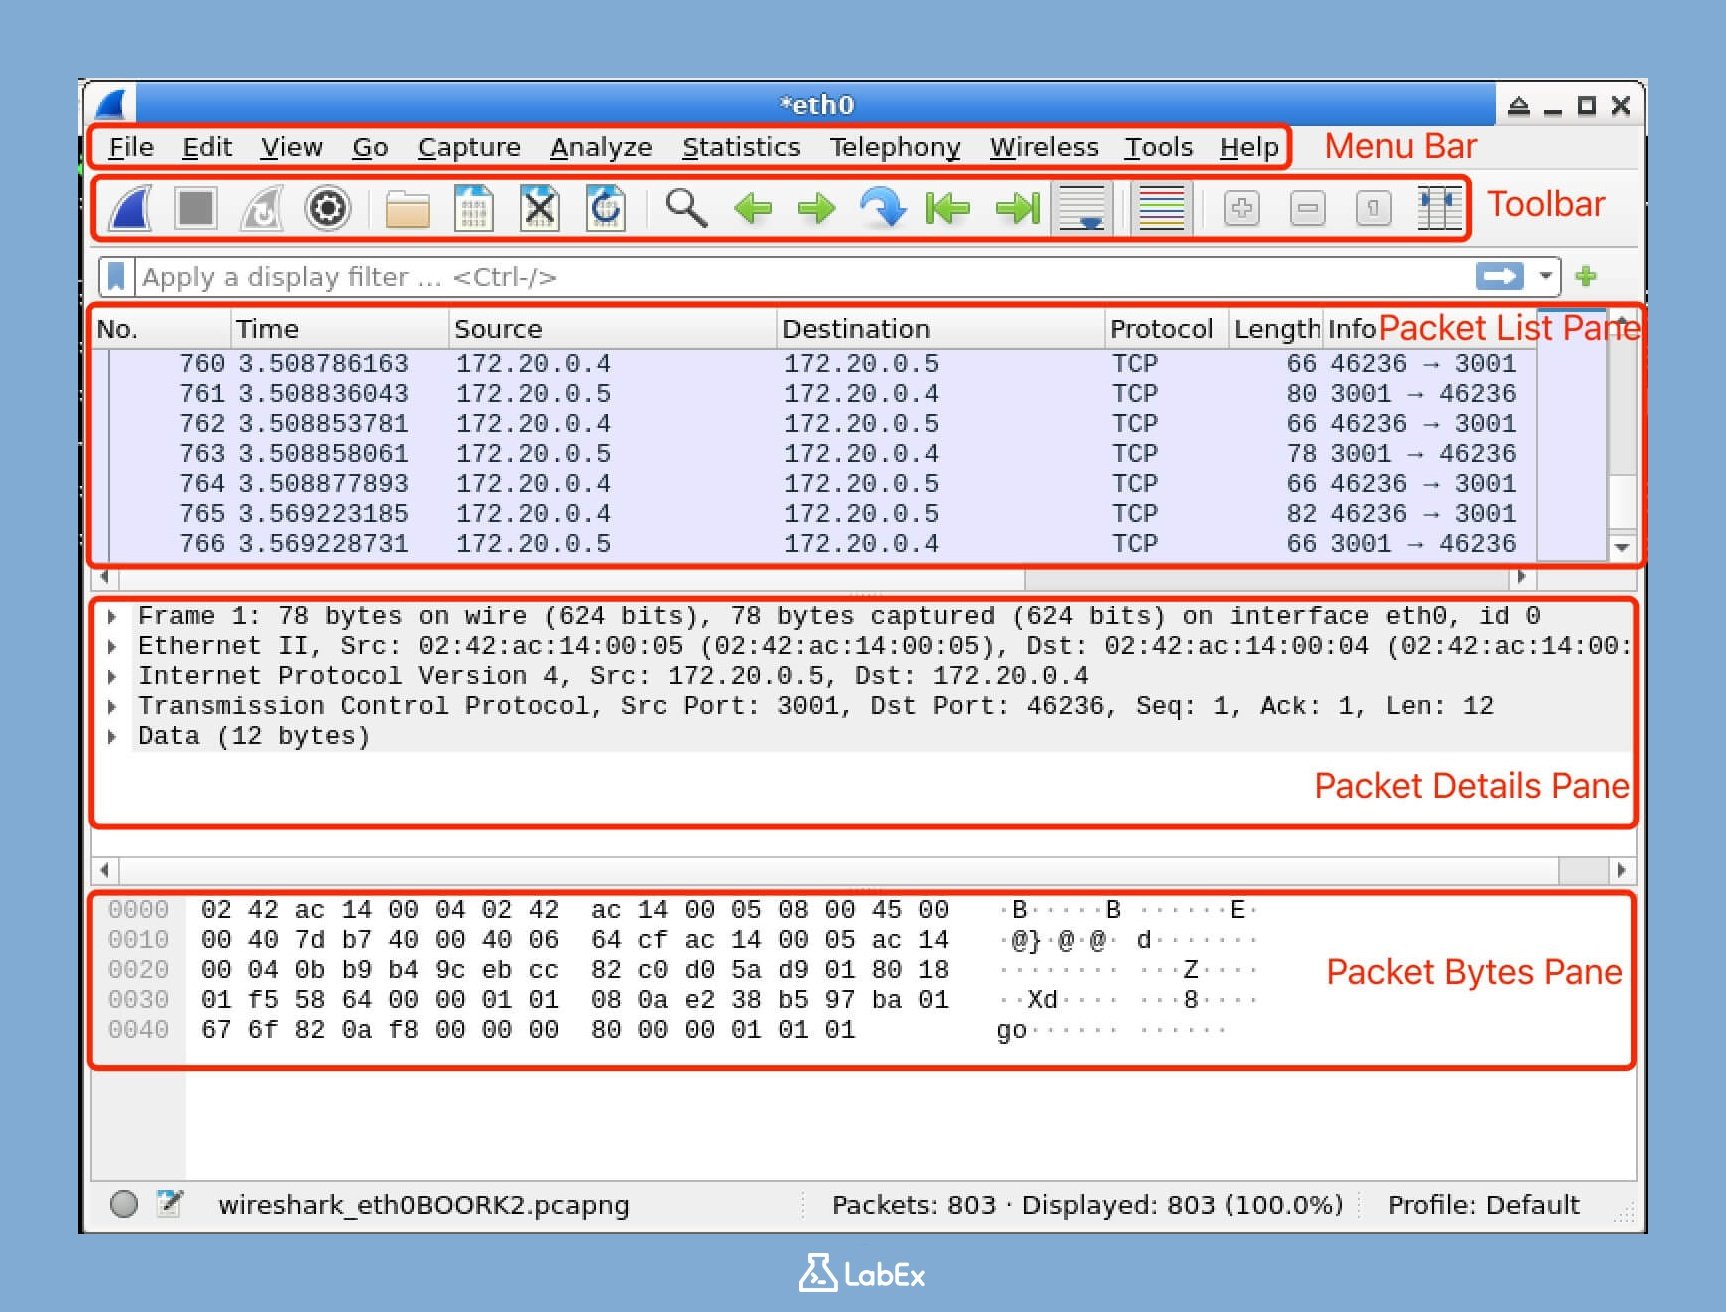
Effective filtering in Wireshark allows analysts to isolate critical data, identify malicious activity, and streamline investigations. This guide covers essential Wireshark filters for security analysis, threat detection, and network forensics.
wireshark-filter - Wireshark display filter syntax and reference.Filters are also used by other features such as statistics generation and packet list colorization (the latter is only available to Wireshark). This manual page describes their syntax.