Blue tick badge scam targets Facebook users
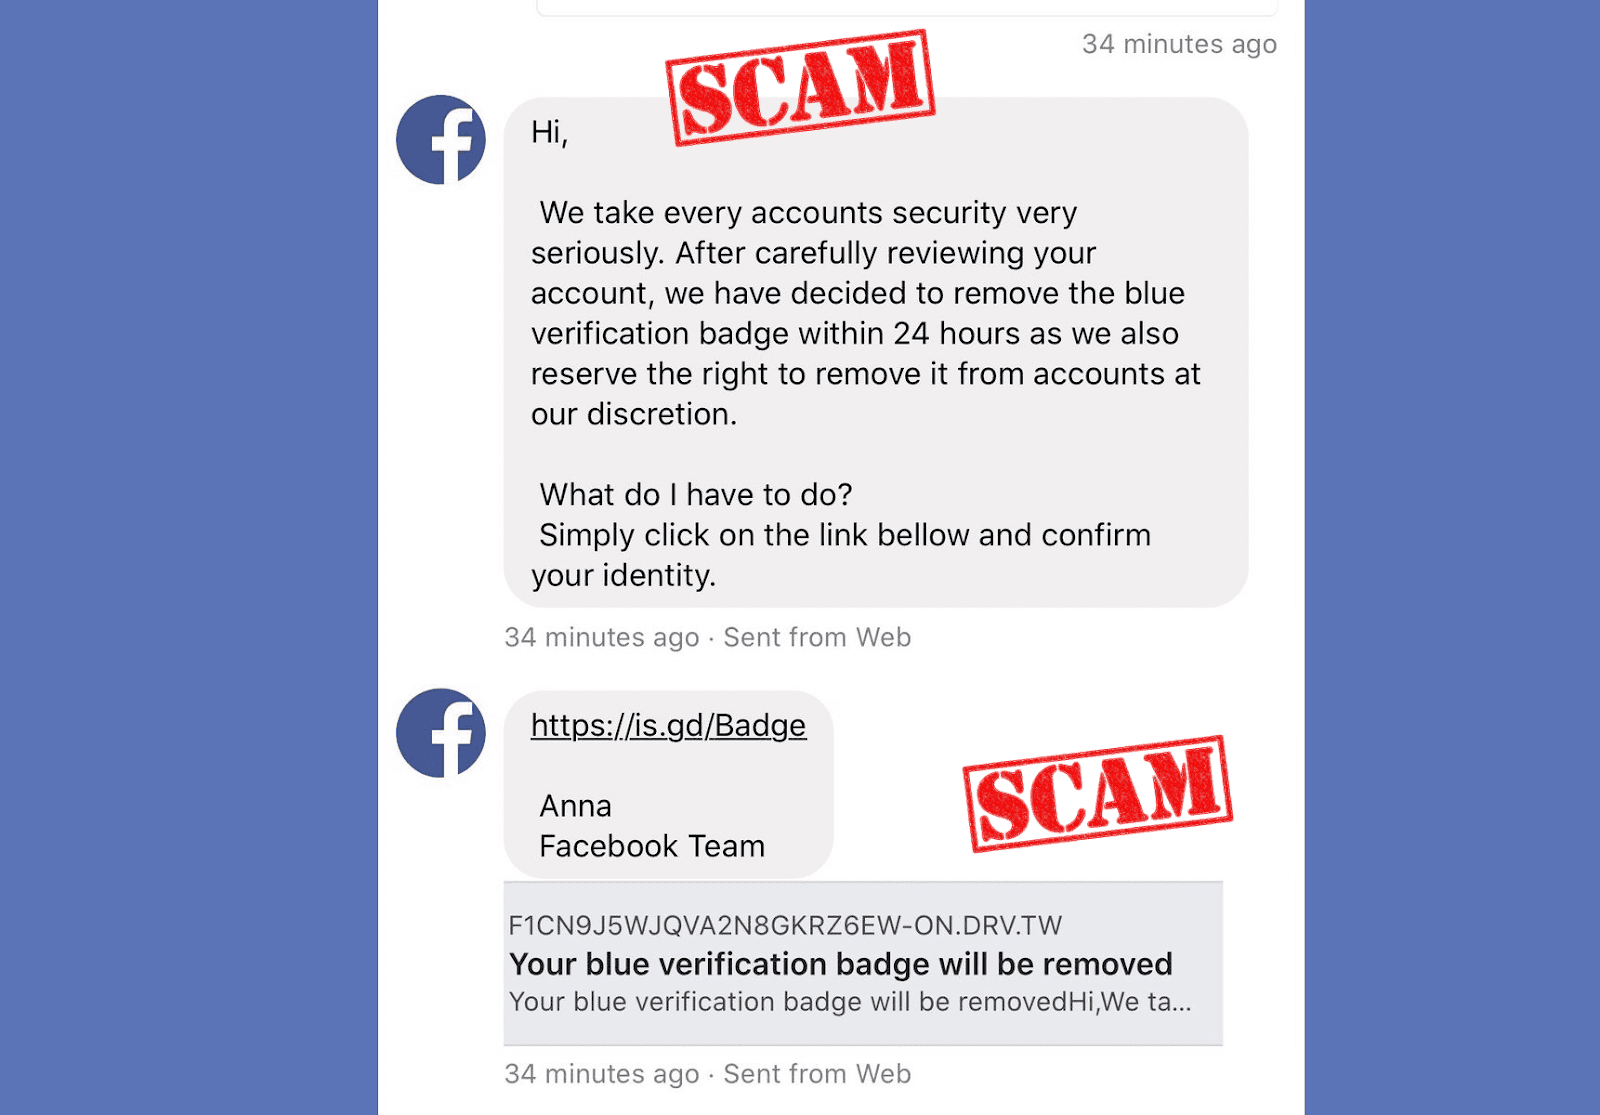
MailGuard has intercepted a new phishing campaign impersonating Meta, designed to harvest personal information, Facebook login credentials and two‑factor authentication codes from page owners and business administrators. The emails claim the recipient's Facebook Page is eligible for the blue verification badge and prompt them to complete a verification process to secure their identity and ...
Meta, the parent company of platforms such as Facebook and Instagram, plays a major role in both personal communication and business operations worldwide. A new phishing campaign is emerging that abuses Meta's verification system and 2FA tokens to gain account access and steal sensitive information. This campaign is particularly convincing and targets both individual users and businesses ...
New Phishing Attack Targets Facebook Users to Steal Login Credentials

Phishing campaign targets Facebook users with fake security emails, cloaked links, and counterfeit login pages to steal credentials.
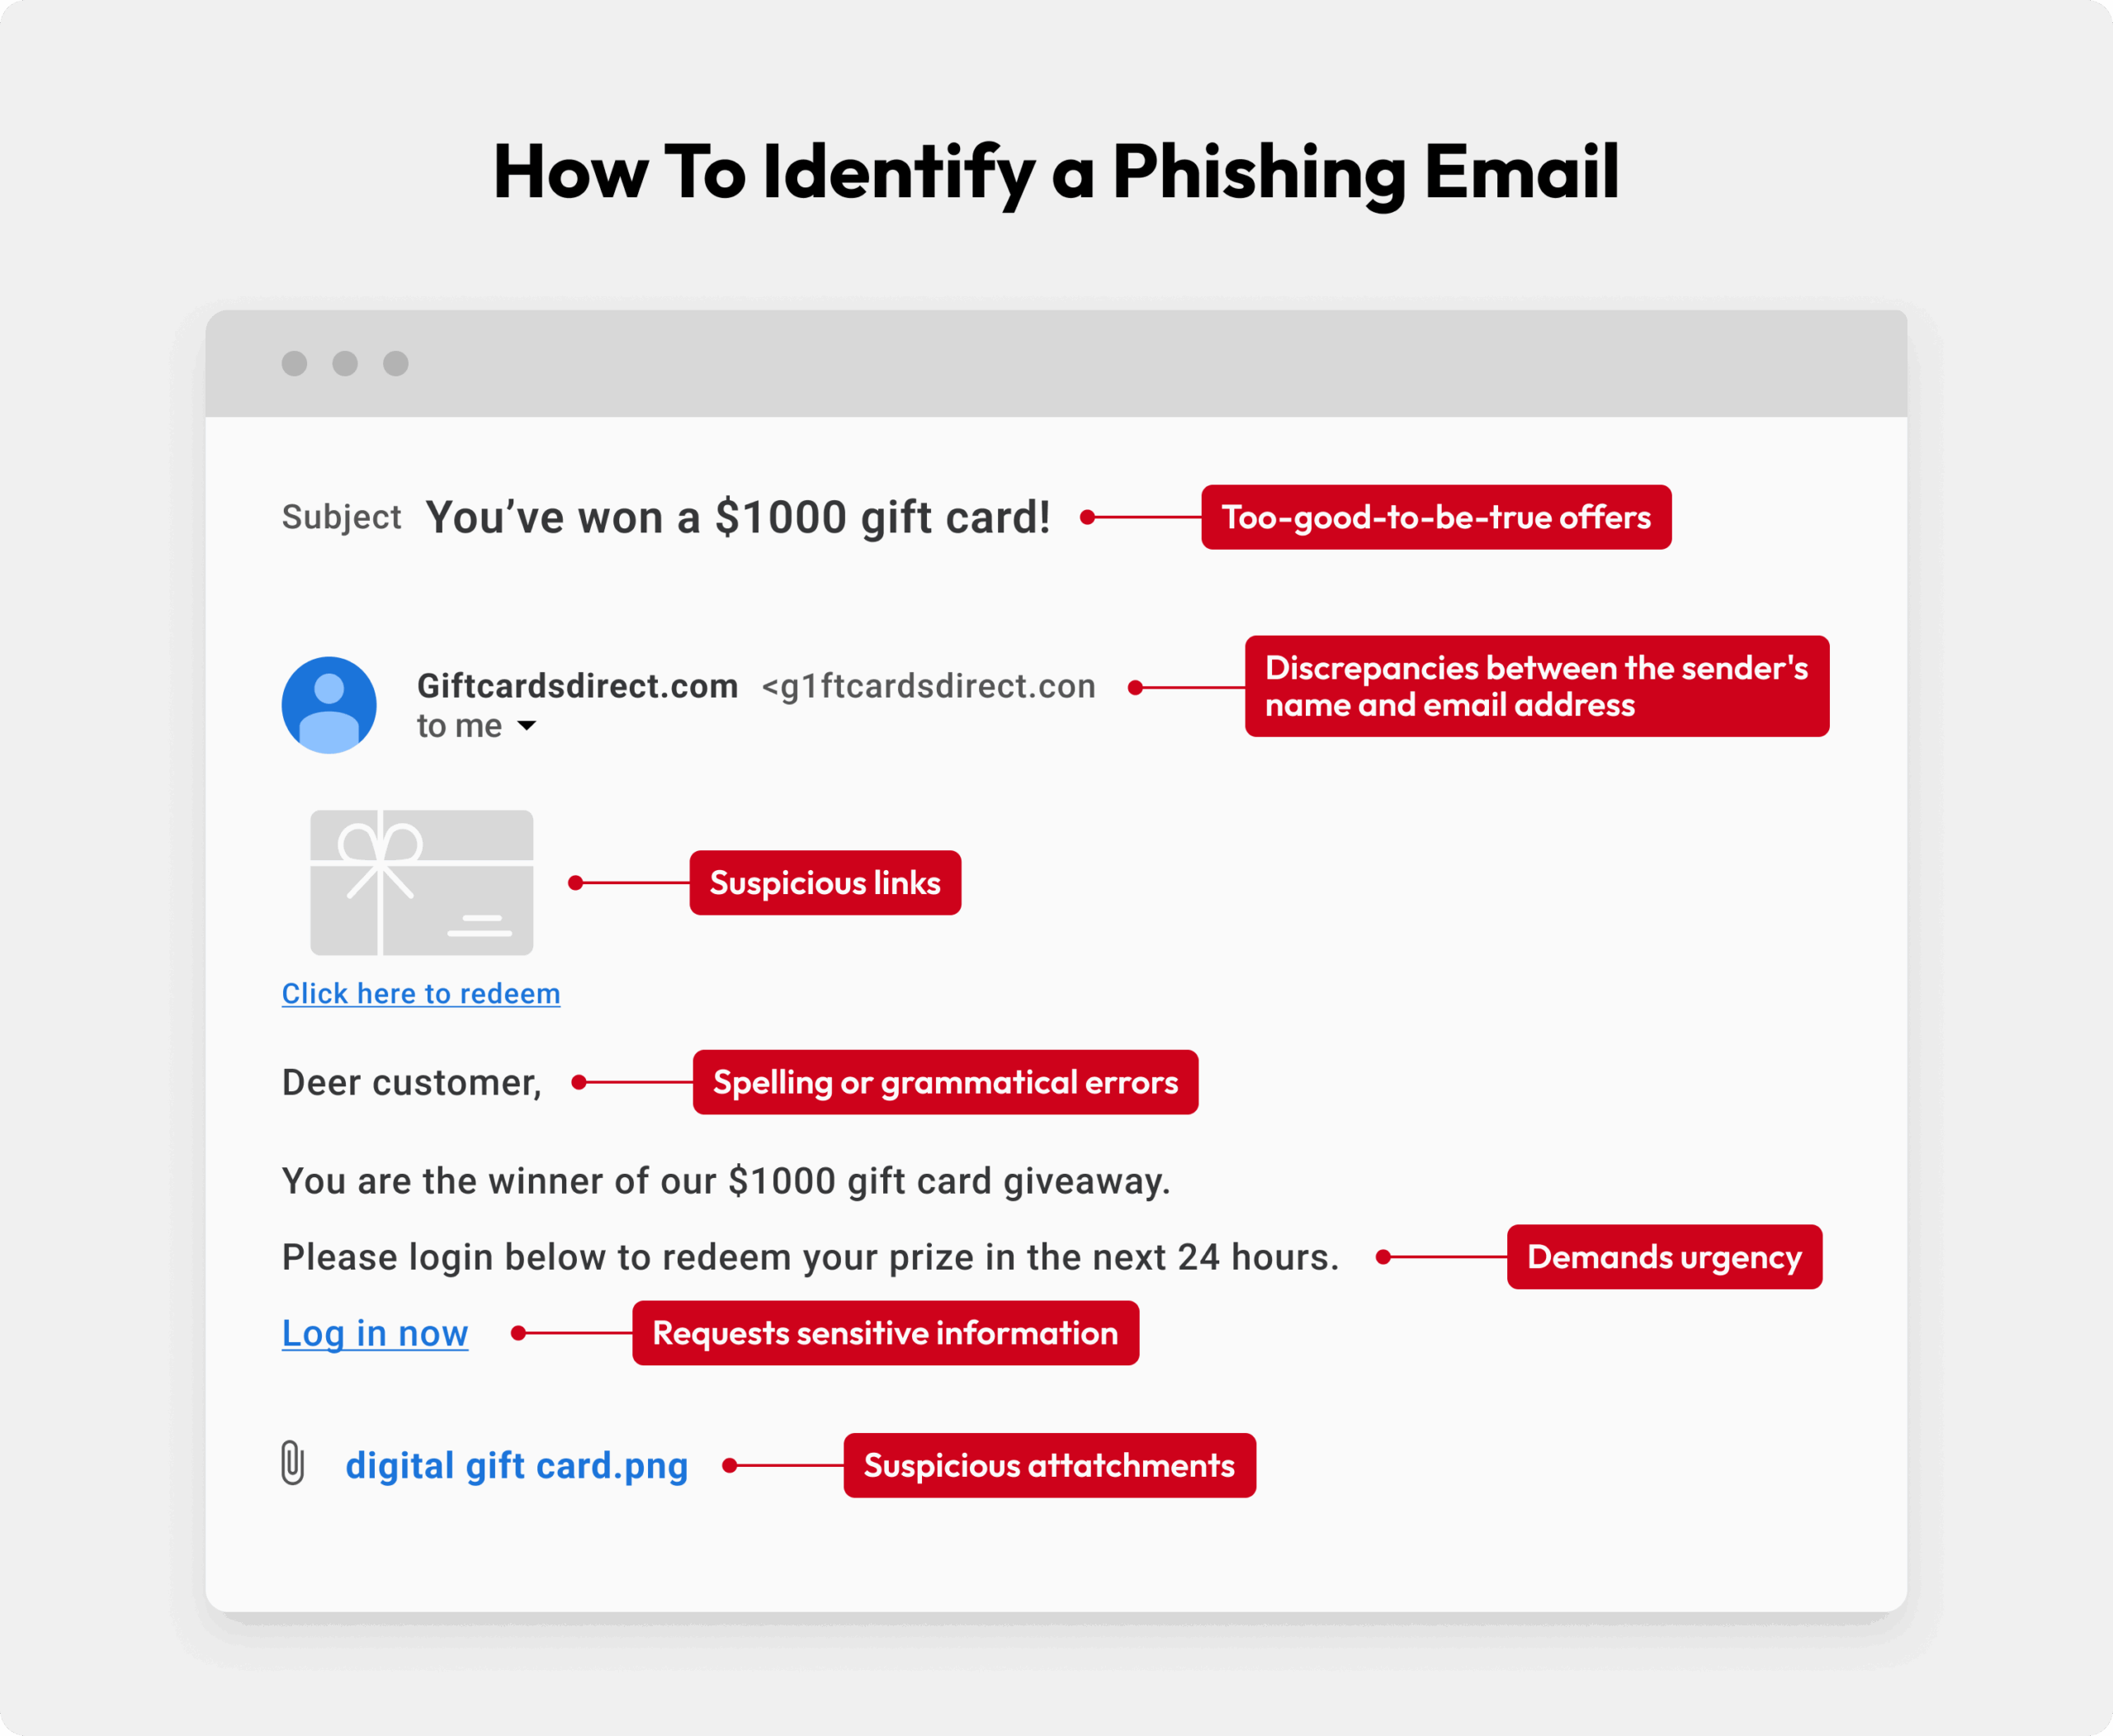
Here's how this campaign works—and how to avoid falling for it. Mailto: phishing targets Facebook accounts This scam begins like many do, with an unsolicited email.
Phishing Attacks Targeted Facebook Users With Fake Verification Offer
As detailed in the Huntress blog post on July 7, the phishing lure claims to offer Facebook Business account users a way to 'protect their brand' with a verified badge. While Facebook does offer a real verification service, it is based around a paid subscription, with the process starting inside the Facebook ecosystem, not via an email.
A sophisticated phishing campaign impersonating Meta is targeting Facebook users through Messenger, threatening account deletion within 24 hours in an attempt to steal login credentials and personal information. The fraudulent message, sent from an account calling itself "Meta Verrified" — notably misspelled — displays the Meta logo and includes a suspicious PDF attachment designed to ...
This Facebook Phishing Attack Could Steal EVERYTHING
The campaign, first observed on December 20th, has already reached over 12,000 email addresses. The majority of targets are located in the U.S. (45%) and Europe (45.5%), with a smaller number in Australia. Deceptive Tactics of the Facebook Phishing Attack This Facebook phishing campaign uses a sophisticated approach.
The scam messages feature the misspelled name "Meta Verrified," alleging the tech company detected "unusual activity" on a Facebook user's account.
New ClickFix Campaign Hijacks Facebook Sessions Using Fake Verification ...
ClickFix campaign steals Facebook session tokens via fake verification pages, using social engineering to target creators.