Understanding Encryption of Data
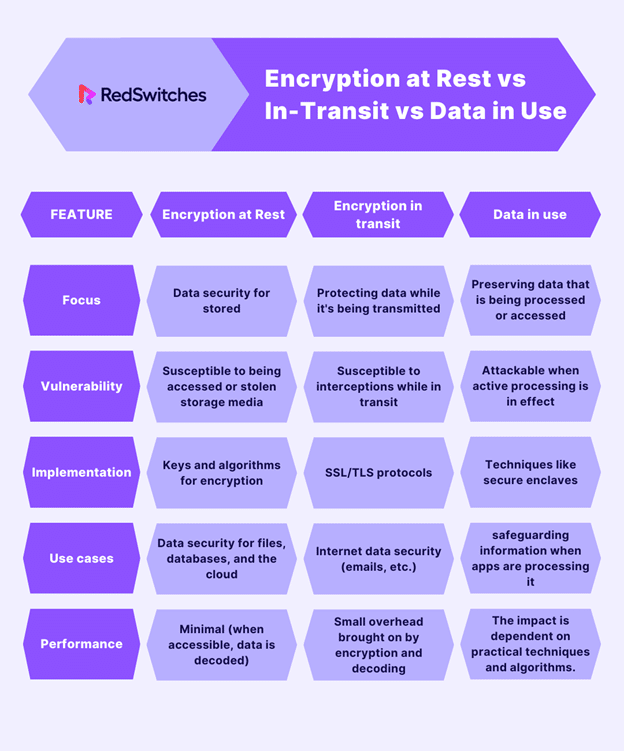
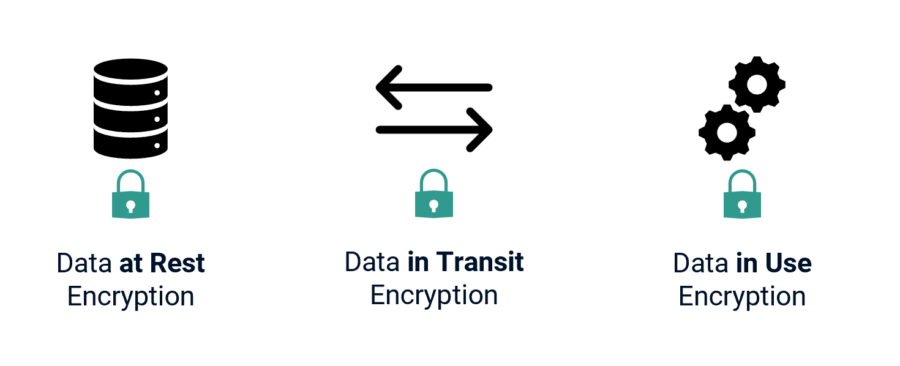
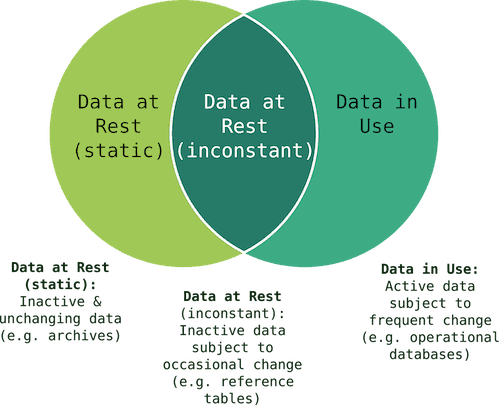
Unlike the static data secured by encryption of data at rest or in transit technologies. Encryption of data in use is used to secure the most valuable and active data within the organization wile that data remains fully encrypted—No decryption necessary to support the operational application (or query) layer.
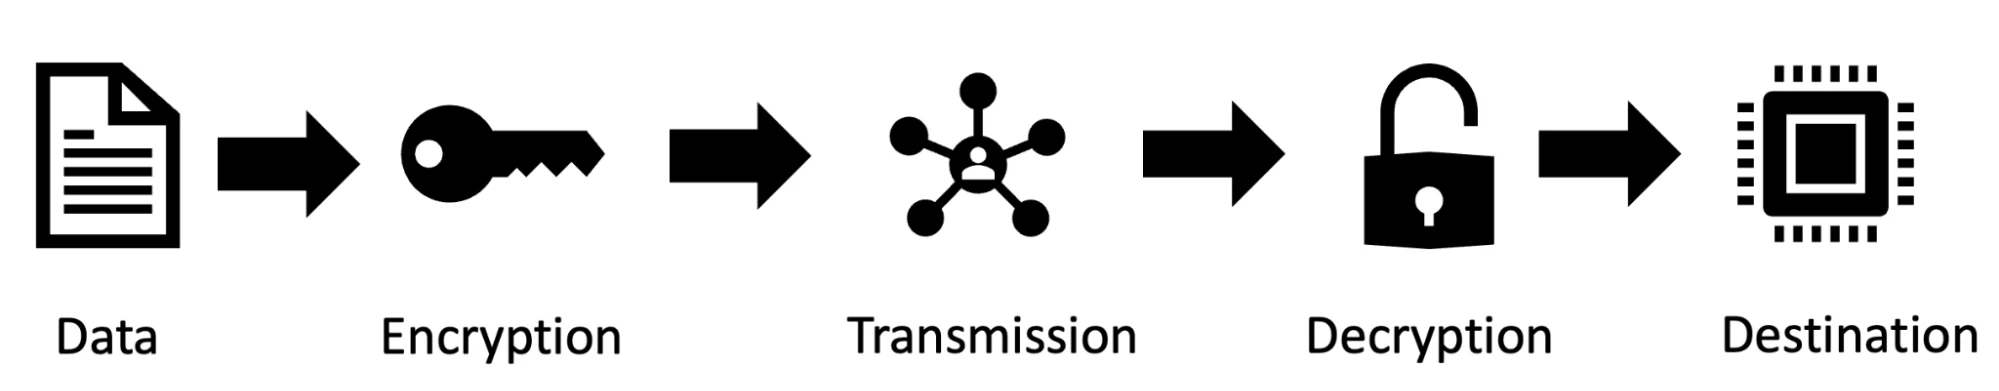
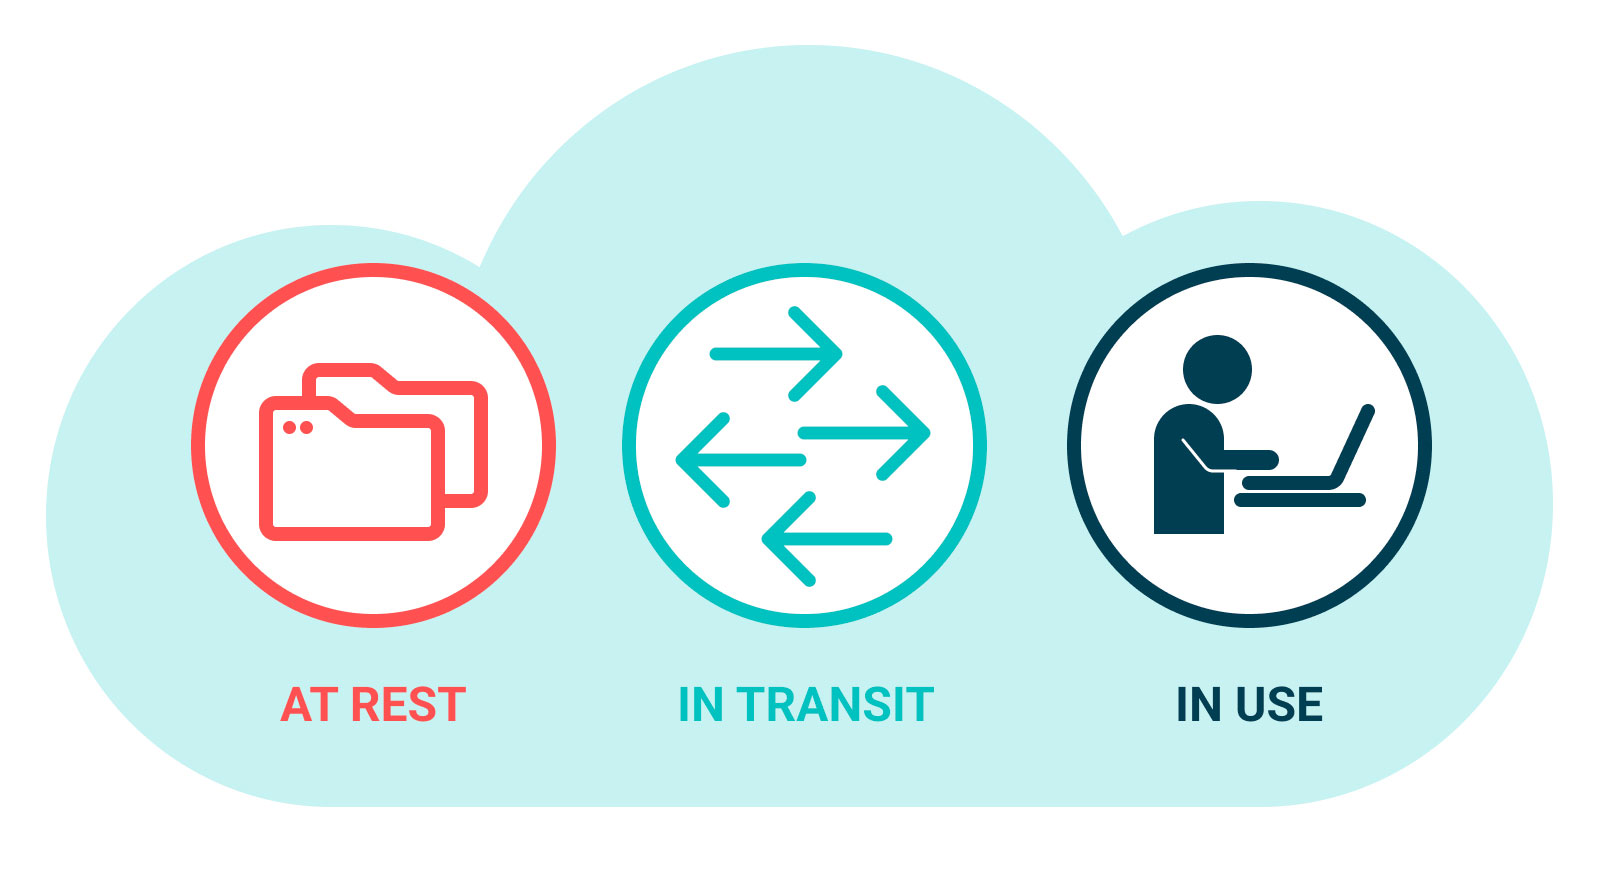
Data encryption is a core component of modern data protection strategy, helping businesses protect data in transit , in use, and at rest . The risk profile for data varies for each of these three states. Best practice approaches and technologies can help companies head off threats to their data wherever it may be.
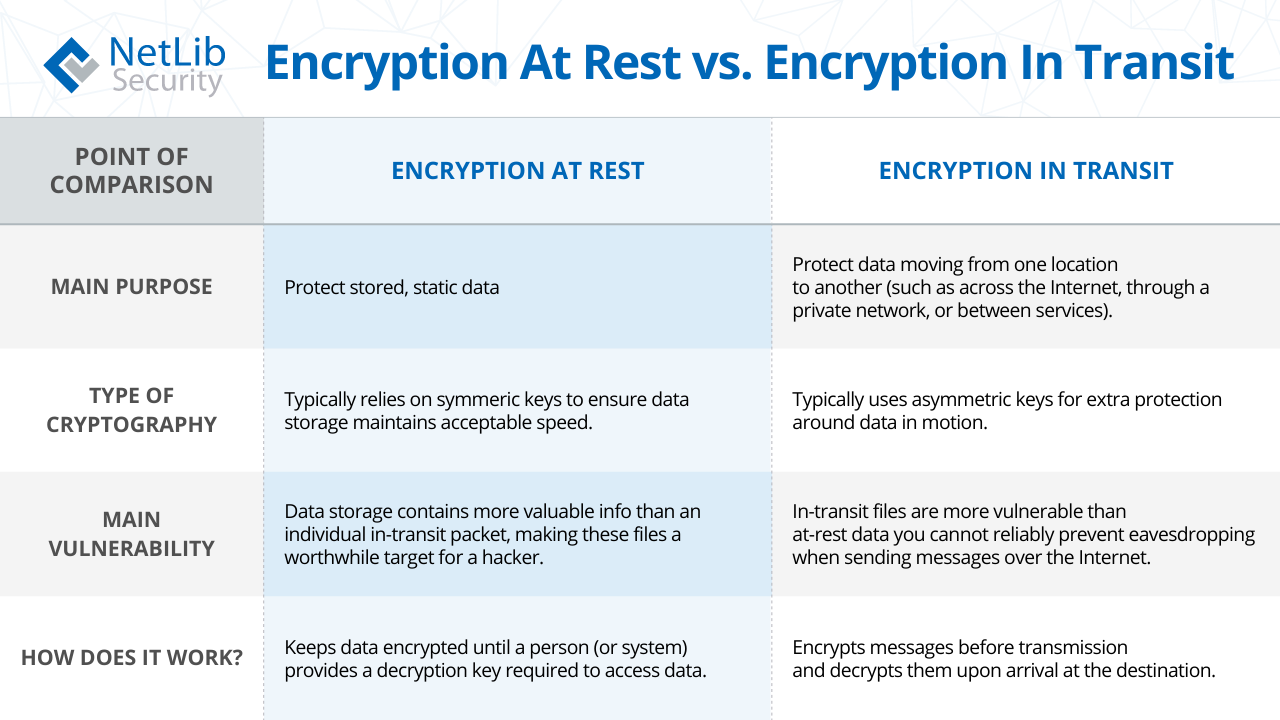
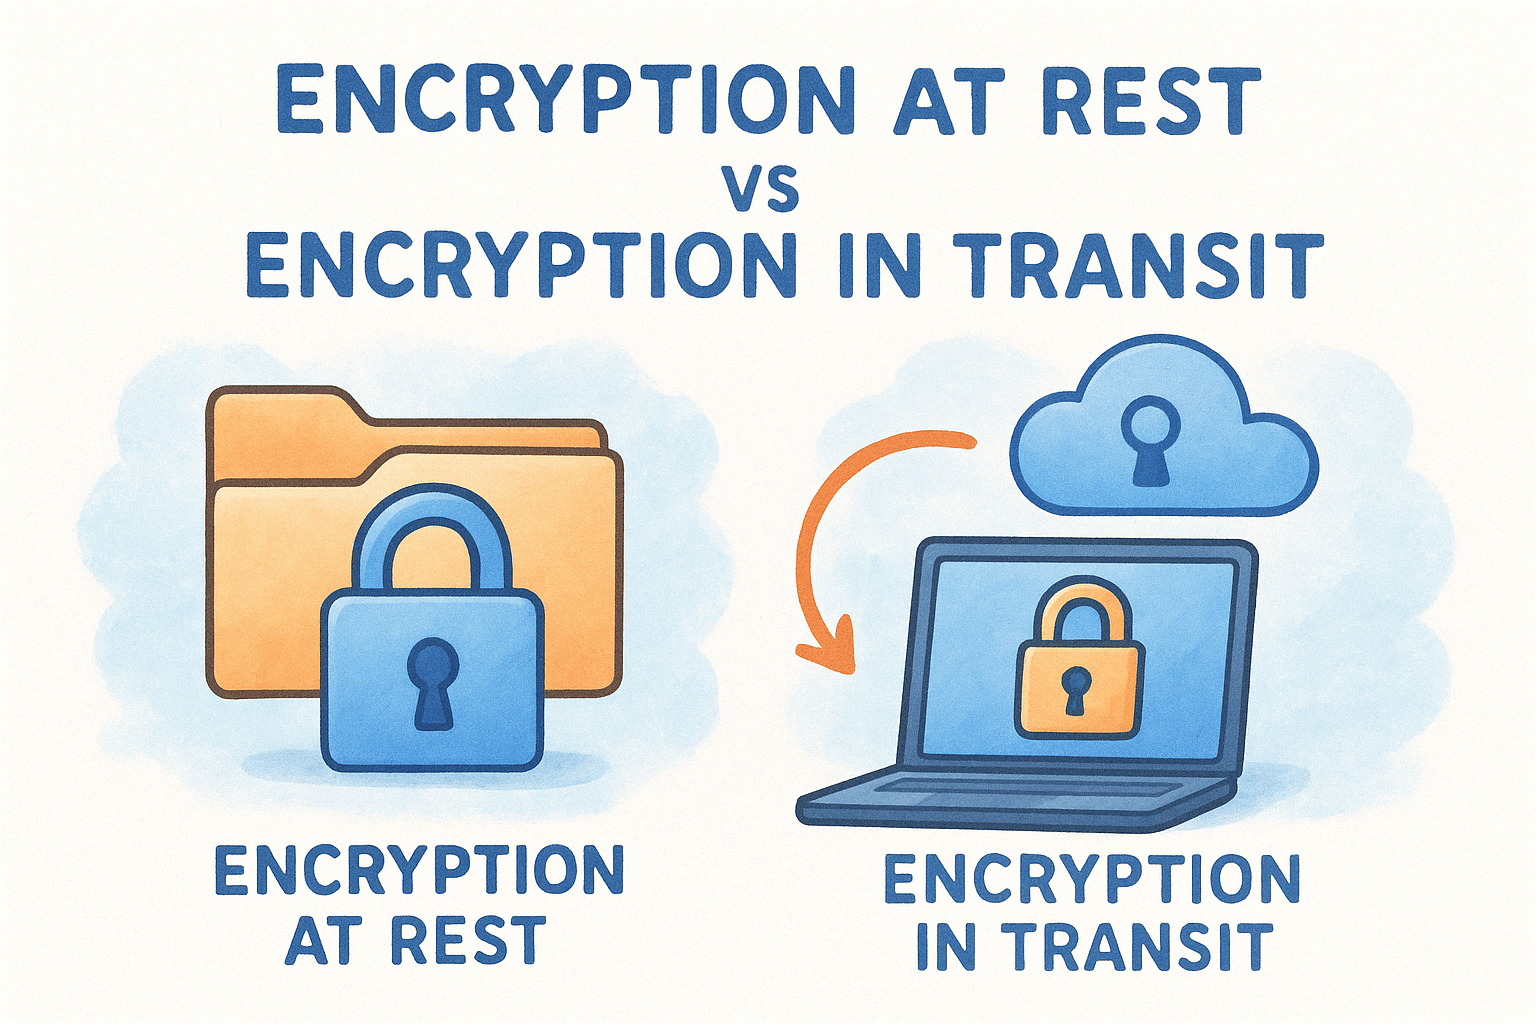
Encryption at Rest vs. Encryption in Transit

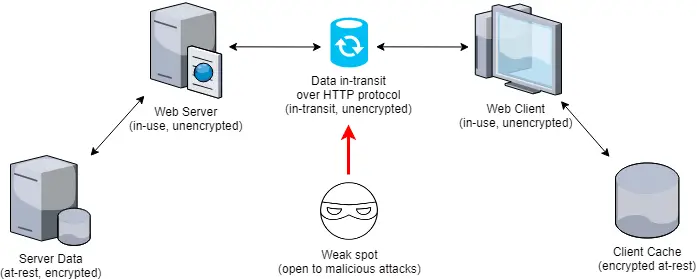
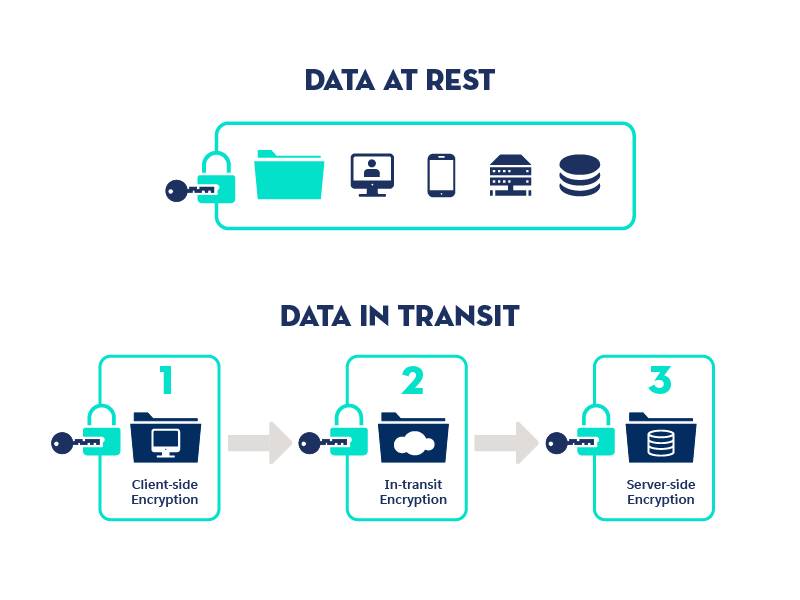
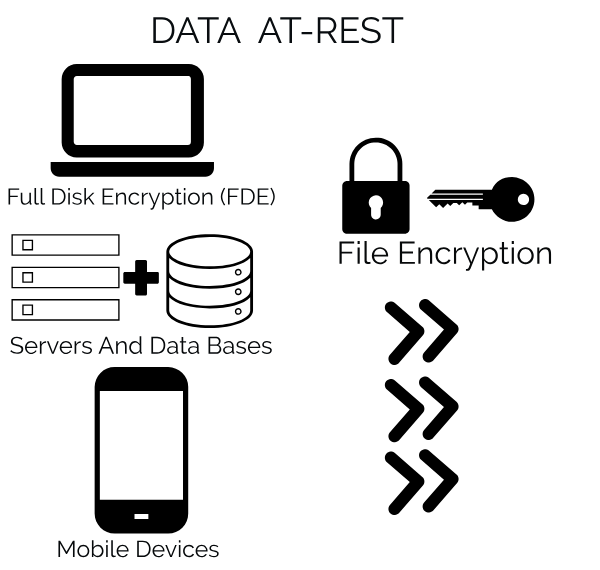
As we can see from the illustration, Encryption At Rest And In Transit has many fascinating aspects to explore.
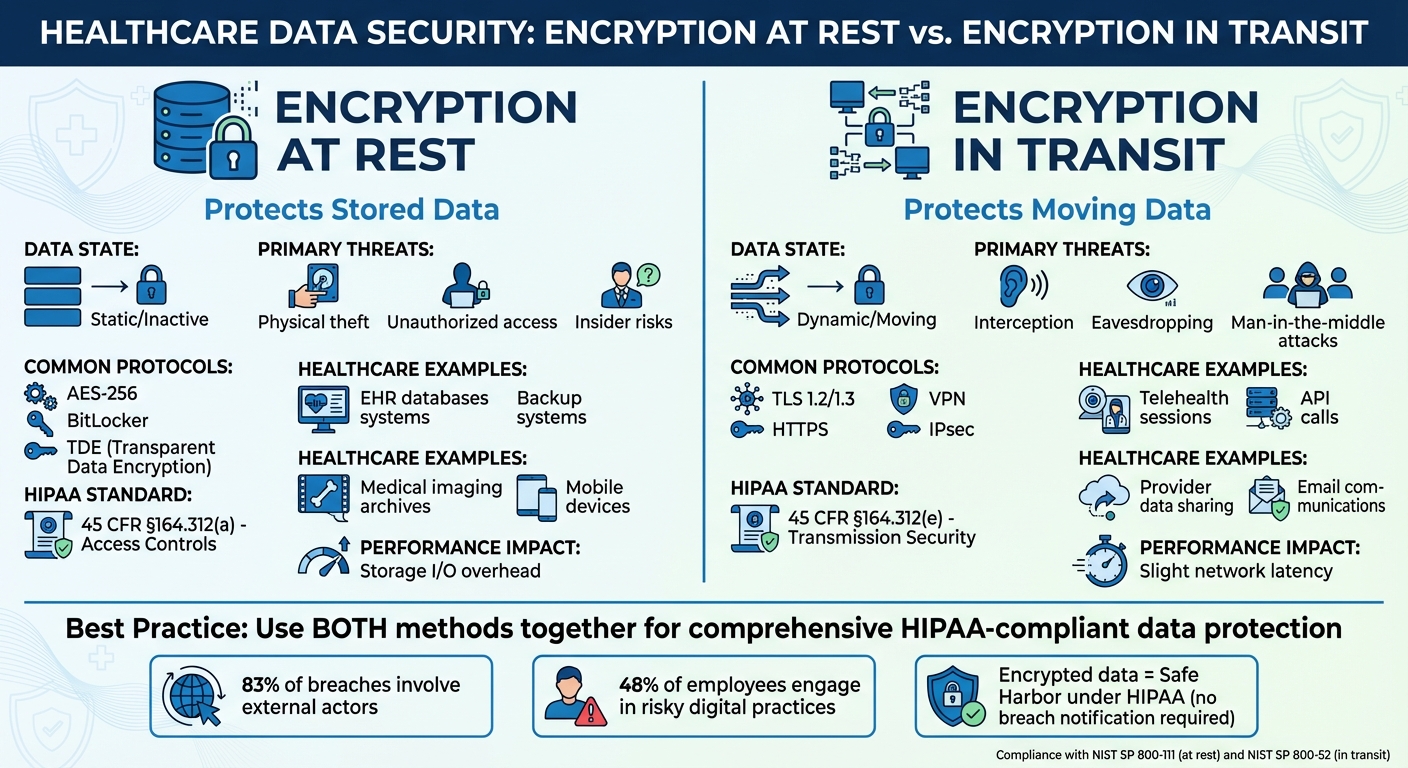
Encryption at Rest vs. Encryption in Transit : Differences Compare encryption at rest and in transit for protecting healthcare data, HIPAA considerations, protocols, and implementation best practices. Protecting sensitive data is non-negotiable, especially in healthcare. Encryption ensures data remains secure, whether it's stored or ...
Learn how to implement encryption at rest and in transit with practical code examples. Cover TLS, database encryption , key management with AWS KMS, and production-ready patterns.
Data Encryption at Rest and in Transit (2026)
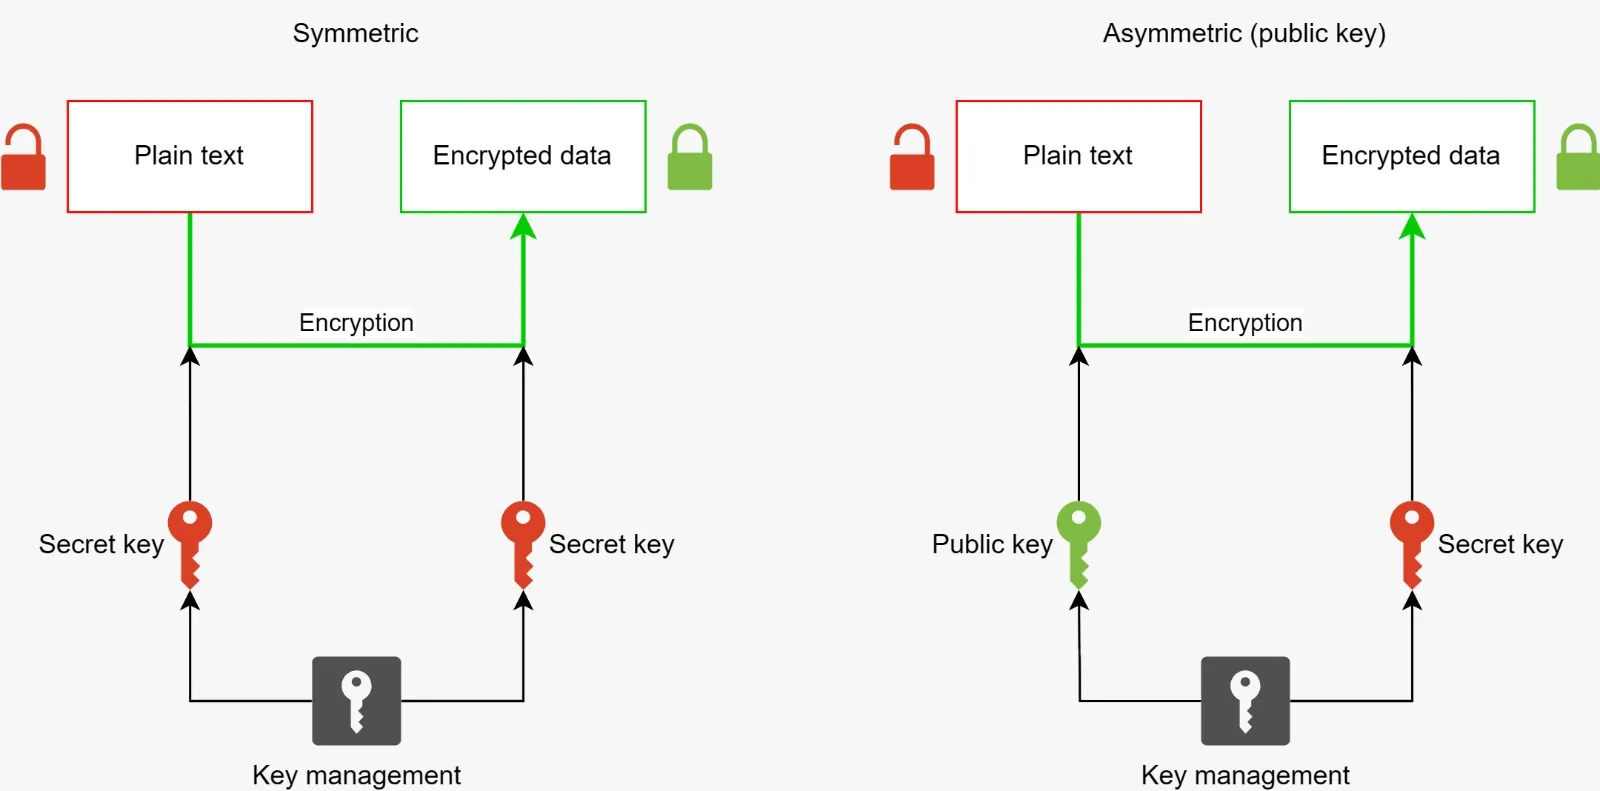
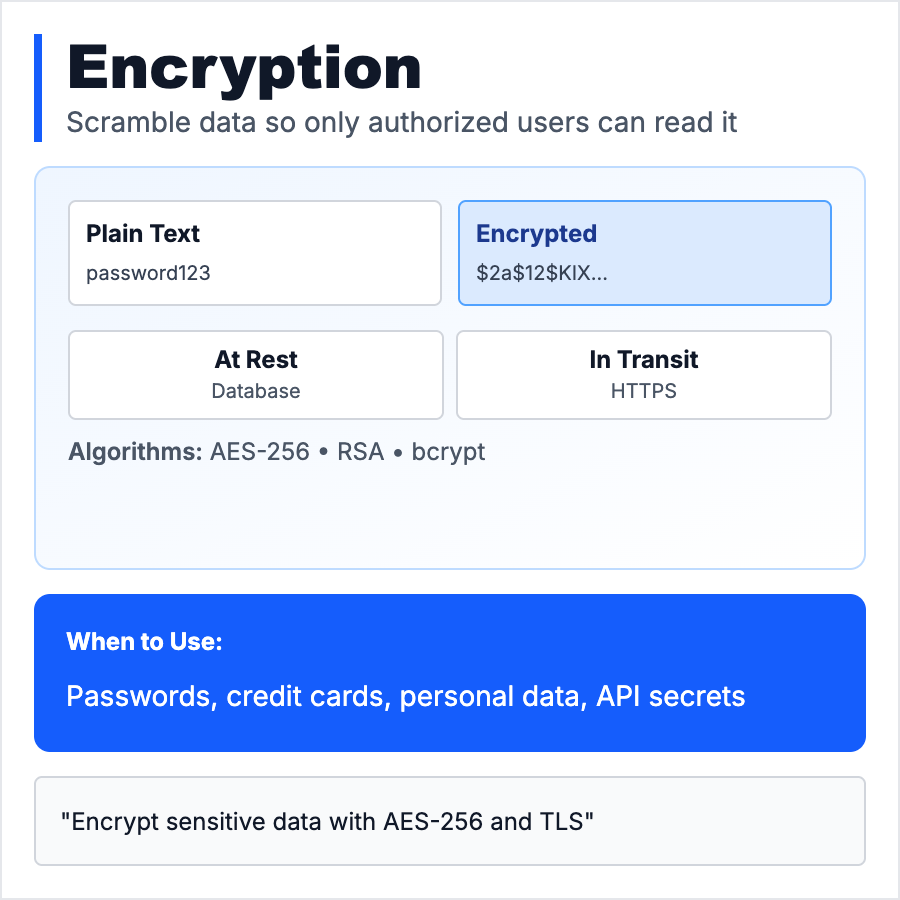
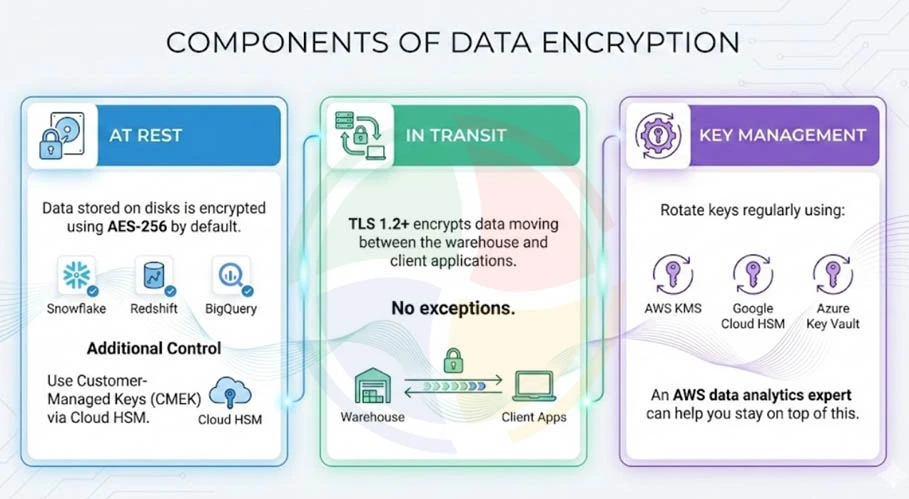
This guide covers the practical implementation of data encryption across the enterprise: algorithm selection, encryption at rest for databases and file systems, TLS configuration for data in transit , envelope encryption with cloud KMS, and the compliance requirements that drive encryption decisions in regulated industries.
Data encryption helps prevent unauthorized access to data storage systems. Read this to learn about data encryption at-rest and in-transit .
What Does At
Such details provide a deeper understanding and appreciation for Encryption At Rest And In Transit.
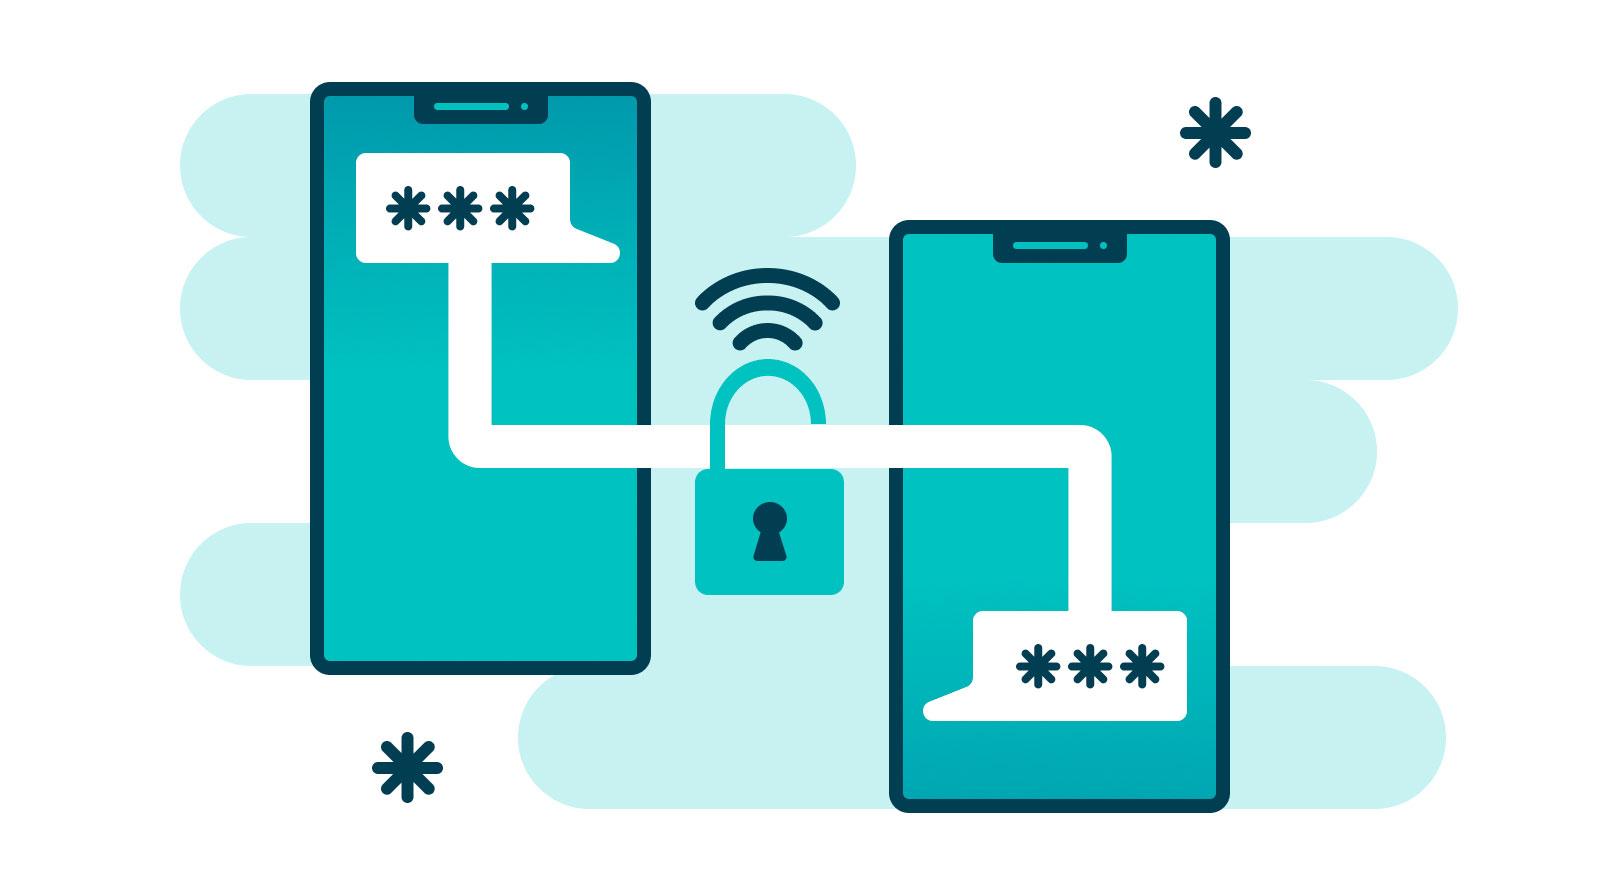
At-rest encryption protects your data while it's stored, making it unreadable without the proper key. It's crucial for securing sensitive information in databases and cloud storage. In contrast, in-transit encryption safeguards your data during transmission, ensuring it stays safe as it travels across networks. Both methods are essential for preventing unauthorized access and data breaches ...
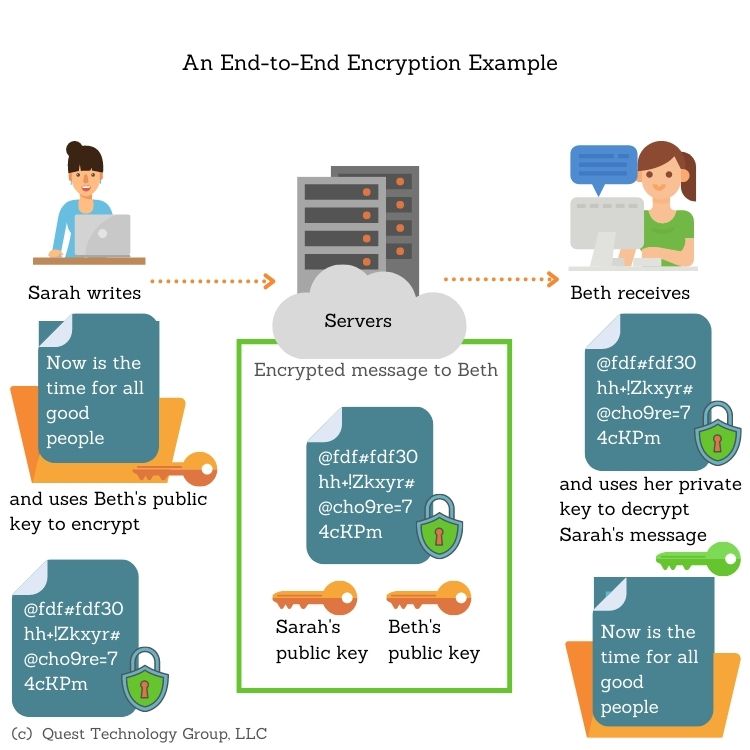
Key Takeaways End-to-end encryption (E2EE) ensures that data is encrypted on the sender's device and can only be decrypted by the intended recipient, protecting information from interception or access by unauthorized parties, including service providers. Essential for maintaining privacy and security in digital communications, E2EE is a critical feature for messaging apps, online transactions ...
Data at Rest vs In Transit vs In Use
What is Encryption at Rest and in Transit ? Encryption at rest and in transit are the two fundamental states where data must be protected cryptographically, addressing the core security problem that data is vulnerable both when stored and when moving between systems.