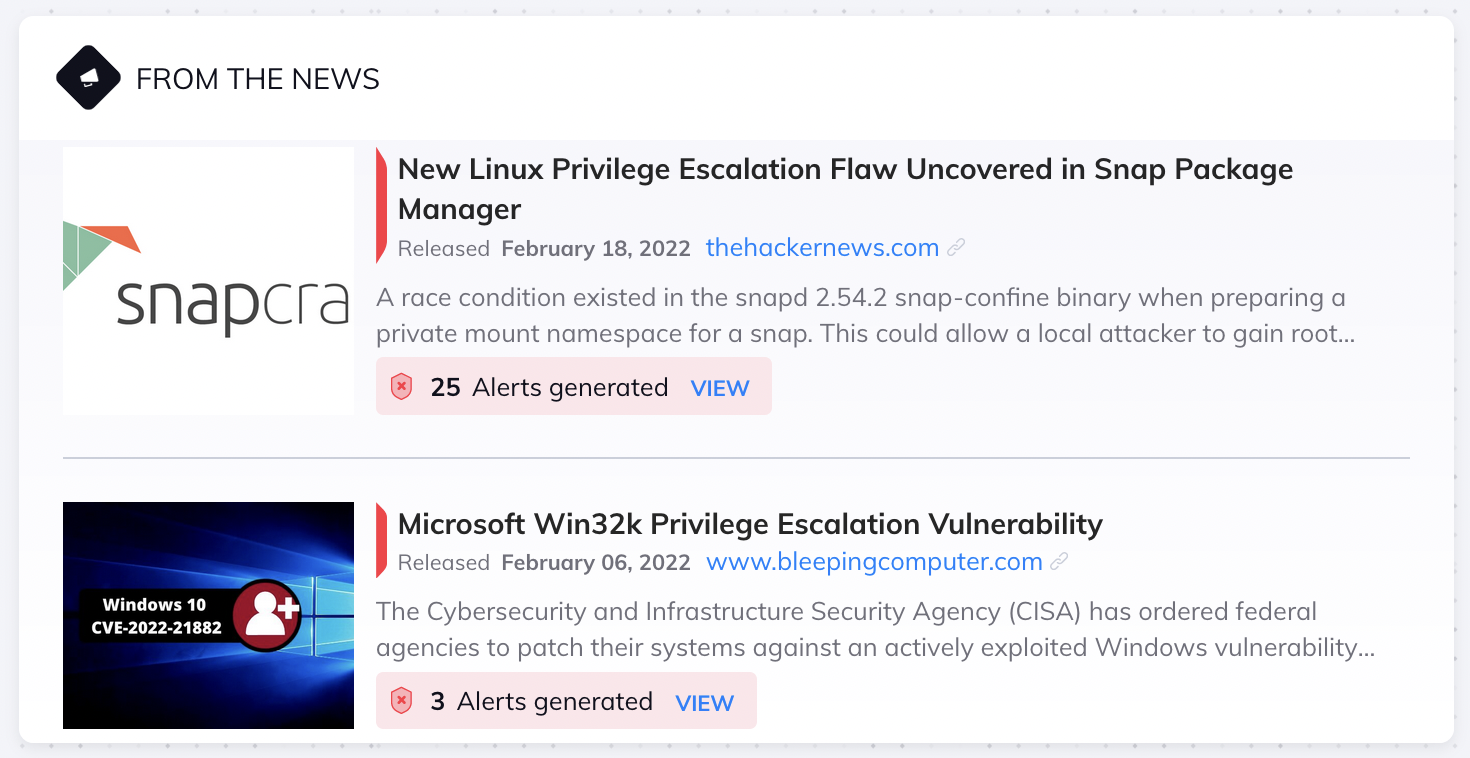
In today’s hyperconnected digital landscape, staying ahead of emerging threats isn’t just a best practice—it’s a necessity. A vulnerability news feed serves as a real-time intelligence stream that aggregates, curates, and delivers critical security advisories, zero-day disclosures, patch updates, and exploit analyses directly to your inbox or dashboard. For cybersecurity professionals, DevOps teams, and IT decision-makers, this isn’t optional—it’s foundational infrastructure.
What Is a Vulnerability News Feed?
A vulnerability news feed is a specialized information pipeline that continuously monitors authoritative sources—such as the National Vulnerability Database (NVD), vendor security bulletins, CERT alerts, and trusted threat intelligence platforms—and distills them into actionable insights. Unlike generic tech news, these feeds focus exclusively on software flaws, misconfigurations, and active exploits. They often include metadata like CVSS scores, affected versions, and remediation steps, enabling rapid triage and response.
Why Organizations Can’t Afford to Ignore It
Consider the 2023 MOVEit breach: within hours of its disclosure, organizations with mature vulnerability news feeds were already assessing exposure, while others scrambled to understand the scope. Delayed awareness translates directly to increased attack surface. A well-configured feed reduces mean time to detect (MTTD) and mean time to respond (MTTR), turning reactive firefighting into proactive defense.

Key Components of an Effective Feed
Not all feeds are created equal. The most valuable ones integrate multiple data streams and apply context-aware filtering. Here’s what to look for:
- Source Diversity: Pulls from NVD, vendor advisories (Microsoft, Apache, Cisco), and underground forums.
- Enrichment: Adds exploit availability, patch status, and asset relevance.
- Customization: Filters by technology stack, severity, and business criticality.
- Delivery Mechanism: Supports RSS, email, Slack, or API integration.
How to Implement a Vulnerability News Feed
Implementation starts with defining your attack surface. Map your software inventory, then select a feed provider—or build one using open-source tools like OpenVAS or commercial platforms like Tenable, Qualys, or Recorded Future. Integrate it with your SIEM or SOAR system for automated playbooks. For example, a high-severity CVE with a known exploit should trigger an immediate scan of affected assets.
Common Pitfalls to Avoid
Many teams drown in alert fatigue because they treat all vulnerabilities equally. A feed without context is noise. Prioritize based on actual risk, not just CVSS scores. Also, ensure your feed includes zero-day intelligence—relying solely on NVD means you’re always at least 24-48 hours behind active threats.

Measuring Success
Track metrics like time-to-patch, reduction in critical vulnerabilities, and false-positive rates. A mature feed should show a downward trend in both. Remember, the goal isn’t to consume every alert—it’s to act on the right ones. In cybersecurity, speed and precision are everything, and a well-tuned vulnerability news feed is your early warning system.