Cybersecurity Incident Management

An Incident Response (IR) plan is a documented approach to address and manage cybersecurity incidents or attacks. A well-defined IR plan outlines the roles, responsibilities, and procedures to be followed during an incident , enabling a coordinated and efficient response . It includes identifying, investigating, mitigating, and recovering from security breaches , cyberattacks, or any unauthorized ...
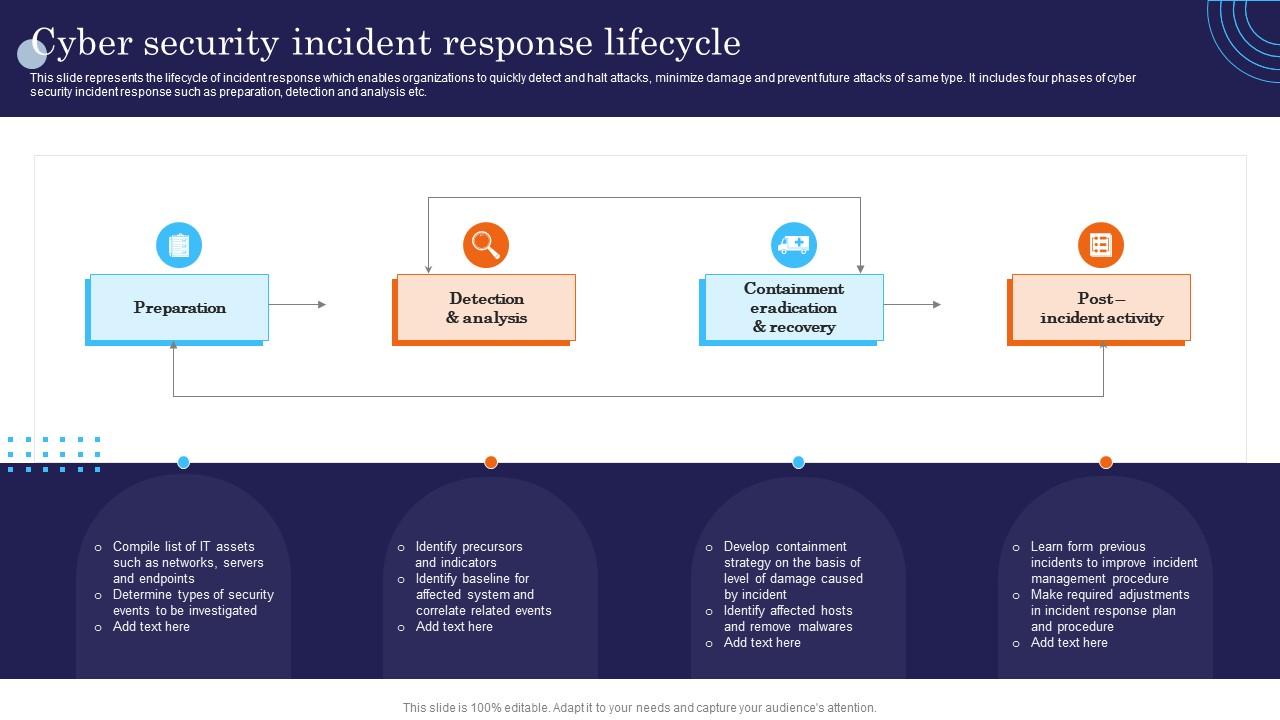
What Incident Response aims to achieve Incident Response aims to quickly minimize the impact of cyber attacks and prevent security breaches . It uses any insights or intelligence gained from the incident to improve future cyber security measures. Its other goals are to ensure business continuity, detect and contain moving threats, and conduct reviews as a part of post- incident activity processes.
The Comprehensive Cybersecurity Incident Response Guide
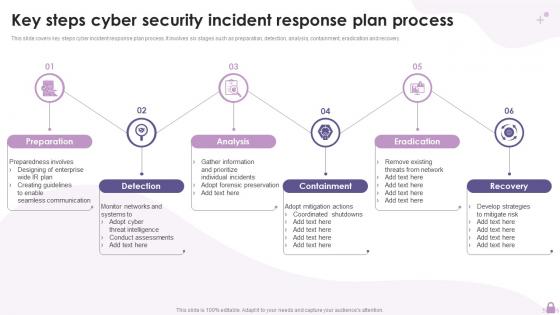
The primary goal of cybersecurity incident response is to detect, contain, and mitigate security threats to minimize damage, ensure business continuity, and prevent future incidents . A well-structured incident response plan helps organizations respond quickly and effectively to cyberattacks.
Explore cyber incident response frameworks, recovery strategies, and best practices to detect, contain, and mitigate security threats effectively.

Responding to a Cyber Incident
Find out what you should do if you think that you have been a victim of a cyber incident . Incident Response Recommendations and Considerations for Cybersecurity Risk Management: A CSF 2.0 Community Profile —seeks to assist organizations with incorporating cybersecurity incident response recommendations and considerations throughout their cybersecurity risk management activities as described ...
A Cybersecurity Incident Response Plan is a document that gives IT and cybersecurity professionals instructions on how to respond to a serious security incident , such as a data breach, data leak, ransomware attack, or loss of sensitive information. Traditionally, experts describe effective incident response plans in four phases: preparation; detection and analysis; containment, eradication ...
PDF Cyber Security Incident Management Guide
This 2025 edition of the Cybersecurity Incident Management Guide provides a comprehensive framework for preparing, detecting, responding to, and recovering from security incidents . It draws on industry standards, regulatory requirements, and practical experience from real-world incident response engagements. The guide is designed to help organisations not only manage incidents more effectively ...
Overview Cyber incidents can harm U.S. national security interests, foreign relations, and the economy and can impact public confidence, civil liberties, and health and safety. Because of this risk, all organizations should have clear, executable cyber incident response plans and strategies to protect their own interests and prevent an incident from growing and causing greater harm.

How to Design a Cybersecurity Incident Response Plan (CSIRP)
A cybersecurity incident response plan (CSIRP) is a set of procedures and guidelines that help prepare for, detect, and respond to cybersecurity incidents . A cybersecurity incident response plan defines the roles and responsibilities of personnel, communication channels, and mitigation steps in the event of a cyber attack.


Step #1: Preparation No organization can spin up an effective incident response on a moment's notice. A plan must be in place to both prevent and respond to events. Define the CSIRT (Computer Security Incident Response Team) To act quickly and completely while an incident is unfolding, everyone on the CSIRT needs to know their responsibilities and the decisions that are theirs to make. The ...