NIST Incident Response

Incident response is a structured process that organizations use to identify and deal with cybersecurity incidents . The NIST framework for incident response provides a structured way for organizations to detect, contain, and recover from security incidents . In this article, we break down the NIST four-phase lifecycle preparation and prevention; detection and analysis; containment, eradication ...

The incident response lifecycle provides a structured framework that guides security teams through the chaos of cyber incidents , ensuring rapid detection, coordinated response , and complete ...
NIST Incident Response Life Cycle in Cybersecurity

Incident handlers—and the entire company—can use these plans in the event of a cyberattack. This article will cover what you need to know about the incident response life cycle and how to help businesses prevent, or manage the aftermath of, a cyberattack.
Learn about the NIST incident response lifecycle and its key steps and phases. Detect, contain, recover, and mitigate cyber incidents fast.
Incident Response Life Cycle
Learn the four phases of the incident response life cycle and discover proven best practices that help security teams detect, contain, and recover from cyber threats faster.
The new incident response life cycle model used in this publication is shown in the figure. The bottom level reflects that the preparation activities of Govern, Identify, and Protect are not part of the incident response itself. Rather, they are much broader cybersecurity risk management activities that also support incident response .

Cybersecurity Incident Response Timeline
Cybersecurity incident response timeline showing detection, containment, eradication, and recovery phases. The Cybersecurity Incident Response Timeline defines how quickly an organization detects, contains, and recovers from a cyberattack. In modern security operations, response speed determines overall impact.
The following are selected examples of additional resources supporting the incident response life cycle. Vulnerability and Threat Information CISA, Automated Indicator Sharing (AIS) CISA, CISA Cyber Threat Indicator and Defensive Measure Submission System CISA, Cybersecurity Alerts & Advisories CISA, Cybersecurity Directives CISA, Ransomware Vulnerability Warning Pilot (RVWP) The MITRE ...
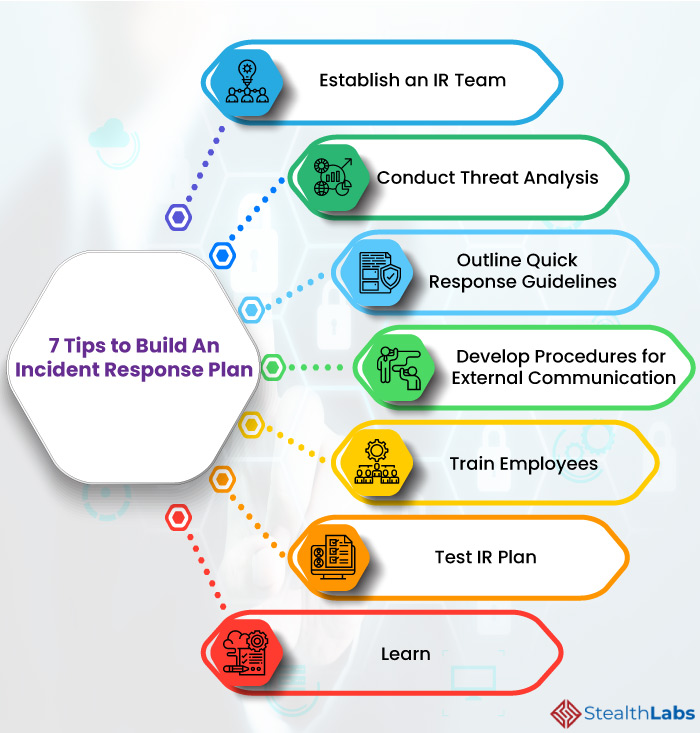
6 Phases of Incident Response (NIST Framework Explained)
Learn the essential steps of the NIST incident response framework with our detailed 2026 guide designed for students and security professionals. We break down the six critical phases including preparation, detection, containment, and recovery to help you build a robust defense strategy. This comprehensive resource explains how to handle cyber threats effectively, ensuring your organization ...


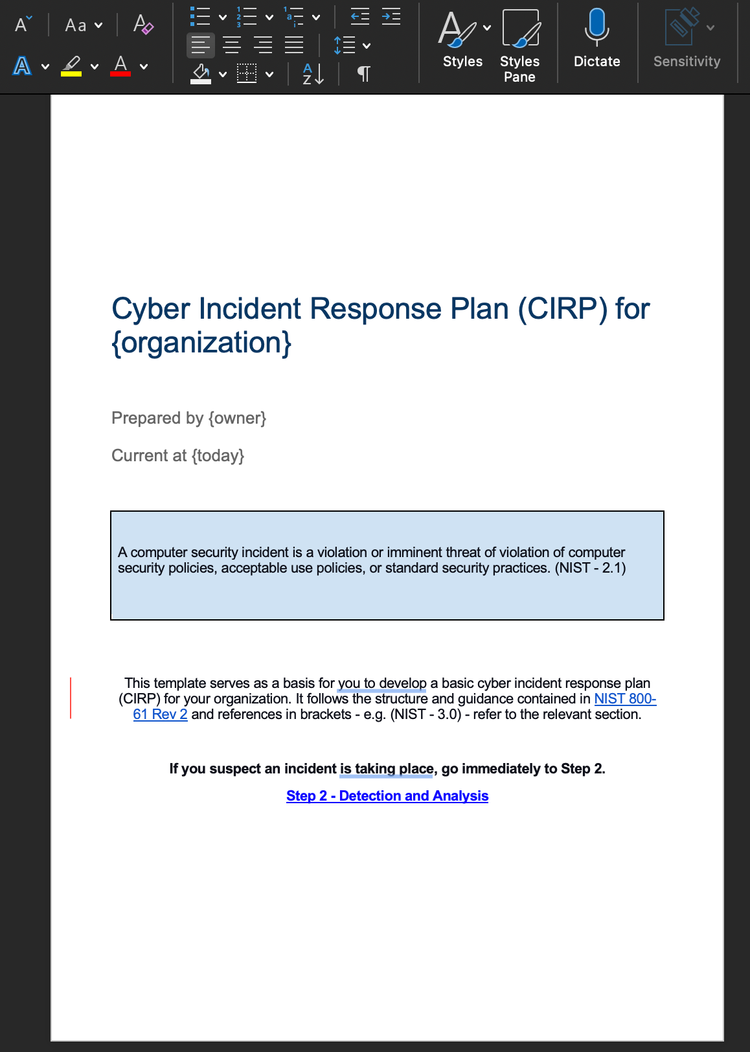


Step #1: Preparation No organization can spin up an effective incident response on a moment's notice. A plan must be in place to both prevent and respond to events. Define the CSIRT (Computer Security Incident Response Team) To act quickly and completely while an incident is unfolding, everyone on the CSIRT needs to know their responsibilities and the decisions that are theirs to make. The ...