Incident Response Plan

Step #1: Preparation No organization can spin up an effective incident response on a moment's notice. A plan must be in place to both prevent and respond to events. Define the CSIRT (Computer Security Incident Response Team) To act quickly and completely while an incident is unfolding, everyone on the CSIRT needs to know their responsibilities and the decisions that are theirs to make. The ...
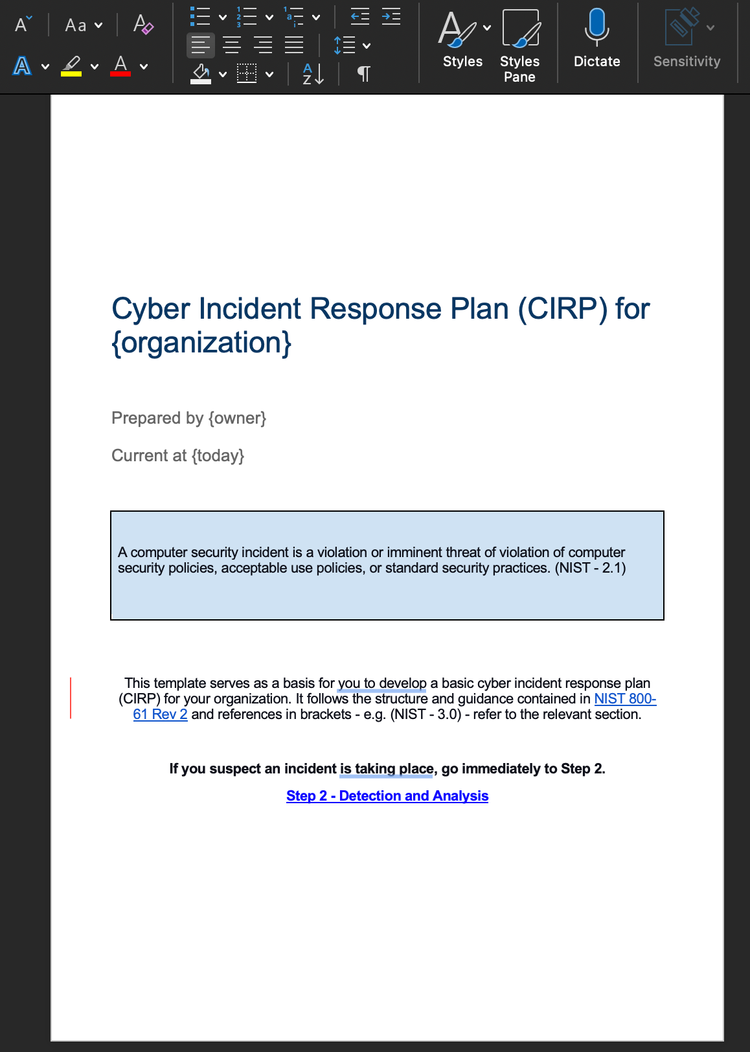
An Incident Response Plan is a written document, formally approved by the senior leadership team, that helps your organization before, during, and after a confirmed or suspected security incident .
What is an incident response plan for IT

An incident response plan is a set of instructions to help IT detect, respond to, and recover from computer network security incidents like cybercrime, data loss, and service outages that threaten daily work flow.
An incident response (IR) plan is a documented strategy outlining how an organization will detect, respond to, and recover from cybersecurity attacks or other disruptions. Its purpose is to minimize the impact of security breaches, data leaks, malware attacks, and other potential threats while ensuring business continuity.

What is incident response
Incident response (sometimes called cybersecurity incident response ) refers to an organization's processes and technologies for detecting and responding to cyberthreats, security breaches or cyberattacks. A formal incident response plan enables cybersecurity teams to limit or prevent damage.
Incident response definition Incident response is the strategic, organized responsed an organization uses following a cyberattack. The response is executed according to planned procedures that seek to limit damage and repair breached vulnerabilities in systems. IT professionals use incident response plans to manage security incidents .

What Is an Incident Response Plan and How to Create One
An effective incident response (IR) plan is a combination of people, processes, and technologies that is documented, tested, and trained in the event of a security incident . Incident response plans are designed to prevent data and monetary loss while supporting the restoration of regular business operations. In some cases, having an incident response plan is required to acquire digital ...
Incident response typically starts when the security team gets a credible alert from a security information and event management (SIEM) system. Team members need to verify that the event qualifies as an incident and then isolate infected systems and remove the threat. If the incident is severe or takes a long time to resolve, organizations may need to restore back up data, deal with a ransom ...

Incident Response
An incident response plan is crucial for organizations that want to minimize operational disruptions, financial losses, and reputational damage. Implementing a strong response strategy helps organizations recover quickly from security incidents , demonstrate a commitment to security, and comply with industry regulations.


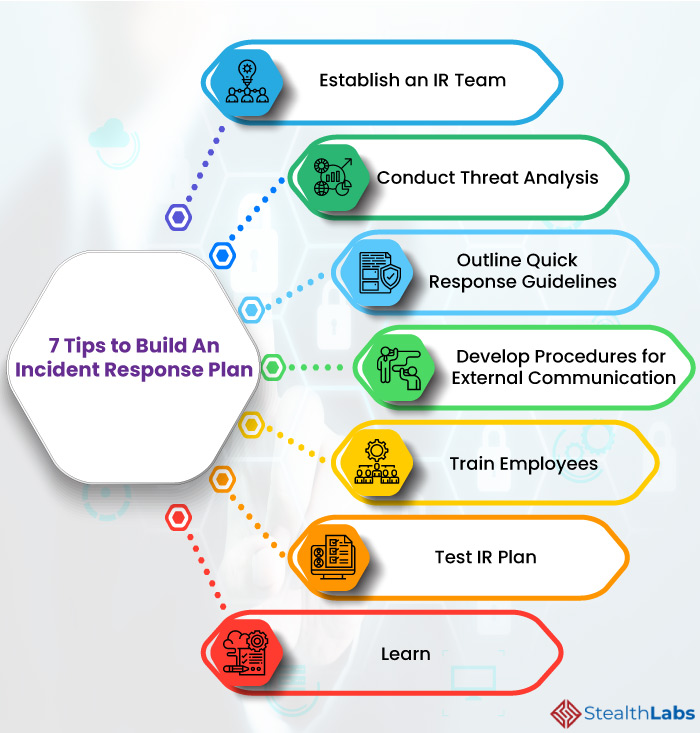


An incident response plan , sometimes called an incident management plan or emergency management plan , is a set of instructions to detect, respond to and limit the effects of an information security event. It provides clear guidelines for a variety of cyberattacks, such as data breaches, DDoS attacks, firewall breaches, ransomware and malware, insider threats, data loss and other disruptive ...