Guests booking a stay at a modern hotel expect a specific set of comforts, but underlying the experience of rest and relaxation is a complex legal framework. Hotel privacy laws exist to balance the operational needs of hospitality businesses with the fundamental right of individuals to maintain personal confidentiality during their stay. Understanding these regulations is essential for both travelers seeking to protect their data and hoteliers navigating the obligations of compliance.
The Legal Foundation of Guest Confidentiality
At its core, the right to privacy in a hotel room is rooted in the concept of a "reasonable expectation of privacy." While the room itself is a shared commercial space, the law generally recognizes the guestroom as a private sanctuary. This legal principle dictates that hotel staff cannot enter a occupied room without a specific, legally valid reason, such as an imminent threat to safety or a valid search warrant. The contractual relationship between the guest and the hotel establishes a duty of care, meaning the property is entrusted with safeguarding personal belongings and ensuring the sanctity of the accommodation is not violated without just cause.
Exceptions to the Right of Entry
It is a common misconception that hotel staff have zero access to occupied rooms under all circumstances. Legal frameworks allow for specific exceptions to protect the property and the safety of other guests. These typically include:

- Immediate response to a safety alarm or noise complaint indicating a medical emergency or dangerous situation.
- Entry to pursue a suspected criminal act, such as manufacturing drugs, where delay could result in evidence destruction.
- Pursuit of a fleeing suspect where the hotel has probable cause to believe the individual is in a specific room.
In these scenarios, the legal standard is usually "exigent circumstances," which justifies bypassing the normal check-in protocols to prevent harm.
Data Privacy in the Digital Age
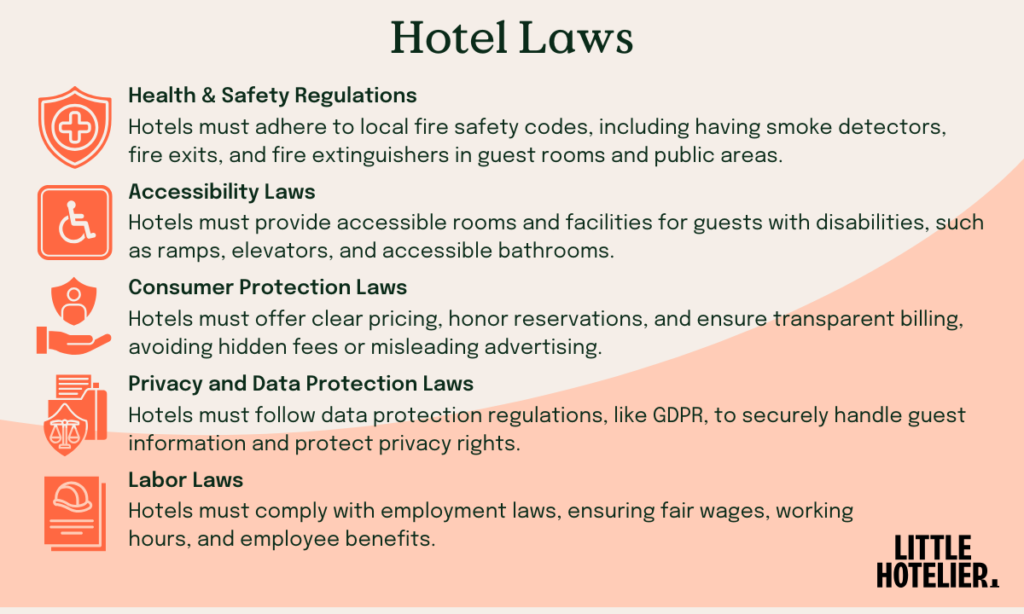
In the 21st century, the most significant privacy concerns often revolve around data rather than physical entry. When a guest checks in, they provide a trove of personal information, including full name, home address, passport details, and credit card information. Hotel privacy laws in jurisdictions like the European Union (GDPR), California (CCPA), and other regions strictly regulate how this data is collected, stored, and processed. Hotels are required to be transparent about their data usage, typically limiting the retention of guest information to what is necessary for billing and legal compliance, after which it must be securely destroyed or anonymized.
Security Camera Ethics and Placement
The deployment of security technology presents a unique challenge to hotel privacy laws. While surveillance is vital for preventing crime and ensuring safety, there are strict boundaries regarding where cameras can be installed. It is almost universally illegal to place cameras in private areas such as bedrooms, bathrooms, or dressing rooms. Any surveillance system must be clearly disclosed to guests, usually through prominent signage in lobbies and corridors. The recording of audio in private spaces is typically prohibited entirely due to wiretapping regulations.
Compliance and Enforcement Mechanisms
Regulatory bodies treat violations of hotel privacy laws seriously. Data breaches, for instance, can result in massive financial penalties and irreparable reputational damage. In many regions, data protection authorities have the power to audit hotel systems and impose fines that scale with the severity of the negligence. Furthermore, guests who experience unlawful intrusion or data theft have the right to pursue civil litigation. This potential for lawsuits creates a strong incentive for hotel chains to invest in robust cybersecurity infrastructure and staff training to ensure strict adherence to privacy protocols.
Global Variations in Privacy Standards
Travelers should note that privacy expectations are not standardized globally. A hotel in Europe will generally operate under a stricter data privacy regime than one in a region with less developed legislation. For example, the GDPR grants EU residents extensive rights to access, correct, or erase their personal data, a level of control that may not exist elsewhere. International travelers are advised to research the specific regulations of the country they are visiting or to simply assume that the highest standard of privacy applies to protect their personal information.
Best Practices for Travelers and Hotels
Whether you are a guest or a proprietor, proactive measures are the best defense against privacy issues. Travelers can protect themselves by using a VPN on hotel Wi-Fi, utilizing the in-room safe for physical documents, and using a credit card rather than a debit card for financial security. Hotels, on the other hand, can mitigate risk by implementing clear signage regarding data collection, conducting regular privacy impact assessments, and ensuring that all third-party vendors, such as booking platforms or cleaning services, adhere to the same stringent privacy standards to maintain a consistent chain of custody for sensitive information.