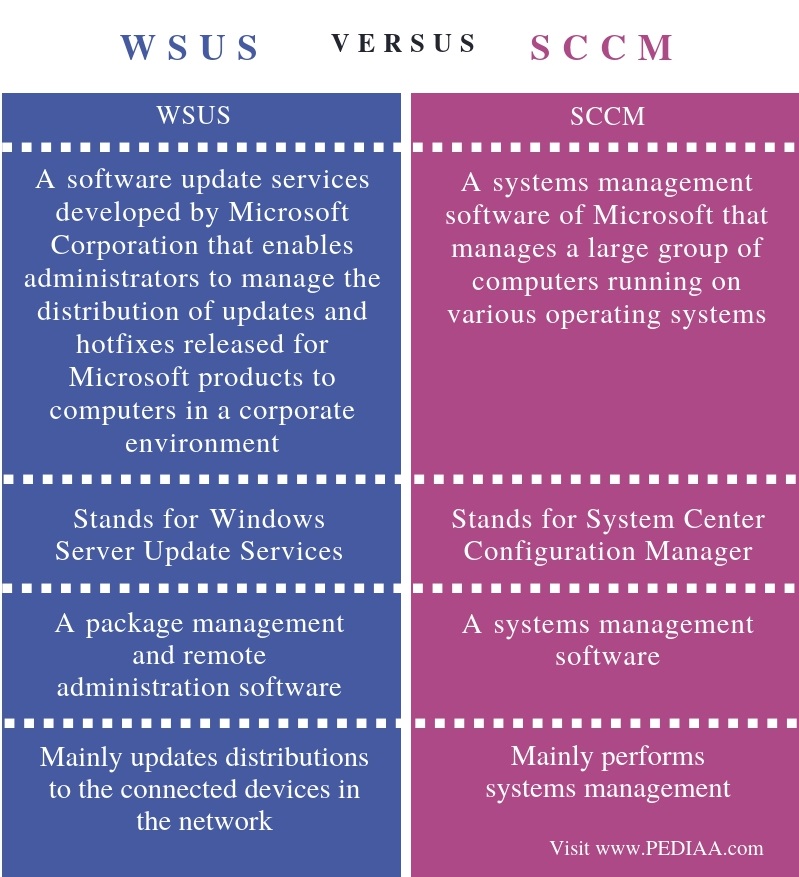
When managing large-scale Windows environments, System Center Configuration Manager (SCCM)—now part of Microsoft Endpoint Configuration Manager—typically relies on Windows Server Update Services (WSUS) to deploy patches and updates. However, there are valid scenarios where organizations may need or prefer to operate SCCM without WSUS, whether due to infrastructure constraints, architectural redesigns, or the adoption of modern alternatives like Windows Update for Business (WUfB) or third-party patch management tools.
Understanding SCCM Without WSUS
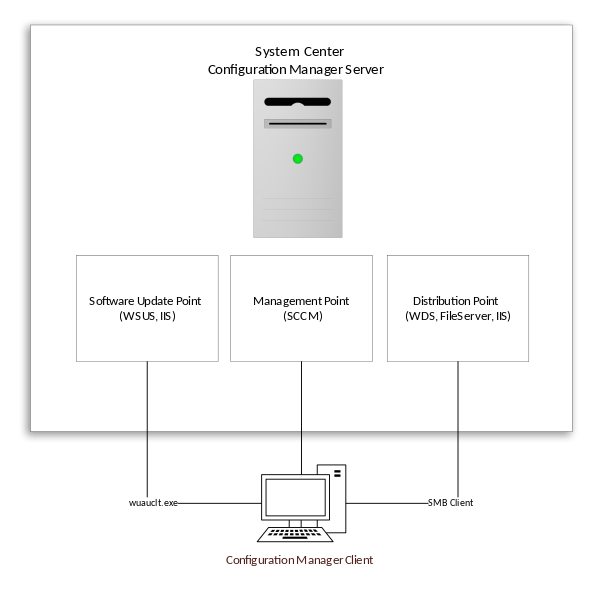
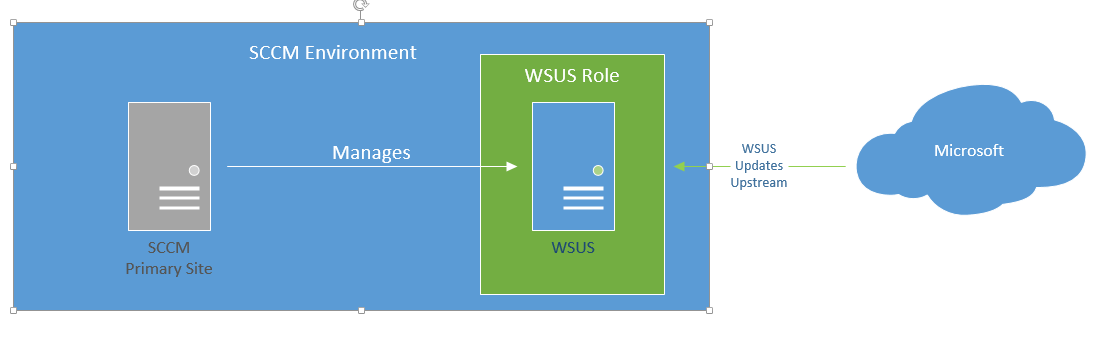
WSUS acts as the backend synchronization point between Microsoft Update and SCCM, enabling administrators to approve, schedule, and deploy updates. Without WSUS, SCCM loses its native integration with Microsoft’s update catalogs unless alternative methods are implemented. Despite this limitation, SCCM can still manage software deployments, application lifecycle management, compliance settings, inventory, and operating system deployment—all core functions that don’t strictly require WSUS.
In environments that have fully embraced cloud-first strategies, some teams choose to bypass WSUS entirely by leveraging cloud-based update policies and direct integration with Microsoft Intune or Azure Automation Update Management. This hybrid approach allows SCCM to handle device configuration and app deployment off-site while delegating patching responsibilities to more agile, internet-facing services.

Key Use Cases for Operating SCCM Without WSUS
Several real-world scenarios justify eliminating WSUS from the SCCM pipeline:
- Cloud-Centric Patch Management: Organizations using Microsoft Intune or Windows Update for Business (WUfB) can apply quality and feature updates directly from Microsoft’s cloud without needing WSUS as an intermediary.
- Reduced Infrastructure Overhead: Maintaining WSUS servers requires disk space, SQL database maintenance, and regular cleanup tasks. Removing this footprint simplifies server management.
- Regulatory or Air-Gapped Networks: In highly secure or isolated environments, WSUS might be excluded intentionally, with patches delivered via offline media or controlled staging servers instead.
- Legacy Modernization: Migrating from older WSUS-based workflows to modern cloud-native patching models often involves decommissioning WSUS entirely.
Limitations to Consider
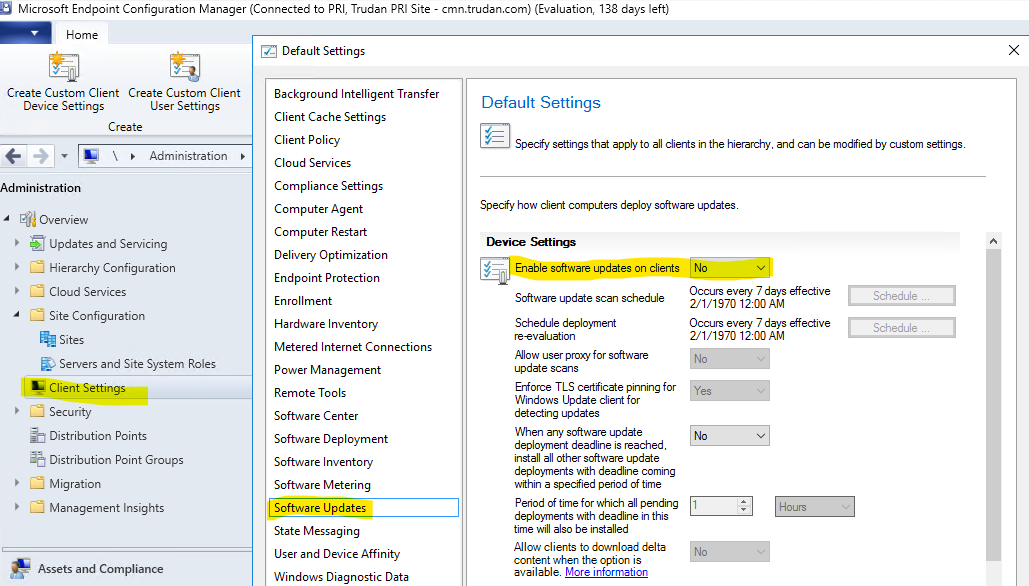
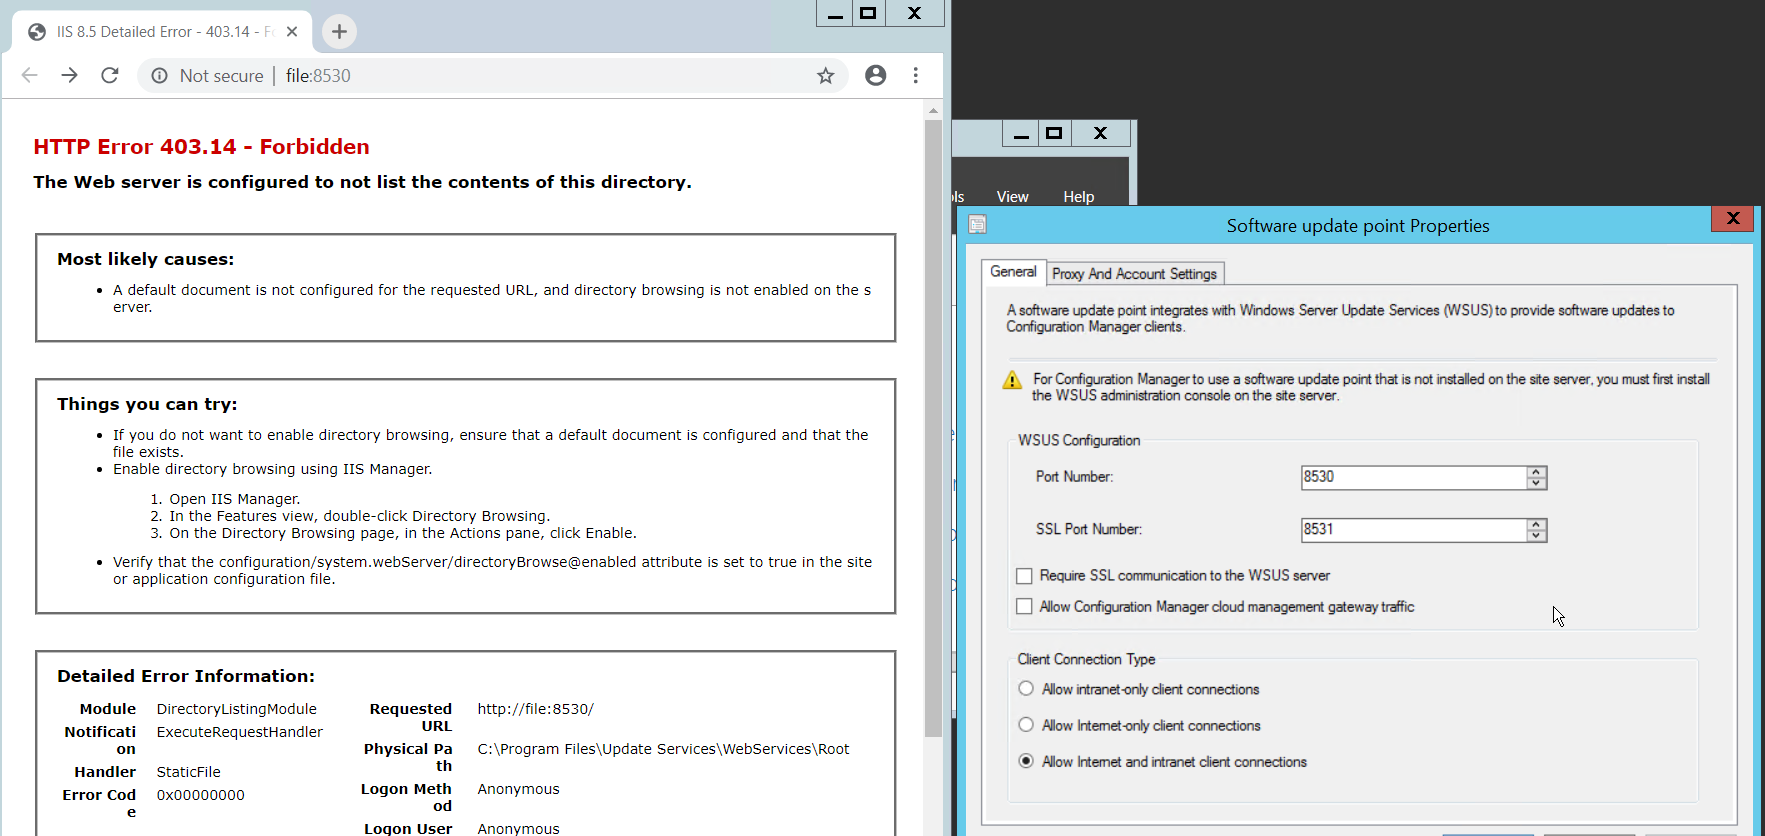
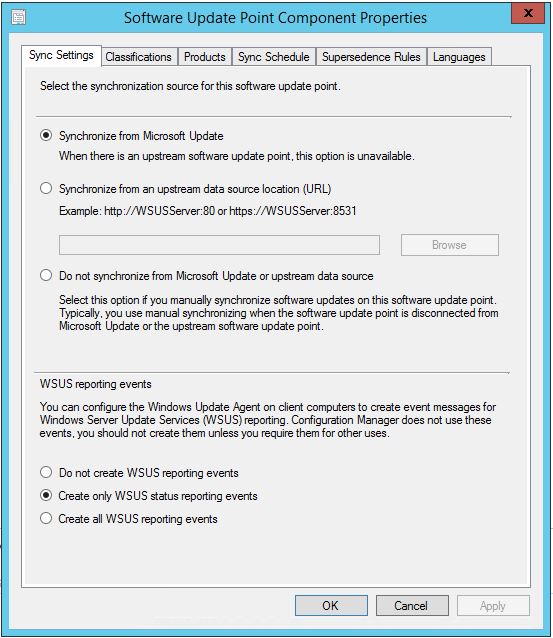
Removing WSUS does come with trade-offs. SCCM’s built-in Software Update Point (SUP) role depends on WSUS to fetch metadata from Microsoft Update. Without it, you lose the ability to:
- Sync security bulletins, hotfixes, and feature update metadata.
- Create traditional software update packages distributed via distribution points.
- Use the classic “Deployment Packages” model for monthly patch cycles.
Additionally, reporting related to update compliance, scan results, and deployment success—once powered by WSUS—must now be sourced from alternative endpoints such as Intune, Azure Monitor, or custom PowerShell scripts.

Alternative Patching Strategies
To maintain effective patch management without WSUS, consider these approaches:
| Method | Description | Best For |
|---|---|---|
| Windows Update for Business (WUfB) | Policy-driven update rings managed via Group Policy or Intune. | Organizations with devices connected to the internet. |
| Azure Automation Update Management | Cloud-based patch orchestration for hybrid environments. | Microsoft Azure-integrated infrastructures. |
| Third-Party Tools | Solutions like Ivanti, Patch My PC, or ManageEngine for external patch catalogs. | Heterogeneous environments with non-Microsoft applications. |
| Manual Import via PowerShell | Scripted ingestion of update .msu/.cab files into SCCM. | Highly controlled, low-frequency patch cycles. |
Configuration Manager Co-Management
One of the most seamless transitions away from WSUS is enabling co-management between SCCM and Intune. During co-management, you can offload the “Workloads” of Compliance Policies, Windows Update policies, and Endpoint Protection to the Intune service. This lets SCCM retain control over application deployment and OS imaging while delegating patching to cloud-based services—effectively rendering WSUS optional rather than mandatory.
Operational Best Practices
If you decide to operate SCCM without WSUS, follow these guidelines to ensure continuity and security:
- Audit all existing update deployments and retire legacy SUP roles.
- Ensure devices have reliable internet access or secure update delivery channels.
- Implement automated compliance baselines using Configuration Items and Baselines or Desired State Configuration (DSC).
- Maintain offline servicing plans for critical systems that cannot reach the internet.
- Document your new patch management workflow thoroughly for audit and disaster recovery.
While WSUS has long been the backbone of enterprise patch management via SCCM, evolving cloud services and modern endpoint management tools provide viable—and often superior—alternatives. Operating SCCM without WSUS is not only feasible but increasingly common in forward-thinking IT environments. The key lies in aligning your patching strategy with your organization’s infrastructure maturity, security posture, and digital transformation goals.
Frequently Asked Questions
Can SCCM deploy applications without WSUS?
Absolutely. Application deployment, package distribution, and task sequences operate independently of WSUS.
Does removing WSUS affect SCCM’s inventory capabilities?
No. Hardware and software inventory, asset intelligence, and compliance settings remain fully functional.
Is it possible to re-enable WSUS later?
Yes. You can reinstall the Software Update Point role and reconfigure synchronization settings as needed.
What happens to existing software update groups?
They become inactive once the SUP is removed, but historical data remains in the SQL database for reporting.