NIST Risk Management Framework

A Comprehensive, Flexible, Risk -Based Approach The Risk Management Framework ( RMF ) provides a process that integrates security, privacy, and cyber supply chain risk management activities into the system development life cycle. The risk -based approach to control selection and specification considers effectiveness, efficiency, and constraints due to applicable laws, directives, Executive Orders ...
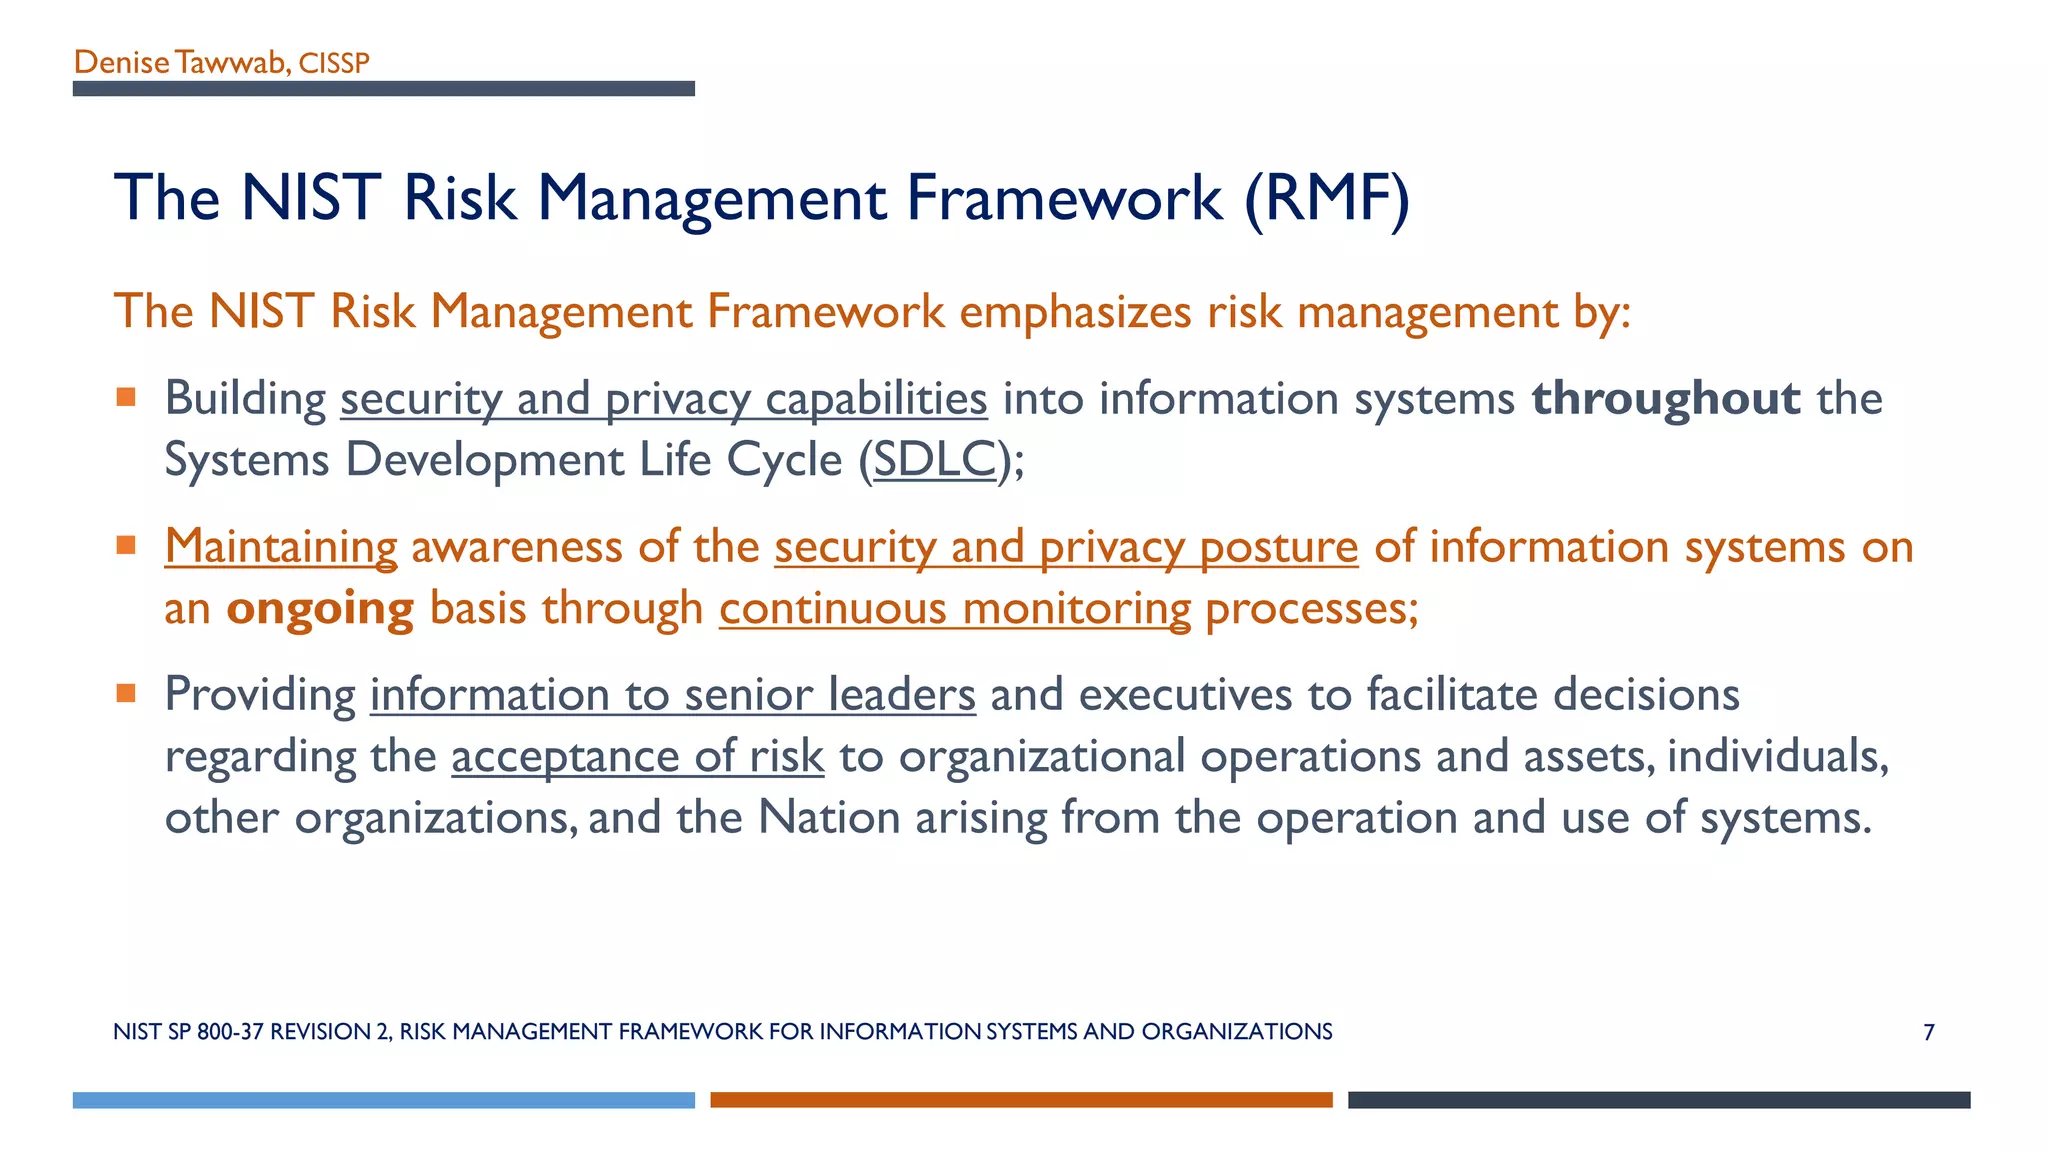
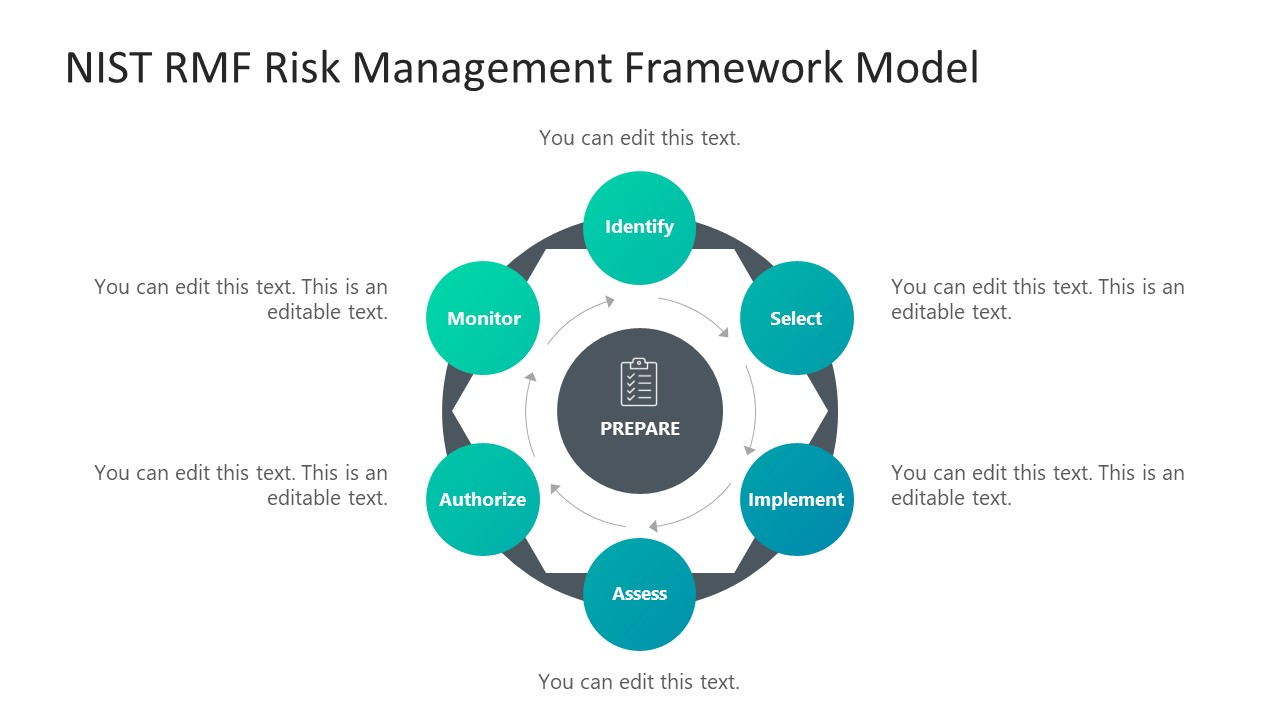
The NIST Risk Management Framework ( RMF ) provides a comprehensive, flexible, repeatable, and measurable 7-step process that any organization can use to manage information security and privacy risk for organizations and systems and links to a suite of NIST standards and guidelines to support implementation of risk management programs to meet the ...
Risk management framework (RMF)
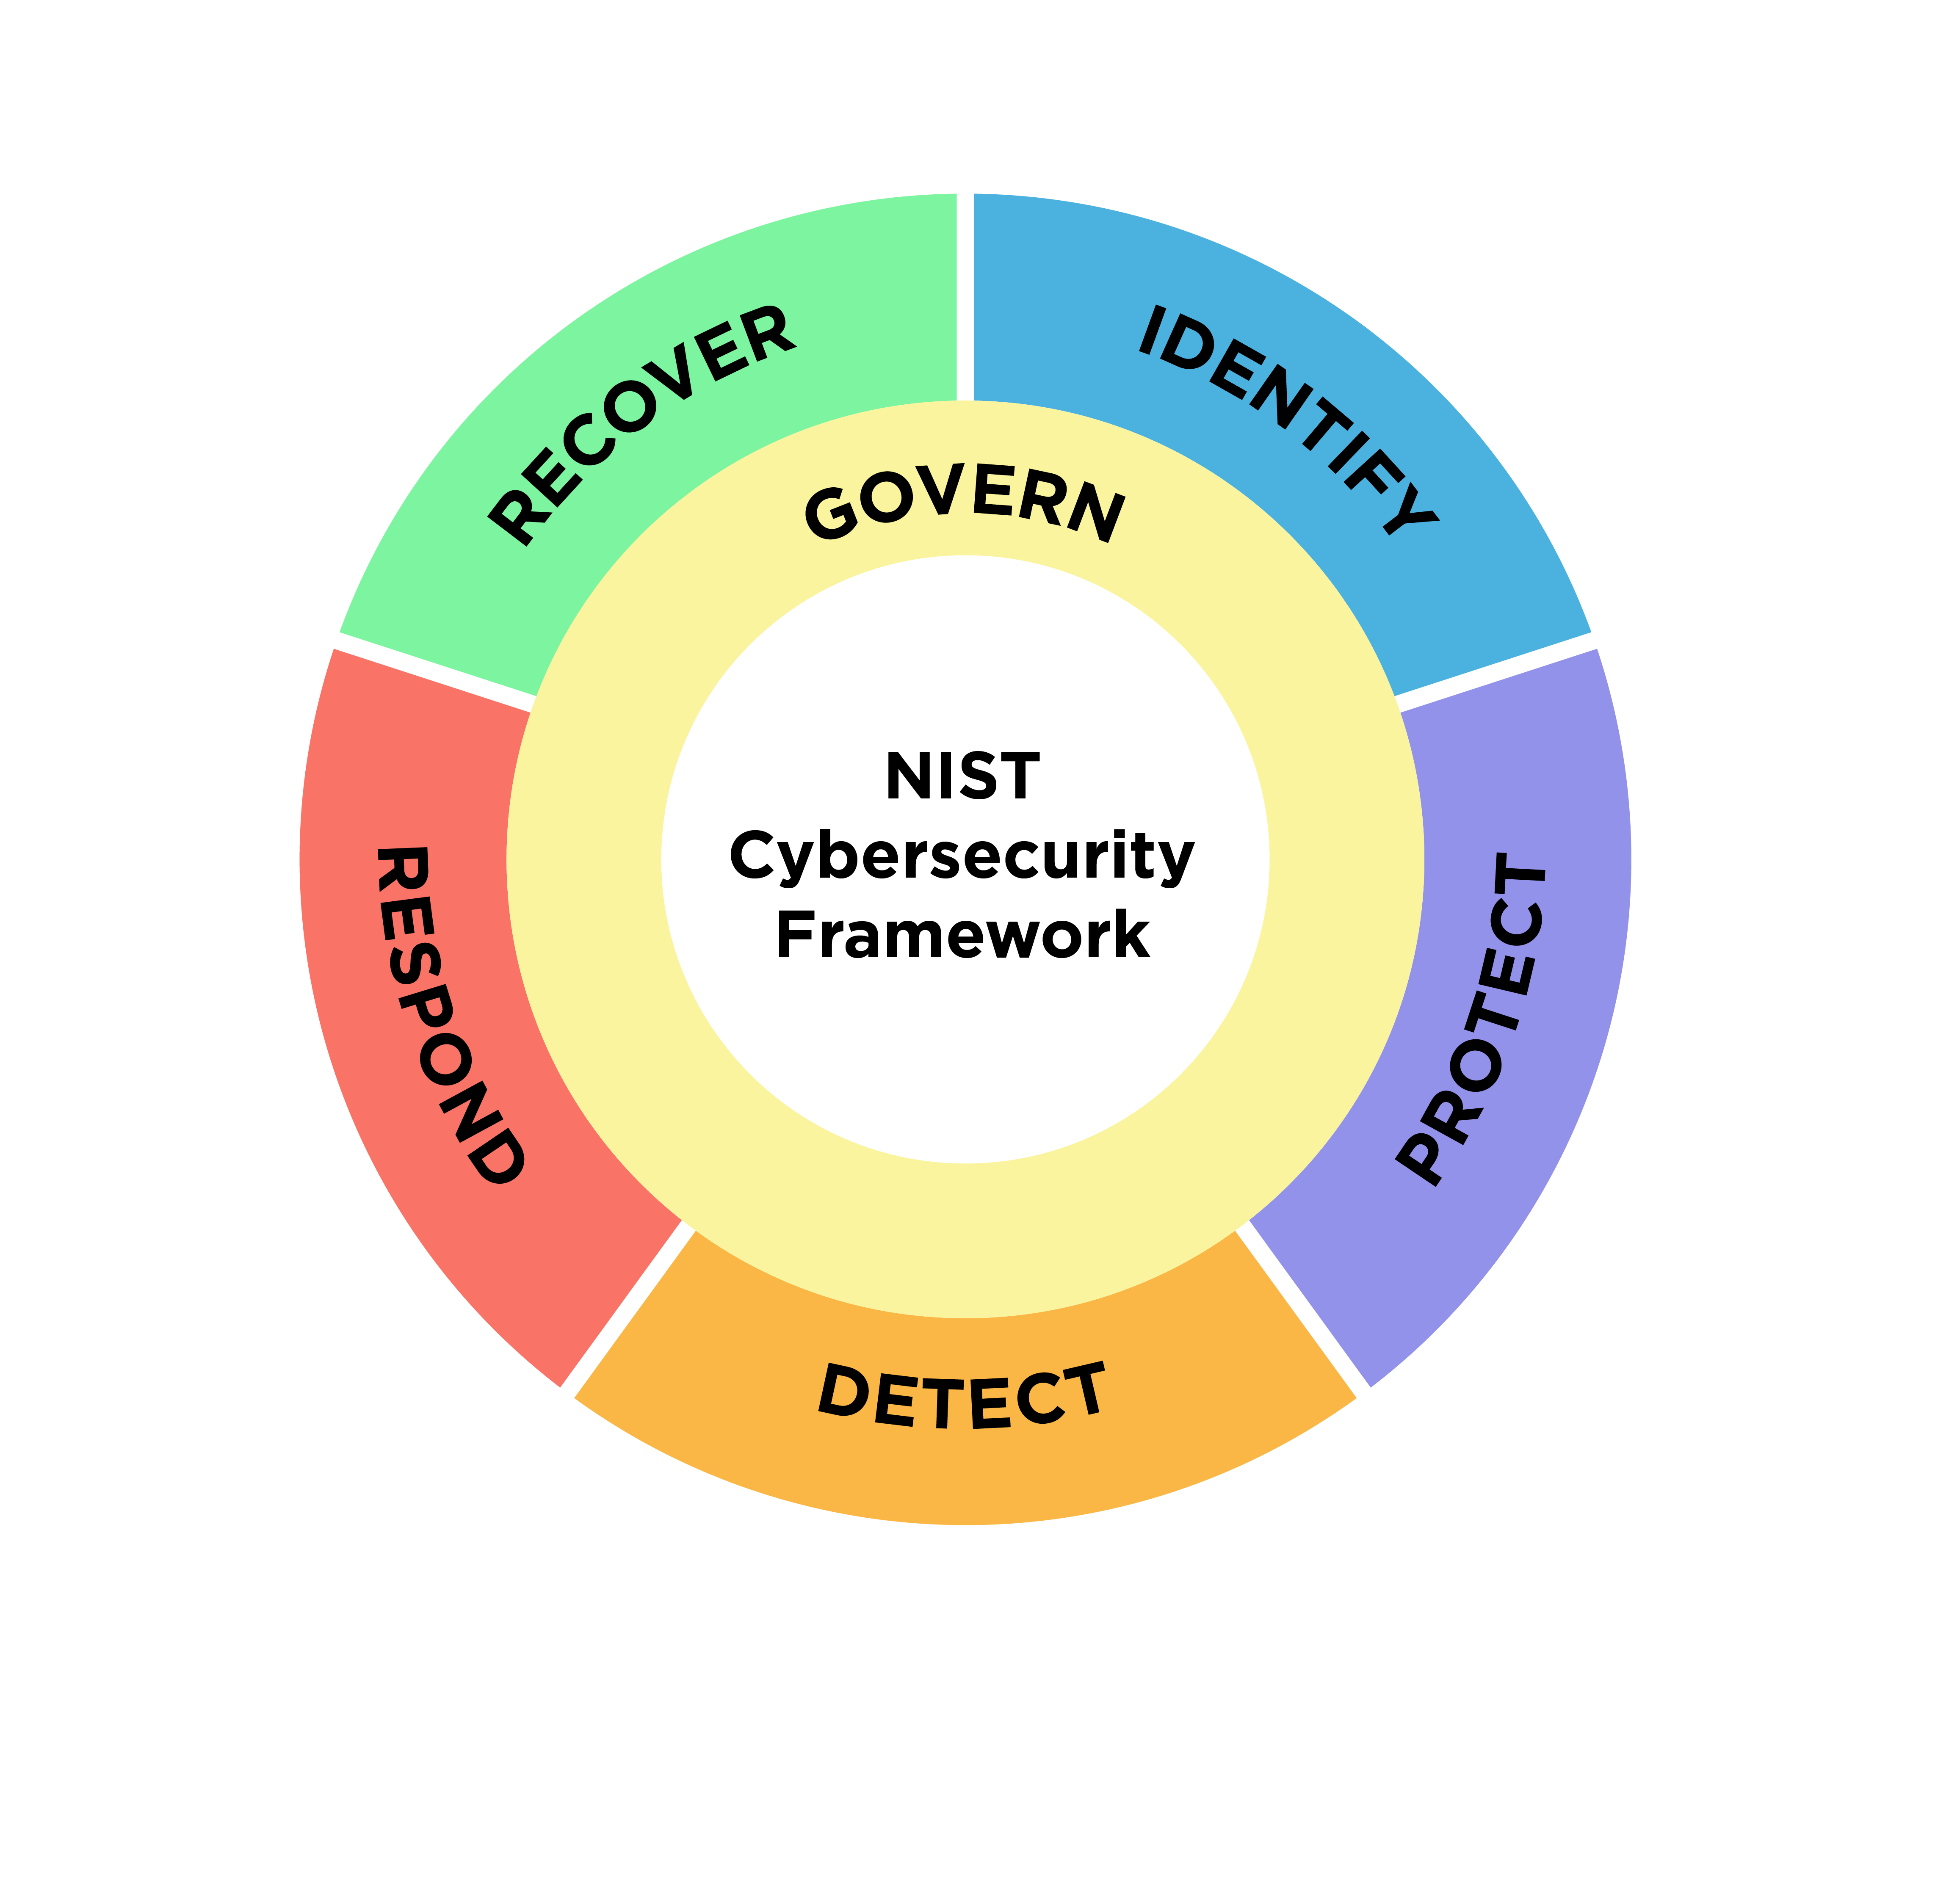
Developing the NIST Risk Management Framework and supporting documentation is a dynamic process where the risk management concepts and related documents are continually being refined and updated to better meet the needs of the user community.
What is the NIST Risk Management Framework ? The NIST Risk Management Framework ( RMF ) is a structured, 7-step process for integrating security and privacy controls into the lifecycle of an information system. Published by the National Institute of Standards and Technology, it gives organizations a consistent, repeatable way to identify, select, implement, and monitor security controls based on ...
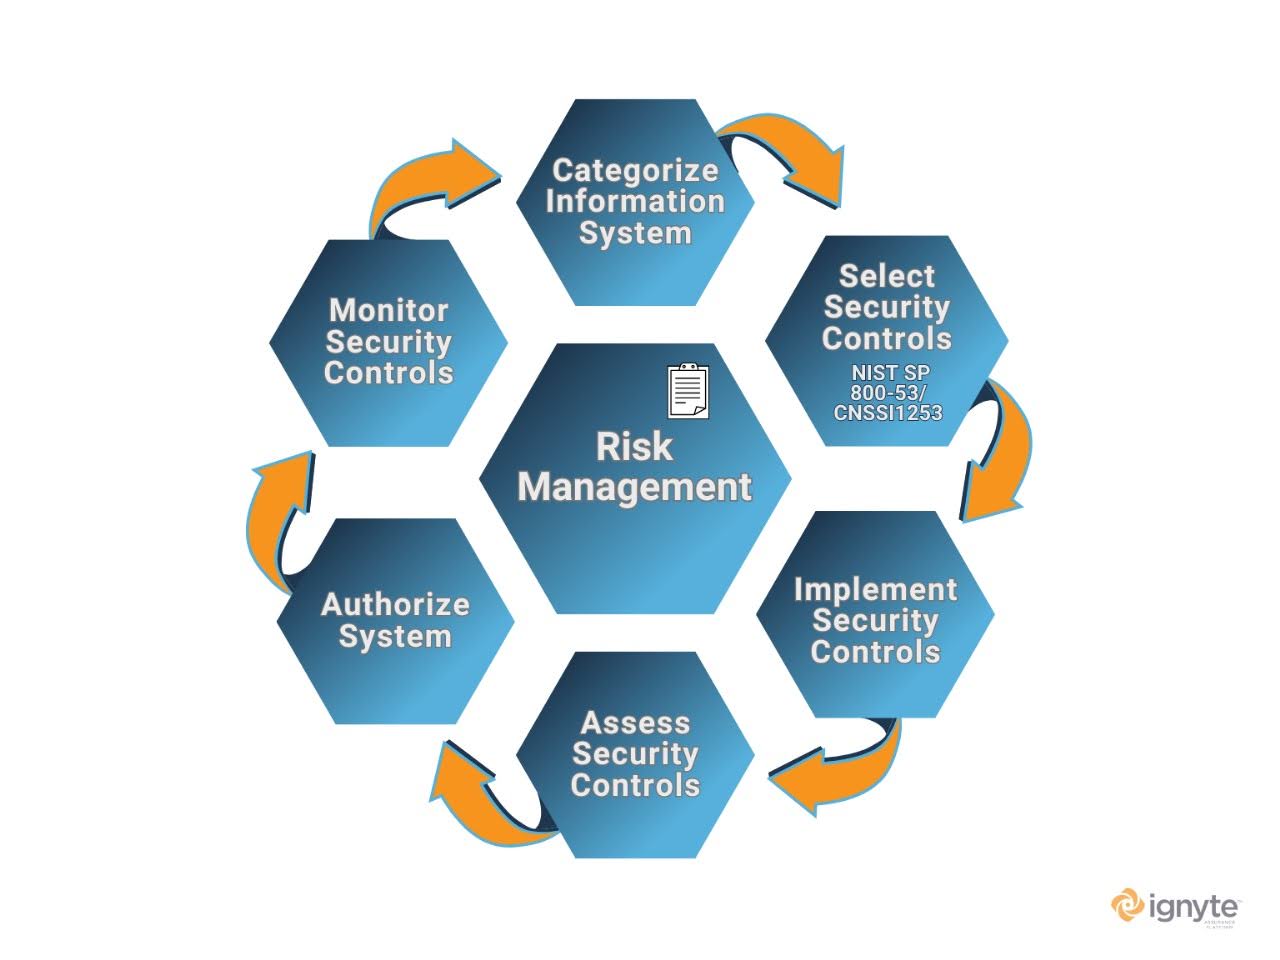
The NIST Risk Management Framework (RMF)
The NIST framework is a well-structured and tested process that builds a strong risk management foundation. The categorization and mitigation techniques described in the NIST RMF are easily adapted and customized to organizations of all types and sizes, ensuring that they are effective regardless of where they are used.
The NIST Risk Management Framework ( RMF ) is a disciplined, structured process for integrating security, privacy, and cyber supply chain risk management into the system development life cycle. It is published by the National Institute of Standards and Technology ( NIST ) in Special Publication 800-37, currently Revision 2.

7 NIST Risk Management Framework (RMF) Steps Explained
Throughout the process , look for ways to lean heavily on automation. NIST encourages organizations to maximize the use of automation, wherever possible, to increase the speed, effectiveness, and efficiency of executing the steps in the Risk Management Framework ( RMF ).
RMF 7 step process The Risk Management Framework ( RMF ) is a United States federal government guideline, standard, and process for managing risk to help secure information systems (computers and networks). The RMF was developed by the National Institute of Standards and Technology ( NIST ), and provides a structured process that integrates information security, privacy, and risk management ...
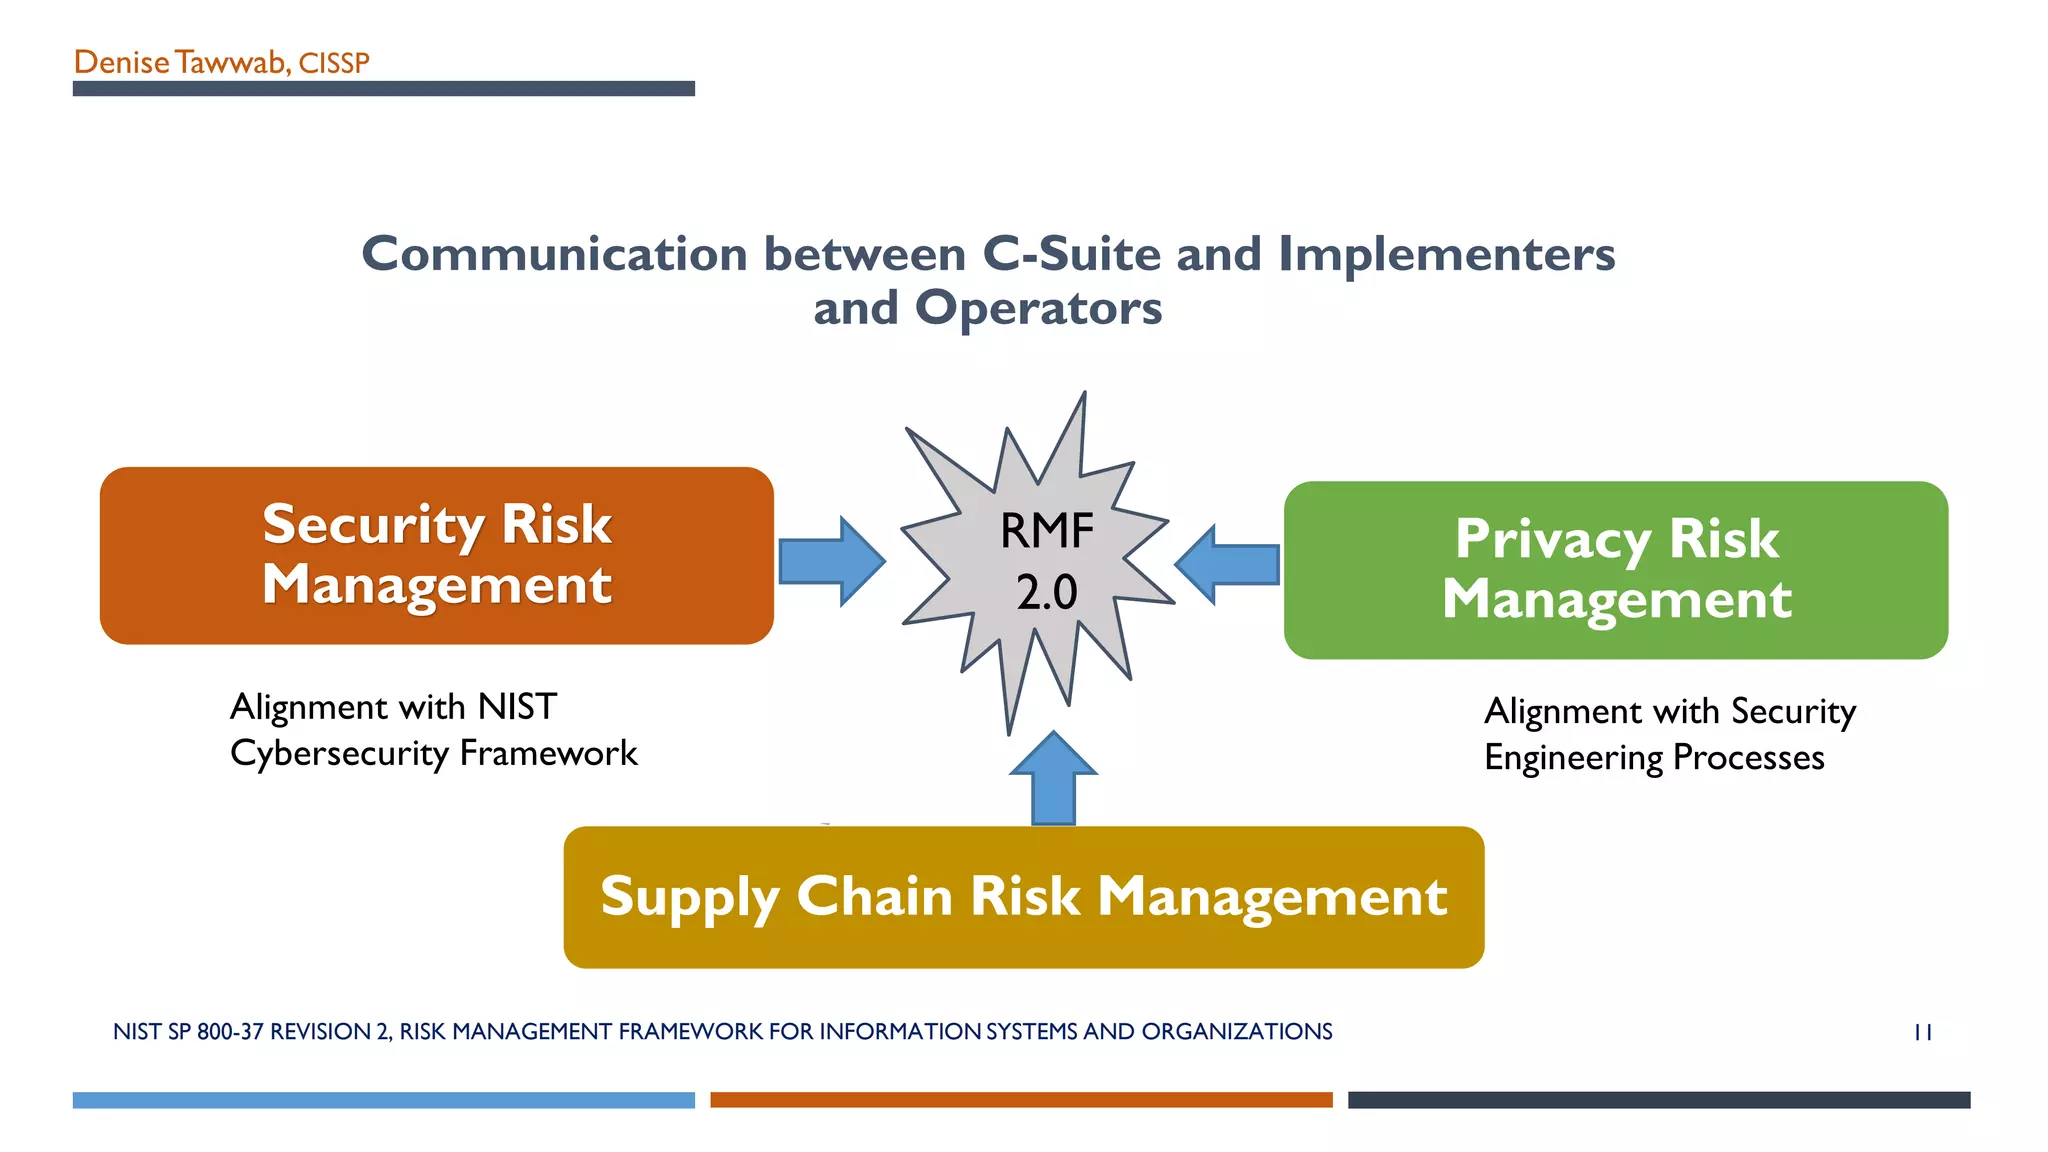
An Introduction to the NIST Risk Management Framework (RMF)
A concise overview of how the NIST Risk Management Framework (SP 800-37 Rev. 2) guides organizations in managing security and privacy risk across the system lifecycle through continuous monitoring, control assessment, authorization, and ongoing risk response to support resilient and compliant operations.



Risk Management Framework ( RMF ) Overview The selection and specification of security controls for a system is accomplished as part of an organization-wide information security program that involves the management of organizational risk ---that is, the risk to the organization or to individuals associated with the operation of a system.