"Top 3 Products for Cloud Security: A Comprehensive Guide"
In today's rapidly evolving digital landscape, securing cloud environments has become a top priority for organizations of all sizes. As businesses migrate more workloads to the public, private, and hybrid cloud, the attack surface expands—demanding a layered defense strategy built on proven technologies. While no single tool can protect every vector, three core product categories consistently emerge as foundational pillars of cloud security: Cloud Access Security Brokers (CASBs), Cloud Workload Protection Platforms (CWPPs), and Cloud Security Posture Management (CSPM) tools. Together, they form a comprehensive framework for visibility, compliance, and threat prevention.
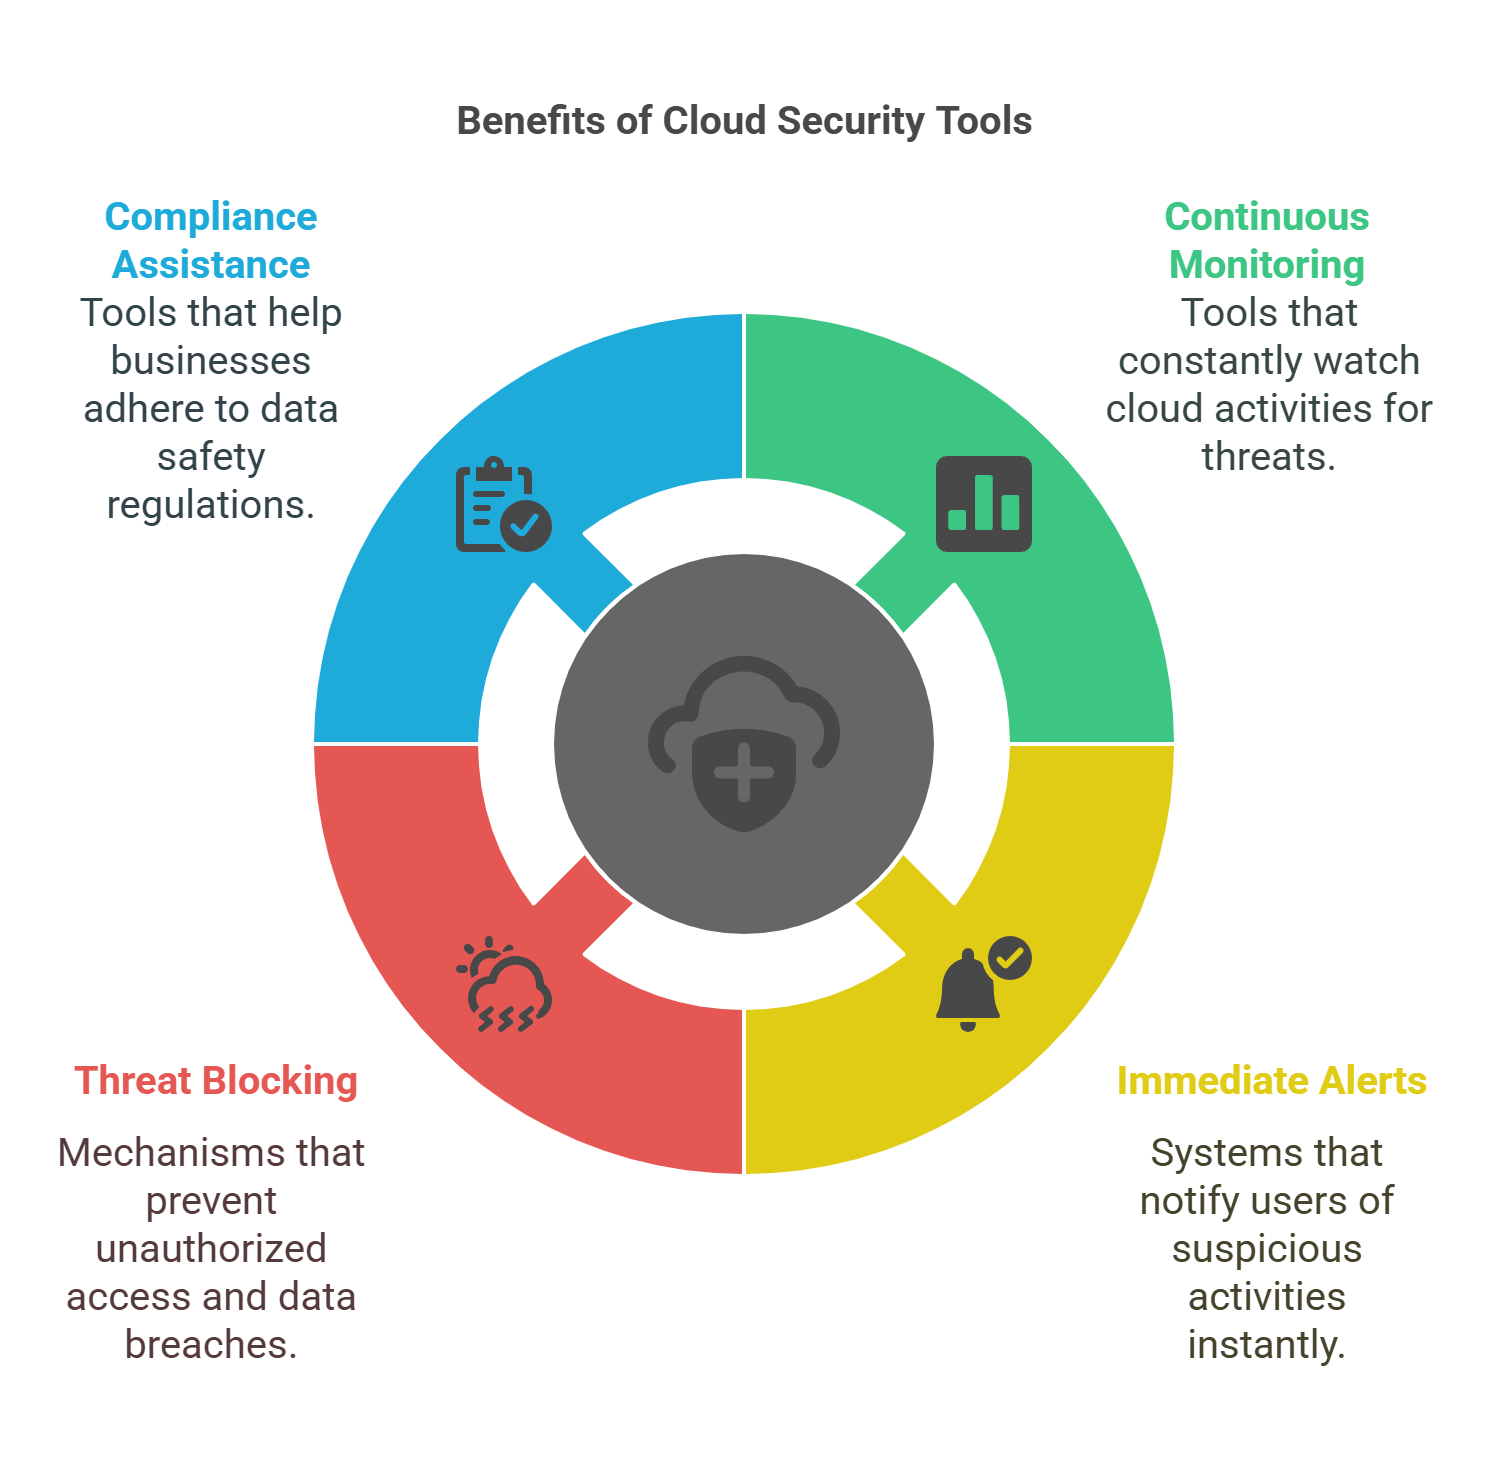
Understanding the Three Pillars of Cloud Security
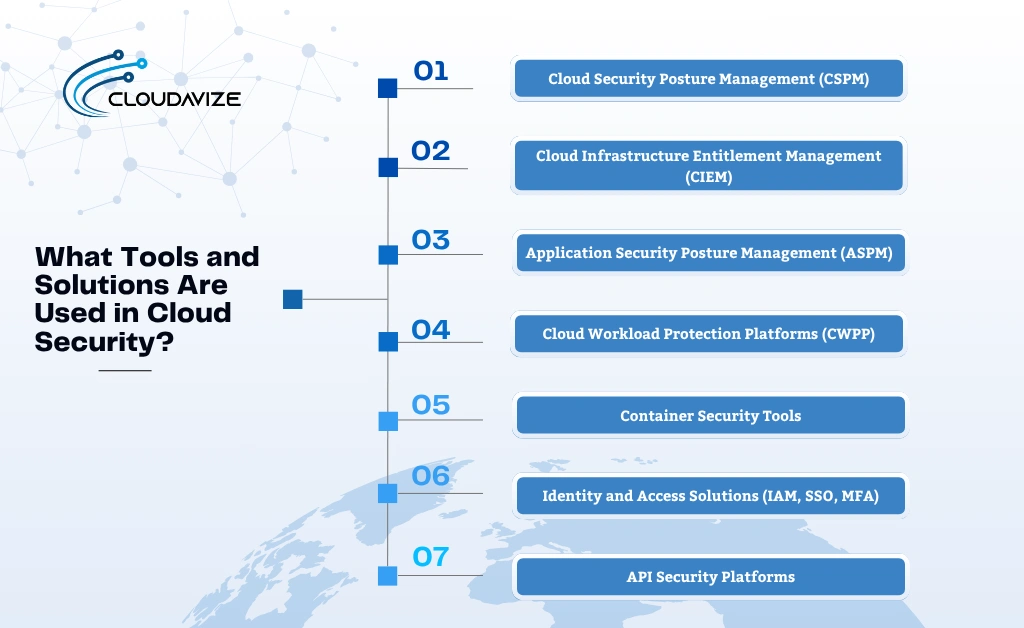
Cloud environments are dynamic by nature—resources spin up and down in minutes, identities multiply, and configurations shift constantly. Traditional perimeter-based security models simply cannot keep pace. That’s why modern cloud security relies on specialized tools engineered for this complexity. The three key products—CASB, CWPP, and CSPM—each address distinct but complementary layers of risk. CASBs enforce policies between users and cloud providers; CWPPs protect virtual machines, containers, and serverless functions; and CSPM tools continuously audit configurations to prevent missteps that could lead to breaches.
Cloud Access Security Brokers (CASBs): Enforcing Governed Access
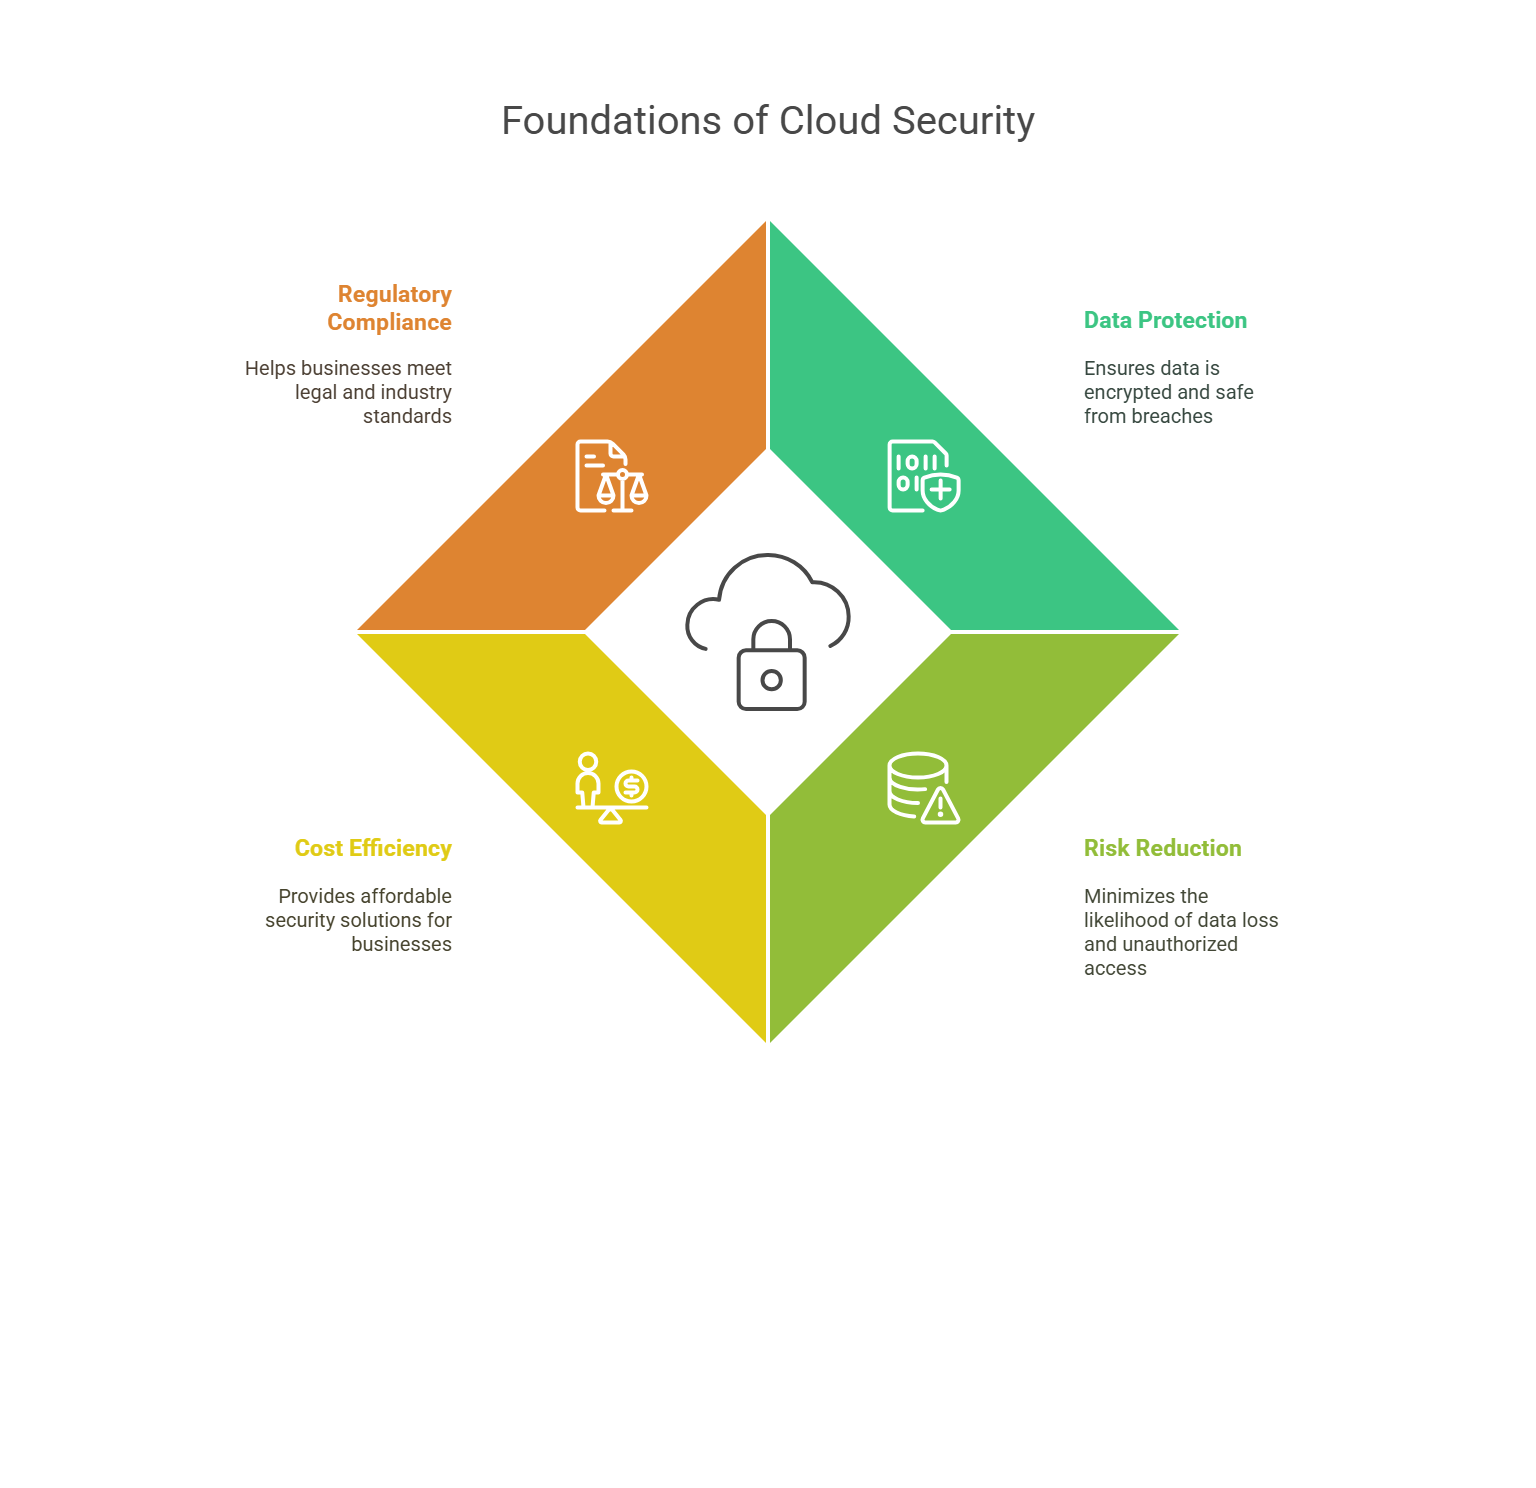
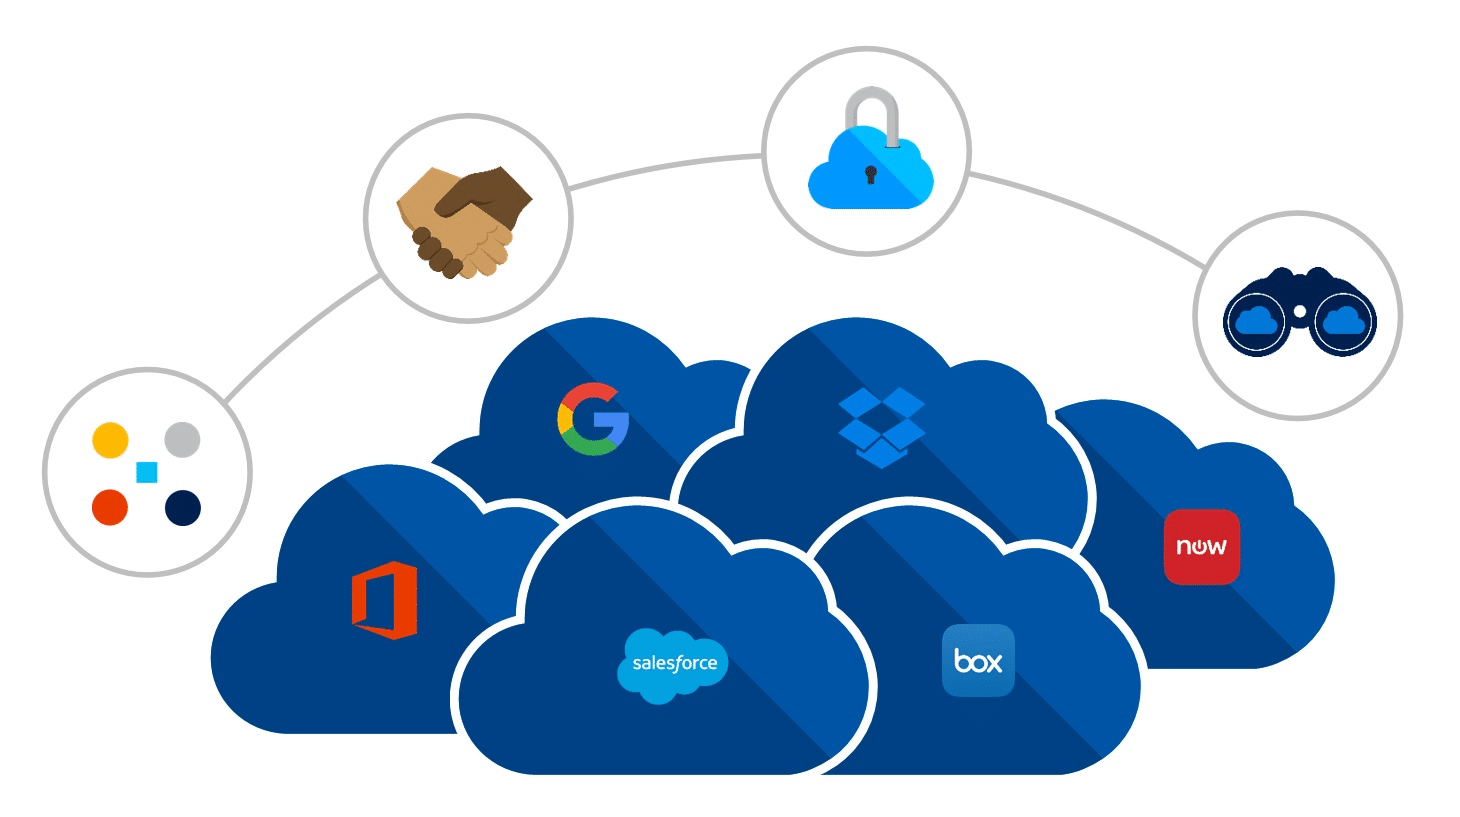
A CASB acts as an intermediary between end users and cloud service providers like Microsoft 365, Google Workspace, or AWS S3. It gives organizations granular control over who accesses what, from which device, and under which conditions. CASBs excel at detecting shadow IT, enforcing data loss prevention (DLP) policies, encrypting sensitive files before they leave the corporate network, and applying adaptive multi-factor authentication based on risk signals such as geolocation or anomalous login times.
Leading CASB solutions—such as Microsoft Defender for Cloud Apps, Netskope, or Palo Alto Networks’ Prisma Access—integrate directly with identity providers and SIEM platforms. They don’t just block threats; they provide deep visibility into user behavior and application usage across sanctioned and unsanctioned cloud apps. For regulated industries handling PII or financial data, CASBs are often non-negotiable for meeting GDPR, HIPAA, or SOC 2 requirements.
Cloud Workload Protection Platforms (CWPPs): Securing What Runs in the Cloud
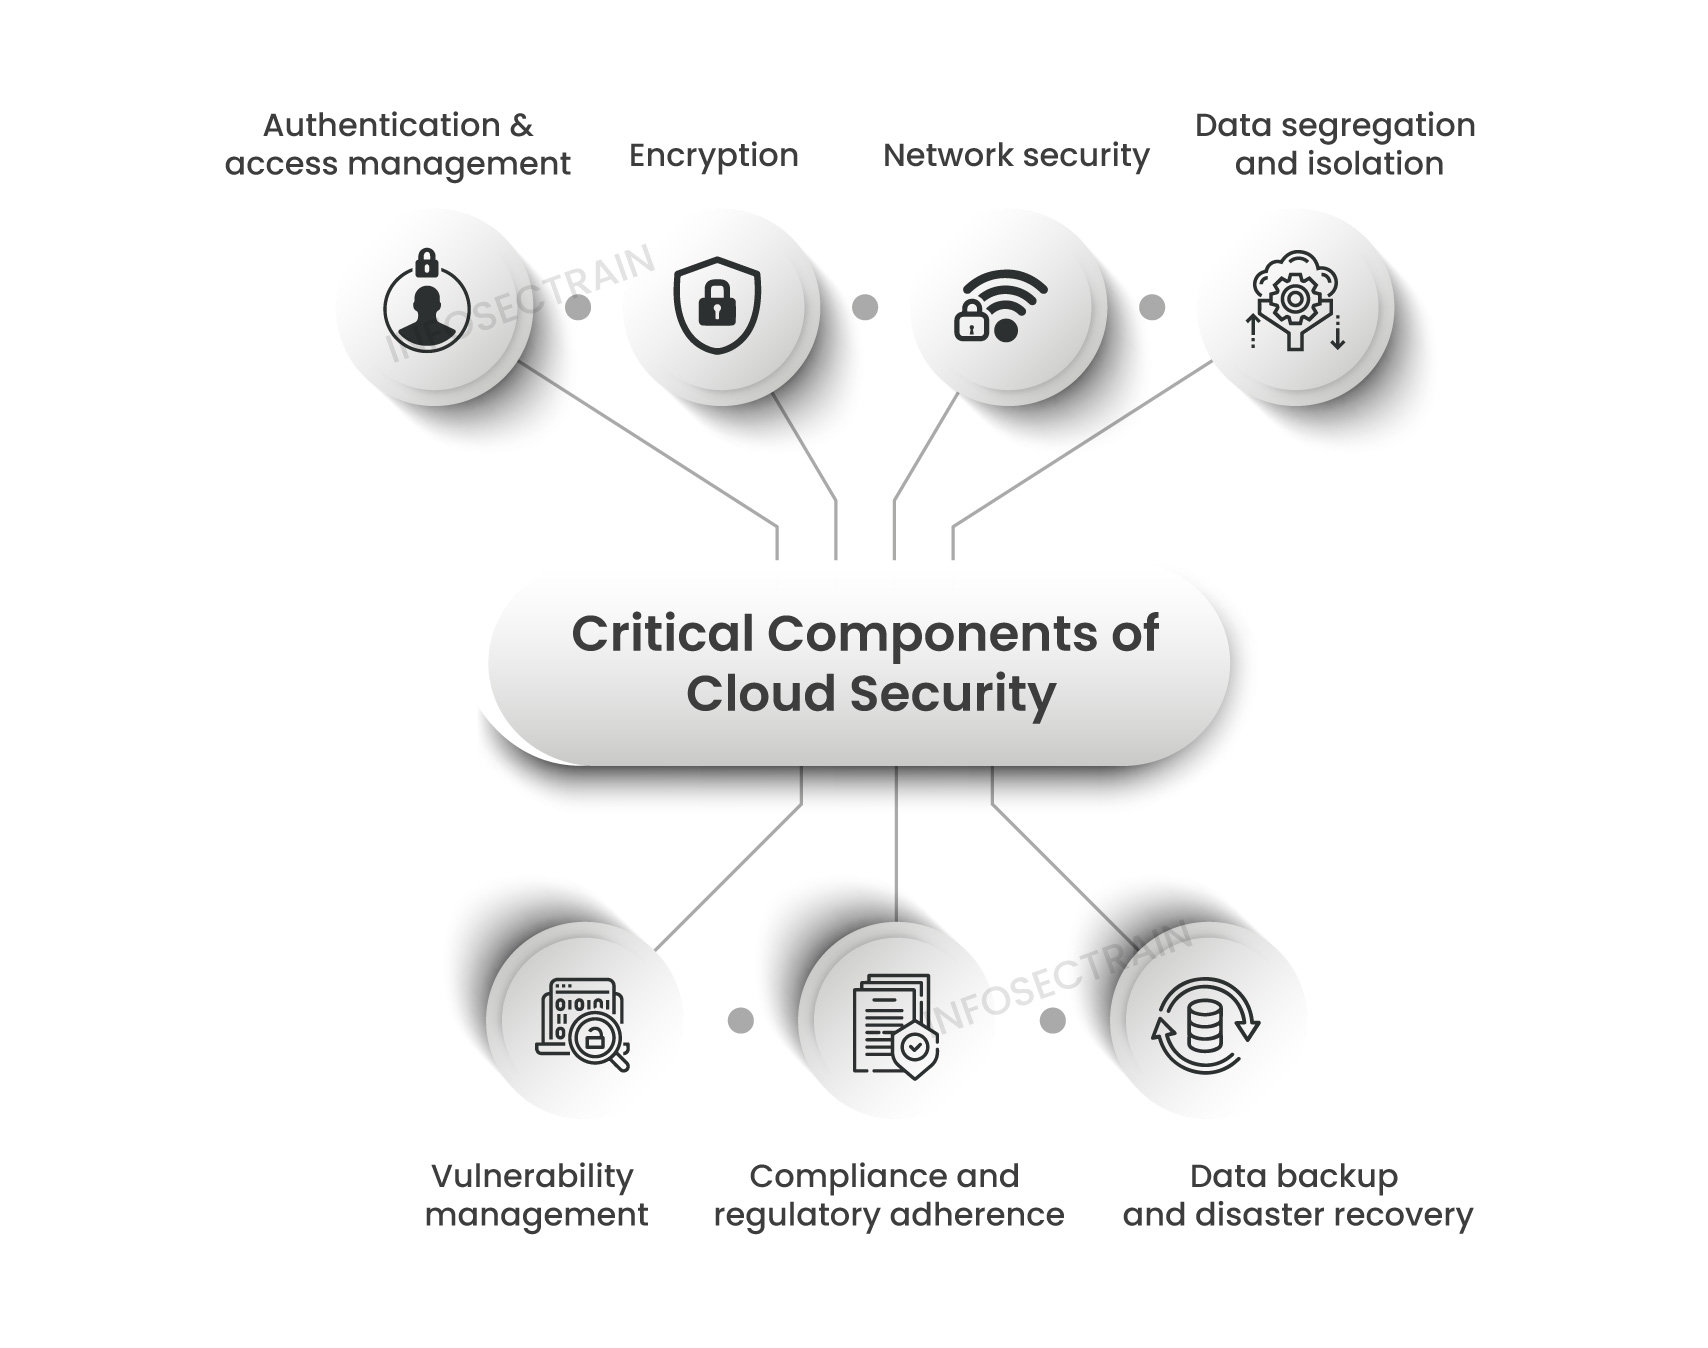
While CASBs secure access and data in transit, CWPPs focus on the workloads themselves—VMs, containers, Kubernetes clusters, and serverless functions. These platforms offer runtime protection, vulnerability scanning, integrity monitoring, micro-segmentation, and behavioral analytics tailored to cloud-native architectures. A CWPP detects known CVEs in container images during CI/CD pipelines, blocks cryptojacking attempts on compromised instances, and enforces least-privilege execution policies.
Solutions like Wiz, Lacework, or Trend Micro Cloud One fall into this category. What sets them apart is agentless or lightweight deployment models that scale elastically with cloud infrastructure. Crucially, they map lateral movement paths—showing how an attacker could pivot from a misconfigured S3 bucket to a production database—enabling proactive hardening before incidents occur.

Cloud Security Posture Management (CSPM): Automating Compliance and Configuration Hygiene
The third critical product category, CSPM, continuously scans cloud configurations against benchmarks like CIS, NIST, or custom compliance frameworks. Misconfigurations remain the leading cause of cloud breaches—publicly exposed storage buckets, overly permissive IAM roles, or unencrypted databases. CSPM tools like AWS Security Hub, Google Security Command Center, or third-party options such as Orca Security and Palo Alto Prisma Cloud automatically detect these risks, prioritize them by exploitability, and often suggest or even auto-remediate fixes.
Unlike reactive monitoring, modern CSPMs integrate into DevOps workflows, flagging drift from secure baselines during infrastructure-as-code deployments. This shift-left approach ensures that security isn’t bolted on post-deployment but baked into the development lifecycle. When combined with CWPPs and CASBs, CSPM closes the loop: it ensures that what’s deployed is configured correctly, that workloads are protected at runtime, and that user access to those workloads is tightly governed.

Building a Unified Cloud Security Strategy
No single product addresses all cloud risks in isolation. The real power lies in integrating CASB, CWPP, and CSPM into a cohesive security fabric that provides end-to-end visibility—from the user’s browser to the container running in a Kubernetes cluster. Forward-thinking organizations are moving toward consolidated platforms (like Palo Alto Prisma Cloud or Microsoft Defender for Cloud) that bundle these capabilities under one pane of glass, reducing alert fatigue and accelerating incident response.







However, consolidation shouldn’t come at the cost of depth. Evaluate each solution based on your specific cloud footprint, regulatory obligations, and internal expertise. Start with CSPM to clean up critical misconfigurations, layer in CWPP for runtime protection of critical workloads, and deploy CASB if you rely heavily on SaaS applications. Whatever your path, remember: cloud security isn’t a product—it’s a continuous practice powered by the right trio of tools.