"Why & How to Use Azure AD: A Comprehensive Guide"
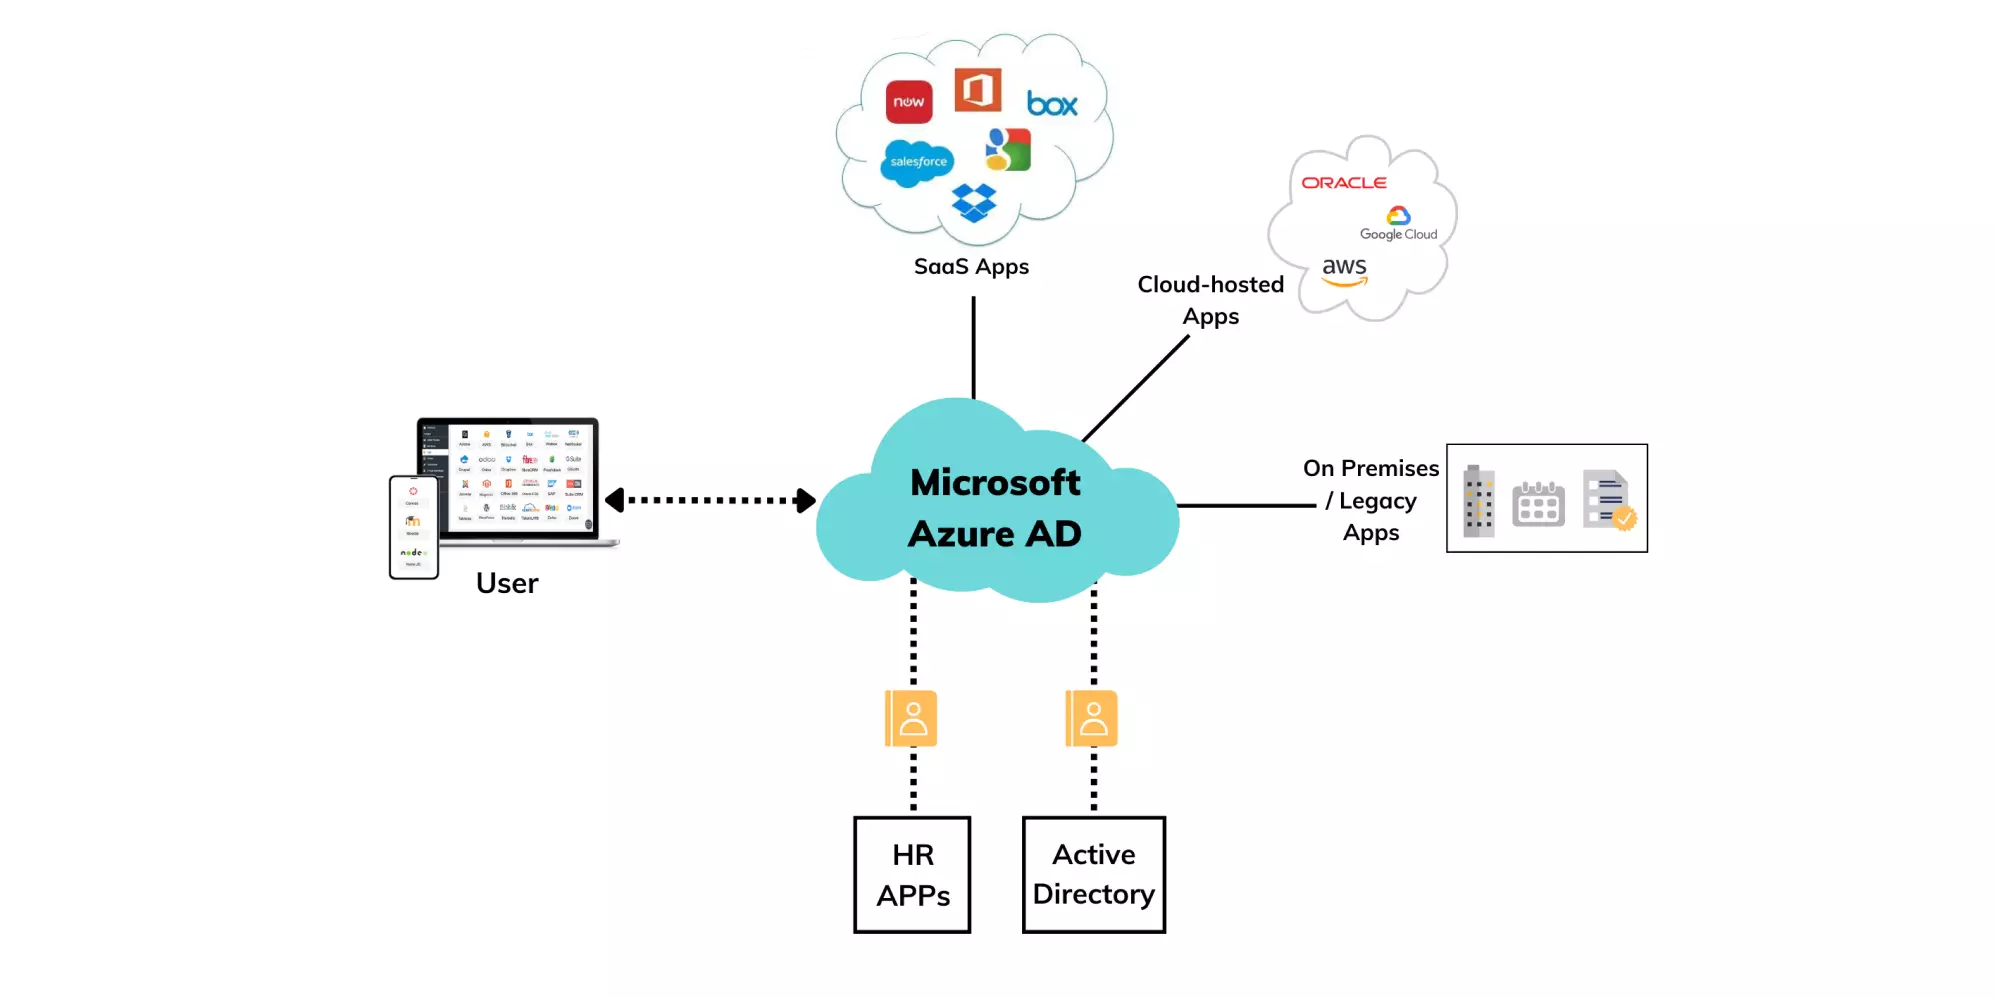
In today’s hybrid and cloud-first work environments, managing user identities securely and efficiently is no longer optional—it’s foundational. Microsoft Azure Active Directory (Azure AD), now rebranded as Microsoft Entra ID, has emerged as a cornerstone solution for organizations seeking centralized identity and access management across cloud apps, on-premises systems, and third-party platforms. But why use Azure AD specifically? The answer lies in its seamless integration with the Microsoft ecosystem, robust security frameworks, and scalable architecture designed for modern enterprise needs.

Unified Identity Across Hybrid Environments

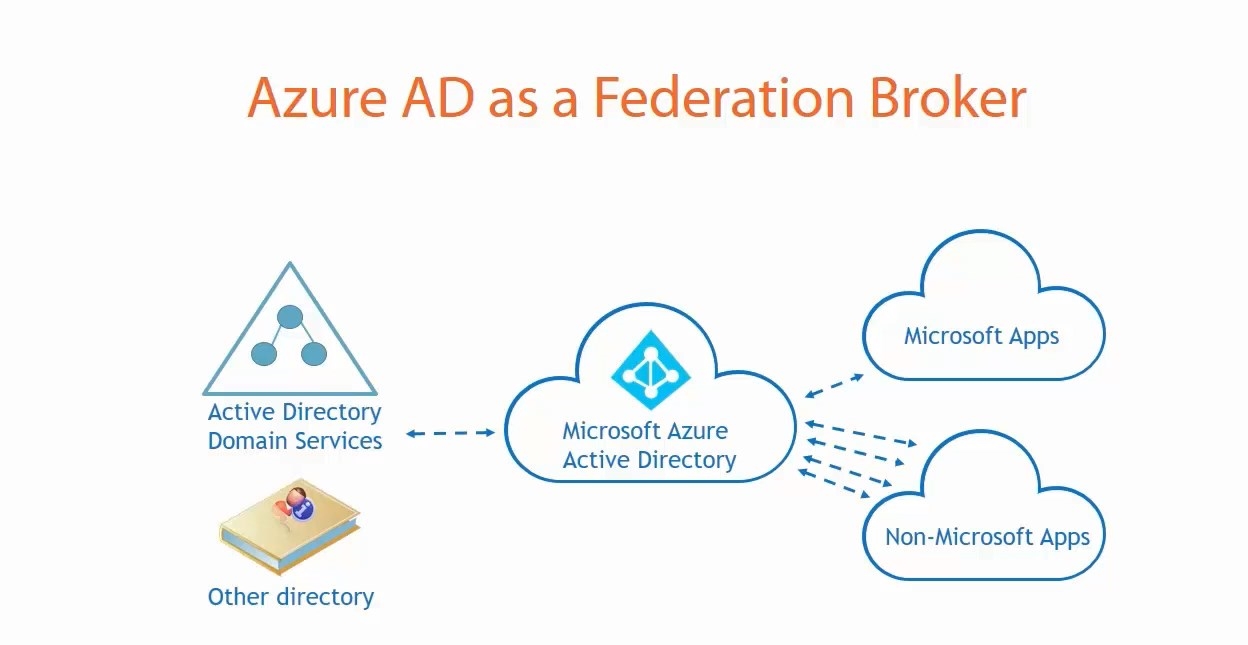
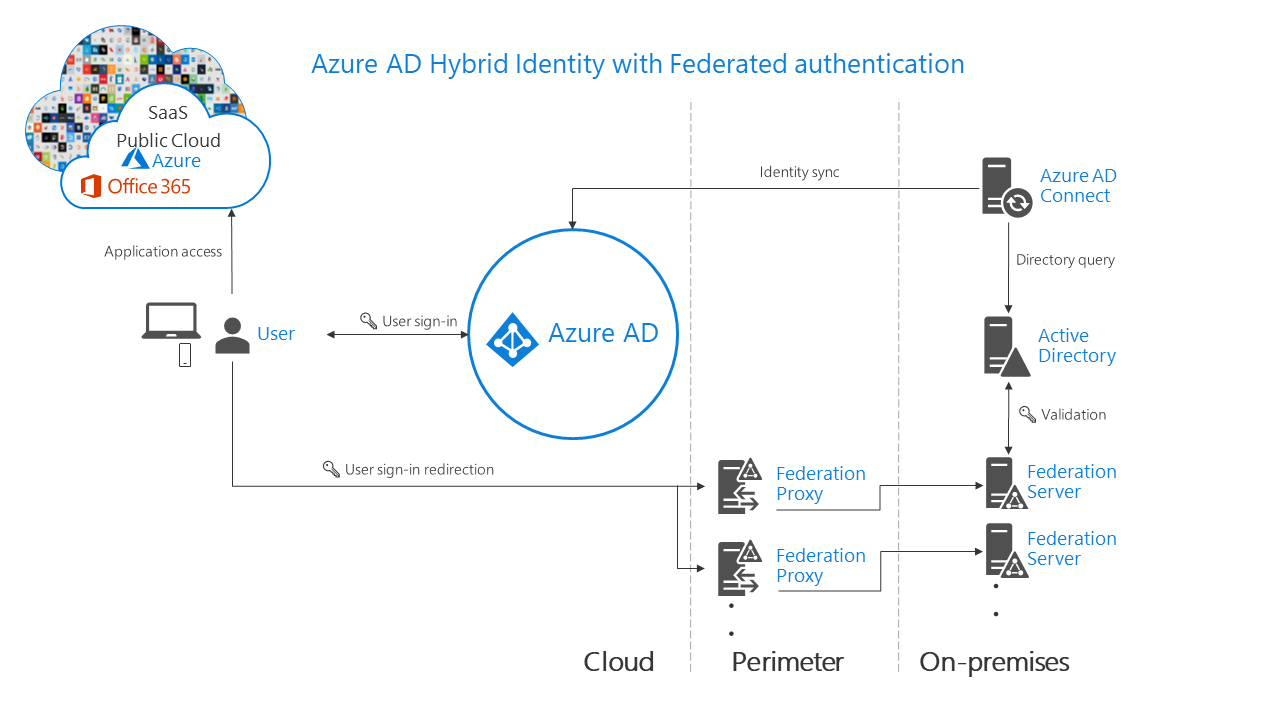
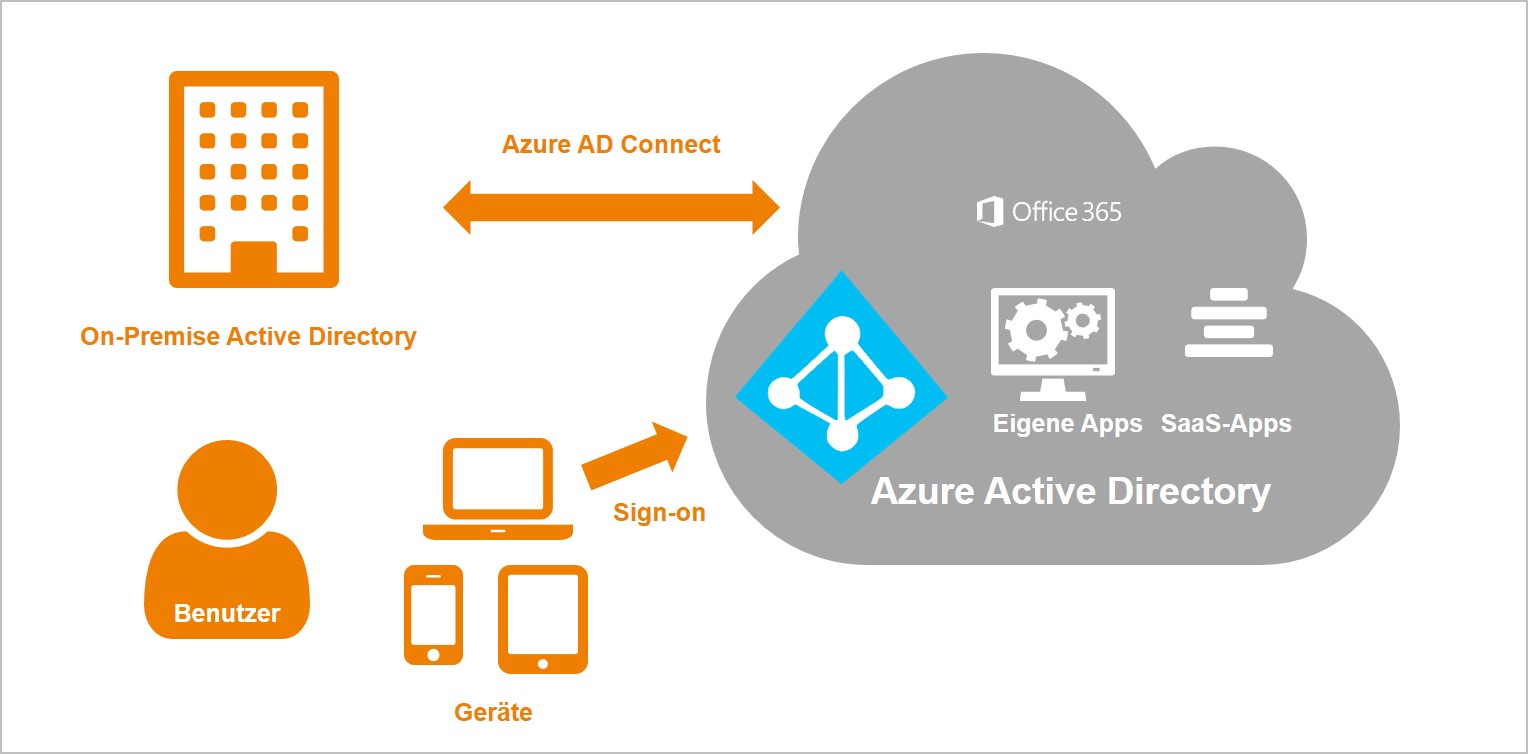
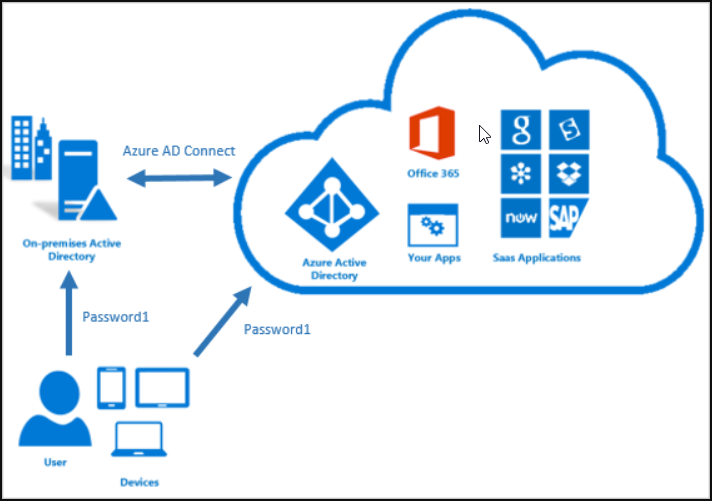
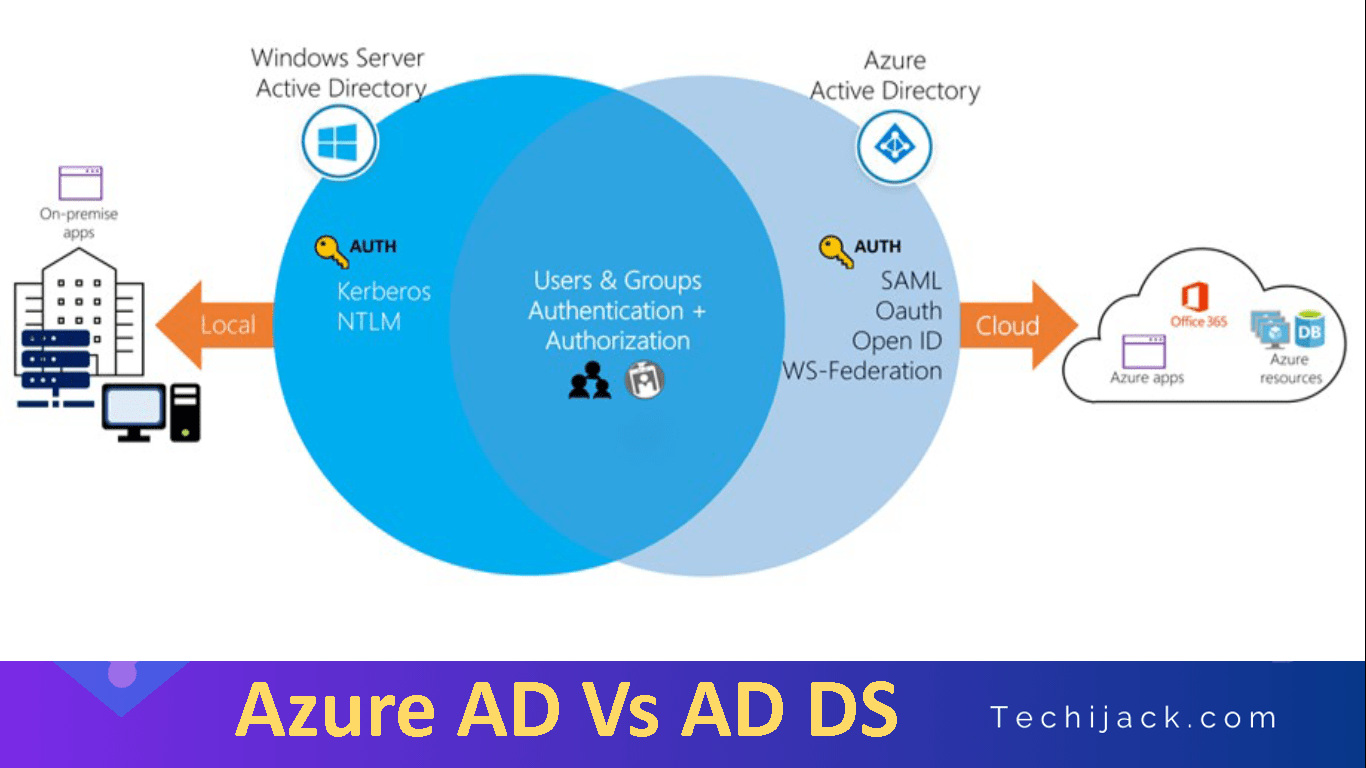
Azure AD bridges the gap between cloud and on-premises directories. Whether your business runs entirely in the cloud or maintains legacy infrastructure, Azure AD synchronizes with your existing Active Directory via Azure AD Connect. This hybrid identity model ensures users have one consistent set of credentials to access both cloud resources like Microsoft 365 and internal line-of-business applications. Eliminating the need for disparate login systems reduces password fatigue, minimizes IT overhead, and streamlines user provisioning—all while maintaining compliance and control.
Seamless Single Sign-On (SSO)
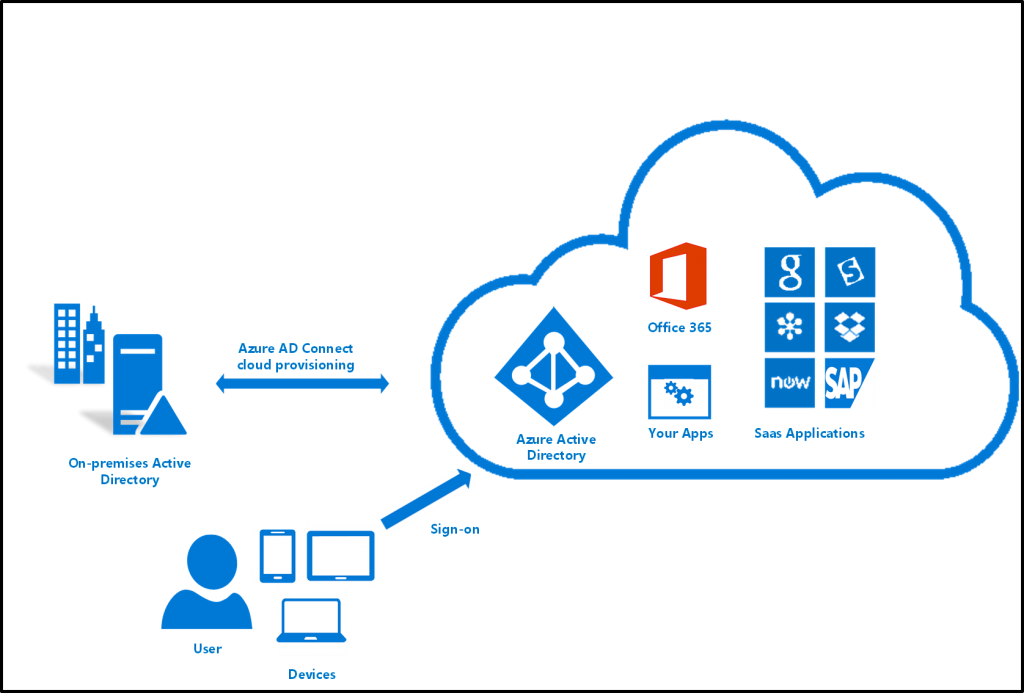
One of the most compelling reasons to adopt Azure AD is its built-in support for Single Sign-On. Once configured, users authenticate just once and gain instant access to thousands of pre-integrated SaaS applications—from Salesforce to ServiceNow—without re-entering credentials. This not only boosts productivity but significantly lowers the risk of phishing attacks tied to password reuse. SSO isn’t just convenience; it’s a strategic security measure that enforces consistent authentication policies across every app your team uses.
Enterprise-Grade Security and Conditional Access
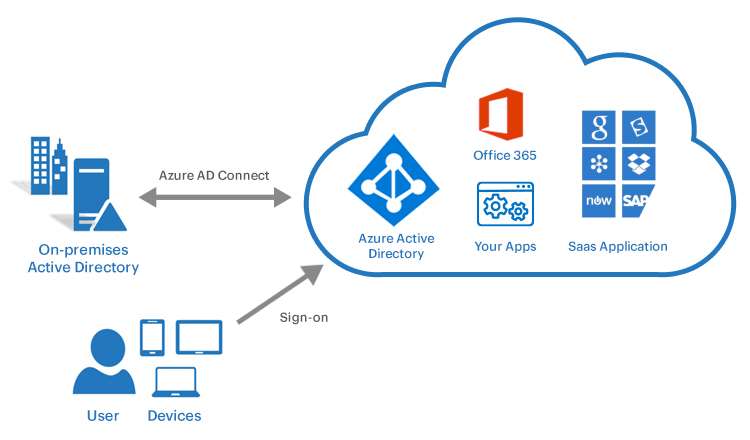
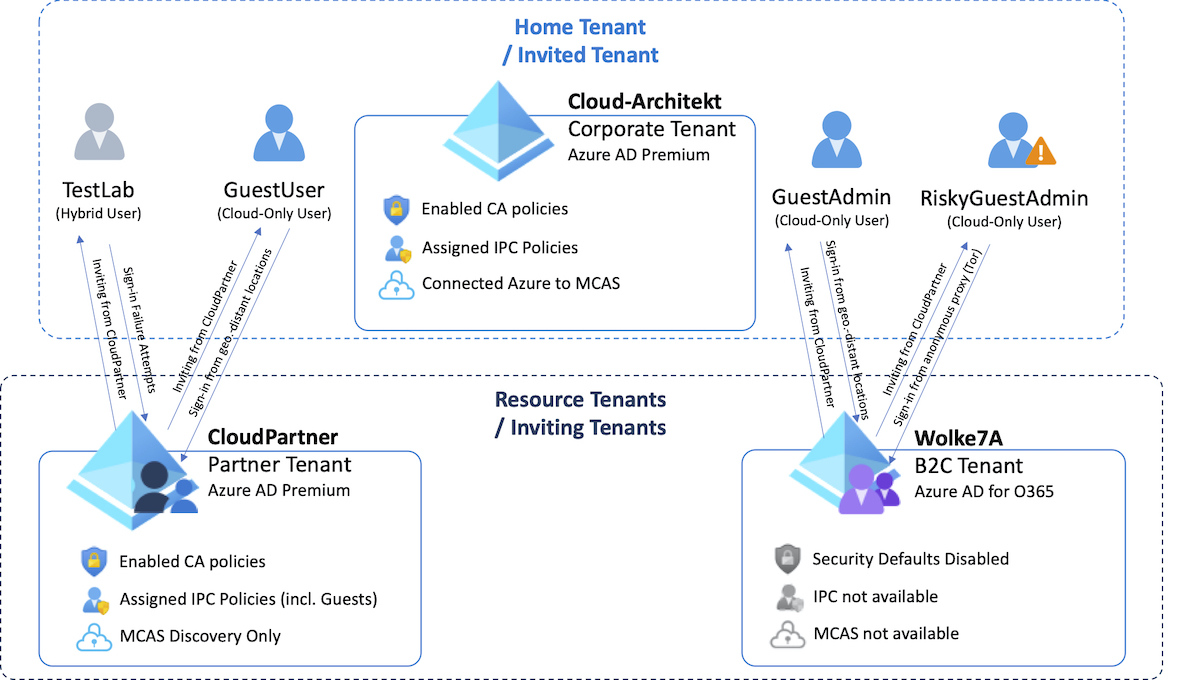
Beyond convenience, Azure AD delivers advanced security capabilities that adapt to today’s dynamic threat landscape. Features like Conditional Access policies let administrators enforce granular rules based on device health, user location, risk level, and app sensitivity. For example, you can require multi-factor authentication (MFA) only when a user logs in from an unfamiliar country or an uncompliant device—balancing security with user experience. These policies integrate natively with Microsoft Intune for device management, creating a zero-trust framework that verifies every access request before granting entry.
| Feature | Azure AD Offerings |
|---|---|
| Identity Protection | Real-time risk detection and automated remediation |
| Privileged Identity Management | Just-in-time access for admin roles |
| Audit Logs | Detailed sign-in and activity tracking |
This layered approach ensures threats are caught early, permissions are tightly scoped, and anomalies trigger instant alerts.
Scalability and Developer Flexibility
For engineering teams, Azure AD provides rich APIs and SDKs that embed identity into custom applications effortlessly. Using the Microsoft Identity Platform (formerly Azure AD v2.0), developers implement OAuth 2.0 and OpenID Connect protocols to outsource authentication logic securely. Whether building internal tools or customer-facing portals, Azure AD handles token issuance, consent flows, and scoping without reinventing auth systems. Its global scale—backed by Microsoft’s infrastructure—guarantees uptime and regional compliance out of the box.
Cost Efficiency and Ecosystem Synergy

While Azure AD Free includes core features like SSO and B2B collaboration, tiers like Azure AD Premium add self-service password reset and advanced reporting. Crucially, if you already use Microsoft 365, Azure AD is included—no extra cost for foundational identity services. Even standalone deployments consolidate spending by replacing fragmented identity solutions with a single pane of glass for access reviews, app assignments, and license tracking.
Compliance Made Transparent

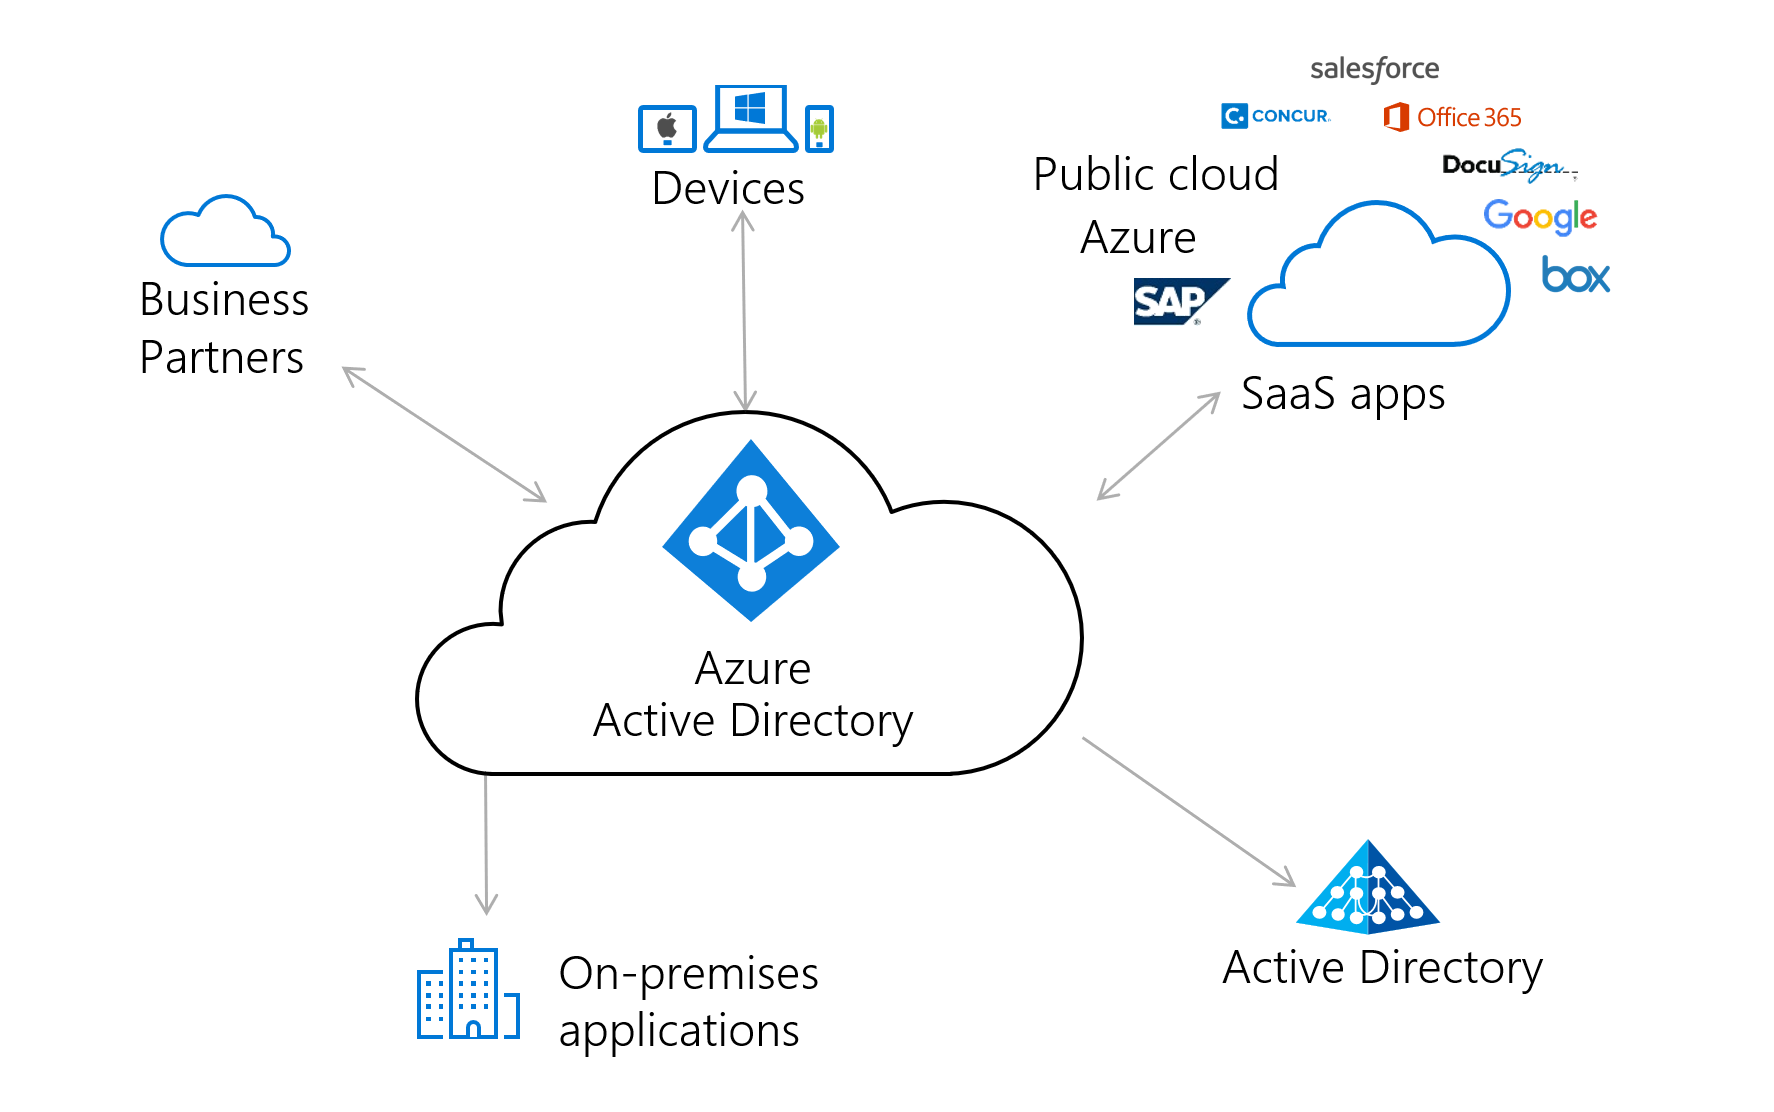
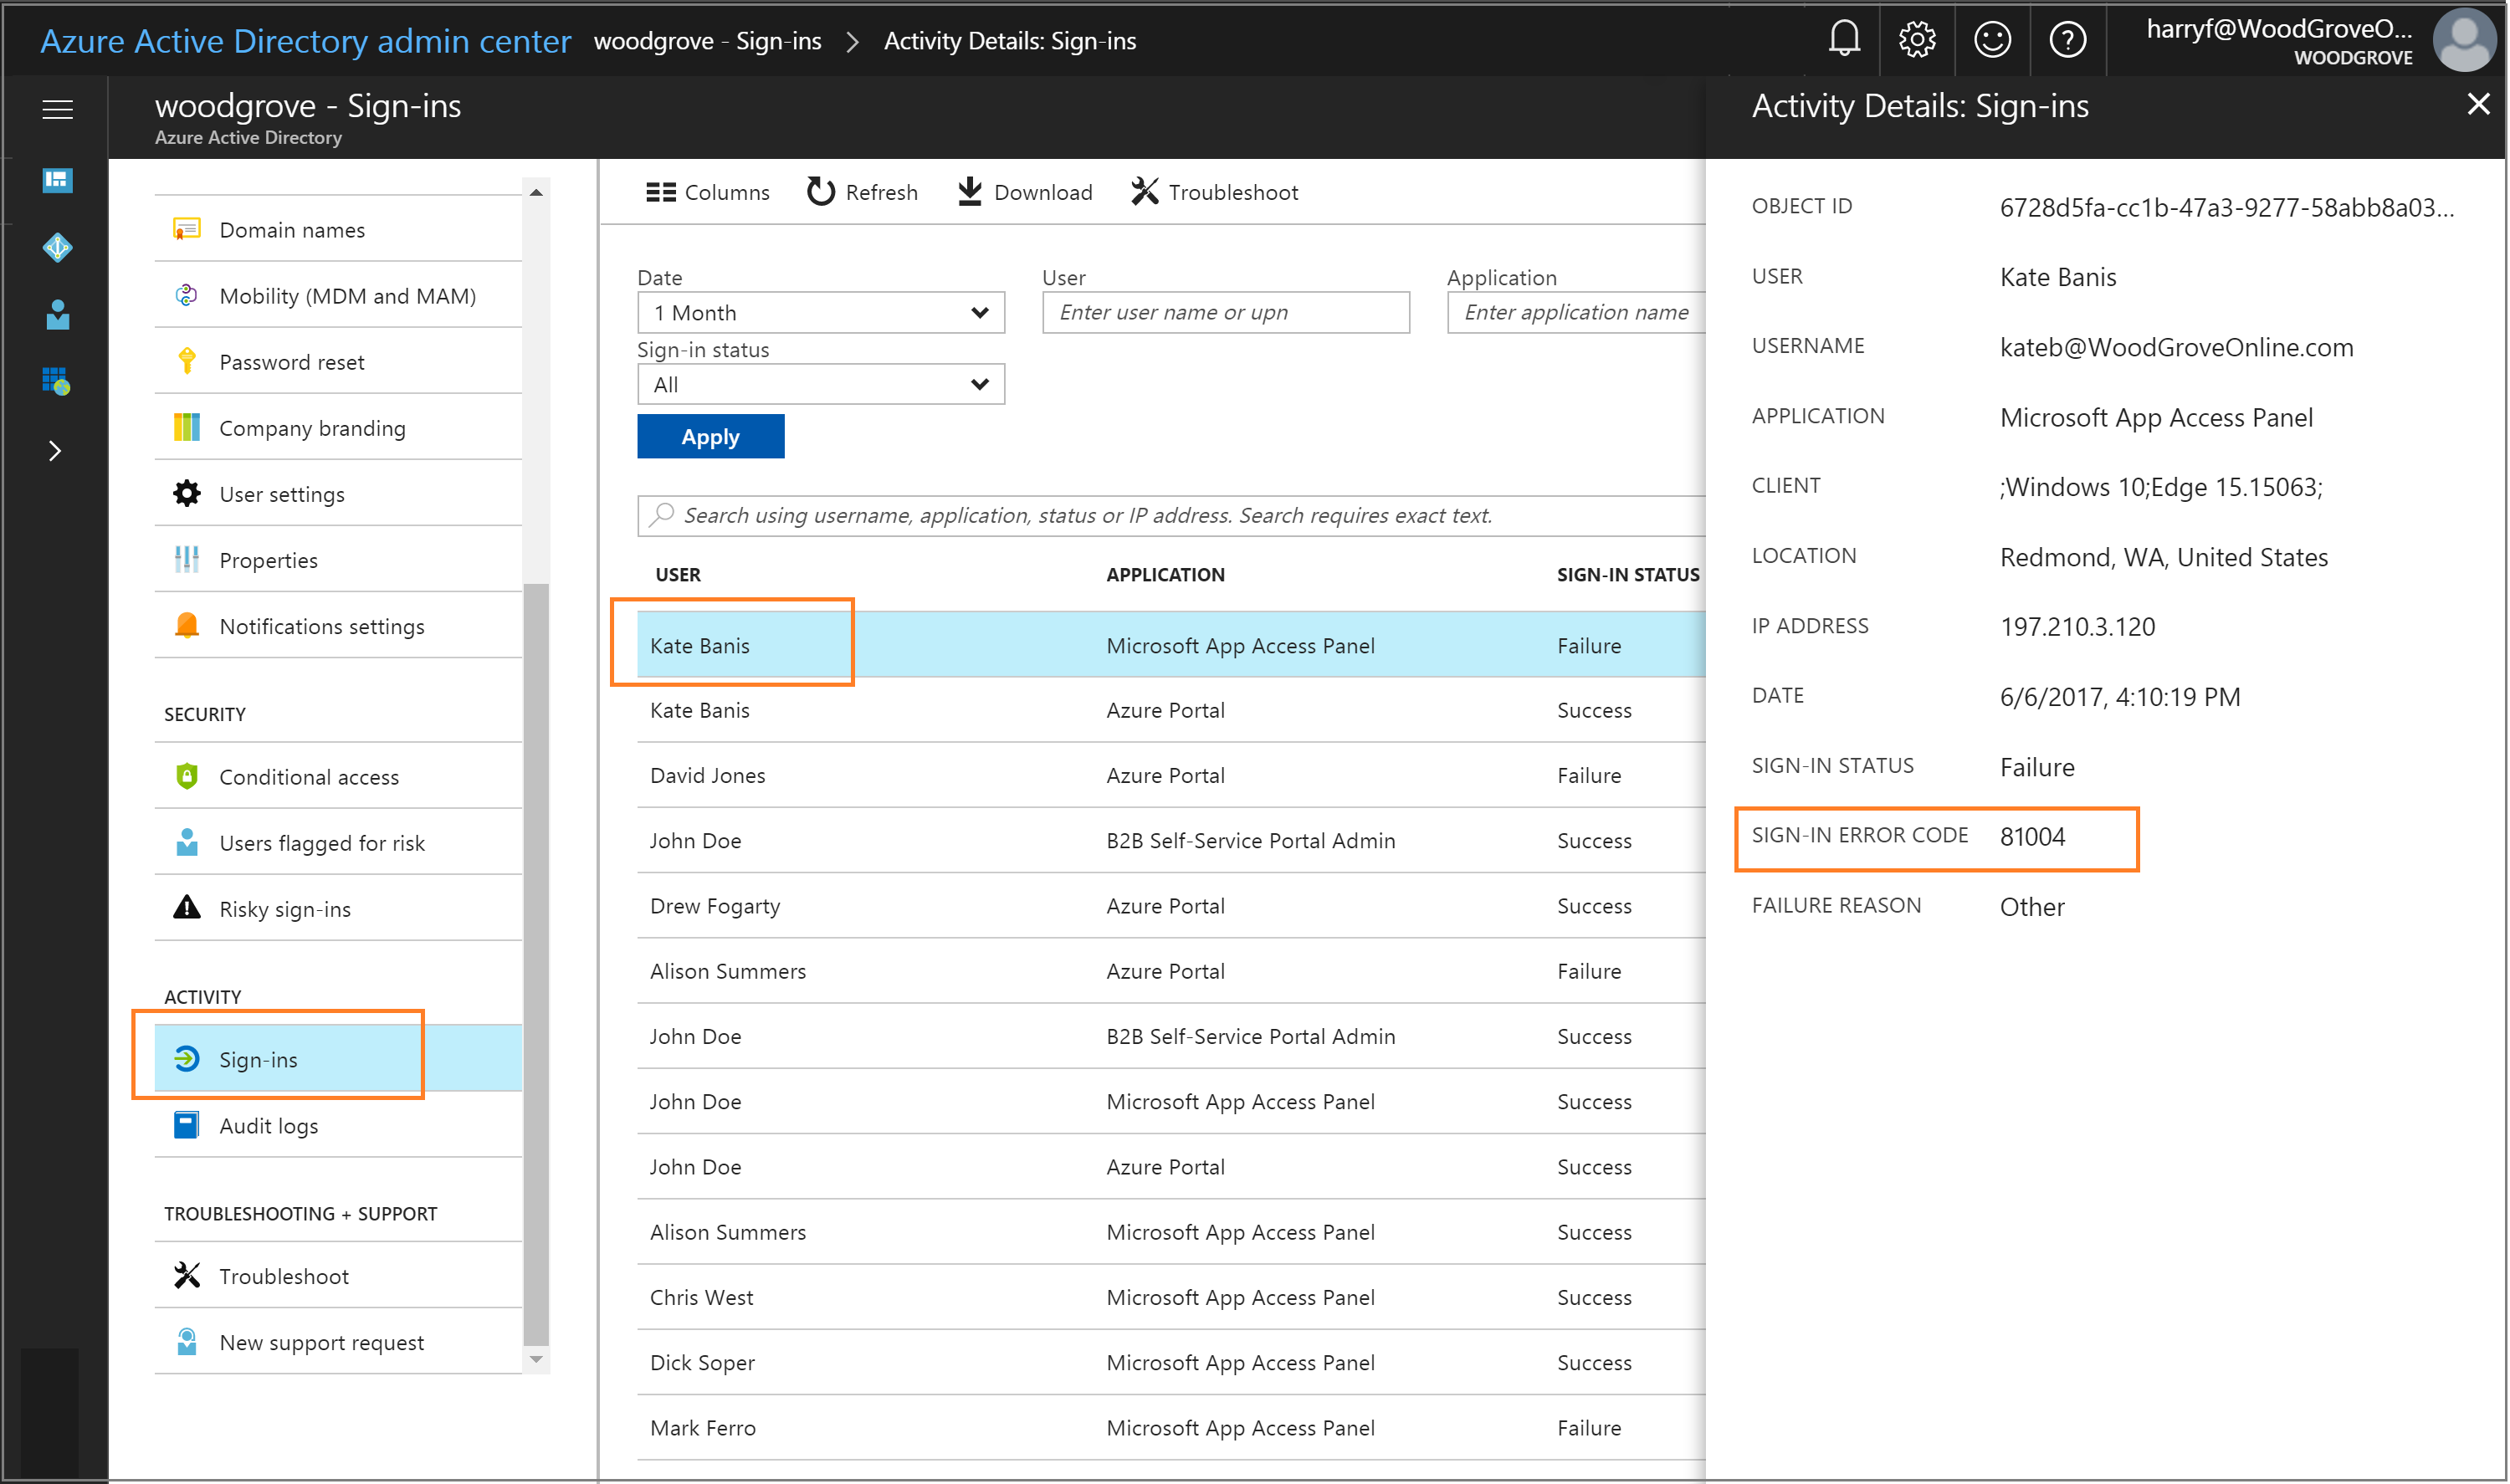



Regulated industries rely on Azure AD’s built-in compliance tools. Automated access reviews ensure least-privilege access, while audit logs satisfy GDPR, HIPAA, or SOX requirements. Privileged Identity Management further restricts admin roles to time-bound sessions only when needed. During audits, teams generate detailed reports showing exactly who accessed what, where, and when—critical for forensic analysis.
Ultimately, Azure AD isn’t just another directory; it’s the connective fabric binding people, devices, and policies in a world where breaches start with compromised credentials. From startups scaling cloud-native apps to enterprises modernizing legacy systems, using Azure AD means fewer vulnerabilities, faster workflows, and a path to true zero trust.