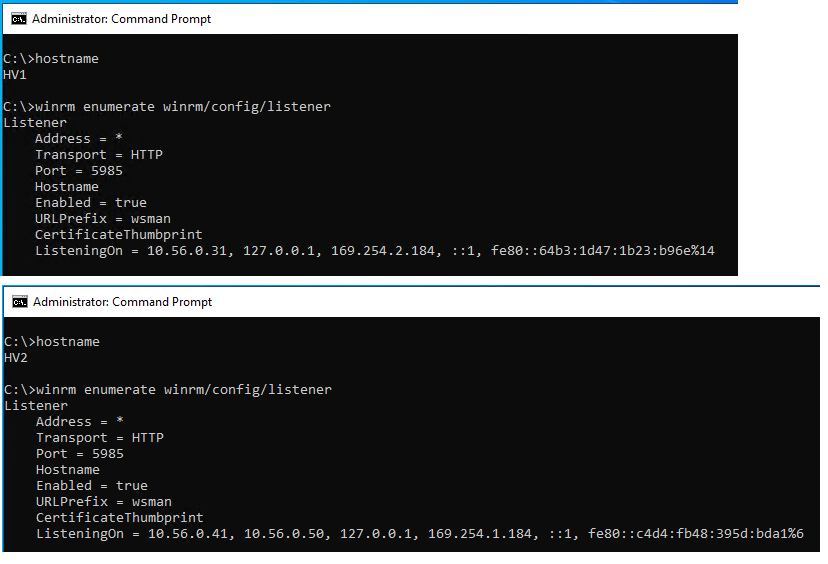
"Fix Windows Server 2016: Server Manager Online Data Retrieval Failures"
When Windows Server 2016 Server Manager online data retrieval failures occur, administrators can find themselves locked out of critical update and role information that keeps their environments secure and compliant. This persistent issue manifests when Server Manager attempts to pull data from Microsoft's online services but encounters connectivity blocks, security restrictions, or infrastructure failures. Understanding the root causes and implementing targeted fixes helps maintain operational continuity and reduces administrative overhead.
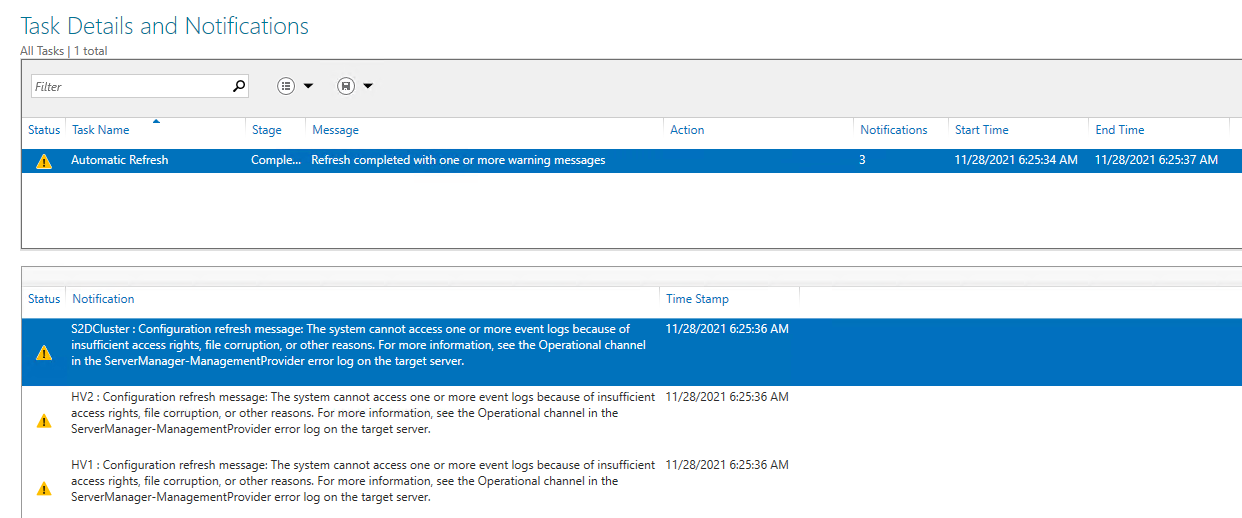
Common Causes of Online Data Retrieval Failures

Several underlying factors trigger these failures. Proxy misconfigurations rank among the most frequent culprits, particularly in enterprise networks where web traffic must route through intermediary servers before reaching external endpoints. SSL/TLS certificate validation errors also play a significant role—when servers lack root certificate updates or when intermediate certificates are misconfigured, secure connections to Microsoft endpoints simply fail.
Network segmentation policies in strict security environments often block the specific URLs and IP ranges that Server Manager relies on. Microsoft operates content delivery networks and dedicated endpoints for update metadata, and overly aggressive firewall rules can inadvertently sever these connections. Authentication issues with Windows Update services compound the problem when cached credentials expire or domain policies restrict automatic online access.
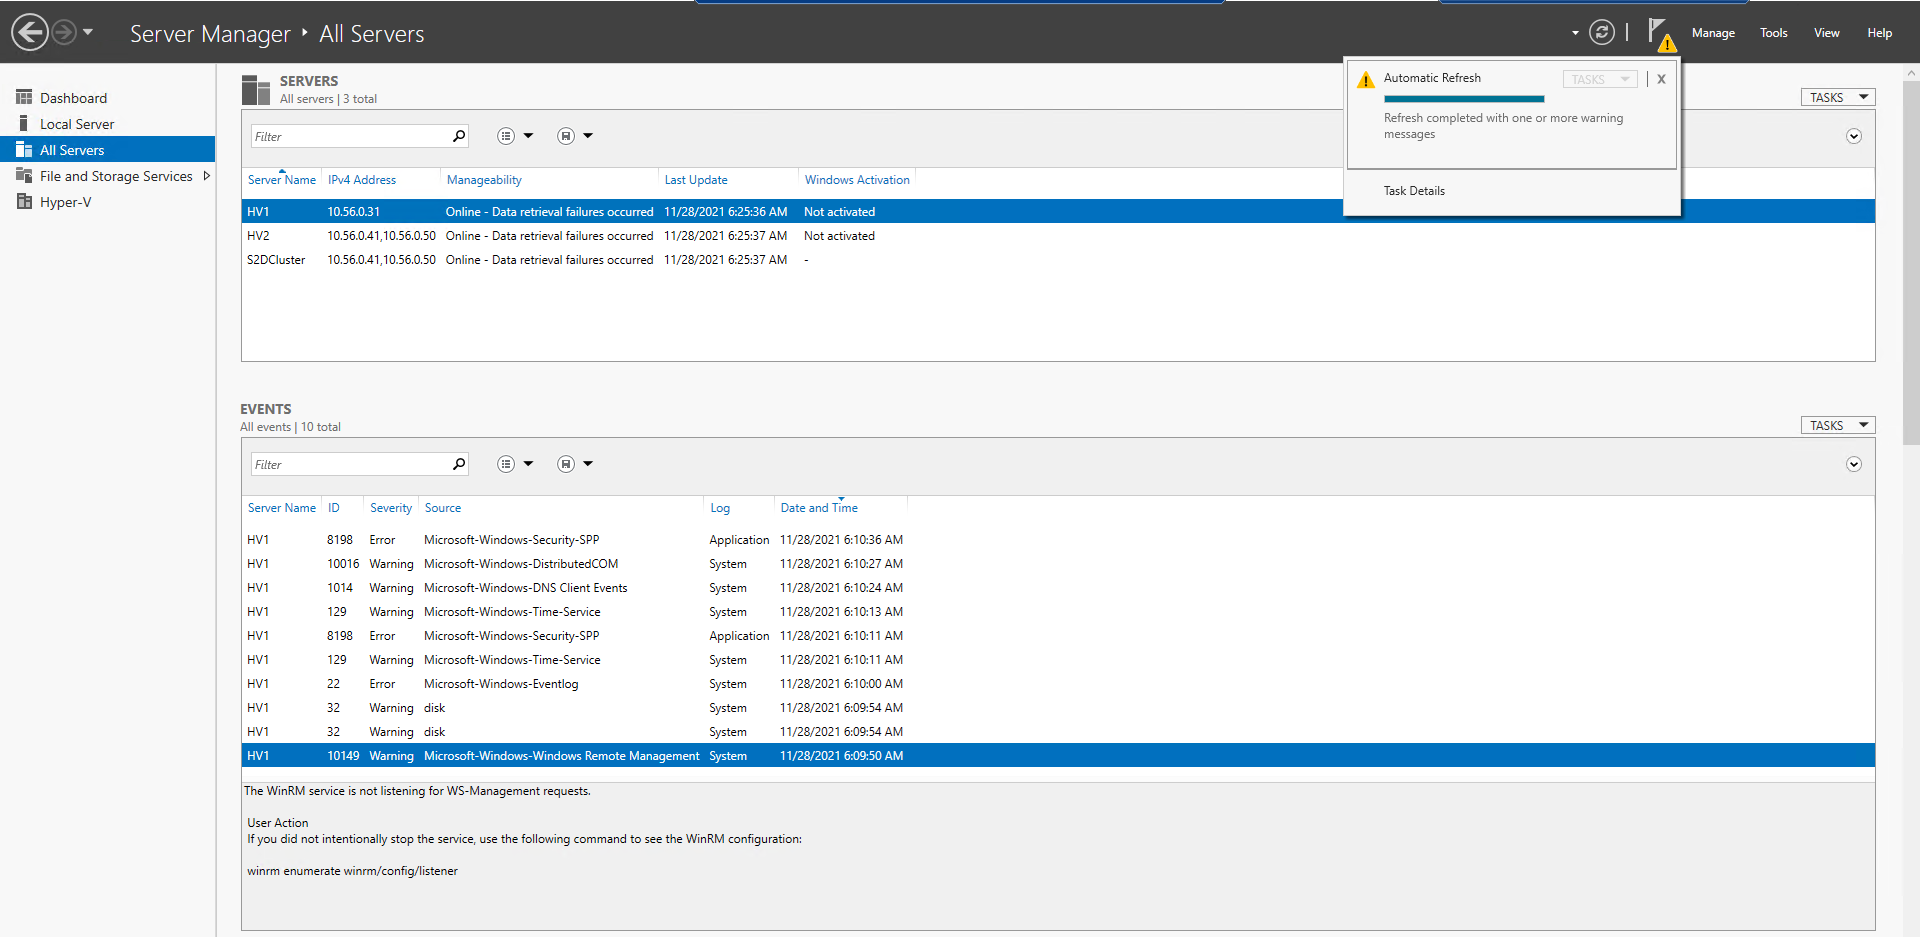
Impact on Server Operations
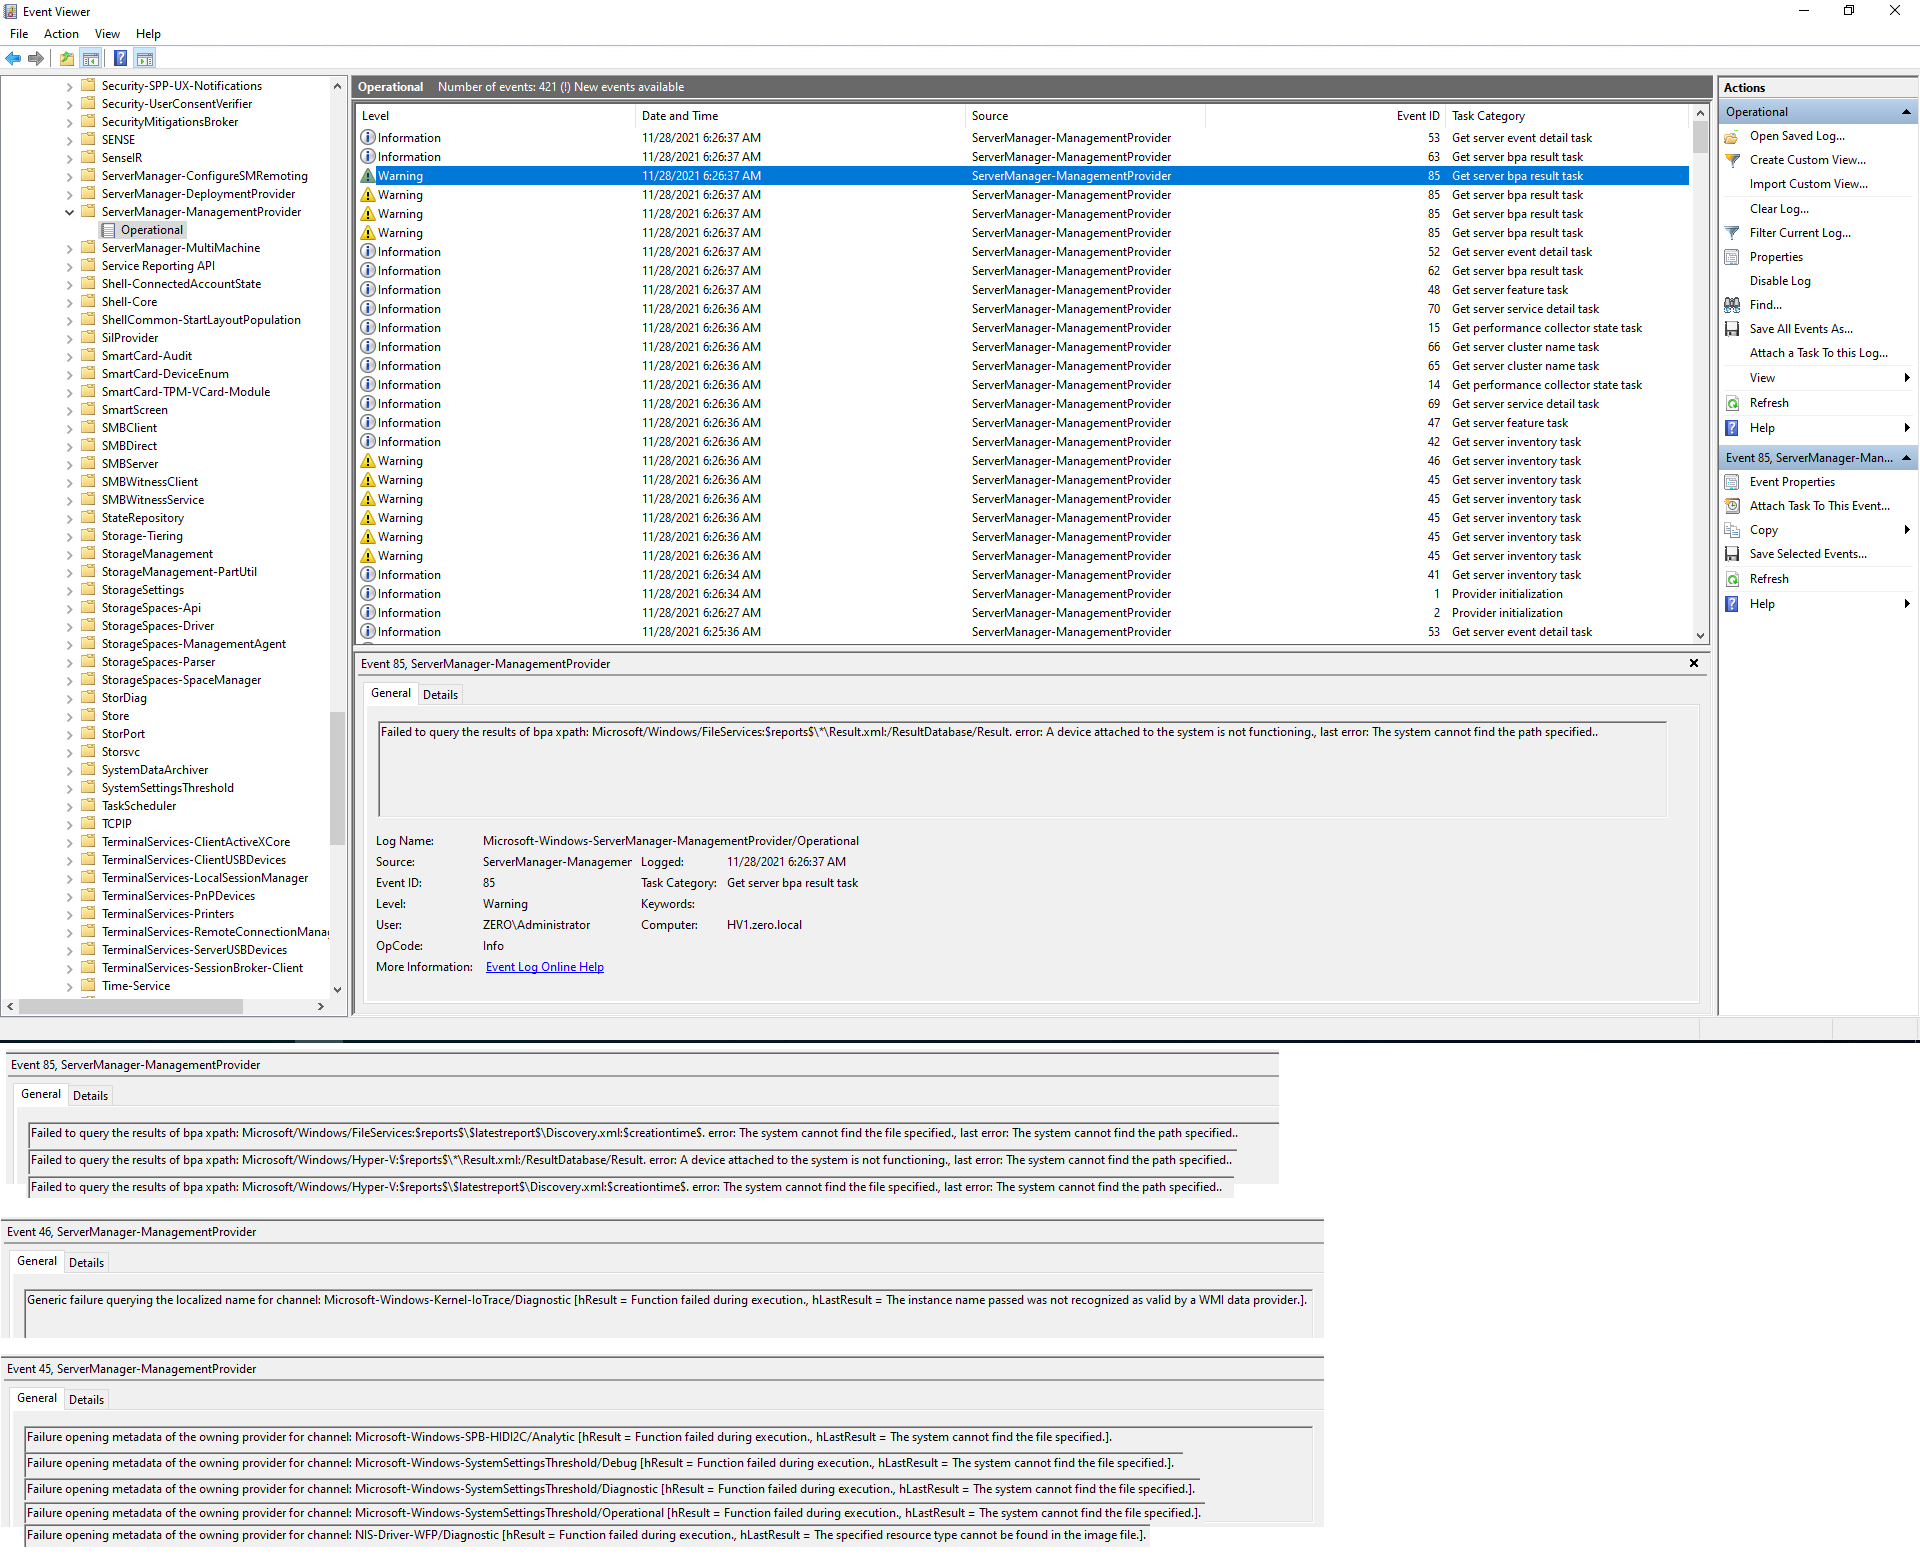
Administrators facing these failures lose access to important dashboard information about available updates, out-of-sync server roles, and deprecated features requiring attention. The Server Manager console may display yellow warning banners or simply show empty data fields where update compliance information should appear. Troubleshooting becomes more difficult when the tools designed to surface diagnostic information require online access to function fully.

Operational Consequences
The inability to retrieve online data delays patch approval workflows that depend on Microsoft's published severity ratings. Capacity planning suffers when administrators cannot see current role deployment trends or performance baselines. Compliance reporting gaps emerge when systems cannot verify they are receiving current security classification data, which creates audit risks in regulated industries.
Configuration and Resolution Steps
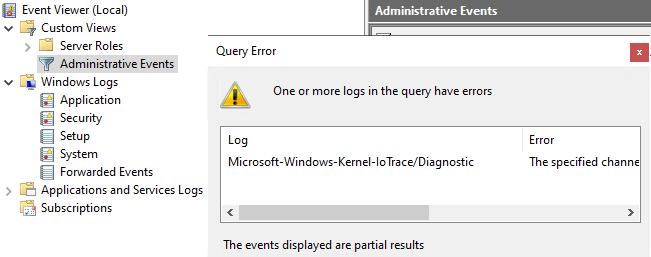
Resolving these failures involves a systematic approach to network configuration and server settings. Verify proxy settings using netsh winhttp commands to ensure they match organizational requirements. If a corporate proxy handles external traffic, explicitly configure it for Server Manager processes. Test connectivity to Microsoft endpoints from the affected servers using PowerShell cmdlets like Test-NetConnection to isolate network-level blocks.
Updating root certificates through Windows Update or manual import resolves many certificate validation failures. Ensure the Cryptographic Services and Windows Update services are running, as they handle certificate store maintenance and online connectivity respectively. Group Policy settings should be reviewed—Computer Configuration > Administrative Templates > Windows Components > Windows Update contains relevant policies that may interfere with Server Manager's background data collection.
Prevention and Monitoring

Preventing recurrence requires ongoing attention to network changes that affect server connectivity. Document all firewall exceptions and proxy configurations so they remain consistent across server builds. Centralized monitoring solutions can alert administrators to when Server Manager stops reaching online endpoints, catching problems before they accumulate into significant operational blind spots.