Every organization eventually faces a difficult decision: what to do with aging technology. When vendor support ends, the risks don't disappear—they multiply. End-of-life (EOL) systems represent one of the most underestimated cybersecurity threats facing modern enterprises, quietly accumulating technical debt while exposing critical infrastructure to exploitation.
The Hidden Danger of Unsupported Software
When a product reaches its end-of-life status, the manufacturer stops releasing security patches, bug fixes, and technical support. This creates a ticking time bomb for organizations still running these systems. Attackers actively scan for known vulnerabilities in EOL software, knowing that no patches will ever be released to fix them. The 2017 WannaCry ransomware attack exploited a vulnerability in Windows XP, an operating system that had already reached end-of-life, affecting hundreds of thousands of systems worldwide.
Why Organizations Delay Migration
Despite the obvious risks, many organizations continue running EOL systems for years. The reasons are often complex and interconnected:

- Cost constraints: Legacy systems may be deeply integrated into business processes, and migration requires significant investment
- Compatibility issues: Newer systems may not support critical applications or hardware dependencies
- Staff expertise: IT teams may lack skills to manage migration or maintain legacy environments
- Regulatory requirements: Some industries mandate specific software versions for compliance
Real-World Consequences
The impact of EOL vulnerabilities extends far beyond theoretical risk. In 2020, the SolarWinds attack demonstrated how supply chain vulnerabilities in outdated components could compromise entire networks. Organizations running unsupported operating systems, databases, or network equipment face exponentially higher breach costs. According to IBM's Cost of a Data Breach Report, organizations with extensive legacy infrastructure experience breach costs 28% higher than those with modernized environments.
Building a Proactive Strategy
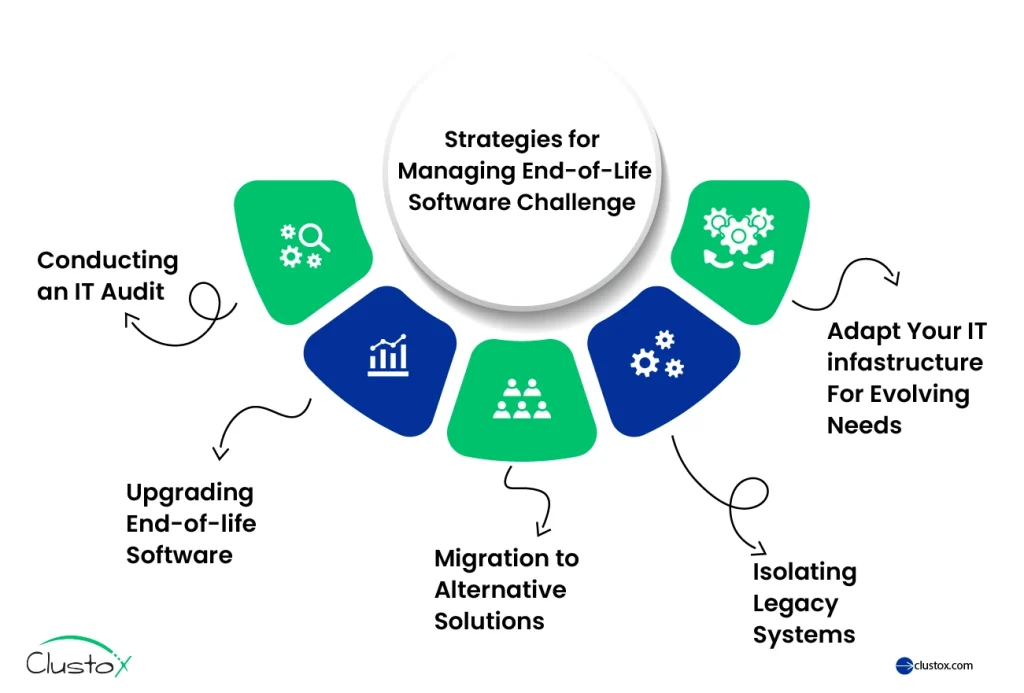
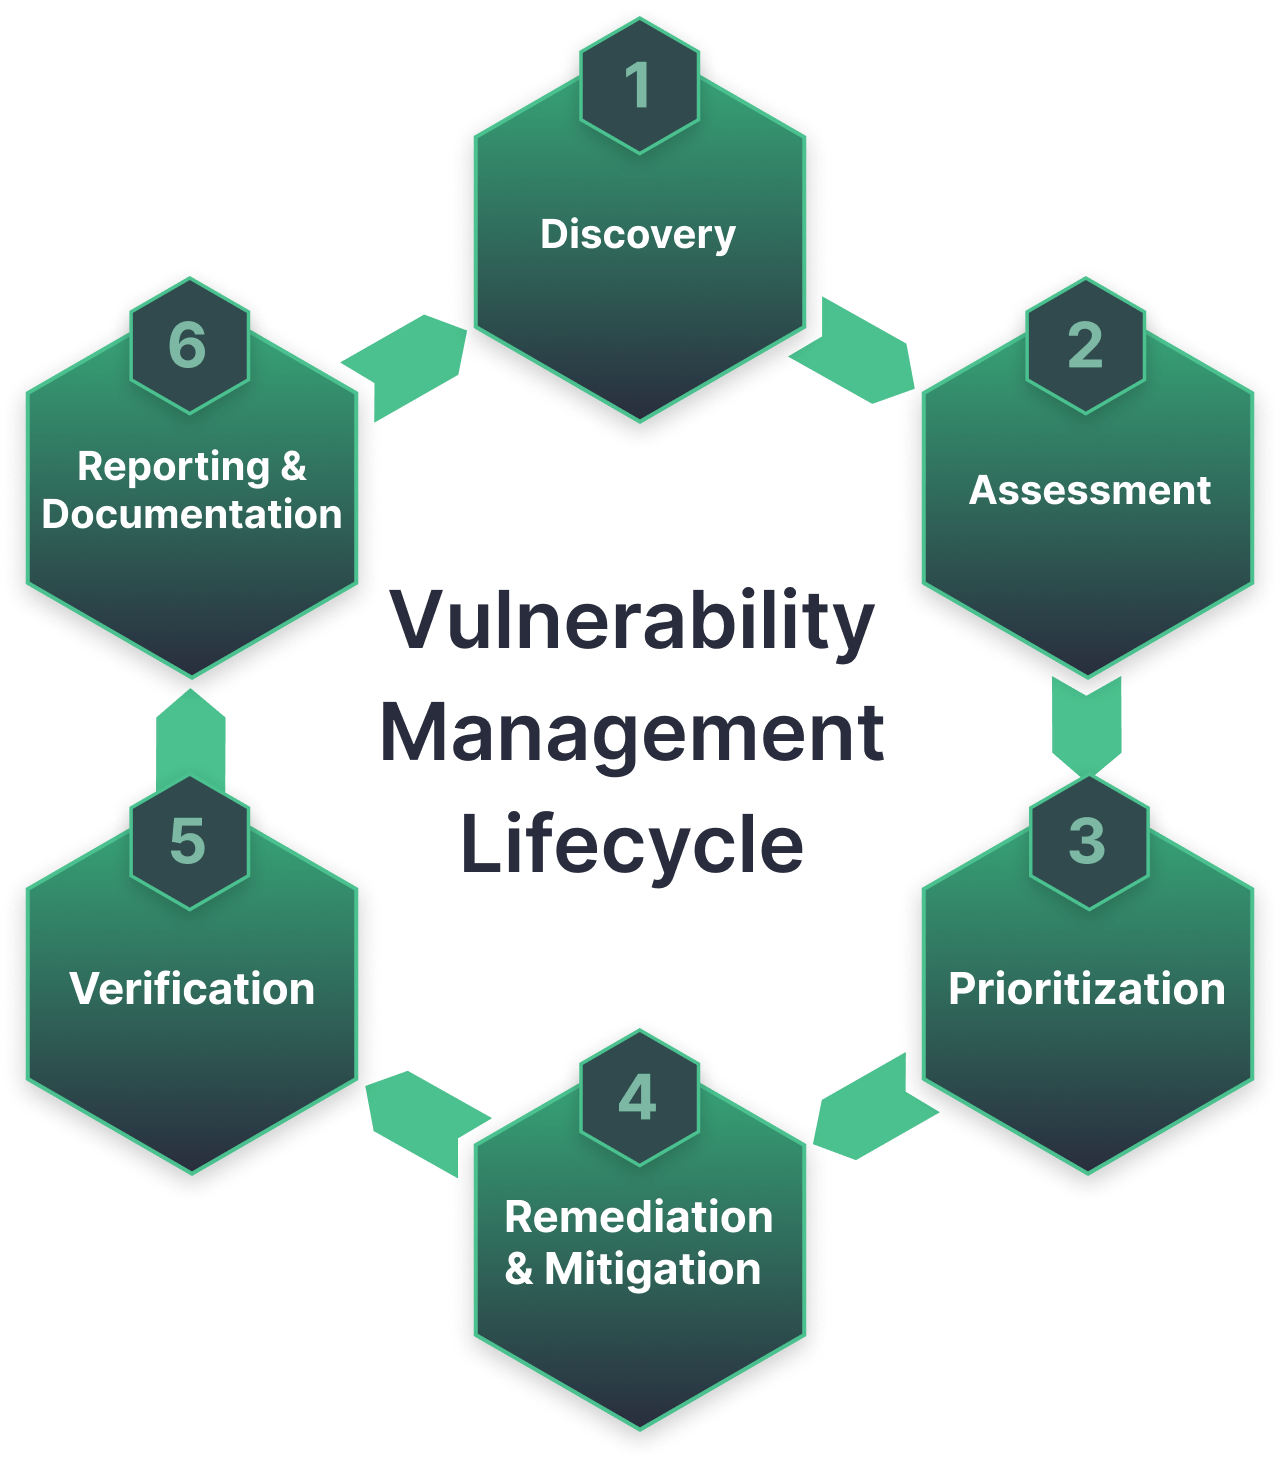
Addressing EOL risks requires systematic planning rather than reactive firefighting. Start with a comprehensive asset inventory to identify all systems approaching or past their end-of-life dates. Prioritize based on business criticality and exposure to external threats. For systems that cannot be immediately replaced, implement compensating controls:
- Network segmentation to isolate legacy systems
- Enhanced monitoring and logging
- Strict access controls and privilege management
- Virtual patching through intrusion prevention systems
Long-Term Modernization
While compensating controls provide temporary relief, they are not sustainable solutions. Organizations must develop multi-year modernization roadmaps that align technology refresh cycles with business objectives. Cloud migration, containerization, and infrastructure-as-code practices reduce dependency on specific hardware and software versions. The goal is to build resilience through continuous evolution rather than maintaining fragile legacy environments.

End-of-life systems represent more than technical debt—they represent strategic risk. Organizations that proactively address EOL vulnerabilities protect not just their infrastructure, but their reputation, customer trust, and competitive position. The cost of modernization is always less than the cost of a breach.






 End of Support (EOS) Risks in Cybersecurity/aseva-blog-EOLandEOSrisks-inline3.jpg?width=850&height=350&name=aseva-blog-EOLandEOSrisks-inline3.jpg)