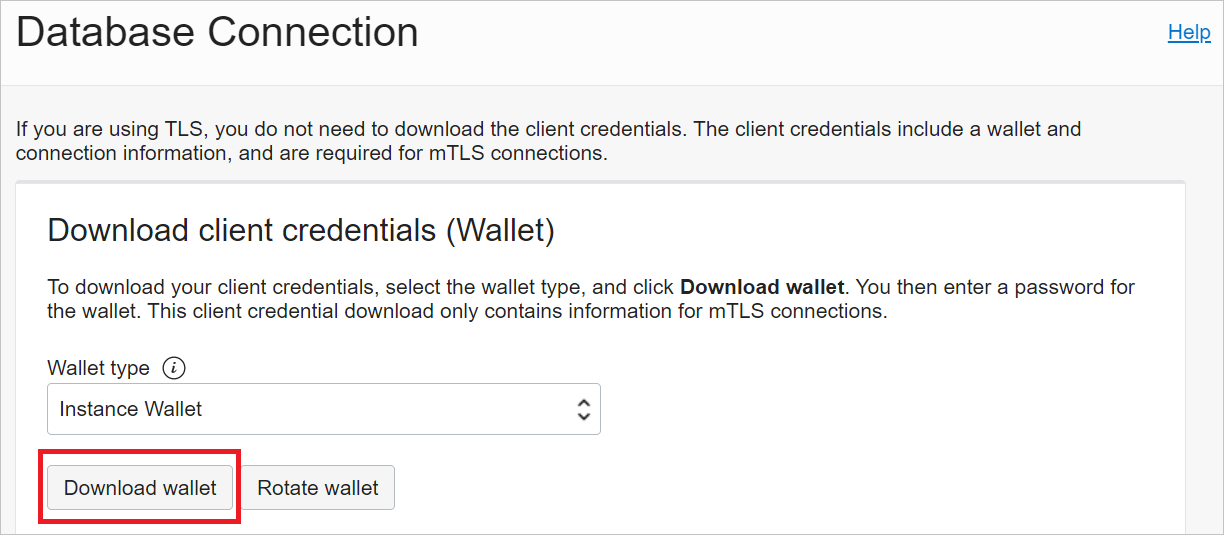
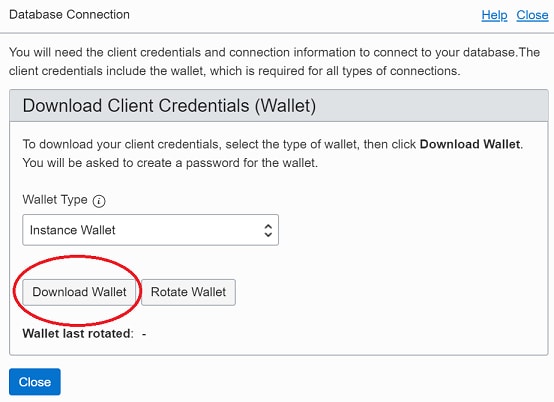
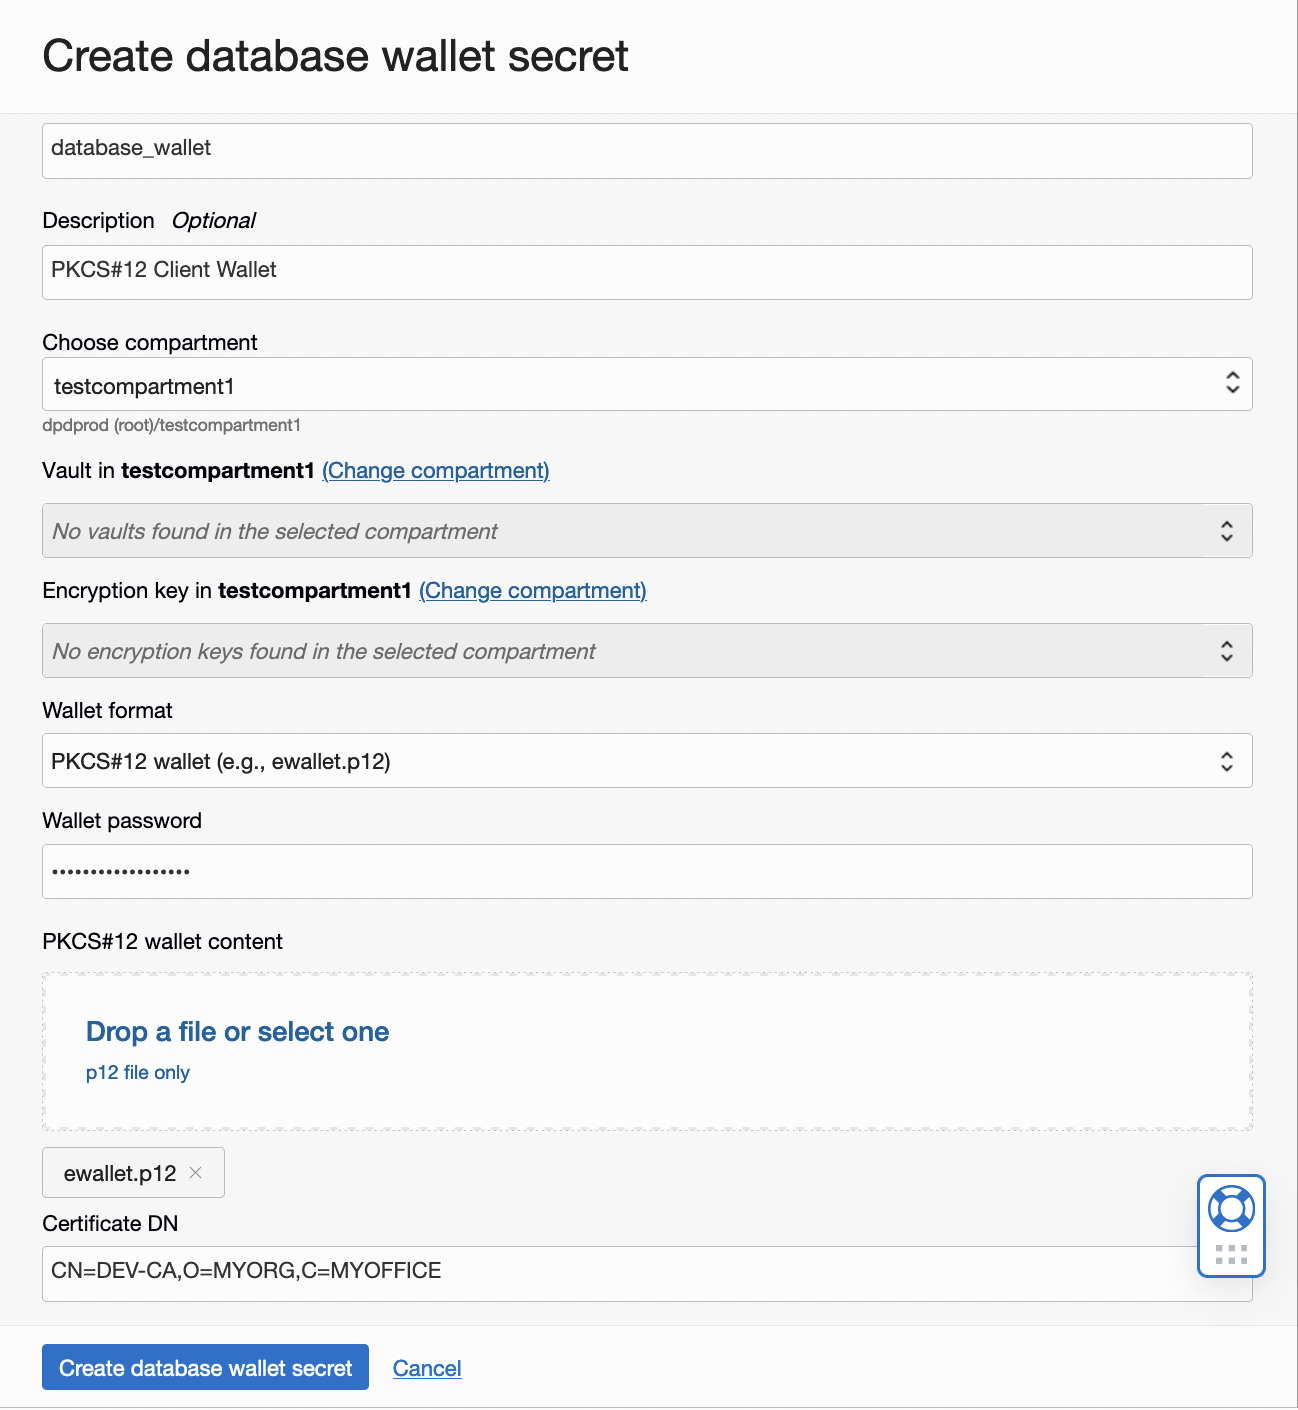
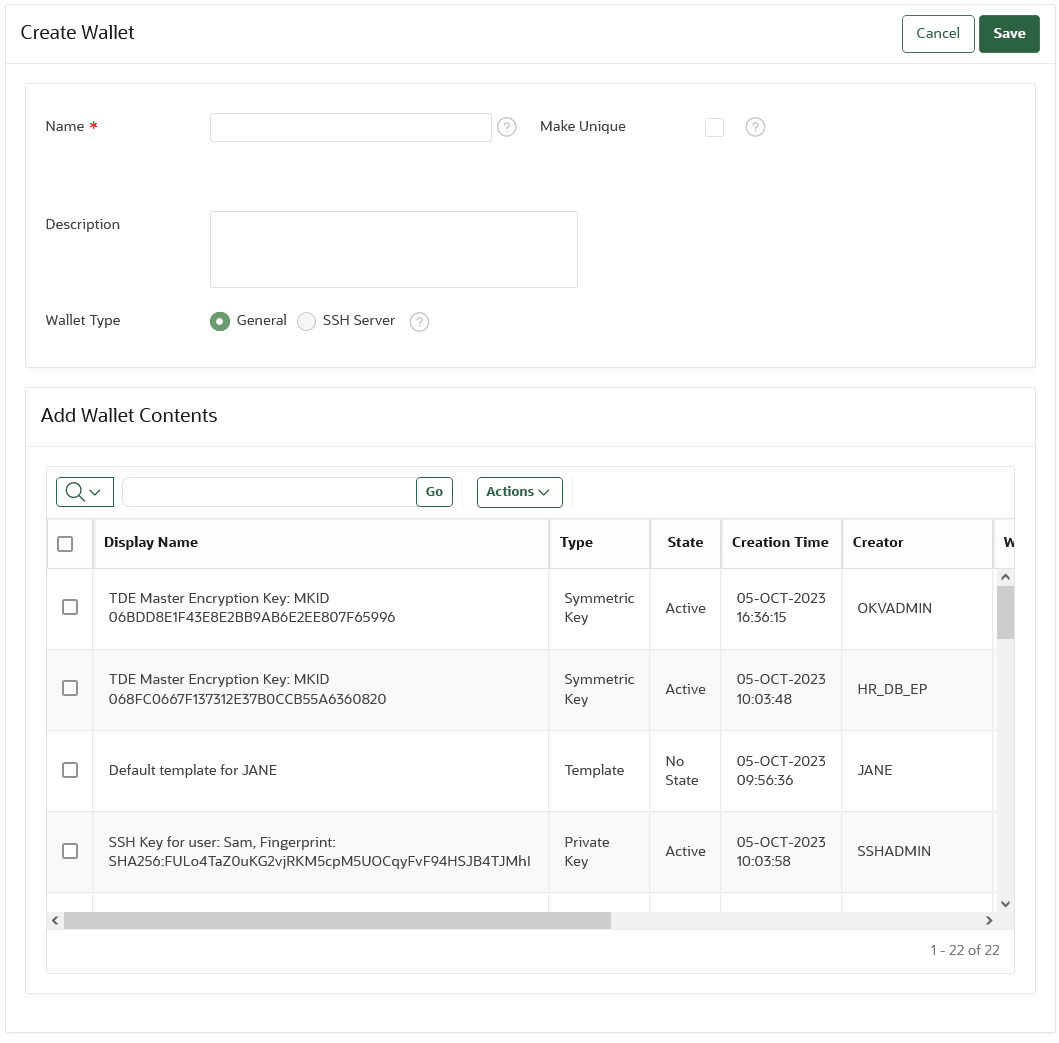
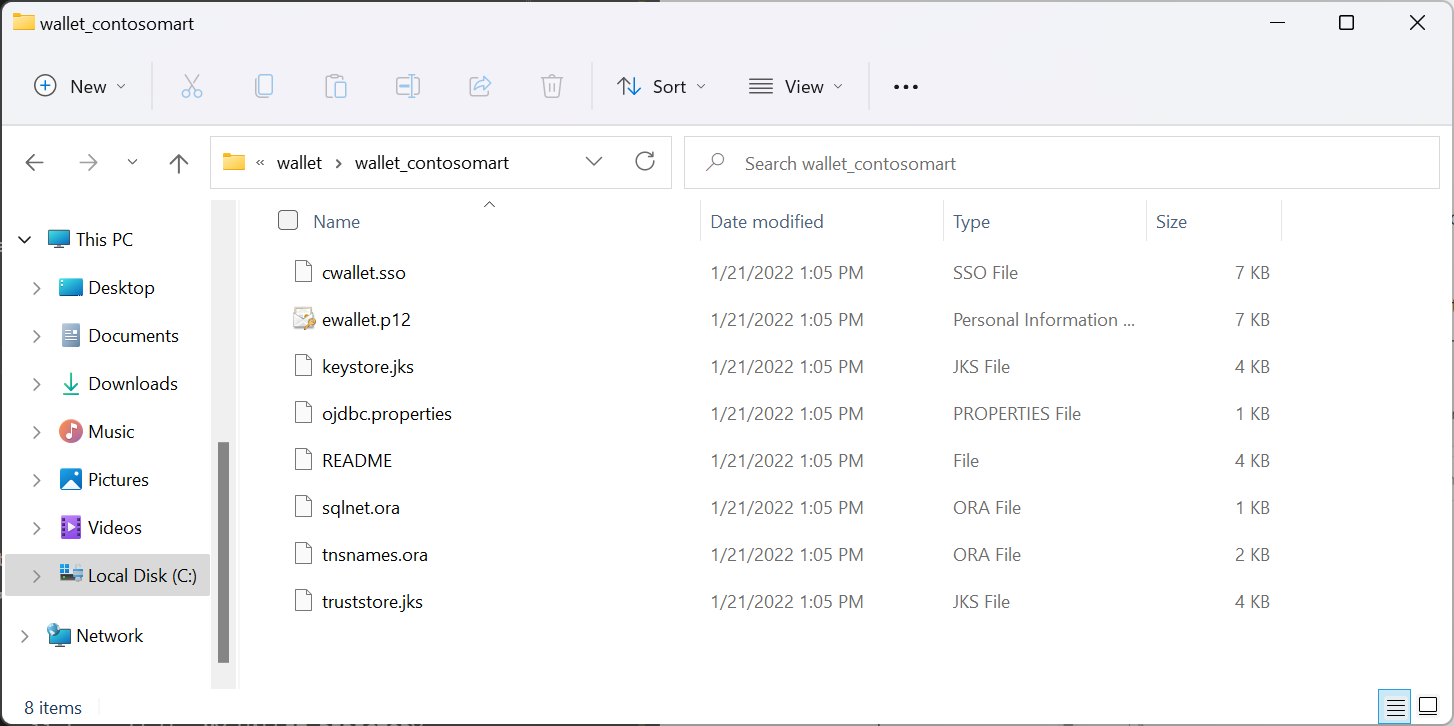
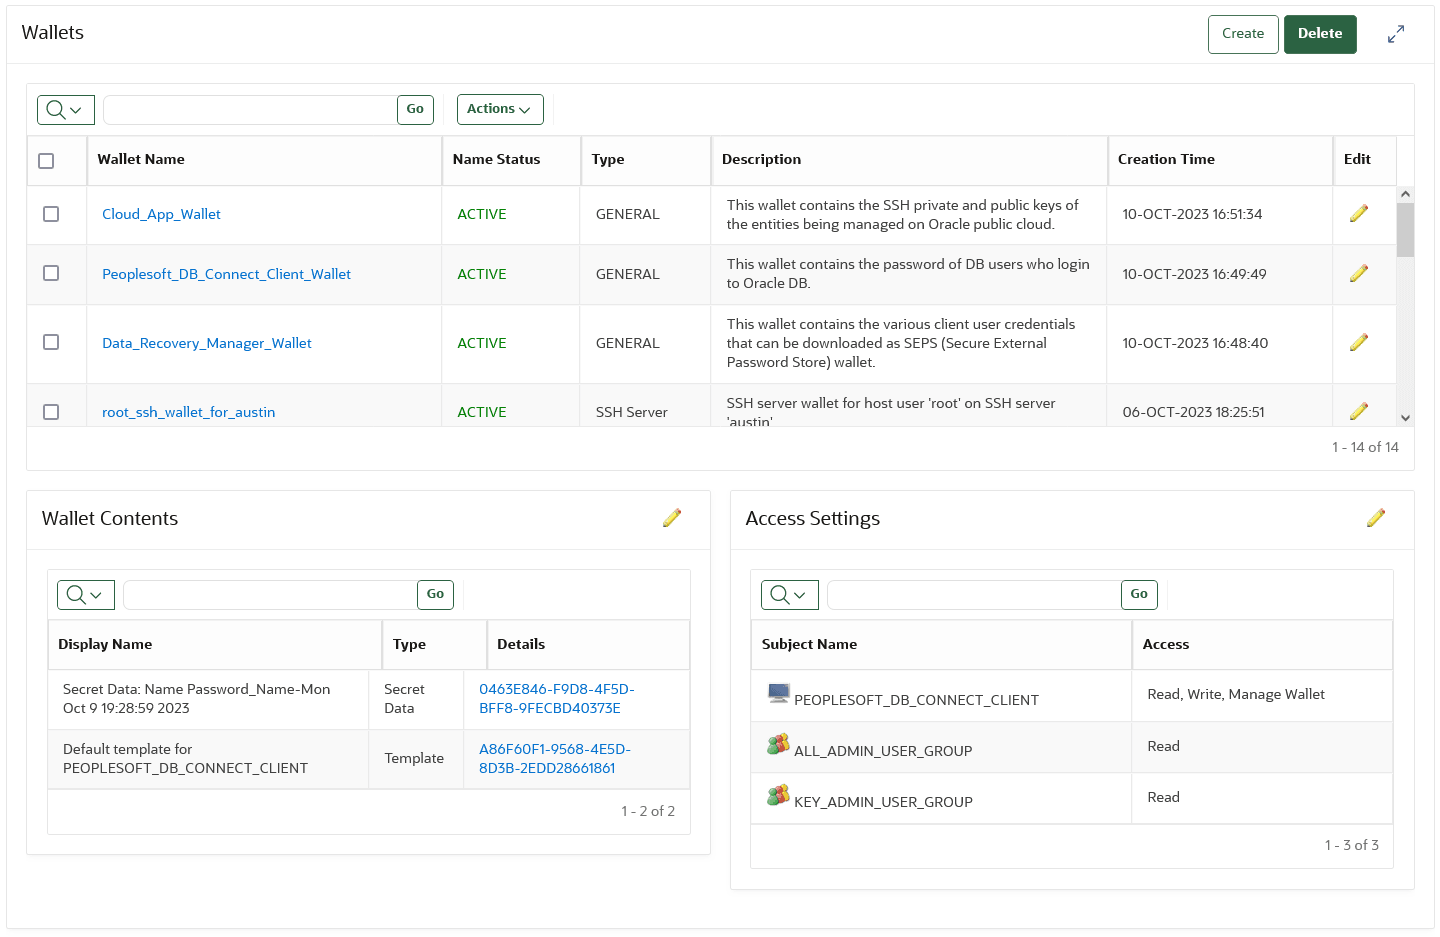
A database wallet is a secure, encrypted repository that stores the cryptographic keys and credentials required to manage access to a database management system. Unlike a physical wallet holding cash and cards, this digital solution safeguards the sensitive information necessary to authenticate users, encrypt data, and maintain the integrity of the entire database ecosystem.
How a Database Wallet Functions
At its core, a database wallet operates by centralizing the management of security credentials. Instead of scattering usernames and passwords across configuration files or script headers, the wallet provides a single, fortified location for this data. When an application needs to connect to the database, it requests a specific credential from the wallet, which authenticates the request and delivers the necessary keys or passwords programmatically.
Core Components and Architecture
The structure of a database wallet is typically modular, consisting of several distinct elements that work in concert to ensure security and usability. The following table outlines the primary components found in most enterprise-grade wallet systems:

| Component | Description |
|---|---|
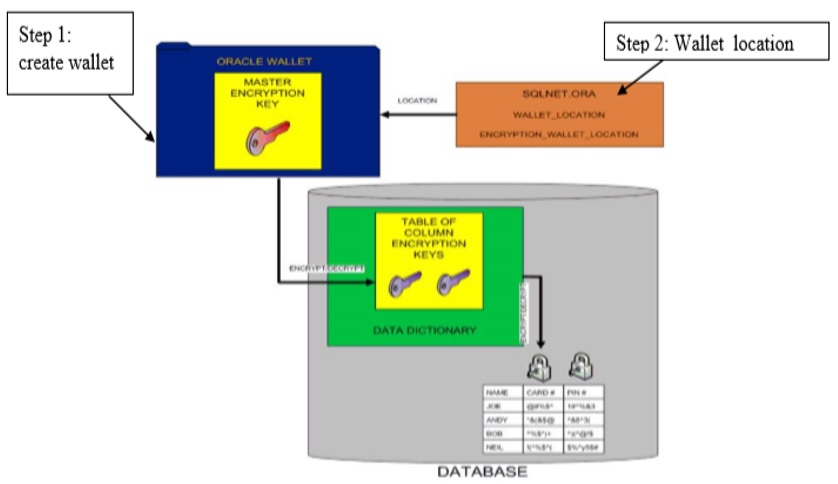
| Master Key | The primary encryption key used to protect the contents of the wallet. This key is often derived from a user password or stored in a hardware security module (HSM). |
| Credentials Store | The secure segment where database usernames, passwords, and SSL certificates are kept in an encrypted format. |
| Authentication Layer | The mechanism that verifies the identity of the application or user attempting to access the stored secrets. |
Integration with Development Workflows
Modern development practices, particularly those adhering to DevOps and CI/CD pipelines, benefit significantly from the database wallet. By integrating the wallet into the build process, developers can eliminate hard-coded secrets within their source code. This integration ensures that environment-specific credentials are pulled securely at runtime, drastically reducing the risk of accidental exposure through version control systems like Git.
Security and Compliance Advantages
For organizations operating under strict regulatory frameworks such as GDPR, HIPAA, or PCI-DSS, the database wallet is not merely a convenience but a compliance necessity. These regulations mandate strict controls over sensitive data, and the wallet provides an auditable trail of access and usage. Security teams can leverage the wallet to enforce the principle of least privilege, ensuring that applications only receive the minimal access required to perform their specific tasks.
Mitigating Insider and External Threats
Cybersecurity threats evolve daily, with attackers constantly寻找新的漏洞。数据库钱包通过加密静态数据(数据 at rest)来对抗这些威胁。即使攻击者设法访问了服务器文件,他们看到的也只是无法破解的加密字符串。此外,钱包的集中式日志记录功能可以追踪谁在何时访问了特定的密钥,这对于调查潜在的安全事件至关重要。
Implementation Best Practices
To maximize the effectiveness of a database wallet, implementation must follow strict best practices. Key management is the most critical aspect; the master key must be stored separately from the data it protects and rotated regularly. Furthermore, access to the wallet should be restricted to authorized services only, utilizing network segmentation and firewall rules to create a robust security perimeter.
The Role of Automation
While security is paramount, the usability of the database wallet cannot be overlooked. Leading solutions offer robust APIs and command-line interfaces that allow for automated credential retrieval. This automation ensures that database connections remain seamless and uninterrupted, allowing security to scale without hindering operational efficiency.