s3 The Provided Token Has Expired: Causes, Remedies, and Preventions

Error messages from AWS S3 can be cryptic and frustrating, leaving users wondering how to resolve the issue. The "s3 the provided token has expired" error is one such message that might appear when trying to access an S3 bucket or perform a specific action. In this article, we will delve into the causes of this error, explore available remedies, and discuss prevention strategies to minimize future occurrences.
Causes of the "s3 the provided token has expired" Error
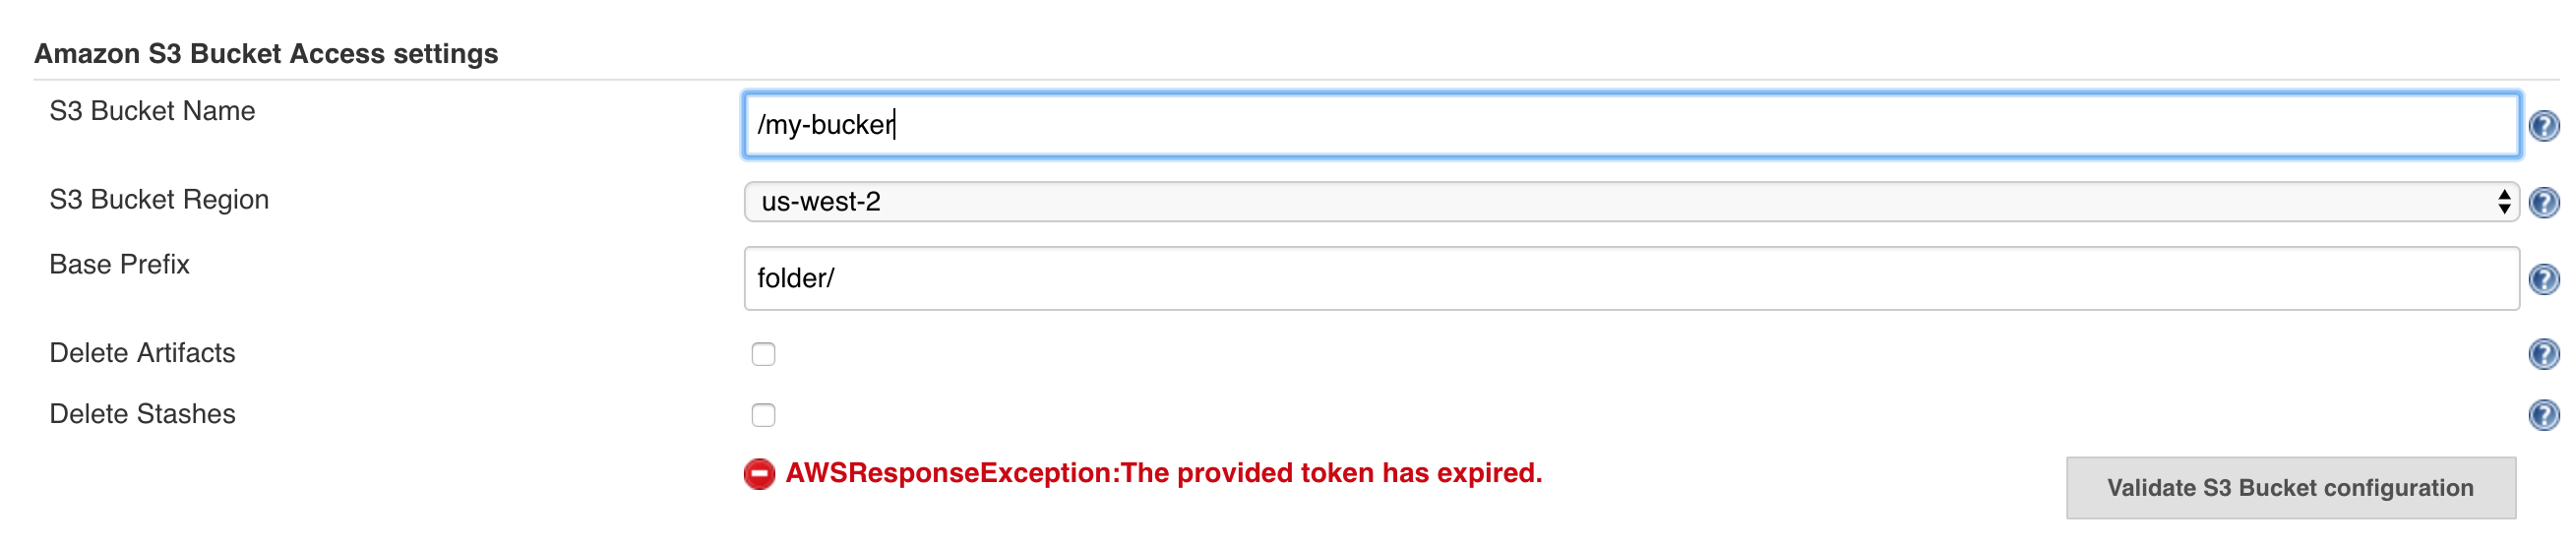
The "s3 the provided token has expired" error typically results from an expired short-term security token used for authentication purposes. AWS S3 uses security tokens to authenticate and authorize users, ensuring that only authorized personnel have access to sensitive resources. There are several reasons why a security token may expire, including:
- Token timeout**: Short-term security tokens have a limited lifespan (typically 15 minutes) and may expire after a certain period of inactivity.
- Token revocation**: When a security token is revoked due to security concerns, password changes, or incorrect usage, it becomes invalid.
- Token caching issues**: Incorrectly cached tokens or issues with token caching mechanisms can lead to expired tokens.
Remedies for the "s3 the provided token has expired" Error

To resolve the "s3 the provided token has expired" error, follow the steps outlined below:
Method 1: Refreshing the security token
When dealing with expired tokens, the most straightforward solution is to obtain a new security token. You can do this by:

- Accessing the AWS Management Console and navigating to your account settings or identity provider.
- Refreshing or re-obtaining the security token from the AWS CloudFormation console or other AWS services.
Method 2: Changing the token expiration time
As an alternative to refreshing the token, you can try adjusting the token expiration time to a longer duration. To do this:
- Navigate to the AWS Management Console and access the AWS IAM console.
- Search for and select the IAM user or role associated with the expired token.
- Update the token expiration time to a longer duration.
Prevention Strategies




While resolving the "s3 the provided token has expired" error is essential, preventing it in the first place can save you time and effort in the long run. Here are some prevention strategies:
1. Implement a token rotation policy**: Regularly rotate security tokens to prevent token expiration and reduce the risk of unauthorized access.
2. Monitor token usage and activity**: Keep a close eye on token usage and activity to identify potential security risks or issues.
3. Use AWS Cognito or other authentication services**: Consider using AWS Cognito or other authentication services that can manage and refresh security tokens automatically.
4. Update IAM user information and access policies**: Regularly update IAM user information, access policies, and permissions to ensure that tokens are associated with the correct resources and permissions.
By understanding the causes of the "s3 the provided token has expired" error, implementing the provided remedies, and adopting prevention strategies, you can minimize the occurrence of this error and ensure smooth operation of your AWS S3 resources.
When working with AWS S3, it's essential to be prepared for unexpected errors like the "s3 the provided token has expired" error. Regularly checking token expiration, refreshing tokens, and implementing prevention strategies can save you and your team countless hours of troubleshooting and minimize the risk of security breaches.