OWASP Secure Coding Practices
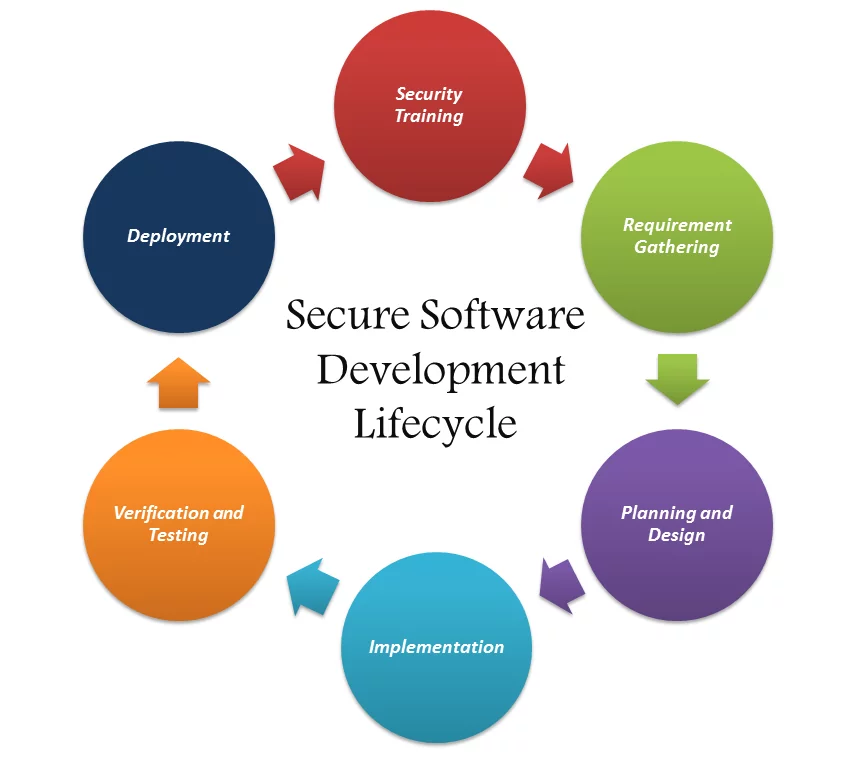
Introduction This technology agnostic document defines a set of general software security coding practices , in a checklist format, that can be integrated into the software development lifecycle. Implementation of these practices will mitigate most common software vulnerabilities. Generally, it is much less expensive to build secure software than to correct security issues after the software ...
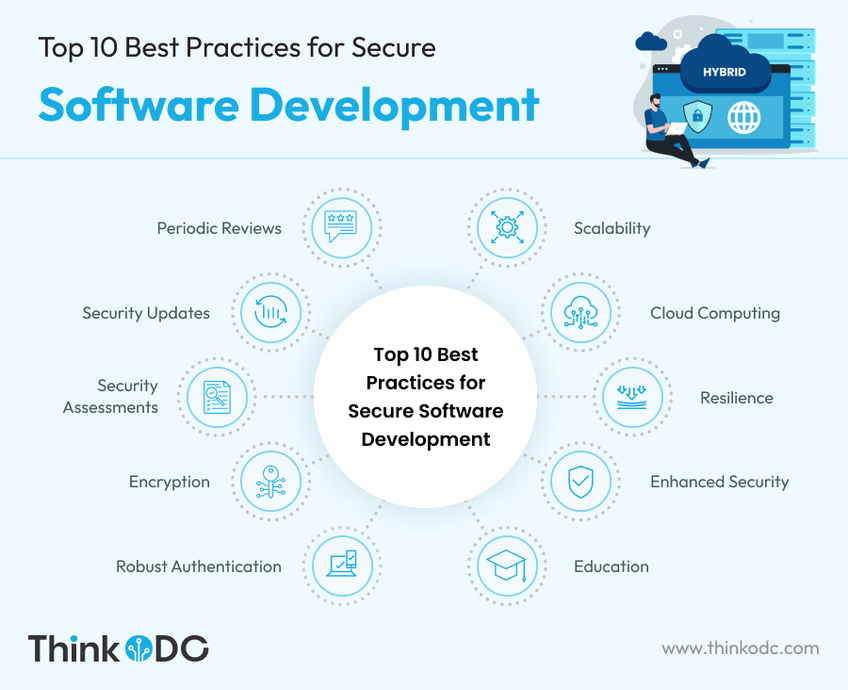
Most web application vulnerabilities are not discovered during a penetration test — they are built in during development . This guide covers ten security practices that every development team should implement from the start, not bolt on at the end.
The use of secure -by-design and secure -by-default principles, memory-safe programming languages (such as C#, Go, Java, Ruby, Rust and Swift), and secure programming practices (supported by agile software development practices , threat modelling and mitigation of common security risks) is an important part of secure software design and development .
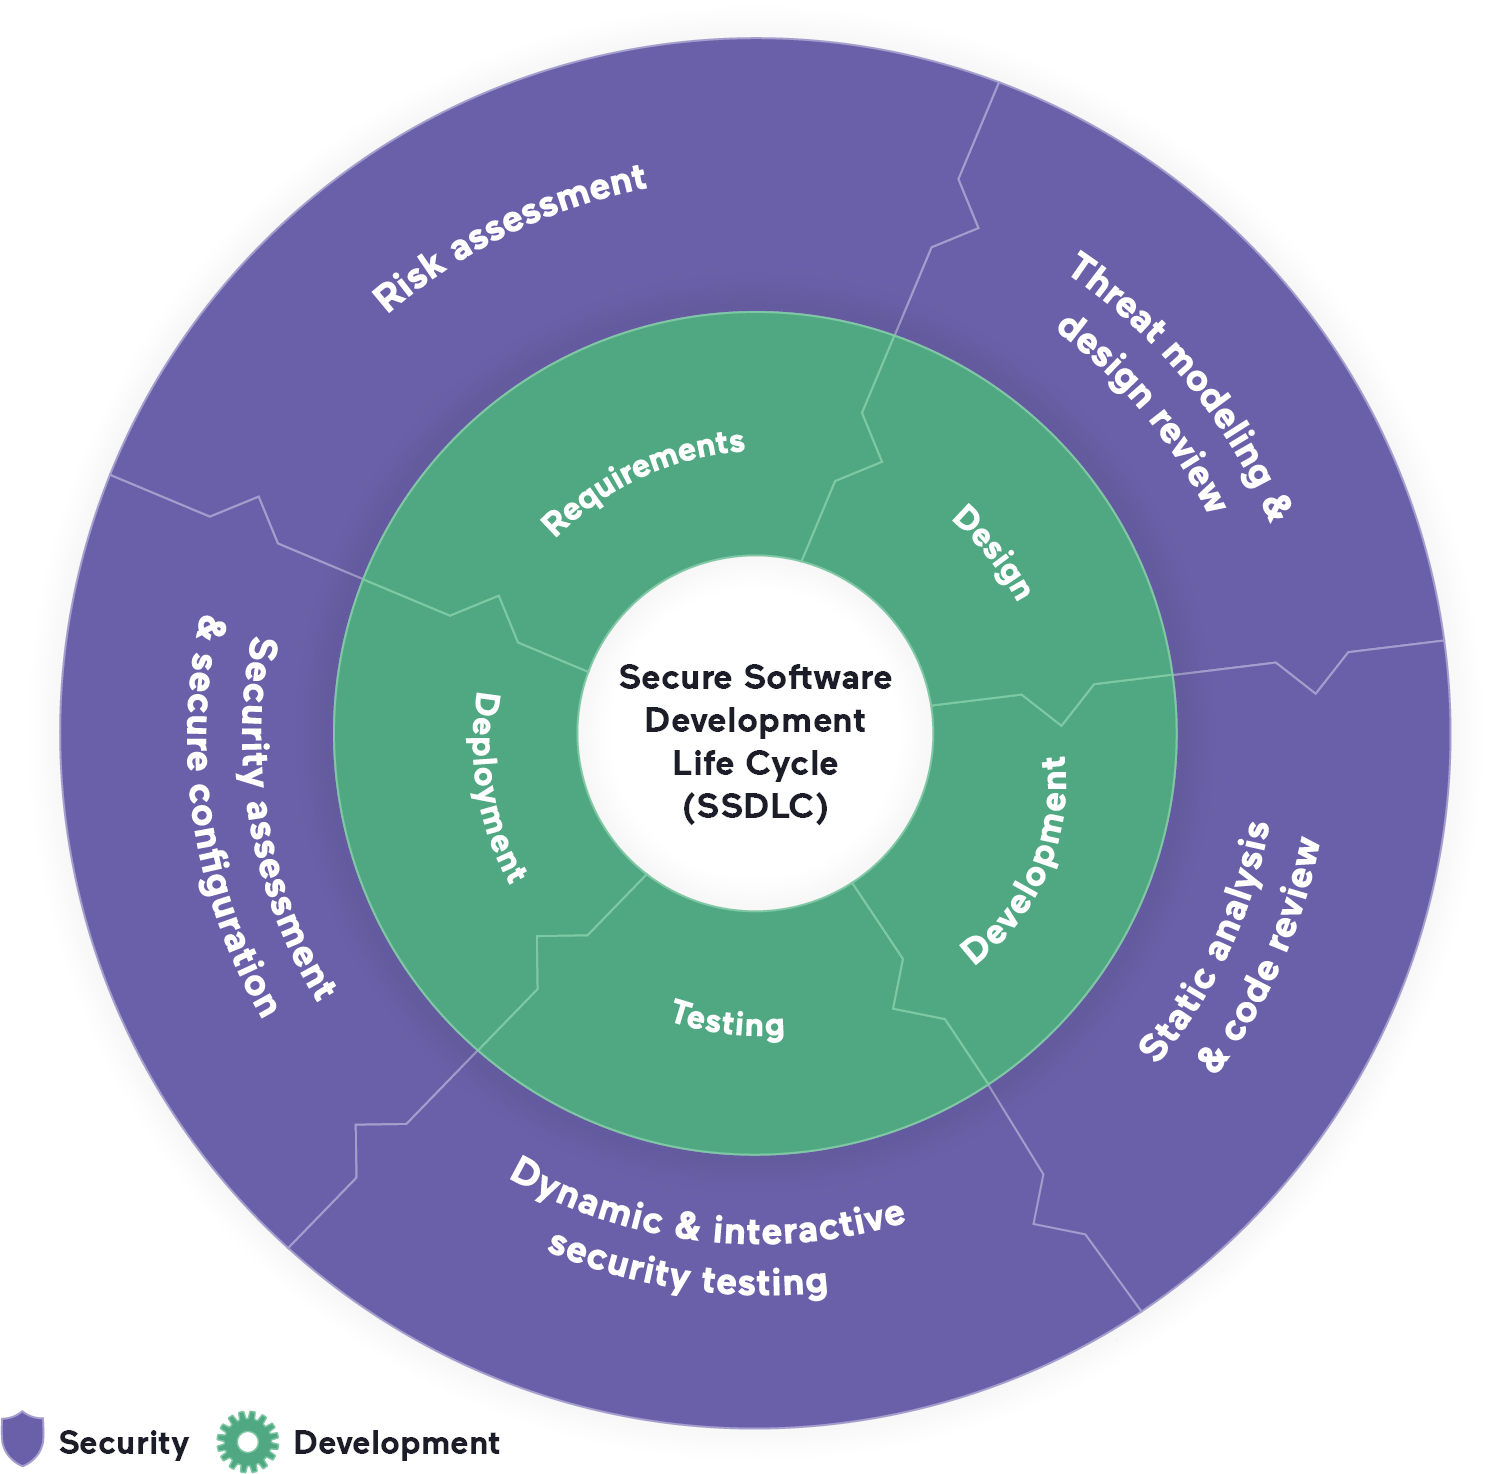
Secure Software Development, Security, and Operations (DevSecOps) Practices
Secure Software Development , Security, and Operations (DevSecOps) Practices View page source

Moving forward, it's essential to keep these visual contexts in mind when discussing Secure Online Development Practices.
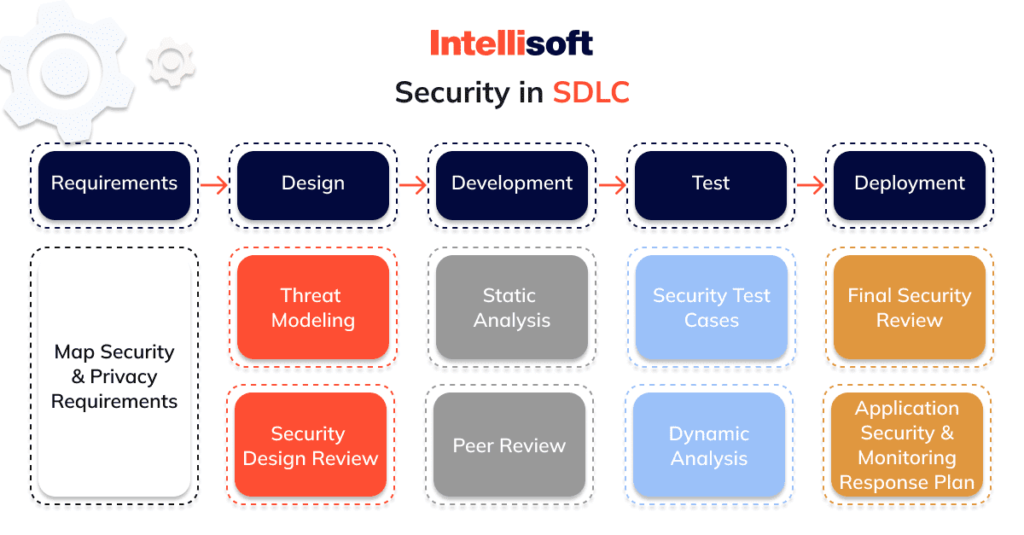
Master secure application development by integrating security in SDLC, fostering a security-first culture, and implementing robust controls. Click now!
Secure Software Development, Security, and Operations (DevSecOps) Practices
Today's software applications are typically constructed by combining a diverse range of elements, including components, frameworks, libraries, and tools. Rather than building everything from the ground up, developers often leverage a mix of internally developed and externally sourced components. This modular development approach, coupled with Development Operations (DevOps) practices that ...
Using best practices for security as part of development is the first step in protecting against these attacks. So, by including security to developments in the early stages of deployment and building applications that are "self-defensive", developers can design apps which are responsive towards external threats as well secure ...
Guidelines for software development

This section describes the controls applicable to mobile application development and extends upon the 'Software development fundamentals' section of these guidelines. Secure mobile application development OWASP provides comprehensive resources for software developers that should be followed when developing mobile applications.
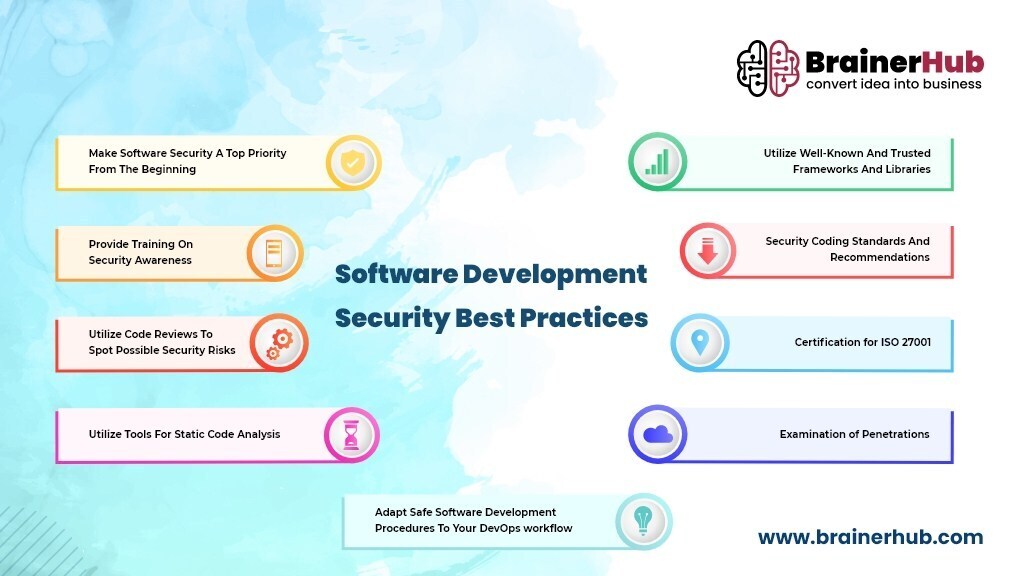
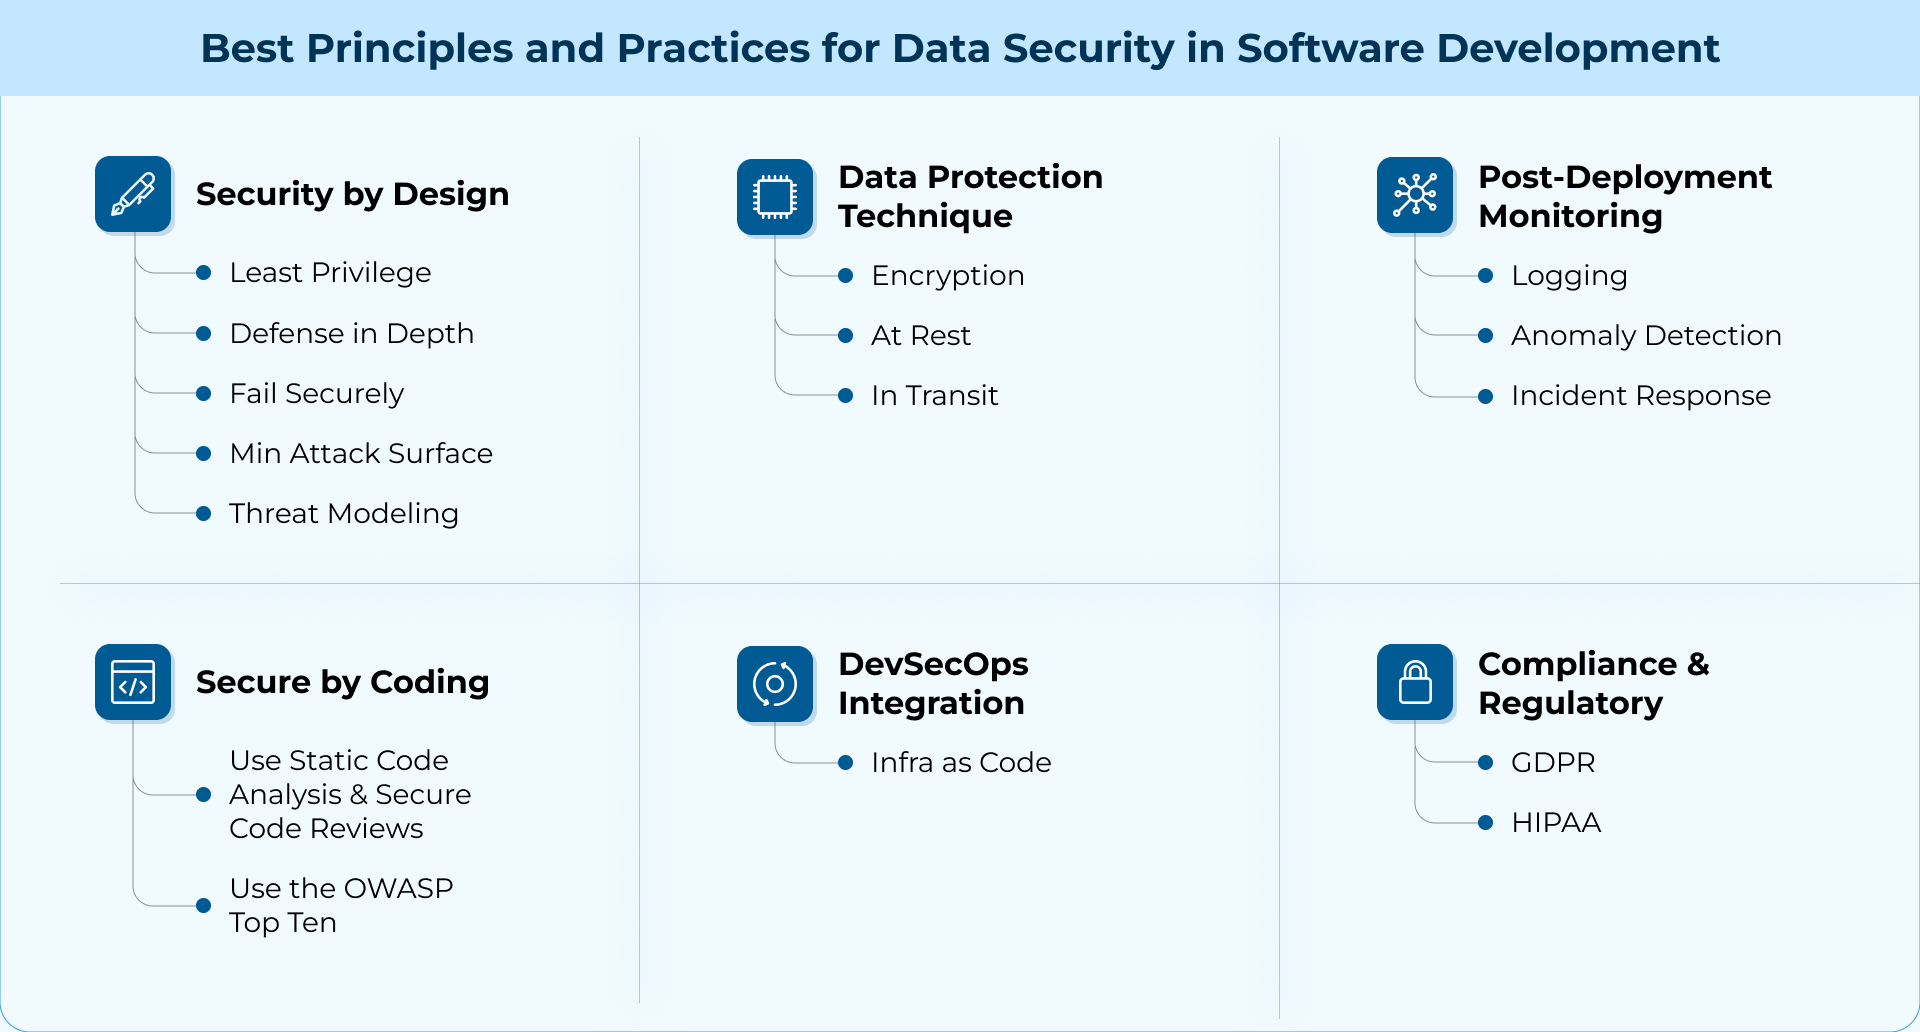
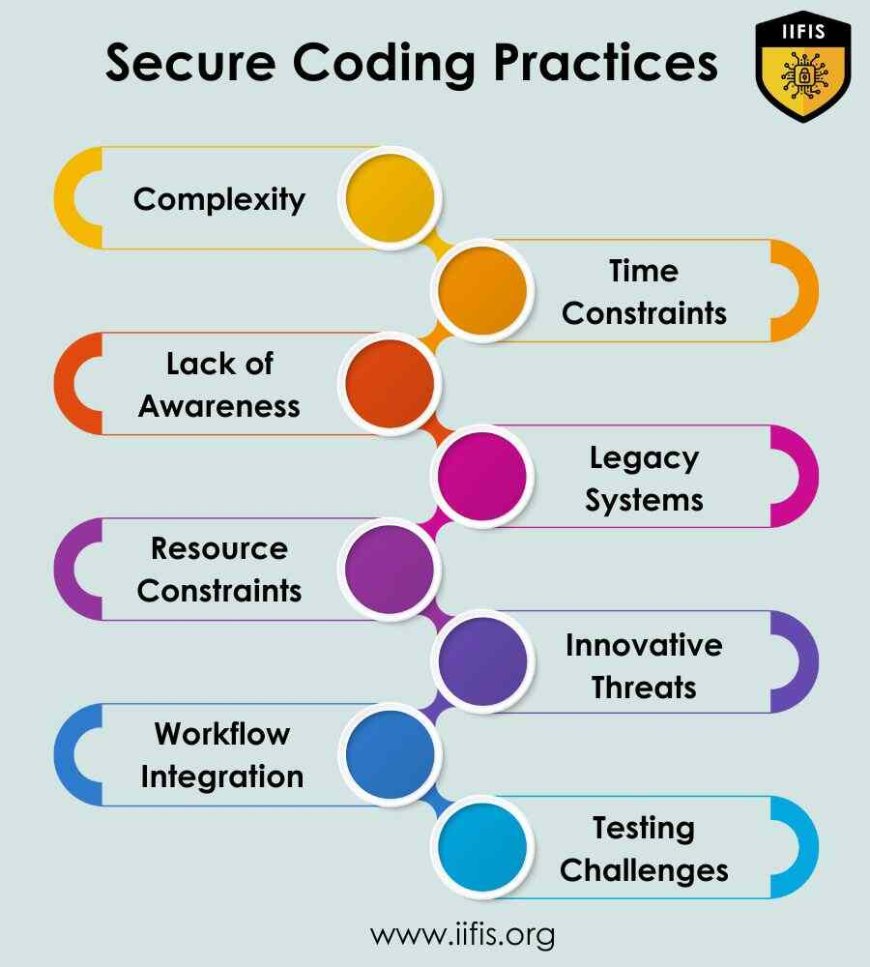
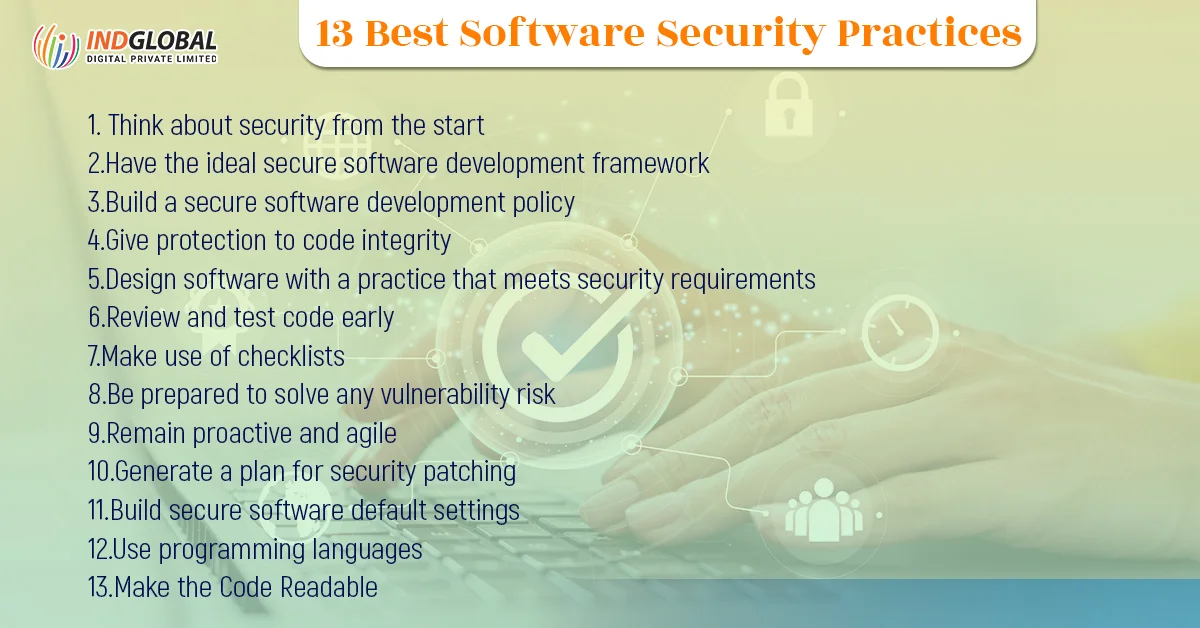
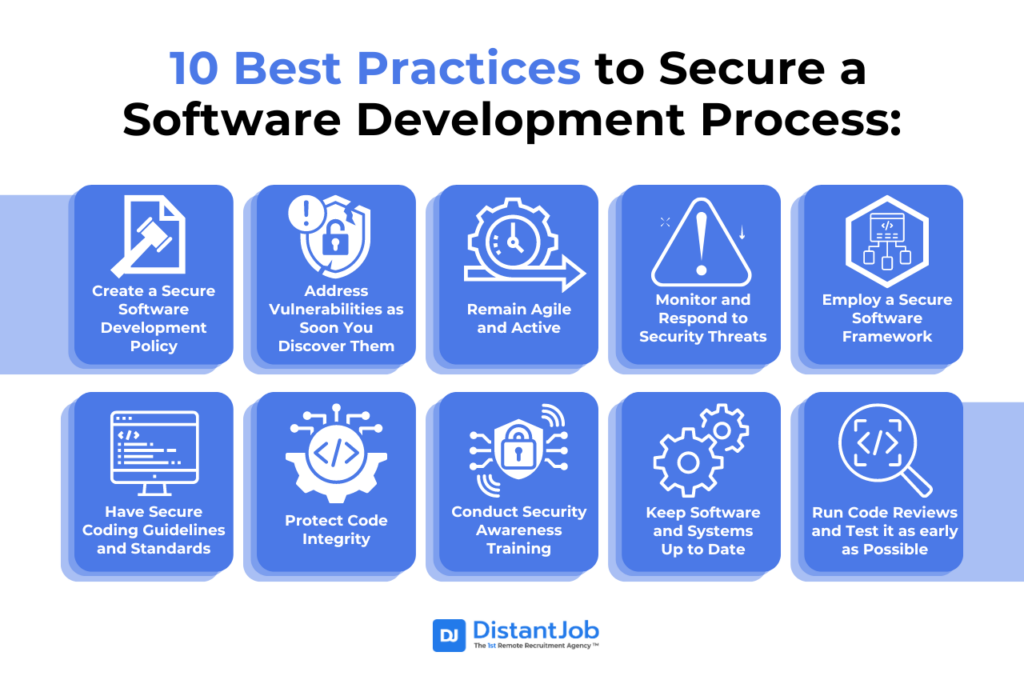
Best practices for secure coding include input validation, output encoding, least privilege access, secure authentication, code reviews, and threat modeling.
Useful Notes on Secure Online Development Practices
Find a Cyber Security Course that Suits You at CourseFinder. Find a course amongst 500+ online courses from leading Australian universities and TAFEs
More Context About Secure Online Development Practices
Sdlc Best Practices. For Secure Online Development Practices, this point helps readers notice the most relevant visual details before moving into the gallery.
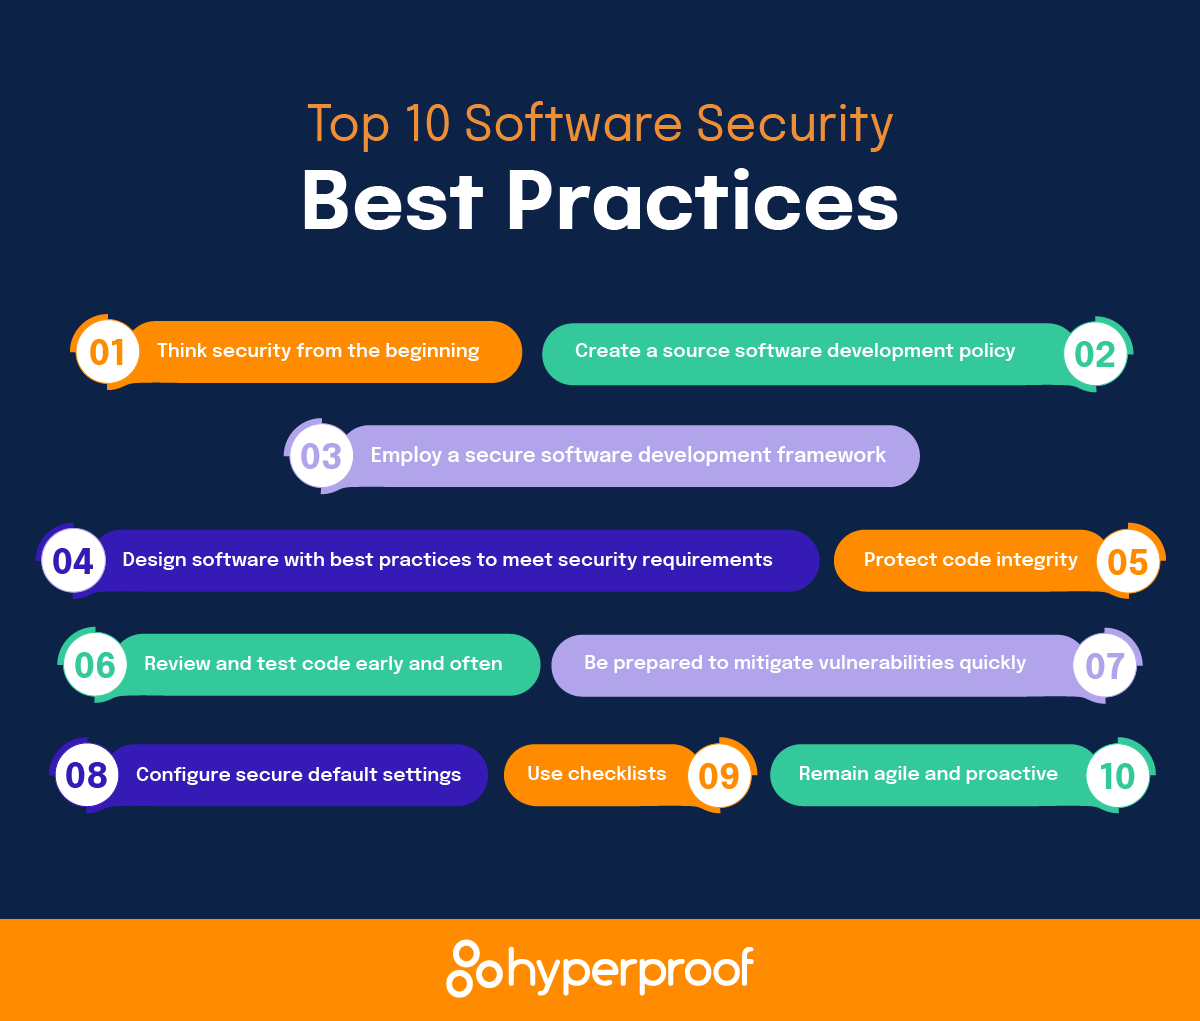
Secure Software Development | Hyperproof | [Best Practices]. This note connects the source idea with the visuals in a simple, reader-friendly way.
Secure Software Development Best Practices, Checklist and Risks. The extra context helps the page feel more useful without forcing the same phrase repeatedly.