Rotate the client secret of the SSO application Unity Cloud Unity Docs
To enable single sign-on ( SSO ) with Unity Virtual Private Cloud , the recommended practice is to establish a procedure to rotate the client secret of the application that you have created in the enterprise identity provider (IdP). For Microsoft Entra ID, the maximum secret lifetime is two years, so you must handle its expiration anyway.
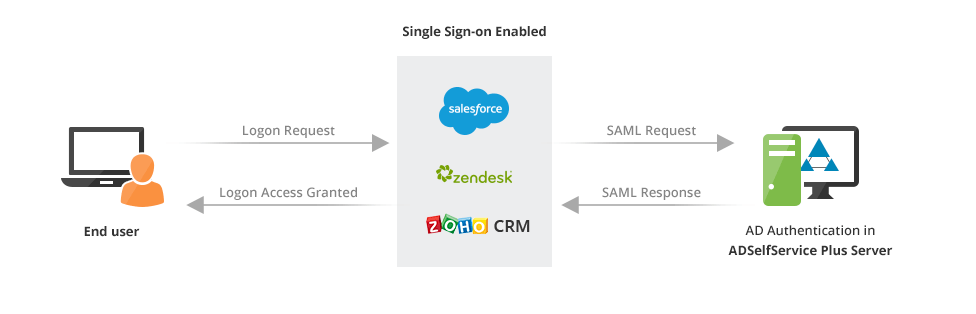
To enable single sign-on ( SSO ) with Self-Hosted Deployment, the recommended practice is to establish a procedure to rotate the client secret of the application that you have created in the enterprise identity provider (IdP). For Microsoft Entra ID, the maximum secret lifetime is two years, so you must handle its expiration anyway.
Search Page
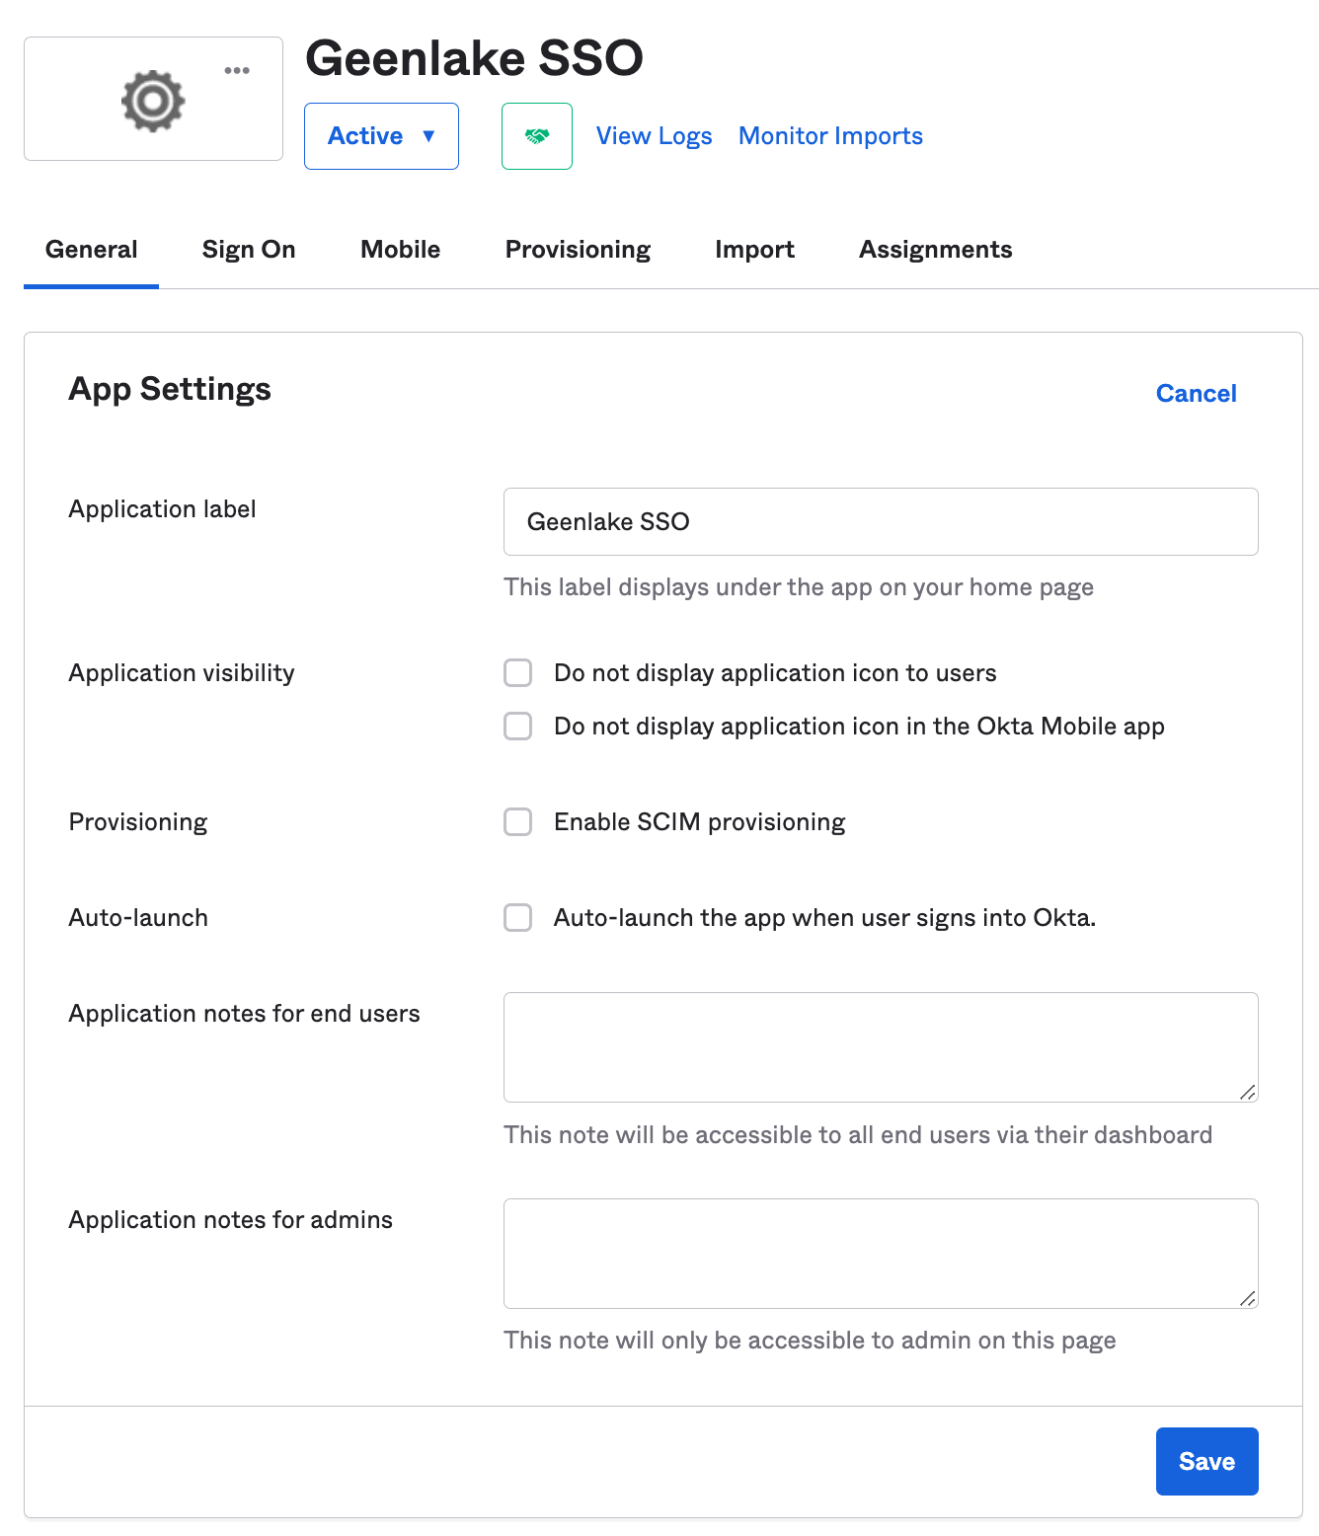
Rotate the client secret of the SSO application ... To enable single sign-on ( SSO ) with Unity Virtual Private Cloud , the recommended practice is to establish a procedure to rotate the client ...
To maintain security of the solution perform these tasks regularly: 1. Rotate the client secret of the SSO application

Rotate Client Secrets
Learn how to rotate an application's client secret using the Auth Dashboard or the Management API.
Overview Streamline the management of users in Self-Hosted Deployment with single sign-on ( SSO ) and just-in-time (JIT) user provisioning. Self-Hosted Deployment implements SSO through an enterprise identity provider (IdP) using the OpenID Connect (OIDC) protocol. You can use any OIDC-compliant IdP. Just-in-time provisioning Keycloak's JIT provisioning mechanism provides these automated ...
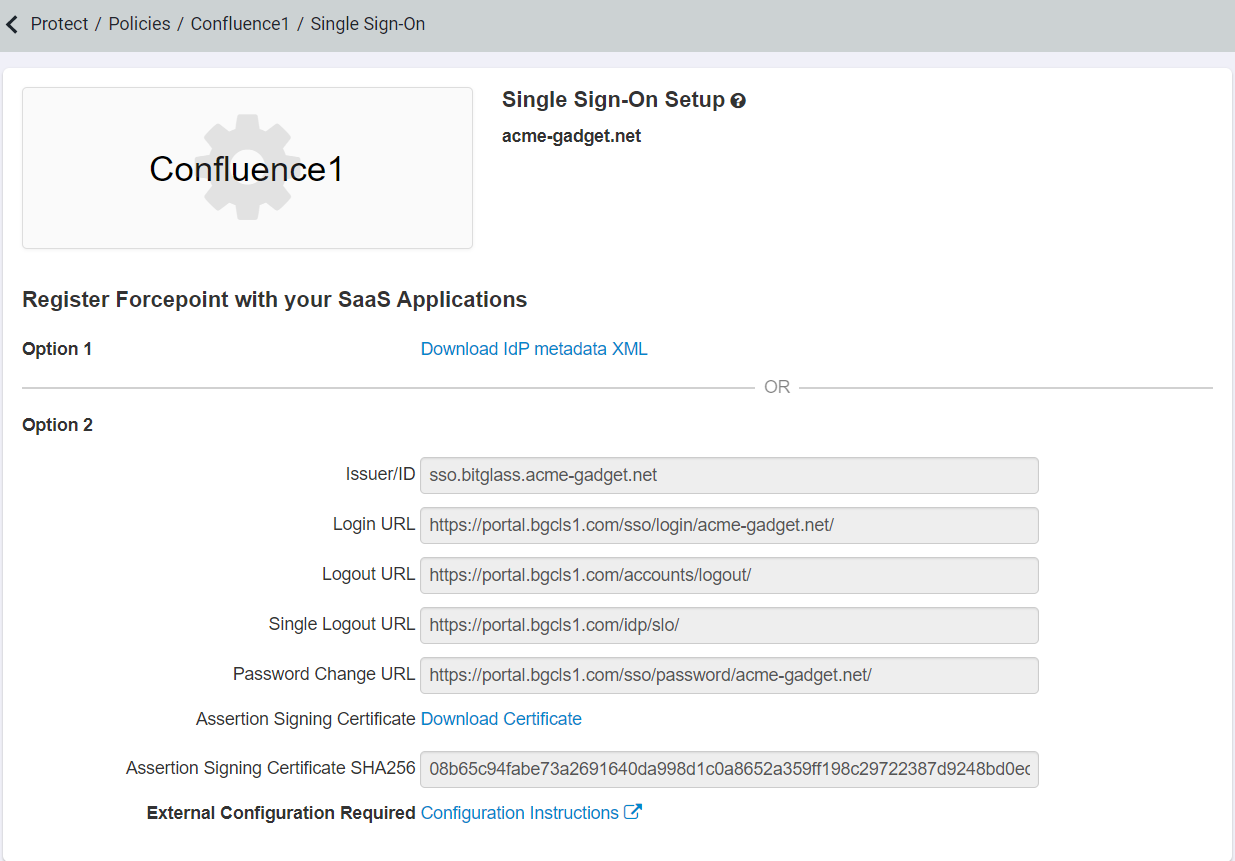
How to proactively rotate or automate the secrets rotation for the ...
As per my understanding, you wanted to know the best practice to avoid performing manual rotation of the client secret values. Unfortunately, we cannot automatically renew a client secret for an app registration and admin should manually create a secret before expiration and update it in the application server.
Azure side is now completed. Cisco Unity Configuration Login to your Cisco Unity Connection admin page. Select Unified Messaging > Unified Messaging Services. Click on your service and selected edit. Change the web based authentication option to OAuth2 and configure the settings: Application Client ID, Client Secret and Directory ID.
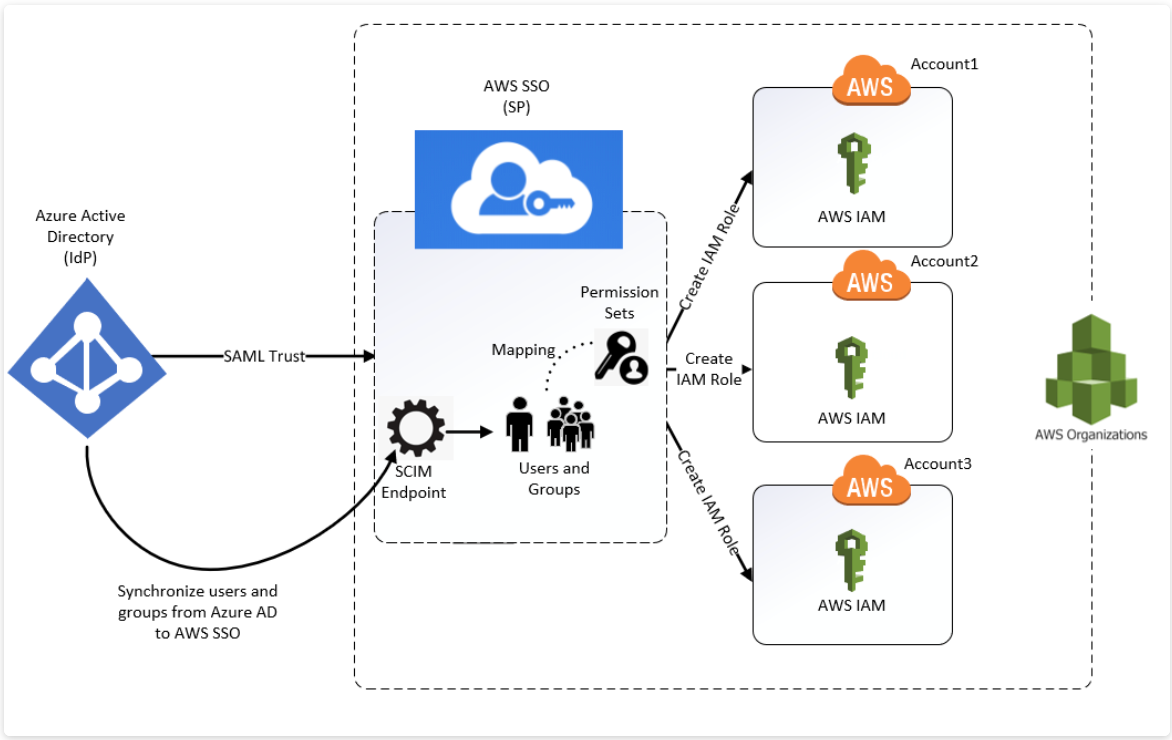
Secrets Rotation
Secret rotation is the process of refreshing the secrets that are used by the application . The best way to authenticate to Azure services is by using a managed identity, but there are some scenarios where that isn't an option. In those cases, access keys or secrets are used. You should periodically rotate access keys or secrets . Why Secrets ...



Unity Services Authentication SDK This package provides services for player authenticaton, unity player accounts and server authentication for Unity Gaming Services.