Secure SSO for cloud access using existing on
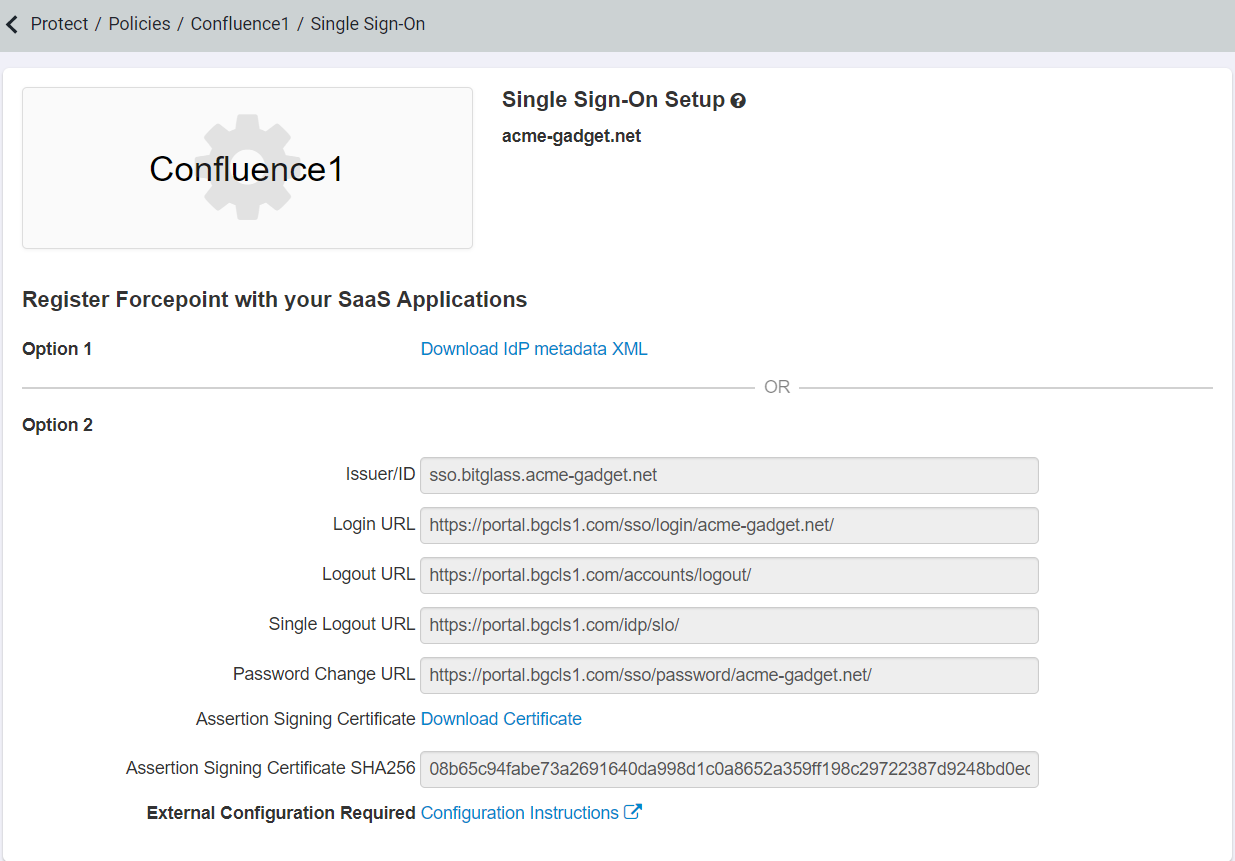
UserLock provides secure single sign- on ( SSO ) for existing on-premises Active Directory (AD) identities, extending access protection to the cloud . Combined with enhanced multi-factor authentication (MFA) and remote access controls, UserLock offers comprehensive access security - protecting network, remote and cloud access , from anywhere.
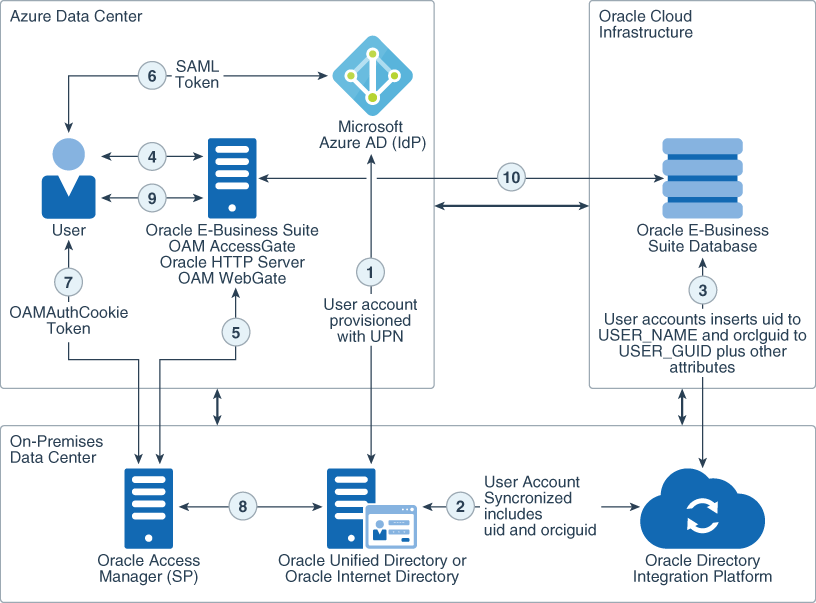
The new release of UserLock 11 provides secure single sign- on ( SSO ) for existing on-premises Active Directory (AD) identities, extending access protection to the cloud . Combined with enhanced multi-factor authentication (MFA) and remote access controls, this new release completes UserLock's comprehensive security solution.
Windows Cloud Detailed Authentication Flow

It covers the integration of Kerberos objects and RdsAadAuth, highlighting the steps involved in the authentication process. The main section, Windows Cloud SSO Authentication Flow, explains how RDS Azure Active Directory (AAD) Auth is enforced as a protocol, and ensuring secure access to both cloud and on-premises resources.
configure Single Sign- On ( SSO ) between my on-premises Active Directory (AD) and multiple cloud applications. My goal is for users to use their existing on -prem AD credentials to seamlessly access these cloud apps without entering passwords multiple times. However, I'm a bit confused about which approach or setup is best suited for my environment.

How to secure cloud access starting with on
For a long time, Active Directory single sign- on ( SSO ) and multi-factor authentication (MFA) were seen as nice-to-have technologies to use on a case-by-case basis to make network access more user-friendly or to add an extra security layer where needed. But recently, as the risks and effects of cybercrime garner public attention, this rather laid-back view of SSO and MFA, and how they work ...
Hybrid identity bridges the gap between on-premises Active Directory and Microsoft Entra ID. By synchronizing identity objects, organizations allow users to access resources hosted on-premises , in Azure Local, and in the public cloud , using a single, secure identity.
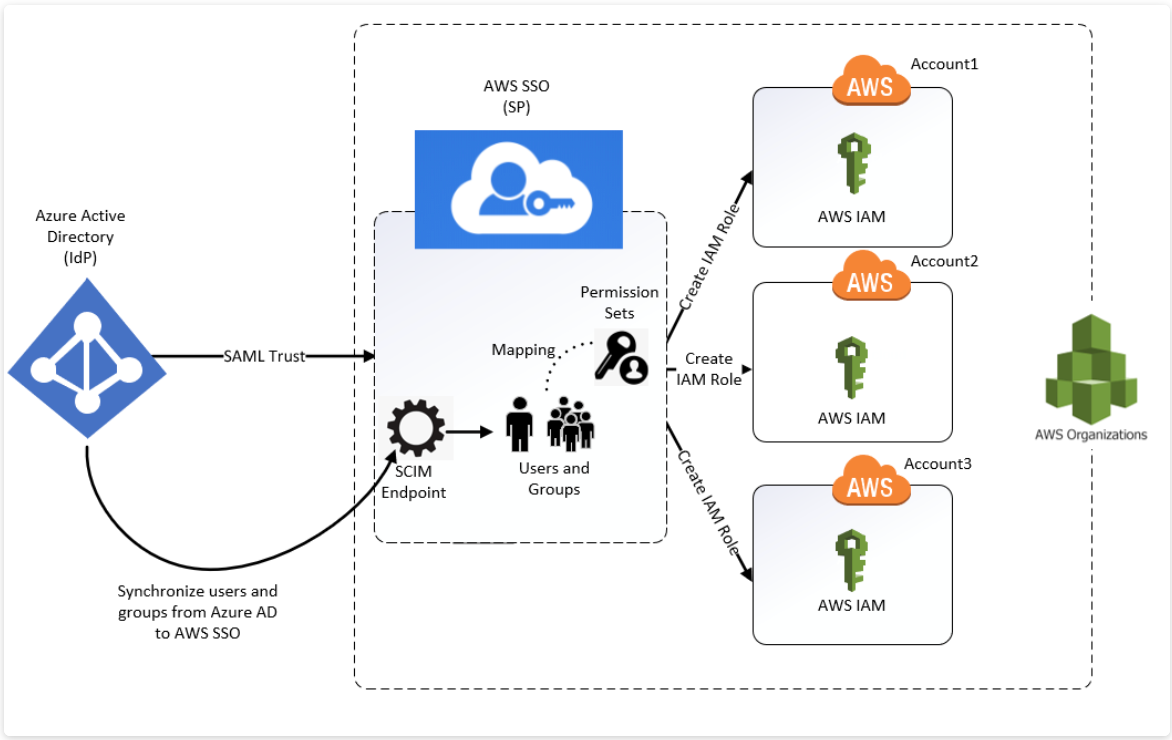
Azure AD SSO Setup for Hybrid Environments
Azure AD SSO Setup for Hybrid Environments Most organisations migrating to Azure do not start from zero. They have on-premise Active Directory , domain-joined devices, and users who already authenticate against their existing infrastructure. Getting those users seamless access to Azure and Microsoft 365 services without a separate login, while keeping their on-premise access working, is the ...
In modern environments where devices are joined only to Microsoft Entra ID, enabling seamless access to on-premises resources like file shares or legacy applications can be a challenge.
Azure AD Pass
Azure Active Directory (Azure AD), a robust cloud -based identity and access management solution by Microsoft, offers various authentication methods. One of these methods is Azure AD Pass-through Authentication, which enables seamless authentication between on-premises and cloud environments.
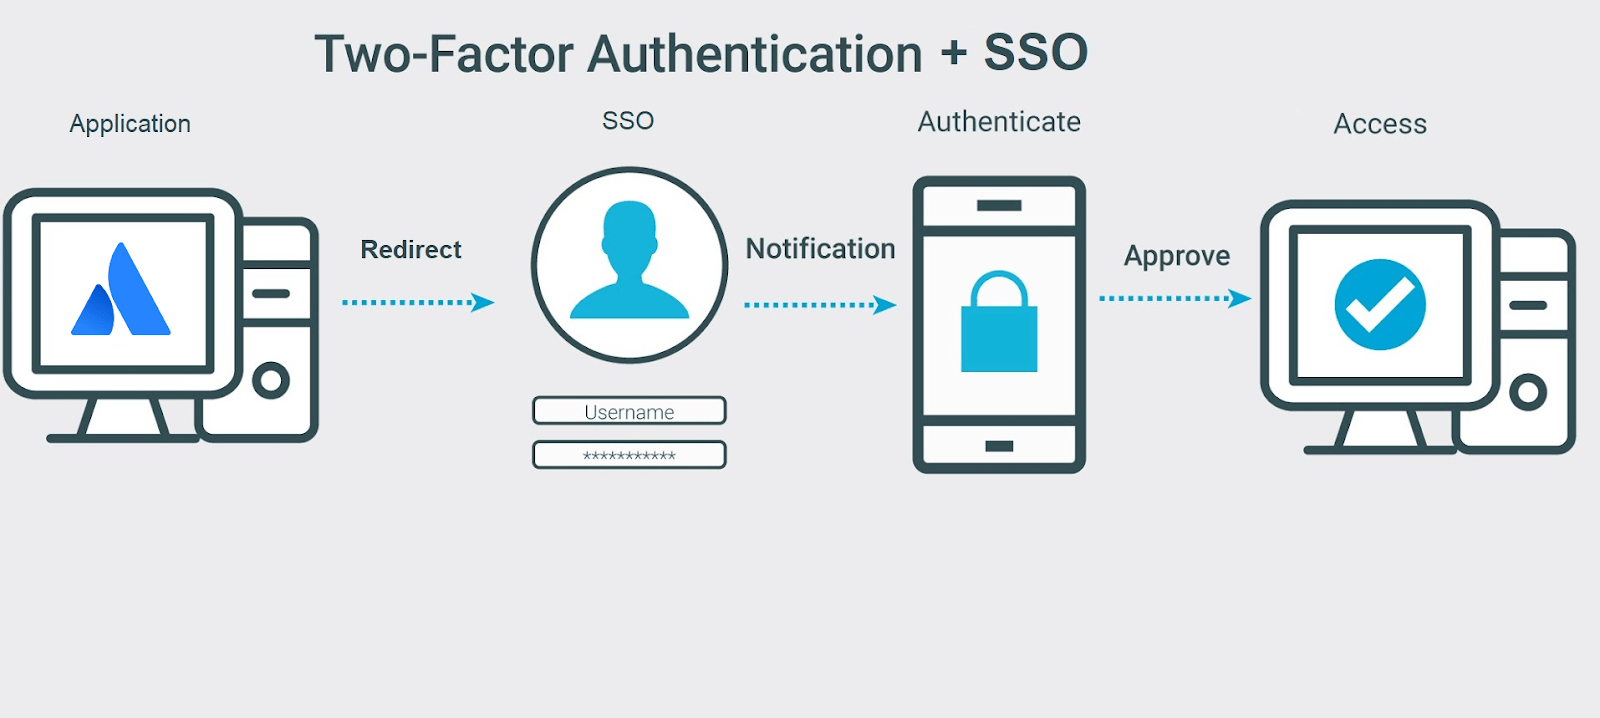


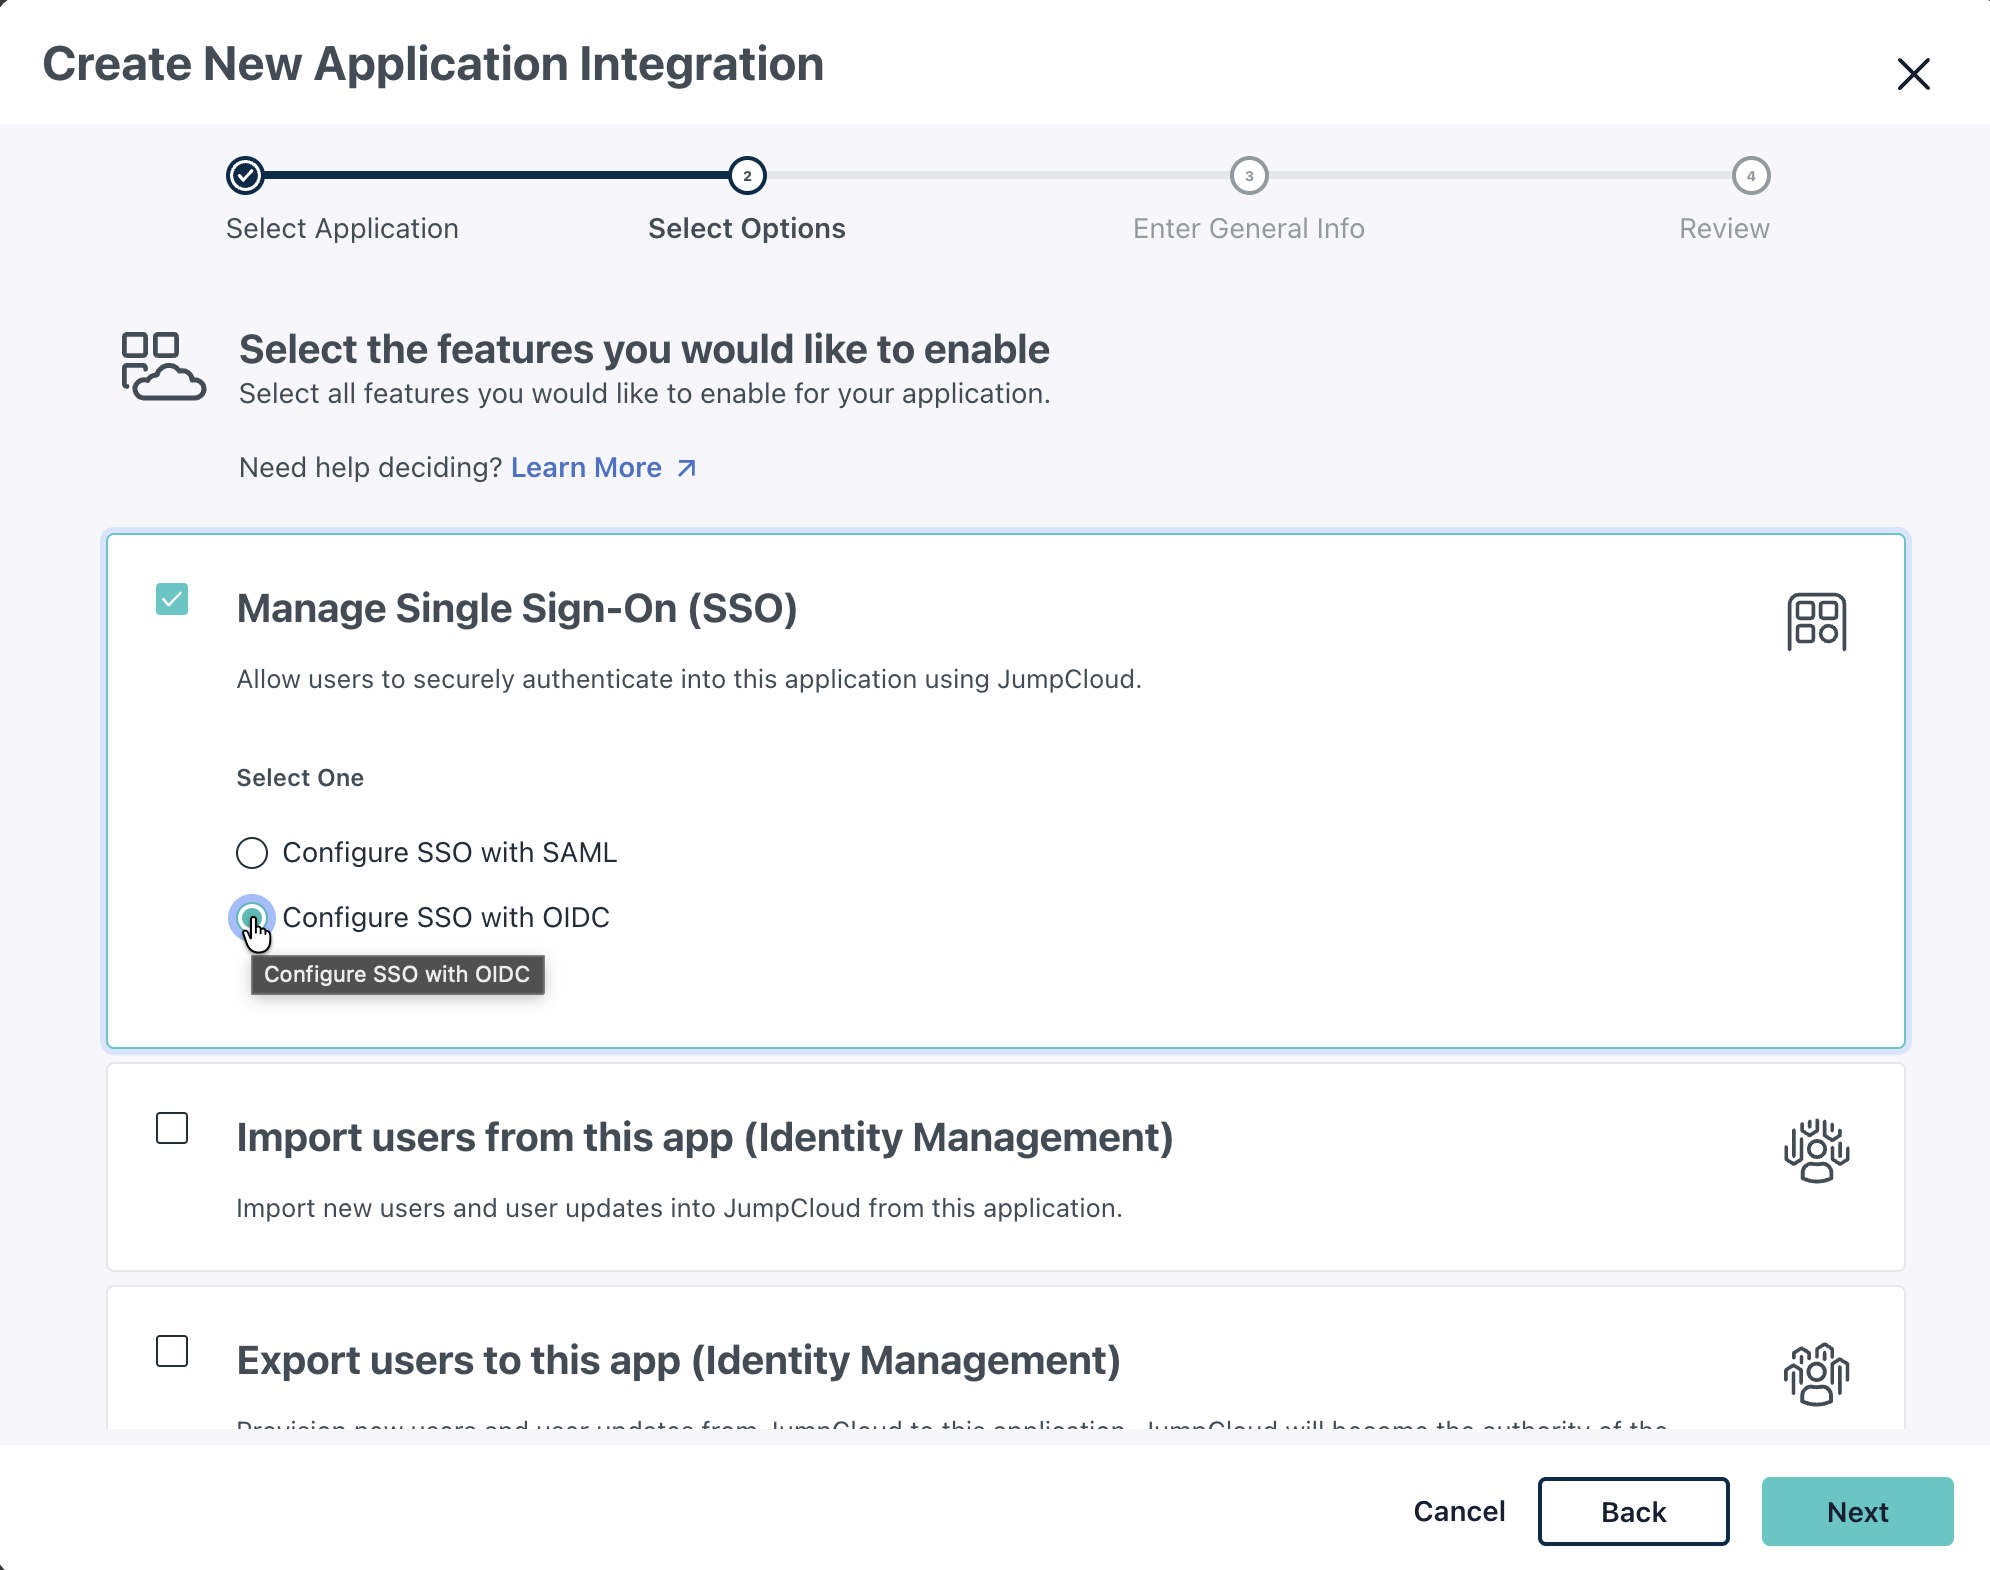

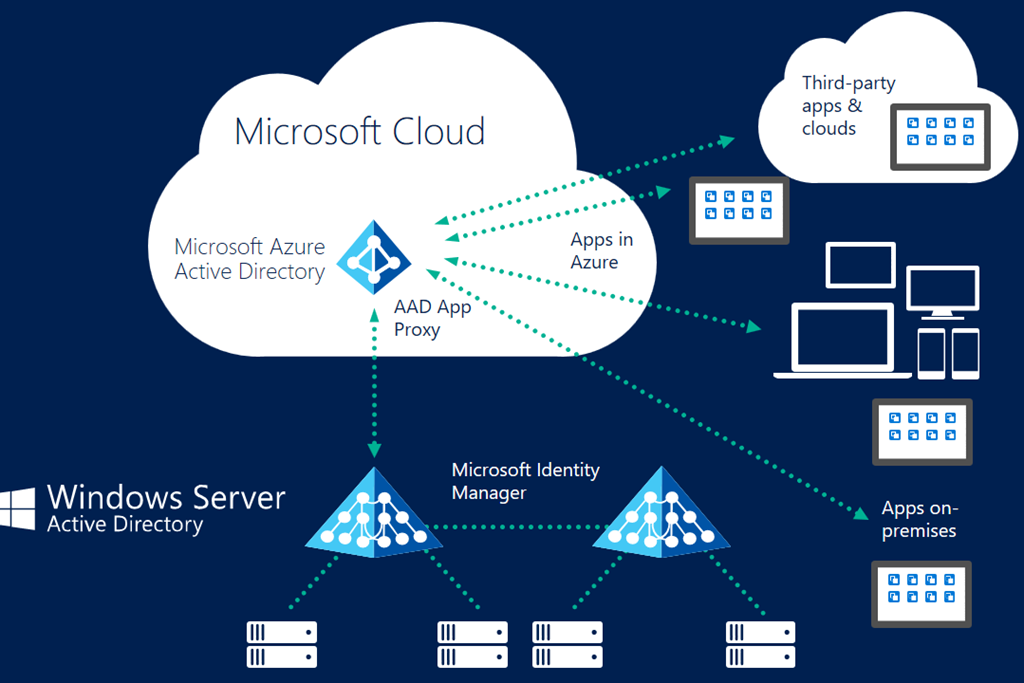
Most teams think " cloud SSO for on -prem AD users" is a single checkbox: sync identities to the cloud , and users magically stop seeing prompts. In reality, you're stitching together two different security worlds: On -prem AD is built around Kerberos, NTLM, LDAP, domain-joined devices, and network locality.