SSO JIT (Just

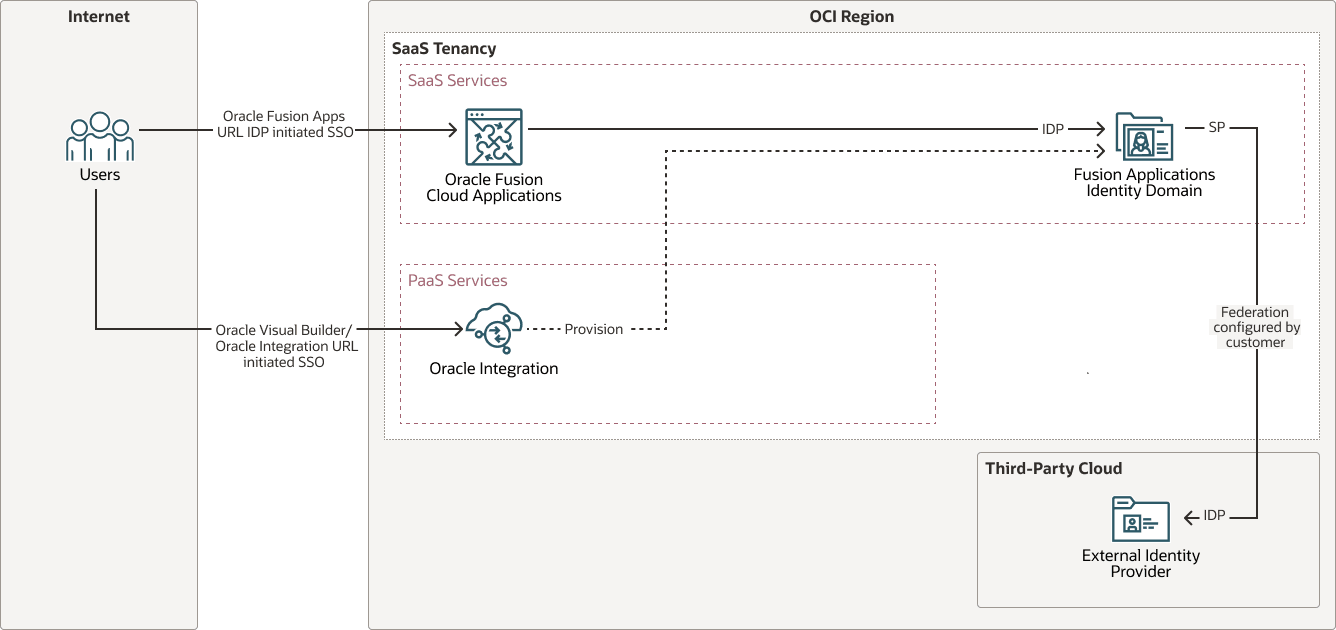
Overview of SSO - JIT Provisioning and Authentication Keeper SSO Connect® Cloud leverages Keeper's zero-knowledge security architecture to securely and seamlessly authenticate users into their Keeper Vault and dynamically provision user vaults to the platform.
Overview of SSO - JIT Provisioning and Authentication Keeper SSO Connect® Cloud leverages Keeper's zero-knowledge security architecture to securely and seamlessly authenticate users into their Keeper Vault and dynamically provision user vaults to the platform.
User and Team Provisioning
For organizations who are already utilizing federated services, Keeper SSO Connect provides real- time authentication and Just-In-Time ( JIT ) provisioning . If you would like to automatically assign users to Roles and Teams through AD security groups or other custom LDAP queries, the Keeper AD Bridge software can also be utilized.
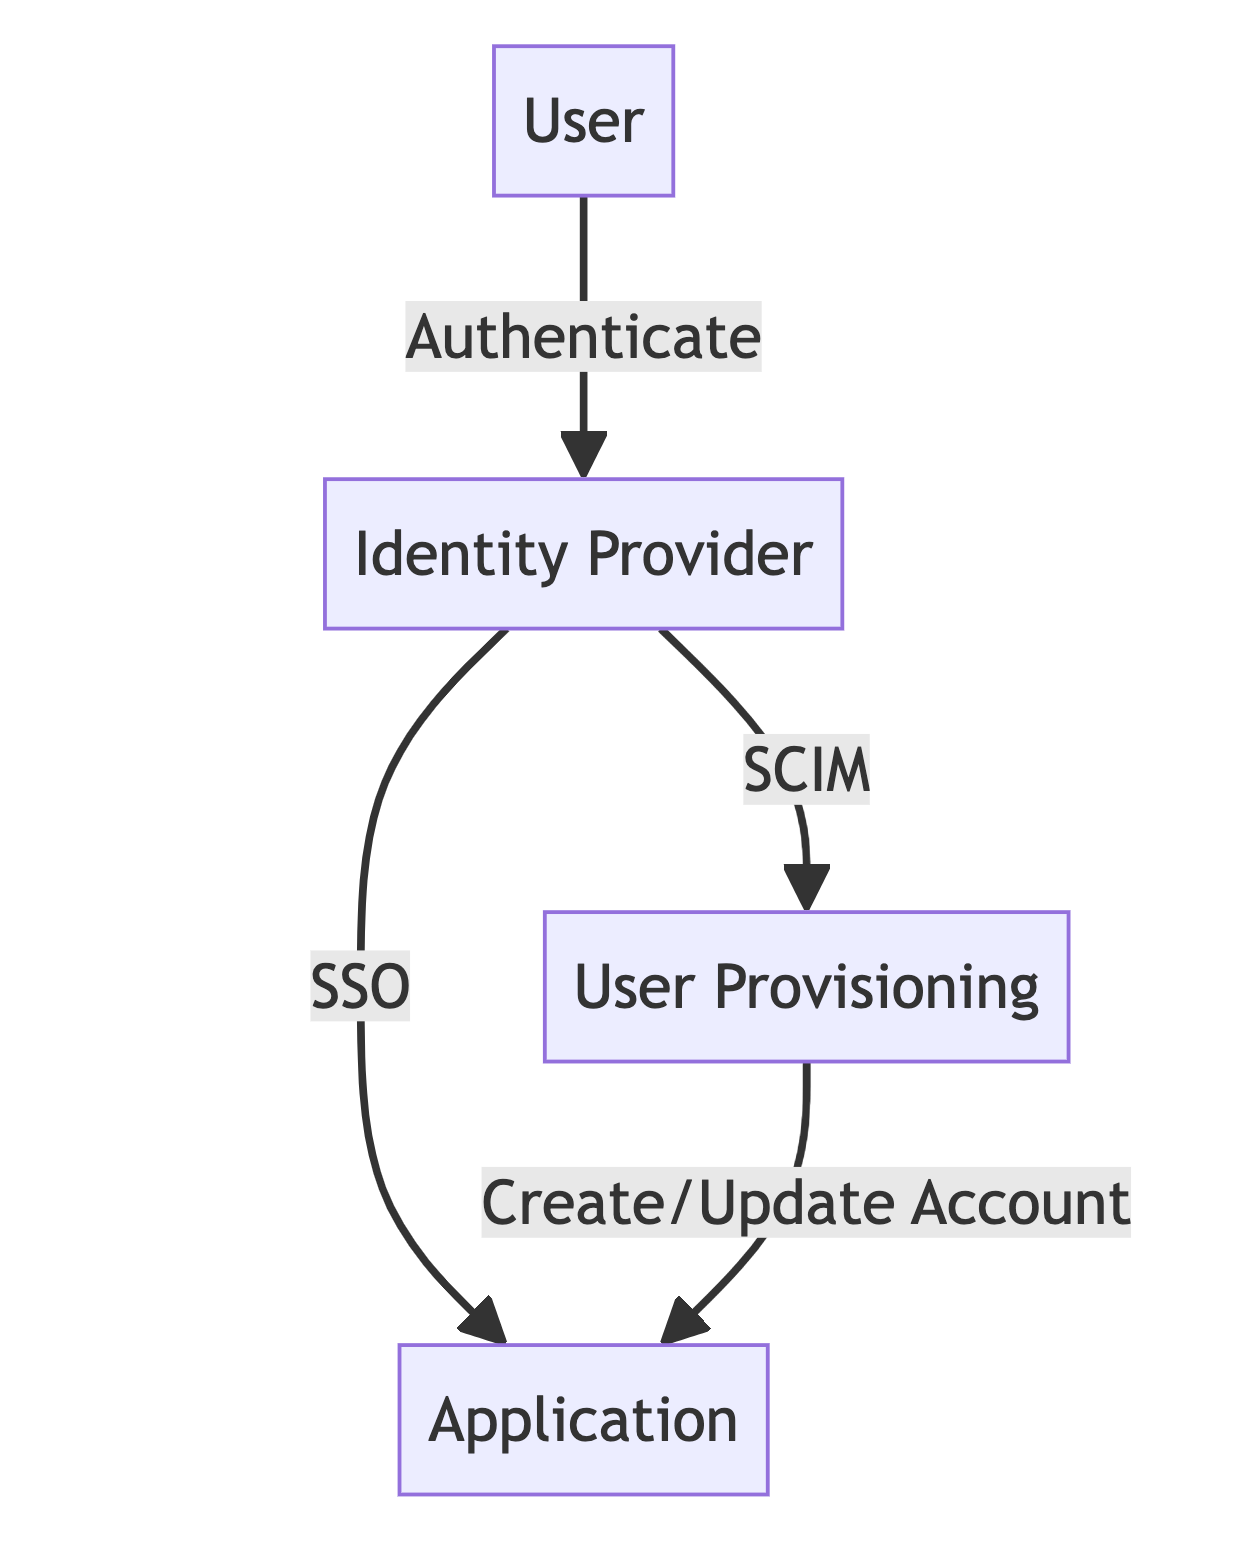
Learn how Just-in-Time ( JIT ) provisioning automates user account creation in SSO . Expert guide for CTOs on SAML, SCIM vs JIT , and enterprise IAM security.
How to Implement Just
SSOJet Add enterprise authentication to your SaaS with SSO connections, SAML, and SCIM—without complex infrastructure.
Just-in-Time ( JIT ) provisioning creates users during SSO login, while SCIM automates user lifecycle via APIs. Learn how to implement JIT provisioning , compare JIT vs SCIM, and build scalable SaaS authentication systems.
Overview of Sso Jit Just In Time Provisioning And Authentication Enterprise Guide
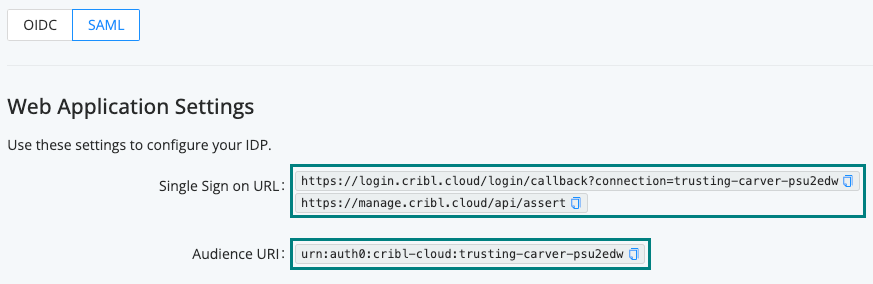
Just-in-Time ( JIT ) Provisioning , or automatic account provisioning , is a process by which accounts for employees are created on-demand during the first time they authenticate via SAML SSO in your application.
JIT provisioning is a method of automatically creating user accounts in a service provider (SP) at the moment of first login, using identity information passed along during the SSO authentication flow.

What Is Just
Learn how Just-in-Time ( JIT ) provisioning automates user onboarding via SSO and SAML, saving admin time while improving access security.


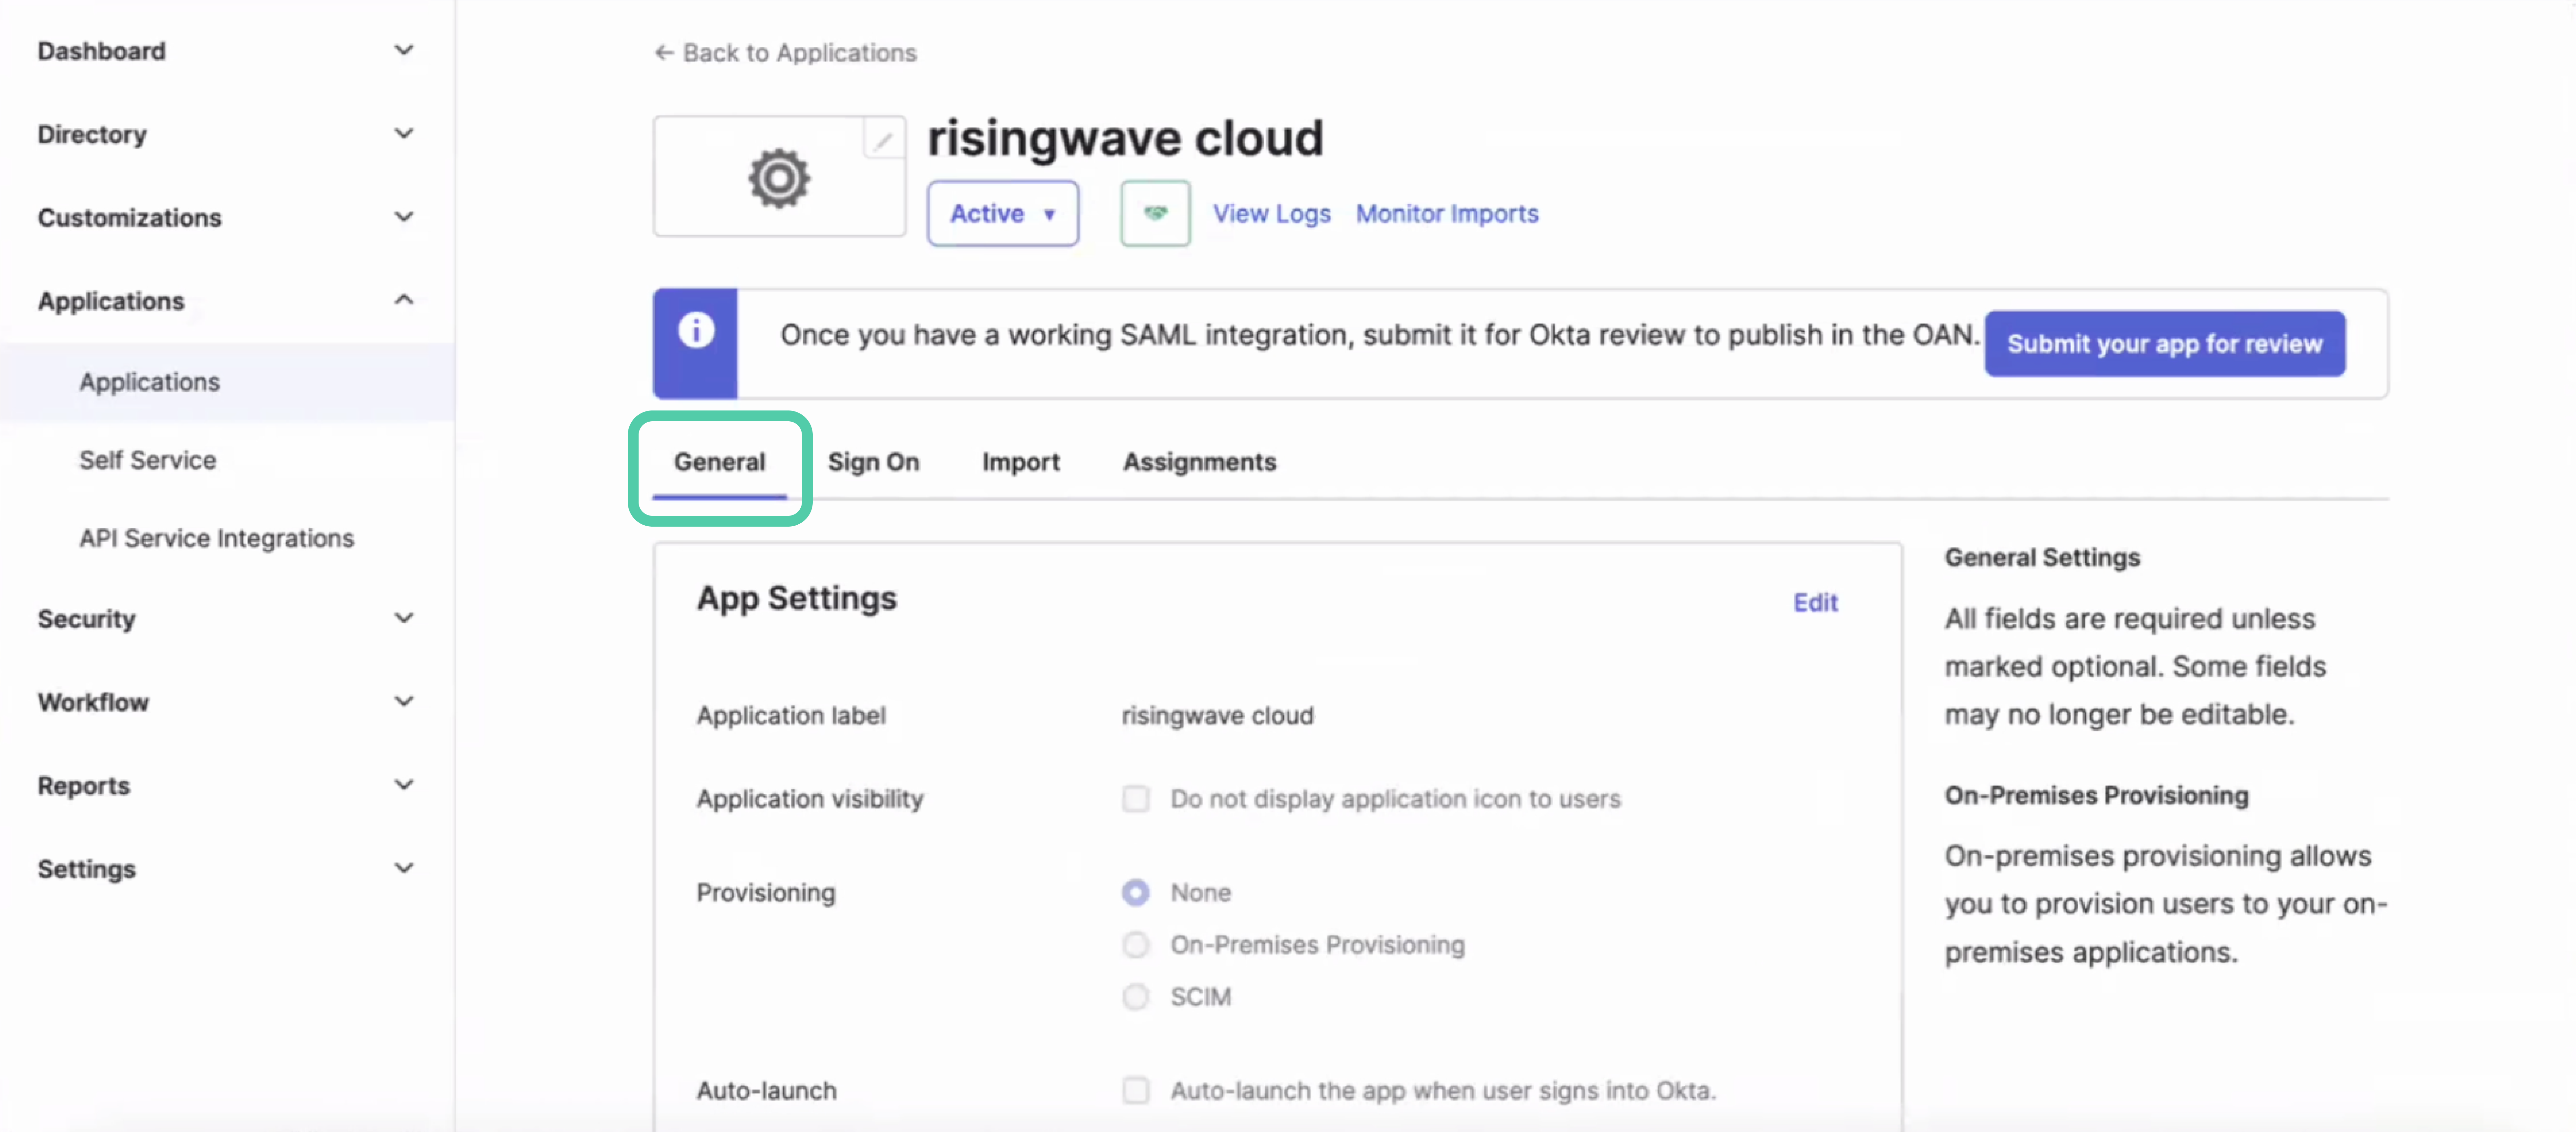


Azure AD JIT provisioning ( just-in-time user creation): the pattern where your application creates a local user account on the user's first successful single sign-on, using attributes carried inside the SAML assertion (or OIDC ID token) that Microsoft Entra ID issues, instead of pre-creating accounts through a separate provisioning API.