The Top Microsoft 365 Phishing Email Examples (In 2025)

What is Microsoft's Strategy for preventing Email Phishing ? What Are Some Emerging Email Phishing Trends in 2025? Conclusion: How To Staying Vigilant Against Phishing Threats? Microsoft 365 (M365) is used by over a million companies worldwide, with over a hundred million customers in the United States using the Office Suite software alone.
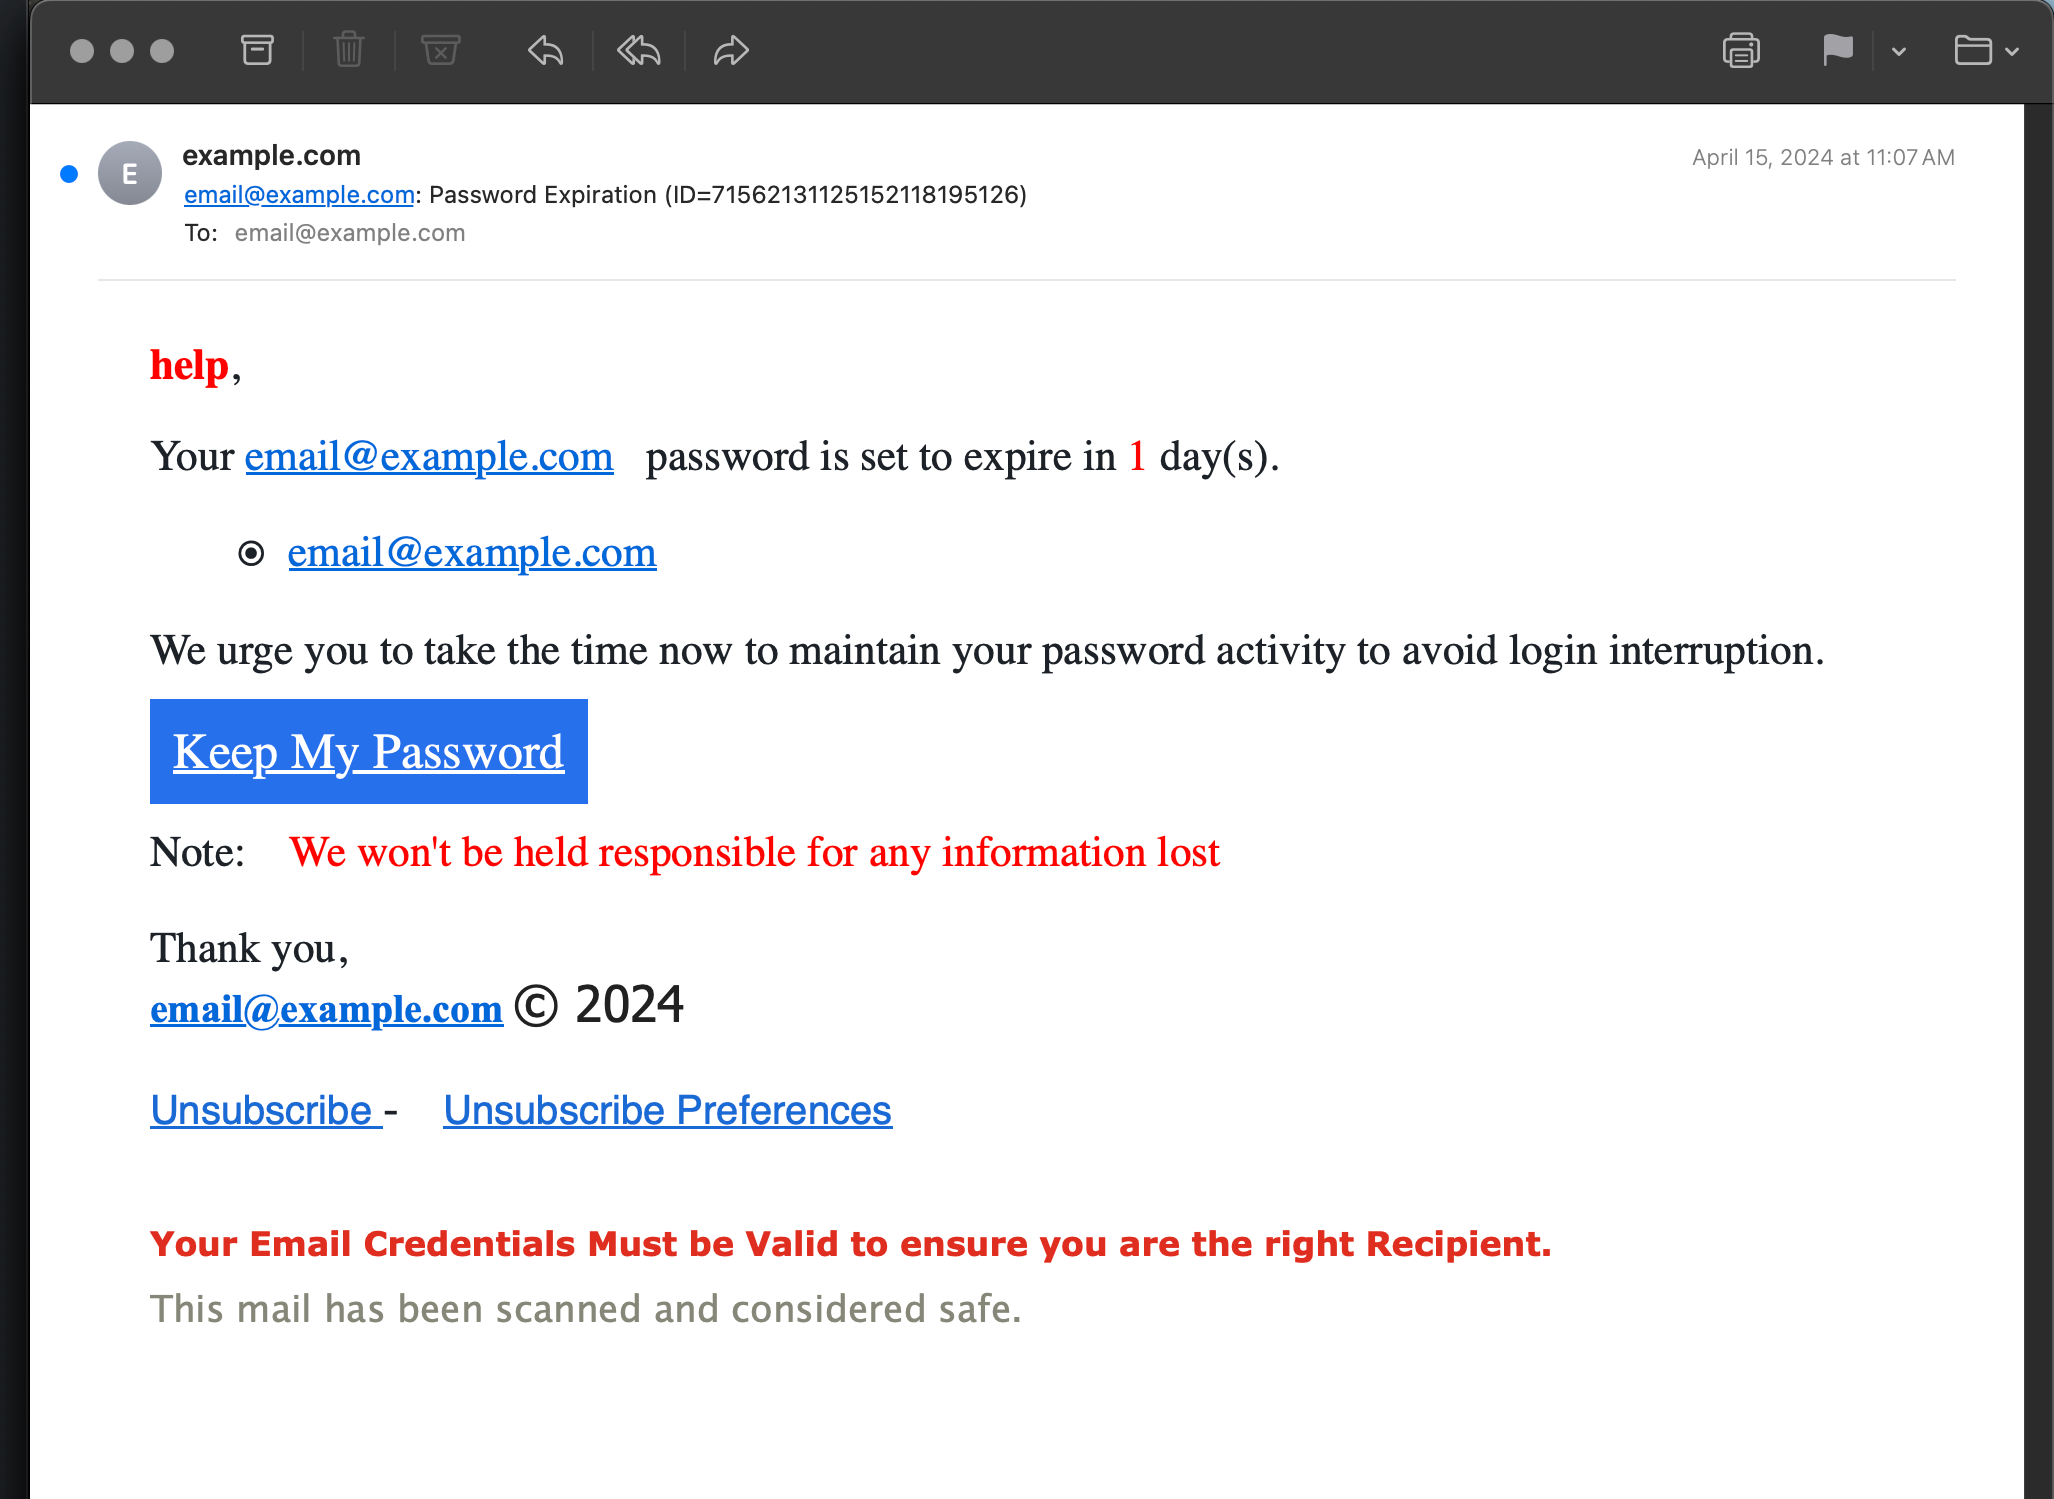
Office 365 Phishing Email Examples Common Office 365 phishing email examples include fake failure-of-delivery notices whose 'send again' link installs malware, storage-limit alerts urging you to activate a malicious 'Quota' fix, spoofed account-reactivation requests leading to fake login pages, and the PhishPoint scam, which hides malicious links inside legitimate SharePoint files to bypass ...
Microsoft 365 Phishing Examples

The bad guys have been targeting Microsoft Office 365 users lately with multiple phishing attacks. Below is a sample of what to be on the lookout for.
Microsoft 365 is one of the most widely used software platforms, providing productivity, collaboration, and security tools that improve workflows. However, because it handles large volumes of sensitive data, it has also become a prime target for phishing attacks. In this blog, we will show the most common Microsoft phishing scam examples , how to recognize them, and how to protect your business ...
Useful Notes on Office 365 Phishing Email Example
The anti- phishing policies for all cloud mailboxes and anti- phishing policies in Defender for Office 365 share several features (default policy, custom policies, common policy settings, spoof settings, and first contact safety tip), but only Defender for Office 365 includes impersonation settings and phishing email thresholds. The specific feature comparison is:
Conclusion Microsoft Office 365 phishing attacks can cause a security breach, leading to data theft or loss for any business using the suite. To enhance your organization's Microsoft 365 phishing protection, you can set MFA, configure anti- phishing policies, apply email authentication standards and update your software.
Simulate a phishing attack with Attack simulation training
Admins can learn how to simulate phishing attacks and train their users on phishing prevention using Attack simulation training in Microsoft Defender for Office 365 Plan 2.
This report details ongoing phishing campaigns specifically targeting organisations utilizing Microsoft 365 , with a primary focus on Office 365 tenants where Multi-Factor Authentication (MFA) is not enforced.

Introducing a new phishing technique for compromising Office 365 accounts
The ongoing global phishing campaings againts Microsoft 365 have used various phishing techniques. Currently attackers are utilising forged login sites and OAuth app consents. In this blog, I'll introduce a new phishing technique based on Azure AD device code authentication flow. I'll also provide instructions on how to detect usage of compromised credentials and what to do to prevent ...


The Federal Bureau of Investigation (FBI) is issuing this Public Service Announcement (PSA) to warn the public about an emerging Phishing 1 -as-a-Service 2 (PhaaS) platform called Kali365, first seen in April 2026. Kali365 has primarily been distributed via Telegram, enabling cyber threat actors to obtain Microsoft 365 access tokens and bypass multi-factor authentication 3 (MFA) protocols ...