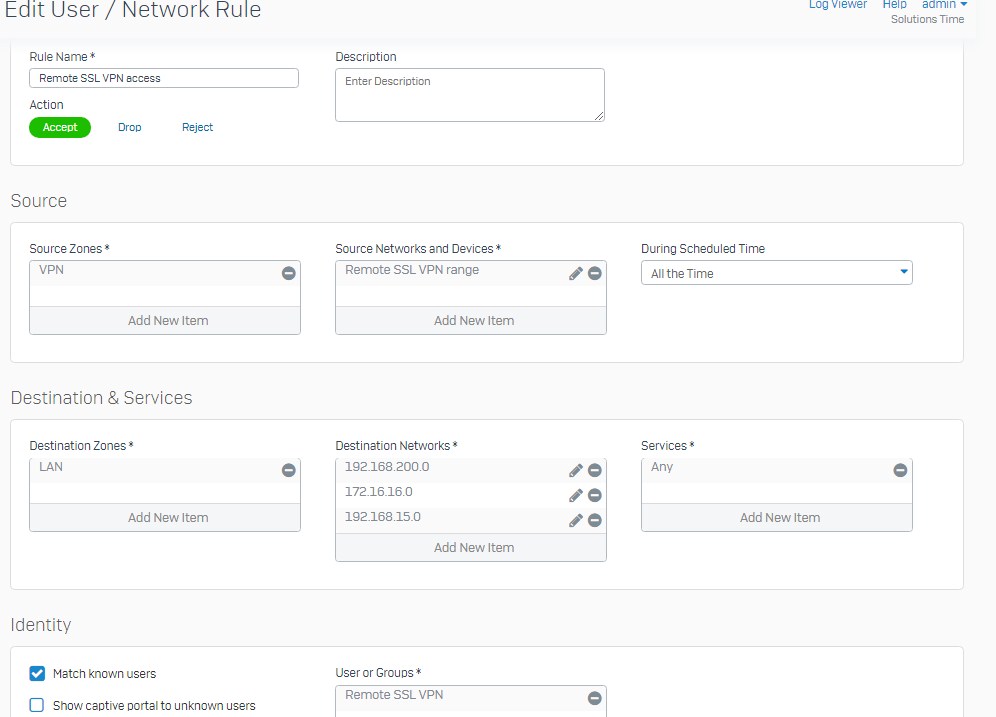
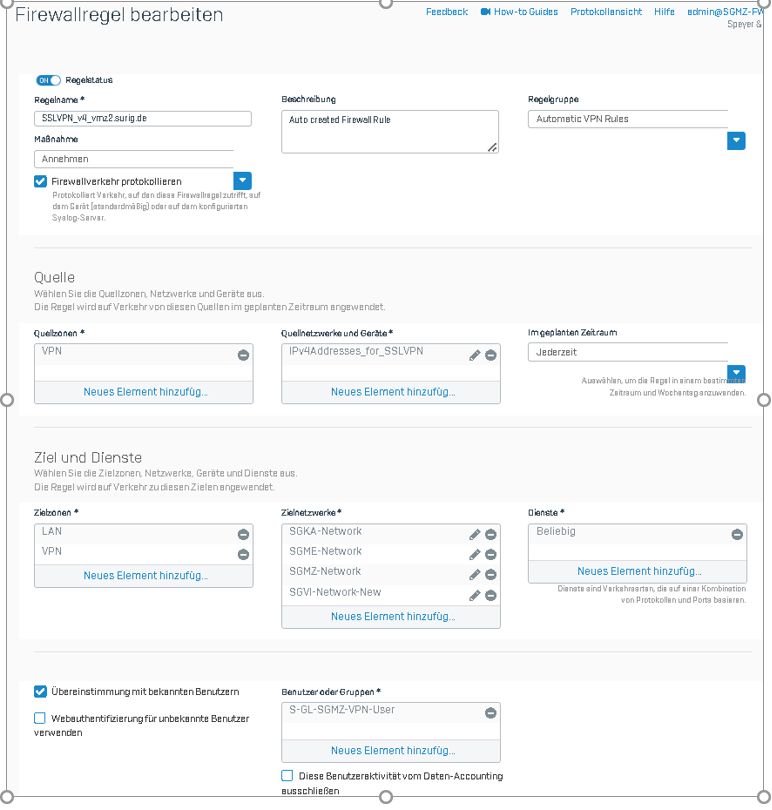
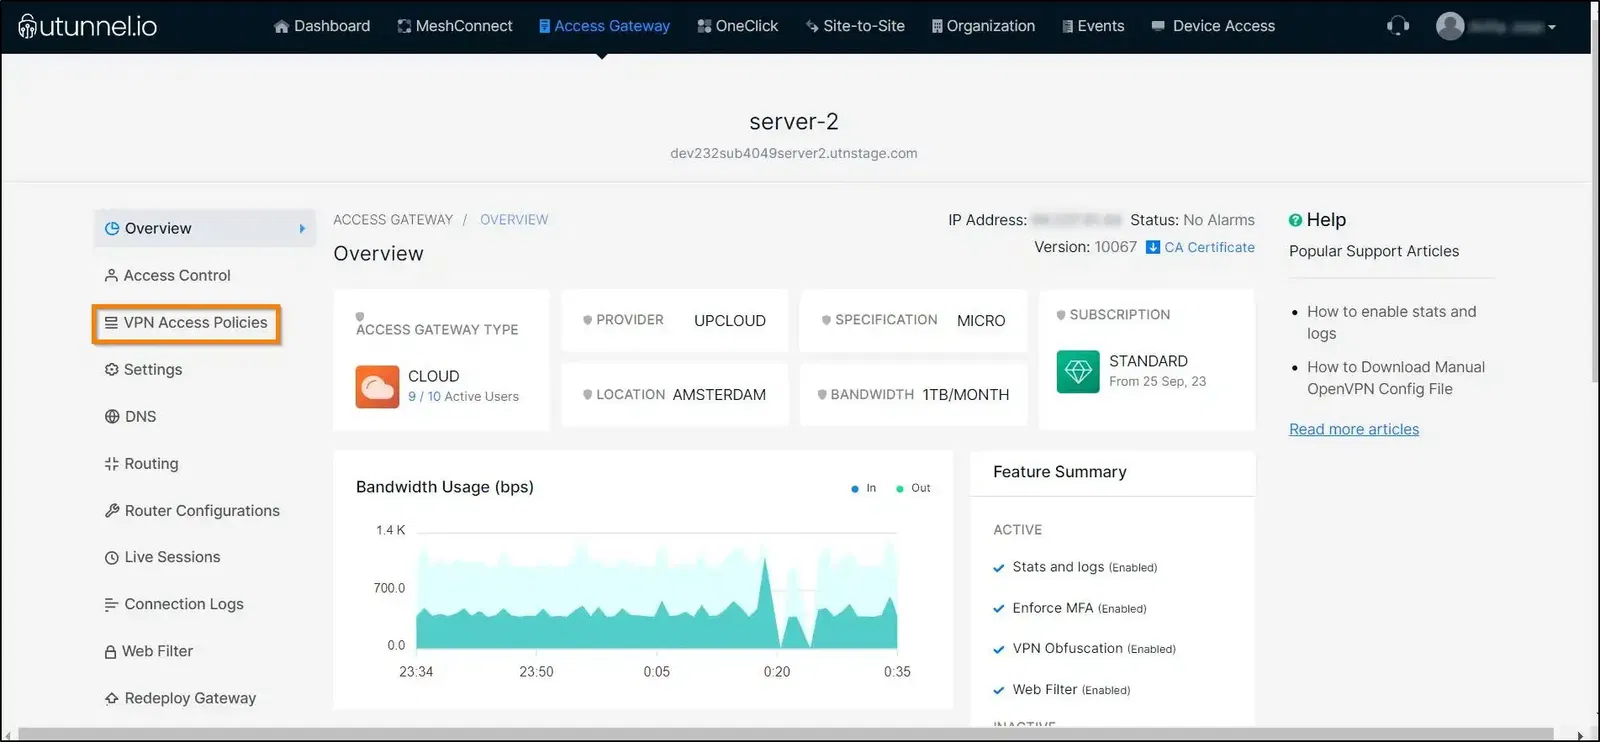
Go to Rules andpolicies> Firewall rules and add a firewall rule or update an existing one to allowaccessto resources through theremoteaccessSSLVPNtunnels.
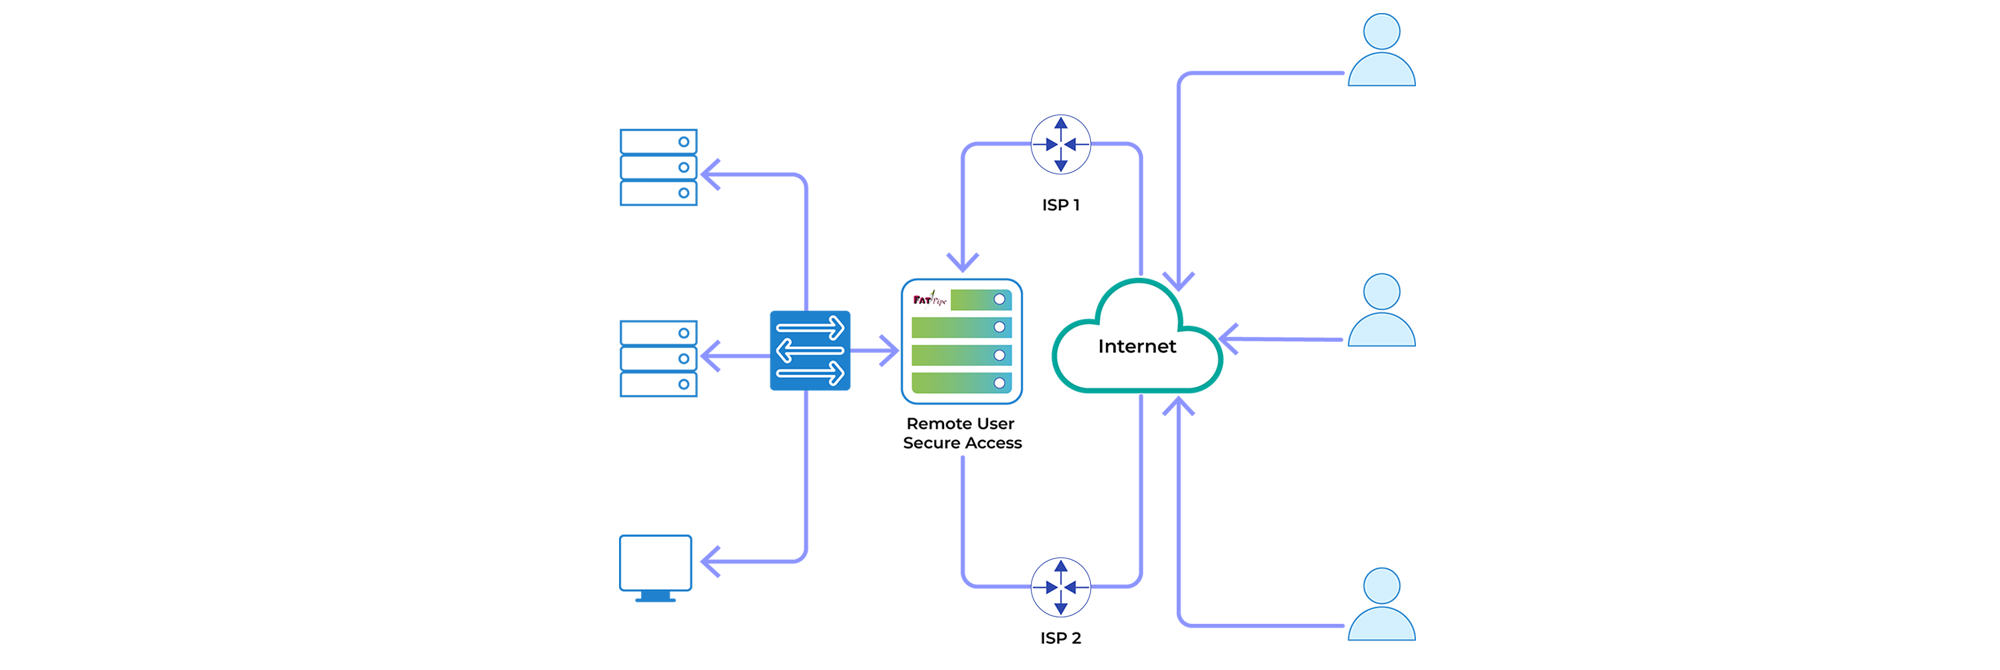
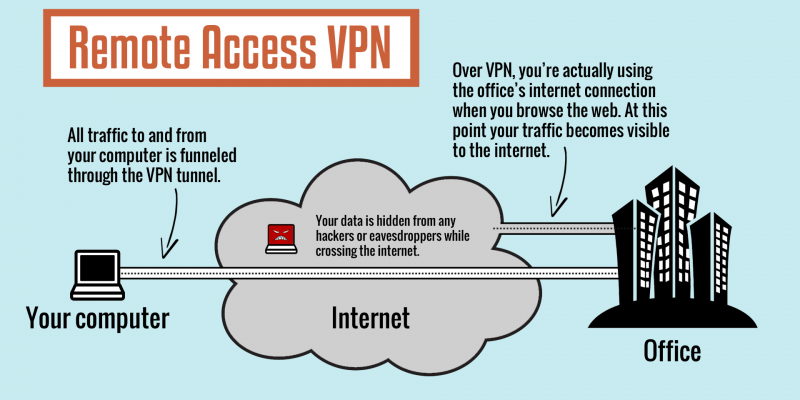
AremoteaccessIPSecVPNconsists of aVPNclient and aVPNheadend device, orVPNgateway. TheVPNclient software resides on a user's workstation and initiates theVPNtunnelaccessto the corporate network. At the other end of theVPNtunnel is theVPNgateway at the edge of the corporate site.
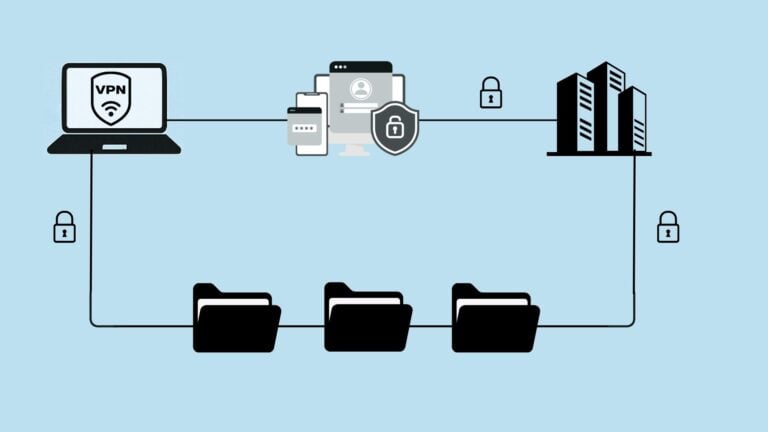
Why use aVPN?VPNsare encrypted network connections. These allowremoteusers to securelyaccessan organisation's services.VPNsare one way to guarantee the security of 'data in transit' across an untrusted network, but they also provide several other benefits.
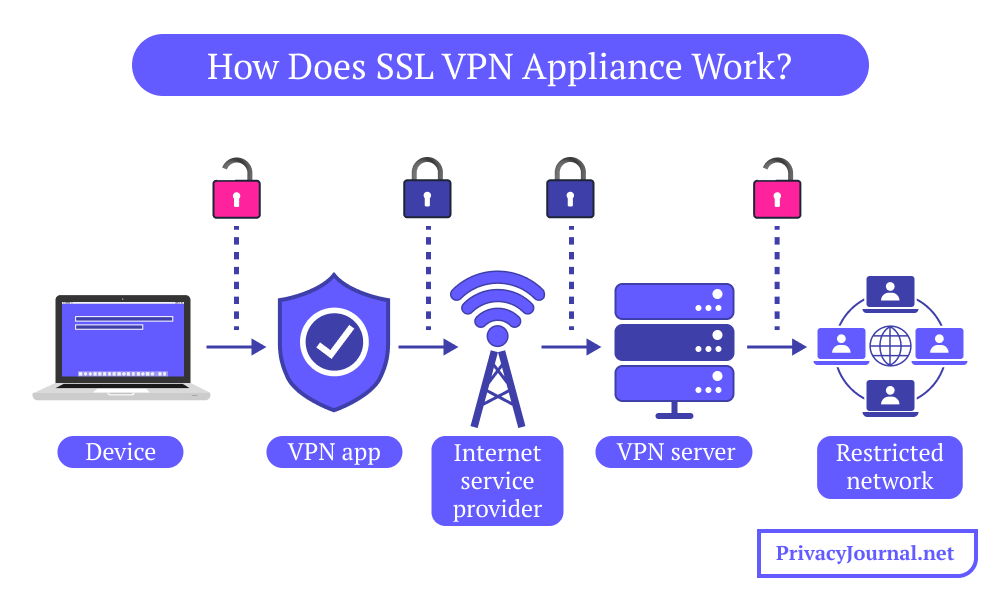
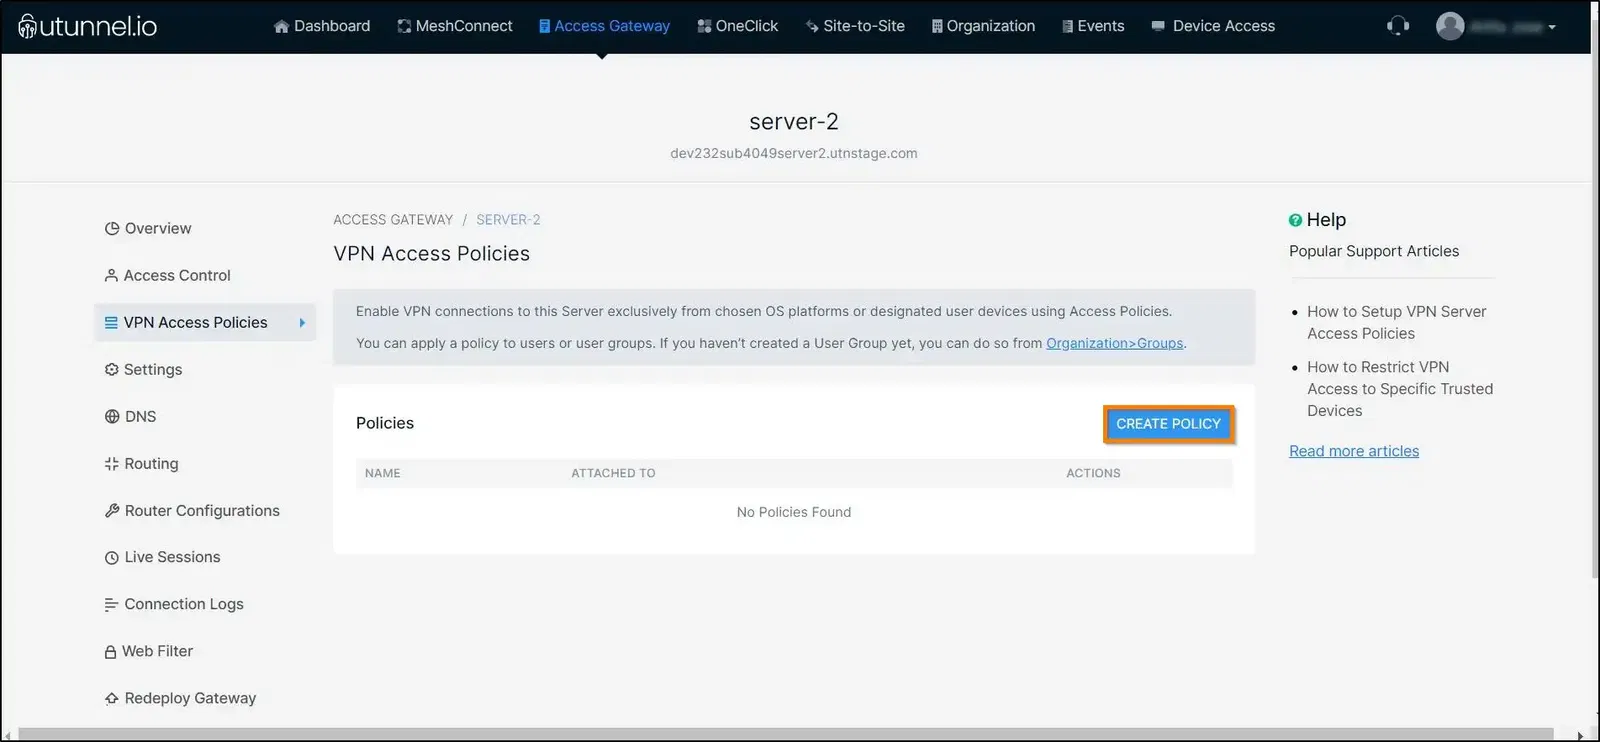
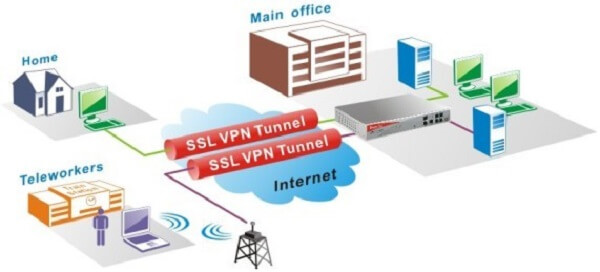
With thesepolicies, you can enableremoteusers to connect to the network securely over the internet usingremoteaccessSSLVPNconnections. The assistant automatically configures aremoteaccesspolicy, firewall rule, and deviceaccesssettings.

For aremoteaccessIPsecVPNhosted on an ASA 8.4 (x) device, you have the option of configuring IKE version 2 (IKEv2). If you decide to use IKEv2, you must configure severalSSLVPNpoliciesin addition to the regular IPSecpolicies. The user also must use the AnyConnect 3.0+VPNclient to make an IKEv2 connection. For more information, see - Creating IPSecVPNsUsing theRemoteAccessVPN...
Discover how to implement secureremoteaccessusingVPNsandSSL/TLS protocols to protect data, credentials, and internal resources in today'sremotework environment.
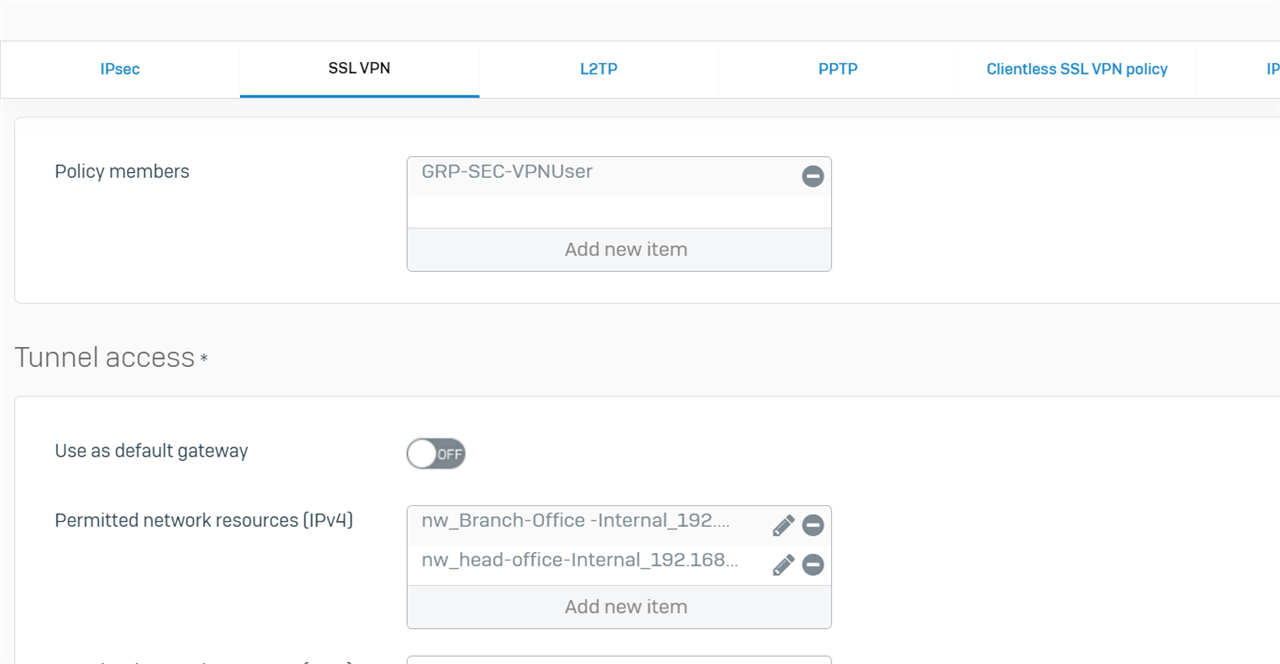
See Sophos Firewall:RemoteaccessVPN. The following are the required configurations on the Sophos Firewall at the local site where theSSLVPNclient is connecting. Allow the IPsecremotenetwork Go toRemoteaccessVPN>SSLVPN. Edit yourremoteaccesspolicy. Go to Tunnelaccessand add the IPsecremotenetwork in Permitted network resources.