Understanding GDPR Cloud Compliance
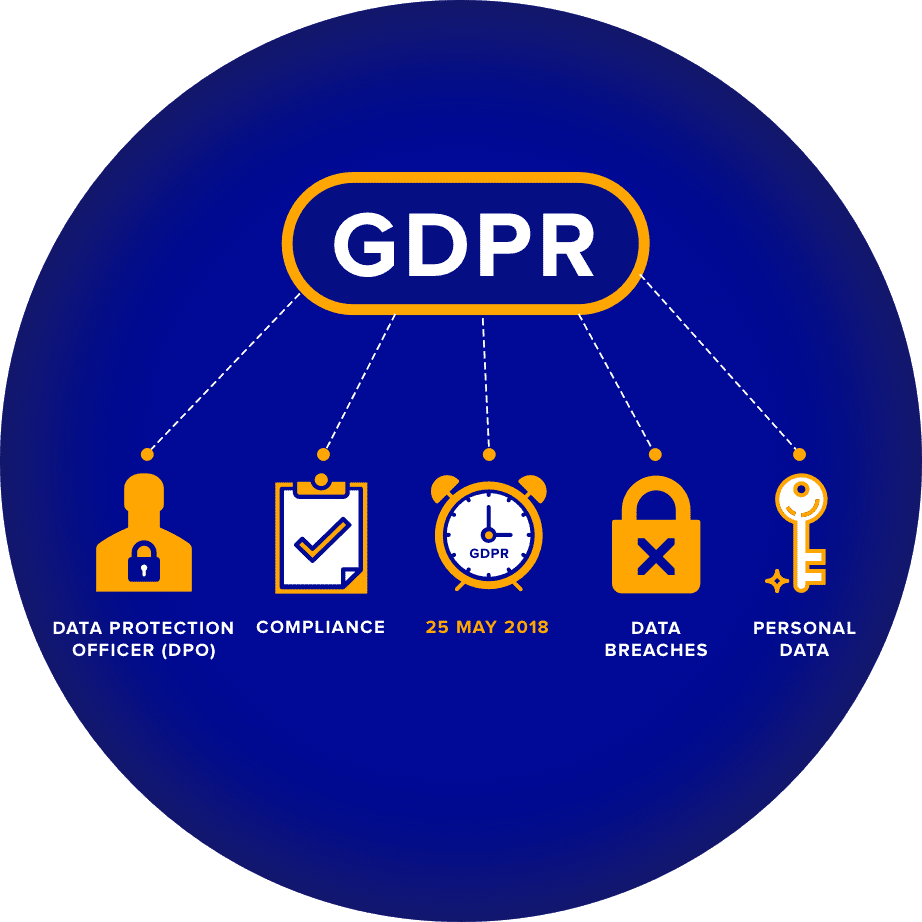
GDPR cloud compliance considerations are crucial for any organization using cloud services to process or store the personal data of EU citizens. Some key considerations include data location and transfers, data access and security , privacy policies and disclosures, and data subject rights.

Learn GDPR cloud compliance requirements, Article 32 controls, data residency rules, and a practical checklist for maintaining continuous cloud compliance .
GDPR Compliance in the Cloud

This article explores the key aspects of GDPR compliance in the cloud , addressing data security measures, data subject rights, incident response, international data transfers, and the role of training and awareness.
At Google Cloud , we champion initiatives that prioritize and improve the security and privacy of customer personal data, and want you, as a Google Cloud customer, to feel confident using our services in light of GDPR requirements. If you partner with Google Cloud , we will support your GDPR compliance efforts by:

Cloud GDPR
Cloud Security Alliance (CSA) - Cloud Controls Matrix (CCM) National Institute of Standards and Technology (NIST) - Cloud Computing Security Reference Architecture FAQ Q: What is the main goal of GDPR compliance in cloud computing? A: The main goal is to protect personal data against unauthorized access, disclosure, or loss.
GDPR compliance in cloud environments is largely shaped by how cloud systems are designed, configured, and governed in practice. The distributed, cross-border nature of cloud computing, combined with evolving regulatory enforcement and geopolitical pressures, means that organizations must treat data protection as a core architectural concern.

General Data Protection Regulation
Explore the Microsoft Service Trust Portal for comprehensive security , compliance , and privacy information related to Microsoft cloud services.
AWS supports 143 security standards and compliance certifications, including PCI-DSS, HIPAA/HITECH, FedRAMP, GDPR , FIPS 140-2, and NIST 800-171, helping customers satisfy compliance requirements around the globe.
PDF Advisory
Customers are advised to seek their own legal counsel to develop and implement their GDPR compliance program in relation to cloud services and to assess the features and functionality provided by Oracle in regard to their specific legal and regulatory requirements.