Secure Boot and BitLocker are two powerful security features built into modern Windows systems. While they're designed to protect your data and prevent unauthorized access, there might be instances where you need to disable them. Perhaps you're troubleshooting, or you're installing a legacy operating system that doesn't play well with Secure Boot. Whatever your reason, this guide will walk you through the process of disabling both Secure Boot and BitLocker.
Understanding Secure Boot and BitLocker
Before we dive into the disabling process, let's briefly understand what these features do:
- Secure Boot: This is a security feature that ensures only trusted software can run during the boot process. It helps prevent rootkits and other malware from infecting your system.
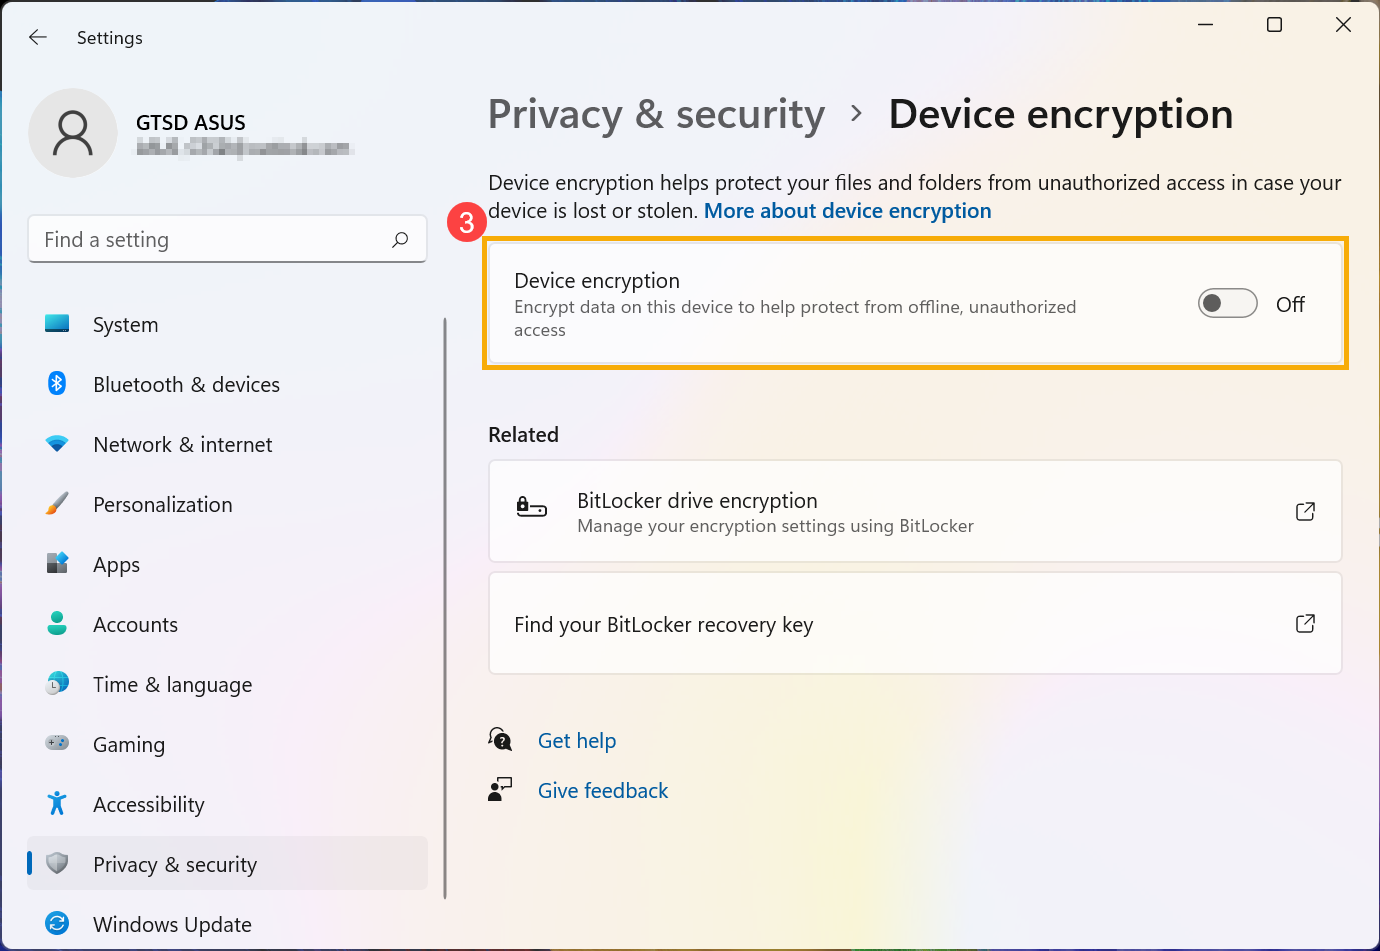
- BitLocker: This is a full-volume encryption tool that protects your data by encrypting your entire hard drive. It prevents unauthorized access to your data, even if your computer is stolen or your hard drive is removed.
Disabling Secure Boot
Method 1: Using the UEFI/BIOS Setup Utility
The most common way to disable Secure Boot is through your computer's UEFI/BIOS setup utility. Here's how:

- Restart your computer and press the key that enters the UEFI/BIOS setup utility. This key varies by manufacturer, so you might need to look it up. Common keys include Esc, Del, F2, F10, or F12.
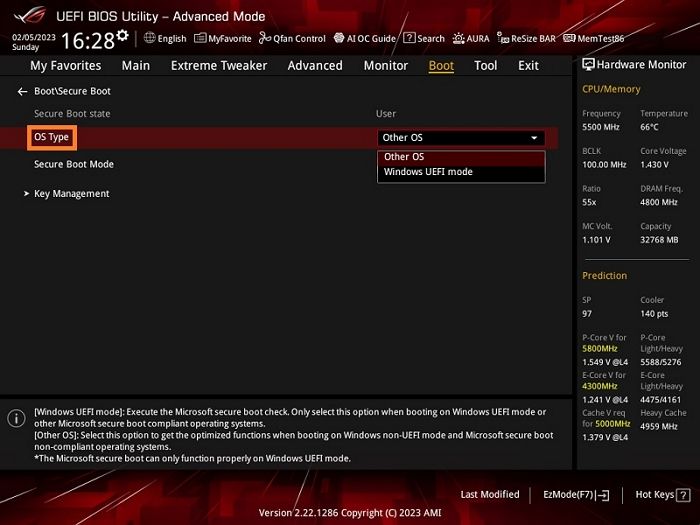
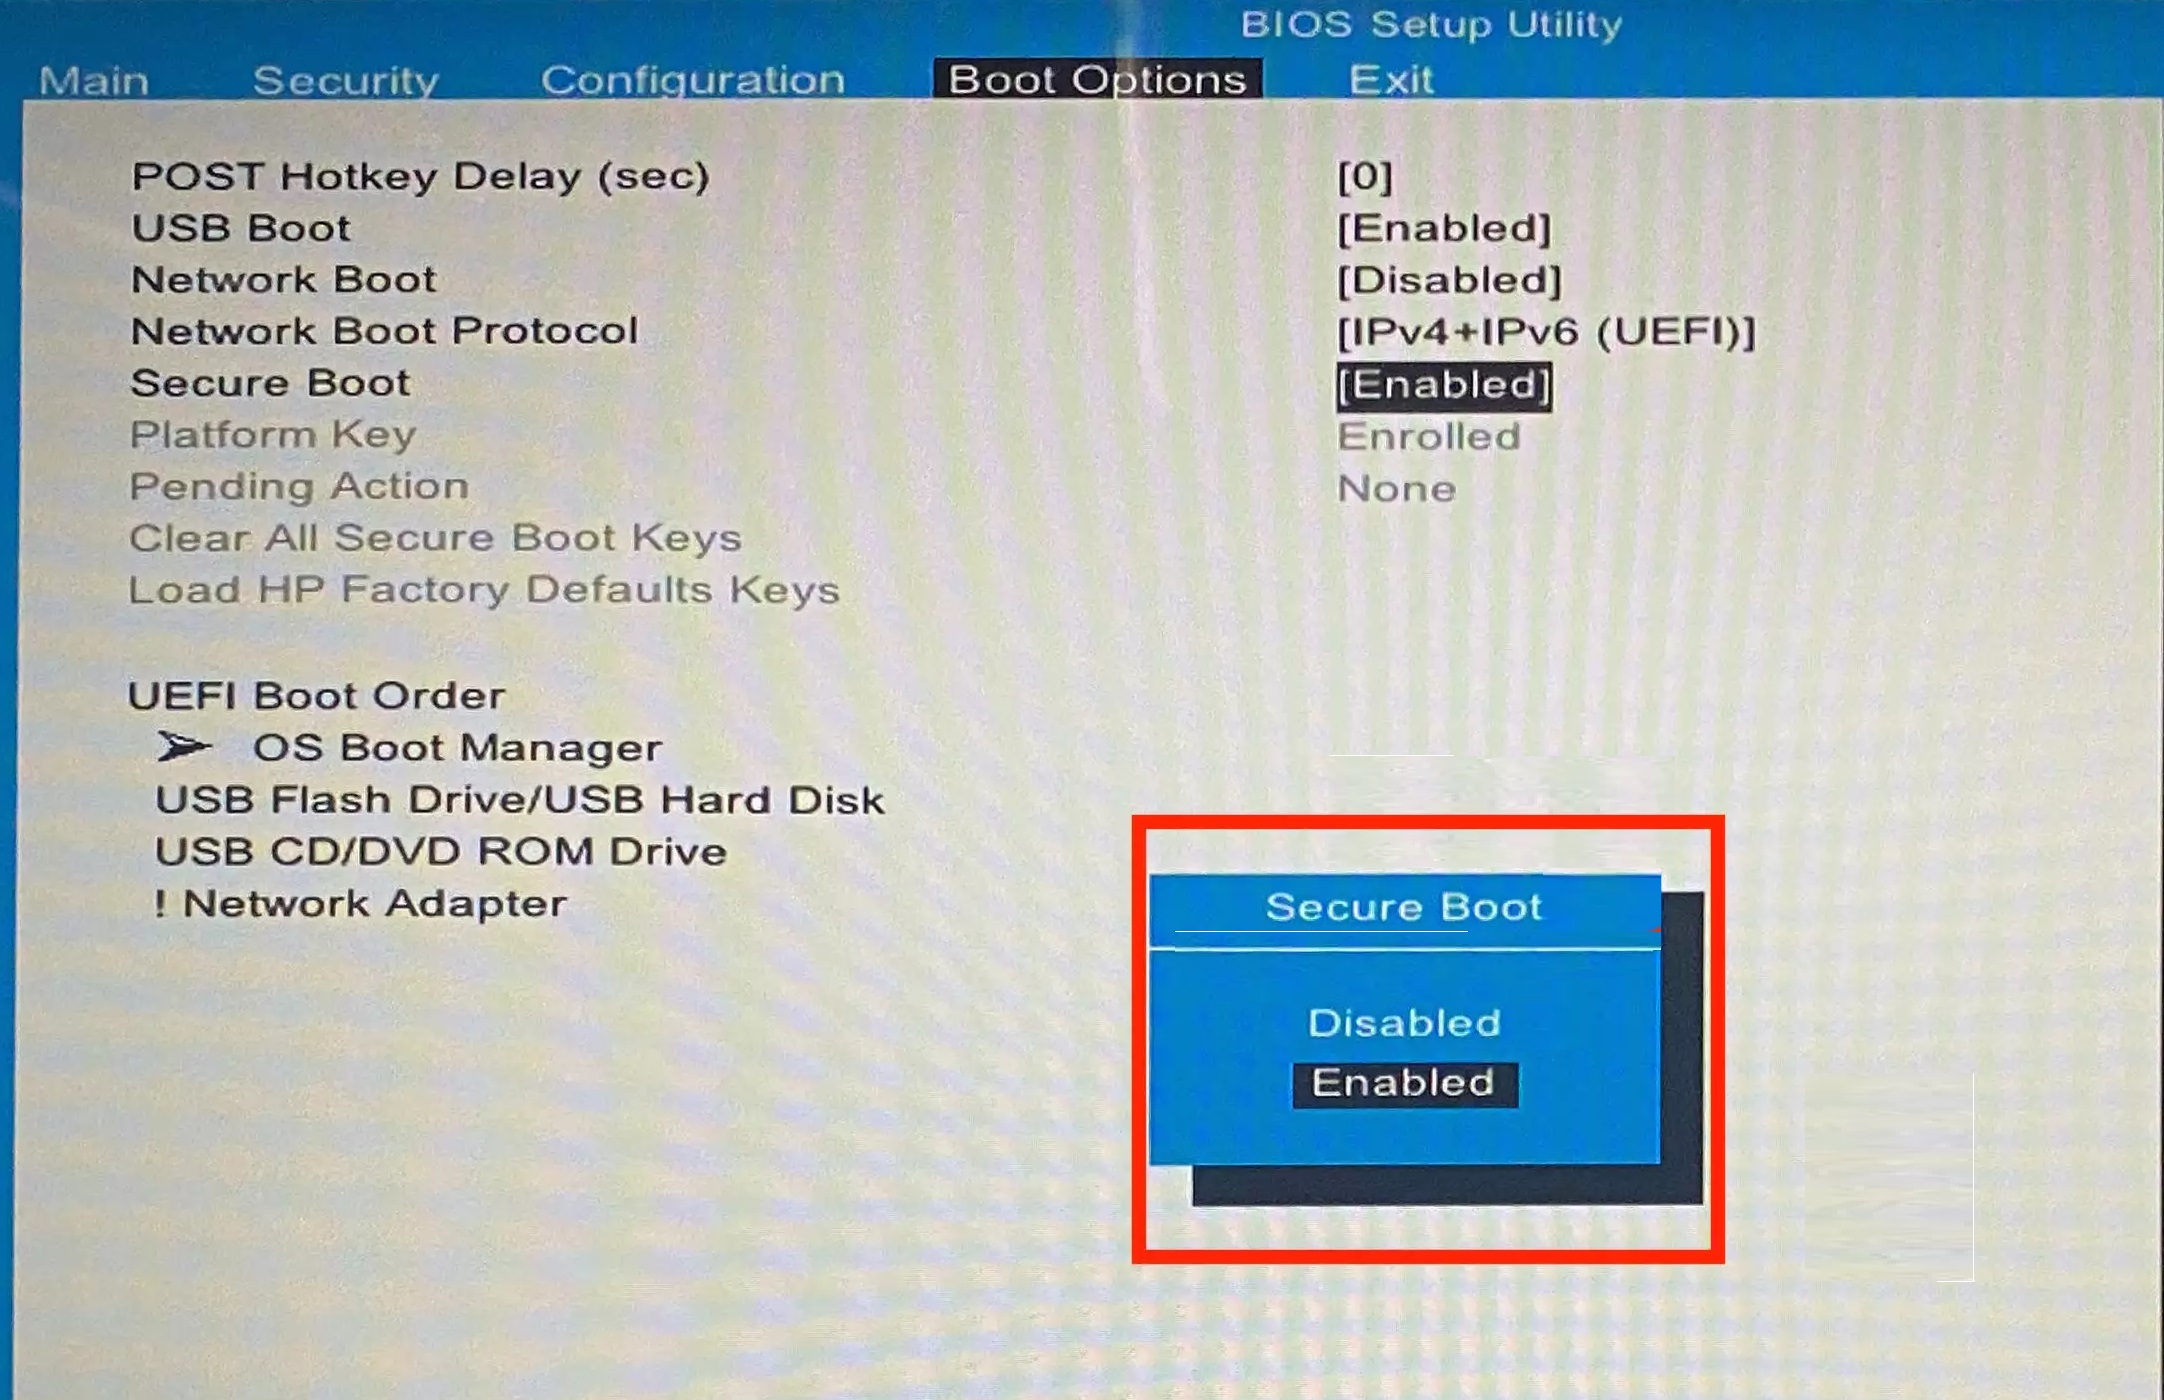
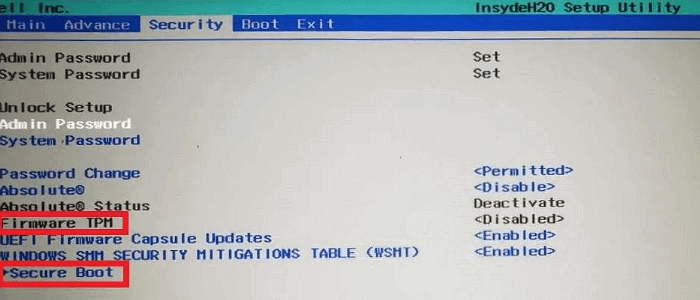
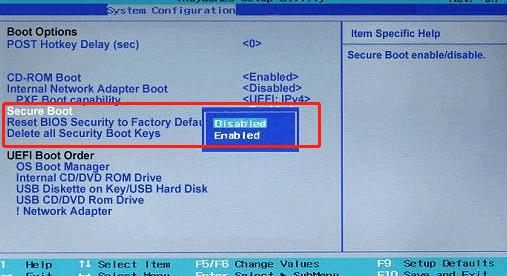
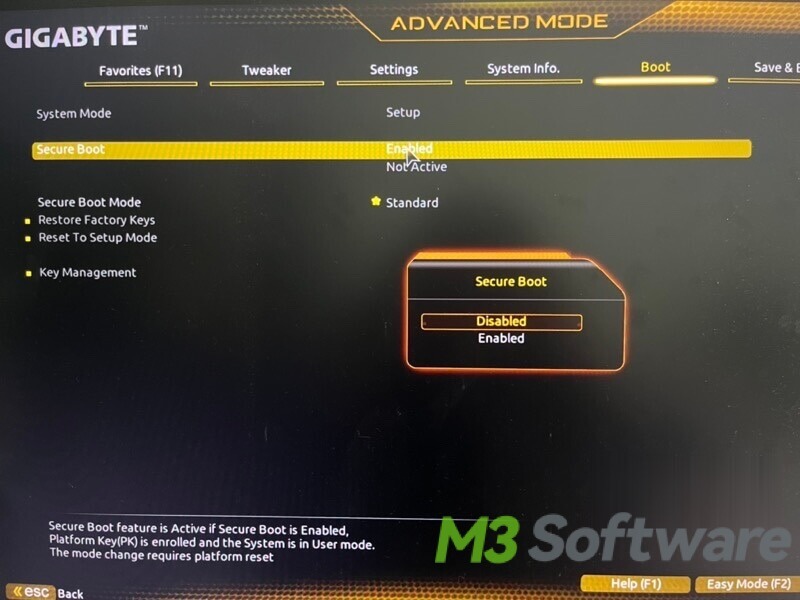
- Once in the UEFI/BIOS setup utility, look for the 'Security' or 'Boot' tab. The exact location of the Secure Boot setting can vary, but it's often found here.
- Change the Secure Boot mode to 'Disabled' or 'Other OS'. Save your changes and exit the UEFI/BIOS setup utility. Your computer will restart, and Secure Boot will be disabled.
Method 2: Using the Command Prompt
If you're unable to access the UEFI/BIOS setup utility, you can use the Command Prompt to disable Secure Boot. Here's how:
- Boot into Windows Recovery Environment by restarting your computer and pressing the power button repeatedly until you see the 'Please wait...' screen. Then, press and hold the power button until your computer turns off. Repeat this process three times. On the fourth time, Windows will boot into the recovery environment.
- In the recovery environment, select 'Troubleshoot' > 'Advanced options' > 'Command Prompt'.
- In the Command Prompt, type the following command and press Enter:
bcdedit /set {bootmgr} path \EFI\Microsoft\Boot\bootmgfw.efi - Then, type the following command and press Enter:
bcdedit /set {default} bootmenupolicy legacy - Finally, type the following command and press Enter:
bcdedit /set {default} bootsectorsignature 32 - Restart your computer. Secure Boot should now be disabled.
Disabling BitLocker
Disabling BitLocker is a bit simpler than disabling Secure Boot. Here's how:
- Press the Windows key + X on your keyboard and select 'Control Panel'.
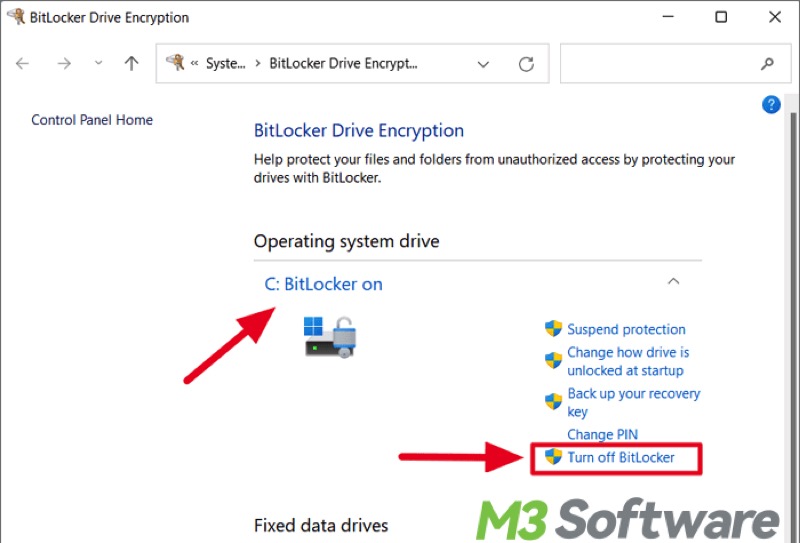
- In the Control Panel, click on 'System and Security' > 'BitLocker Drive Encryption'.
- Select the drive you want to decrypt and click 'Turn off BitLocker'.
- Confirm that you want to turn off BitLocker and click 'Yes'. BitLocker will begin the decryption process. This can take a while, so be patient.
And there you have it! You've successfully disabled both Secure Boot and BitLocker. Remember, disabling these features can make your system less secure, so only do so if you understand the risks and have a valid reason. Always ensure you're following best security practices to protect your data.