Streamlining Your IT Infrastructure: A Comprehensive Guide to Change CN Active Directory
In the dynamic world of IT, Active Directory (AD) is a cornerstone for managing and securing network resources. One common task in AD administration is changing the Common Name (CN) of an object. This article walks you through the process, its implications, and best practices to ensure a smooth transition.
Understanding Active Directory and CN
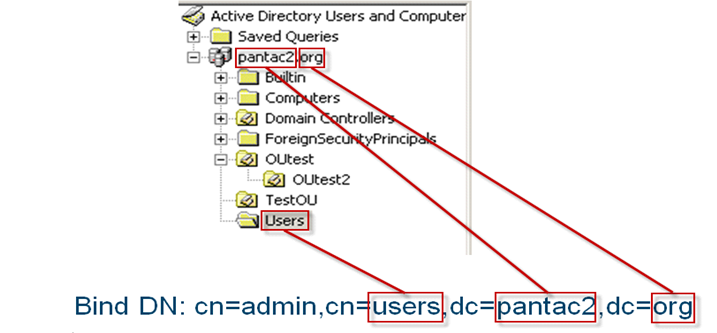
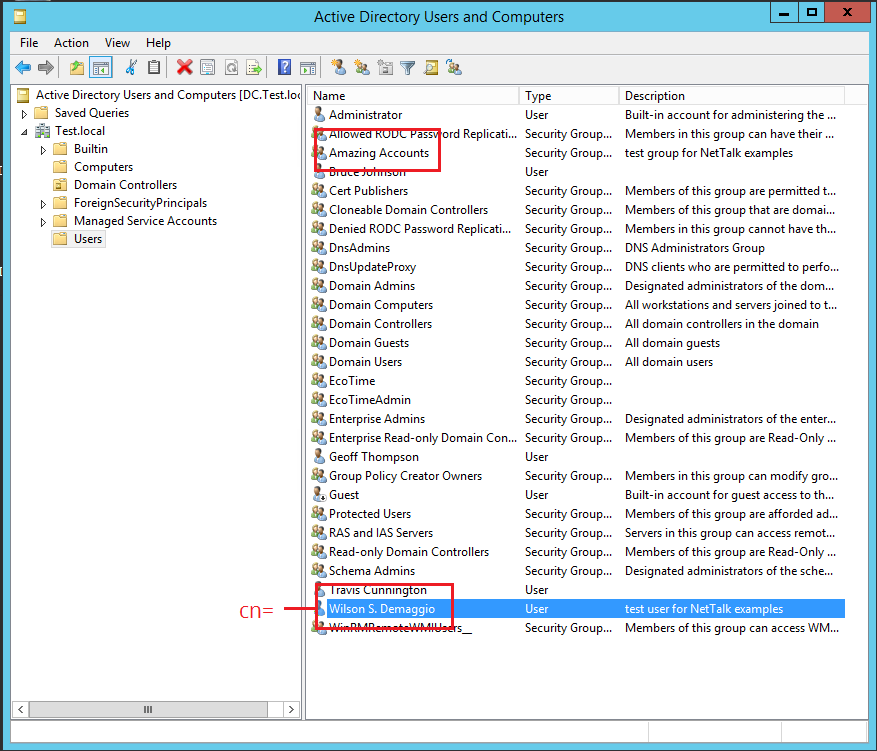
Active Directory is a directory service created by Microsoft for Windows domain networks. It stores and manages information about network resources and users. The Common Name (CN) is a unique identifier for an object in AD, typically used in the display name. Changing the CN can be necessary due to renaming, mergers, or other organizational changes.
Preparation: Assess the Impact
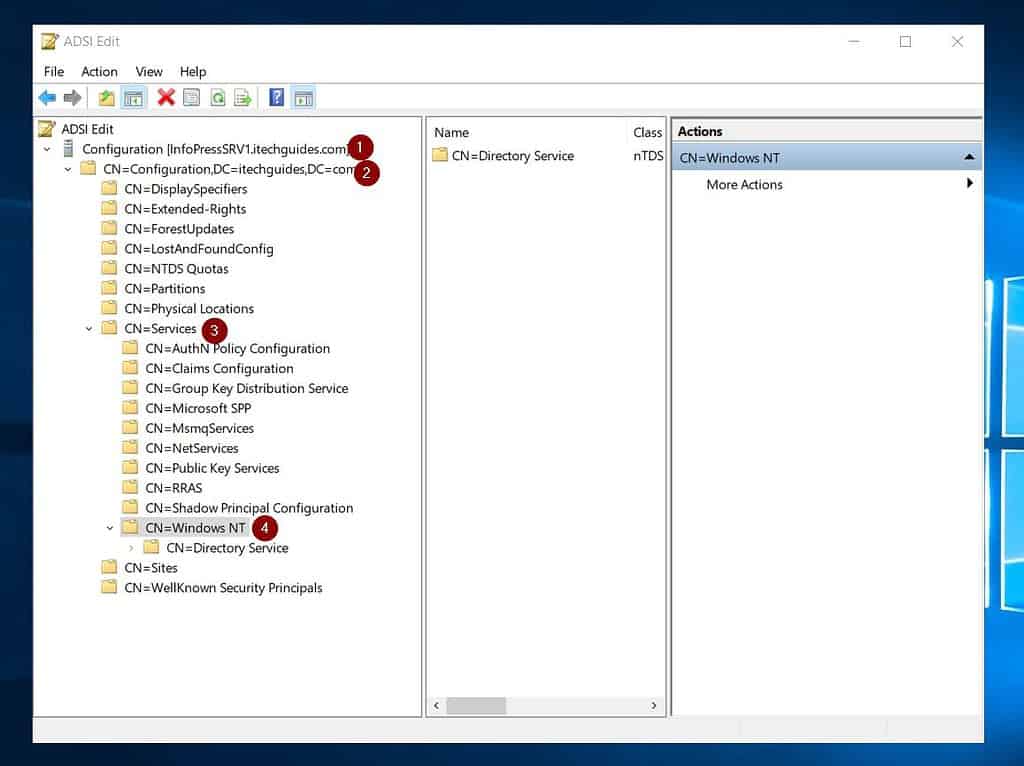
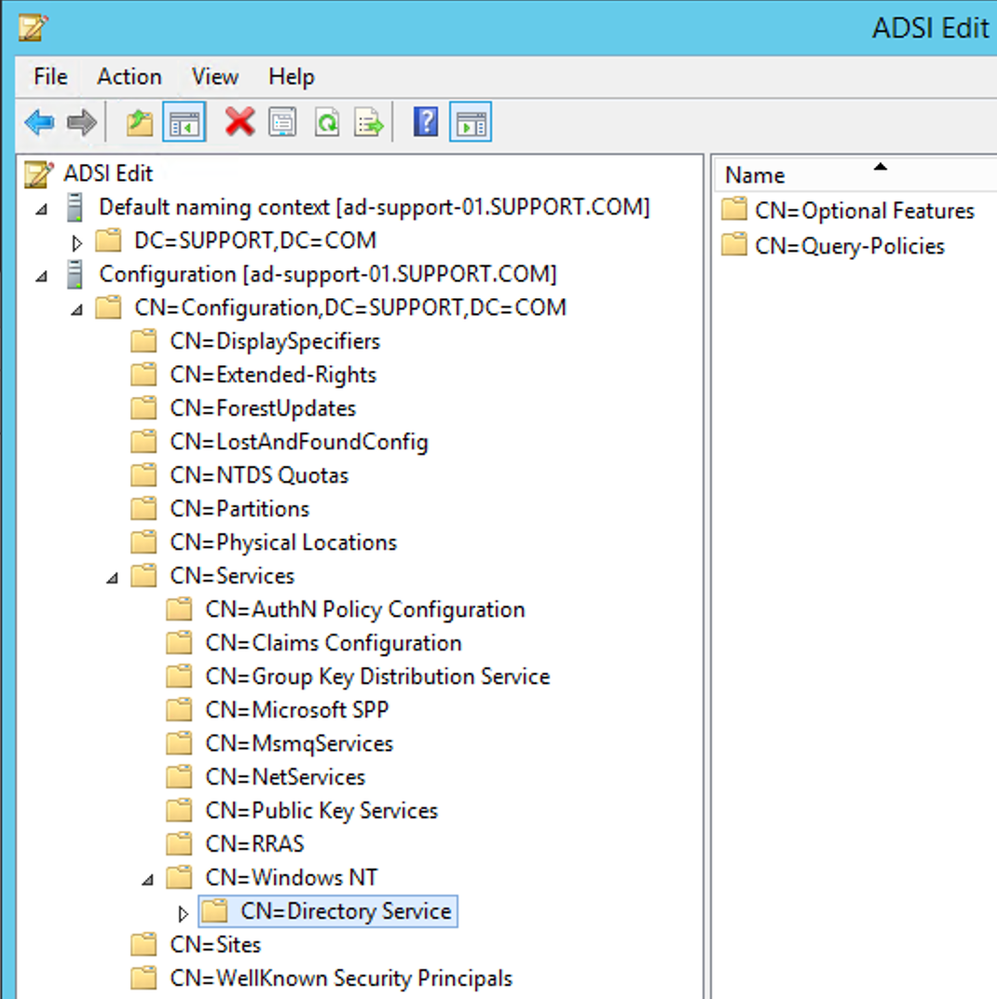
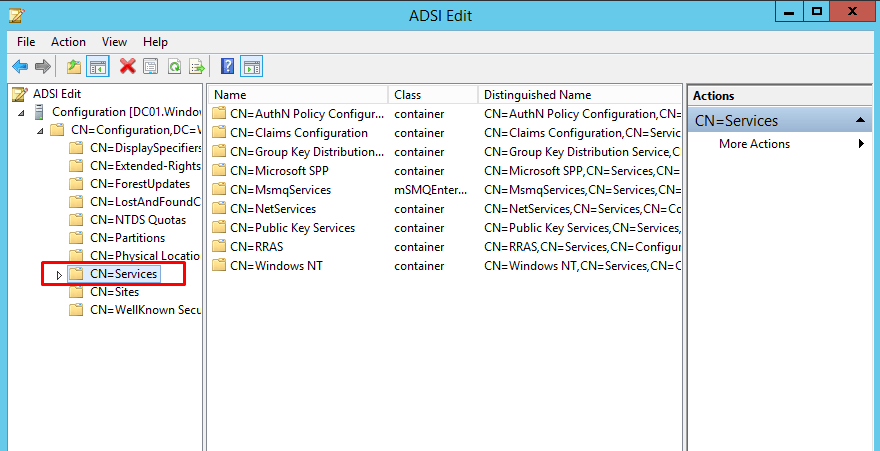
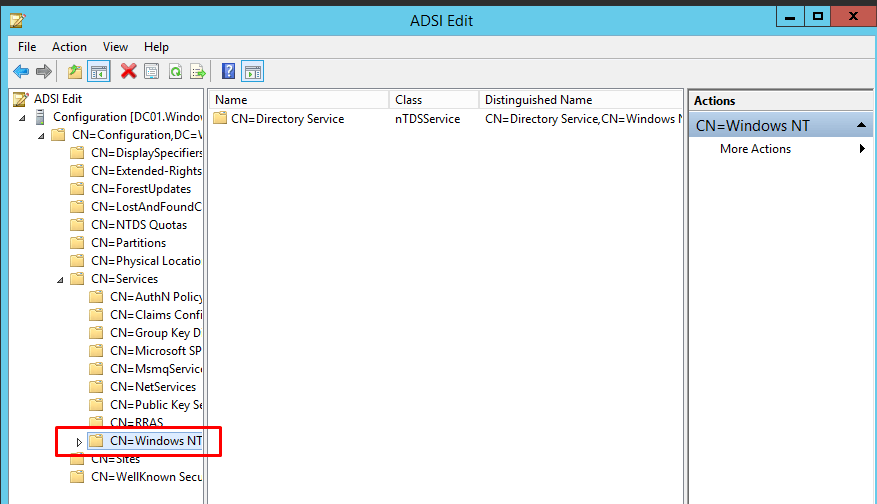
Before proceeding, assess the impact of changing the CN. This includes understanding how the change will affect other AD objects, Group Policy Objects (GPOs), and applications that rely on the current CN. Tools like Microsoft's Active Directory Service Interfaces (ADSI) Edit or third-party software can help with this.
Method 1: Using Active Directory Users and Computers
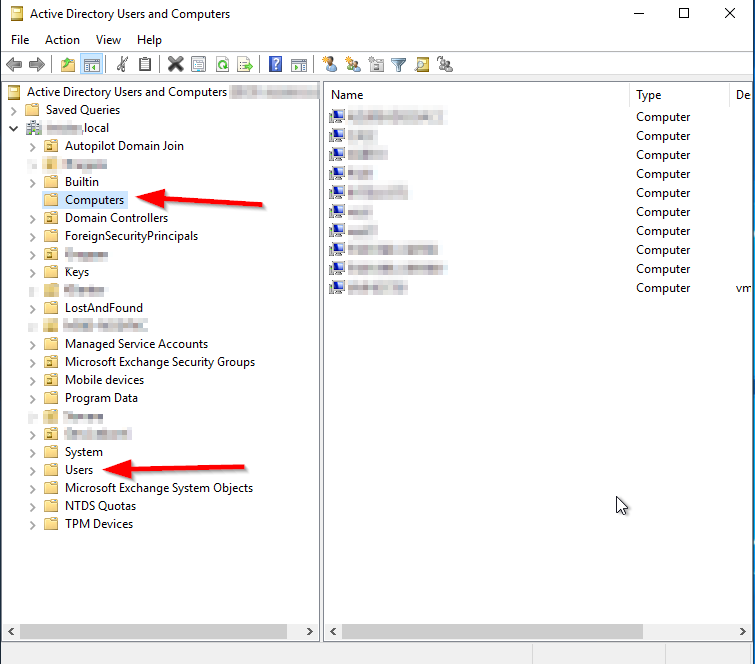
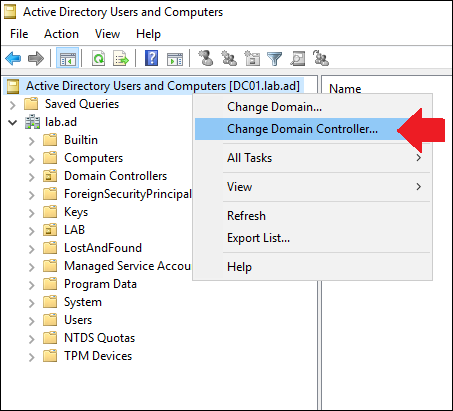
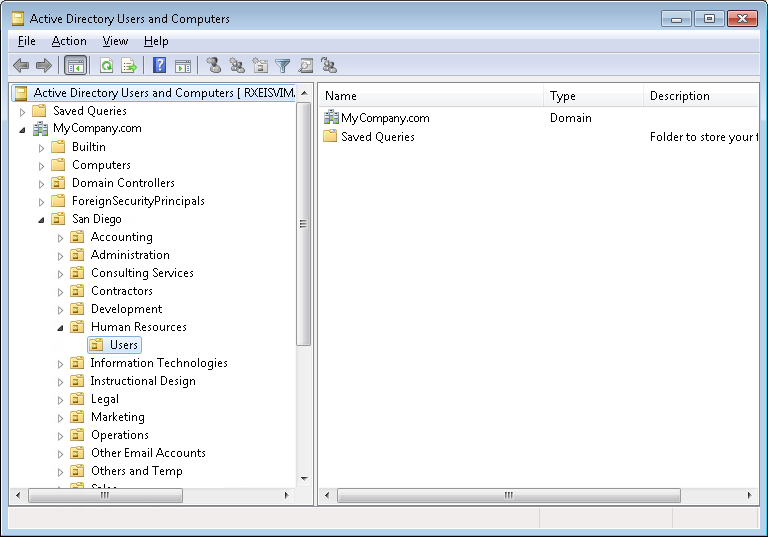
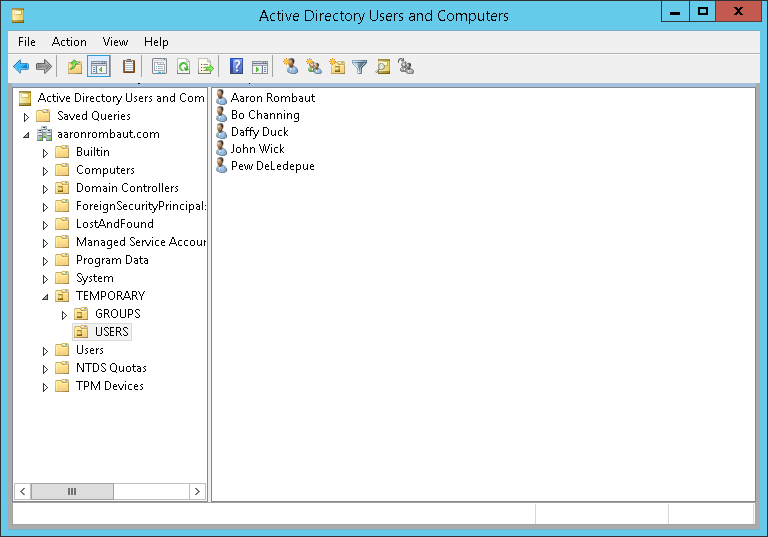
For simple changes, the built-in Active Directory Users and Computers snap-in can be used.
- Right-click the object, select Rename.
- Enter the new CN and press Enter.
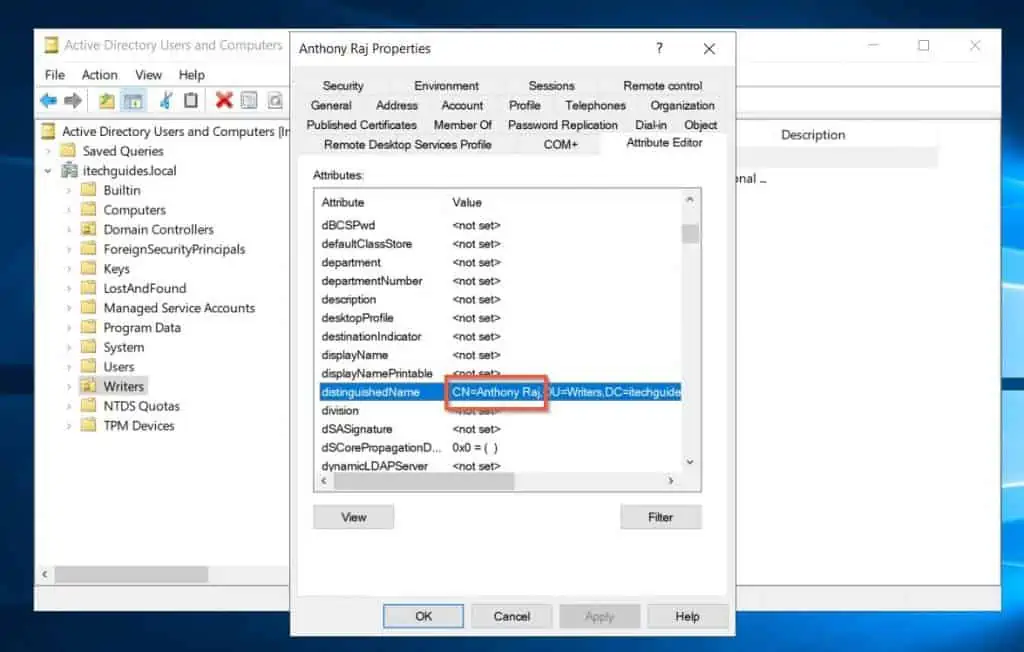
- Confirm the change by clicking Yes to update the distinguished name (DN).
Method 2: Using PowerShell
For bulk changes or complex scenarios, PowerShell is a powerful tool.
Here's a simple example of changing the CN of a user:

Set-ADUser -Identity "Old CN" -NewName "New CN"Post-Change Verification and Cleanup
After changing the CN, verify the change in AD Users and Computers. Also, check if the change propagated to other AD-integrated applications and services. If the old CN is no longer needed, consider deleting the old object to avoid confusion and potential security risks.
Best Practices and Considerations
| Best Practice | Consideration |
|---|---|
| Test the change in a lab environment before implementing it in production. | Ensures minimal disruption to live systems and users. |
| Update any references to the old CN in GPOs, scripts, and applications. | Prevents broken links and unexpected behavior. |
| Monitor the change using AD replication tools and event logs. | Ensures the change propagates to all domain controllers. |
Changing the CN in Active Directory is a common task, but it's crucial to understand the implications and follow best practices to avoid potential issues. By carefully planning and executing the change, you can ensure a smooth transition with minimal disruption to your IT infrastructure.