Understanding the landscape of modern communication security begins with acknowledging the integral role that messaging platforms play in our daily lives. From coordinating professional projects to sharing intimate moments with loved ones, these digital channels have become the primary vessels for our most personal and professional interactions. Consequently, the interest in accessing these conversations is often rooted in a desire for transparency, whether that stems from a parent safeguarding a child's well-being or a partner navigating the complexities of trust. This exploration delves into the methodologies employed to bypass these security measures, offering a perspective on the vulnerabilities inherent in seemingly impenetrable digital fortresses.
Decoding the Digital Lock: The Psychology of Access
The motivation behind attempting to infiltrate a private messenger account is as varied as the individuals who pursue it. In many instances, the driving force is a perceived threat to safety or fidelity, pushing concerned parties to seek answers in the most direct manner possible. The immediacy and intimacy of text-based communication create an environment where secrets are easily exchanged, making the platform a focal point for suspicion. While the ethics of such intrusion are perpetually debated, the technical mechanisms required to execute this access are grounded in standard digital protocols that have been repurposed for covert operations. The psychological weight behind these actions underscores the high stakes involved in the digital privacy battle.
Method One: Exploiting the Web Interface
One of the most straightforward approaches to bypassing security does not require advanced coding skills but rather a keen eye for opportunity. Most modern messaging clients are designed to operate seamlessly across devices, including web browsers. This functionality relies on a temporary authentication process where a user scans a QR code to link their session. An individual with physical access to the target device can open the web version, scan the code, and effectively mirror the entire conversation history on their own screen. This method is a snapshot in time, requiring the physical phone to remain present, but it provides immediate access to real-time and historical messages without the need to infiltrate the cloud servers storing the data.

Executing the Browser-Based Intrusion
To utilize this method effectively, the process involves gaining fleeting possession of the device. Once unlocked, the user navigates to the official web portal of the messaging application. By selecting the "link a device" option, the interface presents a unique QR code. Using the secondary device of the observer, the camera is directed toward this code, establishing a synchronized session. The key to success lies in speed and discretion; the target user must remain unaware to prevent the session from being terminated. This tactic leverages the inherent trust we place in the browsers and devices we use daily, turning a standard feature into a window into private life.
Method Two: The Server-Side Compromise
For those seeking a more permanent solution that does not require physical proximity, the battle moves to the digital infrastructure where data is stored. Every message sent through a cloud-based messenger is archived on remote servers, protected by layers of encryption and guarded by complex login credentials. The most direct route to accessing this archive is through a Server Compromise. This involves sophisticated techniques such as phishing attacks, where the target is tricked into handing over their username and password, or exploiting vulnerabilities within the service provider's infrastructure. Successfully executing this maneuver grants the attacker the master keys to the kingdom, allowing them to decrypt and view the entire communication history from any device, at any time.
Navigating the Technical Hurdles
Unlike the physical method, this approach is constrained by robust security measures implemented by tech companies. End-to-end encryption means that even if a server is breached, the data might remain unreadable without the specific decryption keys held on the user's device. Hackers often pivot to social engineering, crafting convincing fake login pages to steal credentials rather than attacking the encryption itself. The complexity of this method is significantly higher, requiring knowledge of network security, coding, and the patience to navigate countermeasures deployed by security teams. The reward, however, is total and uninterrupted access to the target's digital communications.
Method Three: Utilizing Third-Party Software
Recognizing the demand for surveillance, a market has emerged offering specialized tools designed for monitoring digital activity. These applications, often disguised as legitimate utilities or security software, can be installed on a target device either through physical access or by exploiting vulnerabilities in app stores. Once installed, these programs operate in the background, silently logging every keystroke, capturing screenshots, and forwarding message content to a remote server controlled by the installer. The sophistication of these tools allows them to evade detection by antivirus software, making them a preferred choice for individuals who lack the technical expertise to execute a server breach but still require persistent access to the messaging platform.
Evaluating the Risks and Viability
While the effectiveness of spy software is high, the risks involved are substantial. Installing unauthorized software on a device is a clear violation of privacy laws in most jurisdictions and can constitute a criminal offense. Furthermore, the installation process itself often requires the device to be jailbroken or rooted, which can destabilize the operating system and expose the device to further malware. The trust placed in the software vendor is also a critical factor; the user must believe that the tool itself is not harvesting data for malicious purposes. The trade-off between the desire for access and the legal and technical repercussions is a critical consideration that cannot be overlooked.
Defending the Fortress: Recognizing the Threat
Understanding how these incursions occur is the first step in preventing them. Vigilance is the cornerstone of digital defense. Users should be wary of suspicious links, unexpected file attachments, and requests for personal information, as these are common vectors for credential theft. Keeping operating systems and applications updated ensures that known security vulnerabilities are patched promptly. Employing strong, unique passwords combined with two-factor authentication adds additional layers of complexity that deter opportunistic hackers. By adopting a proactive security posture, individuals can significantly reduce the attack surface available to those seeking unauthorized access.
The Ethical and Legal Boundary
It is imperative to address the legal implications that surround the act of accessing someone else's private communications without consent. In virtually every jurisdiction, intercepting digital communications is a serious criminal offense, often carrying severe penalties including fines and imprisonment. The intent behind the action does not negate the violation; curiosity or concern does not serve as a legal defense. The boundary between protection and infringement is a strict one, and crossing it results in a shift from the role of a concerned individual to that of a perpetrator of cybercrime. Any exploration of these techniques must be tempered with the understanding that knowledge should be used to secure one's own digital life, not to violate the privacy of others.
How To Hack Messenger? 100% Working Without Password | MobileSpy
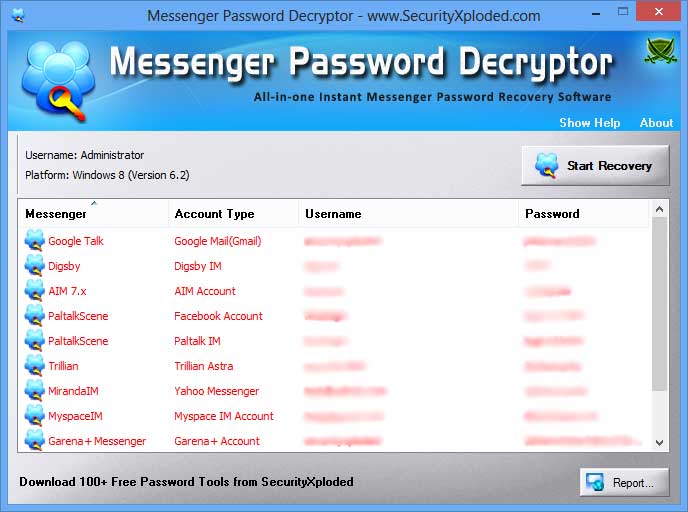
MessengerPasswordDecryptor showing recovered passwords

Hack messenger password - volwind

How Can You Tell if Your Messenger Is Hacked? | ITGeared

google hack facebook password

Nigeria | How to recover a hacked Facebook messenger account
belguide - Blog
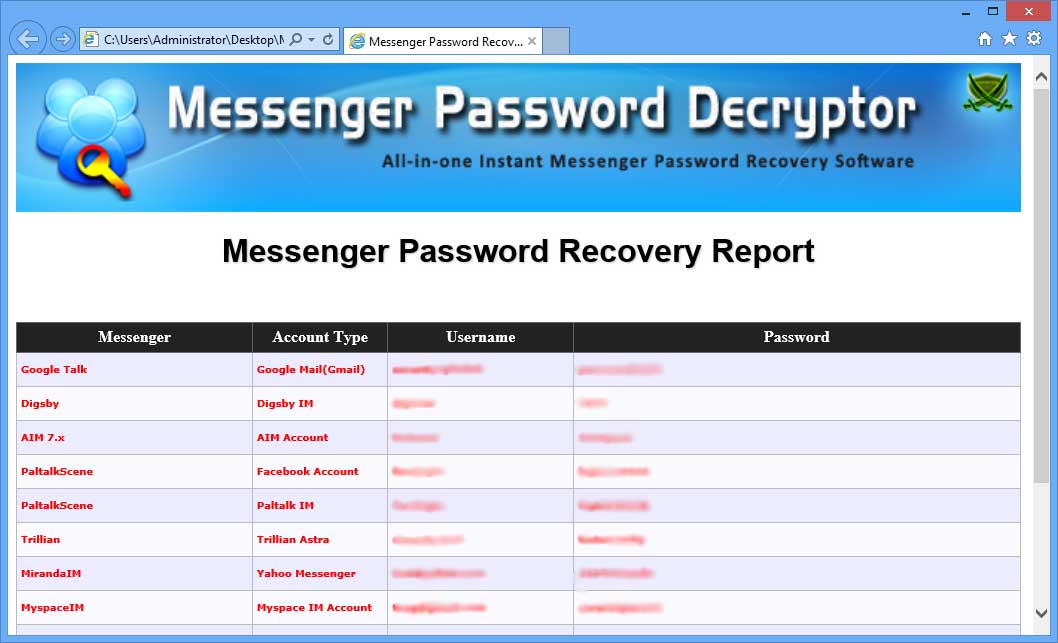
Exported IM Accounts to HTML
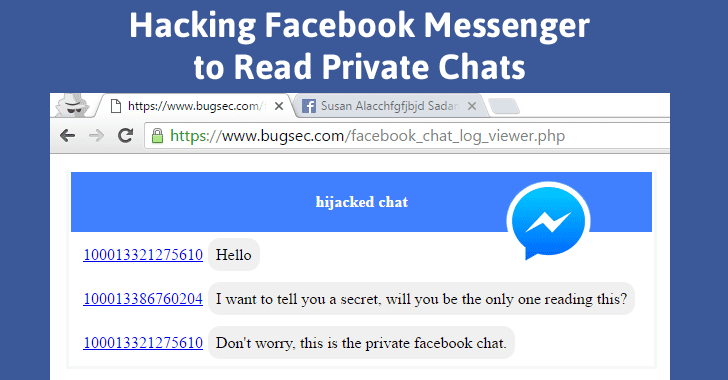
Simple Bug allows Hackers to Read all your Private Facebook Messenger Chats

Facebook Ad Spy: Top Four Ways To Hack Facebook Messenger

Hackers Can Hack Facebook Messenger App To Read Or Alter Messages ...

Messenger bị hack: Nguyên nhân & Cách lấy lại đơn giản

SpyX blog | step to step guide

Facebook Messenger Hack Fix at Mark Cox blog
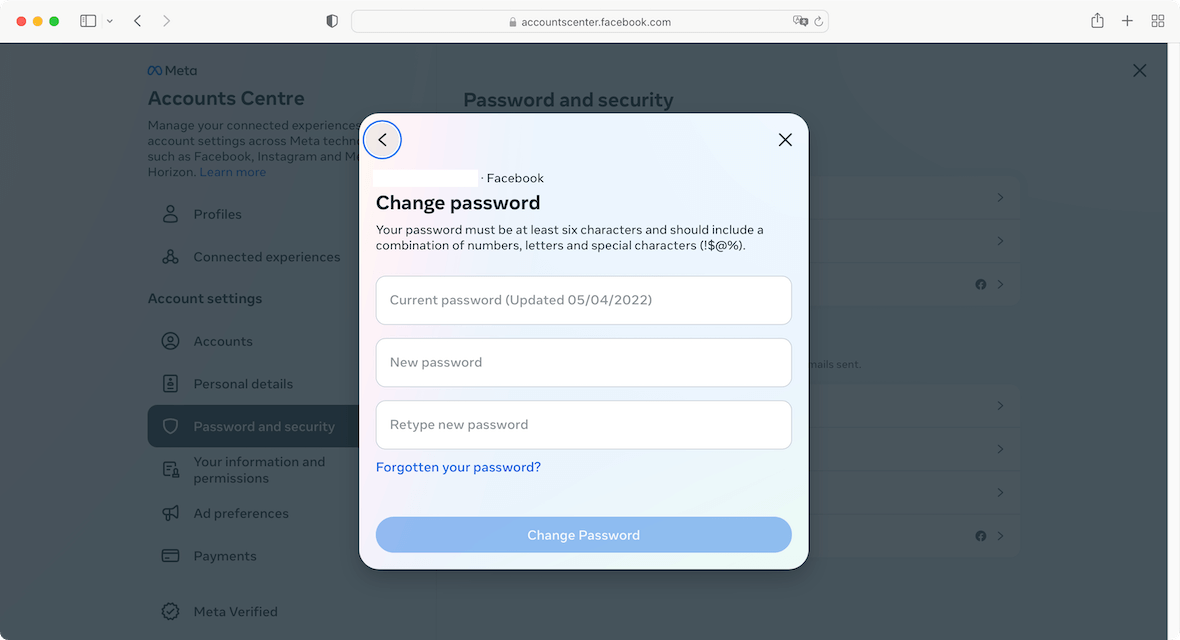
Is your Messenger hacked? Here's how to tell and what to do
How To See Messenger Password - YouTube

How To See Your Messenger Password if You Forgot it (2024) | Find ...

How To See Messenger Password - YouTube

How to See Messenger Password - YouTube

How to Hack Messenger? | Solved