Overview of Network Based Policies In Cloudflare Gateway
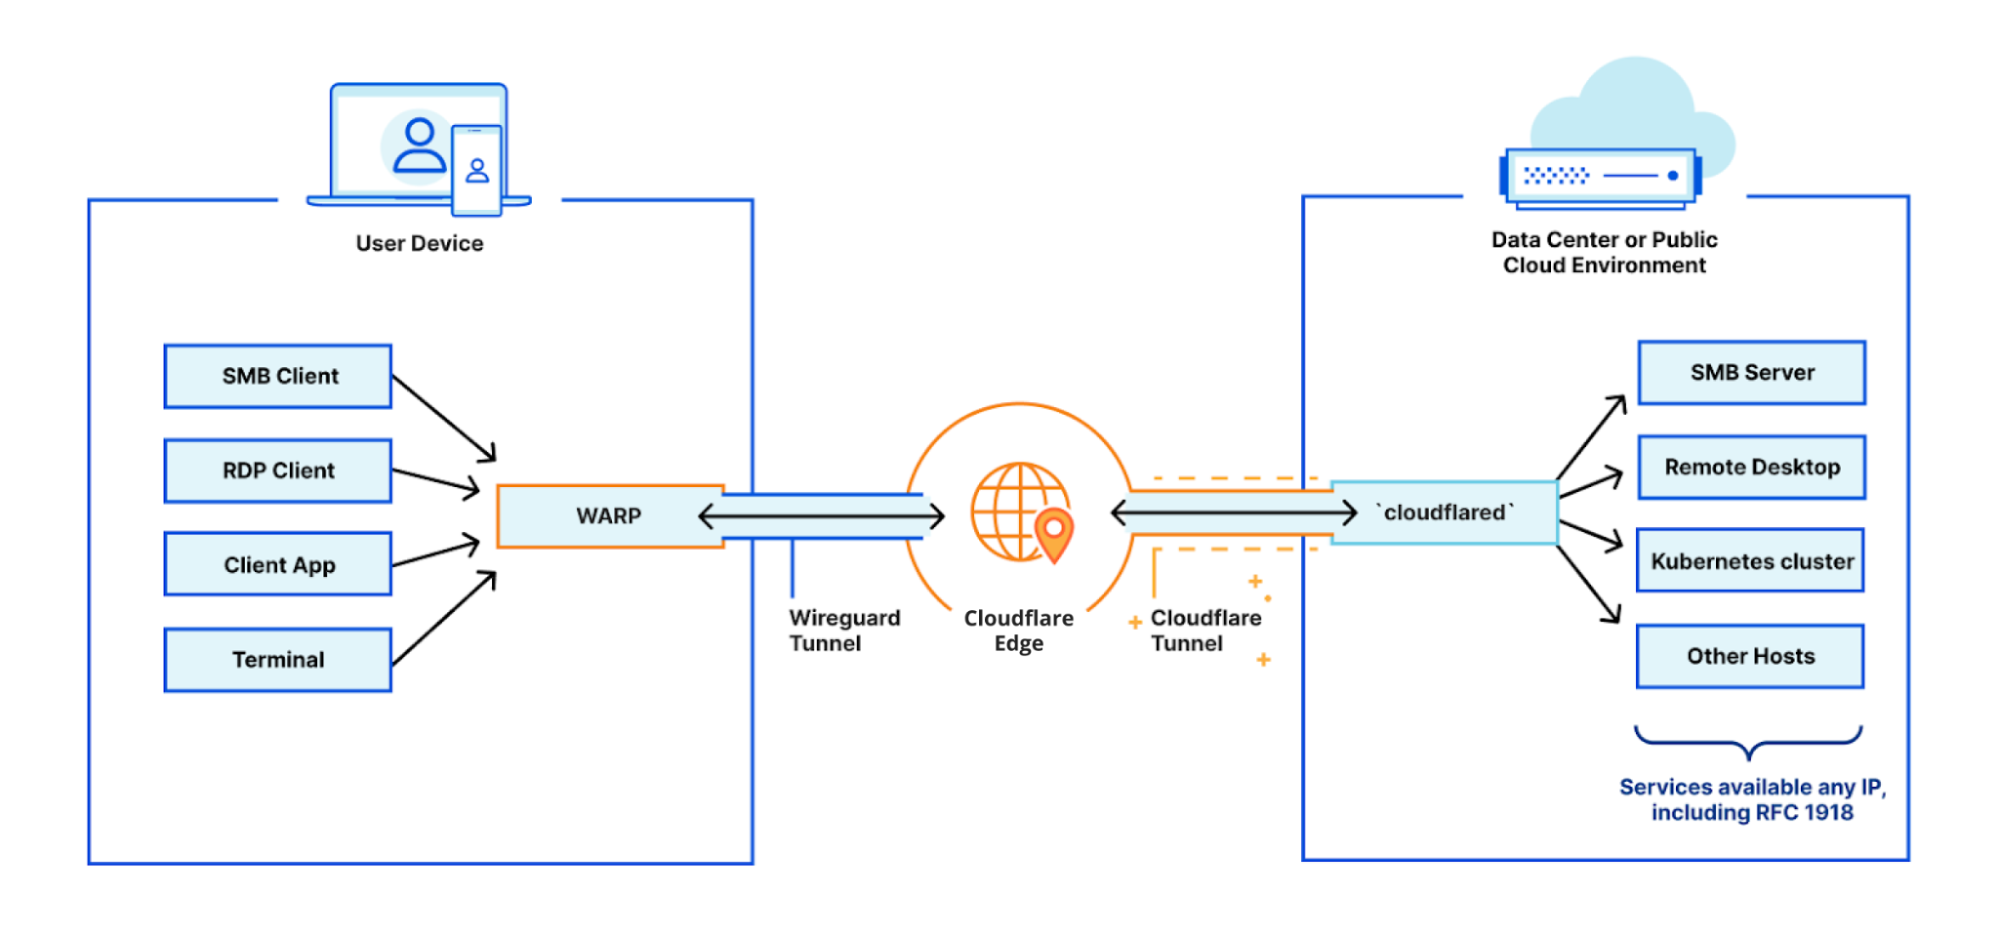
Over the past year, Cloudflare Gateway has grown from a DNS filtering solution to a Secure Web Gateway . That growth has allowed customers to protect their organizations with fine-grained identity- based HTTP policies and malware protection wherever their users are.

Now administrators can configure identity- based rules that apply to private networks built on Cloudflare . What's next? We're laser-focused on our Cloudflare One goal to secure organizations regardless of how their traffic gets to Cloudflare . Applying network policies to both WARP users and routing between private networks is part of that ...
Gateway Rules

Gateway Rules are a core component of the Cloudflare Zero Trust Gateway that allow administrators to define policies for controlling and securing network traffic. These rules determine how traffic should be filtered, monitored, and routed based on various criteria including network traffic characteristics, user identity, and device posture.
Over the past year, Cloudflare Gateway has grown from a DNS filtering solution to a Secure Web Gateway . That growth has allowed customers to protect their organizations with fine-grained identity- based HTTP policies and malware protection wherever their users are.

Useful Notes on Network Based Policies In Cloudflare Gateway
Today we're excited to announce the ability for administrators to configure network-based policies in Cloudflare Gateway . Like DNS and HTTP policy enforcement, organizations can use network selectors like IP address and port to control access to any network origin.
Configure Network policies in Gateway . Turn on Display block notification for Cloudflare One Client to display notifications for Gateway block events. Blocked users will receive an operating system notification from the Cloudflare One Client with a custom message you set. If you do not set a custom message, the Cloudflare One Client will display a default message. Custom messages must be 100 ...

Gateway Policies and Enforcement
The system enforces policies at DNS, Network , and HTTP levels with strict ordering rules that determine evaluation precedence. Policy enforcement integrates with WARP client modes, device posture checks, and identity providers to enable context-aware access control. Policy Evaluation Hierarchy Gateway Order of Enforcement (as of 2025-07-14)
With Cloudflare Zero Trust, you can configure policies to control network -level traffic leaving your endpoints. Using network selectors like IP addresses and ports, your policies will control access to any network origin. Because Cloudflare Zero Trust integrates with your identity provider, it also gives you the ability to create identity- based network policies . This means you can now control ...
Gateway policies Cloudflare Zero Trust docs
Cloudflare Gateway , our comprehensive Secure Web Gateway , allows you to set up policies to inspect DNS, Network , HTTP, and Egress traffic.
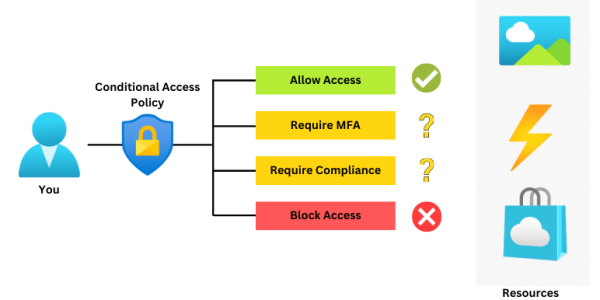
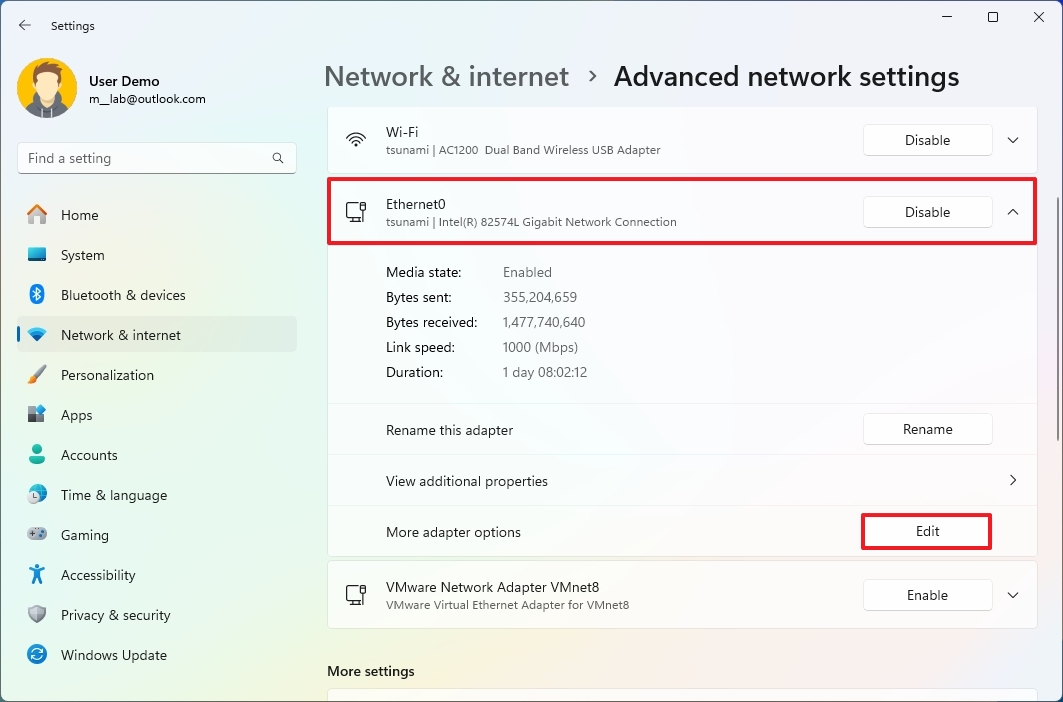
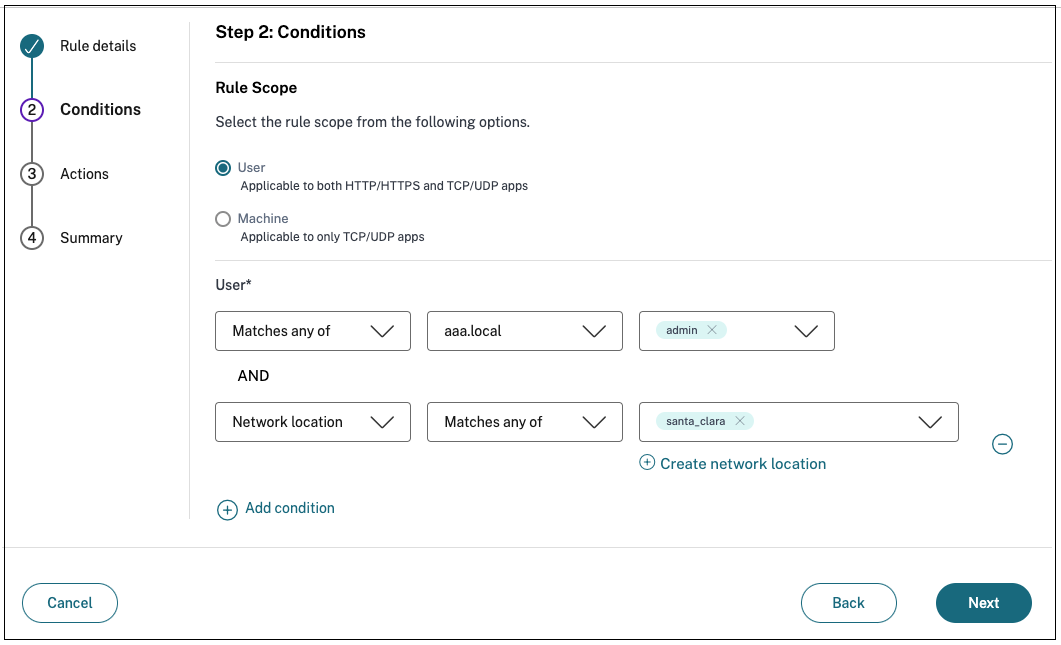
This guide provides comprehensive best practices for managing network rules in Cloudflare Zero Trust Gateway , now that WARP clients are actively generating network traffic. These rules complement your existing DNS filtering rules with network -level security controls.