Project overview: httrack
High level conclusions
Reachability and coverage overview
Project functions overview
The following table shows data about each function in the project. The functions included in this table correspond to all functions that exist in the executables of the fuzzers. As such, there may be functions that are from third-party libraries.
For further technical details on the meaning of columns in the below table, please see the Glossary .
| Func name | Functions filename | Args | Function call depth | Reached by Fuzzers | Runtime reached by Fuzzers | Combined reached by Fuzzers | Fuzzers runtime hit | Func lines hit % | I Count | BB Count | Cyclomatic complexity | Functions reached | Reached by functions | Accumulated cyclomatic complexity | Undiscovered complexity |
|---|
Fuzzer details
Fuzzer: fuzz-codepage
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
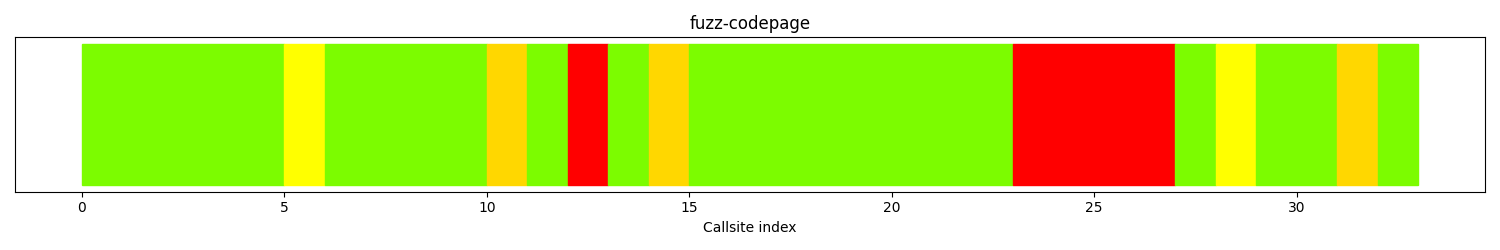
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 5 | 15.1% |
| gold | [1:9] | 3 | 9.09% |
| yellow | [10:29] | 2 | 6.06% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 23 | 69.6% |
| All colors | 33 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 4 | 22 | hts_codepageToUTF8 | call site: 00022 | log_abort_ |
| 1 | 11 | hts_convertStringToUTF8 | call site: 00011 | strdup |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-codepage.c | 1 |
| fuzz/fuzz.h | 1 |
| src/htscharset.c | 10 |
| src/htssafe.h | 2 |
Fuzzer: fuzz-filters
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 1 | 2.32% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 42 | 97.6% |
| All colors | 43 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1 | 5 | LLVMFuzzerTestOneInput | call site: 00005 | strjoker_bounded |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-filters.c | 1 |
| fuzz/fuzz.h | 1 |
| src/htsfilters.c | 8 |
| src/./htslib.h | 1 |
Fuzzer: fuzz-meta
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 0 | 0.0% |
| gold | [1:9] | 1 | 4.16% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 23 | 95.8% |
| All colors | 24 | 100 |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-meta.c | 1 |
| fuzz/fuzz.h | 1 |
| src/htscharset.c | 6 |
Fuzzer: fuzz-header
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
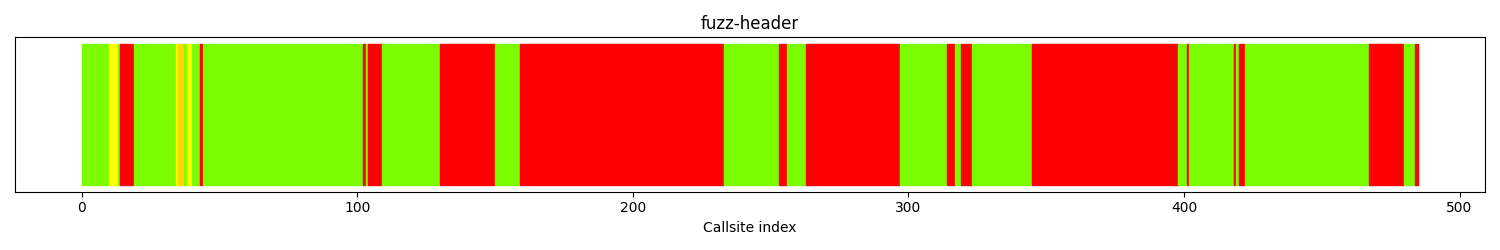
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 221 | 45.5% |
| gold | [1:9] | 2 | 0.41% |
| yellow | [10:29] | 6 | 1.23% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 256 | 52.7% |
| All colors | 485 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 74 | 158 | hts_log_vprint | call site: 00158 | secret_vfprintf |
| 53 | 344 | cookie_domain_is_suffix | call site: 00344 | cookie_remove |
| 34 | 262 | cookie_host | call site: 00262 | hts_convertStringUTF8ToIDNA |
| 20 | 129 | treathead_opt | call site: 00129 | hts_parse_retry_after |
| 13 | 466 | has_login | call site: 00466 | adr_nologin_r |
| 5 | 13 | strcpy_safe_ | call site: 00013 | log_abort_ |
| 5 | 103 | treathead_opt | call site: 00103 | hts_header_param |
| 4 | 318 | treathead_opt | call site: 00318 | cookie_expires_time |
| 3 | 252 | strrchr_limit | call site: 00252 | strchr |
| 3 | 313 | treathead_opt | call site: 00313 | cookie_max_age_time |
| 2 | 419 | cookie_nextfield | call site: 00419 | cookie_delete |
| 1 | 42 | LLVMFuzzerTestOneInput | call site: 00042 | treathead_opt |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-header.c | 2 |
| fuzz/fuzz.h | 1 |
| src/htslib.c | 36 |
| src/./htslib.h | 4 |
| src/./htssafe.h | 11 |
| src/htsurlport.c | 9 |
| src/htscodec.c | 1 |
| src/htsdate.c | 3 |
| src/htscore.c | 2 |
| src/./htsthread.h | 4 |
| src/htsthread.c | 4 |
| src/htsbauth.c | 17 |
| src/htscharset.c | 5 |
| src/punycode.c | 4 |
| src/htspsl.c | 5 |
| src/coucal/coucal.c | 12 |
| src/coucal/murmurhash3.h | 4 |
Fuzzer: fuzz-url
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
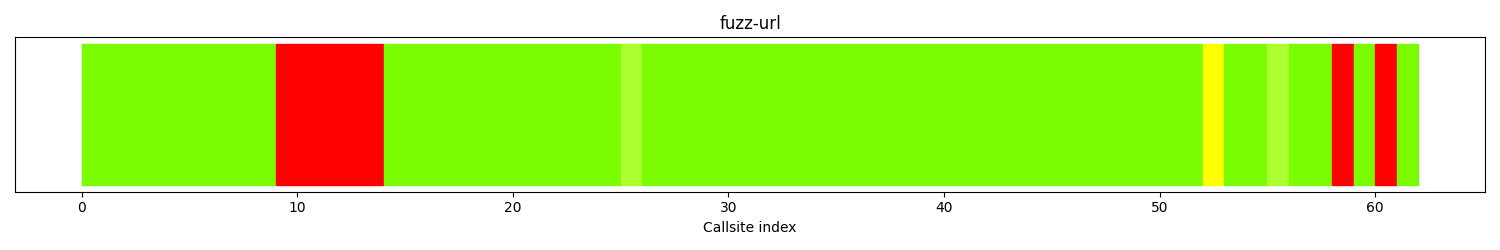
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 7 | 11.2% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 1 | 1.61% |
| greenyellow | [30:49] | 2 | 3.22% |
| lawngreen | 50+ | 52 | 83.8% |
| All colors | 62 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 5 | 8 | strcpy_safe_ | call site: 00008 | log_abort_ |
| 1 | 57 | ident_url_absolute | call site: 00057 | strcpy_safe_ |
| 1 | 59 | ident_url_absolute | call site: 00059 | jump_identification_const |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-url.c | 1 |
| fuzz/fuzz.h | 1 |
| src/htslib.c | 7 |
| src/./htslib.h | 1 |
| src/./htssafe.h | 6 |
Fuzzer: fuzz-unescape
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 29 | 55.7% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 23 | 44.2% |
| All colors | 52 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 22 | 26 | hts_unescapeEntitiesWithCharsetSpecial | call site: 00026 | hts_convertStringFromUTF8Strict |
| 5 | 3 | unescape_http | call site: 00003 | log_abort_ |
| 1 | 24 | hts_isCharsetUTF8 | call site: 00024 | strcasecmp |
| 1 | 50 | hts_unescapeEntitiesWithCharsetSpecial | call site: 00050 | abortf_ |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-unescape.c | 1 |
| fuzz/fuzz.h | 1 |
| src/htslib.c | 4 |
| src/./htssafe.h | 2 |
| src/./htsencoding.h | 2 |
| src/htsencoding.c | 4 |
| src/./htsentities.h | 1 |
| src/htscharset.c | 8 |
Fuzzer: fuzz-idna
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
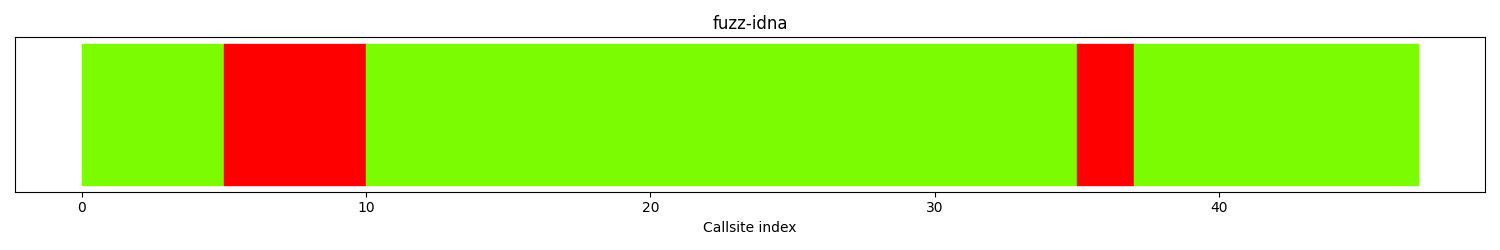
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 7 | 14.8% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 40 | 85.1% |
| All colors | 47 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 5 | 4 | hts_convertStringUTF8ToIDNA | call site: 00004 | log_abort_ |
| 2 | 34 | punycode_decode | call site: 00034 | abortf_ |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-idna.c | 1 |
| fuzz/fuzz.h | 1 |
| src/htscharset.c | 4 |
| src/./htssafe.h | 2 |
| src/htslib.c | 1 |
| src/punycode.c | 6 |
Fuzzer: fuzz-arc
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
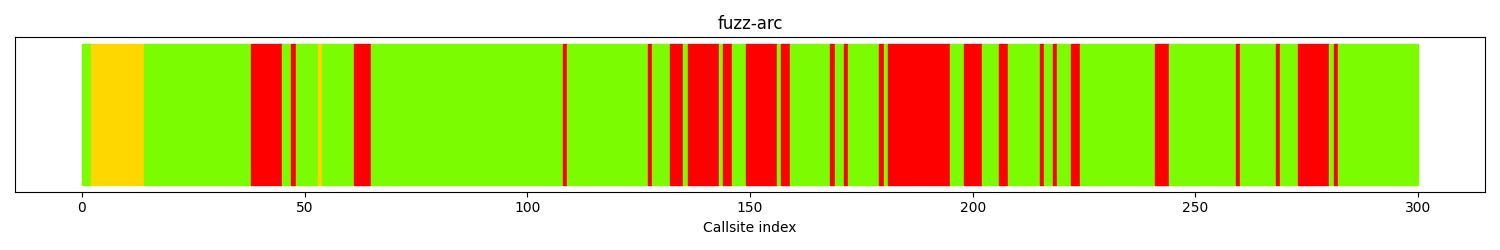
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 75 | 25.0% |
| gold | [1:9] | 13 | 4.33% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 212 | 70.6% |
| All colors | 300 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 14 | 180 | coucal_add_item_ | call site: 00180 | coucal_log_stats |
| 7 | 37 | PT_LoadCache | call site: 00037 | proxytrack_vprint_log |
| 7 | 135 | coucal_log | call site: 00135 | coucal_fail |
| 7 | 148 | coucal_realloc_pool | call site: 00148 | coucal_compact_pool |
| 7 | 272 | coucal_delete | call site: 00272 | coucal_del_name |
| 4 | 60 | vslprintfbuff | call site: 00060 | log_abort_ |
| 4 | 197 | coucal_log_stats | call site: 00197 | coucal_do_warning |
| 3 | 131 | coucal_dup_name_internal | call site: 00131 | coucal_do_crit |
| 3 | 240 | PT_Enumerate | call site: 00240 | fprintf |
| 2 | 143 | coucal_dup_name_internal | call site: 00143 | coucal_do_crit |
| 2 | 156 | coucal_realloc_pool | call site: 00156 | coucal_do_crit |
| 2 | 205 | coucal_write_value | call site: 00205 | coucal_do_crit |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-arc.c | 5 |
| src/coucal/coucal.c | 48 |
| src/proxy/store.c | 13 |
| src/proxy/proxytrack.h | 6 |
| src/htssafe.h | 4 |
| src/coucal/murmurhash3.h | 4 |
| src/htslib.h | 1 |
| src/htsdate.c | 2 |
| src/htsstrings.h | 2 |
Fuzzer: fuzz-sitemap
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 28 | 43.0% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 1 | 1.53% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 36 | 55.3% |
| All colors | 65 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 22 | 37 | hts_unescapeEntitiesWithCharsetSpecial | call site: 00037 | hts_convertStringFromUTF8Strict |
| 5 | 27 | hts_unescapeEntitiesWithCharsetSpecial | call site: 00027 | log_abort_ |
| 1 | 35 | hts_isCharsetUTF8 | call site: 00035 | strcasecmp |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-sitemap.c | 2 |
| src/htssitemap.c | 5 |
| src/htscodec.c | 2 |
| src/htszlib.c | 1 |
| src/htstools.c | 1 |
| src/htsencoding.c | 4 |
| src/./htssafe.h | 2 |
| src/htslib.c | 1 |
| src/./htsentities.h | 1 |
| src/htscharset.c | 8 |
| src/./htsencoding.h | 1 |
| src/./htslib.h | 1 |
Fuzzer: fuzz-entities
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
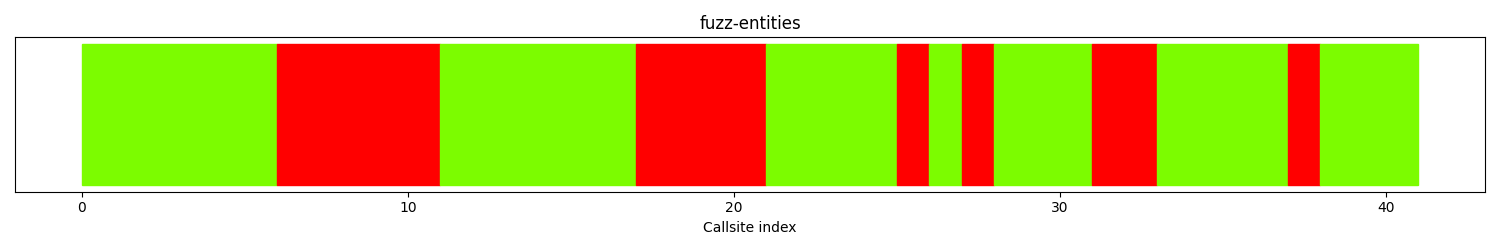
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 14 | 34.1% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 27 | 65.8% |
| All colors | 41 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 5 | 5 | hts_unescapeEntitiesWithCharsetSpecial | call site: 00005 | log_abort_ |
| 4 | 16 | hts_unescapeEntitiesWithCharsetSpecial | call site: 00016 | hts_convertStringFromUTF8Strict |
| 2 | 30 | hts_convertStringCharset | call site: 00030 | realloc |
| 1 | 24 | hts_convertStringFromUTF8 | call site: 00024 | strdup |
| 1 | 26 | hts_convertStringCharset | call site: 00026 | hts_stringMemCopy |
| 1 | 36 | hts_unescapeEntitiesWithCharsetSpecial | call site: 00036 | snprintf |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-entities.c | 1 |
| fuzz/fuzz.h | 1 |
| src/htsencoding.c | 4 |
| src/./htssafe.h | 2 |
| src/htslib.c | 1 |
| src/./htsentities.h | 1 |
| src/htscharset.c | 8 |
| src/./htsencoding.h | 1 |
Fuzzer: fuzz-charset
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
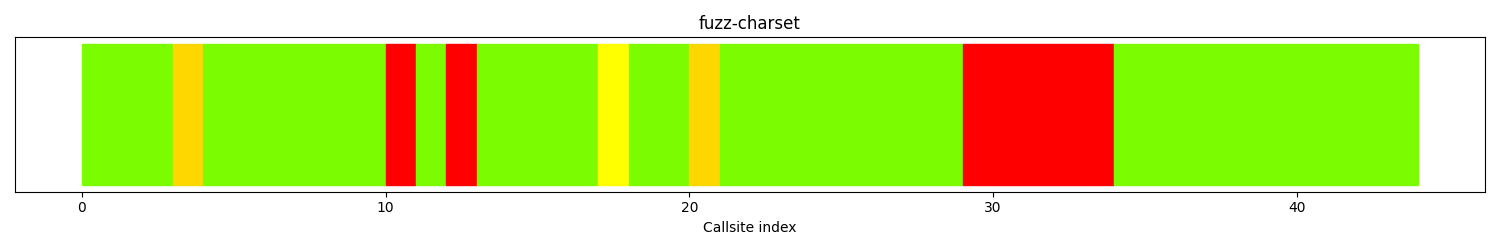
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 7 | 15.9% |
| gold | [1:9] | 2 | 4.54% |
| yellow | [10:29] | 1 | 2.27% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 34 | 77.2% |
| All colors | 44 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 5 | 28 | hts_convertUTF8StringToUCS4 | call site: 00028 | log_abort_ |
| 1 | 9 | hts_convertStringToUTF8 | call site: 00009 | strdup |
| 1 | 11 | hts_convertStringCharset | call site: 00011 | hts_stringMemCopy |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-charset.c | 1 |
| fuzz/fuzz.h | 1 |
| src/htscharset.c | 12 |
| src/./htssafe.h | 2 |
| src/htslib.c | 1 |
Fuzzer: fuzz-singlefile
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
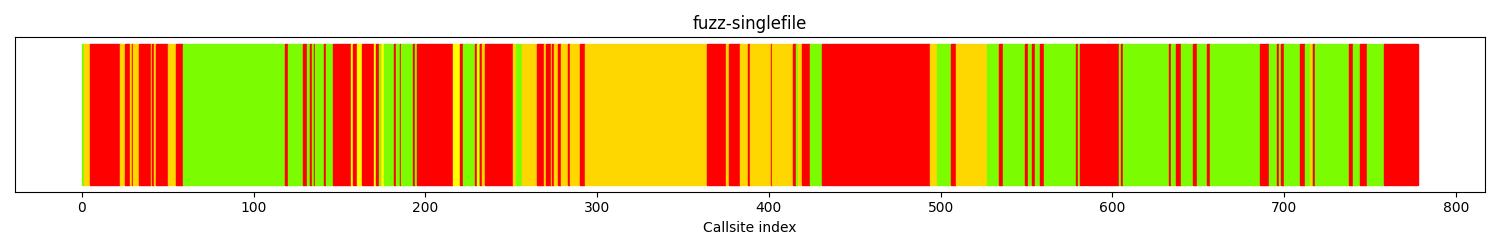
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 298 | 38.3% |
| gold | [1:9] | 173 | 22.2% |
| yellow | [10:29] | 11 | 1.41% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 296 | 38.0% |
| All colors | 778 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 63 | 430 | fspc_count | call site: 00430 | secret_vfprintf |
| 23 | 580 | hts_unescapeEntitiesWithCharsetSpecial | call site: 00580 | hts_convertStringFromUTF8Strict |
| 21 | 194 | coucal_add_item_ | call site: 00194 | coucal_log_stats |
| 20 | 757 | sf_inline | call site: 00757 | sf_append_escaped |
| 17 | 4 | hts_init | call site: 00004 | hts_debug |
| 16 | 234 | coucal_write_value | call site: 00234 | psl_install |
| 11 | 145 | coucal_dup_name_internal | call site: 00145 | coucal_do_crit |
| 11 | 363 | openFunctionLib | call site: 00363 | hts_debug_log_print |
| 7 | 32 | hts_mptcp_probe | call site: 00032 | hts_mptcp_kernel_recovers |
| 7 | 42 | hts_psl_init_from | call site: 00042 | coucal_new |
| 7 | 162 | coucal_realloc_pool | call site: 00162 | coucal_compact_pool |
| 6 | 376 | hts_strerror | call site: 00376 | hts_debug_log_print |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-singlefile.c | 8 |
| src/htslib.c | 39 |
| src/./htssafe.h | 8 |
| src/coucal/coucal.c | 45 |
| src/htsthread.c | 5 |
| src/htspsl.c | 6 |
| src/htscharset.c | 10 |
| src/punycode.c | 4 |
| src/coucal/murmurhash3.h | 4 |
| src/htsmodules.c | 4 |
| src/htsmd5.c | 1 |
| src/md5.c | 5 |
| src/./htsstrings.h | 1 |
| src/./htsthread.h | 4 |
| src/htsstrings.h | 1 |
| src/htssinglefile.c | 21 |
| src/htsrandom.c | 1 |
| src/htscore.c | 2 |
| src/./htslib.h | 3 |
| src/htsencoding.c | 4 |
| src/./htsentities.h | 1 |
| src/./htsencoding.h | 2 |
| src/htsconcat.c | 4 |
| src/htscache.c | 1 |
| src/./htsio.h | 1 |
Fuzzer: fuzz-cachendx
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
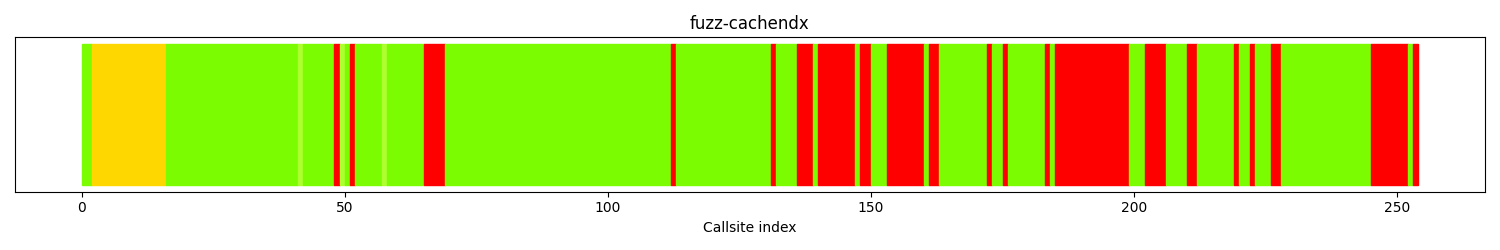
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 64 | 25.1% |
| gold | [1:9] | 14 | 5.51% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 3 | 1.18% |
| lawngreen | 50+ | 173 | 68.1% |
| All colors | 254 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 14 | 184 | coucal_add_item_ | call site: 00184 | coucal_log_stats |
| 7 | 139 | coucal_log | call site: 00139 | coucal_fail |
| 7 | 152 | coucal_realloc_pool | call site: 00152 | coucal_compact_pool |
| 7 | 244 | coucal_delete | call site: 00244 | coucal_del_name |
| 4 | 64 | vslprintfbuff | call site: 00064 | log_abort_ |
| 4 | 201 | coucal_log_stats | call site: 00201 | coucal_do_warning |
| 3 | 135 | coucal_dup_name_internal | call site: 00135 | coucal_do_crit |
| 2 | 147 | coucal_dup_name_internal | call site: 00147 | coucal_do_crit |
| 2 | 160 | coucal_realloc_pool | call site: 00160 | coucal_do_crit |
| 2 | 209 | coucal_write_value | call site: 00209 | coucal_do_crit |
| 2 | 225 | coucal_write_value | call site: 00225 | PT_Index_Delete |
| 1 | 47 | proxytrack_vprint_log | call site: 00047 | __errno_location |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-cachendx.c | 5 |
| src/coucal/coucal.c | 47 |
| src/proxy/store.c | 10 |
| src/proxy/proxytrack.h | 6 |
| src/htssafe.h | 4 |
| src/coucal/murmurhash3.h | 4 |
| src/htslib.h | 1 |
| src/htsdate.c | 2 |
Fuzzer: fuzz-htsparse
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
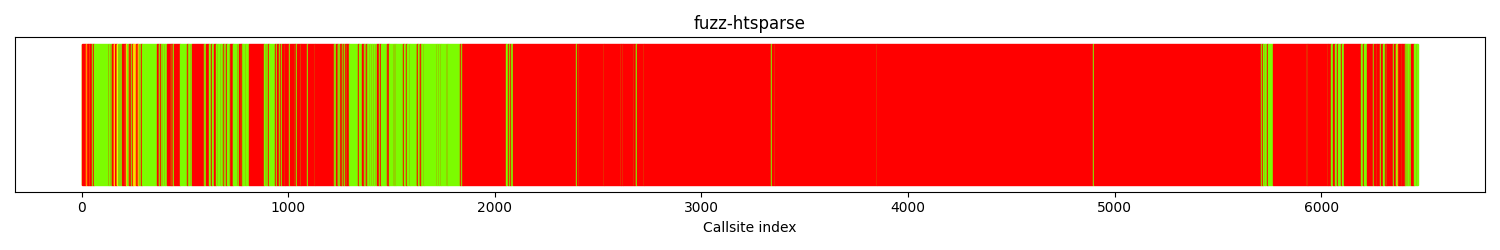
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 5154 | 79.6% |
| gold | [1:9] | 32 | 0.49% |
| yellow | [10:29] | 12 | 0.18% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 1272 | 19.6% |
| All colors | 6470 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1048 | 3849 | span_eq | call site: 03849 | http_xfopen |
| 810 | 4900 | hts_stat_recv_publish | call site: 04900 | url_savename |
| 615 | 2722 | back_finalize | call site: 02722 | cache_mayadd |
| 492 | 3356 | back_delete | call site: 03356 | back_cleanup_background |
| 307 | 2085 | url_savename | call site: 02085 | cache_read_including_broken |
| 208 | 1846 | hts_acceptlink_ | call site: 01846 | hts_wizard_insert_filters |
| 165 | 5767 | htsparse | call site: 05767 | hts_mirror_process_user_interaction |
| 120 | 2405 | back_clear_entry | call site: 02405 | resolve_extension |
| 96 | 5935 | hts_addurl_take | call site: 05935 | hts_wait_delayed |
| 92 | 1130 | time_gmt_rfc822 | call site: 01130 | usercommand |
| 82 | 2526 | back_status | call site: 02526 | hts_wait_available_socket |
| 82 | 6108 | htsparse | call site: 06108 | verif_backblue |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| fuzz/fuzz-htsparse.c | 1 |
| src/htslib.c | 210 |
| src/./htssafe.h | 25 |
| src/coucal/coucal.c | 62 |
| src/htsthread.c | 10 |
| src/htspsl.c | 11 |
| src/htscharset.c | 21 |
| src/punycode.c | 6 |
| src/coucal/murmurhash3.h | 4 |
| src/htsmodules.c | 4 |
| src/htsmd5.c | 1 |
| src/md5.c | 5 |
| src/./htsstrings.h | 1 |
| src/./htsthread.h | 6 |
| src/htscore.c | 69 |
| src/htshash.c | 22 |
| src/./htslib.h | 13 |
| src/htsurlport.c | 14 |
| src/htsfilters.c | 8 |
| src/htsescape.c | 2 |
| src/htsback.c | 101 |
| src/./htsencoding.h | 2 |
| src/./htsarena.h | 5 |
| src/htssafe.h | 6 |
| src/htsparse.c | 30 |
| src/htssinglefile.c | 7 |
| src/htsrandom.c | 1 |
| src/htstools.c | 29 |
| src/htsindex.c | 2 |
| src/htsconcat.c | 7 |
| src/htschanges.c | 10 |
| src/./htsio.h | 2 |
| src/htsencoding.c | 6 |
| src/./htsentities.h | 1 |
| src/htswizard.c | 18 |
| src/htsrobots.c | 4 |
| src/htsname.c | 26 |
| src/htscache.c | 16 |
| src/minizip/unzip.c | 13 |
| src/minizip/ioapi.c | 3 |
| src/htswarc.c | 45 |
| src/htssniff.c | 8 |
| src/./htsback.h | 1 |
| src/htscodec.c | 7 |
| src/htszlib.c | 3 |
| src/./htsbasenet.h | 1 |
| src/htsdate.c | 7 |
| src/./htsname.h | 1 |
| src/./htscore.h | 1 |
| src/minizip/zip.c | 15 |
| src/minizip/crypt.h | 4 |
| src/htsnet.c | 1 |
| src/./htsnet.h | 4 |
| src/htscrashtest.c | 4 |
| src/htsproxy.c | 11 |
| src/htsfetch.c | 28 |
| src/htslines.c | 3 |
| src/htsbauth.c | 25 |
| src/htsbundle.c | 6 |
| src/htsftp.c | 28 |
| src/htssitemap.c | 1 |
Analyses and suggestions
Optimal target analysis
Remaining optimal interesting functions
The following table shows a list of functions that are optimal targets. Optimal targets are identified by finding the functions that in combination, yield a high code coverage.
| Func name | Functions filename | Arg count | Args | Function depth | hitcount | instr count | bb count | cyclomatic complexity | Reachable functions | Incoming references | total cyclomatic complexity | Unreached complexity |
|---|---|---|---|---|---|---|---|---|---|---|---|---|
hts_main_internal
|
/src/httrack/src/htscoremain.c | 3 | ['int', 'N/A', 'N/A'] | 30 | 0 | 22330 | 3965 | 967 | 1485 | 4 | 20289 | 4813 |
st_paste
|
/src/httrack/src/htsbundle_selftest.c | 3 | ['N/A', 'int', 'N/A'] | 18 | 0 | 678 | 123 | 35 | 270 | 0 | 1986 | 406 |
st_copyopt
|
/src/httrack/src/htsopt_selftest.c | 3 | ['N/A', 'int', 'N/A'] | 10 | 0 | 4102 | 643 | 165 | 81 | 0 | 835 | 297 |
st_quotediff
|
/src/httrack/src/htscmdline_selftest.c | 3 | ['N/A', 'int', 'N/A'] | 8 | 0 | 498 | 79 | 21 | 40 | 0 | 378 | 267 |
st_spandiff
|
/src/httrack/src/htslib_selftest.c | 3 | ['N/A', 'int', 'N/A'] | 10 | 0 | 1970 | 344 | 92 | 63 | 0 | 571 | 246 |
st_singlefile
|
/src/httrack/src/htswarc_selftest.c | 3 | ['N/A', 'int', 'N/A'] | 21 | 0 | 4138 | 658 | 157 | 159 | 0 | 3289 | 243 |
PT_ReadCache__Old
|
/src/httrack/src/proxy/store.c | 3 | ['N/A', 'N/A', 'int'] | 9 | 0 | 32 | 3 | 2 | 84 | 0 | 377 | 183 |
Implementing fuzzers that target the above functions will improve reachability such that it becomes:
All functions overview
If you implement fuzzers for these functions, the status of all functions in the project will be:
| Func name | Functions filename | Args | Function call depth | Reached by Fuzzers | Runtime reached by Fuzzers | Combined reached by Fuzzers | Fuzzers runtime hit | Func lines hit % | I Count | BB Count | Cyclomatic complexity | Functions reached | Reached by functions | Accumulated cyclomatic complexity | Undiscovered complexity |
|---|
Fuzz engine guidance
This sections provides heuristics that can be used as input to a fuzz engine when running a given fuzz target. The current focus is on providing input that is usable by libFuzzer.
fuzz/fuzz-codepage.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['hts_codepageToUTF8', 'hts_convertStringToUTF8']fuzz/fuzz-filters.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['LLVMFuzzerTestOneInput']fuzz/fuzz-meta.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
fuzz/fuzz-header.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['hts_log_vprint', 'cookie_domain_is_suffix', 'cookie_host', 'treathead_opt', 'has_login', 'strcpy_safe_', 'strrchr_limit']fuzz/fuzz-url.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['strcpy_safe_', 'ident_url_absolute']fuzz/fuzz-unescape.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['hts_unescapeEntitiesWithCharsetSpecial', 'unescape_http', 'hts_isCharsetUTF8']fuzz/fuzz-idna.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['hts_convertStringUTF8ToIDNA', 'punycode_decode']fuzz/fuzz-arc.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coucal_add_item_', 'PT_LoadCache', 'coucal_log', 'coucal_realloc_pool', 'coucal_delete', 'vslprintfbuff', 'coucal_log_stats', 'coucal_dup_name_internal', 'PT_Enumerate']fuzz/fuzz-sitemap.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['hts_unescapeEntitiesWithCharsetSpecial', 'hts_isCharsetUTF8']fuzz/fuzz-entities.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['hts_unescapeEntitiesWithCharsetSpecial', 'hts_convertStringCharset', 'hts_convertStringFromUTF8']fuzz/fuzz-charset.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['hts_convertUTF8StringToUCS4', 'hts_convertStringToUTF8', 'hts_convertStringCharset']fuzz/fuzz-singlefile.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['fspc_count', 'hts_unescapeEntitiesWithCharsetSpecial', 'coucal_add_item_', 'sf_inline', 'hts_init', 'coucal_write_value', 'coucal_dup_name_internal', 'openFunctionLib', 'hts_mptcp_probe', 'hts_psl_init_from']fuzz/fuzz-cachendx.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coucal_add_item_', 'coucal_log', 'coucal_realloc_pool', 'coucal_delete', 'vslprintfbuff', 'coucal_log_stats', 'coucal_dup_name_internal', 'coucal_write_value']fuzz/fuzz-htsparse.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['span_eq', 'hts_stat_recv_publish', 'back_finalize', 'back_delete', 'url_savename', 'hts_acceptlink_', 'htsparse', 'back_clear_entry', 'hts_addurl_take', 'time_gmt_rfc822']Runtime coverage analysis
This section shows analysis of runtime coverage data.
For futher technical details on how this section is generated, please see the Glossary .
Complex functions with low coverage
| Func name | Function total lines | Lines covered at runtime | percentage covered | Reached by fuzzers |
|---|---|---|---|---|
| cookie_host | 40 | 18 | 45.0% | ['fuzz-htsparse', 'fuzz-header'] |
| hts_log_vprint | 54 | 23 | 42.59% | ['fuzz-singlefile', 'fuzz-htsparse', 'fuzz-header'] |
| coucal_add_item_ | 131 | 64 | 48.85% | ['fuzz-arc', 'fuzz-singlefile', 'fuzz-htsparse', 'fuzz-cachendx'] |
| MD5Update | 31 | 16 | 51.61% | ['fuzz-arc', 'fuzz-singlefile', 'fuzz-htsparse', 'fuzz-cachendx'] |
| plug_wrapper | 45 | 11 | 24.44% | ['fuzz-singlefile', 'fuzz-htsparse'] |
| hts_random_bytes | 36 | 17 | 47.22% | ['fuzz-singlefile', 'fuzz-htsparse'] |
| back_finalize | 385 | 21 | 5.454% | ['fuzz-htsparse'] |
| hts_changes_notify | 53 | 11 | 20.75% | ['fuzz-htsparse'] |
| hts_changes_html | 36 | 11 | 30.55% | ['fuzz-htsparse'] |
| hts_finish_makeindex | 33 | 6 | 18.18% | ['fuzz-htsparse'] |
| hts_finish_html_file | 42 | 16 | 38.09% | ['fuzz-htsparse'] |
| engine_stats | 32 | 8 | 25.0% | ['fuzz-htsparse'] |
| hash_read | 37 | 19 | 51.35% | ['fuzz-htsparse'] |
| hts_query_strip_keys | 36 | 8 | 22.22% | ['fuzz-htsparse'] |
| hts_host_alias_resolve | 76 | 9 | 11.84% | ['fuzz-htsparse'] |
| url_savename | 1041 | 75 | 7.204% | ['fuzz-htsparse'] |
| hts_acceptlink_ | 446 | 32 | 7.174% | ['fuzz-htsparse'] |
Files and Directories in report
This section shows which files and directories are considered in this report. The main reason for showing this is fuzz introspector may include more code in the reasoning than is desired. This section helps identify if too many files/directories are included, e.g. third party code, which may be irrelevant for the threat model. In the event too much is included, fuzz introspector supports a configuration file that can exclude data from the report. See the following link for more information on how to create a config file: link
Files in report
| Source file | Reached by | Covered by |
|---|---|---|
| [] | [] | |
| /src/httrack/src/htsfetch_selftest.c | [] | [] |
| /src/httrack/src/htssniff.c | ['fuzz-htsparse'] | [] |
| /src/httrack/src/./htsname.h | ['fuzz-htsparse'] | [] |
| /src/httrack/src/htszlib.c | ['fuzz-sitemap', 'fuzz-htsparse'] | ['fuzz-sitemap'] |
| /src/httrack/src/htssinglefile.c | ['fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/src/htslib_selftest.c | [] | [] |
| /src/httrack/src/htsproxy.c | ['fuzz-htsparse'] | [] |
| /src/httrack/fuzz/fuzz-sitemap.c | ['fuzz-sitemap'] | ['fuzz-sitemap'] |
| /src/httrack/src/./htsbasenet.h | ['fuzz-htsparse'] | [] |
| /src/httrack/fuzz/fuzz-idna.c | ['fuzz-idna'] | ['fuzz-idna'] |
| /src/httrack/src/htsbundle_selftest.c | [] | [] |
| /src/httrack/src/htscache.c | ['fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-singlefile'] |
| /src/httrack/fuzz/fuzz-url.c | ['fuzz-url'] | ['fuzz-url'] |
| /src/httrack/src/./htsback.h | ['fuzz-htsparse'] | [] |
| /src/httrack/src/htssitemap.c | ['fuzz-sitemap', 'fuzz-htsparse'] | ['fuzz-sitemap', 'fuzz-htsparse'] |
| /src/httrack/fuzz/fuzz-codepage.c | ['fuzz-codepage'] | ['fuzz-codepage'] |
| /src/httrack/src/coucal/coucal.c | ['fuzz-header', 'fuzz-arc', 'fuzz-singlefile', 'fuzz-cachendx', 'fuzz-htsparse'] | ['fuzz-arc', 'fuzz-singlefile', 'fuzz-cachendx', 'fuzz-htsparse'] |
| /src/httrack/src/htsftp.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/src/coucal/murmurhash3.h | ['fuzz-header', 'fuzz-arc', 'fuzz-singlefile', 'fuzz-cachendx', 'fuzz-htsparse'] | ['fuzz-arc', 'fuzz-singlefile', 'fuzz-cachendx', 'fuzz-htsparse'] |
| /src/httrack/fuzz/fuzz-cachendx.c | ['fuzz-cachendx'] | ['fuzz-cachendx'] |
| /src/httrack/src/htsindex.c | ['fuzz-htsparse'] | [] |
| /src/httrack/fuzz/fuzz-singlefile.c | ['fuzz-singlefile'] | ['fuzz-singlefile'] |
| /src/httrack/fuzz/fuzz-header.c | ['fuzz-header'] | ['fuzz-header'] |
| /src/httrack/src/htsrobots.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/src/htsbauth.c | ['fuzz-header', 'fuzz-htsparse'] | ['fuzz-header'] |
| /src/httrack/src/./htsencoding.h | ['fuzz-unescape', 'fuzz-sitemap', 'fuzz-entities', 'fuzz-singlefile', 'fuzz-htsparse'] | [] |
| /src/httrack/fuzz/fuzz-unescape.c | ['fuzz-unescape'] | ['fuzz-unescape'] |
| /src/httrack/src/htssafe.h | ['fuzz-codepage', 'fuzz-arc', 'fuzz-cachendx', 'fuzz-htsparse'] | [] |
| /src/httrack/src/./htsarena.h | ['fuzz-htsparse'] | [] |
| /src/httrack/src/htscoremain.c | [] | [] |
| /src/httrack/src/htscore.c | ['fuzz-header', 'fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/fuzz/fuzz-entities.c | ['fuzz-entities'] | ['fuzz-entities'] |
| /src/httrack/src/htsrandom.c | ['fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-singlefile'] |
| /src/httrack/src/minizip/mztools.c | [] | [] |
| /src/httrack/src/htsnet_selftest.c | [] | [] |
| /src/httrack/src/htsparse_selftest.c | [] | [] |
| /src/httrack/fuzz/fuzz-charset.c | ['fuzz-charset'] | ['fuzz-charset'] |
| /src/httrack/src/htsselftest.c | [] | [] |
| /src/httrack/src/htsfilters_selftest.c | [] | [] |
| /src/httrack/src/./htsnet.h | ['fuzz-htsparse'] | [] |
| /src/httrack/src/htswizard.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/src/htsstrings.h | ['fuzz-arc', 'fuzz-singlefile'] | ['fuzz-arc'] |
| /src/httrack/src/minizip/crypt.h | ['fuzz-htsparse'] | [] |
| /src/httrack/src/htsio_selftest.c | [] | [] |
| /src/httrack/src/htscharset.c | ['fuzz-codepage', 'fuzz-meta', 'fuzz-header', 'fuzz-unescape', 'fuzz-idna', 'fuzz-sitemap', 'fuzz-entities', 'fuzz-charset', 'fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-codepage', 'fuzz-meta', 'fuzz-header', 'fuzz-unescape', 'fuzz-idna', 'fuzz-sitemap', 'fuzz-entities', 'fuzz-charset', 'fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/src/htstools_selftest.c | [] | [] |
| /src/httrack/src/htswizard_selftest.c | [] | [] |
| /src/httrack/src/htsback.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/src/htsalias.c | [] | [] |
| /src/httrack/src/htscookie_selftest.c | [] | [] |
| /src/httrack/src/htshash.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/src/htslines_selftest.c | [] | [] |
| /src/httrack/src/md5.c | ['fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/src/htsdate.c | ['fuzz-header', 'fuzz-arc', 'fuzz-cachendx', 'fuzz-htsparse'] | ['fuzz-arc', 'fuzz-cachendx'] |
| /src/httrack/src/htspsl.c | ['fuzz-header', 'fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-header', 'fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/src/htsdns_selftest.c | [] | [] |
| /src/httrack/fuzz/fuzz-arc.c | ['fuzz-arc'] | ['fuzz-arc'] |
| /src/httrack/src/htstools.c | ['fuzz-sitemap', 'fuzz-htsparse'] | ['fuzz-sitemap', 'fuzz-htsparse'] |
| /src/httrack/src/htsfilters.c | ['fuzz-filters', 'fuzz-htsparse'] | ['fuzz-filters'] |
| /src/httrack/src/htsthread.c | ['fuzz-header', 'fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/src/htsopt_selftest.c | [] | [] |
| /src/httrack/src/./htscore.h | ['fuzz-htsparse'] | [] |
| /src/httrack/src/htscache_selftest.c | [] | [] |
| /src/httrack/src/htswarc_selftest.c | [] | [] |
| /src/httrack/src/./htsio.h | ['fuzz-singlefile', 'fuzz-htsparse'] | [] |
| /src/httrack/src/htsmd5.c | ['fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/src/proxy/proxytrack.h | ['fuzz-arc', 'fuzz-cachendx'] | ['fuzz-arc', 'fuzz-cachendx'] |
| /src/httrack/src/htscrashtest.c | ['fuzz-htsparse'] | [] |
| /src/httrack/src/htsname.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/src/htscmdline.c | [] | [] |
| /src/httrack/src/./htsthread.h | ['fuzz-header', 'fuzz-singlefile', 'fuzz-htsparse'] | [] |
| /src/httrack/src/proxy/store.c | ['fuzz-arc', 'fuzz-cachendx'] | ['fuzz-arc', 'fuzz-cachendx'] |
| /src/httrack/src/htscodec.c | ['fuzz-header', 'fuzz-sitemap', 'fuzz-htsparse'] | ['fuzz-header', 'fuzz-sitemap'] |
| /src/httrack/src/htscharset_selftest.c | [] | [] |
| /src/httrack/src/htsselftest_util.c | [] | [] |
| /src/httrack/src/htsnet.c | ['fuzz-htsparse'] | [] |
| /src/httrack/src/htsheader_selftest.c | [] | [] |
| /src/httrack/src/htsmime_selftest.c | [] | [] |
| /src/httrack/src/htsback_selftest.c | [] | [] |
| /src/httrack/src/htsname_selftest.c | [] | [] |
| /src/httrack/src/./htsentities.h | ['fuzz-unescape', 'fuzz-sitemap', 'fuzz-entities', 'fuzz-singlefile', 'fuzz-htsparse'] | [] |
| /src/httrack/src/htscmdline_selftest.c | [] | [] |
| /src/httrack/src/proxy/proxystrings.h | [] | [] |
| /src/httrack/src/htspsl_selftest.c | [] | [] |
| /src/httrack/src/minizip/ioapi.c | ['fuzz-htsparse'] | [] |
| /src/httrack/src/htswarc.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/src/htshelp.c | [] | [] |
| /src/httrack/src/htslines.c | ['fuzz-htsparse'] | [] |
| /src/httrack/src/htsconcat.c | ['fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/src/punycode.c | ['fuzz-header', 'fuzz-idna', 'fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-idna', 'fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/src/./htssafe.h | ['fuzz-header', 'fuzz-url', 'fuzz-unescape', 'fuzz-idna', 'fuzz-sitemap', 'fuzz-entities', 'fuzz-charset', 'fuzz-singlefile', 'fuzz-htsparse'] | [] |
| /src/httrack/src/./htsstrings.h | ['fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-arc'] |
| /src/httrack/src/htsencoding.c | ['fuzz-unescape', 'fuzz-sitemap', 'fuzz-entities', 'fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-unescape', 'fuzz-sitemap', 'fuzz-entities', 'fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/src/htslib.c | ['fuzz-header', 'fuzz-url', 'fuzz-unescape', 'fuzz-idna', 'fuzz-sitemap', 'fuzz-entities', 'fuzz-charset', 'fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-header', 'fuzz-url', 'fuzz-unescape', 'fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/src/htsparse.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/src/htsbundle.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/fuzz/fuzz-htsparse.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/src/htscatchurl.c | [] | [] |
| /src/httrack/src/htschanges.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/src/./htslib.h | ['fuzz-filters', 'fuzz-header', 'fuzz-url', 'fuzz-sitemap', 'fuzz-singlefile', 'fuzz-htsparse'] | [] |
| /src/httrack/src/htsurlport.c | ['fuzz-header', 'fuzz-htsparse'] | ['fuzz-header', 'fuzz-htsparse'] |
| /src/httrack/src/htsescape.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/src/htsmodules.c | ['fuzz-singlefile', 'fuzz-htsparse'] | ['fuzz-singlefile', 'fuzz-htsparse'] |
| /src/httrack/fuzz/fuzz.h | ['fuzz-codepage', 'fuzz-filters', 'fuzz-meta', 'fuzz-header', 'fuzz-url', 'fuzz-unescape', 'fuzz-idna', 'fuzz-entities', 'fuzz-charset'] | ['fuzz-codepage', 'fuzz-filters', 'fuzz-meta', 'fuzz-header', 'fuzz-url', 'fuzz-unescape', 'fuzz-idna', 'fuzz-entities', 'fuzz-charset'] |
| /src/httrack/src/htsfetch.c | ['fuzz-htsparse'] | ['fuzz-htsparse'] |
| /src/httrack/fuzz/fuzz-filters.c | ['fuzz-filters'] | ['fuzz-filters'] |
| /src/httrack/fuzz/fuzz-meta.c | ['fuzz-meta'] | ['fuzz-meta'] |
| /src/httrack/src/minizip/zip.c | ['fuzz-htsparse'] | [] |
| /src/httrack/src/minizip/unzip.c | ['fuzz-htsparse'] | [] |
Directories in report
| Directory |
|---|
| /src/httrack/src/proxy/ |
| /src/httrack/src/./ |
| /src/httrack/src/ |
| /src/httrack/src/minizip/ |
| /src/httrack/src/coucal/ |
| /src/httrack/fuzz/ |
Metadata section
This sections shows the raw data that is used to produce this report. This is mainly used for further processing and developer debugging.