Project overview: lcms
High level conclusions
Reachability and coverage overview
Warning:
The number of runtime covered functions are larger than the
number of reachable functions. This means that Fuzz Introspector found
there are more functions covered at runtime than what is considered
reachable based on the static analysis. This is a limitation in the
analysis as anything covered at runtime is by definition reachable by the
fuzzers.
This is likely due to a limitation in the static analysis. In this case, the
count of functions covered at runtime is the true value, which means this
is what should be considered "achieved" by the fuzzer.
Use the project functions table below to query all functions that were not covered at runtime.
Project functions overview
The following table shows data about each function in the project. The functions included in this table correspond to all functions that exist in the executables of the fuzzers. As such, there may be functions that are from third-party libraries.
For further technical details on the meaning of columns in the below table, please see the Glossary .
| Func name | Functions filename | Args | Function call depth | Reached by Fuzzers | Runtime reached by Fuzzers | Combined reached by Fuzzers | Fuzzers runtime hit | Func lines hit % | I Count | BB Count | Cyclomatic complexity | Functions reached | Reached by functions | Accumulated cyclomatic complexity | Undiscovered complexity |
|---|
Fuzzer details
Fuzzer: cms_gdb_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 12 | 19.3% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 50 | 80.6% |
| All colors | 62 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 6 | 8 | _cmsContextGetClientChunk | call site: 00008 | _cmsEnterCriticalSectionPrimitive |
| 4 | 3 | _cmsMallocZero | call site: 00003 | cmsSignalError |
| 1 | 26 | ToSpherical | call site: 00026 | cmsSignalError |
| 1 | 28 | GetPoint | call site: 00028 | cmsSignalError |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_gdb_fuzzer.c | 1 |
| lcmscmssm.c | 15 |
| lcmscmserr.c | 3 |
| lcmscmsplugin.c | 3 |
| lcms./lcms2_internal.h | 2 |
| lcmscmsmtrx.c | 3 |
Fuzzer: cms_dict_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 84 | 35.1% |
| gold | [1:9] | 2 | 0.83% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 153 | 64.0% |
| All colors | 239 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 17 | 147 | cmsCreateContext | call site: 00147 | cmsDeleteContext |
| 6 | 39 | RegisterTypesPlugin | call site: 00039 | _cmsPluginMalloc |
| 5 | 131 | _cmsAllocOptimizationPluginChunk | call site: 00131 | _cmsSubAllocDup |
| 4 | 6 | _cmsMalloc | call site: 00006 | cmsSignalError |
| 4 | 27 | _cmsFree | call site: 00027 | cmsDeleteContext |
| 4 | 99 | _cmsAllocCurvesPluginChunk | call site: 00099 | DupPluginCurvesList |
| 4 | 106 | _cmsAllocFormattersPluginChunk | call site: 00106 | DupFormatterFactoryList |
| 3 | 112 | cmsCreateContext | call site: 00112 | DupTagTypeList |
| 3 | 120 | cmsCreateContext | call site: 00120 | DupTagList |
| 3 | 125 | cmsCreateContext | call site: 00125 | DupPluginIntentsList |
| 3 | 137 | cmsCreateContext | call site: 00137 | DupPluginTransformList |
| 3 | 187 | generateWideString | call site: 00187 | cmsDeleteContext |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_dict_fuzzer.c | 2 |
| lcmscmsplugin.c | 10 |
| lcmscmserr.c | 21 |
| lcms./lcms2_internal.h | 2 |
| lcmscmsintrp.c | 2 |
| lcmscmstypes.c | 9 |
| lcmscmspack.c | 3 |
| lcmscmscnvrt.c | 3 |
| lcmscmsgamma.c | 3 |
| lcmscmsopt.c | 3 |
| lcmscmsxform.c | 5 |
| lcmscmsnamed.c | 22 |
Fuzzer: cms_md5_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
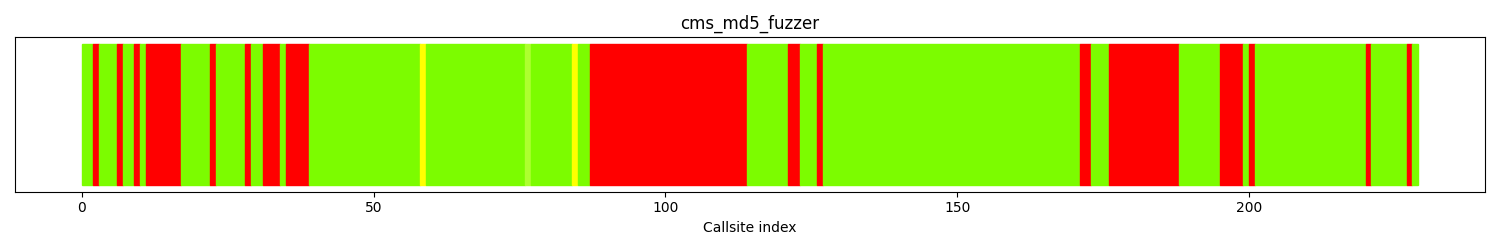
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 69 | 30.1% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 2 | 0.87% |
| greenyellow | [30:49] | 1 | 0.43% |
| lawngreen | 50+ | 157 | 68.5% |
| All colors | 229 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 27 | 86 | cmsOpenProfileFromMemTHR | call site: 00086 | cmsSaveProfileToFile |
| 12 | 175 | _cmsWriteAlignment | call site: 00175 | _cmsGetTagTypeHandler |
| 6 | 10 | _cmsContextGetClientChunk | call site: 00010 | _cmsEnterCriticalSectionPrimitive |
| 4 | 34 | cmsOpenIOhandlerFromMem | call site: 00034 | _cmsFree |
| 4 | 194 | cmsSaveProfileToIOhandler | call site: 00194 | _cmsUnlockMutex |
| 3 | 30 | _cmsMalloc | call site: 00030 | _cmsFree |
| 2 | 120 | cmsOpenIOhandlerFromNULL | call site: 00120 | _cmsFree |
| 2 | 170 | SaveTags | call site: 00170 | _cmsFree |
| 1 | 1 | LLVMFuzzerTestOneInput | call site: 00001 | cmsOpenProfileFromMemTHR |
| 1 | 5 | _cmsMallocZero | call site: 00005 | cmsSignalError |
| 1 | 8 | cmsSignalError | call site: 00008 | __assert_fail |
| 1 | 21 | _cmsCreateMutex | call site: 00021 | _cmsFree |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_md5_fuzzer.c | 1 |
| lcmscmsio0.c | 27 |
| lcmscmserr.c | 10 |
| lcmscmsplugin.c | 14 |
| lcms./lcms2_internal.h | 2 |
| lcmscmstypes.c | 3 |
| lcmscmswtpnt.c | 1 |
| lcmscmsmd5.c | 5 |
Fuzzer: cms_devicelink_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 197 | 52.2% |
| gold | [1:9] | 3 | 0.79% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 68 | 18.0% |
| lawngreen | 50+ | 109 | 28.9% |
| All colors | 377 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 85 | 259 | cmsPipelineFree | call site: 00259 | cmsCloseProfile |
| 24 | 345 | _cmsMalloc | call site: 00345 | SaveTags |
| 8 | 123 | AllocateToneCurveStruct | call site: 00123 | cmsFreeToneCurve |
| 7 | 96 | cmsStageAllocToneCurves | call site: 00096 | cmsEvalToneCurveFloat |
| 6 | 8 | _cmsContextGetClientChunk | call site: 00008 | _cmsEnterCriticalSectionPrimitive |
| 6 | 216 | _cmsGetTagTypeHandler | call site: 00216 | cmsSignalError |
| 5 | 192 | _cmsSearchTag | call site: 00192 | _cmsDeleteTagByPos |
| 4 | 46 | cmsStageAllocCLut16bitGranular | call site: 00046 | FromFloatTo16 |
| 4 | 64 | _cmsSetInterpolationRoutine | call site: 00064 | _cmsFree |
| 4 | 209 | cmsWriteTag | call site: 00209 | cmsSignalError |
| 4 | 241 | cmsMLUsetASCII | call site: 00241 | AddMLUBlock |
| 3 | 200 | _cmsNewTag | call site: 00200 | _cmsDeleteTagByPos |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_devicelink_fuzzer.c | 1 |
| lcmscmsvirt.c | 5 |
| lcmscmserr.c | 13 |
| lcmscmsplugin.c | 12 |
| lcms./lcms2_internal.h | 5 |
| lcmscmsio0.c | 28 |
| lcmscmslut.c | 23 |
| lcmscmspcs.c | 2 |
| lcmscmsintrp.c | 5 |
| lcmscmsgamma.c | 12 |
| lcmscmsnamed.c | 12 |
| lcmscmstypes.c | 3 |
| lcmscmsio1.c | 1 |
| lcmscmswtpnt.c | 1 |
Fuzzer: cms_cgats_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 141 | 33.6% |
| gold | [1:9] | 1 | 0.23% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 3 | 0.71% |
| lawngreen | 50+ | 274 | 65.3% |
| All colors | 419 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 20 | 273 | InStringSymbol | call site: 00273 | InSymbol |
| 12 | 249 | InSymbol | call site: 00249 | StringCat |
| 12 | 334 | DataSection | call site: 00334 | SkipEOLN |
| 10 | 363 | HeaderSection | call site: 00363 | AddToList |
| 8 | 347 | ParseIT8 | call site: 00347 | InSymbol |
| 6 | 8 | _cmsContextGetClientChunk | call site: 00008 | _cmsEnterCriticalSectionPrimitive |
| 6 | 240 | ReadReal | call site: 00240 | NextCh |
| 5 | 142 | WriteHeader | call site: 00142 | Writef |
| 4 | 40 | cmsstrcasecmp | call site: 00040 | SynError |
| 3 | 117 | cmsIT8SaveToFile | call site: 00117 | SynError |
| 3 | 165 | WriteData | call site: 00165 | WriteStr |
| 3 | 227 | InSymbol | call site: 00227 | SynError |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_cgats_fuzzer.c | 1 |
| lcmscmscgats.c | 76 |
| lcmscmserr.c | 4 |
| lcmscmsplugin.c | 3 |
| lcms./lcms2_internal.h | 2 |
Fuzzer: cms_universal_transform_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 408 | 48.6% |
| gold | [1:9] | 3 | 0.35% |
| yellow | [10:29] | 9 | 1.07% |
| greenyellow | [30:49] | 15 | 1.78% |
| lawngreen | 50+ | 404 | 48.1% |
| All colors | 839 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 54 | 589 | SetTextTags | call site: 00589 | _cmsStageAllocIdentityCurves |
| 45 | 123 | _cmsUnlockMutex | call site: 00123 | SaveTags |
| 29 | 86 | cmsOpenProfileFromMemTHR | call site: 00086 | cmsSaveProfileToFile |
| 28 | 807 | cmsMLUdup | call site: 00807 | cmsCreateTransformTHR |
| 20 | 737 | cmsCreateExtendedTransform | call site: 00737 | _cmsCreateGamutCheckPipeline |
| 17 | 378 | OptimizeByResampling | call site: 00378 | PrelinOpt16alloc |
| 13 | 792 | cmsCreateExtendedTransform | call site: 00792 | _cmsCompileProfileSequence |
| 10 | 682 | cmsDoTransform | call site: 00682 | cmsCloseProfile |
| 9 | 522 | cmsCreateExtendedTransform | call site: 00522 | cmsDetectRGBProfileGamma |
| 9 | 671 | cmsStageAllocToneCurves | call site: 00671 | cmsCreateTransformTHR |
| 8 | 30 | _cmsMalloc | call site: 00030 | _cmsFree |
| 8 | 169 | cmsGetProfileVersion | call site: 00169 | _cmsGetTagTypeHandler |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_universal_transform_fuzzer.c | 1 |
| lcmscmsio0.c | 46 |
| lcmscmserr.c | 13 |
| lcmscmsplugin.c | 15 |
| lcms./lcms2_internal.h | 5 |
| lcmscmstypes.c | 4 |
| lcmscmswtpnt.c | 6 |
| lcmscmsxform.c | 15 |
| lcmscmslut.c | 42 |
| lcmscmspack.c | 4 |
| lcmscmsopt.c | 19 |
| lcmscmsmtrx.c | 5 |
| lcmscmspcs.c | 10 |
| lcmscmsgamma.c | 20 |
| lcmscmsintrp.c | 5 |
| lcmscmsnamed.c | 16 |
| lcmscmsgmt.c | 3 |
| lcmscmsvirt.c | 4 |
| lcmscmscnvrt.c | 2 |
| lcmscmsio1.c | 3 |
Fuzzer: cms_transform_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 385 | 45.2% |
| gold | [1:9] | 2 | 0.23% |
| yellow | [10:29] | 17 | 1.99% |
| greenyellow | [30:49] | 1 | 0.11% |
| lawngreen | 50+ | 446 | 52.4% |
| All colors | 851 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 45 | 123 | _cmsUnlockMutex | call site: 00123 | SaveTags |
| 29 | 86 | cmsOpenProfileFromMemTHR | call site: 00086 | cmsSaveProfileToFile |
| 28 | 817 | cmsMLUdup | call site: 00817 | cmsCreateTransformTHR |
| 20 | 747 | cmsCreateExtendedTransform | call site: 00747 | _cmsCreateGamutCheckPipeline |
| 17 | 534 | OptimizeByResampling | call site: 00534 | PrelinOpt16alloc |
| 17 | 636 | cmsCreateExtendedTransform | call site: 00636 | cmsDetectRGBProfileGamma |
| 15 | 800 | cmsCreateExtendedTransform | call site: 00800 | _cmsCompileProfileSequence |
| 10 | 692 | cmsDoTransform | call site: 00692 | cmsCloseProfile |
| 9 | 572 | cmsReverseToneCurveEx | call site: 00572 | cmsBuildTabulatedToneCurve16 |
| 9 | 681 | cmsStageAllocToneCurves | call site: 00681 | cmsCreateTransformTHR |
| 8 | 30 | _cmsMalloc | call site: 00030 | _cmsFree |
| 8 | 169 | cmsGetProfileVersion | call site: 00169 | _cmsGetTagTypeHandler |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_transform_fuzzer.c | 1 |
| lcmscmsio0.c | 46 |
| lcmscmserr.c | 13 |
| lcmscmsplugin.c | 15 |
| lcms./lcms2_internal.h | 5 |
| lcmscmstypes.c | 4 |
| lcmscmswtpnt.c | 6 |
| lcmscmsvirt.c | 7 |
| lcmscmsgamma.c | 20 |
| lcmscmsintrp.c | 5 |
| lcmscmsnamed.c | 16 |
| lcmscmspcs.c | 10 |
| lcmscmsmtrx.c | 5 |
| lcmscmsxform.c | 15 |
| lcmscmslut.c | 42 |
| lcmscmspack.c | 4 |
| lcmscmsopt.c | 19 |
| lcmscmsgmt.c | 3 |
| lcmscmscnvrt.c | 2 |
| lcmscmsio1.c | 3 |
Fuzzer: cms_overwrite_transform_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 408 | 48.6% |
| gold | [1:9] | 3 | 0.35% |
| yellow | [10:29] | 22 | 2.62% |
| greenyellow | [30:49] | 5 | 0.59% |
| lawngreen | 50+ | 401 | 47.7% |
| All colors | 839 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 54 | 589 | SetTextTags | call site: 00589 | _cmsStageAllocIdentityCurves |
| 45 | 123 | _cmsUnlockMutex | call site: 00123 | SaveTags |
| 29 | 86 | cmsOpenProfileFromMemTHR | call site: 00086 | cmsSaveProfileToFile |
| 28 | 807 | cmsMLUdup | call site: 00807 | cmsCreateTransformTHR |
| 20 | 737 | cmsCreateExtendedTransform | call site: 00737 | _cmsCreateGamutCheckPipeline |
| 17 | 378 | OptimizeByResampling | call site: 00378 | PrelinOpt16alloc |
| 13 | 792 | cmsCreateExtendedTransform | call site: 00792 | _cmsCompileProfileSequence |
| 10 | 682 | cmsDoTransform | call site: 00682 | cmsCloseProfile |
| 9 | 522 | cmsCreateExtendedTransform | call site: 00522 | cmsDetectRGBProfileGamma |
| 9 | 671 | cmsStageAllocToneCurves | call site: 00671 | cmsCreateTransformTHR |
| 8 | 30 | _cmsMalloc | call site: 00030 | _cmsFree |
| 8 | 169 | cmsGetProfileVersion | call site: 00169 | _cmsGetTagTypeHandler |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_overwrite_transform_fuzzer.c | 1 |
| lcmscmsio0.c | 46 |
| lcmscmserr.c | 13 |
| lcmscmsplugin.c | 15 |
| lcms./lcms2_internal.h | 5 |
| lcmscmstypes.c | 4 |
| lcmscmswtpnt.c | 6 |
| lcmscmsxform.c | 15 |
| lcmscmslut.c | 42 |
| lcmscmspack.c | 4 |
| lcmscmsopt.c | 19 |
| lcmscmsmtrx.c | 5 |
| lcmscmspcs.c | 10 |
| lcmscmsgamma.c | 20 |
| lcmscmsintrp.c | 5 |
| lcmscmsnamed.c | 16 |
| lcmscmsgmt.c | 3 |
| lcmscmsvirt.c | 4 |
| lcmscmscnvrt.c | 2 |
| lcmscmsio1.c | 3 |
Fuzzer: cms_transform_all_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 282 | 33.5% |
| gold | [1:9] | 5 | 0.59% |
| yellow | [10:29] | 7 | 0.83% |
| greenyellow | [30:49] | 10 | 1.19% |
| lawngreen | 50+ | 536 | 63.8% |
| All colors | 840 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 45 | 124 | _cmsUnlockMutex | call site: 00124 | SaveTags |
| 29 | 87 | cmsOpenProfileFromMemTHR | call site: 00087 | cmsSaveProfileToFile |
| 29 | 607 | cmsCreateRGBProfileTHR | call site: 00607 | cmsCloseProfile |
| 25 | 811 | _cmsCompileProfileSequence | call site: 00811 | cmsCreateTransformTHR |
| 8 | 31 | _cmsMalloc | call site: 00031 | _cmsFree |
| 8 | 170 | cmsGetProfileVersion | call site: 00170 | _cmsGetTagTypeHandler |
| 8 | 191 | _cmsSearchTag | call site: 00191 | SaveTags |
| 7 | 439 | AllocateToneCurveStruct | call site: 00439 | _cmsFree |
| 6 | 11 | _cmsContextGetClientChunk | call site: 00011 | _cmsEnterCriticalSectionPrimitive |
| 6 | 117 | _cmsLockMutex | call site: 00117 | cmsOpenIOhandlerFromNULL |
| 6 | 579 | cmsWriteTag | call site: 00579 | cmsSignalError |
| 6 | 767 | cmsIsMatrixShaper | call site: 00767 | cmsCreateExtendedTransform |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_transform_all_fuzzer.c | 2 |
| lcmscmsio0.c | 46 |
| lcmscmserr.c | 13 |
| lcmscmsplugin.c | 15 |
| lcms./lcms2_internal.h | 5 |
| lcmscmstypes.c | 4 |
| lcmscmswtpnt.c | 6 |
| lcmscmsxform.c | 15 |
| lcmscmslut.c | 42 |
| lcmscmspack.c | 4 |
| lcmscmsopt.c | 19 |
| lcmscmsmtrx.c | 5 |
| lcmscmspcs.c | 10 |
| lcmscmsgamma.c | 20 |
| lcmscmsintrp.c | 5 |
| lcmscmsnamed.c | 16 |
| lcmscmsgmt.c | 3 |
| lcmscmsvirt.c | 4 |
| lcmscmscnvrt.c | 2 |
| lcmscmsio1.c | 3 |
Fuzzer: cms_profile_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
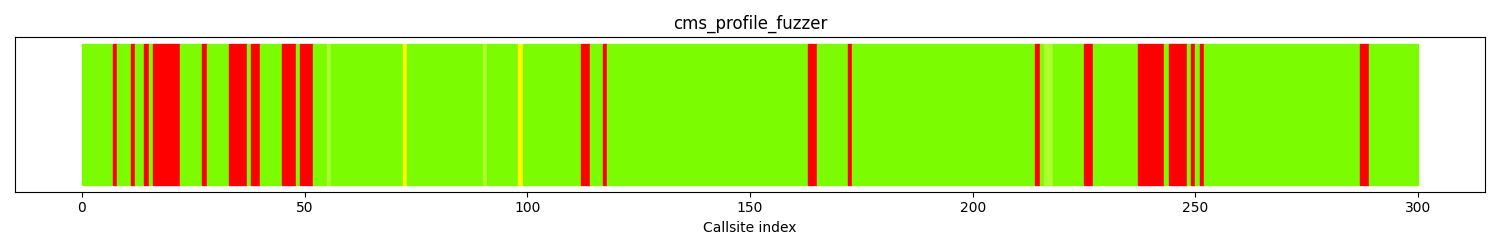
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 45 | 15.0% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 2 | 0.66% |
| greenyellow | [30:49] | 4 | 1.33% |
| lawngreen | 50+ | 249 | 83.0% |
| All colors | 300 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 6 | 15 | _cmsContextGetClientChunk | call site: 00015 | _cmsEnterCriticalSectionPrimitive |
| 6 | 236 | cmsOpenIOhandlerFromMem | call site: 00236 | _cmsFree |
| 4 | 32 | cmsOpenIOhandlerFromFile | call site: 00032 | _cmsFree |
| 4 | 243 | cmsOpenIOhandlerFromMem | call site: 00243 | _cmsFree |
| 3 | 44 | cmsfilelength | call site: 00044 | _cmsFree |
| 3 | 48 | cmsOpenIOhandlerFromFile | call site: 00048 | _cmsFree |
| 2 | 37 | cmsOpenIOhandlerFromFile | call site: 00037 | _cmsFree |
| 2 | 111 | cmsOpenIOhandlerFromNULL | call site: 00111 | _cmsFree |
| 2 | 162 | _cmsMalloc | call site: 00162 | _cmsFree |
| 2 | 224 | cmsReadTag | call site: 00224 | cmsSignalError |
| 2 | 286 | _cmsDeleteTagByPos | call site: 00286 | _cmsUnlockMutex |
| 1 | 6 | LLVMFuzzerTestOneInput | call site: 00006 | cmsOpenProfileFromFileTHR |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_profile_fuzzer.c | 1 |
| lcmscmsio0.c | 36 |
| lcmscmserr.c | 11 |
| lcmscmsplugin.c | 15 |
| lcms./lcms2_internal.h | 2 |
| lcmscmstypes.c | 4 |
| lcmscmswtpnt.c | 1 |
| lcmscmsio1.c | 2 |
| lcmscmsnamed.c | 3 |
Fuzzer: cms_transform_extended_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 378 | 32.2% |
| gold | [1:9] | 11 | 0.93% |
| yellow | [10:29] | 9 | 0.76% |
| greenyellow | [30:49] | 8 | 0.68% |
| lawngreen | 50+ | 766 | 65.3% |
| All colors | 1172 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 45 | 124 | _cmsUnlockMutex | call site: 00124 | SaveTags |
| 29 | 87 | cmsOpenProfileFromMemTHR | call site: 00087 | cmsSaveProfileToFile |
| 25 | 1136 | _cmsCompileProfileSequence | call site: 01136 | cmsCreateTransformTHR |
| 17 | 799 | cmsCreateContext | call site: 00799 | cmsDeleteContext |
| 10 | 1024 | cmsDoTransform | call site: 01024 | cmsCloseProfile |
| 8 | 31 | _cmsMalloc | call site: 00031 | _cmsFree |
| 8 | 170 | cmsGetProfileVersion | call site: 00170 | _cmsGetTagTypeHandler |
| 8 | 191 | _cmsSearchTag | call site: 00191 | SaveTags |
| 8 | 375 | AllocateToneCurveStruct | call site: 00375 | cmsFreeToneCurve |
| 8 | 1014 | cmsCreateExtendedTransform | call site: 01014 | cmsDetectRGBProfileGamma |
| 7 | 598 | run_test | call site: 00598 | cmsCreateBCHSWabstractProfileTHR |
| 6 | 117 | _cmsLockMutex | call site: 00117 | cmsOpenIOhandlerFromNULL |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_transform_extended_fuzzer.c | 2 |
| lcmscmsio0.c | 46 |
| lcmscmserr.c | 27 |
| lcmscmsplugin.c | 22 |
| lcms./lcms2_internal.h | 5 |
| lcmscmstypes.c | 13 |
| lcmscmswtpnt.c | 7 |
| lcmscmsvirt.c | 19 |
| lcmscmspcs.c | 25 |
| lcmscmsnamed.c | 16 |
| lcmscmsmtrx.c | 5 |
| lcmscmslut.c | 46 |
| lcmscmsgamma.c | 23 |
| lcmscmsintrp.c | 7 |
| lcmscmspack.c | 7 |
| lcmscmscnvrt.c | 5 |
| lcmscmsopt.c | 22 |
| lcmscmsxform.c | 19 |
| lcmscmsgmt.c | 3 |
| lcmscmsio1.c | 3 |
Fuzzer: cms_virtual_profile_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 365 | 37.1% |
| gold | [1:9] | 5 | 0.50% |
| yellow | [10:29] | 25 | 2.54% |
| greenyellow | [30:49] | 5 | 0.50% |
| lawngreen | 50+ | 582 | 59.2% |
| All colors | 982 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 45 | 123 | _cmsUnlockMutex | call site: 00123 | SaveTags |
| 29 | 86 | cmsOpenProfileFromMemTHR | call site: 00086 | cmsSaveProfileToFile |
| 28 | 817 | cmsMLUdup | call site: 00817 | cmsCreateTransformTHR |
| 20 | 747 | cmsCreateExtendedTransform | call site: 00747 | _cmsCreateGamutCheckPipeline |
| 16 | 636 | cmsCreateExtendedTransform | call site: 00636 | cmsDetectRGBProfileGamma |
| 12 | 897 | cmsTransform2DeviceLink | call site: 00897 | IsPCS |
| 10 | 692 | cmsDoTransform | call site: 00692 | cmsCloseProfile |
| 9 | 681 | cmsStageAllocToneCurves | call site: 00681 | cmsCreateTransformTHR |
| 9 | 806 | cmsAllocProfileSequenceDescription | call site: 00806 | GetMLUFromProfile |
| 8 | 30 | _cmsMalloc | call site: 00030 | _cmsFree |
| 8 | 169 | cmsGetProfileVersion | call site: 00169 | _cmsGetTagTypeHandler |
| 8 | 190 | _cmsSearchTag | call site: 00190 | SaveTags |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_virtual_profile_fuzzer.c | 1 |
| lcmscmsio0.c | 46 |
| lcmscmserr.c | 13 |
| lcmscmsplugin.c | 15 |
| lcms./lcms2_internal.h | 5 |
| lcmscmstypes.c | 4 |
| lcmscmswtpnt.c | 6 |
| lcmscmsvirt.c | 16 |
| lcmscmsgamma.c | 21 |
| lcmscmsintrp.c | 5 |
| lcmscmsnamed.c | 19 |
| lcmscmspcs.c | 10 |
| lcmscmsmtrx.c | 5 |
| lcmscmsxform.c | 17 |
| lcmscmslut.c | 46 |
| lcmscmspack.c | 4 |
| lcmscmsopt.c | 19 |
| lcmscmsgmt.c | 3 |
| lcmscmscnvrt.c | 2 |
| lcmscmsio1.c | 4 |
Fuzzer: cms_cie_cam02_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 75 | 31.9% |
| gold | [1:9] | 7 | 2.97% |
| yellow | [10:29] | 137 | 58.2% |
| greenyellow | [30:49] | 3 | 1.27% |
| lawngreen | 50+ | 13 | 5.53% |
| All colors | 235 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 17 | 147 | cmsCreateContext | call site: 00147 | cmsDeleteContext |
| 6 | 39 | RegisterTypesPlugin | call site: 00039 | _cmsPluginMalloc |
| 5 | 131 | _cmsAllocOptimizationPluginChunk | call site: 00131 | _cmsSubAllocDup |
| 4 | 6 | _cmsMalloc | call site: 00006 | cmsSignalError |
| 4 | 27 | _cmsFree | call site: 00027 | cmsDeleteContext |
| 4 | 99 | _cmsAllocCurvesPluginChunk | call site: 00099 | DupPluginCurvesList |
| 4 | 106 | _cmsAllocFormattersPluginChunk | call site: 00106 | DupFormatterFactoryList |
| 3 | 112 | cmsCreateContext | call site: 00112 | DupTagTypeList |
| 3 | 120 | cmsCreateContext | call site: 00120 | DupTagList |
| 3 | 125 | cmsCreateContext | call site: 00125 | DupPluginIntentsList |
| 3 | 137 | cmsCreateContext | call site: 00137 | DupPluginTransformList |
| 2 | 32 | cmsUnregisterPluginsTHR | call site: 00032 | _cmsContextGetClientChunk |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_cie_cam02_fuzzer.c | 1 |
| lcmscmsplugin.c | 10 |
| lcmscmserr.c | 18 |
| lcms./lcms2_internal.h | 2 |
| lcmscmsintrp.c | 2 |
| lcmscmstypes.c | 9 |
| lcmscmspack.c | 3 |
| lcmscmscnvrt.c | 3 |
| lcmscmsgamma.c | 3 |
| lcmscmsopt.c | 3 |
| lcmscmsxform.c | 5 |
| lcmscmscam02.c | 19 |
Fuzzer: cmsIT8_load_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 58 | 16.4% |
| gold | [1:9] | 4 | 1.13% |
| yellow | [10:29] | 5 | 1.42% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 285 | 80.9% |
| All colors | 352 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 10 | 265 | HeaderSection | call site: 00265 | AddToList |
| 7 | 317 | WriteHeader | call site: 00317 | Writef |
| 6 | 12 | _cmsContextGetClientChunk | call site: 00012 | _cmsEnterCriticalSectionPrimitive |
| 4 | 253 | HeaderSection | call site: 00253 | InSymbol |
| 3 | 294 | cmsIT8SaveToFile | call site: 00294 | SynError |
| 2 | 303 | WriteStr | call site: 00303 | cmsSignalError |
| 2 | 306 | WriteHeader | call site: 00306 | Writef |
| 2 | 310 | Writef | call site: 00310 | WriteStr |
| 1 | 7 | _cmsMallocZero | call site: 00007 | cmsSignalError |
| 1 | 10 | cmsSignalError | call site: 00010 | __assert_fail |
| 1 | 23 | AllocBigBlock | call site: 00023 | _cmsFree |
| 1 | 25 | _cmsFree | call site: 00025 | SynError |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cmsIT8_load_fuzzer.c | 1 |
| lcmscmscgats.c | 59 |
| lcmscmserr.c | 5 |
| lcmscmsplugin.c | 3 |
| lcms./lcms2_internal.h | 2 |
Fuzzer: cms_postscript_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 418 | 28.4% |
| gold | [1:9] | 12 | 0.81% |
| yellow | [10:29] | 18 | 1.22% |
| greenyellow | [30:49] | 30 | 2.04% |
| lawngreen | 50+ | 992 | 67.4% |
| All colors | 1470 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 45 | 273 | _cmsUnlockMutex | call site: 00273 | SaveTags |
| 29 | 236 | cmsOpenProfileFromMemTHR | call site: 00236 | cmsSaveProfileToFile |
| 29 | 448 | cmsCreateRGBProfileTHR | call site: 00448 | cmsCloseProfile |
| 28 | 965 | cmsMLUdup | call site: 00965 | cmsCreateTransformTHR |
| 17 | 147 | cmsCreateContext | call site: 00147 | cmsDeleteContext |
| 13 | 950 | cmsCreateExtendedTransform | call site: 00950 | _cmsCompileProfileSequence |
| 9 | 621 | _MultiplyMatrix | call site: 00621 | _RemoveElement |
| 8 | 180 | cmsOpenIOhandlerFromMem | call site: 00180 | _cmsFree |
| 8 | 319 | cmsGetProfileVersion | call site: 00319 | _cmsGetTagTypeHandler |
| 8 | 340 | _cmsSearchTag | call site: 00340 | SaveTags |
| 8 | 531 | AllocateToneCurveStruct | call site: 00531 | cmsFreeToneCurve |
| 6 | 39 | RegisterTypesPlugin | call site: 00039 | _cmsPluginMalloc |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| cms_postscript_fuzzer.c | 1 |
| lcmscmsplugin.c | 23 |
| lcmscmserr.c | 27 |
| lcms./lcms2_internal.h | 5 |
| lcmscmsintrp.c | 7 |
| lcmscmstypes.c | 13 |
| lcmscmspack.c | 8 |
| lcmscmscnvrt.c | 5 |
| lcmscmsgamma.c | 23 |
| lcmscmsopt.c | 22 |
| lcmscmsxform.c | 21 |
| lcmscmsio0.c | 48 |
| lcmscmswtpnt.c | 6 |
| lcmscmsps2.c | 32 |
| lcmscmsvirt.c | 6 |
| lcmscmspcs.c | 14 |
| lcmscmsnamed.c | 24 |
| lcmscmsmtrx.c | 5 |
| lcmscmslut.c | 53 |
| lcmscmsgmt.c | 3 |
| lcmscmsio1.c | 11 |
| lcmscmssamp.c | 5 |
Analyses and suggestions
Optimal target analysis
Remaining optimal interesting functions
The following table shows a list of functions that are optimal targets. Optimal targets are identified by finding the functions that in combination, yield a high code coverage.
| Func name | Functions filename | Arg count | Args | Function depth | hitcount | instr count | bb count | cyclomatic complexity | Reachable functions | Incoming references | total cyclomatic complexity | Unreached complexity |
|---|---|---|---|---|---|---|---|---|---|---|---|---|
BlackPreservingKPlaneIntents
|
/src/lcms/src/cmscnvrt.c | 7 | ['N/A', 'int', 'N/A', 'N/A', 'N/A', 'N/A', 'int'] | 17 | 0 | 439 | 70 | 27 | 321 | 0 | 2039 | 409 |
Type_Dictionary_Read
|
/src/lcms/src/cmstypes.c | 4 | ['N/A', 'N/A', 'N/A', 'int'] | 10 | 0 | 441 | 79 | 31 | 42 | 0 | 216 | 131 |
OptimizeMatrixShaper
|
/src/lcms/src/cmsopt.c | 5 | ['N/A', 'int', 'N/A', 'N/A', 'N/A'] | 9 | 0 | 355 | 58 | 24 | 87 | 0 | 424 | 110 |
Type_LUTB2A_Read
|
/src/lcms/src/cmstypes.c | 4 | ['N/A', 'N/A', 'N/A', 'int'] | 13 | 0 | 333 | 58 | 25 | 76 | 0 | 415 | 109 |
OptimizeByComputingLinearization
|
/src/lcms/src/cmsopt.c | 5 | ['N/A', 'int', 'N/A', 'N/A', 'N/A'] | 10 | 0 | 874 | 141 | 51 | 95 | 0 | 646 | 92 |
Type_LUTA2B_Write
|
/src/lcms/src/cmstypes.c | 4 | ['N/A', 'N/A', 'N/A', 'int'] | 6 | 0 | 488 | 73 | 32 | 33 | 0 | 159 | 82 |
cmsCreateDeviceLinkFromCubeFile
|
/src/lcms/src/cmscgats.c | 1 | ['N/A'] | 12 | 0 | 15 | 3 | 2 | 140 | 0 | 687 | 81 |
FloatXFORM
|
/src/lcms/src/cmsxform.c | 6 | ['N/A', 'N/A', 'N/A', 'int', 'int', 'N/A'] | 7 | 0 | 199 | 21 | 7 | 18 | 0 | 101 | 73 |
Type_ProfileSequenceId_Write
|
/src/lcms/src/cmstypes.c | 4 | ['N/A', 'N/A', 'N/A', 'int'] | 10 | 0 | 70 | 8 | 4 | 30 | 0 | 149 | 73 |
Eval15InputsFloat
|
/src/lcms/src/cmsintrp.c | 3 | ['N/A', 'N/A', 'N/A'] | 13 | 0 | 158 | 10 | 4 | 13 | 0 | 70 | 70 |
Implementing fuzzers that target the above functions will improve reachability such that it becomes:
All functions overview
If you implement fuzzers for these functions, the status of all functions in the project will be:
| Func name | Functions filename | Args | Function call depth | Reached by Fuzzers | Runtime reached by Fuzzers | Combined reached by Fuzzers | Fuzzers runtime hit | Func lines hit % | I Count | BB Count | Cyclomatic complexity | Functions reached | Reached by functions | Accumulated cyclomatic complexity | Undiscovered complexity |
|---|
Fuzz engine guidance
This sections provides heuristics that can be used as input to a fuzz engine when running a given fuzz target. The current focus is on providing input that is usable by libFuzzer.
cms_gdb_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['_cmsContextGetClientChunk', '_cmsMallocZero', 'ToSpherical', 'GetPoint']cms_dict_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['cmsCreateContext', 'RegisterTypesPlugin', '_cmsAllocOptimizationPluginChunk', '_cmsMalloc', '_cmsFree', '_cmsAllocCurvesPluginChunk', '_cmsAllocFormattersPluginChunk']cms_md5_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['cmsOpenProfileFromMemTHR', '_cmsWriteAlignment', '_cmsContextGetClientChunk', 'cmsOpenIOhandlerFromMem', 'cmsSaveProfileToIOhandler', '_cmsMalloc', 'cmsOpenIOhandlerFromNULL', 'SaveTags', 'LLVMFuzzerTestOneInput', '_cmsMallocZero']cms_devicelink_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['cmsPipelineFree', '_cmsMalloc', 'AllocateToneCurveStruct', 'cmsStageAllocToneCurves', '_cmsContextGetClientChunk', '_cmsGetTagTypeHandler', '_cmsSearchTag', 'cmsStageAllocCLut16bitGranular', '_cmsSetInterpolationRoutine', 'cmsWriteTag']cms_cgats_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['InStringSymbol', 'InSymbol', 'DataSection', 'HeaderSection', 'ParseIT8', '_cmsContextGetClientChunk', 'ReadReal', 'WriteHeader', 'cmsstrcasecmp', 'cmsIT8SaveToFile']cms_universal_transform_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['SetTextTags', '_cmsUnlockMutex', 'cmsOpenProfileFromMemTHR', 'cmsMLUdup', 'cmsCreateExtendedTransform', 'OptimizeByResampling', 'cmsDoTransform', 'cmsStageAllocToneCurves']cms_transform_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['_cmsUnlockMutex', 'cmsOpenProfileFromMemTHR', 'cmsMLUdup', 'cmsCreateExtendedTransform', 'OptimizeByResampling', 'cmsDoTransform', 'cmsReverseToneCurveEx', 'cmsStageAllocToneCurves']cms_overwrite_transform_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['SetTextTags', '_cmsUnlockMutex', 'cmsOpenProfileFromMemTHR', 'cmsMLUdup', 'cmsCreateExtendedTransform', 'OptimizeByResampling', 'cmsDoTransform', 'cmsStageAllocToneCurves']cms_transform_all_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['_cmsUnlockMutex', 'cmsOpenProfileFromMemTHR', 'cmsCreateRGBProfileTHR', '_cmsCompileProfileSequence', '_cmsMalloc', 'cmsGetProfileVersion', '_cmsSearchTag', 'AllocateToneCurveStruct', '_cmsContextGetClientChunk', '_cmsLockMutex']cms_profile_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['_cmsContextGetClientChunk', 'cmsOpenIOhandlerFromMem', 'cmsOpenIOhandlerFromFile', 'cmsfilelength', 'cmsOpenIOhandlerFromNULL', '_cmsMalloc', 'cmsReadTag']cms_transform_extended_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['_cmsUnlockMutex', 'cmsOpenProfileFromMemTHR', '_cmsCompileProfileSequence', 'cmsCreateContext', 'cmsDoTransform', '_cmsMalloc', 'cmsGetProfileVersion', '_cmsSearchTag', 'AllocateToneCurveStruct', 'cmsCreateExtendedTransform']cms_virtual_profile_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['_cmsUnlockMutex', 'cmsOpenProfileFromMemTHR', 'cmsMLUdup', 'cmsCreateExtendedTransform', 'cmsTransform2DeviceLink', 'cmsDoTransform', 'cmsStageAllocToneCurves', 'cmsAllocProfileSequenceDescription', '_cmsMalloc']cms_cie_cam02_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['cmsCreateContext', 'RegisterTypesPlugin', '_cmsAllocOptimizationPluginChunk', '_cmsMalloc', '_cmsFree', '_cmsAllocCurvesPluginChunk', '_cmsAllocFormattersPluginChunk']cmsIT8_load_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['HeaderSection', 'WriteHeader', '_cmsContextGetClientChunk', 'cmsIT8SaveToFile', 'WriteStr', 'Writef', '_cmsMallocZero', 'cmsSignalError']cms_postscript_fuzzer.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['_cmsUnlockMutex', 'cmsOpenProfileFromMemTHR', 'cmsCreateRGBProfileTHR', 'cmsMLUdup', 'cmsCreateContext', 'cmsCreateExtendedTransform', '_MultiplyMatrix', 'cmsOpenIOhandlerFromMem', 'cmsGetProfileVersion', '_cmsSearchTag']Runtime coverage analysis
This section shows analysis of runtime coverage data.
For futher technical details on how this section is generated, please see the Glossary .
Complex functions with low coverage
| Func name | Function total lines | Lines covered at runtime | percentage covered | Reached by fuzzers |
|---|---|---|---|---|
| cmsPluginTHR | 61 | 7 | 11.47% | ['cms_transform_extended_fuzzer', 'cms_postscript_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_dict_fuzzer'] |
| cmsWriteTag | 71 | 38 | 53.52% | ['cms_universal_transform_fuzzer', 'cms_devicelink_fuzzer', 'cms_transform_all_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_postscript_fuzzer', 'cms_transform_fuzzer'] |
| ParseFloatNumber | 49 | 13 | 26.53% | ['cms_cgats_fuzzer'] |
| HeaderSection | 70 | 38 | 54.28% | ['cmsIT8_load_fuzzer', 'cms_cgats_fuzzer'] |
| _cmsHandleExtraChannels | 67 | 15 | 22.38% | ['cms_universal_transform_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_postscript_fuzzer', 'cms_transform_fuzzer'] |
| PrelinEval8 | 72 | 34 | 47.22% | ['cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_universal_transform_fuzzer'] |
| ComputeAbsoluteIntent | 38 | 9 | 23.68% | ['cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_transform_all_fuzzer', 'cms_postscript_fuzzer'] |
Files and Directories in report
This section shows which files and directories are considered in this report. The main reason for showing this is fuzz introspector may include more code in the reasoning than is desired. This section helps identify if too many files/directories are included, e.g. third party code, which may be irrelevant for the threat model. In the event too much is included, fuzz introspector supports a configuration file that can exclude data from the report. See the following link for more information on how to create a config file: link
Files in report
| Source file | Reached by | Covered by |
|---|---|---|
| [] | [] | |
| /src/cms_gdb_fuzzer.c | ['cms_gdb_fuzzer'] | ['cms_gdb_fuzzer'] |
| /src/cmsIT8_load_fuzzer.c | ['cmsIT8_load_fuzzer'] | ['cmsIT8_load_fuzzer'] |
| /src/lcms/src/cmsvirt.c | ['cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] | ['cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] |
| /src/lcms/src/cmsgmt.c | ['cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] | ['cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_postscript_fuzzer'] |
| /src/lcms/src/cmsnamed.c | ['cms_dict_fuzzer', 'cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] | ['cms_dict_fuzzer', 'cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] |
| /src/cms_transform_fuzzer.c | ['cms_transform_fuzzer'] | ['cms_transform_fuzzer'] |
| /src/cms_postscript_fuzzer.c | ['cms_postscript_fuzzer'] | ['cms_postscript_fuzzer'] |
| /src/lcms/src/cmscnvrt.c | ['cms_dict_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] | ['cms_dict_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] |
| /src/lcms/src/cmspcs.c | ['cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] | ['cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] |
| /src/lcms/src/cmsintrp.c | ['cms_dict_fuzzer', 'cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] | ['cms_dict_fuzzer', 'cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] |
| /src/lcms/src/cmsio1.c | ['cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] | ['cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] |
| /src/cms_transform_all_fuzzer.c | ['cms_transform_all_fuzzer'] | ['cms_transform_all_fuzzer'] |
| /src/lcms/src/cmswtpnt.c | ['cms_md5_fuzzer', 'cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] | ['cms_md5_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] |
| /src/cms_virtual_profile_fuzzer.c | ['cms_virtual_profile_fuzzer'] | ['cms_virtual_profile_fuzzer'] |
| /src/cms_cgats_fuzzer.c | ['cms_cgats_fuzzer'] | ['cms_cgats_fuzzer'] |
| /src/lcms/src/cmslut.c | ['cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] | ['cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] |
| /src/cms_cie_cam02_fuzzer.c | ['cms_cie_cam02_fuzzer'] | ['cms_cie_cam02_fuzzer'] |
| /src/lcms/src/cmssamp.c | ['cms_postscript_fuzzer'] | ['cms_postscript_fuzzer'] |
| /src/cms_md5_fuzzer.c | ['cms_md5_fuzzer'] | ['cms_md5_fuzzer'] |
| /src/lcms/src/cmssm.c | ['cms_gdb_fuzzer'] | ['cms_gdb_fuzzer'] |
| /src/lcms/src/cmscgats.c | ['cms_cgats_fuzzer', 'cmsIT8_load_fuzzer'] | ['cms_cgats_fuzzer', 'cmsIT8_load_fuzzer'] |
| /src/lcms/src/cmsmd5.c | ['cms_md5_fuzzer'] | ['cms_md5_fuzzer'] |
| /src/lcms/src/cmserr.c | ['cms_gdb_fuzzer', 'cms_dict_fuzzer', 'cms_md5_fuzzer', 'cms_devicelink_fuzzer', 'cms_cgats_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cmsIT8_load_fuzzer', 'cms_postscript_fuzzer'] | ['cms_gdb_fuzzer', 'cms_dict_fuzzer', 'cms_md5_fuzzer', 'cms_devicelink_fuzzer', 'cms_cgats_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cmsIT8_load_fuzzer', 'cms_postscript_fuzzer'] |
| /src/lcms/src/cmshalf.c | [] | [] |
| /src/lcms/src/cmsps2.c | ['cms_postscript_fuzzer'] | ['cms_postscript_fuzzer'] |
| /src/lcms/src/cmsgamma.c | ['cms_dict_fuzzer', 'cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] | ['cms_dict_fuzzer', 'cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] |
| /src/cms_profile_fuzzer.c | ['cms_profile_fuzzer'] | ['cms_profile_fuzzer'] |
| /src/lcms/src/cmsopt.c | ['cms_dict_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] | ['cms_dict_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] |
| /src/lcms/src/cmstypes.c | ['cms_dict_fuzzer', 'cms_md5_fuzzer', 'cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] | ['cms_dict_fuzzer', 'cms_md5_fuzzer', 'cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] |
| /src/lcms/src/cmsio0.c | ['cms_md5_fuzzer', 'cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] | ['cms_md5_fuzzer', 'cms_devicelink_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] |
| /src/cms_dict_fuzzer.c | ['cms_dict_fuzzer'] | ['cms_dict_fuzzer'] |
| /src/lcms/src/cmspack.c | ['cms_dict_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] | ['cms_dict_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] |
| /src/lcms/src/cmsxform.c | ['cms_dict_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] | ['cms_dict_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cms_postscript_fuzzer'] |
| /src/lcms/src/cmsplugin.c | ['cms_gdb_fuzzer', 'cms_dict_fuzzer', 'cms_md5_fuzzer', 'cms_devicelink_fuzzer', 'cms_cgats_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cmsIT8_load_fuzzer', 'cms_postscript_fuzzer'] | ['cms_gdb_fuzzer', 'cms_dict_fuzzer', 'cms_md5_fuzzer', 'cms_devicelink_fuzzer', 'cms_cgats_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cmsIT8_load_fuzzer', 'cms_postscript_fuzzer'] |
| /src/cms_transform_extended_fuzzer.c | ['cms_transform_extended_fuzzer'] | ['cms_transform_extended_fuzzer'] |
| /src/cms_overwrite_transform_fuzzer.c | ['cms_overwrite_transform_fuzzer'] | ['cms_overwrite_transform_fuzzer'] |
| /src/lcms/src/cmsalpha.c | [] | [] |
| /src/cms_universal_transform_fuzzer.c | ['cms_universal_transform_fuzzer'] | ['cms_universal_transform_fuzzer'] |
| /src/cms_devicelink_fuzzer.c | ['cms_devicelink_fuzzer'] | ['cms_devicelink_fuzzer'] |
| /src/lcms/src/cmscam02.c | ['cms_cie_cam02_fuzzer'] | ['cms_cie_cam02_fuzzer'] |
| /src/lcms/src/./lcms2_internal.h | ['cms_gdb_fuzzer', 'cms_dict_fuzzer', 'cms_md5_fuzzer', 'cms_devicelink_fuzzer', 'cms_cgats_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_profile_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_cie_cam02_fuzzer', 'cmsIT8_load_fuzzer', 'cms_postscript_fuzzer'] | [] |
| /src/lcms/src/cmsmtrx.c | ['cms_gdb_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] | ['cms_gdb_fuzzer', 'cms_universal_transform_fuzzer', 'cms_transform_fuzzer', 'cms_overwrite_transform_fuzzer', 'cms_transform_all_fuzzer', 'cms_transform_extended_fuzzer', 'cms_virtual_profile_fuzzer', 'cms_postscript_fuzzer'] |
Directories in report
| Directory |
|---|
| /src/lcms/src/ |
| /src/lcms/src/./ |
| /src/ |
Metadata section
This sections shows the raw data that is used to produce this report. This is mainly used for further processing and developer debugging.