Project overview: libcoap
High level conclusions
Reachability and coverage overview
Project functions overview
The following table shows data about each function in the project. The functions included in this table correspond to all functions that exist in the executables of the fuzzers. As such, there may be functions that are from third-party libraries.
For further technical details on the meaning of columns in the below table, please see the Glossary .
| Func name | Functions filename | Args | Function call depth | Reached by Fuzzers | Runtime reached by Fuzzers | Combined reached by Fuzzers | Fuzzers runtime hit | Func lines hit % | I Count | BB Count | Cyclomatic complexity | Functions reached | Reached by functions | Accumulated cyclomatic complexity | Undiscovered complexity |
|---|
Fuzzer details
Fuzzer: oscore_cbor_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 19 | 28.7% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 47 | 71.2% |
| All colors | 66 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 14 | 40 | oscore_cbor_elem_contained | call site: 00040 | print_timestamp |
| 2 | 16 | coap_cleanup | call site: 00016 | ENGINE_finish |
| 1 | 11 | coap_dtls_startup | call site: 00011 | OPENSSL_init_crypto |
| 1 | 14 | LLVMFuzzerTestOneInput | call site: 00014 | coap_cleanup |
| 1 | 20 | coap_cleanup | call site: 00020 | coap_free_type |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/oscore_cbor_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 4 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 3 |
| src/coap_openssl.c | 3 |
| src/coap_debug.c | 6 |
| src/coap_uri.c | 1 |
| src/oscore/oscore_cbor.c | 12 |
Fuzzer: uri_extended_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 83 | 38.0% |
| gold | [1:9] | 5 | 2.29% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 4 | 1.83% |
| lawngreen | 50+ | 126 | 57.7% |
| All colors | 218 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 15 | 186 | coap_uri_into_optlist_abbrev | call site: 00186 | coap_new_optlist |
| 14 | 20 | coap_split_uri_sub | call site: 00020 | print_timestamp |
| 12 | 91 | coap_opt_parse | call site: 00091 | coap_log_impl |
| 6 | 136 | LLVMFuzzerTestOneInput | call site: 00136 | coap_path_into_optlist_abbrev |
| 5 | 147 | coap_new_optlist | call site: 00147 | coap_insert_optlist |
| 4 | 41 | coap_dtls_is_supported | call site: 00041 | coap_log_impl |
| 4 | 53 | coap_tls_is_supported | call site: 00053 | coap_log_impl |
| 4 | 63 | coap_wss_is_supported | call site: 00063 | coap_log_impl |
| 4 | 120 | coap_opt_setheader | call site: 00120 | coap_log_impl |
| 2 | 38 | coap_dtls_is_supported | call site: 00038 | coap_log_impl |
| 2 | 46 | coap_split_uri_sub | call site: 00046 | coap_log_impl |
| 2 | 50 | coap_tls_is_supported | call site: 00050 | coap_log_impl |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/uri_extended_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 4 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 3 |
| src/coap_openssl.c | 5 |
| src/coap_debug.c | 7 |
| src/coap_uri.c | 26 |
| src/coap_strm_posix.c | 1 |
| src/coap_ws.c | 2 |
| src/coap_option.c | 7 |
| src/coap_encode.c | 1 |
| src/coap_pdu.c | 1 |
| ./include/coap3/coap_uri.h | 1 |
Fuzzer: pdu_parse_udp_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 244 | 54.4% |
| gold | [1:9] | 19 | 4.24% |
| yellow | [10:29] | 13 | 2.90% |
| greenyellow | [30:49] | 3 | 0.66% |
| lawngreen | 50+ | 169 | 37.7% |
| All colors | 448 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 159 | 247 | coap_show_pdu | call site: 00247 | coap_option_next |
| 19 | 410 | coap_pdu_encode_header | call site: 00410 | coap_log_impl |
| 17 | 31 | coap_pdu_parse2 | call site: 00031 | coap_log_impl |
| 4 | 56 | coap_pdu_parse_header | call site: 00056 | coap_log_impl |
| 4 | 103 | coap_pdu_parse_opt | call site: 00103 | coap_log_impl |
| 4 | 108 | coap_pdu_parse_opt | call site: 00108 | coap_log_impl |
| 4 | 194 | coap_dtls_is_supported | call site: 00194 | coap_log_impl |
| 4 | 206 | coap_tls_is_supported | call site: 00206 | coap_log_impl |
| 4 | 216 | coap_wss_is_supported | call site: 00216 | coap_log_impl |
| 3 | 175 | coap_get_uri_path | call site: 00175 | coap_new_string |
| 2 | 50 | coap_realloc_type | call site: 00050 | coap_log_impl |
| 2 | 156 | coap_new_string | call site: 00156 | coap_log_impl |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/pdu_parse_udp_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 4 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 4 |
| src/coap_openssl.c | 5 |
| src/coap_pdu.c | 18 |
| src/coap_debug.c | 13 |
| src/coap_option.c | 12 |
| src/coap_encode.c | 3 |
| src/coap_uri.c | 9 |
| src/coap_str.c | 3 |
| src/coap_strm_posix.c | 1 |
| src/coap_ws.c | 2 |
| src/coap_block.c | 1 |
Fuzzer: get_asn1_tag_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 17 | 53.1% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 15 | 46.8% |
| All colors | 32 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 17 | 9 | coap_new_string | call site: 00009 | coap_log_impl |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/get_asn1_tag_target.c | 1 |
| src/coap_asn1.c | 4 |
| src/coap_str.c | 3 |
| src/coap_mem.c | 2 |
| src/coap_debug.c | 4 |
| src/coap_time.c | 3 |
Fuzzer: pdu_parse_tcp_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
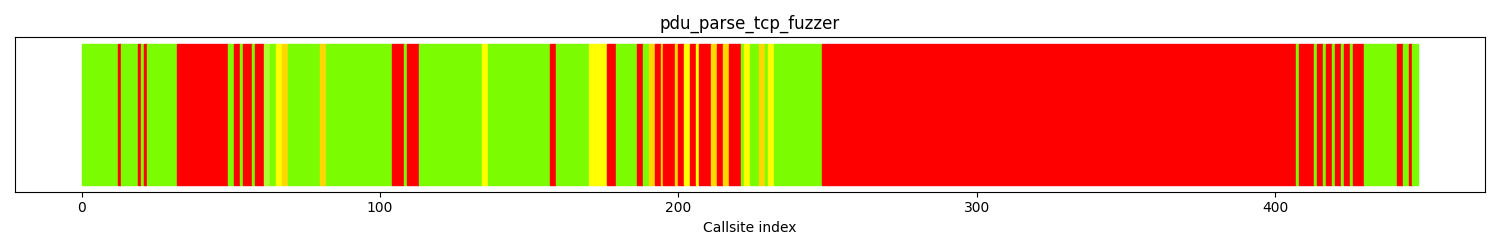
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 242 | 54.0% |
| gold | [1:9] | 14 | 3.12% |
| yellow | [10:29] | 17 | 3.79% |
| greenyellow | [30:49] | 2 | 0.44% |
| lawngreen | 50+ | 173 | 38.6% |
| All colors | 448 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 159 | 247 | coap_show_pdu | call site: 00247 | coap_option_next |
| 17 | 31 | coap_pdu_parse2 | call site: 00031 | coap_log_impl |
| 5 | 407 | LLVMFuzzerTestOneInput | call site: 00407 | coap_log_impl |
| 4 | 103 | coap_pdu_parse_opt | call site: 00103 | coap_log_impl |
| 4 | 108 | coap_pdu_parse_opt | call site: 00108 | coap_log_impl |
| 4 | 194 | coap_dtls_is_supported | call site: 00194 | coap_log_impl |
| 4 | 206 | coap_tls_is_supported | call site: 00206 | coap_log_impl |
| 4 | 216 | coap_wss_is_supported | call site: 00216 | coap_log_impl |
| 4 | 425 | coap_pdu_encode_header | call site: 00425 | coap_log_impl |
| 3 | 53 | coap_pdu_parse2 | call site: 00053 | coap_log_impl |
| 3 | 57 | coap_pdu_parse_header | call site: 00057 | coap_log_impl |
| 3 | 175 | coap_get_uri_path | call site: 00175 | coap_new_string |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/pdu_parse_tcp_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 4 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 4 |
| src/coap_openssl.c | 5 |
| src/coap_pdu.c | 18 |
| src/coap_debug.c | 13 |
| src/coap_option.c | 12 |
| src/coap_encode.c | 3 |
| src/coap_uri.c | 9 |
| src/coap_str.c | 3 |
| src/coap_strm_posix.c | 1 |
| src/coap_ws.c | 2 |
| src/coap_block.c | 1 |
Fuzzer: pdu_parse_ws_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 245 | 54.6% |
| gold | [1:9] | 17 | 3.79% |
| yellow | [10:29] | 12 | 2.67% |
| greenyellow | [30:49] | 4 | 0.89% |
| lawngreen | 50+ | 170 | 37.9% |
| All colors | 448 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 159 | 247 | coap_show_pdu | call site: 00247 | coap_option_next |
| 17 | 31 | coap_pdu_parse2 | call site: 00031 | coap_log_impl |
| 13 | 416 | coap_pdu_encode_header | call site: 00416 | coap_log_impl |
| 5 | 407 | LLVMFuzzerTestOneInput | call site: 00407 | coap_log_impl |
| 4 | 53 | coap_pdu_parse2 | call site: 00053 | coap_log_impl |
| 4 | 103 | coap_pdu_parse_opt | call site: 00103 | coap_log_impl |
| 4 | 108 | coap_pdu_parse_opt | call site: 00108 | coap_log_impl |
| 4 | 194 | coap_dtls_is_supported | call site: 00194 | coap_log_impl |
| 4 | 206 | coap_tls_is_supported | call site: 00206 | coap_log_impl |
| 4 | 216 | coap_wss_is_supported | call site: 00216 | coap_log_impl |
| 3 | 175 | coap_get_uri_path | call site: 00175 | coap_new_string |
| 2 | 50 | coap_realloc_type | call site: 00050 | coap_log_impl |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/pdu_parse_ws_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 4 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 4 |
| src/coap_openssl.c | 5 |
| src/coap_pdu.c | 18 |
| src/coap_debug.c | 13 |
| src/coap_option.c | 12 |
| src/coap_encode.c | 3 |
| src/coap_uri.c | 9 |
| src/coap_str.c | 3 |
| src/coap_strm_posix.c | 1 |
| src/coap_ws.c | 2 |
| src/coap_block.c | 1 |
Fuzzer: cache_key_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4689 | 93.9% |
| gold | [1:9] | 39 | 0.78% |
| yellow | [10:29] | 15 | 0.30% |
| greenyellow | [30:49] | 211 | 4.22% |
| lawngreen | 50+ | 36 | 0.72% |
| All colors | 4990 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1006 | 3808 | coap_pdu_parse_opt | call site: 03808 | coap_handle_event_lkd |
| 707 | 1019 | coap_socket_connect_udp | call site: 01019 | coap_session_reestablished |
| 702 | 2781 | coap_cache_derive_key_w_ignore | call site: 02781 | coap_cancel_observe_lkd |
| 542 | 2238 | coap_session_check_connect | call site: 02238 | coap_session_release_lkd |
| 305 | 633 | coap_check_dots | call site: 00633 | coap_session_release_lkd |
| 284 | 1855 | coap_session_connected | call site: 01855 | coap_handle_event_lkd |
| 268 | 3493 | coap_session_free | call site: 03493 | coap_dtls_handle_timeout |
| 125 | 1727 | coap_delete_str_const | call site: 01727 | coap_cancel_session_messages |
| 88 | 428 | coap_opt_parse | call site: 00428 | coap_split_proxy_uri |
| 70 | 99 | coap_dtls_new_context | call site: 00099 | coap_session_str |
| 69 | 250 | coap_dtls_free_context | call site: 00250 | coap_new_endpoint_lkd |
| 68 | 4815 | coap_pdu_parse | call site: 04815 | coap_handle_event_lkd |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/cache_key_target.c | 1 |
| src/coap_net.c | 60 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 16 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 11 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 20 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
Fuzzer: split_uri_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 22 | 33.3% |
| gold | [1:9] | 13 | 19.6% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 4 | 6.06% |
| lawngreen | 50+ | 27 | 40.9% |
| All colors | 66 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 4 | 28 | coap_dtls_is_supported | call site: 00028 | coap_log_impl |
| 4 | 40 | coap_tls_is_supported | call site: 00040 | coap_log_impl |
| 4 | 50 | coap_wss_is_supported | call site: 00050 | coap_log_impl |
| 2 | 25 | coap_dtls_is_supported | call site: 00025 | coap_log_impl |
| 2 | 33 | coap_split_uri_sub | call site: 00033 | coap_log_impl |
| 2 | 37 | coap_tls_is_supported | call site: 00037 | coap_log_impl |
| 2 | 46 | coap_ws_is_supported | call site: 00046 | coap_log_impl |
| 1 | 6 | coap_split_uri_sub | call site: 00006 | vsnprintf |
| 1 | 17 | coap_log_impl | call site: 00017 | snprintf |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/split_uri_target.c | 1 |
| src/coap_uri.c | 2 |
| src/coap_debug.c | 4 |
| src/coap_time.c | 3 |
| src/coap_openssl.c | 2 |
| src/coap_strm_posix.c | 1 |
| src/coap_ws.c | 2 |
Fuzzer: network_message_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4271 | 84.6% |
| gold | [1:9] | 49 | 0.97% |
| yellow | [10:29] | 42 | 0.83% |
| greenyellow | [30:49] | 39 | 0.77% |
| lawngreen | 50+ | 643 | 12.7% |
| All colors | 5044 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 417 | 2478 | setup_pki_ssl | call site: 02478 | coap_session_release_lkd |
| 325 | 3871 | coap_dispatch | call site: 03871 | coap_oscore_decrypt_pdu |
| 291 | 3088 | handle_request | call site: 03088 | coap_session_max_pdu_size_lkd |
| 284 | 1865 | coap_session_connected | call site: 01865 | coap_handle_event_lkd |
| 270 | 4281 | coap_dispatch | call site: 04281 | coap_send_ack_lkd |
| 259 | 3503 | coap_session_free | call site: 03503 | coap_dtls_handle_timeout |
| 252 | 1394 | coap_send_internal | call site: 01394 | coap_oscore_new_pdu_encrypted_lkd |
| 225 | 2248 | coap_session_check_connect | call site: 02248 | coap_session_release_lkd |
| 214 | 1070 | coap_pdu_encode_header | call site: 01070 | coap_proxy_forward_request_lkd |
| 157 | 721 | coap_show_pdu | call site: 00721 | coap_session_release_lkd |
| 145 | 4740 | coap_epoll_ctl_mod | call site: 04740 | coap_accept_endpoint |
| 83 | 2960 | coap_send_error_lkd | call site: 02960 | coap_pdu_duplicate_lkd |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/network_message_target.c | 7 |
| src/coap_net.c | 74 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 66 |
| src/coap_debug.c | 19 |
| src/coap_address.c | 16 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 20 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
Fuzzer: oscore_decrypt_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4582 | 89.9% |
| gold | [1:9] | 133 | 2.61% |
| yellow | [10:29] | 292 | 5.73% |
| greenyellow | [30:49] | 18 | 0.35% |
| lawngreen | 50+ | 69 | 1.35% |
| All colors | 5094 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1107 | 2494 | oscore_context_release_recipients | call site: 02494 | coap_session_release_lkd |
| 708 | 4293 | coap_oscore_decrypt_pdu | call site: 04293 | coap_delete_node_lkd |
| 376 | 3611 | coap_session_free | call site: 03611 | coap_dtls_handle_timeout |
| 284 | 1983 | coap_session_connected | call site: 01983 | coap_handle_event_lkd |
| 259 | 1184 | coap_pdu_encode_header | call site: 01184 | coap_proxy_forward_request_lkd |
| 228 | 843 | coap_show_pdu | call site: 00843 | coap_session_release_lkd |
| 94 | 4197 | coap_oscore_decrypt_pdu | call site: 04197 | coap_handle_event_lkd |
| 82 | 569 | coap_option_filter_get | call site: 00569 | coap_split_proxy_uri |
| 70 | 85 | coap_delete_bin_const | call site: 00085 | coap_parse_oscore_rcp_conf_mem |
| 70 | 237 | coap_dtls_new_context | call site: 00237 | coap_session_str |
| 69 | 388 | coap_dtls_free_context | call site: 00388 | coap_new_endpoint_lkd |
| 59 | 1448 | coap_add_data_after | call site: 01448 | coap_rebuild_pdu_for_proxy |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/oscore_decrypt_target.c | 1 |
| src/coap_net.c | 60 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_oscore.c | 28 |
| src/coap_str.c | 10 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 20 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
Fuzzer: persist_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4574 | 88.2% |
| gold | [1:9] | 2 | 0.03% |
| yellow | [10:29] | 4 | 0.07% |
| greenyellow | [30:49] | 2 | 0.03% |
| lawngreen | 50+ | 599 | 11.5% |
| All colors | 5181 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1006 | 3828 | coap_pdu_parse_opt | call site: 03828 | coap_handle_event_lkd |
| 503 | 2297 | coap_make_str_const | call site: 02297 | coap_session_release_lkd |
| 268 | 3513 | coap_session_free | call site: 03513 | coap_dtls_handle_timeout |
| 230 | 1929 | coap_digest_free | call site: 01929 | coap_handle_event_lkd |
| 217 | 2813 | coap_cache_derive_key_w_ignore | call site: 02813 | coap_cancel_observe_lkd |
| 216 | 3092 | coap_get_resource_from_uri_path_lkd | call site: 03092 | coap_session_max_pdu_size_lkd |
| 214 | 1400 | coap_send_internal | call site: 01400 | coap_oscore_new_pdu_encrypted_lkd |
| 169 | 1071 | coap_pdu_encode_header | call site: 01071 | coap_proxy_forward_request_lkd |
| 153 | 3350 | coap_touch_observer | call site: 03350 | coap_delete_observer_request |
| 152 | 1247 | coap_new_bin_const | call site: 01247 | coap_send_internal |
| 148 | 730 | coap_show_pdu | call site: 00730 | coap_option_next |
| 77 | 1795 | coap_send_internal | call site: 01795 | coap_io_process_lkd |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/persist_target.c | 5 |
| src/coap_subscribe.c | 15 |
| src/coap_net.c | 60 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 18 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 29 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 13 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| src/coap_async.c | 4 |
Fuzzer: block_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4317 | 85.4% |
| gold | [1:9] | 147 | 2.91% |
| yellow | [10:29] | 69 | 1.36% |
| greenyellow | [30:49] | 49 | 0.97% |
| lawngreen | 50+ | 469 | 9.28% |
| All colors | 5051 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 608 | 2286 | coap_make_str_const | call site: 02286 | coap_session_release_lkd |
| 287 | 1389 | coap_send_internal | call site: 01389 | coap_oscore_new_pdu_encrypted_lkd |
| 259 | 3502 | coap_session_free | call site: 03502 | coap_dtls_handle_timeout |
| 253 | 4639 | coap_handle_dgram | call site: 04639 | coap_handle_event_lkd |
| 248 | 3870 | coap_dispatch | call site: 03870 | coap_oscore_decrypt_pdu |
| 193 | 1060 | coap_pdu_encode_header | call site: 01060 | coap_proxy_forward_request_lkd |
| 157 | 719 | coap_show_pdu | call site: 00719 | coap_session_release_lkd |
| 146 | 4404 | coap_handle_response_get_block | call site: 04404 | coap_send_rst_lkd |
| 131 | 2017 | coap_add_data_large_internal | call site: 02017 | coap_add_data_large_request_lkd |
| 123 | 3227 | coap_handle_request_send_block | call site: 03227 | coap_pdu_duplicate_lkd |
| 110 | 3114 | coap_handle_request_put_block | call site: 03114 | coap_request_missing_q_block1 |
| 107 | 4119 | coap_find_lg_crcv | call site: 04119 | coap_pdu_duplicate_lkd |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/block_target.c | 3 |
| src/coap_net.c | 60 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_io.c | 10 |
| src/coap_session.c | 55 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 59 |
| src/coap_resource.c | 25 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
| tests/oss-fuzz/coap_fuzz_helper.c | 2 |
Fuzzer: block_check_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4547 | 89.2% |
| gold | [1:9] | 6 | 0.11% |
| yellow | [10:29] | 381 | 7.47% |
| greenyellow | [30:49] | 49 | 0.96% |
| lawngreen | 50+ | 111 | 2.17% |
| All colors | 5094 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1245 | 3625 | coap_io_do_epoll_lkd | call site: 03625 | coap_read_endpoint |
| 697 | 2287 | coap_make_str_const | call site: 02287 | coap_session_release_lkd |
| 397 | 1329 | coap_add_data_after | call site: 01329 | coap_oscore_new_pdu_encrypted_lkd |
| 201 | 1029 | coap_socket_connect_udp | call site: 01029 | coap_session_reestablished |
| 198 | 3082 | coap_get_resource_from_uri_path_lkd | call site: 03082 | coap_session_max_pdu_size_lkd |
| 161 | 720 | coap_show_pdu | call site: 00720 | coap_session_release_lkd |
| 147 | 3281 | coap_add_block_b_data | call site: 03281 | coap_send_internal |
| 94 | 2055 | coap_add_block | call site: 02055 | coap_next_block_to_send |
| 72 | 1778 | coap_add_option | call site: 01778 | coap_send_internal |
| 70 | 109 | coap_dtls_new_context | call site: 00109 | coap_session_str |
| 66 | 458 | coap_new_string | call site: 00458 | coap_split_proxy_uri |
| 57 | 891 | coap_find_lg_xmit_response | call site: 00891 | coap_delete_observer |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/block_check_target.c | 2 |
| src/coap_net.c | 60 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_io.c | 10 |
| src/coap_session.c | 55 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 5 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 61 |
| src/coap_resource.c | 23 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
Fuzzer: dtls_define_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 15 | 25.0% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 45 | 75.0% |
| All colors | 60 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 15 | 10 | coap_dtls_define_issue | call site: 00010 | print_timestamp |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/dtls_define_target.c | 1 |
| src/coap_debug.c | 5 |
| src/coap_dtls.c | 3 |
| src/coap_time.c | 3 |
Fuzzer: proxy_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4518 | 89.9% |
| gold | [1:9] | 94 | 1.87% |
| yellow | [10:29] | 97 | 1.93% |
| greenyellow | [30:49] | 242 | 4.81% |
| lawngreen | 50+ | 70 | 1.39% |
| All colors | 5021 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1390 | 3503 | coap_session_free | call site: 03503 | coap_dtls_handle_timeout |
| 456 | 3037 | coap_free_resource | call site: 03037 | coap_check_async |
| 389 | 2392 | coap_proxy_get_ongoing_session | call site: 02392 | coap_new_client_session_oscore_pki3_lkd |
| 255 | 1865 | coap_session_connected | call site: 01865 | coap_handle_event_lkd |
| 214 | 1390 | coap_send_internal | call site: 01390 | coap_oscore_new_pdu_encrypted_lkd |
| 157 | 720 | coap_show_pdu | call site: 00720 | coap_session_release_lkd |
| 144 | 2883 | coap_proxy_forward_request_lkd | call site: 02883 | coap_proxy_call_response_handler |
| 143 | 2248 | coap_session_check_connect | call site: 02248 | coap_session_release_lkd |
| 87 | 1237 | coap_new_bin_const | call site: 01237 | coap_send_internal |
| 70 | 109 | coap_dtls_new_context | call site: 00109 | coap_session_str |
| 69 | 260 | coap_dtls_free_context | call site: 00260 | coap_new_endpoint_lkd |
| 64 | 884 | coap_free_resource | call site: 00884 | coap_notify_observers |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/proxy_target.c | 4 |
| src/coap_net.c | 60 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 23 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 23 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
Fuzzer: oscore_conf_parse_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 30 | 17.2% |
| gold | [1:9] | 20 | 11.4% |
| yellow | [10:29] | 10 | 5.74% |
| greenyellow | [30:49] | 5 | 2.87% |
| lawngreen | 50+ | 109 | 62.6% |
| All colors | 174 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 16 | 41 | coap_new_string | call site: 00041 | coap_log_impl |
| 4 | 94 | coap_delete_bin_const | call site: 00094 | coap_log_impl |
| 4 | 126 | coap_parse_oscore_rcp_conf_mem | call site: 00126 | coap_log_impl |
| 2 | 16 | coap_cleanup | call site: 00016 | ENGINE_finish |
| 1 | 11 | coap_dtls_startup | call site: 00011 | OPENSSL_init_crypto |
| 1 | 14 | LLVMFuzzerTestOneInput | call site: 00014 | coap_cleanup |
| 1 | 20 | coap_cleanup | call site: 00020 | coap_free_type |
| 1 | 148 | coap_parse_oscore_conf_mem | call site: 00148 | __assert_fail |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/oscore_conf_parse_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 4 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 3 |
| src/coap_openssl.c | 3 |
| src/coap_debug.c | 6 |
| src/coap_uri.c | 1 |
| src/coap_oscore.c | 10 |
| src/coap_str.c | 6 |
| src/oscore/oscore_cose.c | 4 |
| src/oscore/oscore.c | 1 |
Fuzzer: ws_frame_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4868 | 94.7% |
| gold | [1:9] | 34 | 0.66% |
| yellow | [10:29] | 30 | 0.58% |
| greenyellow | [30:49] | 196 | 3.81% |
| lawngreen | 50+ | 9 | 0.17% |
| All colors | 5137 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1390 | 3493 | coap_session_free | call site: 03493 | coap_dtls_handle_timeout |
| 1245 | 2238 | coap_session_check_connect | call site: 02238 | coap_session_release_lkd |
| 679 | 1019 | coap_socket_connect_udp | call site: 01019 | coap_session_reestablished |
| 399 | 539 | coap_session_free | call site: 00539 | coap_delete_proxy_subscriber |
| 284 | 1855 | coap_session_connected | call site: 01855 | coap_handle_event_lkd |
| 135 | 386 | coap_handle_event_lkd | call site: 00386 | coap_proxy_remove_association |
| 118 | 1734 | coap_session_disconnected_lkd | call site: 01734 | coap_delete_node_lkd |
| 70 | 99 | coap_dtls_new_context | call site: 00099 | coap_session_str |
| 69 | 250 | coap_dtls_free_context | call site: 00250 | coap_new_endpoint_lkd |
| 46 | 328 | coap_socket_dgrm_close | call site: 00328 | coap_netif_strm_listen |
| 44 | 4969 | coap_ws_rd_http_header_client | call site: 04969 | coap_ws_build_key_hash |
| 41 | 2188 | coap_session_create_client | call site: 02188 | coap_netif_strm_connect1 |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/ws_frame_target.c | 4 |
| src/coap_net.c | 60 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 67 |
| src/coap_debug.c | 16 |
| src/coap_io.c | 10 |
| src/coap_session.c | 53 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 15 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 34 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 20 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
Fuzzer: observe_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4346 | 86.3% |
| gold | [1:9] | 92 | 1.82% |
| yellow | [10:29] | 65 | 1.29% |
| greenyellow | [30:49] | 225 | 4.47% |
| lawngreen | 50+ | 303 | 6.02% |
| All colors | 5031 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 503 | 2286 | coap_make_str_const | call site: 02286 | coap_session_release_lkd |
| 325 | 3870 | coap_dispatch | call site: 03870 | coap_oscore_decrypt_pdu |
| 270 | 4280 | coap_dispatch | call site: 04280 | coap_send_ack_lkd |
| 263 | 1060 | coap_pdu_encode_header | call site: 01060 | coap_proxy_forward_request_lkd |
| 259 | 3502 | coap_session_free | call site: 03502 | coap_dtls_handle_timeout |
| 253 | 4639 | coap_handle_dgram | call site: 04639 | coap_handle_event_lkd |
| 230 | 1918 | coap_digest_free | call site: 01918 | coap_handle_event_lkd |
| 214 | 1389 | coap_send_internal | call site: 01389 | coap_oscore_new_pdu_encrypted_lkd |
| 182 | 3109 | handle_request | call site: 03109 | coap_handle_request_put_block |
| 148 | 719 | coap_show_pdu | call site: 00719 | coap_option_next |
| 92 | 2802 | coap_cache_derive_key_w_ignore | call site: 02802 | coap_cancel_observe_lkd |
| 72 | 3420 | handle_request | call site: 03420 | coap_resource_release_lkd |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/observe_target.c | 3 |
| src/coap_net.c | 60 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 25 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
| tests/oss-fuzz/coap_fuzz_helper.c | 2 |
Fuzzer: async_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4467 | 87.8% |
| gold | [1:9] | 106 | 2.08% |
| yellow | [10:29] | 370 | 7.28% |
| greenyellow | [30:49] | 44 | 0.86% |
| lawngreen | 50+ | 95 | 1.86% |
| All colors | 5082 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 608 | 2286 | coap_make_str_const | call site: 02286 | coap_session_release_lkd |
| 356 | 3870 | coap_dispatch | call site: 03870 | coap_oscore_decrypt_pdu |
| 284 | 1864 | coap_session_connected | call site: 01864 | coap_handle_event_lkd |
| 270 | 4280 | coap_dispatch | call site: 04280 | coap_send_ack_lkd |
| 263 | 1060 | coap_pdu_encode_header | call site: 01060 | coap_proxy_forward_request_lkd |
| 259 | 3502 | coap_session_free | call site: 03502 | coap_dtls_handle_timeout |
| 253 | 4639 | coap_handle_dgram | call site: 04639 | coap_handle_event_lkd |
| 245 | 3108 | handle_request | call site: 03108 | coap_handle_request_put_block |
| 214 | 1389 | coap_send_internal | call site: 01389 | coap_oscore_new_pdu_encrypted_lkd |
| 157 | 719 | coap_show_pdu | call site: 00719 | coap_session_release_lkd |
| 70 | 108 | coap_dtls_new_context | call site: 00108 | coap_session_str |
| 70 | 1606 | coap_pdu_duplicate_lkd | call site: 01606 | oscore_new_association |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/async_target.c | 3 |
| src/coap_net.c | 60 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_io.c | 10 |
| src/coap_session.c | 55 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 24 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| src/coap_async.c | 15 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
| tests/oss-fuzz/coap_fuzz_helper.c | 2 |
Analyses and suggestions
Optimal target analysis
Remaining optimal interesting functions
The following table shows a list of functions that are optimal targets. Optimal targets are identified by finding the functions that in combination, yield a high code coverage.
| Func name | Functions filename | Arg count | Args | Function depth | hitcount | instr count | bb count | cyclomatic complexity | Reachable functions | Incoming references | total cyclomatic complexity | Unreached complexity |
|---|---|---|---|---|---|---|---|---|---|---|---|---|
hnd_get_wellknown_lkd
|
/src/libcoap/src/coap_net.c | 5 | ['N/A', 'N/A', 'N/A', 'N/A', 'N/A'] | 64 | 0 | 304 | 50 | 16 | 692 | 0 | 7212 | 121 |
coap_netif_dgrm_write
|
/src/libcoap/src/coap_netif.c | 3 | ['N/A', 'N/A', 'size_t'] | 6 | 0 | 179 | 33 | 10 | 67 | 0 | 336 | 72 |
coap_tls_engine_configure
|
/src/libcoap/src/coap_openssl.c | 1 | ['N/A'] | 6 | 0 | 575 | 124 | 34 | 32 | 0 | 121 | 52 |
coap_endpoint_join_mcast_group_intf
|
/src/libcoap/src/coap_net.c | 3 | ['N/A', 'N/A', 'N/A'] | 6 | 0 | 52 | 9 | 4 | 37 | 0 | 133 | 42 |
coap_op_resource_deleted
|
/src/libcoap/src/coap_subscribe.c | 3 | ['N/A', 'N/A', 'N/A'] | 6 | 0 | 252 | 40 | 16 | 37 | 0 | 129 | 40 |
coap_session_set_type_server
|
/src/libcoap/src/coap_session.c | 1 | ['N/A'] | 74 | 0 | 18 | 3 | 2 | 688 | 0 | 7127 | 36 |
Implementing fuzzers that target the above functions will improve reachability such that it becomes:
All functions overview
If you implement fuzzers for these functions, the status of all functions in the project will be:
| Func name | Functions filename | Args | Function call depth | Reached by Fuzzers | Runtime reached by Fuzzers | Combined reached by Fuzzers | Fuzzers runtime hit | Func lines hit % | I Count | BB Count | Cyclomatic complexity | Functions reached | Reached by functions | Accumulated cyclomatic complexity | Undiscovered complexity |
|---|
Fuzz engine guidance
This sections provides heuristics that can be used as input to a fuzz engine when running a given fuzz target. The current focus is on providing input that is usable by libFuzzer.
tests/oss-fuzz/oscore_cbor_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['oscore_cbor_elem_contained', 'coap_cleanup', 'coap_dtls_startup', 'LLVMFuzzerTestOneInput']tests/oss-fuzz/uri_extended_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_uri_into_optlist_abbrev', 'coap_split_uri_sub', 'coap_opt_parse', 'LLVMFuzzerTestOneInput', 'coap_new_optlist', 'coap_dtls_is_supported', 'coap_tls_is_supported', 'coap_wss_is_supported', 'coap_opt_setheader']tests/oss-fuzz/pdu_parse_udp_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_show_pdu', 'coap_pdu_encode_header', 'coap_pdu_parse2', 'coap_pdu_parse_header', 'coap_pdu_parse_opt', 'coap_dtls_is_supported', 'coap_tls_is_supported', 'coap_wss_is_supported', 'coap_get_uri_path']tests/oss-fuzz/get_asn1_tag_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_new_string']tests/oss-fuzz/pdu_parse_tcp_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_show_pdu', 'coap_pdu_parse2', 'LLVMFuzzerTestOneInput', 'coap_pdu_parse_opt', 'coap_dtls_is_supported', 'coap_tls_is_supported', 'coap_wss_is_supported', 'coap_pdu_encode_header']tests/oss-fuzz/pdu_parse_ws_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_show_pdu', 'coap_pdu_parse2', 'coap_pdu_encode_header', 'LLVMFuzzerTestOneInput', 'coap_pdu_parse_opt', 'coap_dtls_is_supported', 'coap_tls_is_supported', 'coap_wss_is_supported']tests/oss-fuzz/cache_key_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_pdu_parse_opt', 'coap_socket_connect_udp', 'coap_cache_derive_key_w_ignore', 'coap_session_check_connect', 'coap_check_dots', 'coap_session_connected', 'coap_session_free', 'coap_delete_str_const', 'coap_opt_parse', 'coap_dtls_new_context']tests/oss-fuzz/split_uri_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_dtls_is_supported', 'coap_tls_is_supported', 'coap_wss_is_supported', 'coap_split_uri_sub', 'coap_ws_is_supported', 'coap_log_impl']tests/oss-fuzz/network_message_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['setup_pki_ssl', 'coap_dispatch', 'handle_request', 'coap_session_connected', 'coap_session_free', 'coap_send_internal', 'coap_session_check_connect', 'coap_pdu_encode_header', 'coap_show_pdu']tests/oss-fuzz/oscore_decrypt_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['oscore_context_release_recipients', 'coap_oscore_decrypt_pdu', 'coap_session_free', 'coap_session_connected', 'coap_pdu_encode_header', 'coap_show_pdu', 'coap_option_filter_get', 'coap_delete_bin_const', 'coap_dtls_new_context']tests/oss-fuzz/persist_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_pdu_parse_opt', 'coap_make_str_const', 'coap_session_free', 'coap_digest_free', 'coap_cache_derive_key_w_ignore', 'coap_get_resource_from_uri_path_lkd', 'coap_send_internal', 'coap_pdu_encode_header', 'coap_touch_observer', 'coap_new_bin_const']tests/oss-fuzz/block_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_make_str_const', 'coap_send_internal', 'coap_session_free', 'coap_handle_dgram', 'coap_dispatch', 'coap_pdu_encode_header', 'coap_show_pdu', 'coap_handle_response_get_block', 'coap_add_data_large_internal', 'coap_handle_request_send_block']tests/oss-fuzz/block_check_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_io_do_epoll_lkd', 'coap_make_str_const', 'coap_add_data_after', 'coap_socket_connect_udp', 'coap_get_resource_from_uri_path_lkd', 'coap_show_pdu', 'coap_add_block_b_data', 'coap_add_block', 'coap_add_option', 'coap_dtls_new_context']tests/oss-fuzz/dtls_define_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_dtls_define_issue']tests/oss-fuzz/proxy_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_session_free', 'coap_free_resource', 'coap_proxy_get_ongoing_session', 'coap_session_connected', 'coap_send_internal', 'coap_show_pdu', 'coap_proxy_forward_request_lkd', 'coap_session_check_connect', 'coap_new_bin_const', 'coap_dtls_new_context']tests/oss-fuzz/oscore_conf_parse_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_new_string', 'coap_delete_bin_const', 'coap_parse_oscore_rcp_conf_mem', 'coap_cleanup', 'coap_dtls_startup', 'LLVMFuzzerTestOneInput', 'coap_parse_oscore_conf_mem']tests/oss-fuzz/ws_frame_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_session_free', 'coap_session_check_connect', 'coap_socket_connect_udp', 'coap_session_connected', 'coap_handle_event_lkd', 'coap_session_disconnected_lkd', 'coap_dtls_new_context', 'coap_dtls_free_context', 'coap_socket_dgrm_close']tests/oss-fuzz/observe_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_make_str_const', 'coap_dispatch', 'coap_pdu_encode_header', 'coap_session_free', 'coap_handle_dgram', 'coap_digest_free', 'coap_send_internal', 'handle_request', 'coap_show_pdu']tests/oss-fuzz/async_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_make_str_const', 'coap_dispatch', 'coap_session_connected', 'coap_pdu_encode_header', 'coap_session_free', 'coap_handle_dgram', 'handle_request', 'coap_send_internal', 'coap_show_pdu']Runtime coverage analysis
This section shows analysis of runtime coverage data.
For futher technical details on how this section is generated, please see the Glossary .
Complex functions with low coverage
| Func name | Function total lines | Lines covered at runtime | percentage covered | Reached by fuzzers |
|---|---|---|---|---|
| coap_show_pdu | 327 | 20 | 6.116% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'pdu_parse_tcp_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_ws_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_socket_connect_udp | 165 | 62 | 37.57% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_new_context | 69 | 37 | 53.62% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_session_connected | 60 | 11 | 18.33% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_print_addr | 40 | 15 | 37.5% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_print_ip_addr | 49 | 15 | 30.61% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'uri_extended_fuzzer', 'cache_key_fuzzer', 'ws_frame_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_debug_send_packet | 42 | 22 | 52.38% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_debug_set_packet_common | 41 | 15 | 36.58% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_socket_send | 118 | 16 | 13.55% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_test_cid_tuple_change | 31 | 4 | 12.90% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_send_internal | 164 | 77 | 46.95% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_remove_from_queue | 38 | 6 | 15.78% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_cancel_session_messages | 32 | 5 | 15.62% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_call_response_handler | 43 | 18 | 41.86% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_dispatch | 399 | 180 | 45.11% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_handle_event_lkd | 71 | 25 | 35.21% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_is_session_proxy | 58 | 10 | 17.24% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| prepend_508_ip | 90 | 35 | 38.88% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_remove_from_queue_token | 45 | 4 | 8.888% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| handle_signaling | 77 | 33 | 42.85% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| handle_response | 74 | 21 | 28.37% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_dtls_info_callback | 66 | 26 | 39.39% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_dgram_ctrl | 61 | 31 | 50.81% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| setup_pki_ssl | 291 | 13 | 4.467% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_remove_option | 78 | 13 | 16.66% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_delete_proxy_subscriber | 39 | 5 | 12.82% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_session_delay_pdu | 38 | 17 | 44.73% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_socket_connect_tcp1 | 102 | 36 | 35.29% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_socket_write | 39 | 20 | 51.28% | ['network_message_fuzzer'] |
| coap_oscore_decrypt_pdu | 677 | 163 | 24.07% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| oscore_validate_sender_seq | 51 | 18 | 35.29% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| oscore_cbor_put_unsigned | 47 | 10 | 21.27% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| oscore_find_context | 105 | 30 | 28.57% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| oscore_log_context | 39 | 4 | 10.25% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_socket_bind_udp | 75 | 29 | 38.66% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_pdu_duplicate_lkd | 75 | 31 | 41.33% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_add_resource_lkd | 38 | 20 | 52.63% | ['block_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer'] |
| coap_add_observer | 143 | 62 | 43.35% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_delete_observer_internal | 40 | 18 | 45.0% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_new_endpoint_lkd | 97 | 34 | 35.05% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_persist_observe_add_lkd | 202 | 30 | 14.85% | ['persist_fuzzer'] |
| coap_find_lg_xmit | 57 | 10 | 17.54% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_find_lg_crcv | 31 | 10 | 32.25% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_handle_request_send_block | 268 | 31 | 11.56% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_handle_request_put_block | 455 | 40 | 8.791% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_handle_response_send_block | 252 | 11 | 4.365% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_handle_response_get_block | 583 | 29 | 4.974% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| setup_block_b | 35 | 18 | 51.42% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_print_wellknown_lkd | 143 | 75 | 52.44% | ['block_fuzzer'] |
| coap_add_data_blocked_response | 101 | 51 | 50.49% | ['block_check_fuzzer'] |
| coap_cancel_observe_lkd | 72 | 13 | 18.05% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_block_check_lg_xmit_timeouts | 41 | 22 | 53.65% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_block_check_lg_crcv_timeouts | 57 | 19 | 33.33% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_block_check_lg_srcv_timeouts | 75 | 19 | 25.33% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_block_check_q_block1_xmit | 52 | 12 | 23.07% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_block_check_q_block2_xmit | 50 | 13 | 26.0% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_io_prepare_io_lkd | 346 | 74 | 21.38% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_client_delay_first | 47 | 5 | 10.63% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_io_do_epoll_lkd | 69 | 10 | 14.49% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_proxy_check_timeouts | 44 | 7 | 15.90% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_resolve_address_info_lkd | 132 | 71 | 53.78% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| get_coap_addr_info | 55 | 16 | 29.09% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| update_coap_addr_port | 39 | 8 | 20.51% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_send_lkd | 290 | 32 | 11.03% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_proxy_log_entry | 32 | 3 | 9.375% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_proxy_del_req | 34 | 10 | 29.41% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_verify_proxy_scheme_supported | 45 | 7 | 15.55% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_proxy_forward_request_lkd | 243 | 108 | 44.44% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_proxy_get_ongoing_session | 162 | 63 | 38.88% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_get_uri_proxy_scheme_info | 51 | 16 | 31.37% | ['block_fuzzer', 'network_message_fuzzer', 'observe_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_resource_proxy_uri_init2 | 37 | 16 | 43.24% | ['proxy_fuzzer'] |
| coap_ws_write | 71 | 9 | 12.67% | ['ws_frame_fuzzer'] |
| coap_ws_rd_http_header_server | 79 | 10 | 12.65% | ['ws_frame_fuzzer'] |
| coap_ws_rd_http_header_client | 62 | 11 | 17.74% | ['ws_frame_fuzzer'] |
Files and Directories in report
This section shows which files and directories are considered in this report. The main reason for showing this is fuzz introspector may include more code in the reasoning than is desired. This section helps identify if too many files/directories are included, e.g. third party code, which may be irrelevant for the threat model. In the event too much is included, fuzz introspector supports a configuration file that can exclude data from the report. See the following link for more information on how to create a config file: link
Files in report
| Source file | Reached by | Covered by |
|---|---|---|
| [] | [] | |
| /src/libcoap/./include/coap3/coap_uri.h | ['uri_extended_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | [] |
| /src/libcoap/./include/coap3/coap_resource_internal.h | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | [] |
| /src/libcoap/src/coap_openssl.c | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'split_uri_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'split_uri_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_str.c | ['pdu_parse_udp_fuzzer', 'get_asn1_tag_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['pdu_parse_udp_fuzzer', 'get_asn1_tag_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_session.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/pdu_parse_udp_target.c | ['pdu_parse_udp_fuzzer'] | ['pdu_parse_udp_fuzzer'] |
| /src/libcoap/src/coap_dgrm_posix.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /usr/include/openssl/ssl.h | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | [] |
| /src/libcoap/src/oscore/oscore_crypto.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['oscore_decrypt_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/async_target.c | ['async_fuzzer'] | ['async_fuzzer'] |
| /src/libcoap/./include/coap3/coap_pdu_internal.h | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | [] |
| /src/libcoap/src/coap_address.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/oscore/oscore.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['oscore_decrypt_fuzzer', 'oscore_conf_parse_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/proxy_target.c | ['proxy_fuzzer'] | ['proxy_fuzzer'] |
| /src/libcoap/src/coap_asn1.c | ['get_asn1_tag_fuzzer'] | ['get_asn1_tag_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/oscore_decrypt_target.c | ['oscore_decrypt_fuzzer'] | ['oscore_decrypt_fuzzer'] |
| /src/libcoap/src/coap_option.c | ['uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/oscore/oscore_cbor.c | ['oscore_cbor_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['oscore_cbor_fuzzer', 'oscore_decrypt_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/cache_key_target.c | ['cache_key_fuzzer'] | ['cache_key_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/uri_extended_target.c | ['uri_extended_fuzzer'] | ['uri_extended_fuzzer'] |
| /src/libcoap/src/coap_strm_posix.c | ['uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'split_uri_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'split_uri_fuzzer', 'network_message_fuzzer'] |
| /src/libcoap/src/oscore/oscore_cose.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['oscore_decrypt_fuzzer', 'oscore_conf_parse_fuzzer'] |
| /src/libcoap/src/coap_event.c | ['block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_ws.c | ['uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'split_uri_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'split_uri_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/persist_target.c | ['persist_fuzzer'] | ['persist_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/pdu_parse_ws_target.c | ['pdu_parse_ws_fuzzer'] | ['pdu_parse_ws_fuzzer'] |
| /src/libcoap/src/coap_pdu.c | ['uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/oscore/oscore_context.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/observe_target.c | ['observe_fuzzer'] | ['observe_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/get_asn1_tag_target.c | ['get_asn1_tag_fuzzer'] | ['get_asn1_tag_fuzzer'] |
| /src/libcoap/src/coap_time.c | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'get_asn1_tag_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'split_uri_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'dtls_define_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'split_uri_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/split_uri_target.c | ['split_uri_fuzzer'] | ['split_uri_fuzzer'] |
| /src/libcoap/src/coap_io_posix.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_mem.c | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'get_asn1_tag_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'get_asn1_tag_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_block.c | ['pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['network_message_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/pdu_parse_tcp_target.c | ['pdu_parse_tcp_fuzzer'] | ['pdu_parse_tcp_fuzzer'] |
| /usr/include/openssl/x509v3.h | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | [] |
| /src/libcoap/src/coap_proxy.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_oscore.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/oscore_conf_parse_target.c | ['oscore_conf_parse_fuzzer'] | ['oscore_conf_parse_fuzzer'] |
| /src/libcoap/src/coap_cache.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'persist_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'observe_fuzzer'] |
| /src/libcoap/src/coap_async.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/coap_fuzz_helper.c | ['block_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['block_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_debug.c | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'get_asn1_tag_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'split_uri_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'dtls_define_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'split_uri_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'dtls_define_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_resource.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_io.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['network_message_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/ws_frame_target.c | ['ws_frame_fuzzer'] | ['ws_frame_fuzzer'] |
| /src/libcoap/src/coap_encode.c | ['uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_prng.c | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_uri.c | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'split_uri_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'split_uri_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/dtls_define_target.c | ['dtls_define_fuzzer'] | ['dtls_define_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/oscore_cbor_target.c | ['oscore_cbor_fuzzer'] | ['oscore_cbor_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/network_message_target.c | ['network_message_fuzzer'] | ['network_message_fuzzer'] |
| /src/libcoap/./include/coap3/coap_block_internal.h | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | [] |
| /src/libcoap/tests/oss-fuzz/block_target.c | ['block_fuzzer'] | ['block_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/block_check_target.c | ['block_check_fuzzer'] | ['block_check_fuzzer'] |
| /src/libcoap/src/coap_subscribe.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/src/coap_net.c | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['oscore_cbor_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'pdu_parse_ws_fuzzer', 'cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'oscore_conf_parse_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
| /src/libcoap/./include/coap3/coap_address.h | [] | [] |
| /src/libcoap/src/coap_dtls.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'dtls_define_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['network_message_fuzzer', 'dtls_define_fuzzer'] |
| /src/libcoap/src/coap_netif.c | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] | ['cache_key_fuzzer', 'network_message_fuzzer', 'oscore_decrypt_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'proxy_fuzzer', 'ws_frame_fuzzer', 'observe_fuzzer', 'async_fuzzer'] |
Directories in report
| Directory |
|---|
| /src/libcoap/src/ |
| /src/libcoap/src/oscore/ |
| /src/libcoap/./include/coap3/ |
| /src/libcoap/tests/oss-fuzz/ |
| /usr/include/openssl/ |
Metadata section
This sections shows the raw data that is used to produce this report. This is mainly used for further processing and developer debugging.