Project overview: libcoap
High level conclusions
Reachability and coverage overview
Project functions overview
The following table shows data about each function in the project. The functions included in this table correspond to all functions that exist in the executables of the fuzzers. As such, there may be functions that are from third-party libraries.
For further technical details on the meaning of columns in the below table, please see the Glossary .
| Func name | Functions filename | Args | Function call depth | Reached by Fuzzers | Runtime reached by Fuzzers | Combined reached by Fuzzers | Fuzzers runtime hit | Func lines hit % | I Count | BB Count | Cyclomatic complexity | Functions reached | Reached by functions | Accumulated cyclomatic complexity | Undiscovered complexity |
|---|
Fuzzer details
Fuzzer: dtls_define_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
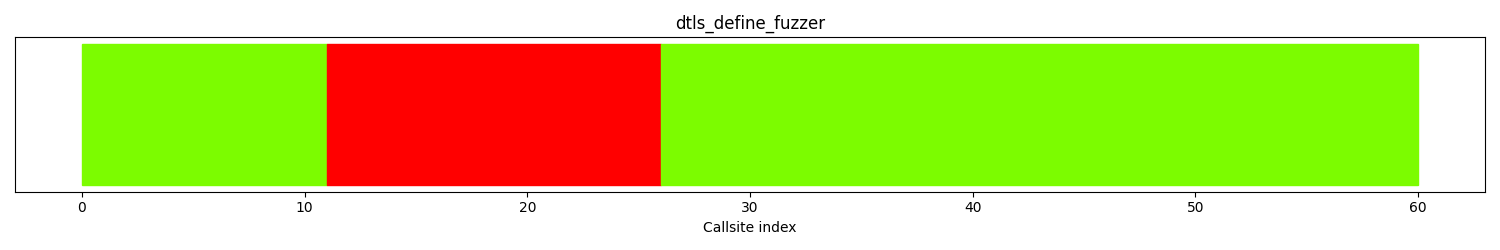
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 15 | 25.0% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 45 | 75.0% |
| All colors | 60 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 15 | 10 | coap_dtls_define_issue | call site: 00010 | print_timestamp |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/dtls_define_target.c | 1 |
| src/coap_debug.c | 5 |
| src/coap_dtls.c | 3 |
| src/coap_time.c | 3 |
Fuzzer: get_asn1_tag_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 17 | 53.1% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 15 | 46.8% |
| All colors | 32 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 17 | 9 | coap_new_string | call site: 00009 | coap_log_impl |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/get_asn1_tag_target.c | 1 |
| src/coap_asn1.c | 4 |
| src/coap_str.c | 3 |
| src/coap_mem.c | 2 |
| src/coap_debug.c | 4 |
| src/coap_time.c | 3 |
Fuzzer: split_uri_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 22 | 33.3% |
| gold | [1:9] | 13 | 19.6% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 4 | 6.06% |
| lawngreen | 50+ | 27 | 40.9% |
| All colors | 66 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 4 | 28 | coap_dtls_is_supported | call site: 00028 | coap_log_impl |
| 4 | 40 | coap_tls_is_supported | call site: 00040 | coap_log_impl |
| 4 | 50 | coap_wss_is_supported | call site: 00050 | coap_log_impl |
| 2 | 25 | coap_dtls_is_supported | call site: 00025 | coap_log_impl |
| 2 | 33 | coap_split_uri_sub | call site: 00033 | coap_log_impl |
| 2 | 37 | coap_tls_is_supported | call site: 00037 | coap_log_impl |
| 2 | 46 | coap_ws_is_supported | call site: 00046 | coap_log_impl |
| 1 | 6 | coap_split_uri_sub | call site: 00006 | vsnprintf |
| 1 | 17 | coap_log_impl | call site: 00017 | snprintf |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/split_uri_target.c | 1 |
| src/coap_uri.c | 2 |
| src/coap_debug.c | 4 |
| src/coap_time.c | 3 |
| src/coap_openssl.c | 2 |
| src/coap_strm_posix.c | 1 |
| src/coap_ws.c | 2 |
Fuzzer: oscore_cbor_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 5 | 10.0% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 45 | 90.0% |
| All colors | 50 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 2 | 16 | coap_cleanup | call site: 00016 | ENGINE_finish |
| 1 | 11 | coap_dtls_startup | call site: 00011 | OPENSSL_init_crypto |
| 1 | 14 | LLVMFuzzerTestOneInput | call site: 00014 | coap_cleanup |
| 1 | 20 | coap_cleanup | call site: 00020 | coap_free_type |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/oscore_cbor_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 3 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 3 |
| src/coap_openssl.c | 3 |
| src/coap_debug.c | 2 |
| src/coap_uri.c | 1 |
| src/oscore/oscore_cbor.c | 12 |
Fuzzer: oscore_conf_parse_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 30 | 17.2% |
| gold | [1:9] | 20 | 11.4% |
| yellow | [10:29] | 10 | 5.74% |
| greenyellow | [30:49] | 4 | 2.29% |
| lawngreen | 50+ | 110 | 63.2% |
| All colors | 174 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 16 | 41 | coap_new_string | call site: 00041 | coap_log_impl |
| 4 | 94 | coap_delete_bin_const | call site: 00094 | coap_log_impl |
| 4 | 126 | coap_parse_oscore_rcp_conf_mem | call site: 00126 | coap_log_impl |
| 2 | 16 | coap_cleanup | call site: 00016 | ENGINE_finish |
| 1 | 11 | coap_dtls_startup | call site: 00011 | OPENSSL_init_crypto |
| 1 | 14 | LLVMFuzzerTestOneInput | call site: 00014 | coap_cleanup |
| 1 | 20 | coap_cleanup | call site: 00020 | coap_free_type |
| 1 | 148 | coap_parse_oscore_conf_mem | call site: 00148 | __assert_fail |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/oscore_conf_parse_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 4 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 3 |
| src/coap_openssl.c | 3 |
| src/coap_debug.c | 6 |
| src/coap_uri.c | 1 |
| src/coap_oscore.c | 10 |
| src/coap_str.c | 6 |
| src/oscore/oscore_cose.c | 4 |
| src/oscore/oscore.c | 1 |
Fuzzer: pdu_parse_udp_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 242 | 54.2% |
| gold | [1:9] | 19 | 4.26% |
| yellow | [10:29] | 14 | 3.13% |
| greenyellow | [30:49] | 2 | 0.44% |
| lawngreen | 50+ | 169 | 37.8% |
| All colors | 446 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 157 | 247 | coap_show_pdu | call site: 00247 | coap_option_next |
| 19 | 408 | coap_pdu_encode_header | call site: 00408 | coap_log_impl |
| 17 | 31 | coap_pdu_parse2 | call site: 00031 | coap_log_impl |
| 4 | 56 | coap_pdu_parse_header | call site: 00056 | coap_log_impl |
| 4 | 103 | coap_pdu_parse_opt | call site: 00103 | coap_log_impl |
| 4 | 108 | coap_pdu_parse_opt | call site: 00108 | coap_log_impl |
| 4 | 194 | coap_dtls_is_supported | call site: 00194 | coap_log_impl |
| 4 | 206 | coap_tls_is_supported | call site: 00206 | coap_log_impl |
| 4 | 216 | coap_wss_is_supported | call site: 00216 | coap_log_impl |
| 3 | 175 | coap_get_uri_path | call site: 00175 | coap_new_string |
| 2 | 50 | coap_realloc_type | call site: 00050 | coap_log_impl |
| 2 | 156 | coap_new_string | call site: 00156 | coap_log_impl |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/pdu_parse_udp_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 4 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 4 |
| src/coap_openssl.c | 5 |
| src/coap_pdu.c | 18 |
| src/coap_debug.c | 13 |
| src/coap_option.c | 12 |
| src/coap_encode.c | 3 |
| src/coap_uri.c | 9 |
| src/coap_str.c | 3 |
| src/coap_strm_posix.c | 1 |
| src/coap_ws.c | 2 |
| src/coap_block.c | 1 |
Fuzzer: observe_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4416 | 87.2% |
| gold | [1:9] | 52 | 1.02% |
| yellow | [10:29] | 278 | 5.49% |
| greenyellow | [30:49] | 10 | 0.19% |
| lawngreen | 50+ | 304 | 6.00% |
| All colors | 5060 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 499 | 2166 | coap_make_str_const | call site: 02166 | coap_session_release_lkd |
| 355 | 3892 | coap_dispatch | call site: 03892 | coap_oscore_decrypt_pdu |
| 355 | 4302 | coap_dispatch | call site: 04302 | handle_response |
| 271 | 1343 | coap_send_internal | call site: 01343 | coap_send_pdu |
| 262 | 3519 | coap_session_free | call site: 03519 | coap_dtls_handle_timeout |
| 245 | 4665 | coap_handle_dgram | call site: 04665 | coap_handle_event_lkd |
| 223 | 1804 | coap_find_lg_xmit_response | call site: 01804 | coap_handle_event_lkd |
| 185 | 3116 | handle_request | call site: 03116 | coap_handle_request_put_block |
| 177 | 1053 | coap_socket_connect_udp | call site: 01053 | coap_session_reestablished |
| 158 | 729 | coap_show_pdu | call site: 00729 | coap_send_test_extended_token |
| 79 | 3430 | handle_request | call site: 03430 | coap_resource_release_lkd |
| 71 | 2700 | coap_pdu_release_lkd | call site: 02700 | coap_session_max_pdu_size_lkd |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/observe_target.c | 3 |
| src/coap_net.c | 64 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 25 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
| tests/oss-fuzz/coap_fuzz_helper.c | 2 |
Fuzzer: cache_key_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4685 | 93.3% |
| gold | [1:9] | 39 | 0.77% |
| yellow | [10:29] | 32 | 0.63% |
| greenyellow | [30:49] | 215 | 4.28% |
| lawngreen | 50+ | 46 | 0.91% |
| All colors | 5017 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1010 | 3828 | coap_pdu_parse_opt | call site: 03828 | coap_handle_event_lkd |
| 722 | 1044 | coap_socket_connect_udp | call site: 01044 | coap_session_reestablished |
| 539 | 2117 | coap_session_check_connect | call site: 02117 | coap_session_release_lkd |
| 473 | 3027 | coap_delete_str_const | call site: 03027 | coap_delete_observer_internal |
| 271 | 3510 | coap_session_free | call site: 03510 | coap_dtls_handle_timeout |
| 261 | 617 | coap_check_dots | call site: 00617 | coap_add_data_large_request_lkd |
| 241 | 1777 | coap_digest_free | call site: 01777 | coap_handle_event_lkd |
| 241 | 2669 | coap_cache_derive_key_w_ignore | call site: 02669 | coap_cancel_observe_lkd |
| 113 | 2913 | coap_session_connected | call site: 02913 | coap_handle_event_lkd |
| 87 | 429 | coap_option_next | call site: 00429 | coap_split_proxy_uri |
| 84 | 879 | coap_session_max_pdu_size_lkd | call site: 00879 | coap_send_internal |
| 70 | 99 | coap_dtls_new_context | call site: 00099 | coap_session_str |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/cache_key_target.c | 1 |
| src/coap_net.c | 64 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 16 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 11 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 20 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
Fuzzer: oscore_decrypt_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4609 | 89.9% |
| gold | [1:9] | 140 | 2.73% |
| yellow | [10:29] | 294 | 5.73% |
| greenyellow | [30:49] | 21 | 0.40% |
| lawngreen | 50+ | 61 | 1.19% |
| All colors | 5125 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 705 | 4316 | coap_oscore_decrypt_pdu | call site: 04316 | coap_delete_node_lkd |
| 656 | 2374 | oscore_context_release_recipients | call site: 02374 | coap_session_release_lkd |
| 473 | 3147 | coap_delete_str_const | call site: 03147 | coap_delete_observer_internal |
| 381 | 3630 | coap_session_free | call site: 03630 | coap_dtls_handle_timeout |
| 307 | 1842 | coap_send_internal | call site: 01842 | coap_io_process_lkd |
| 213 | 853 | coap_show_pdu | call site: 00853 | coap_send_test_extended_token |
| 177 | 1175 | coap_socket_connect_udp | call site: 01175 | coap_session_reestablished |
| 113 | 3033 | coap_session_connected | call site: 03033 | coap_handle_event_lkd |
| 95 | 4219 | coap_oscore_decrypt_pdu | call site: 04219 | coap_handle_event_lkd |
| 82 | 569 | coap_option_filter_get | call site: 00569 | coap_split_proxy_uri |
| 73 | 1391 | coap_add_data_after | call site: 01391 | coap_rebuild_pdu_for_proxy |
| 70 | 85 | coap_delete_bin_const | call site: 00085 | coap_parse_oscore_rcp_conf_mem |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/oscore_decrypt_target.c | 1 |
| src/coap_net.c | 64 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_oscore.c | 28 |
| src/coap_str.c | 10 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 20 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
Fuzzer: block_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4299 | 84.6% |
| gold | [1:9] | 166 | 3.26% |
| yellow | [10:29] | 35 | 0.68% |
| greenyellow | [30:49] | 98 | 1.92% |
| lawngreen | 50+ | 482 | 9.48% |
| All colors | 5080 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 499 | 2166 | coap_make_str_const | call site: 02166 | coap_session_release_lkd |
| 354 | 4302 | coap_dispatch | call site: 04302 | handle_response |
| 324 | 3892 | coap_dispatch | call site: 03892 | coap_oscore_decrypt_pdu |
| 271 | 1343 | coap_send_internal | call site: 01343 | coap_send_pdu |
| 262 | 3519 | coap_session_free | call site: 03519 | coap_dtls_handle_timeout |
| 245 | 4665 | coap_handle_dgram | call site: 04665 | coap_handle_event_lkd |
| 177 | 1053 | coap_socket_connect_udp | call site: 01053 | coap_session_reestablished |
| 158 | 729 | coap_show_pdu | call site: 00729 | coap_send_test_extended_token |
| 134 | 1893 | coap_add_data_large_internal | call site: 01893 | coap_send_q_block1 |
| 119 | 3241 | coap_handle_request_send_block | call site: 03241 | coap_send_internal |
| 79 | 3430 | handle_request | call site: 03430 | coap_resource_release_lkd |
| 71 | 2700 | coap_pdu_release_lkd | call site: 02700 | coap_session_max_pdu_size_lkd |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/block_target.c | 3 |
| src/coap_net.c | 64 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_io.c | 10 |
| src/coap_session.c | 55 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 59 |
| src/coap_resource.c | 25 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
| tests/oss-fuzz/coap_fuzz_helper.c | 2 |
Fuzzer: network_message_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4292 | 84.6% |
| gold | [1:9] | 52 | 1.02% |
| yellow | [10:29] | 72 | 1.41% |
| greenyellow | [30:49] | 19 | 0.37% |
| lawngreen | 50+ | 638 | 12.5% |
| All colors | 5073 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 344 | 2356 | setup_pki_ssl | call site: 02356 | coap_session_release_lkd |
| 324 | 3893 | coap_dispatch | call site: 03893 | coap_oscore_decrypt_pdu |
| 307 | 1721 | coap_send_internal | call site: 01721 | coap_io_process_lkd |
| 294 | 3095 | handle_request | call site: 03095 | coap_session_max_pdu_size_lkd |
| 272 | 4304 | coap_dispatch | call site: 04304 | coap_send_ack_lkd |
| 262 | 3520 | coap_session_free | call site: 03520 | coap_dtls_handle_timeout |
| 235 | 1348 | coap_send_internal | call site: 01348 | coap_send_pdu |
| 224 | 2127 | coap_session_check_connect | call site: 02127 | coap_session_release_lkd |
| 176 | 1055 | coap_socket_connect_udp | call site: 01055 | coap_session_reestablished |
| 158 | 731 | coap_show_pdu | call site: 00731 | coap_send_test_extended_token |
| 147 | 4764 | coap_epoll_ctl_mod | call site: 04764 | coap_accept_endpoint |
| 113 | 2923 | coap_session_connected | call site: 02923 | coap_handle_event_lkd |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/network_message_target.c | 7 |
| src/coap_net.c | 78 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 66 |
| src/coap_debug.c | 19 |
| src/coap_address.c | 16 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 20 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
Fuzzer: pdu_parse_ws_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 243 | 54.4% |
| gold | [1:9] | 15 | 3.36% |
| yellow | [10:29] | 18 | 4.03% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 170 | 38.1% |
| All colors | 446 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 157 | 247 | coap_show_pdu | call site: 00247 | coap_option_next |
| 17 | 31 | coap_pdu_parse2 | call site: 00031 | coap_log_impl |
| 13 | 414 | coap_pdu_encode_header | call site: 00414 | coap_log_impl |
| 5 | 405 | LLVMFuzzerTestOneInput | call site: 00405 | coap_log_impl |
| 4 | 53 | coap_pdu_parse2 | call site: 00053 | coap_log_impl |
| 4 | 103 | coap_pdu_parse_opt | call site: 00103 | coap_log_impl |
| 4 | 108 | coap_pdu_parse_opt | call site: 00108 | coap_log_impl |
| 4 | 194 | coap_dtls_is_supported | call site: 00194 | coap_log_impl |
| 4 | 206 | coap_tls_is_supported | call site: 00206 | coap_log_impl |
| 4 | 216 | coap_wss_is_supported | call site: 00216 | coap_log_impl |
| 3 | 175 | coap_get_uri_path | call site: 00175 | coap_new_string |
| 2 | 50 | coap_realloc_type | call site: 00050 | coap_log_impl |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/pdu_parse_ws_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 4 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 4 |
| src/coap_openssl.c | 5 |
| src/coap_pdu.c | 18 |
| src/coap_debug.c | 13 |
| src/coap_option.c | 12 |
| src/coap_encode.c | 3 |
| src/coap_uri.c | 9 |
| src/coap_str.c | 3 |
| src/coap_strm_posix.c | 1 |
| src/coap_ws.c | 2 |
| src/coap_block.c | 1 |
Fuzzer: uri_extended_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 83 | 38.0% |
| gold | [1:9] | 4 | 1.83% |
| yellow | [10:29] | 1 | 0.45% |
| greenyellow | [30:49] | 6 | 2.75% |
| lawngreen | 50+ | 124 | 56.8% |
| All colors | 218 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 15 | 186 | coap_uri_into_optlist_abbrev | call site: 00186 | coap_new_optlist |
| 14 | 20 | coap_split_uri_sub | call site: 00020 | print_timestamp |
| 12 | 91 | coap_opt_parse | call site: 00091 | coap_log_impl |
| 6 | 136 | LLVMFuzzerTestOneInput | call site: 00136 | coap_path_into_optlist_abbrev |
| 5 | 147 | coap_new_optlist | call site: 00147 | coap_insert_optlist |
| 4 | 41 | coap_dtls_is_supported | call site: 00041 | coap_log_impl |
| 4 | 53 | coap_tls_is_supported | call site: 00053 | coap_log_impl |
| 4 | 63 | coap_wss_is_supported | call site: 00063 | coap_log_impl |
| 4 | 120 | coap_opt_setheader | call site: 00120 | coap_log_impl |
| 2 | 38 | coap_dtls_is_supported | call site: 00038 | coap_log_impl |
| 2 | 46 | coap_split_uri_sub | call site: 00046 | coap_log_impl |
| 2 | 50 | coap_tls_is_supported | call site: 00050 | coap_log_impl |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/uri_extended_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 4 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 3 |
| src/coap_openssl.c | 5 |
| src/coap_debug.c | 7 |
| src/coap_uri.c | 26 |
| src/coap_strm_posix.c | 1 |
| src/coap_ws.c | 2 |
| src/coap_option.c | 7 |
| src/coap_encode.c | 1 |
| src/coap_pdu.c | 1 |
| ./include/coap3/coap_uri.h | 1 |
Fuzzer: persist_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4596 | 88.2% |
| gold | [1:9] | 6 | 0.11% |
| yellow | [10:29] | 2 | 0.03% |
| greenyellow | [30:49] | 4 | 0.07% |
| lawngreen | 50+ | 599 | 11.5% |
| All colors | 5207 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1008 | 3850 | coap_pdu_parse_opt | call site: 03850 | coap_handle_event_lkd |
| 499 | 2177 | coap_make_str_const | call site: 02177 | coap_session_release_lkd |
| 271 | 1354 | coap_send_internal | call site: 01354 | coap_send_pdu |
| 271 | 3530 | coap_session_free | call site: 03530 | coap_dtls_handle_timeout |
| 223 | 1815 | coap_find_lg_xmit_response | call site: 01815 | coap_handle_event_lkd |
| 219 | 3099 | coap_get_resource_from_uri_path_lkd | call site: 03099 | coap_session_max_pdu_size_lkd |
| 177 | 1064 | coap_socket_connect_udp | call site: 01064 | coap_session_reestablished |
| 160 | 2711 | coap_pdu_release_lkd | call site: 02711 | coap_session_max_pdu_size_lkd |
| 160 | 3360 | coap_touch_observer | call site: 03360 | coap_delete_observer_request |
| 158 | 740 | coap_show_pdu | call site: 00740 | coap_send_test_extended_token |
| 111 | 1242 | coap_add_option | call site: 01242 | coap_send_internal |
| 79 | 1630 | coap_send_internal | call site: 01630 | coap_session_disconnected_lkd |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/persist_target.c | 5 |
| src/coap_subscribe.c | 15 |
| src/coap_net.c | 64 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 18 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 29 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 13 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_async.c | 4 |
Fuzzer: proxy_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
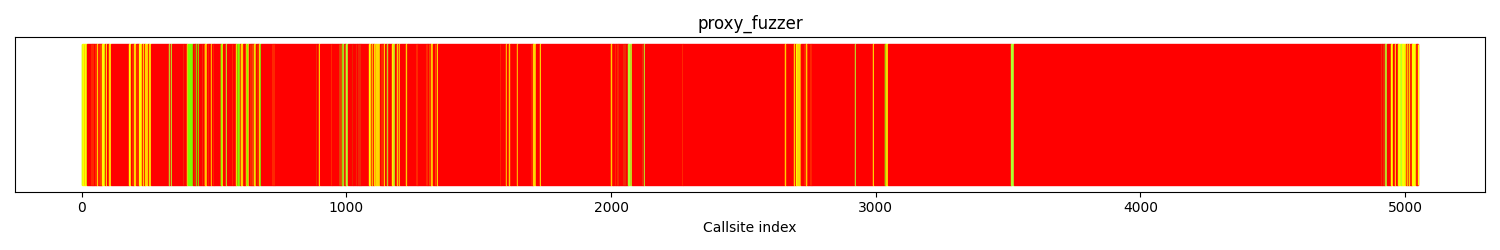
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4535 | 89.8% |
| gold | [1:9] | 106 | 2.09% |
| yellow | [10:29] | 251 | 4.97% |
| greenyellow | [30:49] | 92 | 1.82% |
| lawngreen | 50+ | 66 | 1.30% |
| All colors | 5050 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1391 | 3520 | coap_session_free | call site: 03520 | coap_dtls_handle_timeout |
| 466 | 3044 | coap_free_resource | call site: 03044 | coap_check_async |
| 387 | 2270 | coap_proxy_get_ongoing_session | call site: 02270 | coap_new_client_session_oscore_pki3_lkd |
| 266 | 1733 | coap_send_lkd | call site: 01733 | coap_cancel_observe_lkd |
| 239 | 1344 | coap_send_internal | call site: 01344 | coap_send_pdu |
| 160 | 2760 | coap_proxy_forward_request_lkd | call site: 02760 | coap_proxy_call_response_handler |
| 158 | 730 | coap_show_pdu | call site: 00730 | coap_send_test_extended_token |
| 142 | 2127 | coap_session_check_connect | call site: 02127 | coap_session_release_lkd |
| 70 | 109 | coap_dtls_new_context | call site: 00109 | coap_session_str |
| 69 | 260 | coap_dtls_free_context | call site: 00260 | coap_new_endpoint_lkd |
| 66 | 2923 | coap_session_connected | call site: 02923 | coap_handle_event_lkd |
| 53 | 1646 | coap_delete_node_lkd | call site: 01646 | coap_delete_observers |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/proxy_target.c | 4 |
| src/coap_net.c | 64 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_io.c | 10 |
| src/coap_session.c | 54 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 23 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 23 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
Fuzzer: pdu_parse_tcp_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
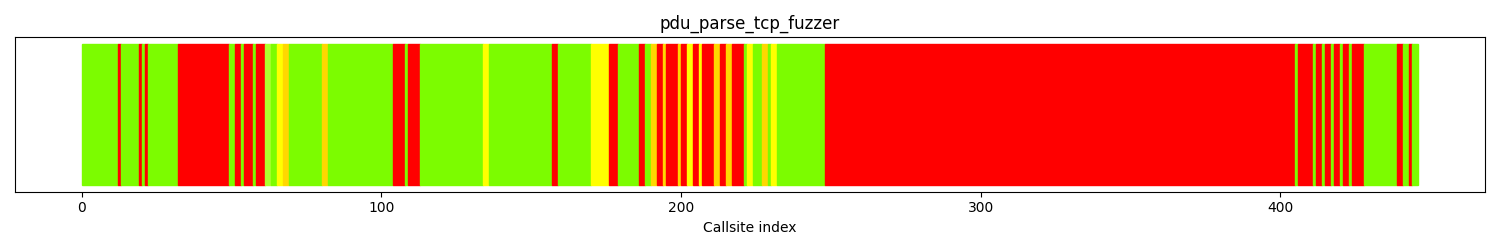
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 240 | 53.8% |
| gold | [1:9] | 14 | 3.13% |
| yellow | [10:29] | 17 | 3.81% |
| greenyellow | [30:49] | 2 | 0.44% |
| lawngreen | 50+ | 173 | 38.7% |
| All colors | 446 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 157 | 247 | coap_show_pdu | call site: 00247 | coap_option_next |
| 17 | 31 | coap_pdu_parse2 | call site: 00031 | coap_log_impl |
| 5 | 405 | LLVMFuzzerTestOneInput | call site: 00405 | coap_log_impl |
| 4 | 103 | coap_pdu_parse_opt | call site: 00103 | coap_log_impl |
| 4 | 108 | coap_pdu_parse_opt | call site: 00108 | coap_log_impl |
| 4 | 194 | coap_dtls_is_supported | call site: 00194 | coap_log_impl |
| 4 | 206 | coap_tls_is_supported | call site: 00206 | coap_log_impl |
| 4 | 216 | coap_wss_is_supported | call site: 00216 | coap_log_impl |
| 4 | 423 | coap_pdu_encode_header | call site: 00423 | coap_log_impl |
| 3 | 53 | coap_pdu_parse2 | call site: 00053 | coap_log_impl |
| 3 | 57 | coap_pdu_parse_header | call site: 00057 | coap_log_impl |
| 3 | 175 | coap_get_uri_path | call site: 00175 | coap_new_string |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/pdu_parse_tcp_target.c | 1 |
| src/coap_net.c | 2 |
| src/coap_time.c | 4 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 4 |
| src/coap_openssl.c | 5 |
| src/coap_pdu.c | 18 |
| src/coap_debug.c | 13 |
| src/coap_option.c | 12 |
| src/coap_encode.c | 3 |
| src/coap_uri.c | 9 |
| src/coap_str.c | 3 |
| src/coap_strm_posix.c | 1 |
| src/coap_ws.c | 2 |
| src/coap_block.c | 1 |
Fuzzer: async_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4504 | 88.1% |
| gold | [1:9] | 67 | 1.31% |
| yellow | [10:29] | 113 | 2.21% |
| greenyellow | [30:49] | 297 | 5.81% |
| lawngreen | 50+ | 130 | 2.54% |
| All colors | 5111 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 533 | 2166 | coap_make_str_const | call site: 02166 | coap_session_release_lkd |
| 355 | 3892 | coap_dispatch | call site: 03892 | coap_oscore_decrypt_pdu |
| 272 | 4303 | coap_dispatch | call site: 04303 | coap_send_ack_lkd |
| 271 | 1343 | coap_send_internal | call site: 01343 | coap_send_pdu |
| 262 | 3519 | coap_session_free | call site: 03519 | coap_dtls_handle_timeout |
| 248 | 3115 | handle_request | call site: 03115 | coap_handle_request_put_block |
| 245 | 4665 | coap_handle_dgram | call site: 04665 | coap_handle_event_lkd |
| 223 | 1804 | coap_find_lg_xmit_response | call site: 01804 | coap_handle_event_lkd |
| 177 | 1053 | coap_socket_connect_udp | call site: 01053 | coap_session_reestablished |
| 158 | 729 | coap_show_pdu | call site: 00729 | coap_send_test_extended_token |
| 81 | 1720 | coap_send_internal | call site: 01720 | coap_io_process_lkd |
| 72 | 3437 | coap_free_async_sub | call site: 03437 | coap_retransmit |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/async_target.c | 3 |
| src/coap_net.c | 64 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_io.c | 10 |
| src/coap_session.c | 55 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 24 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_async.c | 15 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
| tests/oss-fuzz/coap_fuzz_helper.c | 2 |
Fuzzer: block_check_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4576 | 89.3% |
| gold | [1:9] | 10 | 0.19% |
| yellow | [10:29] | 380 | 7.41% |
| greenyellow | [30:49] | 47 | 0.91% |
| lawngreen | 50+ | 111 | 2.16% |
| All colors | 5124 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1252 | 3644 | coap_io_do_epoll_lkd | call site: 03644 | coap_read_endpoint |
| 709 | 2167 | coap_make_str_const | call site: 02167 | coap_session_release_lkd |
| 396 | 1270 | coap_add_data_after | call site: 01270 | coap_send_pdu |
| 201 | 3089 | coap_get_resource_from_uri_path_lkd | call site: 03089 | coap_session_max_pdu_size_lkd |
| 177 | 1054 | coap_socket_connect_udp | call site: 01054 | coap_session_reestablished |
| 158 | 730 | coap_show_pdu | call site: 00730 | coap_send_test_extended_token |
| 147 | 3291 | coap_add_block_b_data | call site: 03291 | coap_send_internal |
| 94 | 1934 | coap_add_block | call site: 01934 | coap_send_internal |
| 88 | 1674 | coap_block_delete_lg_xmit | call site: 01674 | coap_cancel_session_messages |
| 70 | 109 | coap_dtls_new_context | call site: 00109 | coap_session_str |
| 66 | 458 | coap_new_string | call site: 00458 | coap_split_proxy_uri |
| 66 | 2923 | coap_session_connected | call site: 02923 | coap_handle_event_lkd |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/block_check_target.c | 2 |
| src/coap_net.c | 64 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 65 |
| src/coap_debug.c | 19 |
| src/coap_io.c | 10 |
| src/coap_session.c | 55 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 2 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 5 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 35 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 61 |
| src/coap_resource.c | 23 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
Fuzzer: ws_frame_fuzzer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 4897 | 94.8% |
| gold | [1:9] | 49 | 0.94% |
| yellow | [10:29] | 206 | 3.98% |
| greenyellow | [30:49] | 3 | 0.05% |
| lawngreen | 50+ | 9 | 0.17% |
| All colors | 5164 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 1391 | 3510 | coap_session_free | call site: 03510 | coap_dtls_handle_timeout |
| 793 | 2117 | coap_session_check_connect | call site: 02117 | coap_session_release_lkd |
| 583 | 1044 | coap_socket_connect_udp | call site: 01044 | coap_session_reestablished |
| 473 | 3027 | coap_delete_str_const | call site: 03027 | coap_delete_observer_internal |
| 424 | 539 | coap_session_free | call site: 00539 | coap_delete_proxy_subscriber |
| 345 | 1673 | coap_session_disconnected_lkd | call site: 01673 | coap_delete_node_lkd |
| 135 | 386 | coap_handle_event_lkd | call site: 00386 | coap_proxy_remove_association |
| 113 | 2913 | coap_session_connected | call site: 02913 | coap_handle_event_lkd |
| 70 | 99 | coap_dtls_new_context | call site: 00099 | coap_session_str |
| 69 | 250 | coap_dtls_free_context | call site: 00250 | coap_new_endpoint_lkd |
| 46 | 328 | coap_socket_dgrm_close | call site: 00328 | coap_netif_strm_listen |
| 43 | 4994 | coap_ws_rd_http_header_client | call site: 04994 | coap_ws_build_key_hash |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/oss-fuzz/ws_frame_target.c | 4 |
| src/coap_net.c | 64 |
| src/coap_time.c | 5 |
| src/coap_prng.c | 2 |
| src/coap_mem.c | 5 |
| src/coap_openssl.c | 67 |
| src/coap_debug.c | 16 |
| src/coap_io.c | 10 |
| src/coap_session.c | 53 |
| src/coap_address.c | 16 |
| src/coap_netif.c | 11 |
| src/coap_strm_posix.c | 6 |
| src/coap_ws.c | 15 |
| src/coap_dgrm_posix.c | 5 |
| src/coap_io_posix.c | 4 |
| src/coap_proxy.c | 22 |
| src/coap_uri.c | 20 |
| src/coap_option.c | 21 |
| src/coap_encode.c | 6 |
| src/coap_str.c | 10 |
| src/coap_pdu.c | 34 |
| src/coap_cache.c | 5 |
| src/coap_block.c | 54 |
| src/coap_resource.c | 20 |
| src/coap_oscore.c | 19 |
| ./include/coap3/coap_uri.h | 1 |
| src/oscore/oscore_cose.c | 19 |
| src/oscore/oscore_context.c | 27 |
| src/oscore/oscore.c | 8 |
| src/oscore/oscore_cbor.c | 11 |
| ./include/coap3/coap_block_internal.h | 6 |
| src/oscore/oscore_crypto.c | 4 |
| /usr/include/openssl/ssl.h | 3 |
| src/coap_dtls.c | 5 |
| /usr/include/openssl/x509v3.h | 3 |
| ./include/coap3/coap_pdu_internal.h | 1 |
| ./include/coap3/coap_resource_internal.h | 1 |
| src/coap_async.c | 4 |
| src/coap_subscribe.c | 3 |
| src/coap_event.c | 1 |
Analyses and suggestions
Optimal target analysis
Remaining optimal interesting functions
The following table shows a list of functions that are optimal targets. Optimal targets are identified by finding the functions that in combination, yield a high code coverage.
| Func name | Functions filename | Arg count | Args | Function depth | hitcount | instr count | bb count | cyclomatic complexity | Reachable functions | Incoming references | total cyclomatic complexity | Unreached complexity |
|---|---|---|---|---|---|---|---|---|---|---|---|---|
hnd_get_wellknown_lkd
|
/src/libcoap/src/coap_net.c | 5 | ['N/A', 'N/A', 'N/A', 'N/A', 'N/A'] | 116 | 0 | 304 | 50 | 16 | 696 | 0 | 7254 | 121 |
coap_netif_dgrm_write
|
/src/libcoap/src/coap_netif.c | 3 | ['N/A', 'N/A', 'size_t'] | 8 | 0 | 179 | 33 | 10 | 67 | 0 | 336 | 72 |
coap_tls_engine_configure
|
/src/libcoap/src/coap_openssl.c | 1 | ['N/A'] | 6 | 0 | 575 | 124 | 34 | 32 | 0 | 121 | 52 |
coap_endpoint_join_mcast_group_intf
|
/src/libcoap/src/coap_net.c | 3 | ['N/A', 'N/A', 'N/A'] | 6 | 0 | 52 | 9 | 4 | 37 | 0 | 133 | 42 |
coap_op_resource_deleted
|
/src/libcoap/src/coap_subscribe.c | 3 | ['N/A', 'N/A', 'N/A'] | 6 | 0 | 252 | 40 | 16 | 37 | 0 | 129 | 40 |
coap_session_set_type_server
|
/src/libcoap/src/coap_session.c | 1 | ['N/A'] | 113 | 0 | 18 | 3 | 2 | 692 | 0 | 7169 | 36 |
Implementing fuzzers that target the above functions will improve reachability such that it becomes:
All functions overview
If you implement fuzzers for these functions, the status of all functions in the project will be:
| Func name | Functions filename | Args | Function call depth | Reached by Fuzzers | Runtime reached by Fuzzers | Combined reached by Fuzzers | Fuzzers runtime hit | Func lines hit % | I Count | BB Count | Cyclomatic complexity | Functions reached | Reached by functions | Accumulated cyclomatic complexity | Undiscovered complexity |
|---|
Fuzz engine guidance
This sections provides heuristics that can be used as input to a fuzz engine when running a given fuzz target. The current focus is on providing input that is usable by libFuzzer.
tests/oss-fuzz/dtls_define_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_dtls_define_issue']tests/oss-fuzz/get_asn1_tag_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_new_string']tests/oss-fuzz/split_uri_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_dtls_is_supported', 'coap_tls_is_supported', 'coap_wss_is_supported', 'coap_split_uri_sub', 'coap_ws_is_supported', 'coap_log_impl']tests/oss-fuzz/oscore_cbor_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_cleanup', 'coap_dtls_startup', 'LLVMFuzzerTestOneInput']tests/oss-fuzz/oscore_conf_parse_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_new_string', 'coap_delete_bin_const', 'coap_parse_oscore_rcp_conf_mem', 'coap_cleanup', 'coap_dtls_startup', 'LLVMFuzzerTestOneInput', 'coap_parse_oscore_conf_mem']tests/oss-fuzz/pdu_parse_udp_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_show_pdu', 'coap_pdu_encode_header', 'coap_pdu_parse2', 'coap_pdu_parse_header', 'coap_pdu_parse_opt', 'coap_dtls_is_supported', 'coap_tls_is_supported', 'coap_wss_is_supported', 'coap_get_uri_path']tests/oss-fuzz/observe_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_make_str_const', 'coap_dispatch', 'coap_send_internal', 'coap_session_free', 'coap_handle_dgram', 'coap_find_lg_xmit_response', 'handle_request', 'coap_socket_connect_udp', 'coap_show_pdu']tests/oss-fuzz/cache_key_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_pdu_parse_opt', 'coap_socket_connect_udp', 'coap_session_check_connect', 'coap_delete_str_const', 'coap_session_free', 'coap_check_dots', 'coap_digest_free', 'coap_cache_derive_key_w_ignore', 'coap_session_connected', 'coap_option_next']tests/oss-fuzz/oscore_decrypt_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_oscore_decrypt_pdu', 'oscore_context_release_recipients', 'coap_delete_str_const', 'coap_session_free', 'coap_send_internal', 'coap_show_pdu', 'coap_socket_connect_udp', 'coap_session_connected', 'coap_option_filter_get']tests/oss-fuzz/block_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_make_str_const', 'coap_dispatch', 'coap_send_internal', 'coap_session_free', 'coap_handle_dgram', 'coap_socket_connect_udp', 'coap_show_pdu', 'coap_add_data_large_internal', 'coap_handle_request_send_block']tests/oss-fuzz/network_message_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['setup_pki_ssl', 'coap_dispatch', 'coap_send_internal', 'handle_request', 'coap_session_free', 'coap_session_check_connect', 'coap_socket_connect_udp', 'coap_show_pdu']tests/oss-fuzz/pdu_parse_ws_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_show_pdu', 'coap_pdu_parse2', 'coap_pdu_encode_header', 'LLVMFuzzerTestOneInput', 'coap_pdu_parse_opt', 'coap_dtls_is_supported', 'coap_tls_is_supported', 'coap_wss_is_supported']tests/oss-fuzz/uri_extended_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_uri_into_optlist_abbrev', 'coap_split_uri_sub', 'coap_opt_parse', 'LLVMFuzzerTestOneInput', 'coap_new_optlist', 'coap_dtls_is_supported', 'coap_tls_is_supported', 'coap_wss_is_supported', 'coap_opt_setheader']tests/oss-fuzz/persist_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_pdu_parse_opt', 'coap_make_str_const', 'coap_send_internal', 'coap_session_free', 'coap_find_lg_xmit_response', 'coap_get_resource_from_uri_path_lkd', 'coap_socket_connect_udp', 'coap_pdu_release_lkd', 'coap_touch_observer', 'coap_show_pdu']tests/oss-fuzz/proxy_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_session_free', 'coap_free_resource', 'coap_proxy_get_ongoing_session', 'coap_send_lkd', 'coap_send_internal', 'coap_proxy_forward_request_lkd', 'coap_show_pdu', 'coap_session_check_connect', 'coap_dtls_new_context', 'coap_dtls_free_context']tests/oss-fuzz/pdu_parse_tcp_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_show_pdu', 'coap_pdu_parse2', 'LLVMFuzzerTestOneInput', 'coap_pdu_parse_opt', 'coap_dtls_is_supported', 'coap_tls_is_supported', 'coap_wss_is_supported', 'coap_pdu_encode_header']tests/oss-fuzz/async_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_make_str_const', 'coap_dispatch', 'coap_send_internal', 'coap_session_free', 'handle_request', 'coap_handle_dgram', 'coap_find_lg_xmit_response', 'coap_socket_connect_udp', 'coap_show_pdu']tests/oss-fuzz/block_check_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_io_do_epoll_lkd', 'coap_make_str_const', 'coap_add_data_after', 'coap_get_resource_from_uri_path_lkd', 'coap_socket_connect_udp', 'coap_show_pdu', 'coap_add_block_b_data', 'coap_add_block', 'coap_block_delete_lg_xmit', 'coap_dtls_new_context']tests/oss-fuzz/ws_frame_target.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['coap_session_free', 'coap_session_check_connect', 'coap_socket_connect_udp', 'coap_delete_str_const', 'coap_session_disconnected_lkd', 'coap_handle_event_lkd', 'coap_session_connected', 'coap_dtls_new_context', 'coap_dtls_free_context']Runtime coverage analysis
This section shows analysis of runtime coverage data.
For futher technical details on how this section is generated, please see the Glossary .
Complex functions with low coverage
| Func name | Function total lines | Lines covered at runtime | percentage covered | Reached by fuzzers |
|---|---|---|---|---|
| coap_show_pdu | 327 | 20 | 6.116% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_tcp_fuzzer', 'block_fuzzer', 'pdu_parse_ws_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_debug_send_packet | 42 | 23 | 54.76% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_debug_set_packet_common | 41 | 15 | 36.58% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_socket_connect_udp | 165 | 74 | 44.84% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_socket_send | 118 | 39 | 33.05% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_test_cid_tuple_change | 31 | 4 | 12.90% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_new_context | 69 | 37 | 53.62% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_send_internal | 164 | 77 | 46.95% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_cancel_session_messages | 32 | 5 | 15.62% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_dispatch | 399 | 179 | 44.86% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_handle_event_lkd | 71 | 25 | 35.21% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_is_session_proxy | 58 | 10 | 17.24% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_remove_from_queue_token | 45 | 4 | 8.888% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_pdu_duplicate_lkd | 74 | 30 | 40.54% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_remove_option | 78 | 13 | 16.66% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_add_resource_lkd | 38 | 20 | 52.63% | ['proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'block_check_fuzzer'] |
| coap_add_observer | 145 | 63 | 43.44% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_delete_observer_internal | 40 | 18 | 45.0% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_session_connected | 58 | 11 | 18.96% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_oscore_decrypt_pdu | 685 | 165 | 24.08% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| oscore_validate_sender_seq | 51 | 18 | 35.29% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| oscore_cbor_put_unsigned | 42 | 9 | 21.42% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| oscore_find_context | 106 | 30 | 28.30% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| oscore_log_context | 39 | 4 | 10.25% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_handle_request_send_block | 268 | 34 | 12.68% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_handle_request_put_block | 473 | 169 | 35.72% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| setup_block_b | 35 | 18 | 51.42% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_remove_from_queue | 38 | 6 | 15.78% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_delete_proxy_subscriber | 39 | 5 | 12.82% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_print_wellknown_lkd | 143 | 78 | 54.54% | ['block_fuzzer'] |
| coap_print_addr | 40 | 15 | 37.5% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_print_ip_addr | 49 | 15 | 30.61% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'uri_extended_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_call_response_handler | 43 | 17 | 39.53% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| prepend_508_ip | 90 | 35 | 38.88% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| handle_signaling | 79 | 33 | 41.77% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| handle_response | 74 | 17 | 22.97% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_dtls_info_callback | 66 | 26 | 39.39% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_dgram_ctrl | 61 | 31 | 50.81% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| setup_pki_ssl | 291 | 13 | 4.467% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_session_delay_pdu | 38 | 17 | 44.73% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_socket_connect_tcp1 | 102 | 36 | 35.29% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_socket_write | 39 | 20 | 51.28% | ['network_message_fuzzer'] |
| coap_socket_bind_udp | 75 | 29 | 38.66% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_new_endpoint_lkd | 97 | 34 | 35.05% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_persist_observe_add_lkd | 202 | 30 | 14.85% | ['persist_fuzzer'] |
| get_coap_addr_info | 55 | 16 | 29.09% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| update_coap_addr_port | 39 | 8 | 20.51% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_send_lkd | 290 | 32 | 11.03% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_proxy_log_entry | 32 | 3 | 9.375% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_proxy_del_req | 34 | 10 | 29.41% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_verify_proxy_scheme_supported | 45 | 11 | 24.44% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_proxy_remove_association | 40 | 14 | 35.0% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_proxy_forward_request_lkd | 243 | 108 | 44.44% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_proxy_get_ongoing_session | 162 | 67 | 41.35% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_resource_proxy_uri_init2 | 37 | 16 | 43.24% | ['proxy_fuzzer'] |
| coap_add_data_blocked_response | 101 | 51 | 50.49% | ['block_check_fuzzer'] |
| coap_cancel_observe_lkd | 72 | 13 | 18.05% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_block_check_lg_xmit_timeouts | 41 | 22 | 53.65% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_block_check_lg_crcv_timeouts | 57 | 19 | 33.33% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_block_check_lg_srcv_timeouts | 75 | 19 | 25.33% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_block_check_q_block1_xmit | 54 | 12 | 22.22% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_block_check_q_block2_xmit | 52 | 14 | 26.92% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_io_prepare_io_lkd | 336 | 74 | 22.02% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_client_delay_first | 47 | 5 | 10.63% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_io_do_epoll_lkd | 69 | 10 | 14.49% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_proxy_check_timeouts | 44 | 7 | 15.90% | ['network_message_fuzzer', 'proxy_fuzzer', 'observe_fuzzer', 'async_fuzzer', 'cache_key_fuzzer', 'persist_fuzzer', 'block_fuzzer', 'ws_frame_fuzzer', 'block_check_fuzzer', 'oscore_decrypt_fuzzer'] |
| coap_ws_rd_http_header_client | 64 | 7 | 10.93% | ['ws_frame_fuzzer'] |
Files and Directories in report
This section shows which files and directories are considered in this report. The main reason for showing this is fuzz introspector may include more code in the reasoning than is desired. This section helps identify if too many files/directories are included, e.g. third party code, which may be irrelevant for the threat model. In the event too much is included, fuzz introspector supports a configuration file that can exclude data from the report. See the following link for more information on how to create a config file: link
Files in report
| Source file | Reached by | Covered by |
|---|---|---|
| [] | [] | |
| /src/libcoap/src/coap_uri.c | ['split_uri_fuzzer', 'oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['split_uri_fuzzer', 'oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/./include/coap3/coap_address.h | [] | [] |
| /src/libcoap/src/coap_mem.c | ['get_asn1_tag_fuzzer', 'oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['get_asn1_tag_fuzzer', 'oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/coap_netif.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/coap_ws.c | ['split_uri_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['split_uri_fuzzer', 'pdu_parse_udp_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_tcp_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/./include/coap3/coap_pdu_internal.h | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | [] |
| /src/libcoap/src/coap_subscribe.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/async_target.c | ['async_fuzzer'] | ['async_fuzzer'] |
| /src/libcoap/src/coap_net.c | ['oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/coap_pdu.c | ['pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /usr/include/openssl/x509v3.h | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | [] |
| /src/libcoap/tests/oss-fuzz/network_message_target.c | ['network_message_fuzzer'] | ['network_message_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/proxy_target.c | ['proxy_fuzzer'] | ['proxy_fuzzer'] |
| /src/libcoap/src/coap_session.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/oscore_conf_parse_target.c | ['oscore_conf_parse_fuzzer'] | ['oscore_conf_parse_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/observe_target.c | ['observe_fuzzer'] | ['observe_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/pdu_parse_tcp_target.c | ['pdu_parse_tcp_fuzzer'] | ['pdu_parse_tcp_fuzzer'] |
| /src/libcoap/src/coap_io_posix.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/oscore/oscore_cbor.c | ['oscore_cbor_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['oscore_cbor_fuzzer', 'oscore_decrypt_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/coap_fuzz_helper.c | ['observe_fuzzer', 'block_fuzzer', 'async_fuzzer'] | ['observe_fuzzer', 'block_fuzzer', 'async_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/persist_target.c | ['persist_fuzzer'] | ['persist_fuzzer'] |
| /src/libcoap/src/oscore/oscore_crypto.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['oscore_decrypt_fuzzer'] |
| /src/libcoap/./include/coap3/coap_block_internal.h | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | [] |
| /src/libcoap/tests/oss-fuzz/block_target.c | ['block_fuzzer'] | ['block_fuzzer'] |
| /src/libcoap/src/coap_dtls.c | ['dtls_define_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['dtls_define_fuzzer', 'network_message_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/cache_key_target.c | ['cache_key_fuzzer'] | ['cache_key_fuzzer'] |
| /src/libcoap/src/coap_strm_posix.c | ['split_uri_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['split_uri_fuzzer', 'pdu_parse_udp_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'pdu_parse_tcp_fuzzer'] |
| /src/libcoap/src/coap_str.c | ['get_asn1_tag_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['get_asn1_tag_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/coap_proxy.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/block_check_target.c | ['block_check_fuzzer'] | ['block_check_fuzzer'] |
| /src/libcoap/src/coap_debug.c | ['dtls_define_fuzzer', 'get_asn1_tag_fuzzer', 'split_uri_fuzzer', 'oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['dtls_define_fuzzer', 'split_uri_fuzzer', 'oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/coap_prng.c | ['oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/coap_event.c | ['observe_fuzzer', 'block_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'block_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/coap_oscore.c | ['oscore_conf_parse_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['oscore_conf_parse_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/./include/coap3/coap_resource_internal.h | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | [] |
| /src/libcoap/src/coap_async.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/coap_address.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/dtls_define_target.c | ['dtls_define_fuzzer'] | ['dtls_define_fuzzer'] |
| /src/libcoap/src/coap_dgrm_posix.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/coap_openssl.c | ['split_uri_fuzzer', 'oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['split_uri_fuzzer', 'oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/coap_block.c | ['pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'async_fuzzer', 'block_check_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/uri_extended_target.c | ['uri_extended_fuzzer'] | ['uri_extended_fuzzer'] |
| /src/libcoap/src/oscore/oscore.c | ['oscore_conf_parse_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['oscore_conf_parse_fuzzer', 'oscore_decrypt_fuzzer'] |
| /src/libcoap/./include/coap3/coap_uri.h | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | [] |
| /src/libcoap/tests/oss-fuzz/get_asn1_tag_target.c | ['get_asn1_tag_fuzzer'] | ['get_asn1_tag_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/pdu_parse_ws_target.c | ['pdu_parse_ws_fuzzer'] | ['pdu_parse_ws_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/oscore_cbor_target.c | ['oscore_cbor_fuzzer'] | ['oscore_cbor_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/oscore_decrypt_target.c | ['oscore_decrypt_fuzzer'] | ['oscore_decrypt_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/split_uri_target.c | ['split_uri_fuzzer'] | ['split_uri_fuzzer'] |
| /src/libcoap/src/oscore/oscore_context.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/coap_time.c | ['dtls_define_fuzzer', 'get_asn1_tag_fuzzer', 'split_uri_fuzzer', 'oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['split_uri_fuzzer', 'oscore_cbor_fuzzer', 'oscore_conf_parse_fuzzer', 'pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/src/oscore/oscore_cose.c | ['oscore_conf_parse_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['oscore_conf_parse_fuzzer', 'oscore_decrypt_fuzzer'] |
| /src/libcoap/src/coap_asn1.c | ['get_asn1_tag_fuzzer'] | ['get_asn1_tag_fuzzer'] |
| /src/libcoap/src/coap_cache.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'cache_key_fuzzer', 'block_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'block_check_fuzzer'] |
| /src/libcoap/src/coap_resource.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/pdu_parse_udp_target.c | ['pdu_parse_udp_fuzzer'] | ['pdu_parse_udp_fuzzer'] |
| /src/libcoap/tests/oss-fuzz/ws_frame_target.c | ['ws_frame_fuzzer'] | ['ws_frame_fuzzer'] |
| /usr/include/openssl/ssl.h | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | [] |
| /src/libcoap/src/coap_option.c | ['pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer'] |
| /src/libcoap/src/coap_encode.c | ['pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['pdu_parse_udp_fuzzer', 'observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'pdu_parse_ws_fuzzer', 'uri_extended_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'pdu_parse_tcp_fuzzer', 'async_fuzzer', 'block_check_fuzzer'] |
| /src/libcoap/src/coap_io.c | ['observe_fuzzer', 'cache_key_fuzzer', 'oscore_decrypt_fuzzer', 'block_fuzzer', 'network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer', 'ws_frame_fuzzer'] | ['network_message_fuzzer', 'persist_fuzzer', 'proxy_fuzzer', 'async_fuzzer', 'block_check_fuzzer'] |
Directories in report
| Directory |
|---|
| /src/libcoap/src/ |
| /src/libcoap/src/oscore/ |
| /usr/include/openssl/ |
| /src/libcoap/tests/oss-fuzz/ |
| /src/libcoap/./include/coap3/ |
Metadata section
This sections shows the raw data that is used to produce this report. This is mainly used for further processing and developer debugging.