Project overview: nanopb
High level conclusions
Reachability and coverage overview
Warning:
The number of runtime covered functions are larger than the
number of reachable functions. This means that Fuzz Introspector found
there are more functions covered at runtime than what is considered
reachable based on the static analysis. This is a limitation in the
analysis as anything covered at runtime is by definition reachable by the
fuzzers.
This is likely due to a limitation in the static analysis. In this case, the
count of functions covered at runtime is the true value, which means this
is what should be considered "achieved" by the fuzzer.
Use the project functions table below to query all functions that were not covered at runtime.
Project functions overview
The following table shows data about each function in the project. The functions included in this table correspond to all functions that exist in the executables of the fuzzers. As such, there may be functions that are from third-party libraries.
For further technical details on the meaning of columns in the below table, please see the Glossary .
| Func name | Functions filename | Args | Function call depth | Reached by Fuzzers | Runtime reached by Fuzzers | Combined reached by Fuzzers | Fuzzers runtime hit | Func lines hit % | I Count | BB Count | Cyclomatic complexity | Functions reached | Reached by functions | Accumulated cyclomatic complexity | Undiscovered complexity |
|---|
Fuzzer details
Fuzzer: fuzztest_proto3_static
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 68 | 25.9% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 1 | 0.38% |
| lawngreen | 50+ | 193 | 73.6% |
| All colors | 262 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 14 | 127 | validate_static | call site: 00127 | validate_pointer |
| 7 | 64 | pb_field_iter_find_extension | call site: 00064 | decode_extension |
| 7 | 106 | decode_static_field | call site: 00106 | pb_message_set_to_defaults |
| 6 | 165 | pb_encode | call site: 00165 | encode_extension_field |
| 5 | 21 | pb_message_set_to_defaults | call site: 00021 | pb_message_set_to_defaults |
| 5 | 81 | pb_close_string_substream | call site: 00081 | read_raw_value |
| 2 | 14 | pb_decode_inner | call site: 00014 | pb_decode_tag |
| 2 | 78 | pb_skip_field | call site: 00078 | pb_make_string_substream |
| 2 | 103 | decode_static_field | call site: 00103 | pb_message_set_to_defaults |
| 2 | 142 | validate_message | call site: 00142 | fprintf |
| 2 | 199 | pb_encode_tag_for_field | call site: 00199 | encode_basic_field |
| 2 | 227 | do_roundtrip | call site: 00227 | fprintf |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/build/fuzztest/fuzztest.c | 6 |
| tests/build/common/malloc_wrappers.c | 5 |
| pb_decode.c | 37 |
| pb_common.c | 10 |
| tests/build/fuzztest/validation.c | 3 |
| pb_encode.c | 27 |
| tests/build/fuzztest/flakystream.c | 1 |
Fuzzer: fuzztest_proto2_static
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 40 | 14.5% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 234 | 85.4% |
| All colors | 274 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 14 | 127 | validate_static | call site: 00127 | validate_pointer |
| 5 | 172 | encode_field | call site: 00172 | pb_check_proto3_default_value |
| 3 | 110 | pb_field_set_to_default | call site: 00110 | pb_decode_inner |
| 2 | 106 | decode_static_field | call site: 00106 | pb_message_set_to_defaults |
| 2 | 142 | validate_message | call site: 00142 | fprintf |
| 2 | 199 | pb_encode_tag_for_field | call site: 00199 | encode_basic_field |
| 2 | 227 | do_roundtrip | call site: 00227 | fprintf |
| 2 | 271 | do_callback_decode | call site: 00271 | get_alloc_count |
| 1 | 22 | pb_field_set_to_default | call site: 00022 | pb_field_iter_begin |
| 1 | 31 | pb_decode_bool | call site: 00031 | pb_decode_varint32_eof |
| 1 | 68 | default_extension_decoder | call site: 00068 | decode_pointer_field |
| 1 | 70 | decode_field | call site: 00070 | pb_skip_field |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/build/fuzztest/fuzztest.c | 7 |
| tests/build/common/malloc_wrappers.c | 5 |
| pb_decode.c | 37 |
| pb_common.c | 10 |
| tests/build/fuzztest/validation.c | 3 |
| pb_encode.c | 27 |
| tests/build/fuzztest/flakystream.c | 1 |
Fuzzer: fuzztest_io_errors
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:
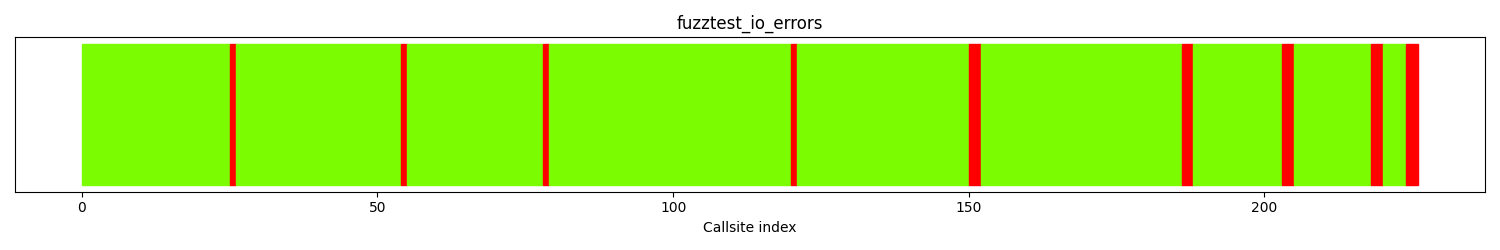
The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 14 | 6.19% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 212 | 93.8% |
| All colors | 226 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 2 | 149 | decode_static_field | call site: 00149 | pb_message_set_to_defaults |
| 2 | 185 | validate_message | call site: 00185 | fprintf |
| 2 | 202 | do_decode | call site: 00202 | fprintf |
| 2 | 217 | pb_decode | call site: 00217 | fprintf |
| 2 | 223 | do_callback_decode | call site: 00223 | get_alloc_count |
| 1 | 24 | pb_field_set_to_default | call site: 00024 | pb_field_iter_begin |
| 1 | 53 | pb_decode_bool | call site: 00053 | pb_decode_varint32_eof |
| 1 | 77 | realloc_with_check | call site: 00077 | free_with_check |
| 1 | 119 | decode_field | call site: 00119 | pb_skip_field |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/build/fuzztest/fuzztest.c | 5 |
| tests/build/common/malloc_wrappers.c | 9 |
| tests/build/fuzztest/flakystream.c | 1 |
| pb_decode.c | 41 |
| pb_common.c | 9 |
| tests/build/fuzztest/validation.c | 3 |
Fuzzer: fuzztest_proto3_pointer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 77 | 25.6% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 0 | 0.0% |
| lawngreen | 50+ | 223 | 74.3% |
| All colors | 300 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 13 | 204 | pb_encode | call site: 00204 | encode_extension_field |
| 8 | 161 | validate_message | call site: 00161 | __assert_fail |
| 7 | 126 | pb_skip_field | call site: 00126 | pb_make_string_substream |
| 7 | 136 | pb_dec_submessage | call site: 00136 | decode_basic_field |
| 7 | 148 | decode_static_field | call site: 00148 | pb_message_set_to_defaults |
| 5 | 21 | pb_message_set_to_defaults | call site: 00021 | pb_message_set_to_defaults |
| 4 | 93 | pb_field_iter_find_extension | call site: 00093 | decode_extension |
| 3 | 144 | pb_message_set_to_defaults | call site: 00144 | decode_basic_field |
| 2 | 14 | pb_decode_inner | call site: 00014 | pb_decode_tag |
| 2 | 32 | pb_release_union_field | call site: 00032 | pb_release_single_field |
| 2 | 112 | pb_close_string_substream | call site: 00112 | allocate_field |
| 2 | 117 | decode_pointer_field | call site: 00117 | decode_callback_field |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/build/fuzztest/fuzztest.c | 6 |
| tests/build/common/malloc_wrappers.c | 6 |
| pb_decode.c | 41 |
| pb_common.c | 10 |
| tests/build/fuzztest/validation.c | 3 |
| pb_encode.c | 27 |
| tests/build/fuzztest/flakystream.c | 1 |
Fuzzer: fuzztest_proto2_pointer
Call tree
The calltree shows the control flow of the fuzzer. This is overlaid with coverage information to display how much of the potential code a fuzzer can reach is in fact covered at runtime. In the following there is a link to a detailed calltree visualisation as well as a bitmap showing a high-level view of the calltree. For further information about these topics please see the glossary for full calltree and calltree overview
Call tree overview bitmap:

The distribution of callsites in terms of coloring is
| Color | Runtime hitcount | Callsite count | Percentage |
|---|---|---|---|
| red | 0 | 47 | 15.6% |
| gold | [1:9] | 0 | 0.0% |
| yellow | [10:29] | 0 | 0.0% |
| greenyellow | [30:49] | 1 | 0.33% |
| lawngreen | 50+ | 252 | 84.0% |
| All colors | 300 | 100 |
Fuzz blockers
The following nodes represent call sites where fuzz blockers occur.
| Amount of callsites blocked | Calltree index | Parent function | Callsite | Largest blocked function |
|---|---|---|---|---|
| 8 | 161 | validate_message | call site: 00161 | __assert_fail |
| 7 | 148 | decode_static_field | call site: 00148 | pb_message_set_to_defaults |
| 6 | 137 | decode_static_field | call site: 00137 | decode_basic_field |
| 5 | 211 | encode_field | call site: 00211 | pb_check_proto3_default_value |
| 3 | 144 | pb_message_set_to_defaults | call site: 00144 | decode_basic_field |
| 2 | 14 | pb_decode_inner | call site: 00014 | pb_decode_tag |
| 2 | 184 | validate_message | call site: 00184 | fprintf |
| 2 | 266 | do_roundtrip | call site: 00266 | fprintf |
| 2 | 297 | do_stream_decode | call site: 00297 | get_alloc_count |
| 1 | 22 | pb_field_set_to_default | call site: 00022 | pb_field_iter_begin |
| 1 | 25 | pb_field_set_to_default | call site: 00025 | decode_field |
| 1 | 51 | pb_decode_bool | call site: 00051 | pb_decode_varint32_eof |
Runtime coverage analysis
| Function name | source code lines | source lines hit | percentage hit |
|---|
Files reached
| filename | functions hit |
|---|---|
| tests/build/fuzztest/fuzztest.c | 6 |
| tests/build/common/malloc_wrappers.c | 6 |
| pb_decode.c | 41 |
| pb_common.c | 10 |
| tests/build/fuzztest/validation.c | 3 |
| pb_encode.c | 27 |
| tests/build/fuzztest/flakystream.c | 1 |
Analyses and suggestions
Optimal target analysis
Remaining optimal interesting functions
The following table shows a list of functions that are optimal targets. Optimal targets are identified by finding the functions that in combination, yield a high code coverage.
| Func name | Functions filename | Arg count | Args | Function depth | hitcount | instr count | bb count | cyclomatic complexity | Reachable functions | Incoming references | total cyclomatic complexity | Unreached complexity |
|---|
Implementing fuzzers that target the above functions will improve reachability such that it becomes:
All functions overview
If you implement fuzzers for these functions, the status of all functions in the project will be:
| Func name | Functions filename | Args | Function call depth | Reached by Fuzzers | Runtime reached by Fuzzers | Combined reached by Fuzzers | Fuzzers runtime hit | Func lines hit % | I Count | BB Count | Cyclomatic complexity | Functions reached | Reached by functions | Accumulated cyclomatic complexity | Undiscovered complexity |
|---|
Fuzz engine guidance
This sections provides heuristics that can be used as input to a fuzz engine when running a given fuzz target. The current focus is on providing input that is usable by libFuzzer.
tests/build/fuzztest/fuzztest.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['validate_static', 'pb_field_iter_find_extension', 'decode_static_field', 'pb_encode', 'pb_message_set_to_defaults', 'pb_close_string_substream', 'pb_decode_inner', 'pb_skip_field', 'validate_message']tests/build/fuzztest/fuzztest.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['validate_static', 'encode_field', 'pb_field_set_to_default', 'decode_static_field', 'validate_message', 'pb_encode_tag_for_field', 'do_roundtrip', 'do_callback_decode', 'pb_decode_bool']tests/build/fuzztest/fuzztest.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['decode_static_field', 'validate_message', 'do_decode', 'pb_decode', 'do_callback_decode', 'pb_field_set_to_default', 'pb_decode_bool', 'realloc_with_check', 'decode_field']tests/build/fuzztest/fuzztest.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['pb_encode', 'validate_message', 'pb_skip_field', 'pb_dec_submessage', 'decode_static_field', 'pb_message_set_to_defaults', 'pb_field_iter_find_extension', 'pb_decode_inner', 'pb_release_union_field']tests/build/fuzztest/fuzztest.c
Dictionary
Use this with the libFuzzer -dict=DICT.file flag
Fuzzer function priority
Use one of these functions as input to libfuzzer with flag: -focus_function name
-focus_function=['validate_message', 'decode_static_field', 'encode_field', 'pb_message_set_to_defaults', 'pb_decode_inner', 'do_roundtrip', 'do_stream_decode', 'pb_field_set_to_default']Runtime coverage analysis
This section shows analysis of runtime coverage data.
For futher technical details on how this section is generated, please see the Glossary .
Complex functions with low coverage
| Func name | Function total lines | Lines covered at runtime | percentage covered | Reached by fuzzers |
|---|
Files and Directories in report
This section shows which files and directories are considered in this report. The main reason for showing this is fuzz introspector may include more code in the reasoning than is desired. This section helps identify if too many files/directories are included, e.g. third party code, which may be irrelevant for the threat model. In the event too much is included, fuzz introspector supports a configuration file that can exclude data from the report. See the following link for more information on how to create a config file: link
Files in report
| Source file | Reached by | Covered by |
|---|---|---|
| [] | [] | |
| /src/nanopb/tests/build/fuzztest/fuzztest.c | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] |
| /src/nanopb/pb_common.c | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] |
| /src/nanopb/pb_decode.c | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] |
| /src/nanopb/tests/build/fuzztest/validation.c | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] |
| /src/nanopb/tests/build/common/malloc_wrappers.c | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] |
| /src/nanopb/pb_encode.c | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] |
| /src/nanopb/tests/build/fuzztest/flakystream.c | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] | ['fuzztest_proto3_static', 'fuzztest_proto2_static', 'fuzztest_io_errors', 'fuzztest_proto3_pointer', 'fuzztest_proto2_pointer'] |
Directories in report
| Directory |
|---|
| /src/nanopb/ |
| /src/nanopb/tests/build/common/ |
| /src/nanopb/tests/build/fuzztest/ |
Metadata section
This sections shows the raw data that is used to produce this report. This is mainly used for further processing and developer debugging.
| Fuzzer | Calltree file | Program data file | Coverage file |
|---|---|---|---|
| fuzztest_proto3_static | fuzzerLogFile-0-ukGsTnKVON.data | fuzzerLogFile-0-ukGsTnKVON.data.yaml | fuzztest_proto3_static.covreport |
| fuzztest_proto2_static | fuzzerLogFile-0-U4KsL2hX5F.data | fuzzerLogFile-0-U4KsL2hX5F.data.yaml | fuzztest_proto2_static.covreport |
| fuzztest_io_errors | fuzzerLogFile-0-8tAadDj9z0.data | fuzzerLogFile-0-8tAadDj9z0.data.yaml | fuzztest_io_errors.covreport |
| fuzztest_proto3_pointer | fuzzerLogFile-0-SBUR24Ga4F.data | fuzzerLogFile-0-SBUR24Ga4F.data.yaml | fuzztest_proto3_pointer.covreport |
| fuzztest_proto2_pointer | fuzzerLogFile-0-uRCBDbfBRy.data | fuzzerLogFile-0-uRCBDbfBRy.data.yaml | fuzztest_proto2_pointer.covreport |