Checking open ports on a Mac is a fundamental task for diagnosing network issues, troubleshooting application conflicts, and ensuring system security. The Terminal provides a powerful and efficient way to perform this action without relying solely on graphical user interfaces. By leveraging standard command-line utilities, users can gain deep visibility into which processes are listening for network connections. This guide walks through the specific commands and methodologies required to inspect port activity effectively.
Understanding Ports and Network Sockets
Before diving into the commands, it is essential to understand what a "port" represents in networking. Think of an IP address as a specific building, while the port number functions as an apartment number within that building. When a service like a web server or file sharing is active, it binds to a specific port, such as 80 for HTTP or 443 for HTTPS. On macOS, this endpoint is managed through sockets, and the Terminal allows you to query these sockets to see which applications are currently utilizing network resources.
Using the lsof Command
The lsof Approach
The lsof (list open files) command is one of the most versatile tools for this task, as macOS treats network connections as files. To see all network connections and listening ports, you can use the following command in the Terminal. This provides a detailed list that includes the command, process ID, user, and the specific port number being used.
lsof -i -P– Lists all network connections without converting port numbers to service names.lsof -iTCP -sTCP:LISTEN– Filters the results to show only TCP ports that are currently listening for incoming connections.lsof -i :80– Checks specifically if port 80 is open and which process is managing it.
Leveraging the netstat Utility
Analyzing Protocol Statistics
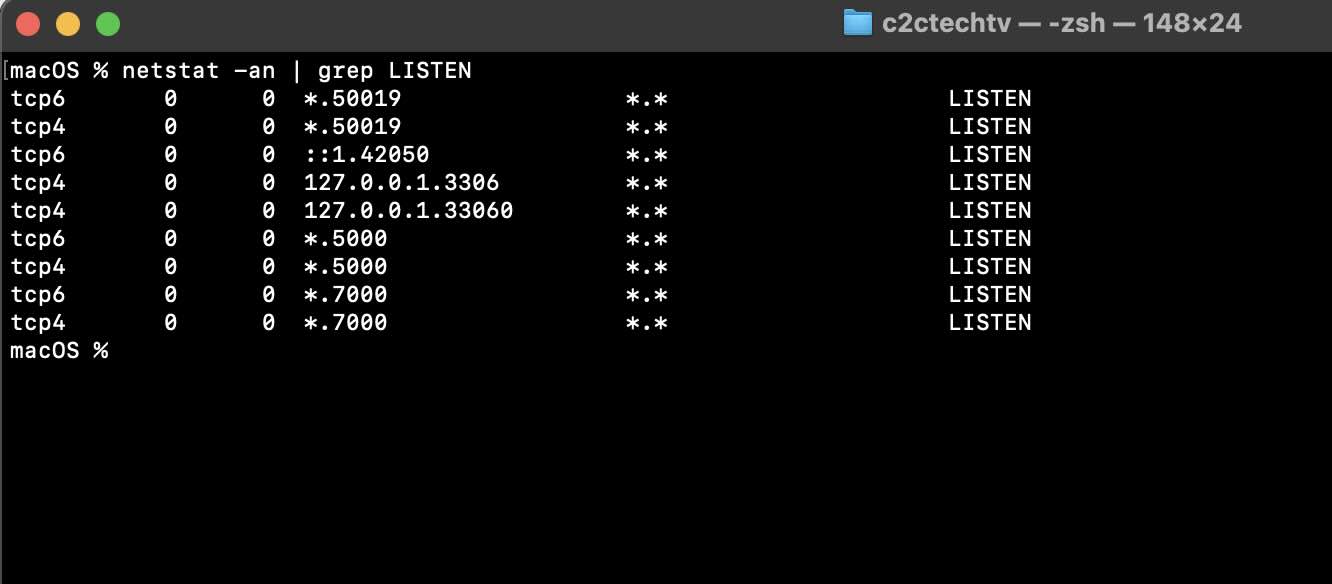
While lsof focuses on files, netstat (network statistics) provides a broader view of routing tables, interface statistics, and open sockets. Although largely superseded by lsof in modern macOS versions, netstat remains a valuable tool for understanding protocol-level activity. Combining specific flags allows you to filter for listening ports associated with the TCP or UDP protocols.
netstat -an -f inet– Displays all network connections and listening ports for IPv4 addresses without resolving hostnames.netstat -rn -f inet– Shows the routing table, which is useful for diagnosing path issues.netstat -sp tcp– Limits the output to TCP protocol statistics specifically.
Filtering Results with grep
Refining Your Search
When you are looking for a specific service, piping the output of lsof or netstat to grep is an essential technique for managing clutter. This allows you to search for a particular port number or protocol string directly within the terminal buffer. This method is particularly useful when you are trying to verify if a specific application, such as a local development server, is running correctly on its designated port.
l -iTCP -sTCP:LISTEN \| grep 8080– Searches for listening processes on port 8080.netstat -an -f inet \| grep ".80"– Finds all connections involving port 80.
Identifying the Process ID (PID)
Knowing which port is open is often not enough; you need to identify the specific process that is using it. Both lsof and netstat display the Process ID (PID), which is the unique identifier for the running application. With this PID, you can manage the process directly. For instance, if a rogue service is occupying a port required by another application, you can terminate it using the kill command followed by the PID number.
Visualizing Activity with whatnetwork
For users who prefer a visual representation over raw text, the whatnetwork script is an excellent third-party tool. While not installed by default, it can be easily added to your system to provide a colorful, real-time dashboard of network activity. This script simplifies the complexity of netstat and lsof by organizing the data into readable columns, making it ideal for quickly spotting unauthorized network access or unexpected listening services.
Securing Your Network Interfaces
After identifying open ports, you might determine that certain services should not be exposed to the network. On macOS, you can manage this through the Sharing System Preferences pane or by adjusting the launchd configuration files that control background daemons. Furthermore, utilizing the built-in firewall allows you to block incoming connections selectively. Regularly checking your ports ensures that only necessary services, such as SSH or a local development server, are actively listening, thereby reducing the attack surface for potential threats.
See a List of All Open Ports using Mac Terminal | Code2care
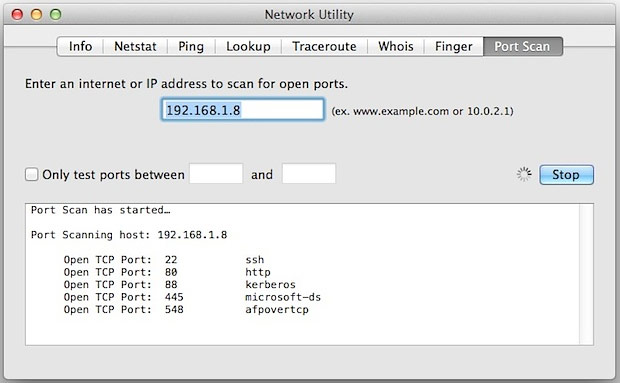
How to Check if a Port is Open to Stream on Mac | Dacast
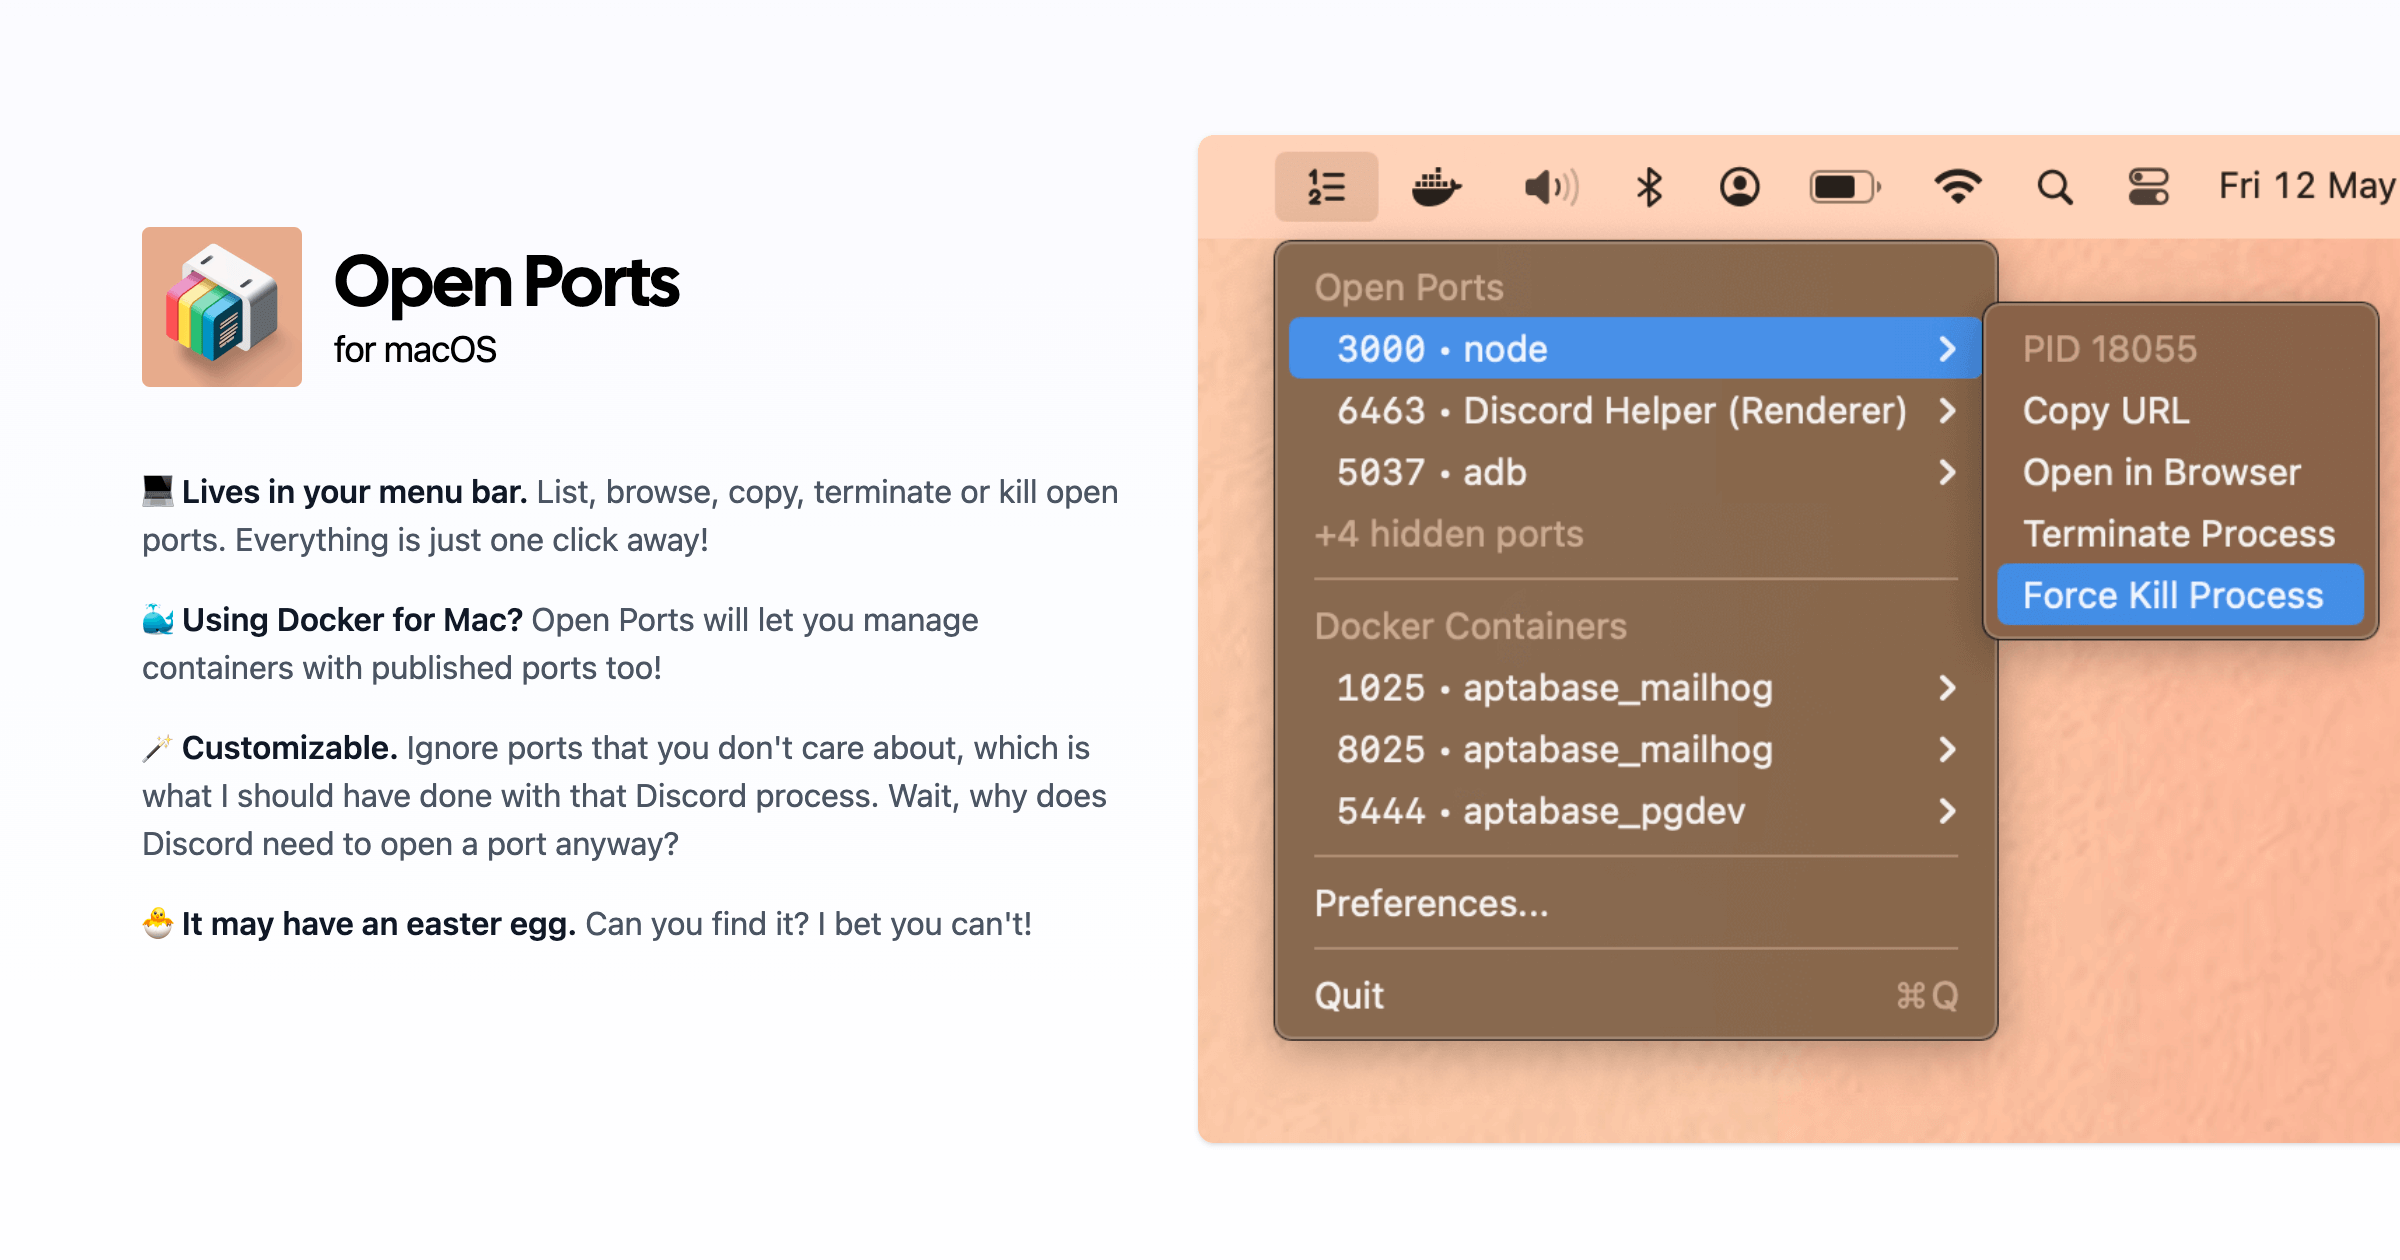
Open Ports for macOS
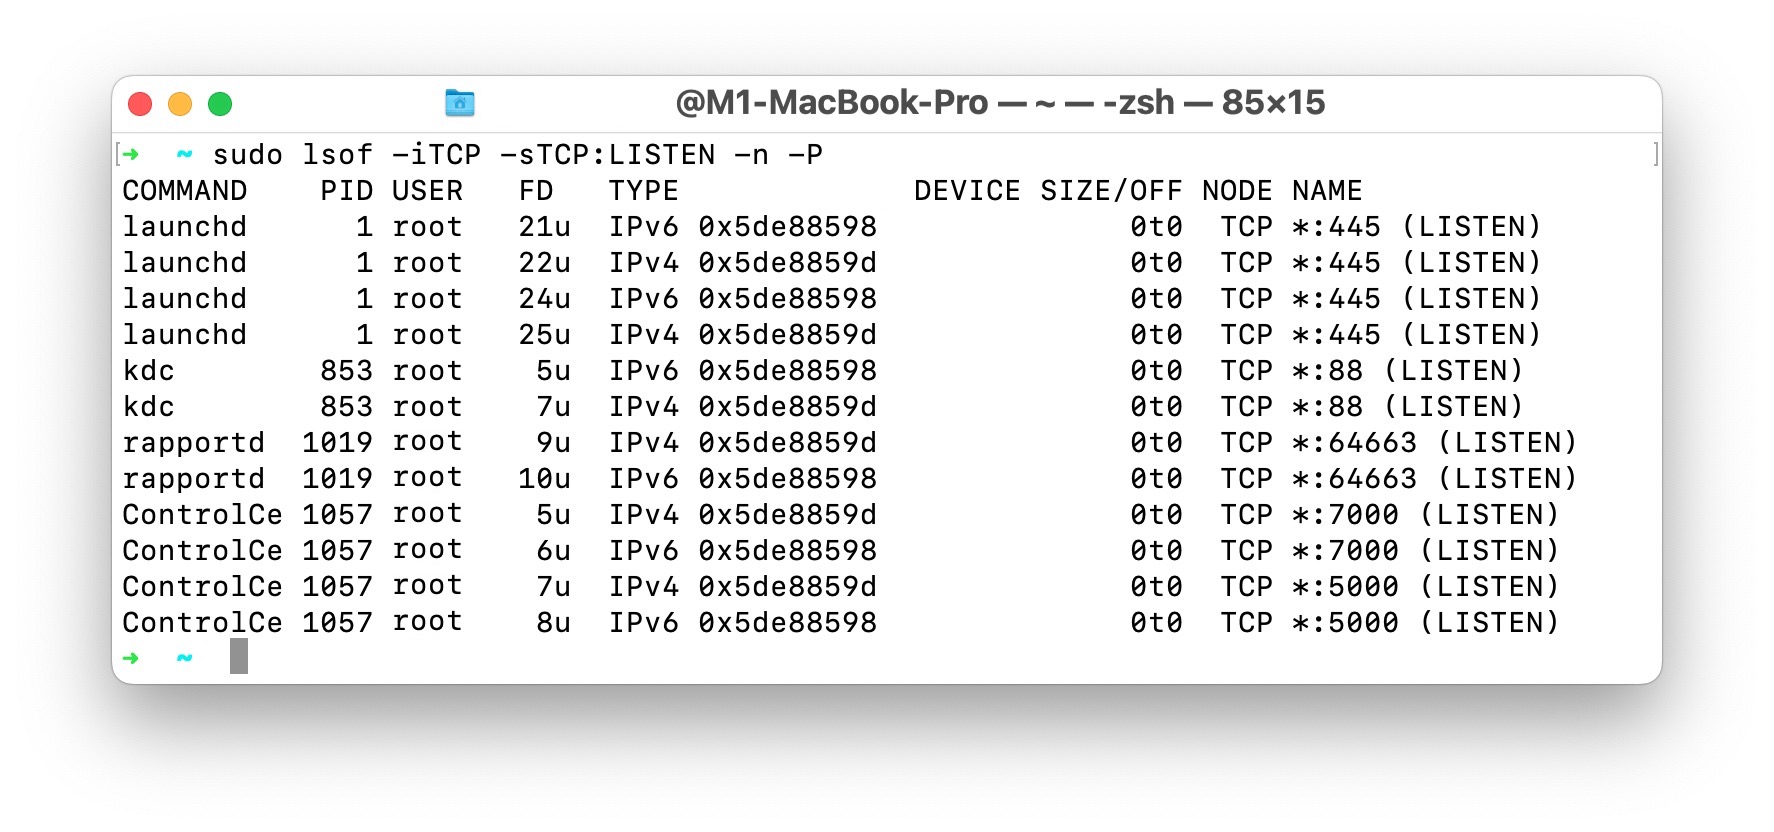
How to Find Who/What is Listening on TCP Ports on Mac

How to check for open ports on Mac-MAC-php.cn
What is MAC Filtering | All You Need to Know About It?
How to Open Terminal on Mac | in 6 Ways - EaseUS
How To Open A Port On Mac – Including Firewall Ports – iTechTalk

Terminal Mac Code at Dorothy Lim blog
How to open Terminal on Mac to do Anything You Want
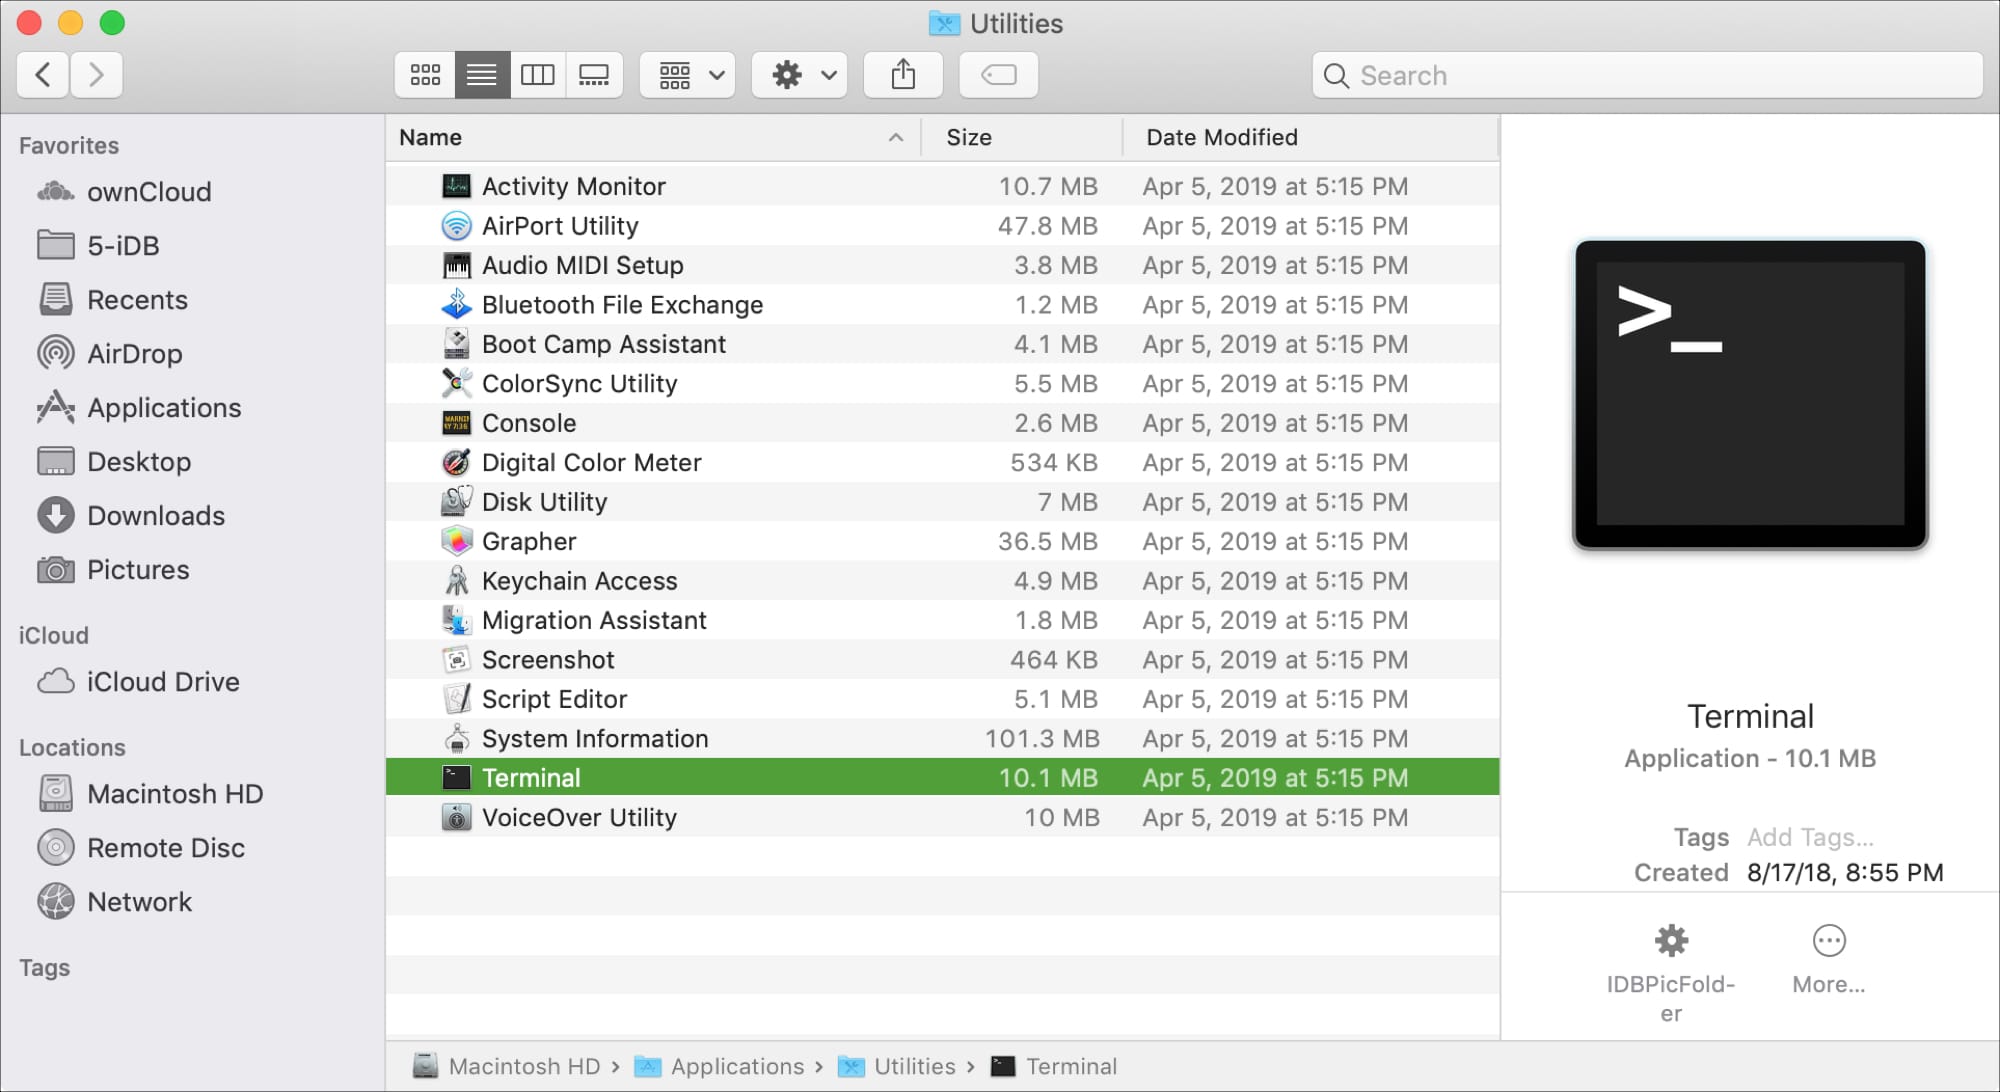
6 simple ways to open Terminal on Mac

Terminal on Mac How to Open? | How to Open Mac Command Line - YouTube
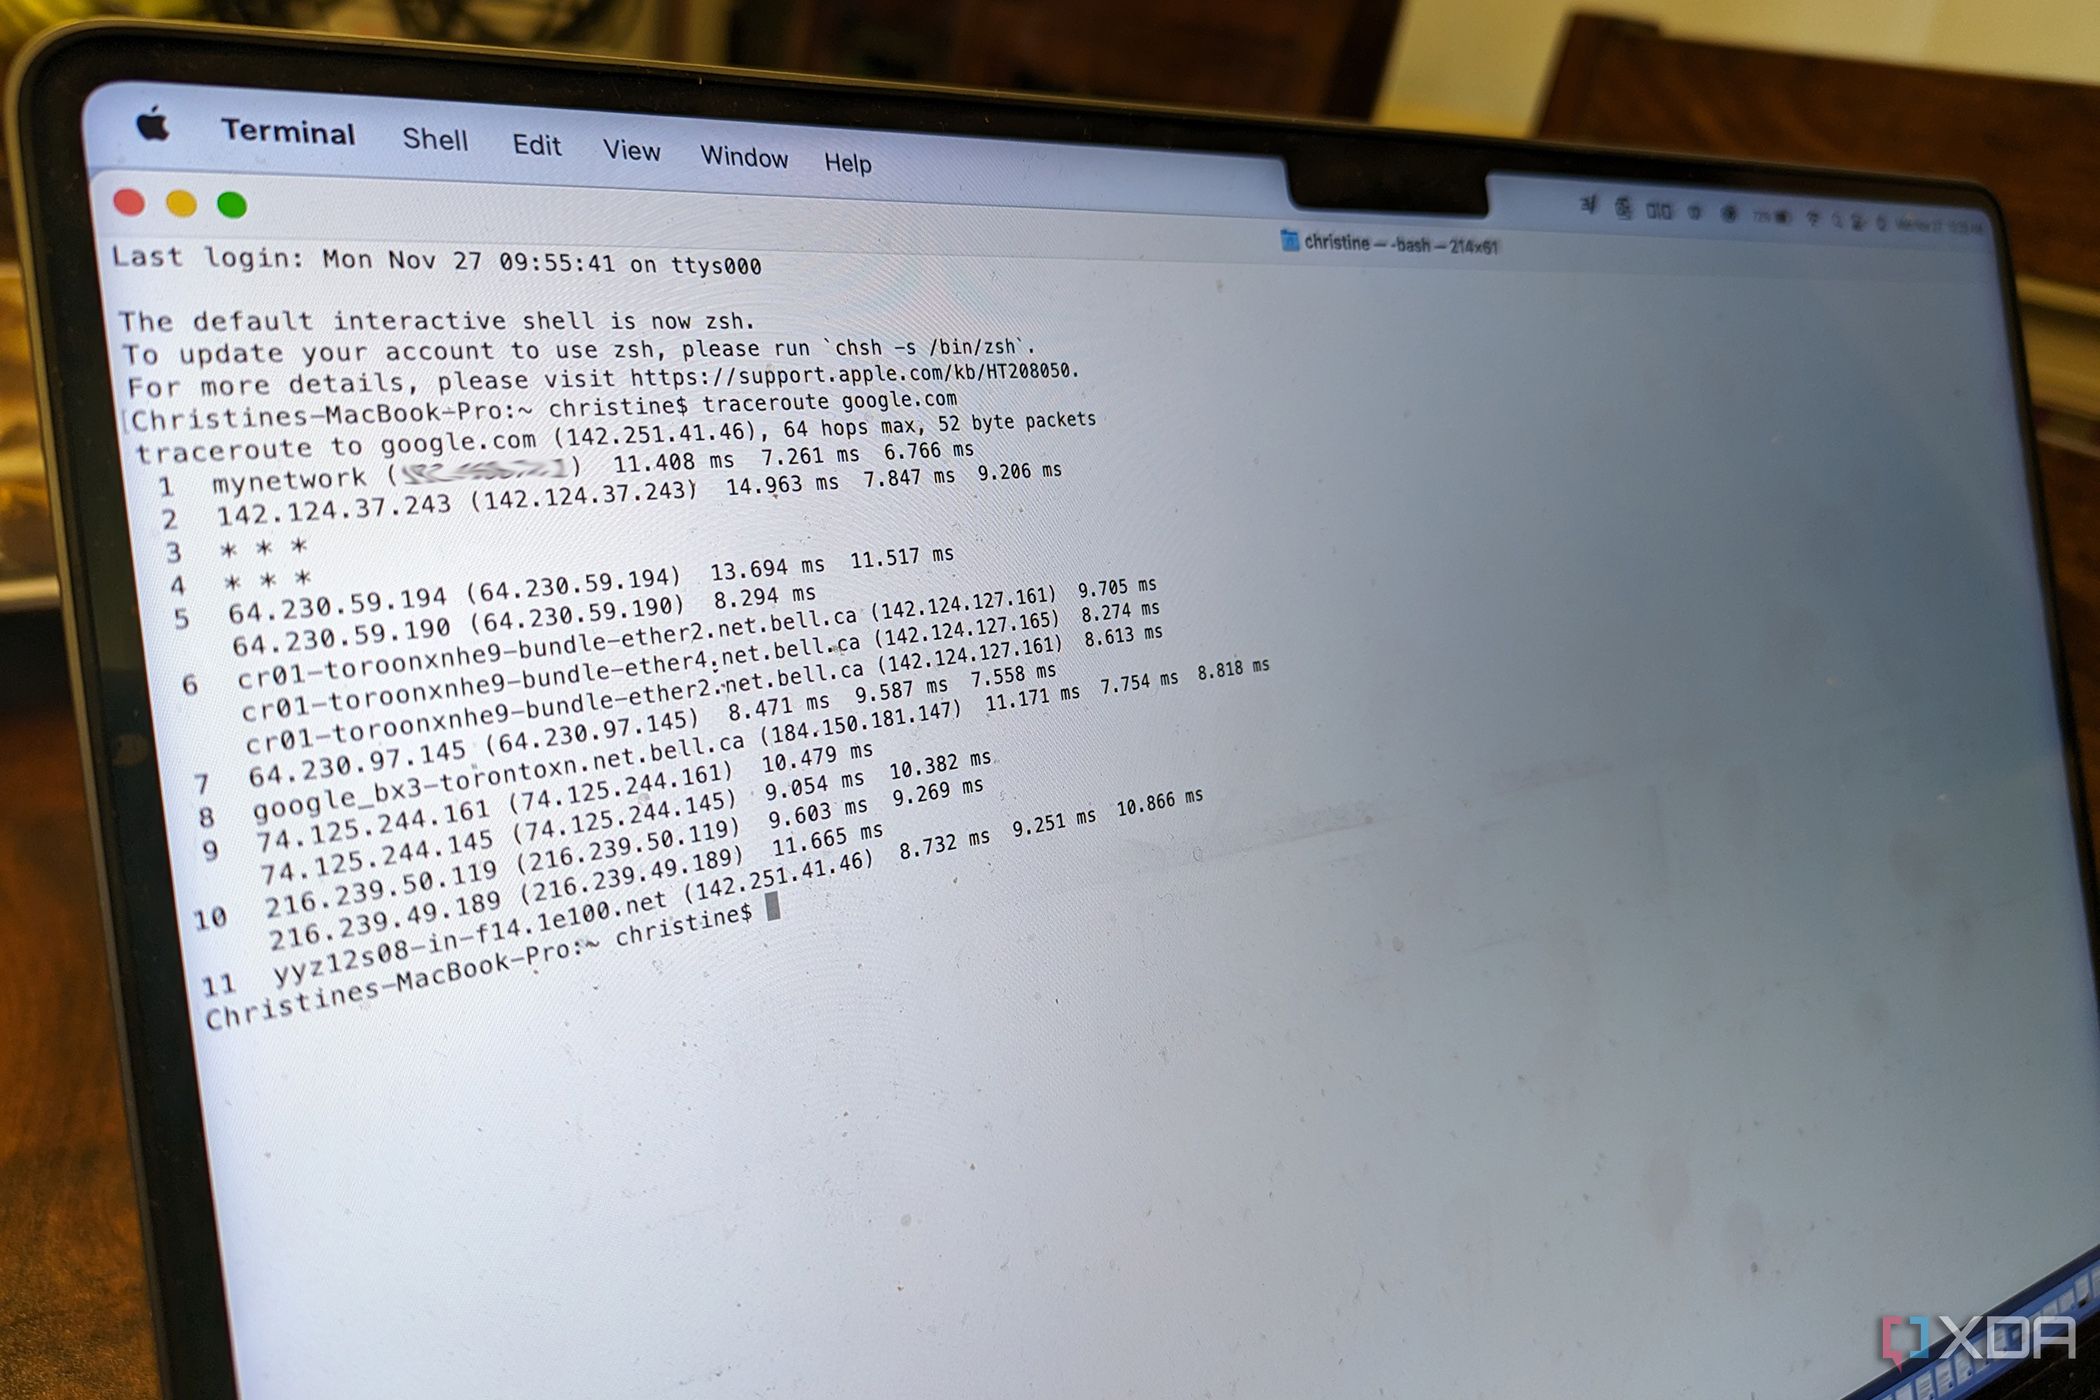
How to use Terminal on Mac
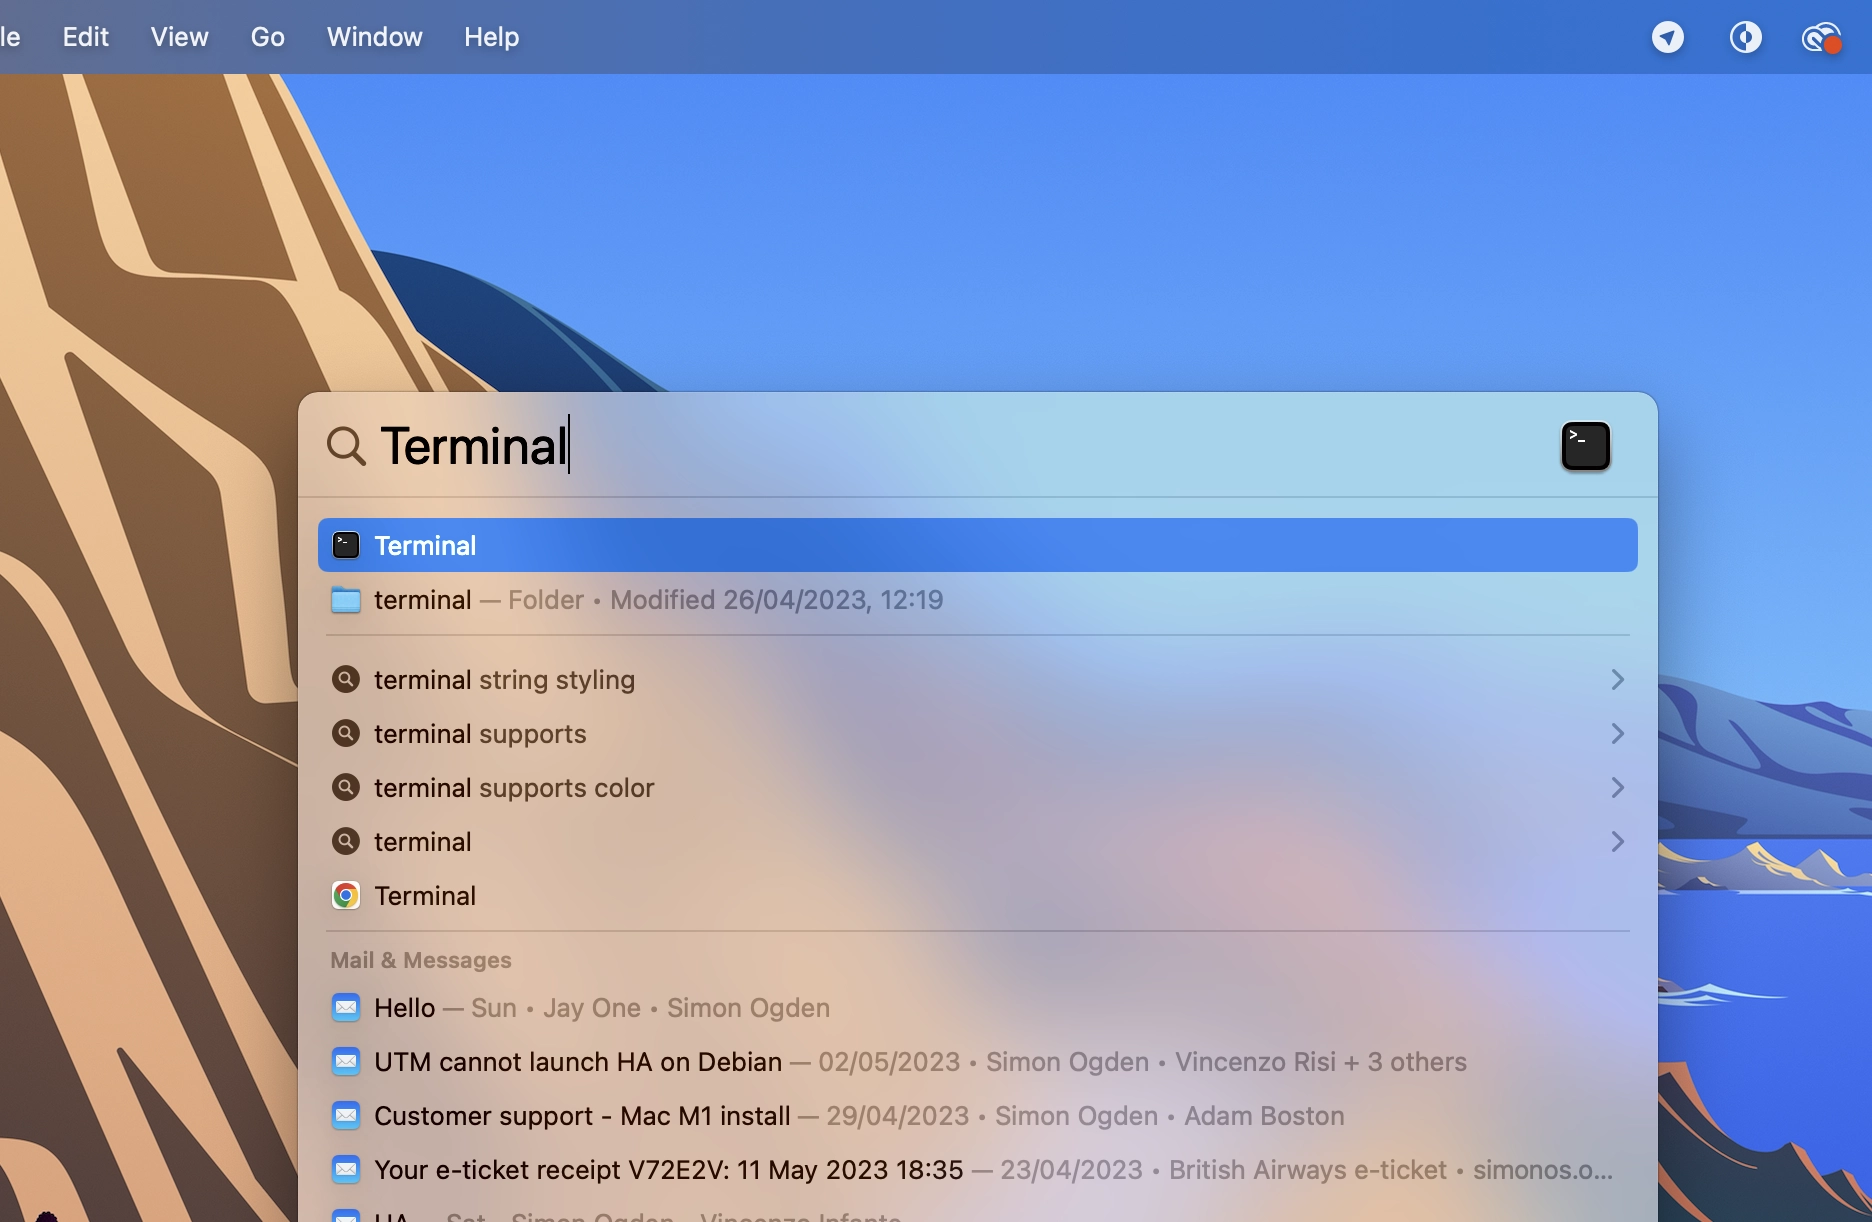
7 Easy Ways to Open a macOS Terminal (A Dummies Guide) – Siytek
MAC OS - How to Open Terminal (Command Prompt) on Mac - YouTube
How to Check if Port is Open Linux: A Comprehensive Guide – Position Is ...

How To Check Open Ports In Linux Terminal - Dibujos Cute Para Imprimir

Linux Command To Check Open Ports On Remote Server - Dibujos Cute Para ...

How To Check The List Of Open Ports In Linux - Dibujos Cute Para Imprimir
Check Open Ports Windows | Chtoby Pomnili