Your Android device is a powerful computer that holds the keys to your digital life. While the Android ecosystem is robust against threats, the evolving landscape of mobile malware demands vigilance. Understanding how to detect a virus on Android is less about spotting futuristic digital specters and more about recognizing subtle changes in performance and unauthorized data behavior. This guide provides a methodical approach to identifying, confirming, and neutralizing malicious software on your device.
Recognizing the Subtle Signs of Compromise
The first line of defense in detecting malware is observing your device's daily behavior. Modern Android malware is often designed to be stealthy, but it inevitably leaves traces. Unlike desktop viruses that might crash systems dramatically, mobile threats typically manifest as resource drains and performance hiccups. Paying attention to these subtle signs can alert you to an issue before it escalates.
Performance and Battery Anomalies
One of the most reliable indicators of a background infection is a sudden drop in performance. If your phone, which was once snappy, now feels sluggish or apps take longer to load, something might be consuming processing power. Similarly, an unexplained drop in battery life is a major red flag. Malware running in the background—such as crypto miners or bots participating in distributed denial-of-service (DDoS) attacks—requires significant energy, causing your device to drain faster than usual even when you are not actively using it.

Data Usage and Unexplained Charges
Another critical symptom is unexpected data consumption. Malware often communicates with command-and-control servers to receive instructions or exfiltrate stolen data. If you notice your mobile data usage spiking without a corresponding increase in your own browsing or streaming habits, it is worth investigating. Furthermore, if you receive a phone bill with mysterious premium service charges or unfamiliar fees, this strongly suggests that malicious software is subscribing to paid services without your knowledge.
Investigating the Source of the Infection
Once you suspect an infection, the next step is to identify the likely entry point. Android malware rarely appears spontaneously; it usually requires user interaction to gain a foothold. Adware, for example, often piggybacks on "cracked" versions of popular games or utility apps found on unofficial third-party stores. By reviewing your recent installation history, you can often trace the origin of the problem back to a specific app that promised too much.
| Symptom | Likely Cause | Immediate Action |
|---|---|---|
| Rapid battery drain | Background processes/crypto mining | Check battery usage stats |
| High data usage | Data exfiltration or ad clicks | Review app data usage |
| Unrecognized charges | Sim hijacking or premium SMS malware | Contact billing immediately |
| Pop-up ads | Adware infection | Uninstall recent suspicious apps |
Leveraging Built-in Security Tools
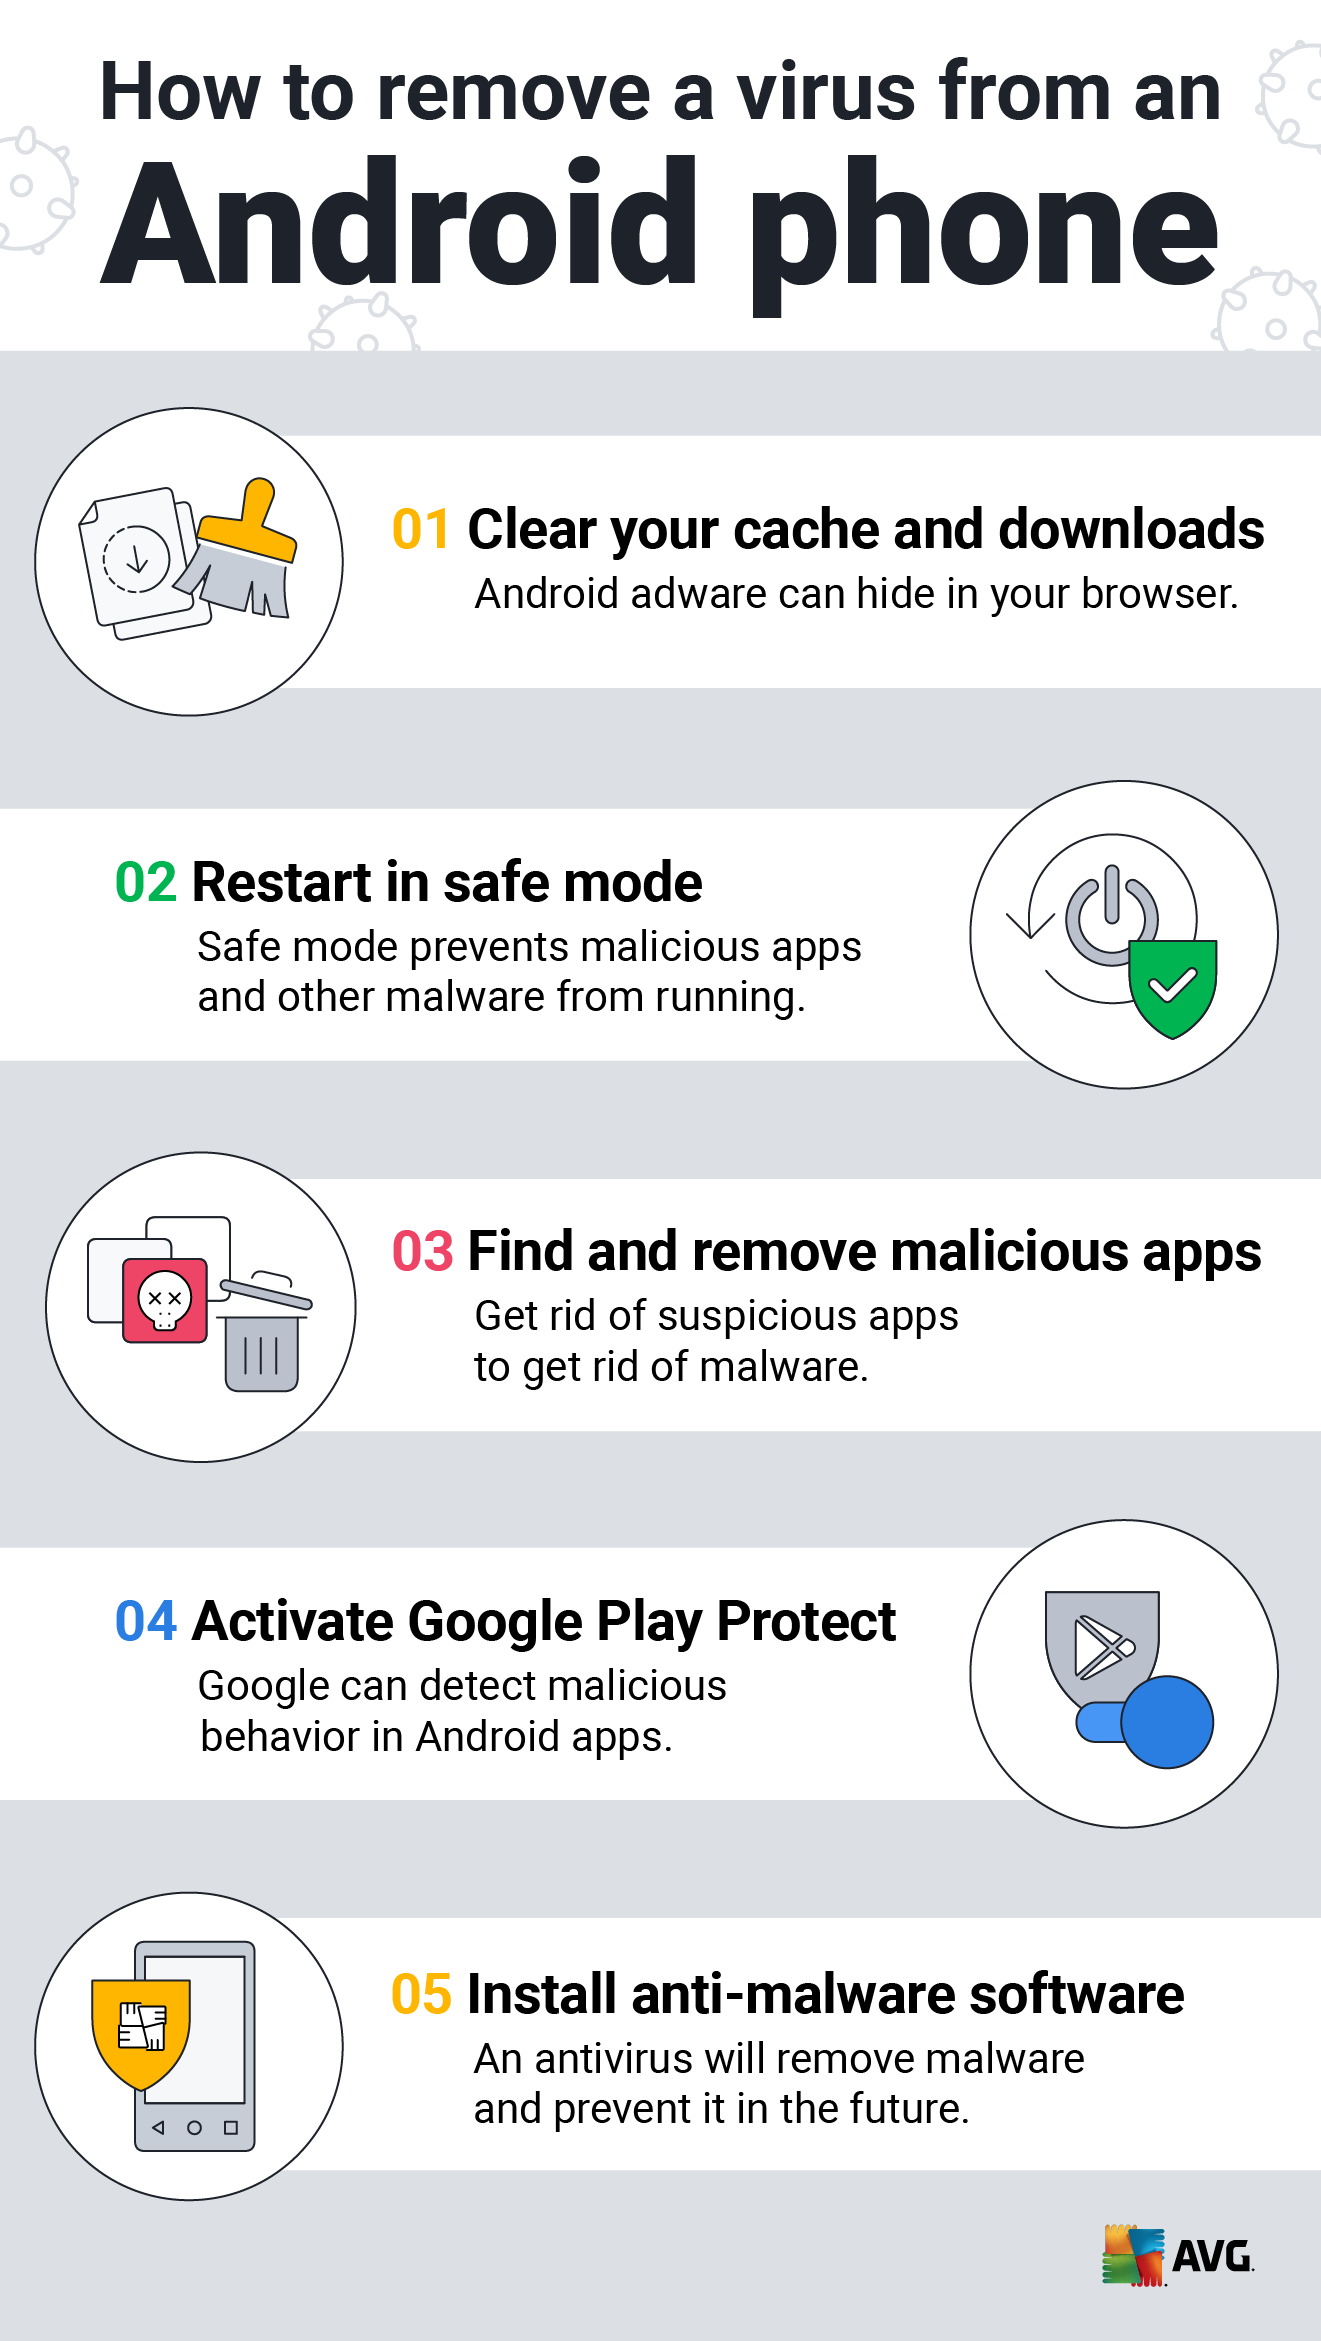
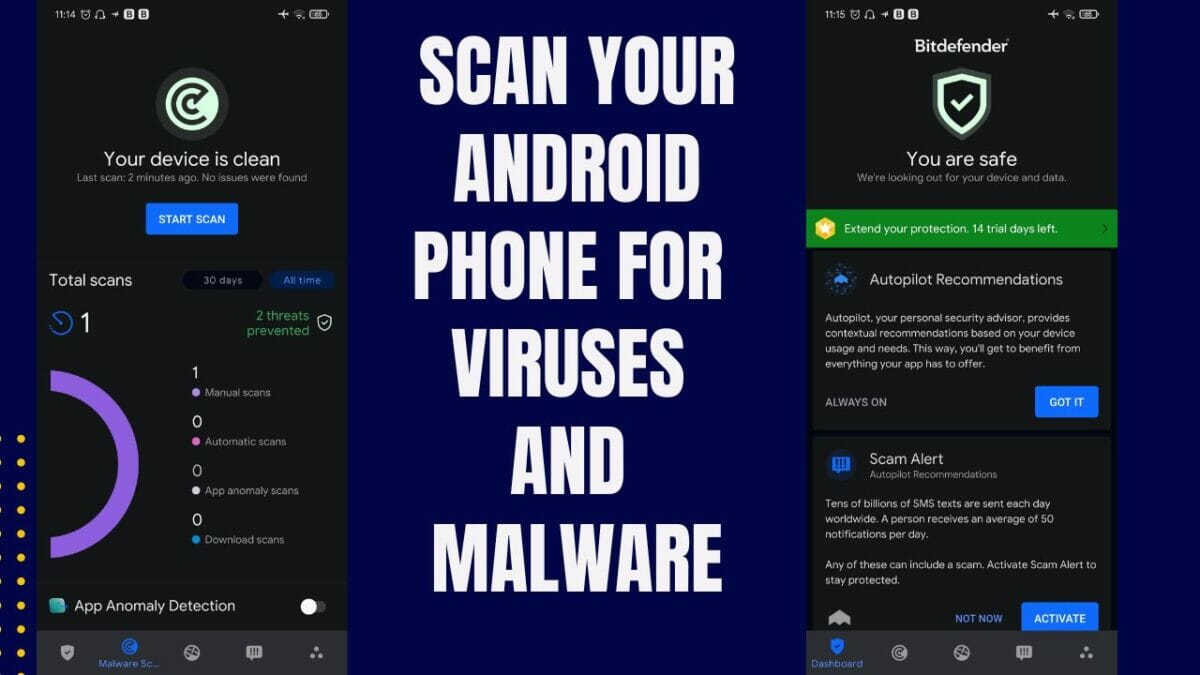
Before resorting to third-party solutions, utilize the security infrastructure Google has built into the Android operating system. Google Play Protect acts as a constant background scanner, analyzing apps as they are installed and periodically scanning the device for known threats. Ensuring this feature is active provides a baseline level of security and is often the first place to look for a diagnosis.
Running a Play Protect Scan
To manually leverage these tools, open the Google Play Store app, tap your profile icon, and select "Play Protect." From here, you can initiate a scan of your device. While this process is thorough, it relies on a database of known signatures. Therefore, it might not catch zero-day exploits or sophisticated obfuscated malware immediately, but it is an essential step in ruling out common threats.
The Manual Investigation and Removal Process
If the built-in tools do not resolve the issue, a manual investigation is necessary. This involves a degree of digital forensics, where you must play detective on your own device. The goal is to isolate the malicious app, which is usually the weakest link in the security chain. This often requires booting the device into Safe Mode, a diagnostic state that disables all third-party applications.
Identifying and Quarantining the Culprit
In Safe Mode, observe if the symptoms of the virus disappear. If the device runs smoothly, you have confirmed that a third-party app is the source. You can then methodically review your app list, looking for anything unfamiliar, recently installed, or with suspicious permissions—such as a flashlight app requesting access to your contacts or a game demanding SMS permissions. Uninstalling this app usually resolves the immediate threat, but it is crucial to change any passwords accessed through the compromised device.
How To Detect And Remove Malware From Your Android device - TechStory
How to Remove Virus from Android Free | Step-by-Step Guide

How to Detect a Phone Virus on Android: 10 Steps (with Pictures)

How to Scan Viruses & Malware from Your Android Phone - YouTube
How to Remove a Virus from an Android Phone or iPhone | AVG

How to Detect a Phone Virus on Android: 10 Steps (with Pictures)

How to Remove Viruses from Android Phone? (Super Easy!) - YouTube
How to Scan Your Android Phone for Viruses and Malware in 2023 ...
How to Find and Remove Viruses on Android Smartphones

How to Detect a Phone Virus on Android: 10 Steps (with Pictures)
How to Know If Your Phone Has a Virus? Here’re Various Signs! - MiniTool
How to Detect Apps with Virus on Android Phone - YouTube

How to check for viruses on Android (and get rid of them)
How to Check Android for Virus (How to Know if Your Android Phone Has a ...
How To Detect And Remove Viruses From Your Phone A Step By Step Guide

The Best Way to Run an Android Virus Scan on Your Device - norse-corp.com

How to Detect a Phone Virus on Android: 10 Steps (with Pictures)
Here's The Easiest Way To Scan Your Android Phone For Viruses

Detect and Remove Android Viruses [Virus Removal for Android]
How to detect Malware on Android device? - AstrillVPN Blog