Managing Active Directory Users and Computers in Windows 10
As a Windows 10 administrator, managing Active Directory (AD) users and computers is a crucial task to maintain the security and efficiency of your organization's network. In this article, we will delve into the world of Active Directory management, exploring its benefits, key features, and best practices for managing users and computers on your Windows 10 network.
What is Active Directory?
Active Directory is a directory service developed by Microsoft to manage and authenticate users, computers, and other resources on a network. It provides a centralized repository for storing and managing user data, group policies, and other network settings. AD allows administrators to control access, assign permissions, and monitor activity on the network.
Benefits of Active Directory in Windows 10
The benefits of using Active Directory in Windows 10 are numerous:
- Centralized management: AD provides a single point of control for managing users, computers, and other network resources.
- Improved security: AD enables you to implement security policies, such as password policies, account lockout policies, and access control lists (ACLs).
- Reduced administrative burden: AD automates tasks such as user account creation, password management, and group membership management.
- Enhanced user experience: AD provides a unified login experience for users, allowing them to access resources and applications across the network with a single set of credentials.
Active Directory Users and Computers Tool
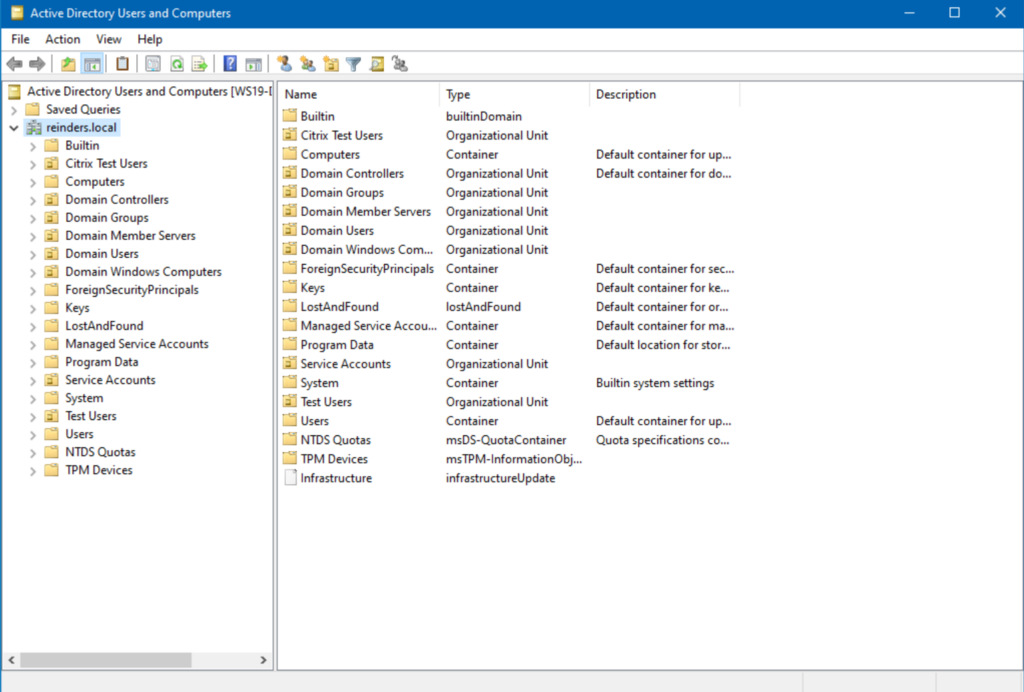
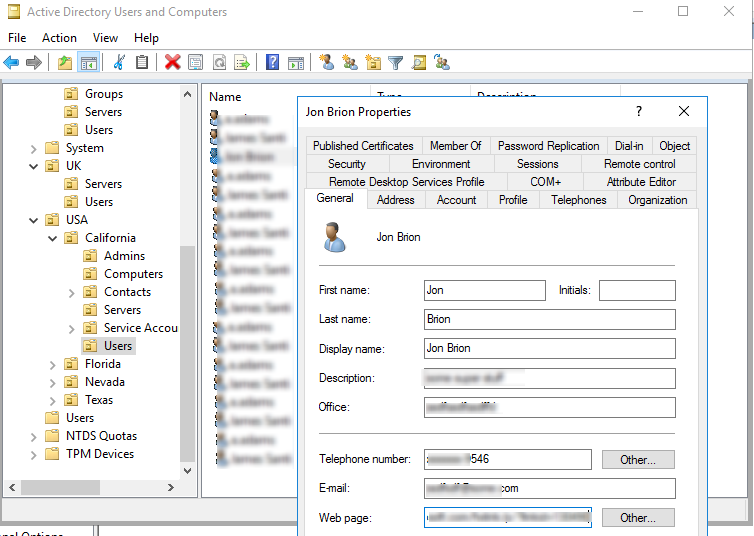
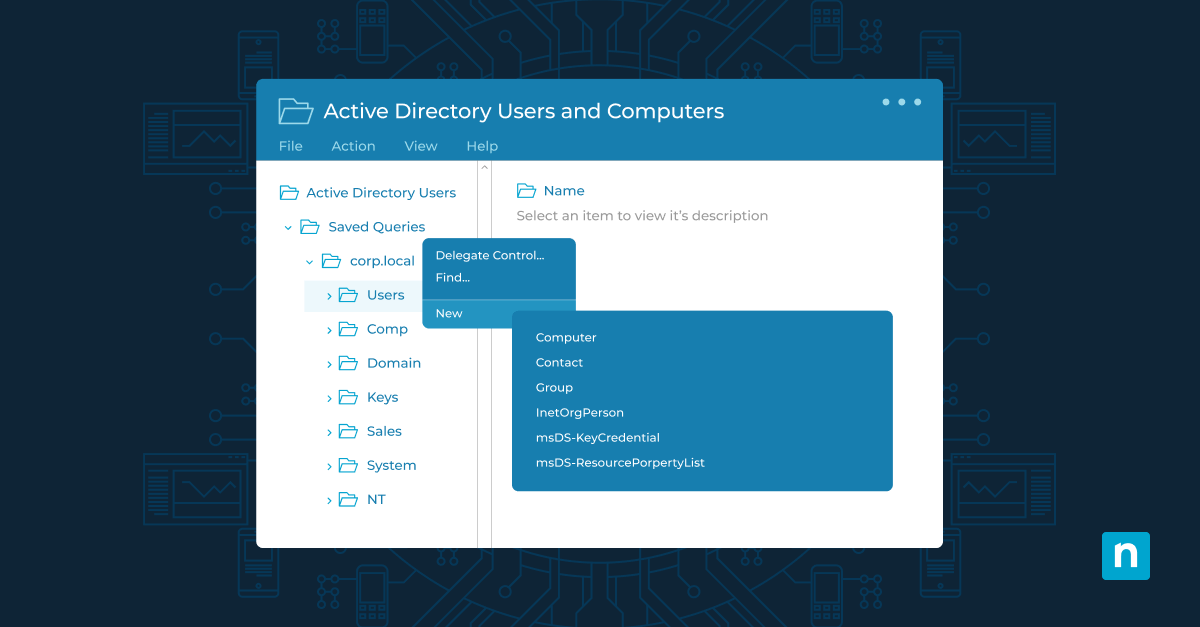
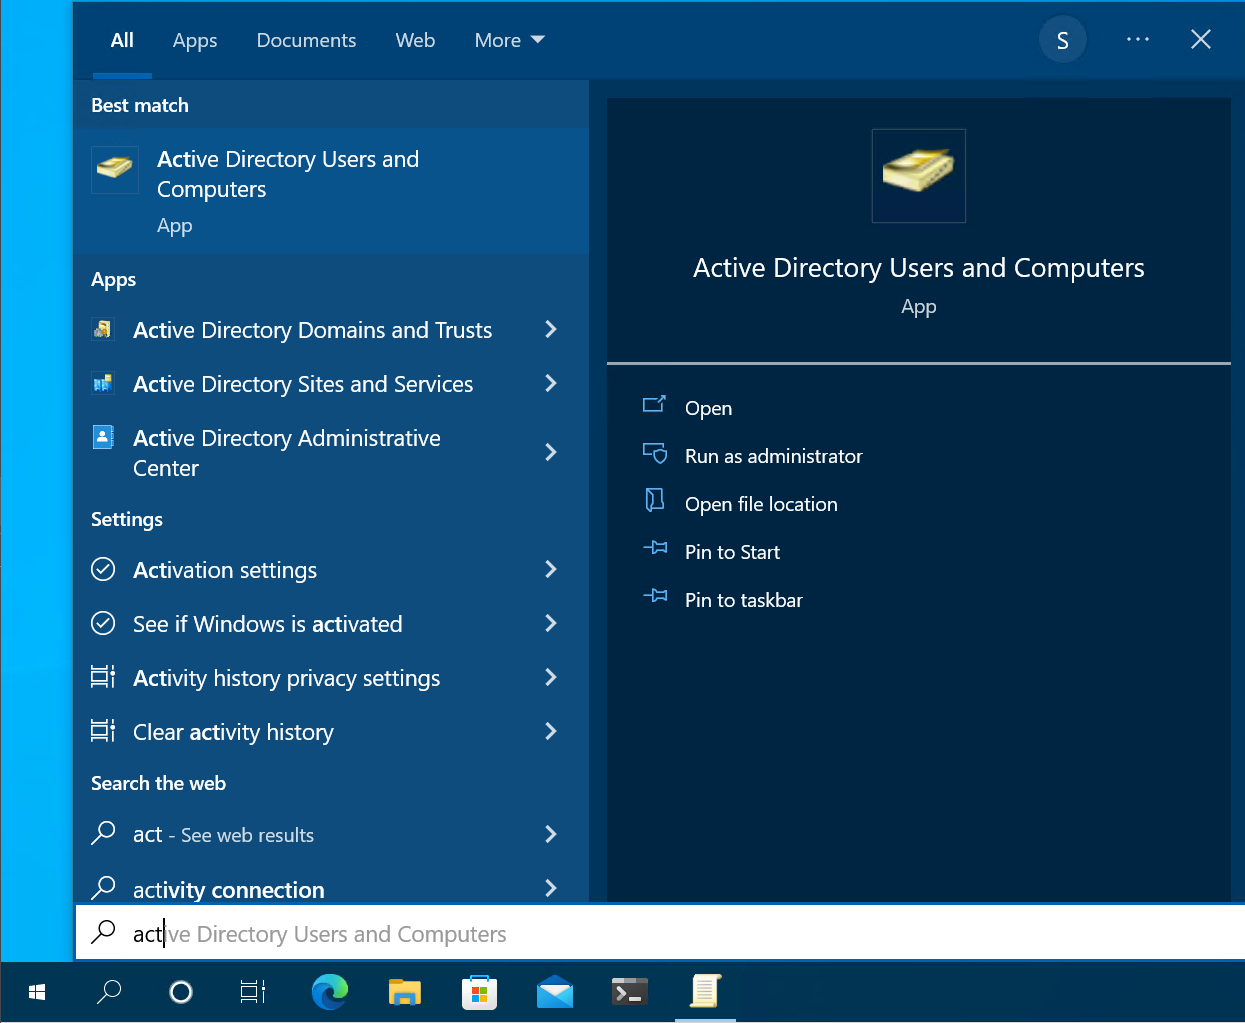
The Active Directory Users and Computers (ADUC) tool is a graphical user interface (GUI) that allows administrators to manage AD users, computers, and other resources. To access ADUC in Windows 10, follow these steps:
1. Open the Start menu and search for "Active Directory Users and Computers."
2. Click on the result to open the ADUC console.

3. You will see a tree view of your AD structure, including domains, organizational units (OUs), and users and computers.
Managing AD Users
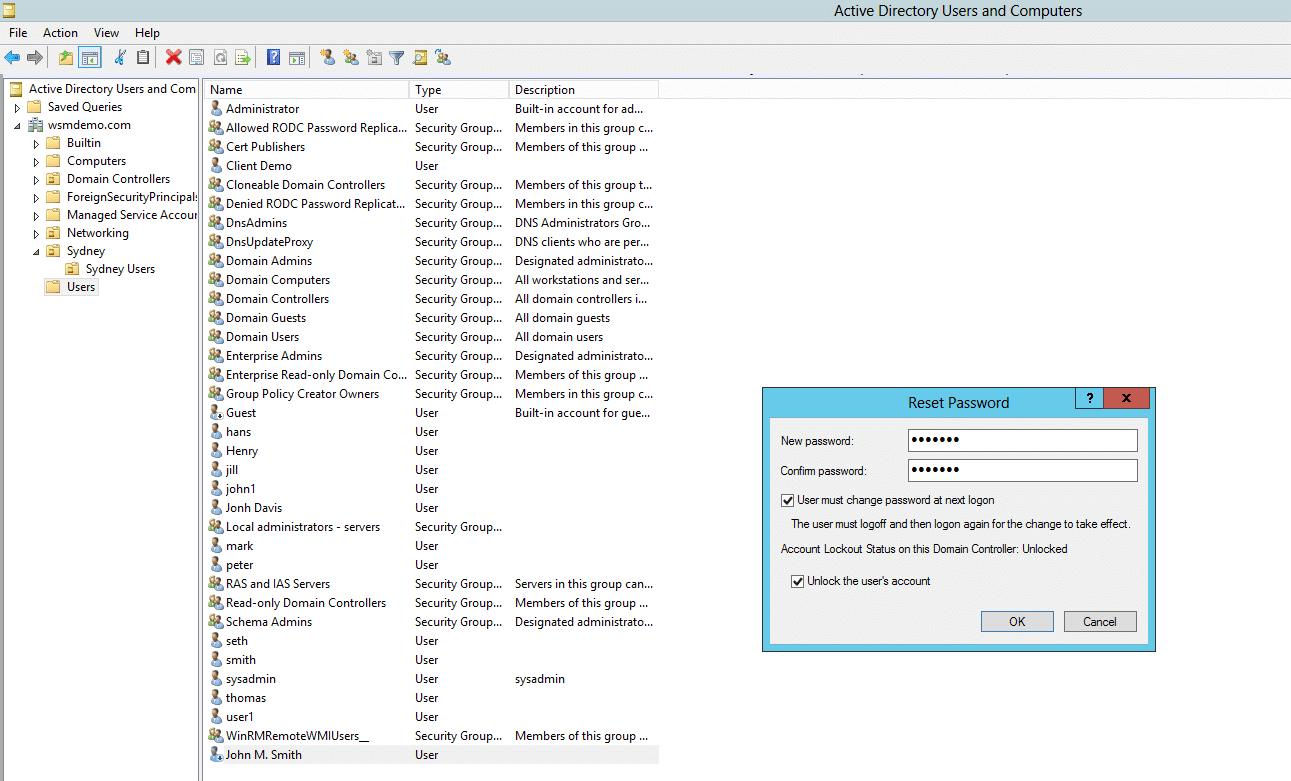
Managing AD users involves creating, modifying, and deleting user accounts, as well as assigning permissions and group memberships.
To create a new user account, follow these steps:
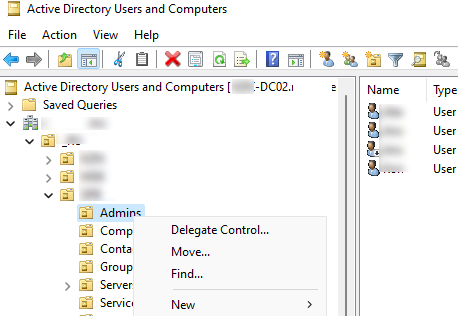
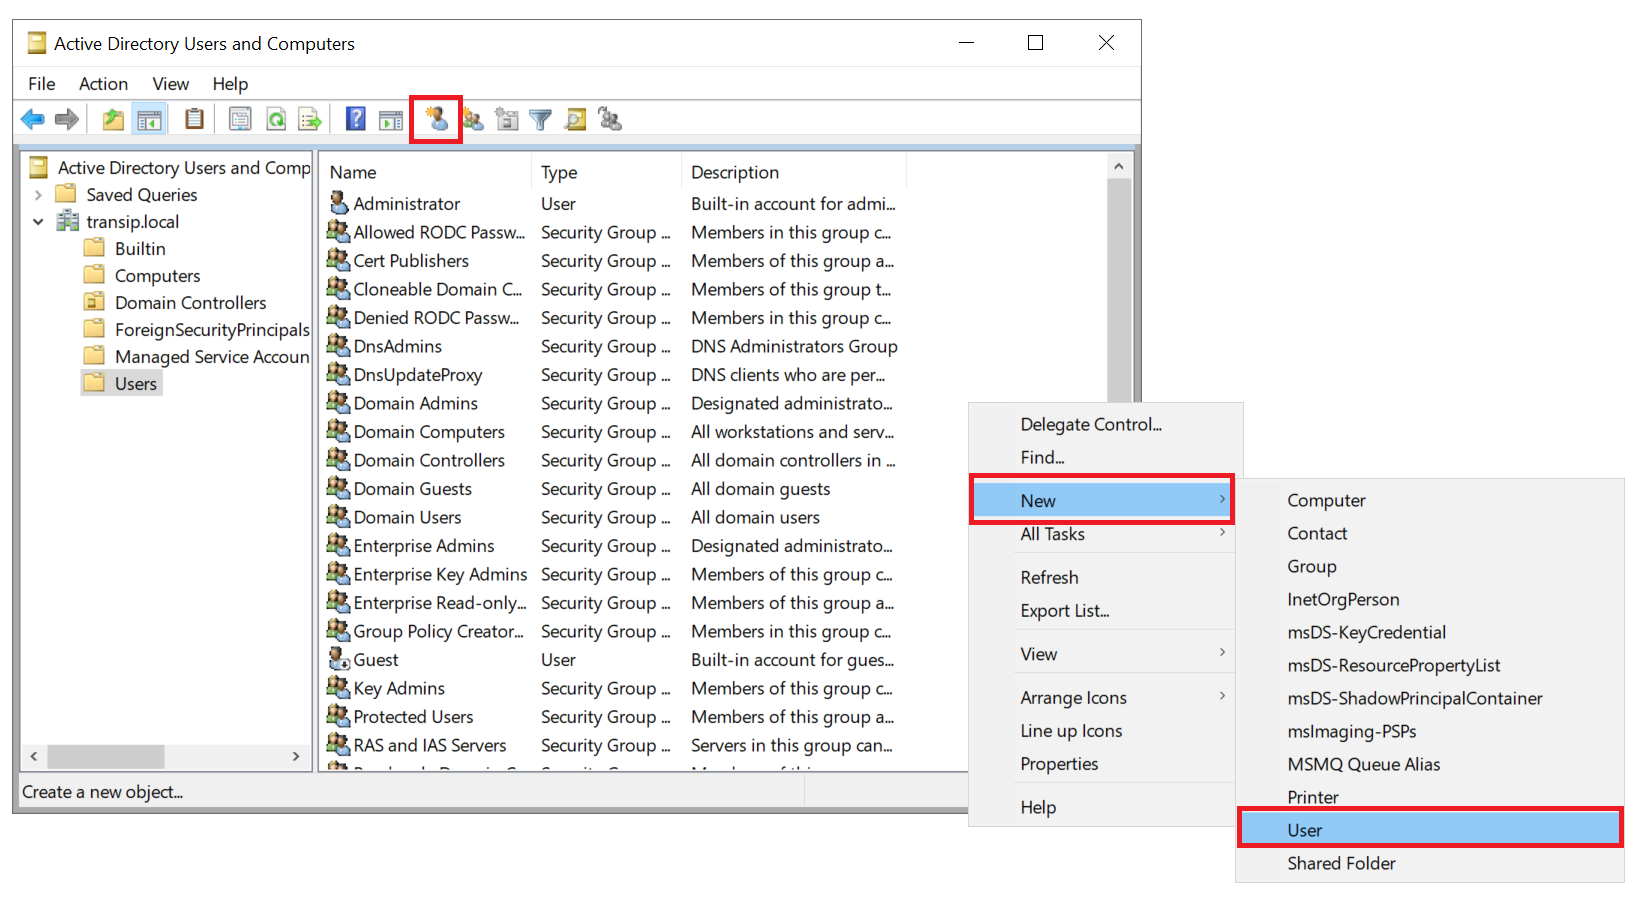
1. Open the ADUC console and navigate to the OU where you want to create the new user account.
2. Right-click on the OU and select "New" > "User."
3. Fill in the required user information, including the user name, first name, last name, and password.
4. Assign the user to a group or assign permissions as needed.
Managing AD Computers
Managing AD computers involves adding, modifying, and deleting computer accounts, as well as assigning computer properties and group memberships.
To add a new computer account, follow these steps:
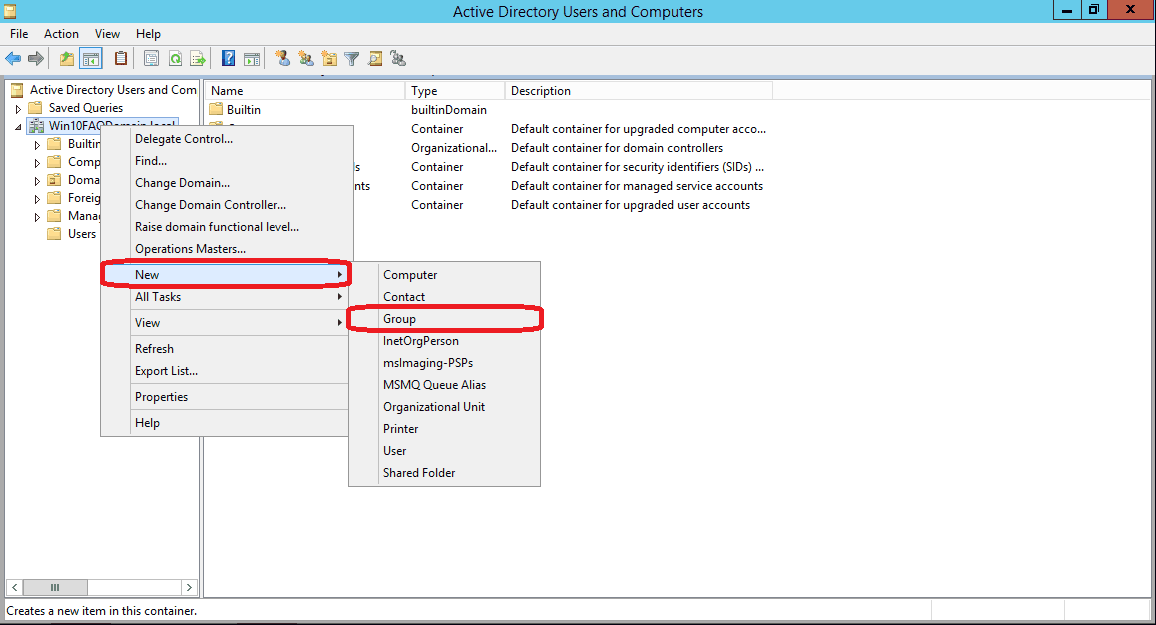
1. Open the ADUC console and navigate to the OU where you want to add the new computer account.
2. Right-click on the OU and select "New" > "Computer."
3. Fill in the required computer information, including the computer name and DNS host name.
4. Assign the computer to a group or assign properties as needed.
Best Practices for Active Directory Management
To ensure the security and efficiency of your AD environment, follow these best practices:
- Regularly back up AD databases to prevent data loss in case of a disaster.
- Use strong passwords and password policies to prevent unauthorized access.
- Monitor AD activity and alert logs to detect potential security threats.
- Regularly update and patch AD servers to prevent vulnerabilities.
Conclusion
Active Directory is a powerful tool for managing users and computers on your Windows 10 network. By understanding the benefits, key features, and best practices for AD management, you can ensure the security and efficiency of your organization's network. Remember to regularly back up AD databases, use strong passwords and password policies, and monitor AD activity to prevent potential security threats.