When it comes to maintaining the security and integrity of your Windows operating system, disabling network access to the Windows Registry is a crucial step. The Windows Registry is a critical component of your system, storing vital information such as system settings, user preferences, and application data. However, if malicious actors gain access to your Registry, they can cause significant harm to your system, including deleting or modifying critical settings, injecting malware, or even taking control of your system remotely. In this article, we will explore why disabling network access to the Windows Registry is essential and provide a step-by-step guide on how to do it safely and effectively.
Why Disabling Network Access to the Windows Registry Matters
The Windows Registry is a complex and sensitive area of your system, and compromising its security can have serious consequences. If a malicious actor gains network access to your Registry, they can:
- Modify or delete critical system settings, leading to system instability or crashes.
- Inject malware or viruses into your system, potentially causing significant damage.
- Take control of your system remotely, allowing them to access sensitive data or cause harm.
- Steal sensitive information, such as login credentials or credit card numbers.
How to Disable Network Access to the Windows Registry
To disable network access to the Windows Registry, you'll need to follow these steps:

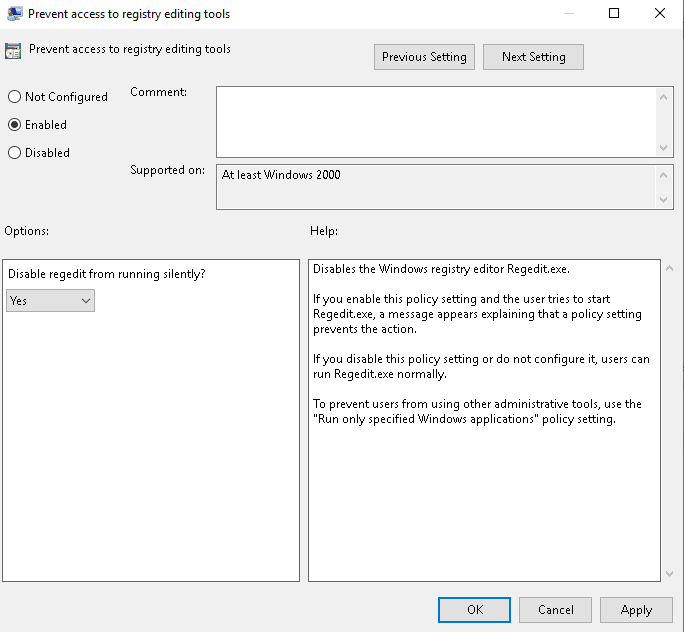
Method 1: Using Group Policy Editor
- Open the Group Policy Editor by searching for "gpedit.msc" in the Start menu.
- Navigate to Computer Configuration > Administrative Templates > Windows Components > Windows Remote Management (WinRM) > WinRM Service.
- Double-click on the "Allow automatic configuration of DNS client settings" policy and set it to "Disabled".
- Double-click on the "Allow remote access to the Windows Registry" policy and set it to "Disabled".
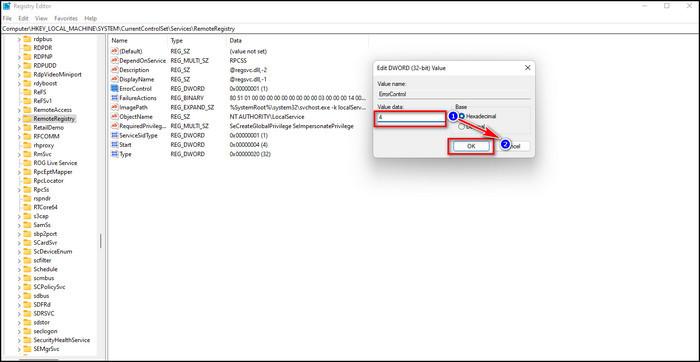
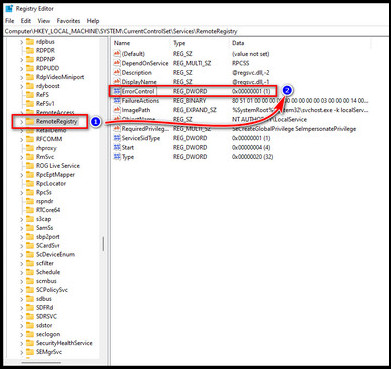
Method 2: Using Registry Editor
- Open the Registry Editor by searching for "regedit" in the Start menu.
- Navigate to the following key: HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\winmgmt\Parameters
- Double-click on the "RemoteAccess" value and set it to "0" (zero).
- Double-click on the "WinRmAllowRemoteAccess" value and set it to "0" (zero).
Verifying Network Access to the Windows Registry
To ensure that network access to the Windows Registry has been successfully disabled, you can follow these steps:
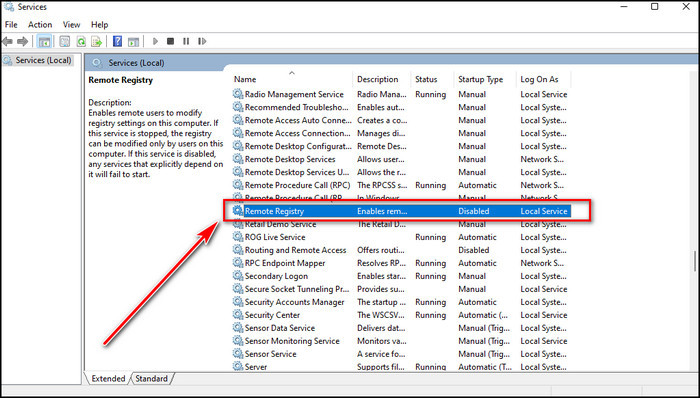
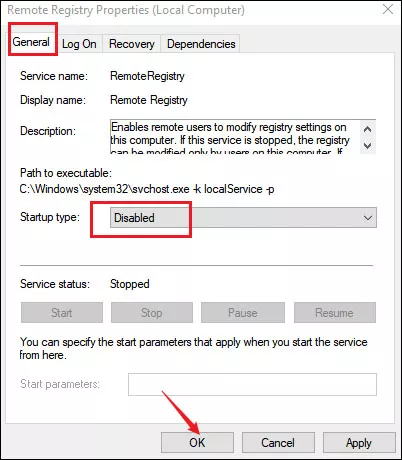
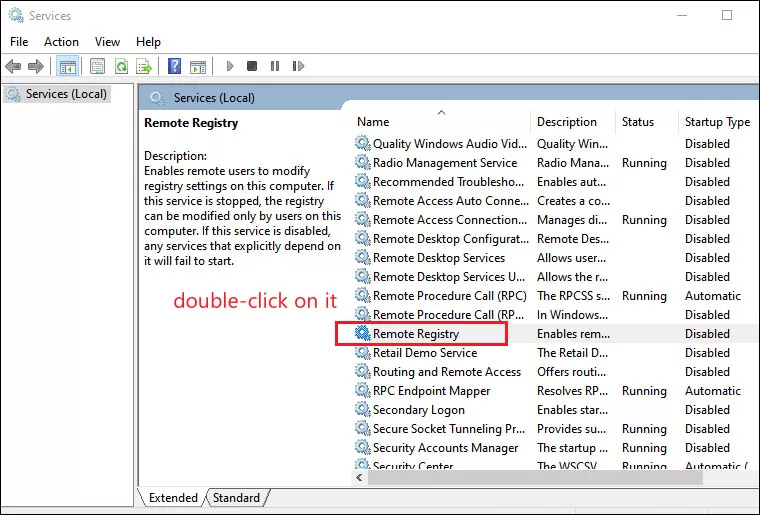
- Open the Windows Services console by searching for "services.msc" in the Start menu.
- Navigate to the Windows Remote Management (WinRM) service and check that its status is set to "Stopped".
- Open the Registry Editor and navigate to the Windows Registry key: HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\winmgmt\Parameters
- Verify that the "RemoteAccess" value is set to "0" (zero) and the "WinRmAllowRemoteAccess" value is set to "0" (zero).
Tips and Considerations
Before disabling network access to the Windows Registry, keep the following in mind:
- This step may impact certain system features or applications that rely on remote access to the Registry.
- Disabling network access to the Windows Registry does not eliminate the risk of malware or other security threats.
- You should regularly update your operating system and antivirus software to maintain the security of your system.
Conclusion
Disabling network access to the Windows Registry is a critical step in maintaining the security and integrity of your Windows operating system. By following the steps outlined in this article, you can significantly reduce the risk of malicious actors gaining unauthorized access to your system's most sensitive areas. Remember to regularly verify that network access to the Windows Registry has been successfully disabled and to consider the potential impacts on system features and applications.