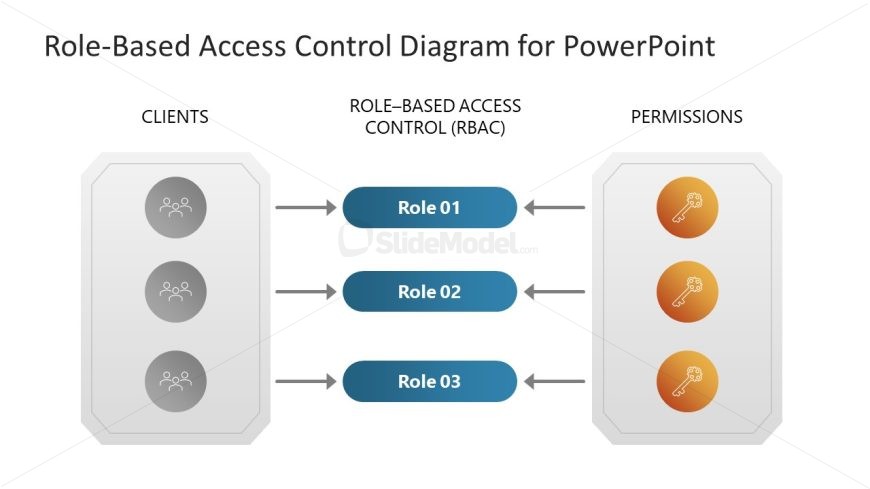
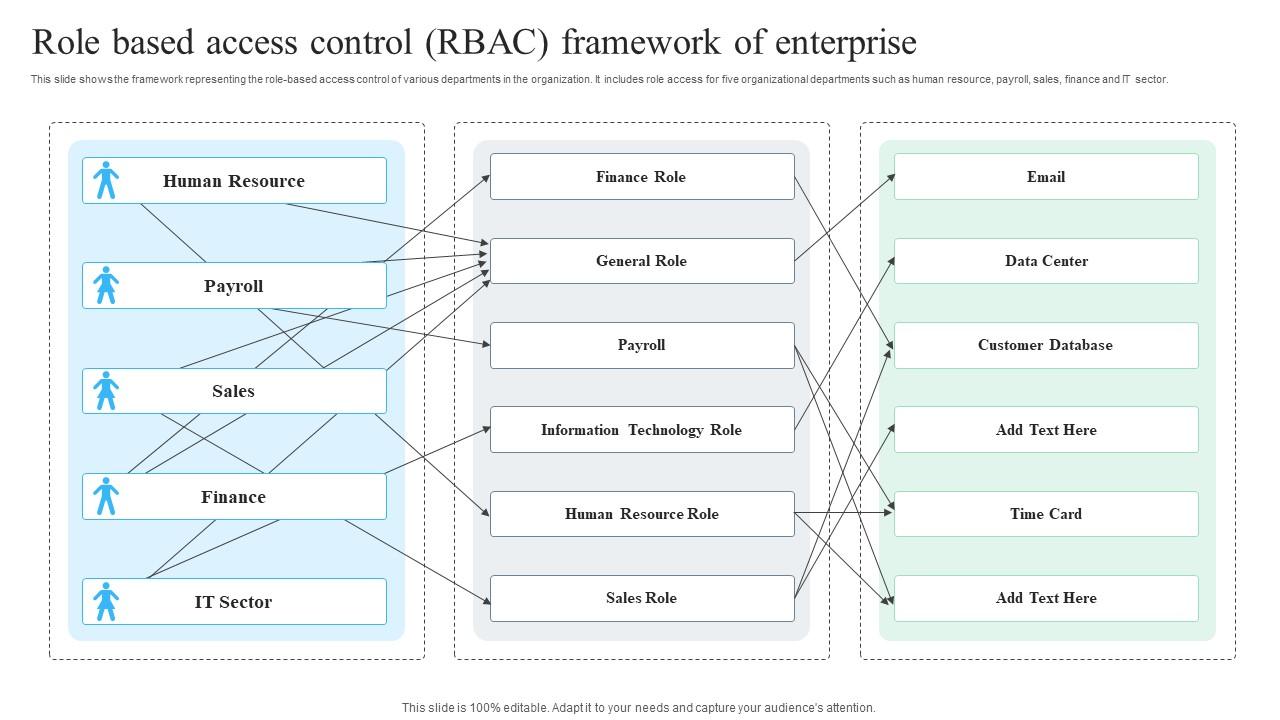
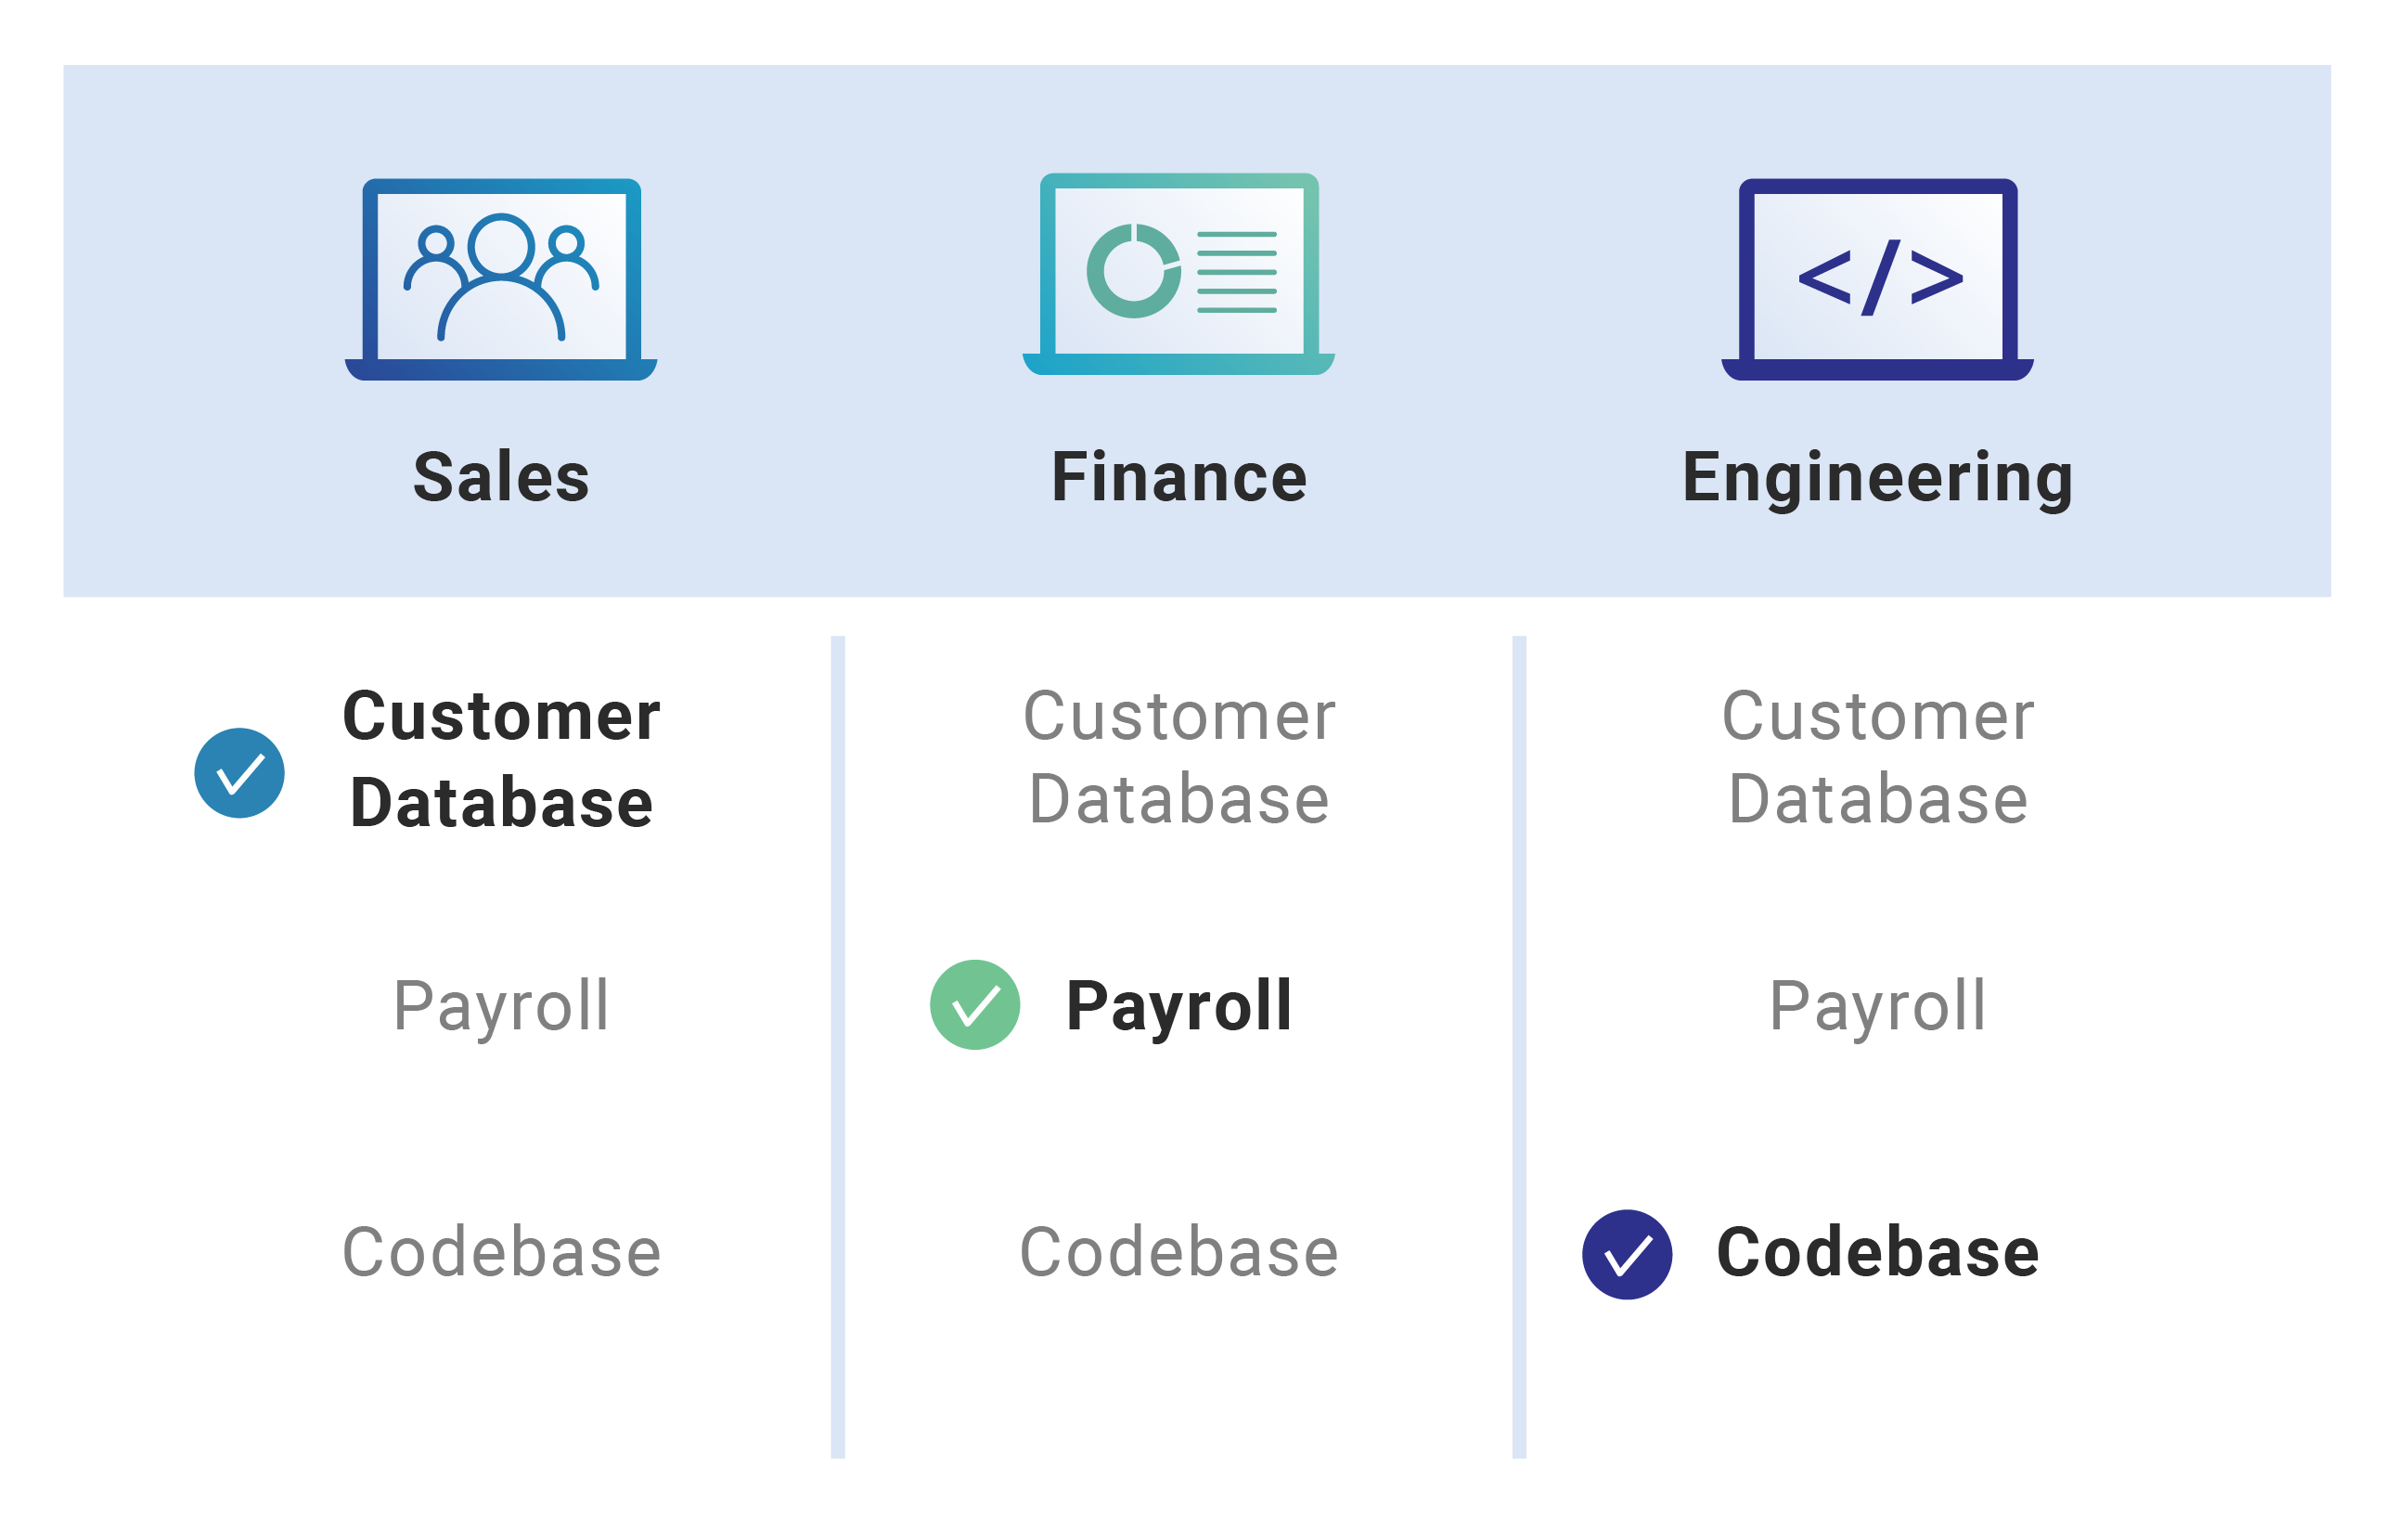
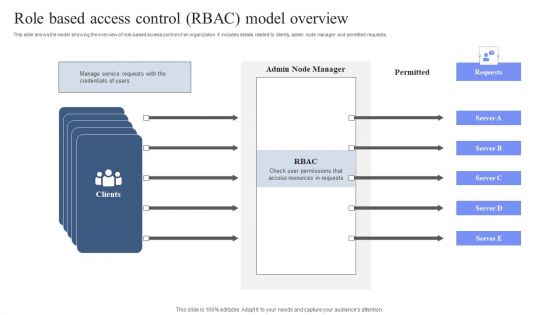
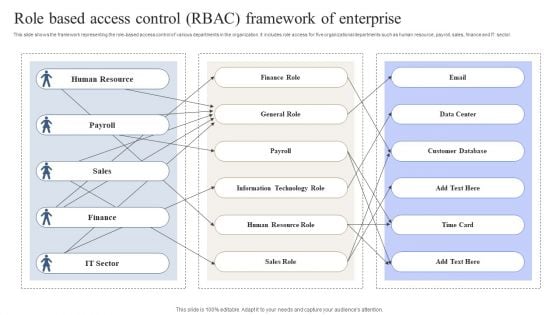
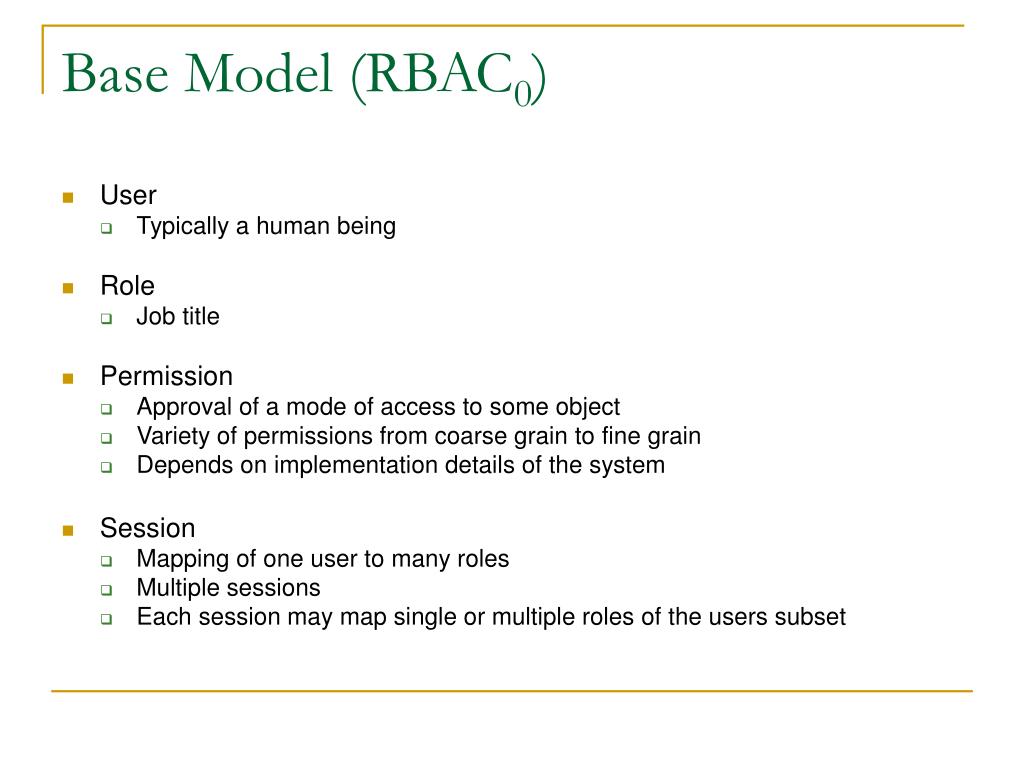
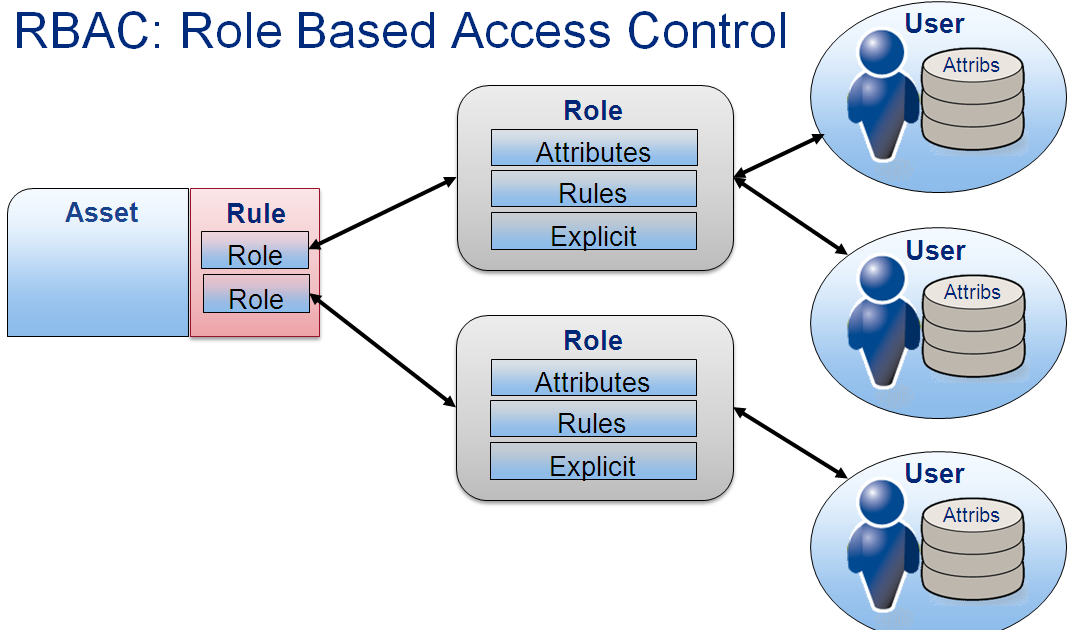
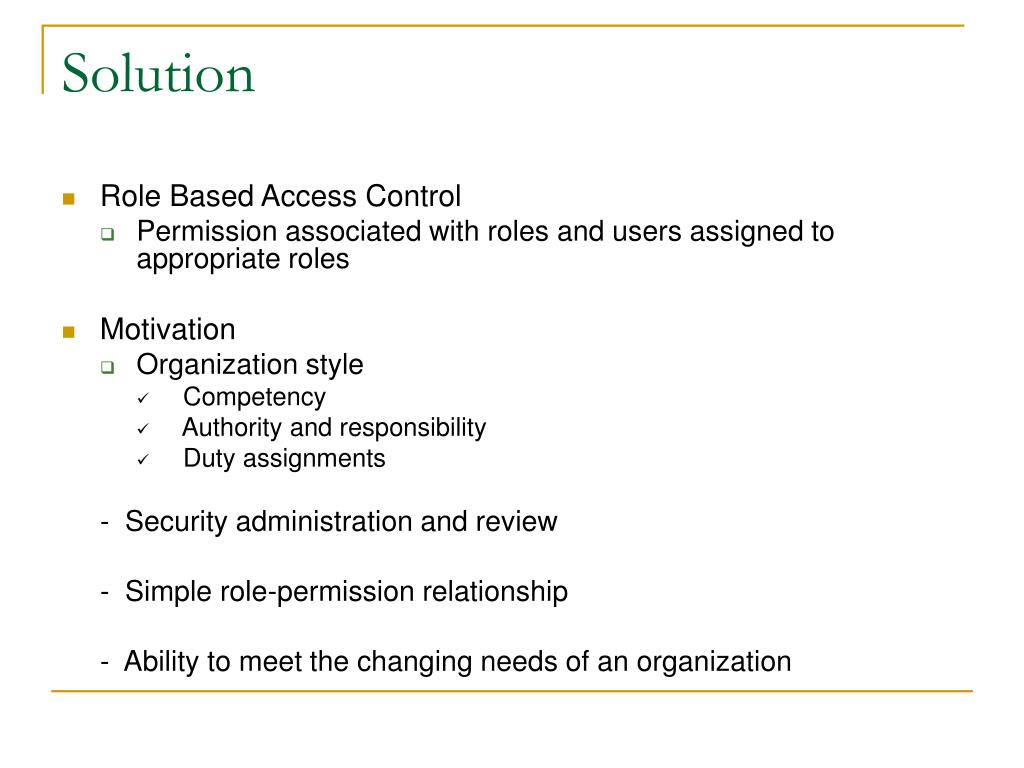
In computer systems security, role-based access control (RBAC) or role-based security is an approach to restricting system access to authorized users, and to implementing mandatory access control (MAC) or discretionary access control (DAC).Role-based access control is a policy-neutral access control mechanism defined around roles and privileges. The components of RBAC such as role-permissions, user-role and role-role relationships make it simple to perform user assignments. A study by NIST has demonstrated that RBAC addresses many needs of commercial and government organizations. RBAC can be used to facilitate administration of security in large organizations with hundreds of users and thousands of permissions. Although RBAC is different from MAC and DAC access control frameworks, it can enforce these policies without any complication.
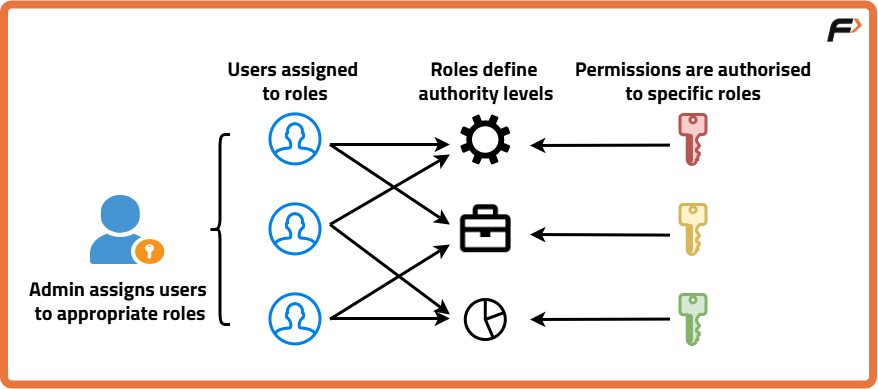
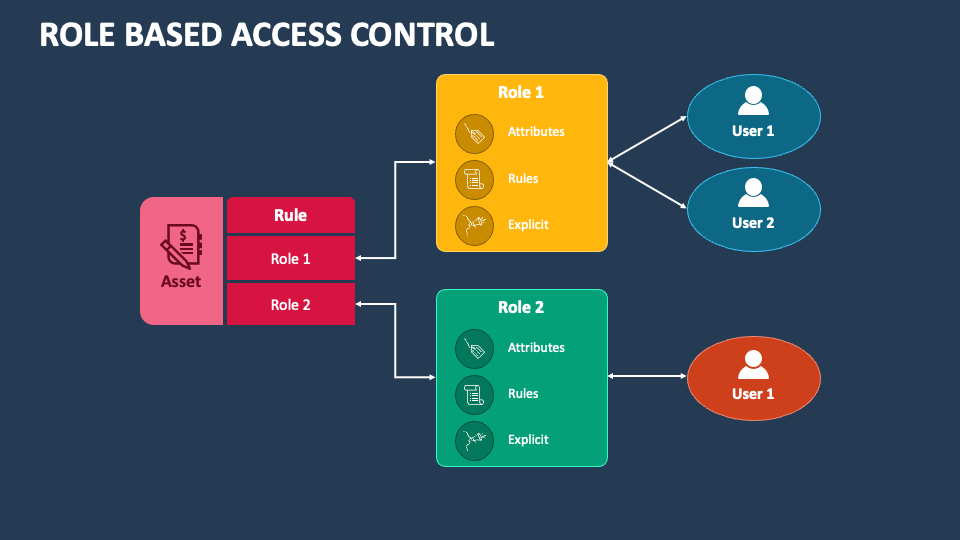
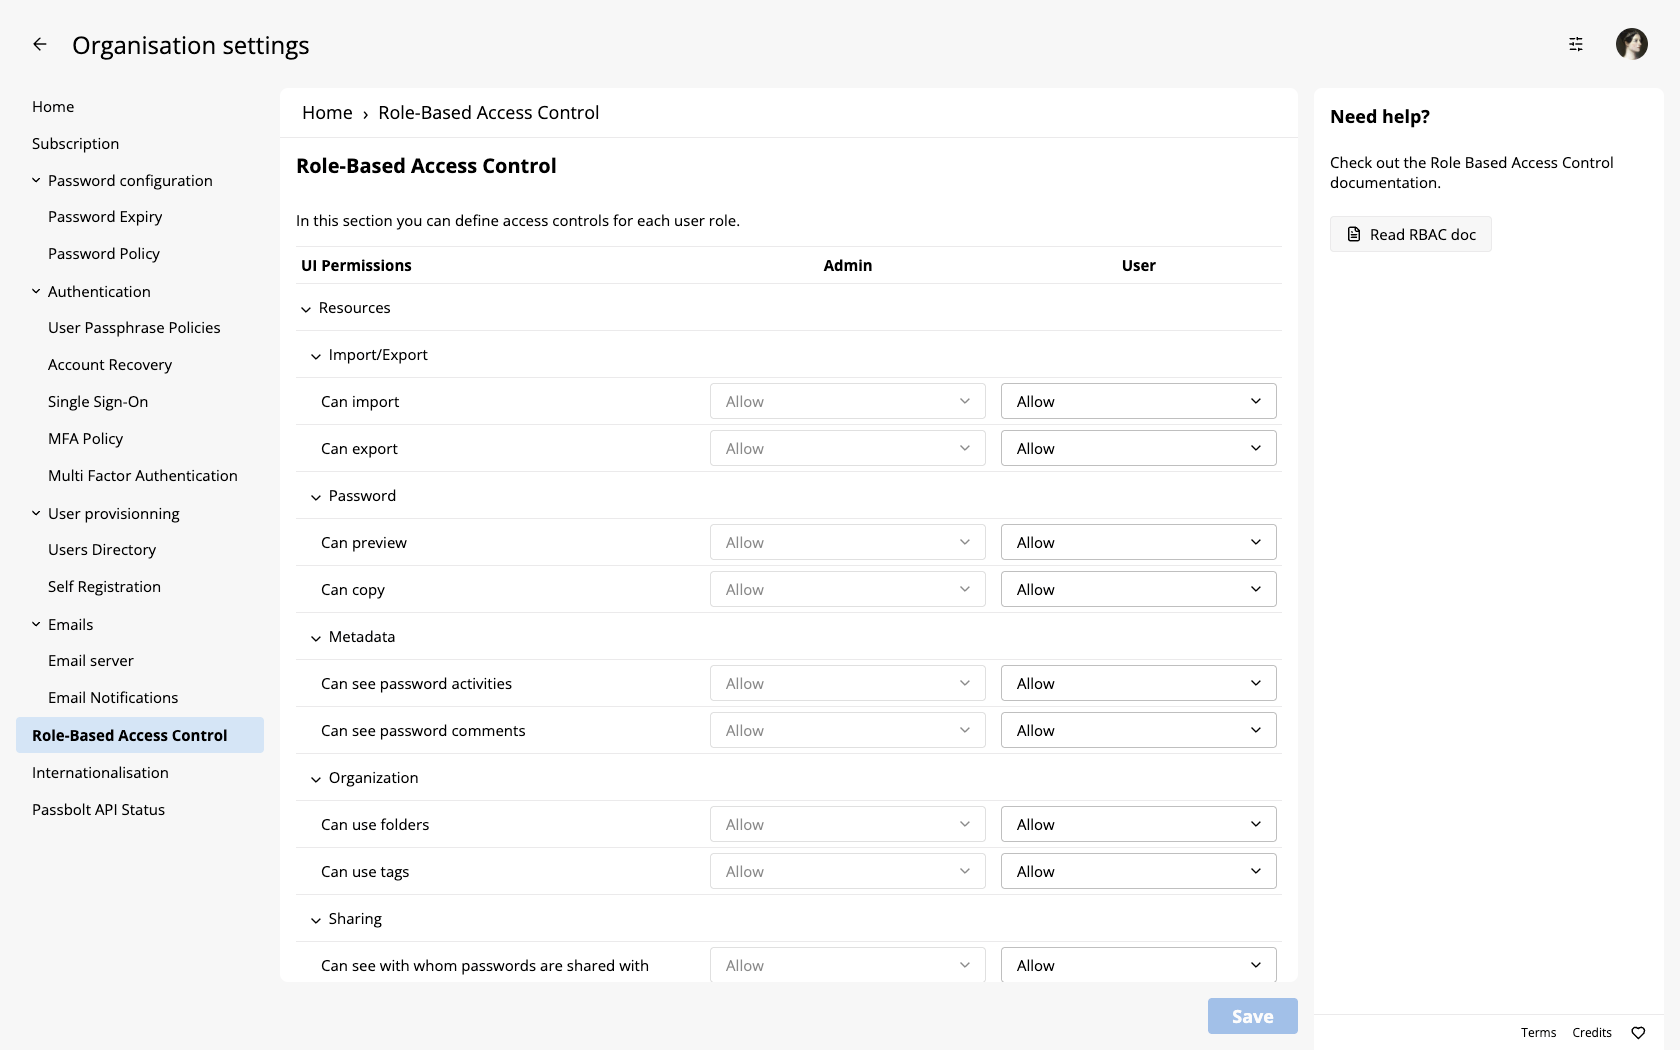
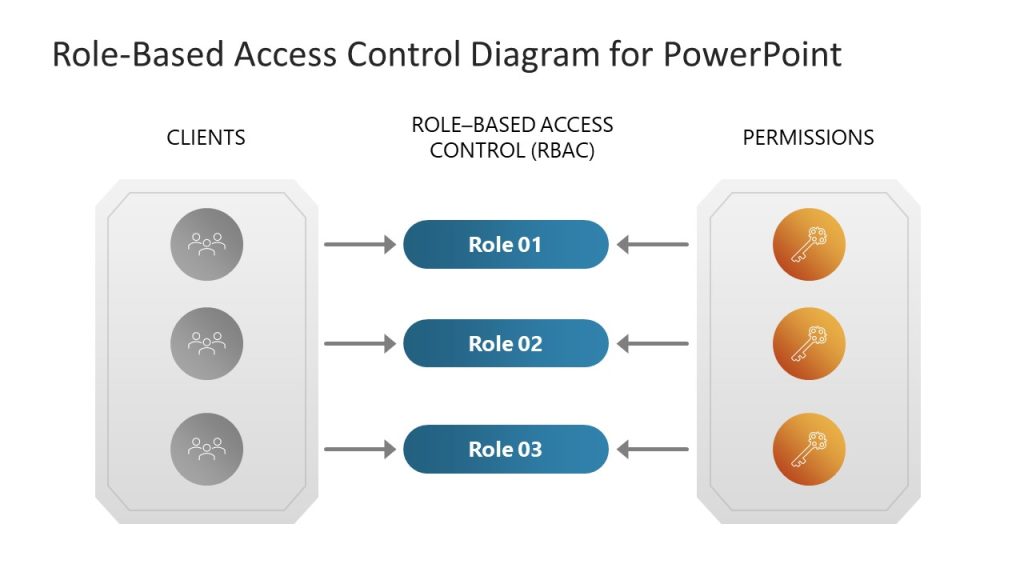
Role-basedaccesscontrolis a mechanism where you allow users toaccesscertain resourcesbasedon permissions defined for the roles they are assigned to.
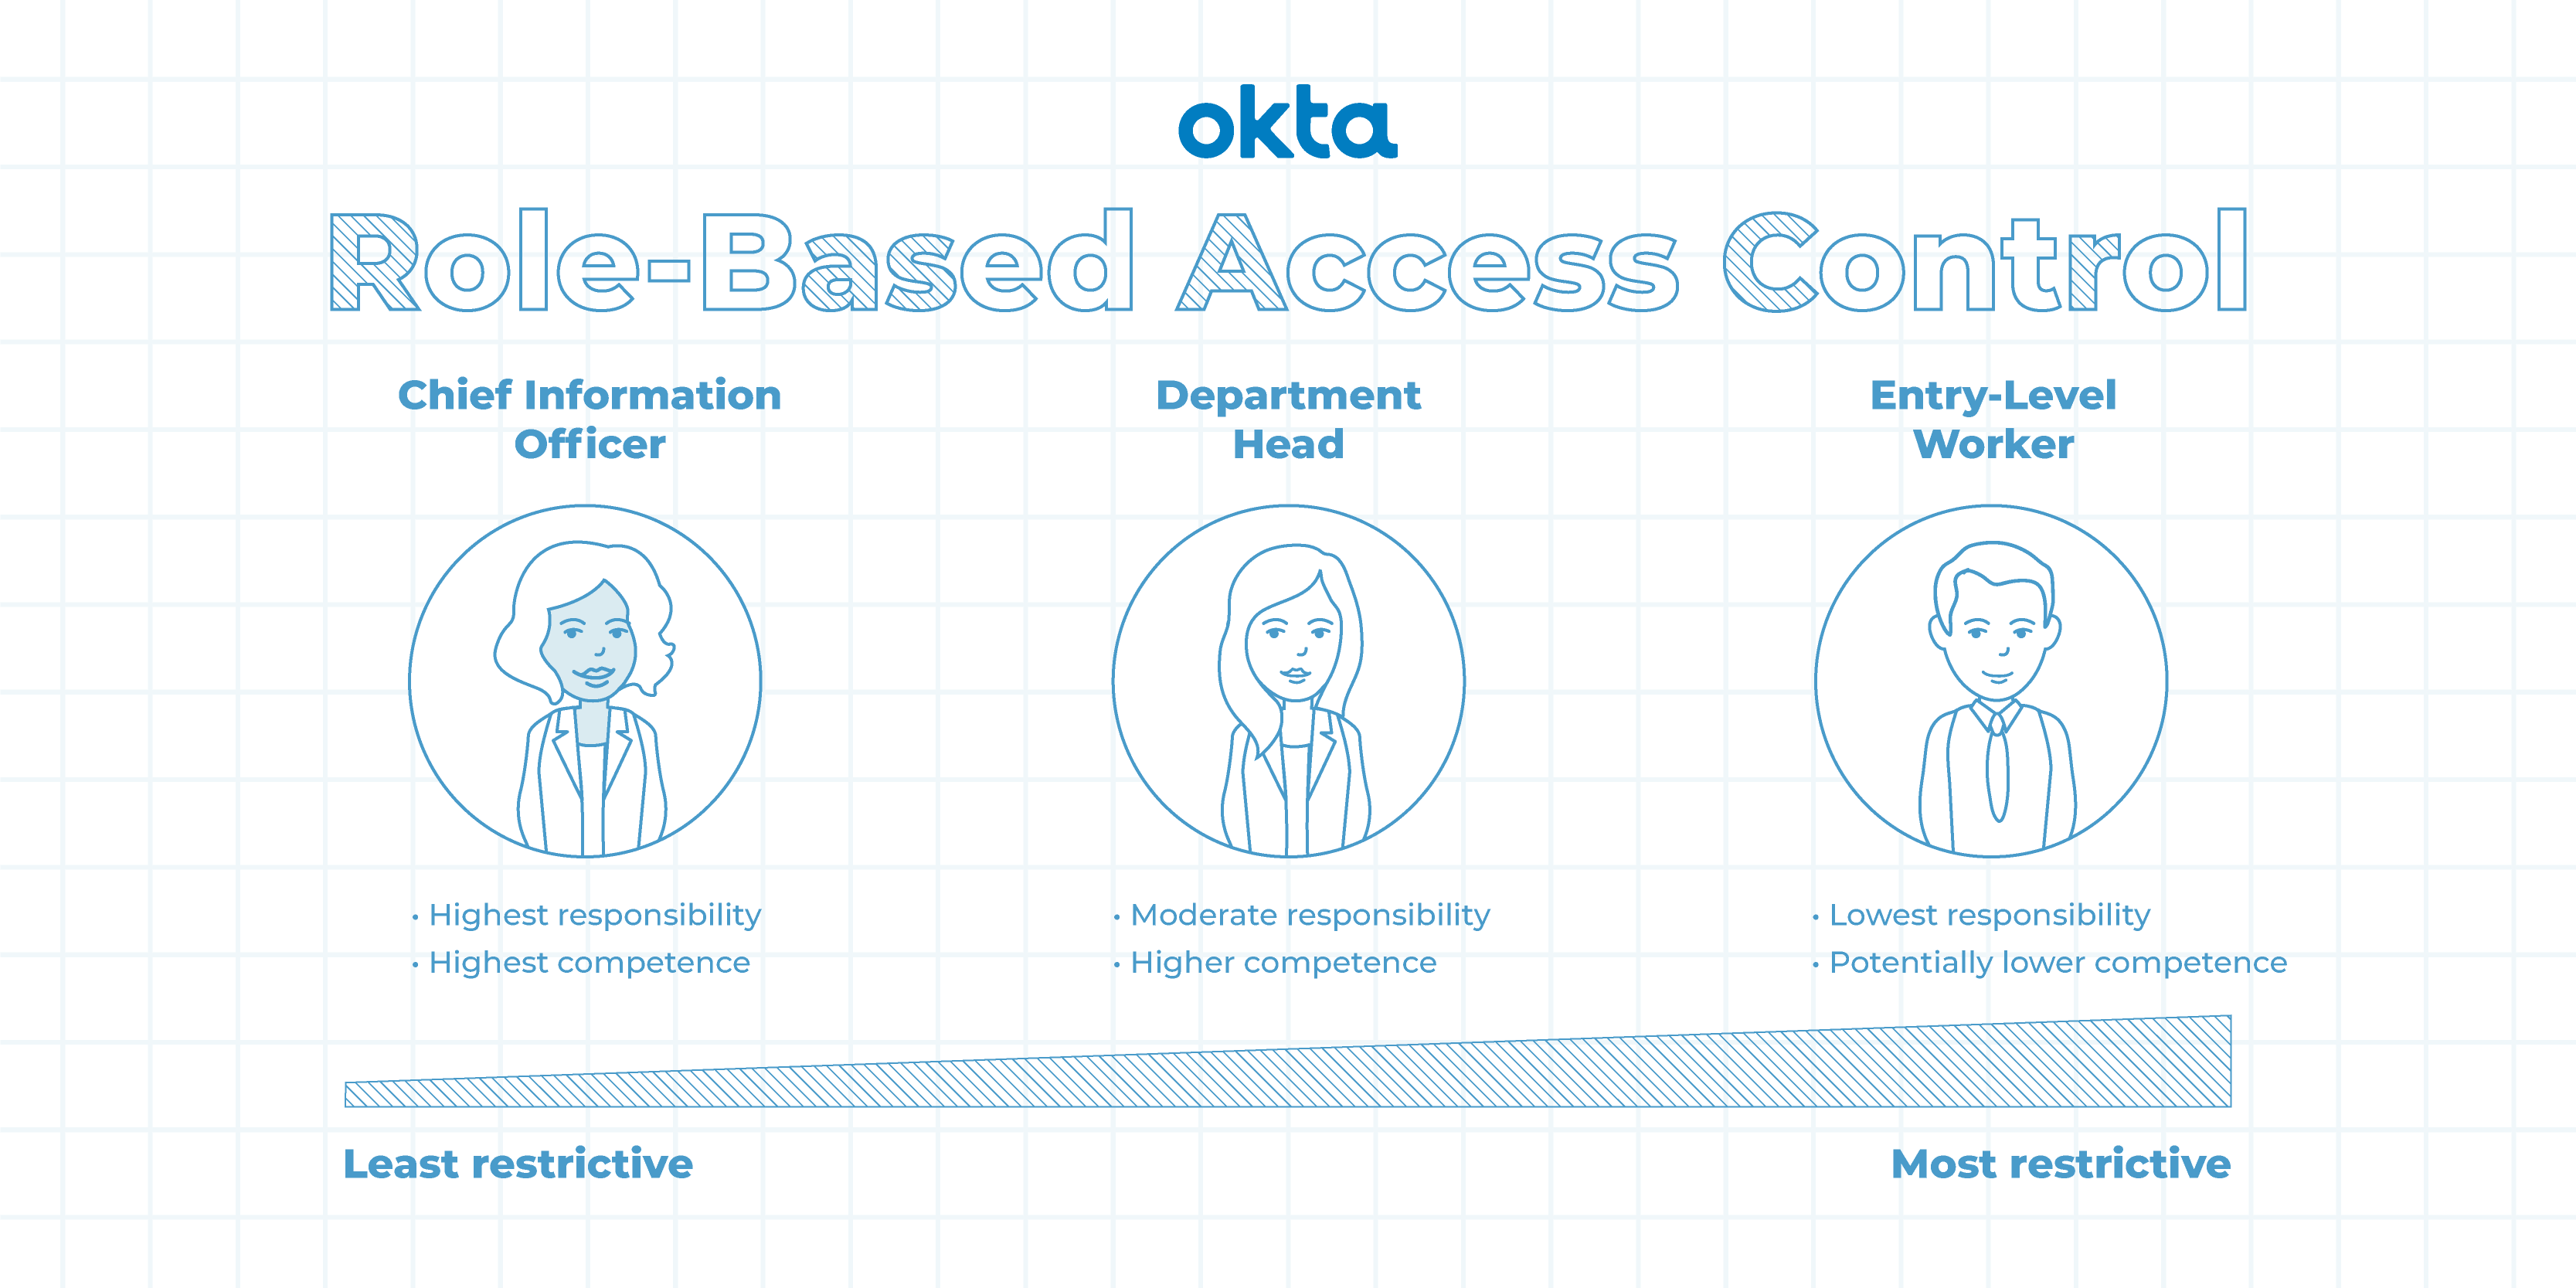
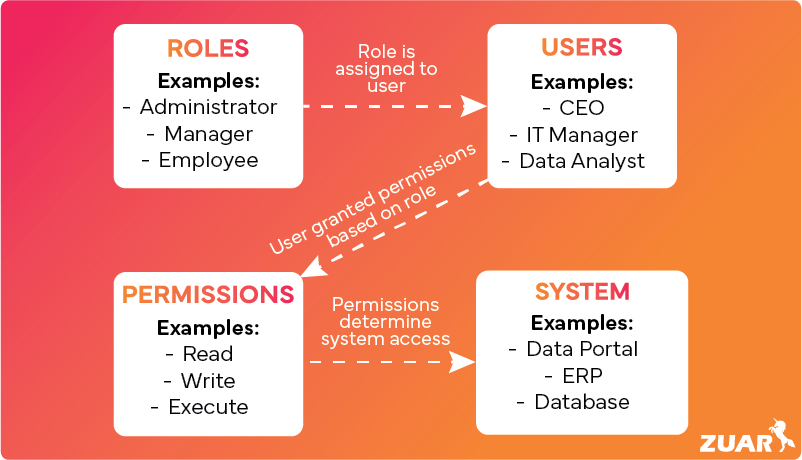
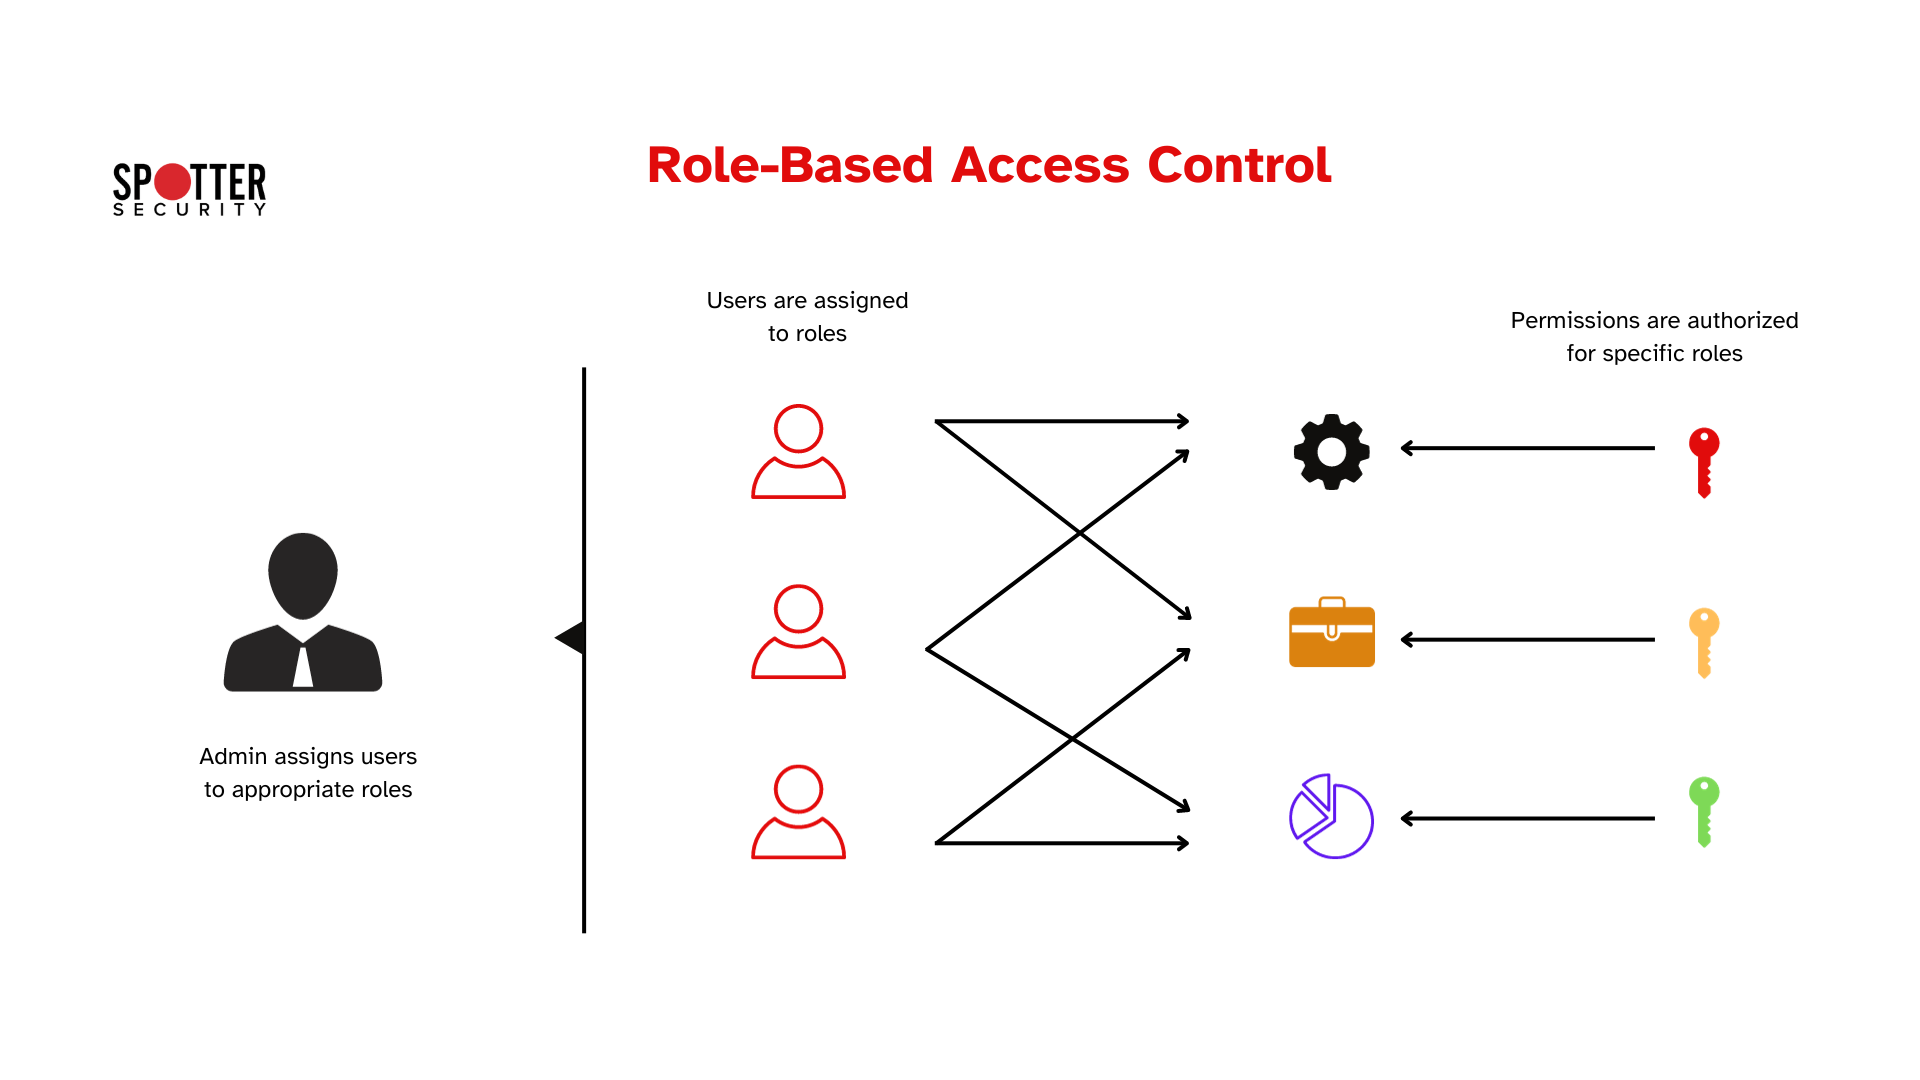
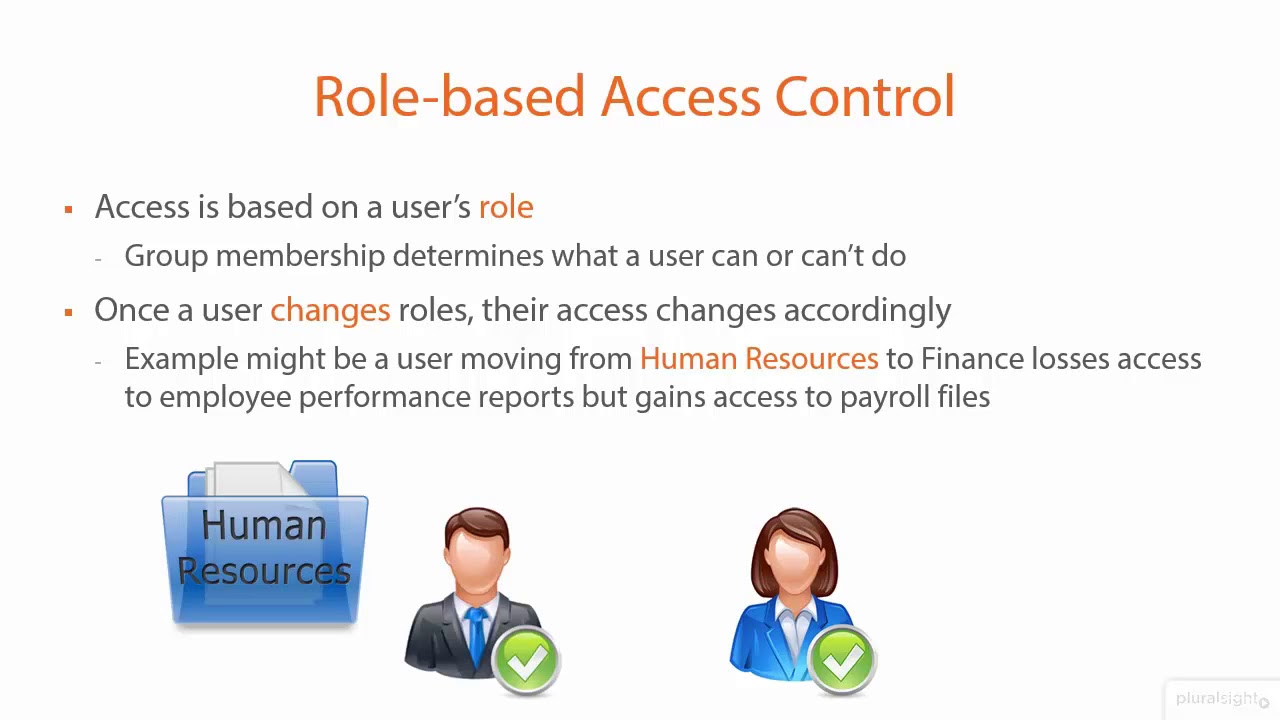
What Is Role-BasedAccessControl? Role-basedaccesscontrolis a security model that grantsaccessbasedon a user’s role — not on who they are as a person. Instead of giving each user a custom set of rights, you create roles (like Admin, Editor, or Viewer), assign rights to those roles, and then add users to the roles they need.
Role-basedaccesscontrol(RBAC), also known asrole-basedsecurity, is a mechanism that restricts systemaccess. It involves setting permissions and privileges to enableaccessto authorized users.

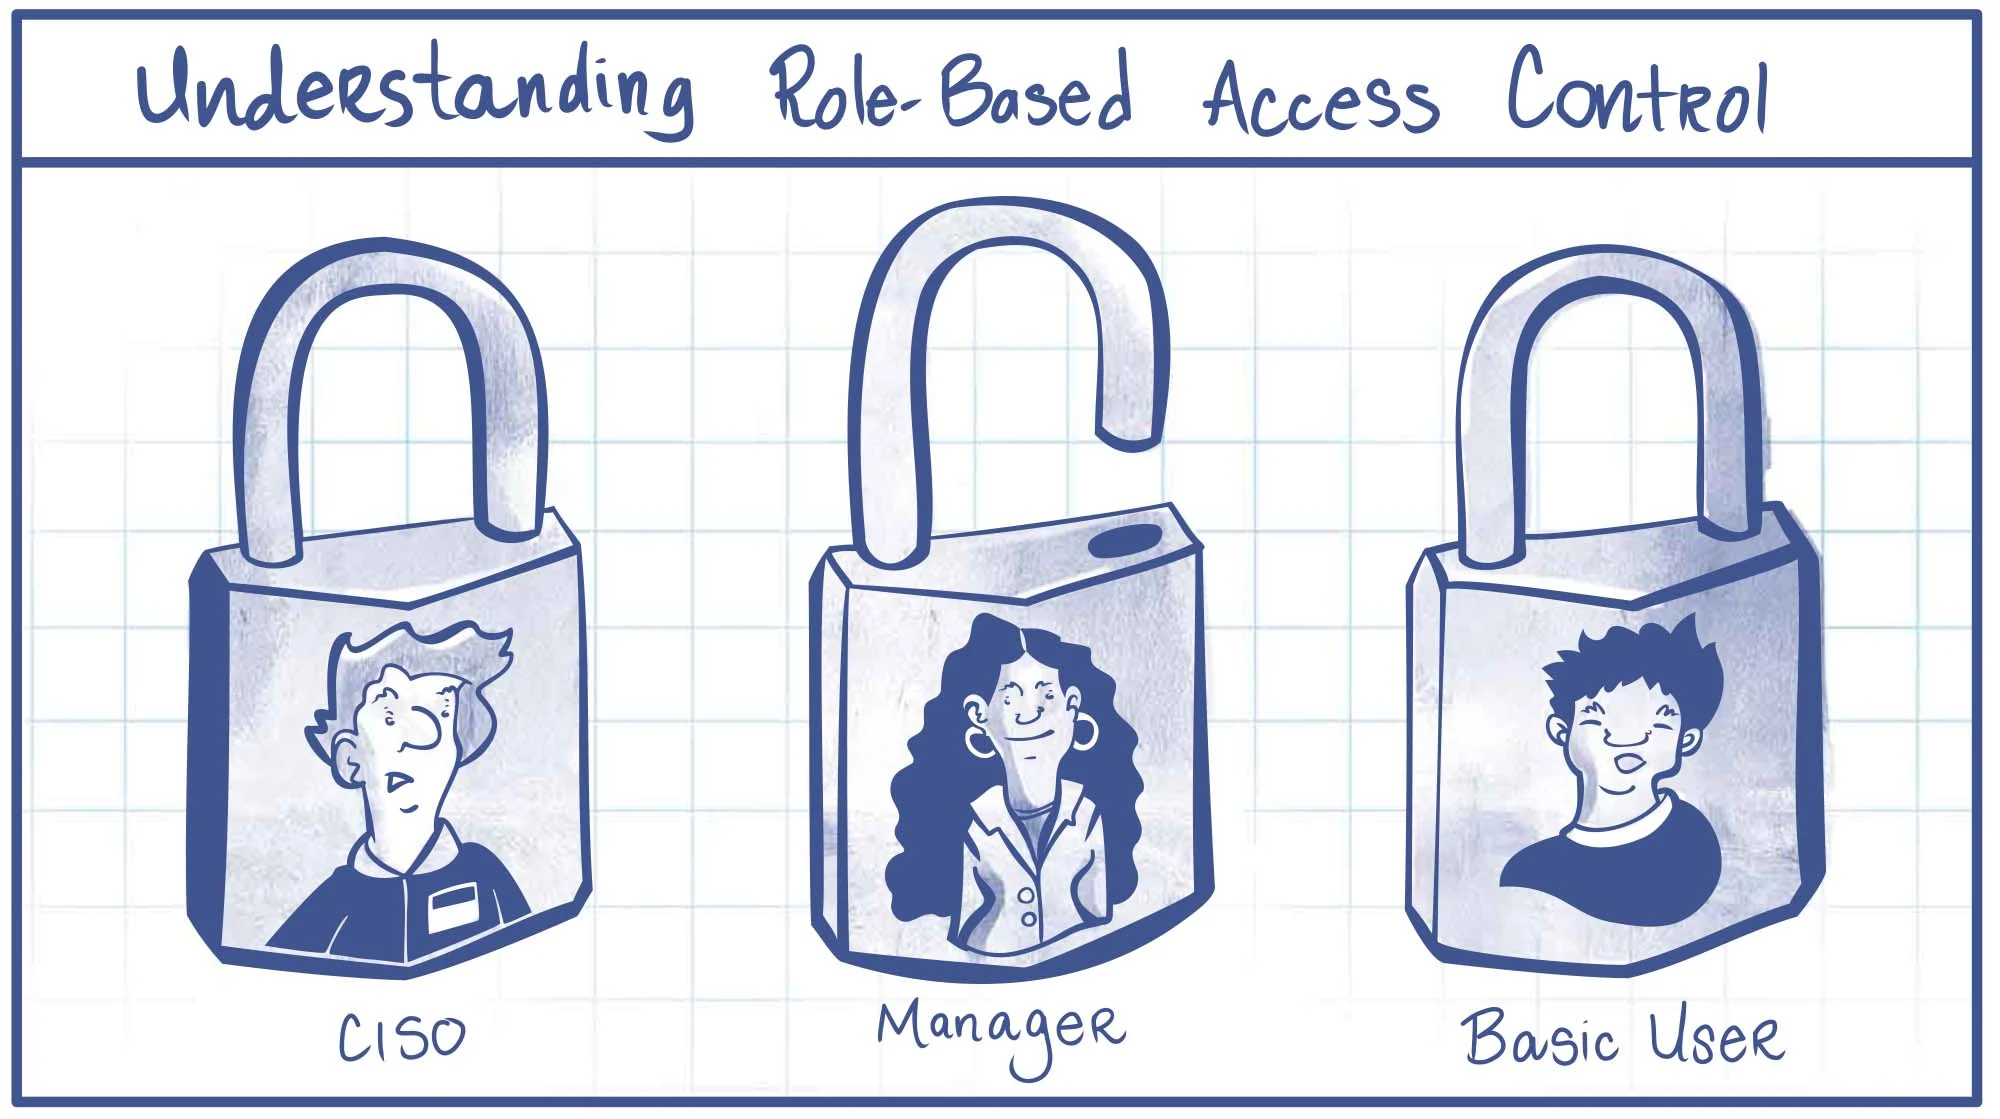
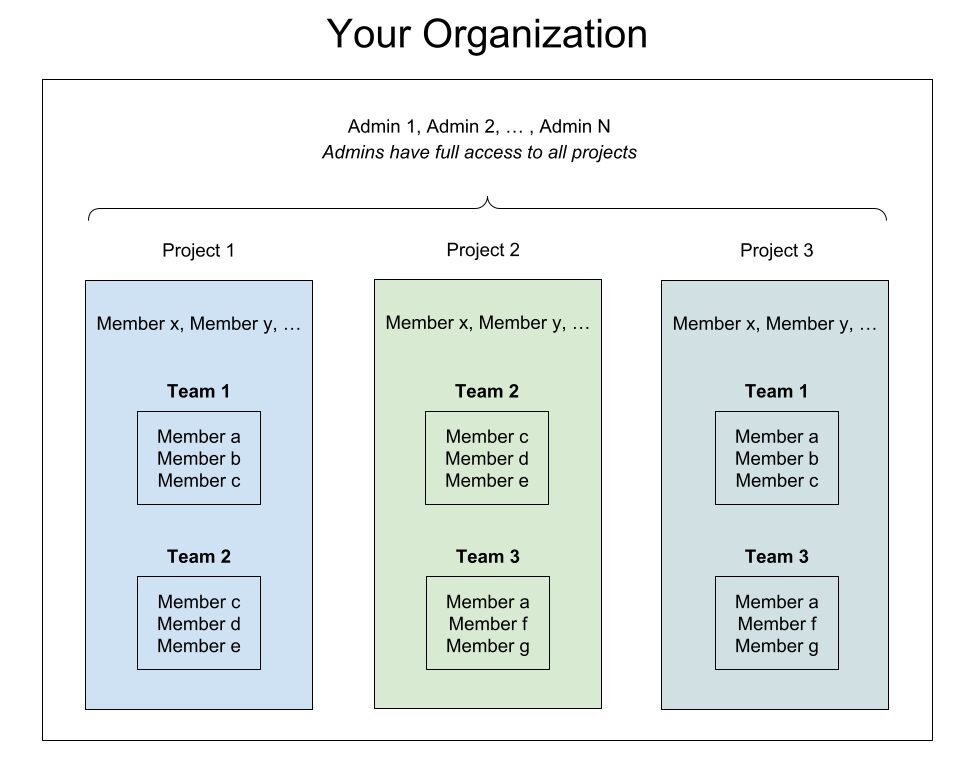
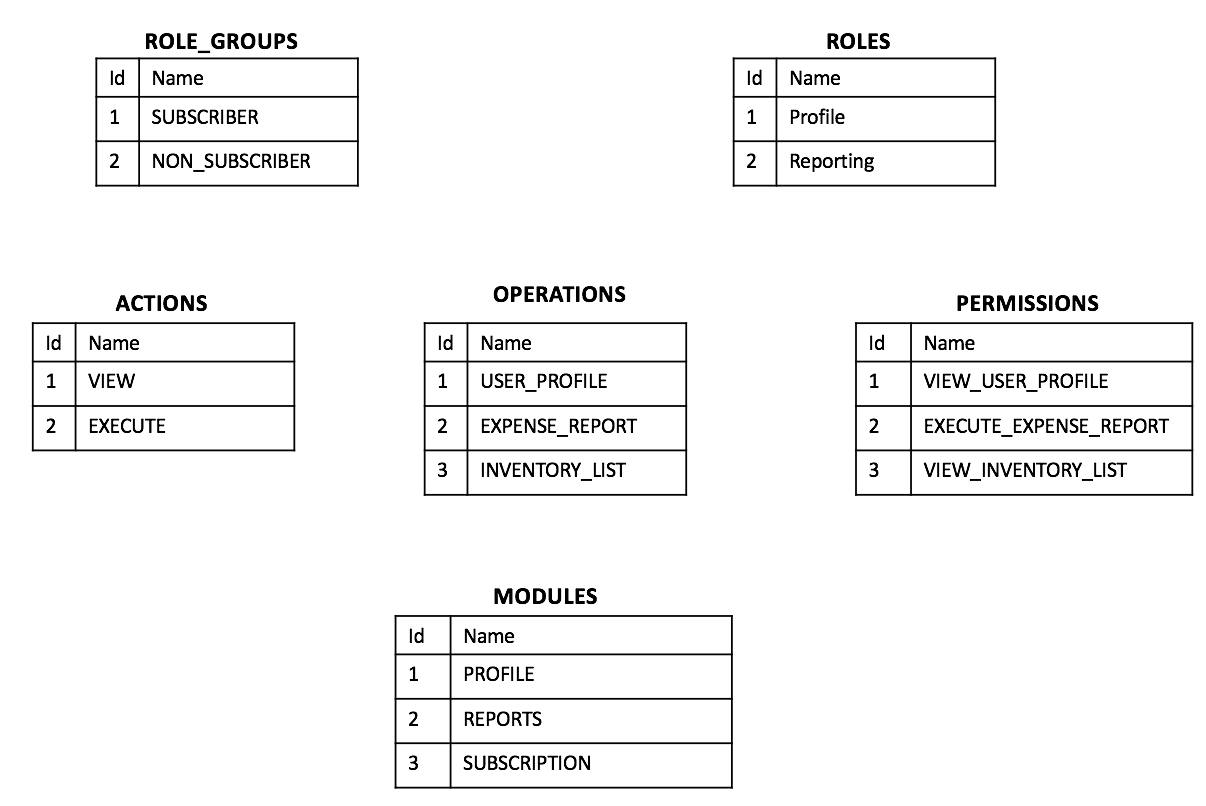
As we can see from the illustration, Role-Based Access Controls has many fascinating aspects to explore.
Role-basedaccesscontrol(RBAC) is a method forcontrollingwhat users are able to do within a company's IT systems.RBACaccomplishes this by assigning one or more "roles" to each user, and giving each role different permissions.