In the realm of Windows security, the term "null user" might sound mysterious, but it's a crucial concept to understand. It's not a user account in the traditional sense, but rather a special system account that plays a significant role in Windows' security architecture. Let's delve into the context of Windows security to unravel the enigma of the null user.
Understanding the Null User in Windows
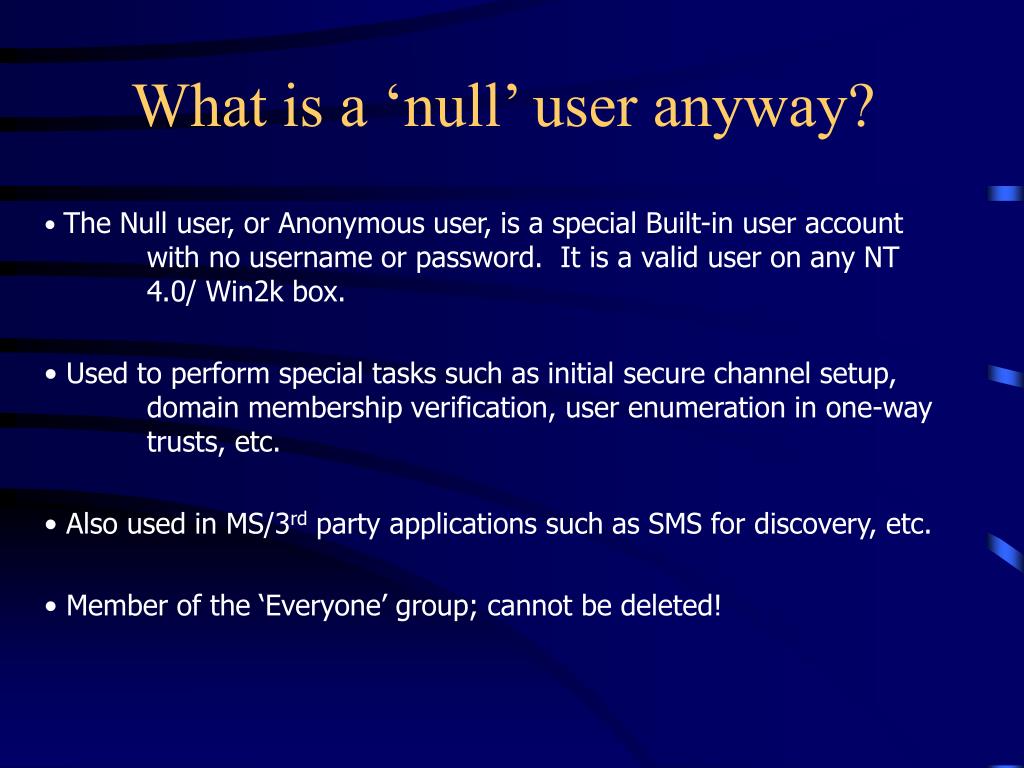
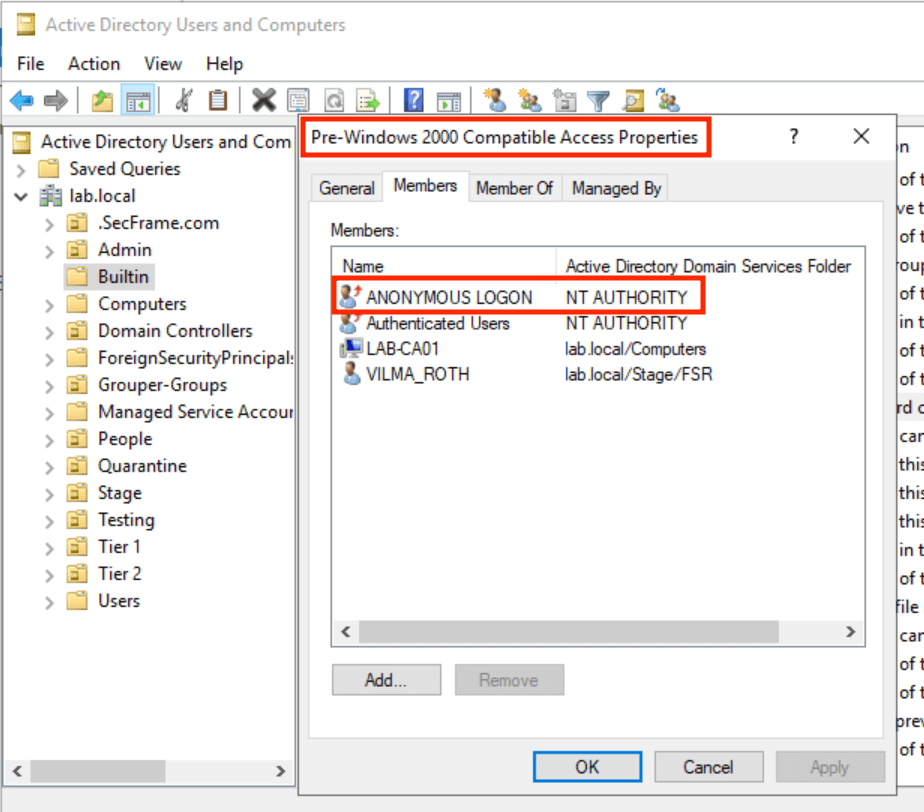
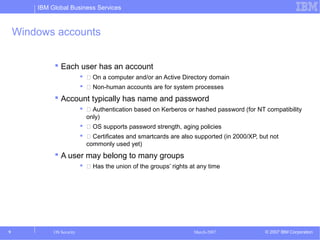
The null user, also known as the anonymous user or the guest user, is a built-in user account in Windows. It's not associated with any specific user or group, and it has minimal privileges. The null user is represented by the SID (Security Identifier) S-1-5-18, which is often used in security-related discussions.
Why Does the Null User Exist?
The null user serves a unique purpose in Windows security. It's used in scenarios where no user context is available, such as when a service is running or when a user is not logged in. Here are a few key reasons for its existence:
- Service Accounts: Many Windows services run under the null user context. This is a security measure to limit the damage if a service is compromised.
- Network Access: The null user is used when accessing network resources without user credentials, such as when browsing shared folders on a network.
- Security Auditing: The null user is often used in security auditing to track system-level activities that don't involve a specific user.
Null User and Security Implications
The null user, despite its limited privileges, plays a significant role in Windows security. Understanding its behavior can help in troubleshooting security issues and configuring security settings.
Null User and UAC
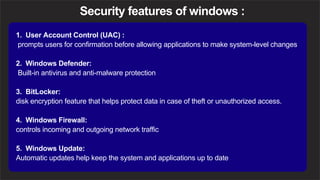
One of the most notable interactions of the null user is with User Account Control (UAC). When a process running as the null user attempts to perform an action that requires higher privileges, UAC prompts for elevation. This is a key security feature that helps prevent unauthorized access.
Null User and Network Access
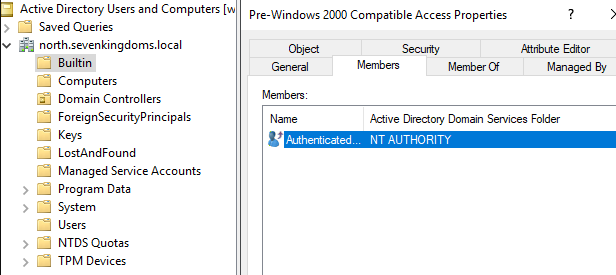
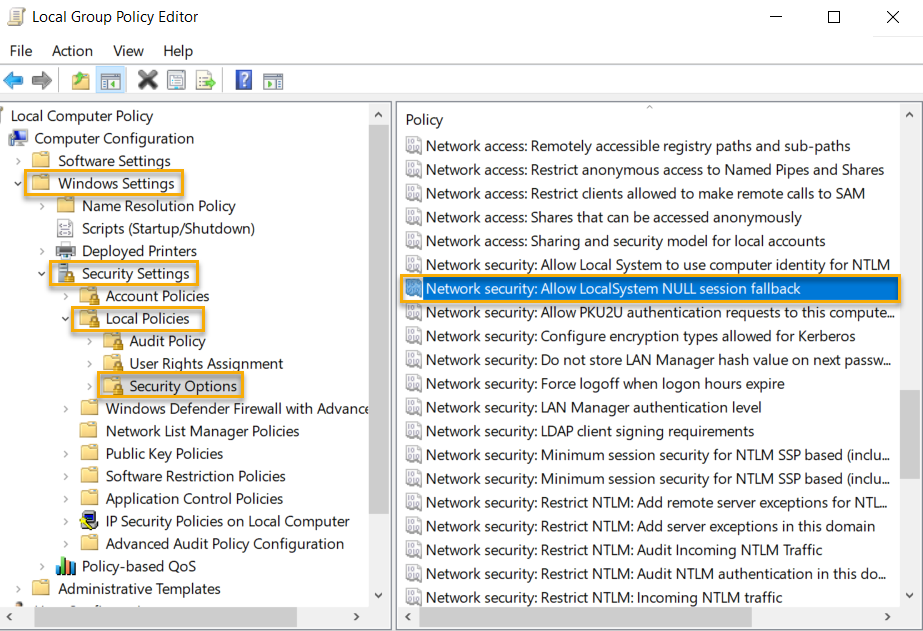
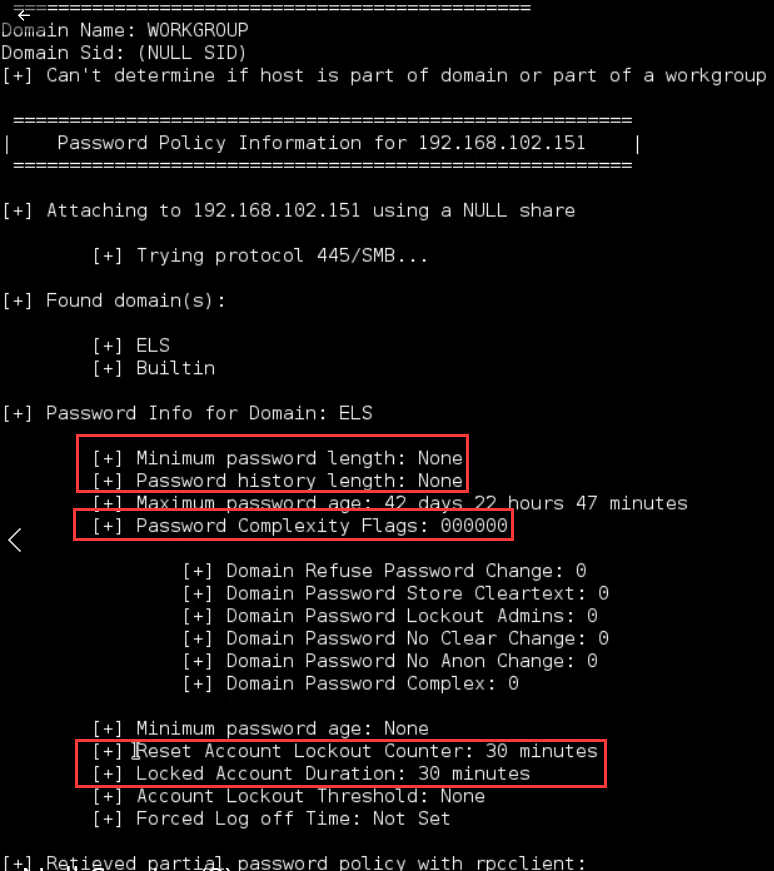
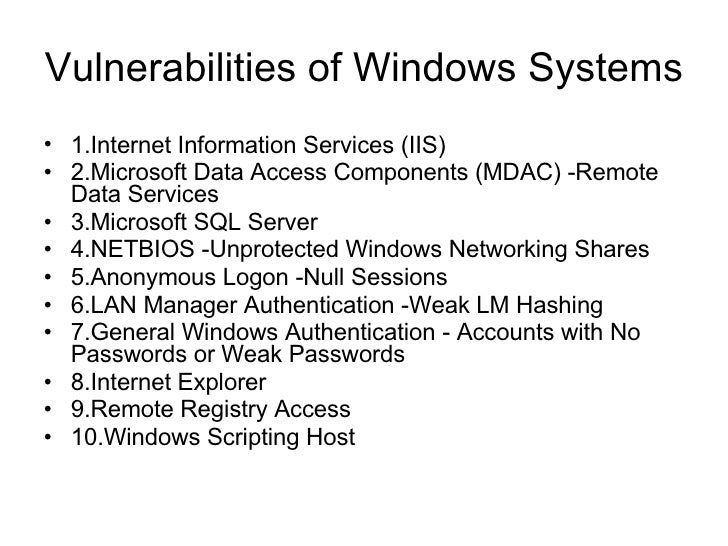
When accessing network resources, Windows first attempts to use the credentials of the logged-in user. If that fails, it falls back to using the null user. This can sometimes lead to unexpected access denials or permissions errors, as the null user has limited network access rights.

Managing the Null User in Windows
While the null user is a system-level account and can't be deleted or modified like regular user accounts, understanding its behavior can help in managing Windows security.
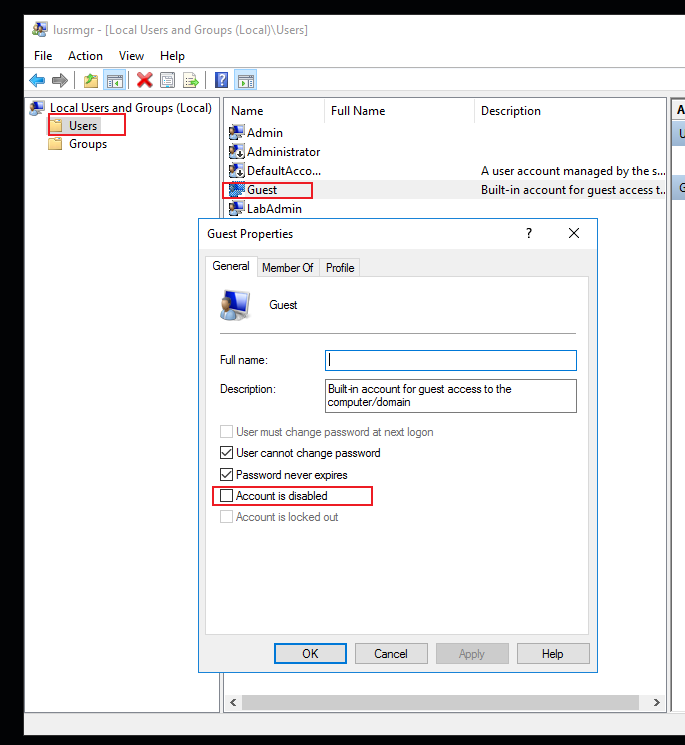
Disabling the Guest Account
In older versions of Windows, the null user was represented by the Guest account. While this account is disabled by default in modern Windows versions, it's a good practice to ensure it remains disabled to prevent unauthorized access.
Monitoring Null User Activity
Monitoring activities performed under the null user can provide valuable insights into system-level activities and potential security threats. Tools like the Windows Event Log and third-party security software can help in this regard.
In the context of Windows security, the null user is a critical yet often overlooked component. Understanding its role and behavior can significantly enhance your security knowledge and help you make informed decisions when managing Windows systems.