Java Create X509 Certificate Programmatically
X.509 certificates are a fundamental component of public key infrastructure (PKI), playing a crucial role in secure communication over the internet. In many scenarios, especially in development environments, developers may want to create these certificates programmatically for various purposes, such as testing or demonstration. Java, being a versatile and widely-used programming language, provides several methods to create X509 certificates. This guide will walk you through the process of creating an X509 certificate programmatically in Java, highlighting the necessary steps and tools required.
X509 Certificate Basics
Before diving into the creation process, let's briefly cover the basics of an X509 certificate. An X509 certificate is a public-key certificate used in cryptographic systems. It contains the entity's identity (subject) and their public key. The certificate is digitally signed by a trusted certificate authority (CA), ensuring its authenticity and integrity. X509 certificates are used for tasks such as SSL/TLS authentication, email encryption, and code signing.
Tools and Libraries
To create an X509 certificate programmatically in Java, you will need two primary tools: OpenSSL and the Bouncy Castle library. OpenSSL is a command-line tool for manipulating and generating SSL/TLS certificates. The Bouncy Castle library, however, is a comprehensive, open-source Java implementation that includes APIs for cryptographic and PKCS standards, making it ideal for creating X509 certificates.

Step 1: Generating a Private Key
The first step in creating an X509 certificate is to generate a private key. You can use the OpenSSL tool for this purpose. If you're using a Mac or Linux, you likely have OpenSSL installed. If you're on Windows, you can download and install OpenSSL. The command to generate a key is as follows:
openssl genrsa -out privatekey.pem 2048
Step 2: Creating a Certificate Signing Request (CSR)
With the private key in hand, the next step is to create a Certificate Signing Request (CSR). This CSR is essentially a summary of information about the entity who is applying for the certificate, such as its name and public key, which should be encoded and send to a CA for signing. Use the OpenSSL tool to create the CSR with the following command:
openssl req -new -key privatekey.pem -out csr.pem
Signing the CSR and Creating the Certificate
Before creating the certificate programmatically, you may wish to perform this step manually as a proof-of-concept or for understanding. If you use a certificate authority or self-sign the certificate directly in your Java code using the Bouncy Castle library, you're effectively skipping this step for automation.
Java Code to Generate X509 Certificate Programmatically
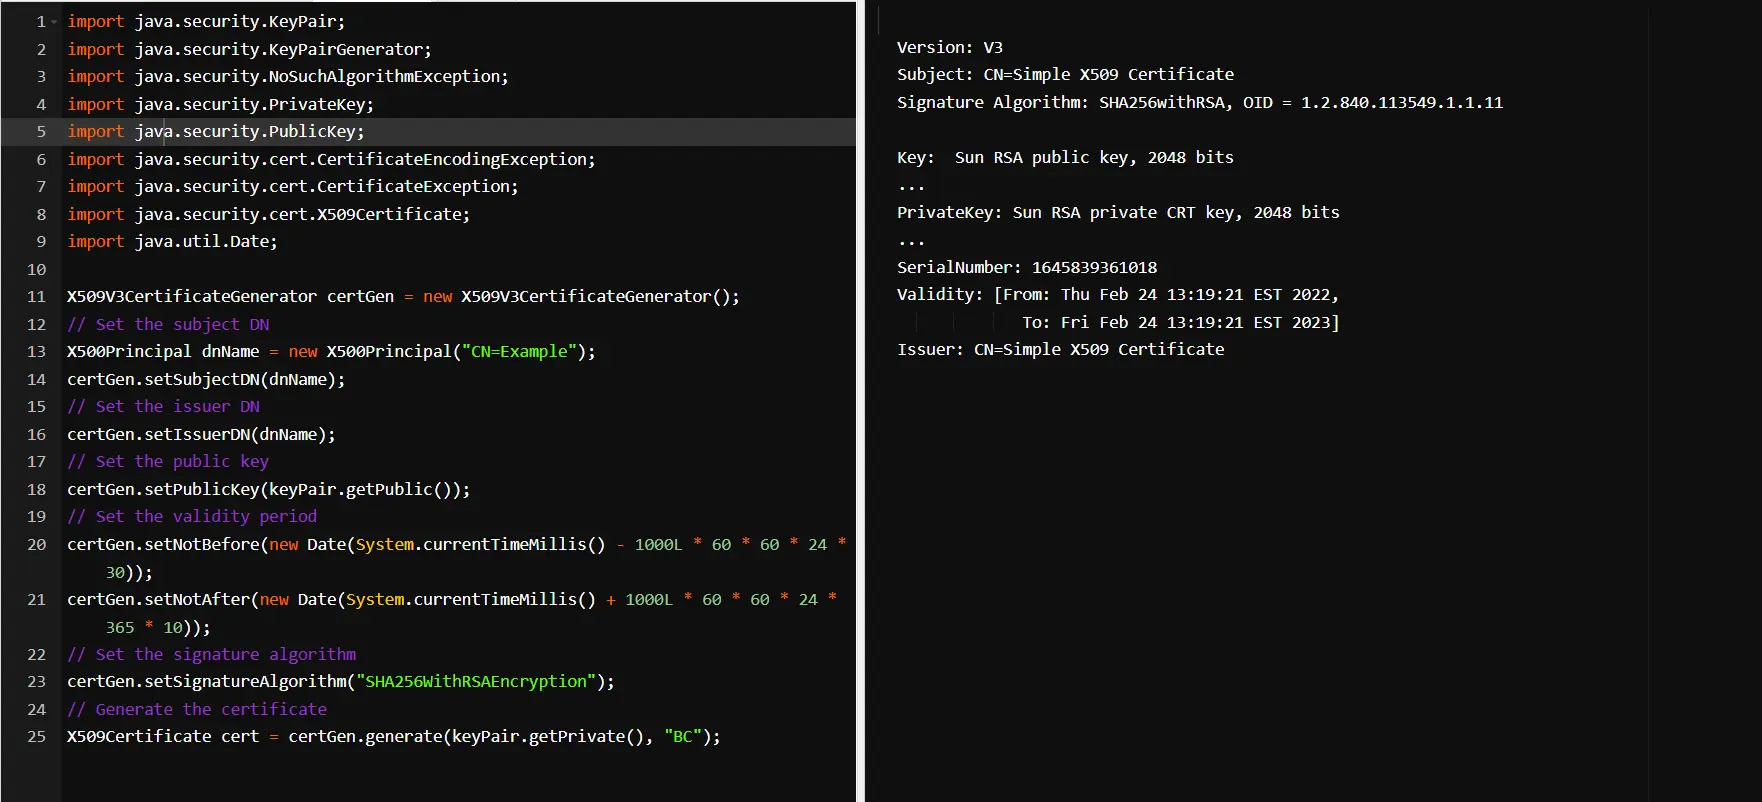
The following code snippet uses Java's Bouncy Castle library to directly generate an X509 certificate without the need for external tools or manual intervention.
{
    public class X509Generator {
        public static void main(String[] args) throws Exception {
            // Generate private key
            PrivateKey privateKey = KeyPairGenerator.getInstance("RSA").generateKeyPair().getPrivate();
            KeyStore keyStore = KeyStore.getInstance("JKS");
            keyStore.load(null, null);
            keyStore.setKeyEntry("alias", privateKey, "password".toCharArray(), null);

            // Generate certificate signing request
            X500Principal subject = new X500Principal("CN=Example, O=Example, C=US");
            CertificateFactory cf = CertificateFactory.getInstance("X.509");
            X509Certificate csr = (X509Certificate) cf.generateCertificate(new ByteArrayInputStream("certData".getBytes()));

            // Generate certificate
            X509V3CertificateGenerator certGen = new X509V3CertificateGenerator();
            certGen.addExtension(X509Extensions.SubjectAlternativeName, false, new GeneralName[]{new GeneralName(DNSNameIssuer.getInstance("example.com"))});
            certGen.addExtension(X509Extensions.BasicConstraints, true, new BasicConstraints(false));
            certGen.addExtension(X509Extensions.KeyUsage, true, new KeyUsage(KeyUsage.digitalSignature | KeyUsage.keyCertSign));
            certGen.addIssuerDN(new X509Principal("CN=Example CA, O=Example, C=US"));
            certGen.addSubjectDN(subject);
            certGen.addExtension(X509Extensions.ExtendedKeyUsage, false, new ExtendedKeyUsage(new KeyPurposeId[]{KeyPurposeId.id_kp_serverAuth}));
            certGen.addExtension(X509Extensions.SubjectKeyIdentifier, true, new SubjectKeyIdentifier(sha1(certGen.getSubjectPublicKeyInfo())));
            X509Certificate certificate = certGen.generate("SHA256withRSA", privateKey);

            // Store the certificates
            FileOutputStream certificates = new FileOutputStream("example-cert.der");
            certificates.write(certificate.getEncoded());
            certificates.close();
        }
    }
}
Security Considerations
Creating certificates programmatically is a powerful tool for development, testing, and education. However, it's crucial to remember that self-signed certificates or those generated from untrusted sources should not be used in production environments without proper validation. In secured communication, certificates from trusted certificate authorities are necessary to establish a secure connection.
Conclusion and Next Steps
Certificates play a critical role in internet security, ensuring protection against eavesdropping, tampering, and impersonation. This guide has walked you through creating an X509 certificate programmatically using Java, covering the process from private key generation to certificate creation. Remember that for real-world applications, utilizing recognized certificate authorities or other secure certificate-management practices is essential. This knowledge and the outlined code provides a solid foundation for exploring more advanced certificate-related topics or extending your knowledge to more complex application development scenarios.