Capital One Lawsuit 2020: A Deep Dive into the Data Breach and Its Impact
The year 2020 marked a significant event in the cybersecurity landscape with the Capital One lawsuit, stemming from a massive data breach that exposed the personal information of over 100 million customers. This article delves into the details of the Capital One lawsuit, the data breach that preceded it, and the subsequent impact on the financial institution and its customers.
The Capital One Data Breach: An Overview
In July 2019, Capital One, one of the largest banks in the United States, suffered a significant data breach. The breach, which went undetected for several months, exposed sensitive customer data, including names, addresses, phone numbers, and credit card data. The breach affected approximately 106 million individuals in the United States and 6 million in Canada.
The Mastermind Behind the Breach
The mastermind behind the Capital One data breach was identified as Paige Thompson, a former Amazon Web Services (AWS) software engineer. Thompson, who went by the online alias "erratic," exploited a misconfiguration in Capital One's AWS cloud storage to access the sensitive data.

The Capital One Lawsuit: Charges and Arrest
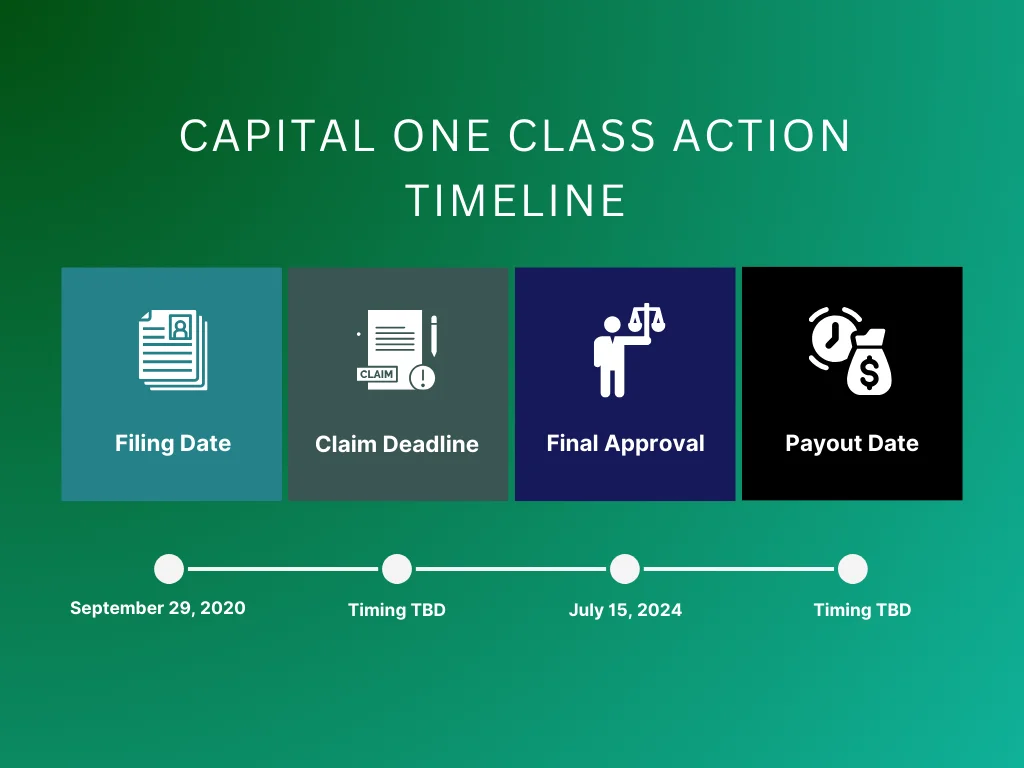
Following the discovery of the breach, Capital One filed a lawsuit against Thompson in August 2019. Thompson was arrested and charged with computer fraud and abuse. The charges carried a maximum penalty of five years in prison and a $250,000 fine. In addition to the criminal charges, Capital One also pursued a civil lawsuit against Thompson to recover damages.
Impact on Capital One and Its Customers
The Capital One data breach and subsequent lawsuit had significant implications for the financial institution and its customers. Capital One faced potential financial losses due to the breach, including the cost of notifying customers, providing credit monitoring services, and addressing potential fraud. The breach also damaged Capital One's reputation, leading to a drop in its stock price and a loss of customer trust.
For customers, the breach posed a significant risk of identity theft and financial fraud. Although Capital One offered free credit monitoring services to affected customers, the breach highlighted the importance of vigilance in protecting personal information. In the wake of the breach, many customers took steps to protect their credit, such as freezing their credit reports and monitoring their credit card statements for unusual activity.

The Role of Cloud Security in the Capital One Breach
The Capital One data breach raised important questions about the security of cloud-based storage systems. Although cloud storage offers numerous benefits, such as scalability and cost savings, it also presents unique security challenges. In the case of Capital One, a misconfiguration in the bank's AWS cloud storage allowed Thompson to access sensitive customer data.
In response to the breach, Capital One and other financial institutions have taken steps to enhance their cloud security. These measures include investing in advanced threat detection systems, conducting regular security audits, and implementing strict access controls for cloud storage.
Lessons Learned from the Capital One Lawsuit
The Capital One lawsuit and data breach offer valuable lessons for businesses and individuals alike. For businesses, the breach underscores the importance of robust cybersecurity measures, including regular security audits, strict access controls, and employee training. For individuals, the breach highlights the importance of vigilance in protecting personal information and the need to take proactive steps to prevent identity theft and financial fraud.
In the ever-evolving landscape of cybersecurity, the Capital One lawsuit serves as a stark reminder of the potential consequences of inadequate security measures. As businesses increasingly rely on cloud-based storage and other digital technologies, it is crucial to prioritize cybersecurity and stay vigilant against emerging threats.