Essential vulnerability management policies

Discover a structured, four-step roadmap to identify, assess, and remediate risks through essential vulnerability management policies that strengthen your security posture.
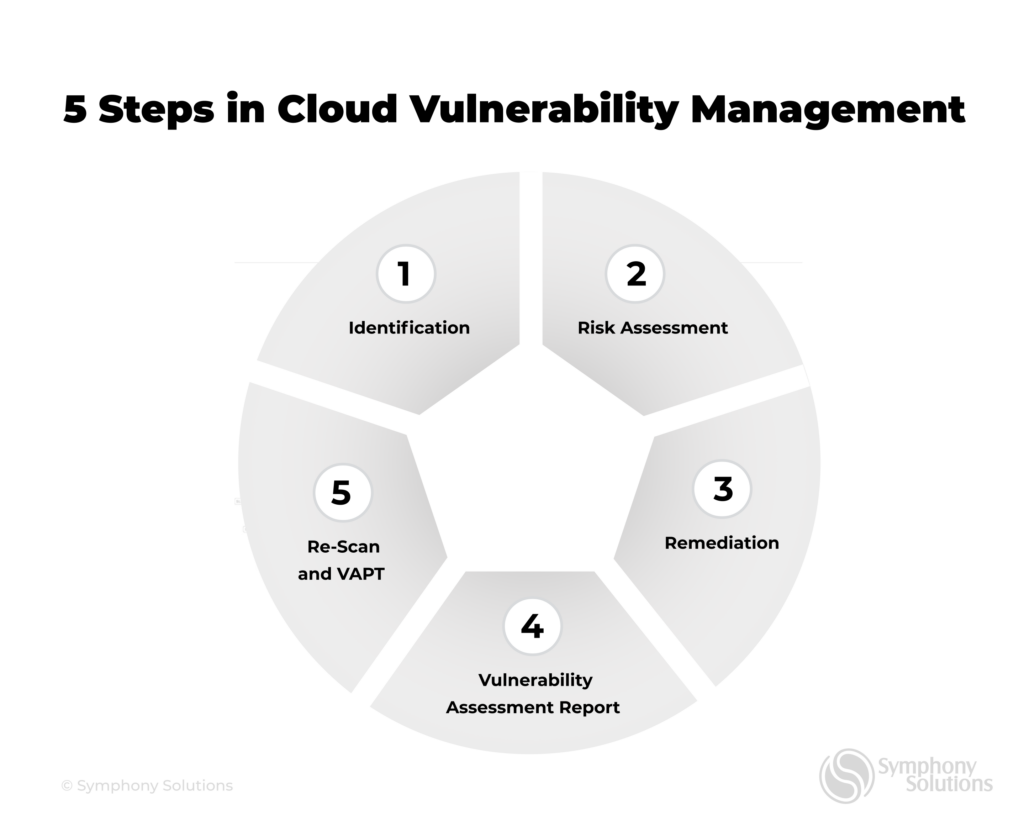
What are vulnerability management policies ? Vulnerability management policies are structured guidelines that organizations put in place to identify, evaluate, prioritize, and address security weaknesses in their systems, applications, and networks.
PDF OWASP Vulnerability Management Guide (OVMG)
During the detection cycle, we conduct the tasks that support vulnerability tests in essential ways by defining the: who, what, where, why, and how. The principal activities are focused on defining and refining the scope after each round of the tricycle, getting tools ready and verifying their integrity, conducting tests, and verifying results.
Learn about the best practices for vulnerability management and how to protect your business from cyber threats. Read our ultimate guide now.
Vulnerability Management Plan
This in-depth guide explores the essentials of a vulnerability management plan, detailing benefits, key components, best practices, and KPIs for successful, ongoing security measures.
The vulnerability management guide should help to breakdown vulnerability management process into a manageable repeatable cycles tailored to your organizational needs. Target audience: information security practitioners of all levels, IT professionals, and business leaders.

A Step
Learn what vulnerability management is, what steps are involved in the process, and how you can implement a robust vulnerability management program that leverages automation.
Learn top vulnerability management , scanning, and remediation best practices to protect your systems and reduce security risks effectively. Read today!

Vulnerability management
A vulnerability management process shouldn't exist in isolation. It is a cross-cutting effort and involves not just those working in IT operations, but also security and risk teams. Time, budget and risks should all be added to your organisation's risk register, and you may need to involve your senior leaders, particularly if different teams report to different board members.


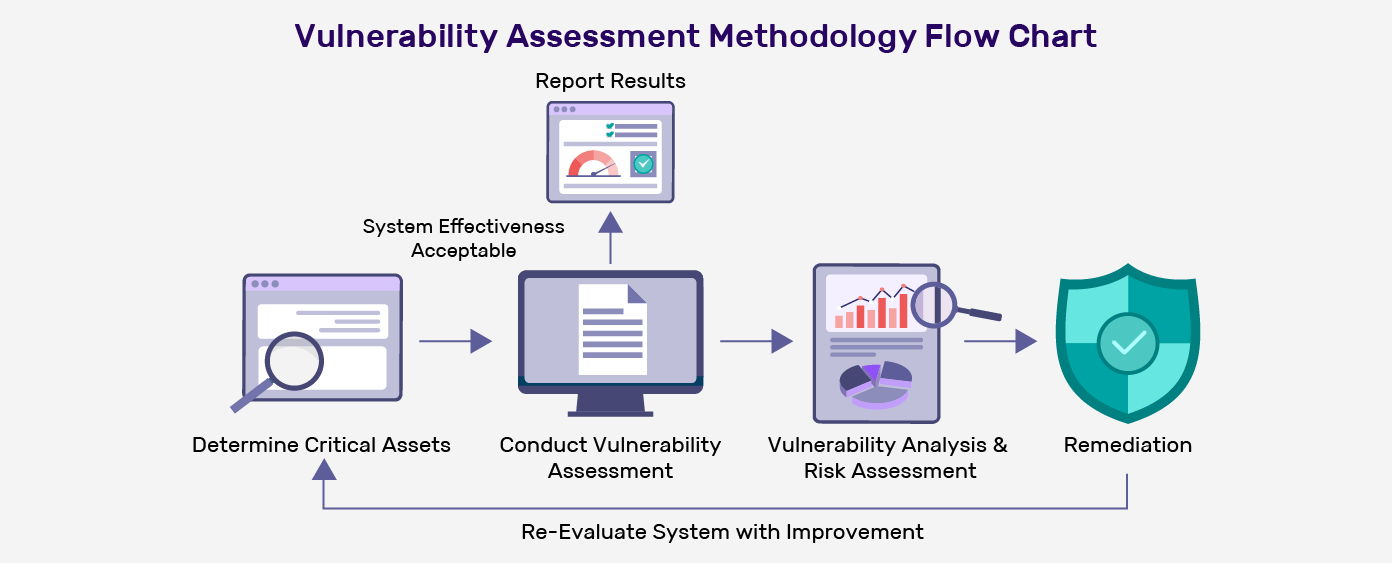


We have provided everything you need to create a vulnerability management policy for your organization. Download the template now.