PDF Secure Software Development Life Cycle
As a result, businesses started implementing more agile methods of software development , such as Scrum and Lean, which emphasized the incremental and iterative delivery of software . Nonetheless, despite this adoption of agile approaches, there was still a barrier between the development and operations teams.
Agile development emphasizes speed and flexibility, but without integrated security, software can become vulnerable to cyber threats. Many developers hesitate to incorporate security into Agile , fearing it will slow down iterations. However, Secure Software Development Life Cycle (SSDLC) ensures security without disrupting agility—especially when automated security testing and AI-driven ...
Secure Software Development Life Cycle (Secure SDLC)

In the world of Agile development , new versions and small updates are released daily for many companies, where small teams work side-by-side to improve products daily. Agile offers benefits including higher confidence by customers, the ability to make changes and fix issues immediately and in small increments, better, faster testing, and improved planning. Tech companies like Netflix, Etsy ...
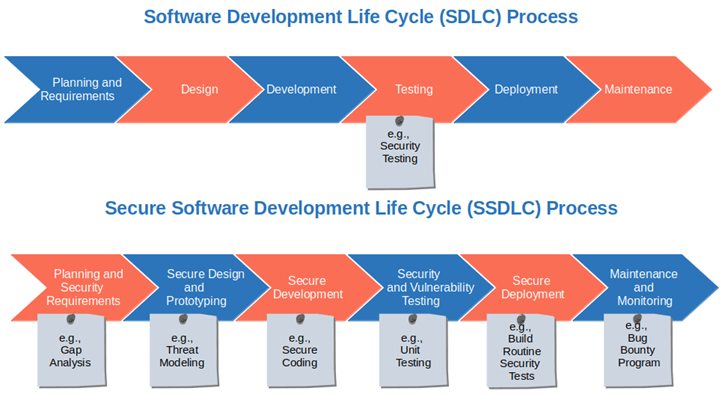
What is SSDLC? SSDLC ( Secure Software Development Life Cycle ) is a security-augmented development lifecycle . It doesn't replace SDLC — it overlays SDLC with concrete security requirements, activities, controls, and evidence so that releases are secure -by- design and secure -by-default.

Software Development Life Cycle (SDLC) in Agile Development
This comprehensive documentation serves as a guide to implementing the Agile Software Development Life Cycle , offering insights into principles, practices, roles, and tools essential for successful Agile development .
The secure software development lifecycle (SSDLC) integrates security into every phase of the software development process rather than only conducting security testing in later phases.

Secure SDLC
Learn more about Secure Software Development Lifecycle (SSDLC), and how to integrate security at every stage of the SDLC to enhance software integrity and protect against vulnerabilities.
Discover proven secure SDLC phases and best practices to protect your applications. Learn how early vulnerability detection and compliance drive success.

Secure Development for Agile Workflow
Agile SDLC: Streamlining Secure Development for Faster Delivery Discover how the secure development lifecycle (SDL) fits into Agile workflows to strengthen security while maintaining development speed. Proactive practices like risk assessments, secure coding, and penetration testing help reduce vulnerabilities, achieve compliance, and protect against threats.



Few software development life cycle (SDLC) models explicitly address software security in detail, so secure software development practices usually need to be added to each SDLC model to ensure that the software being developed is well-secured. This document recommends the Secure Software Development Framework (SSDF) - a core set of high-level secure software development practices that can be ...