Vulnerability Management WAN Architecture
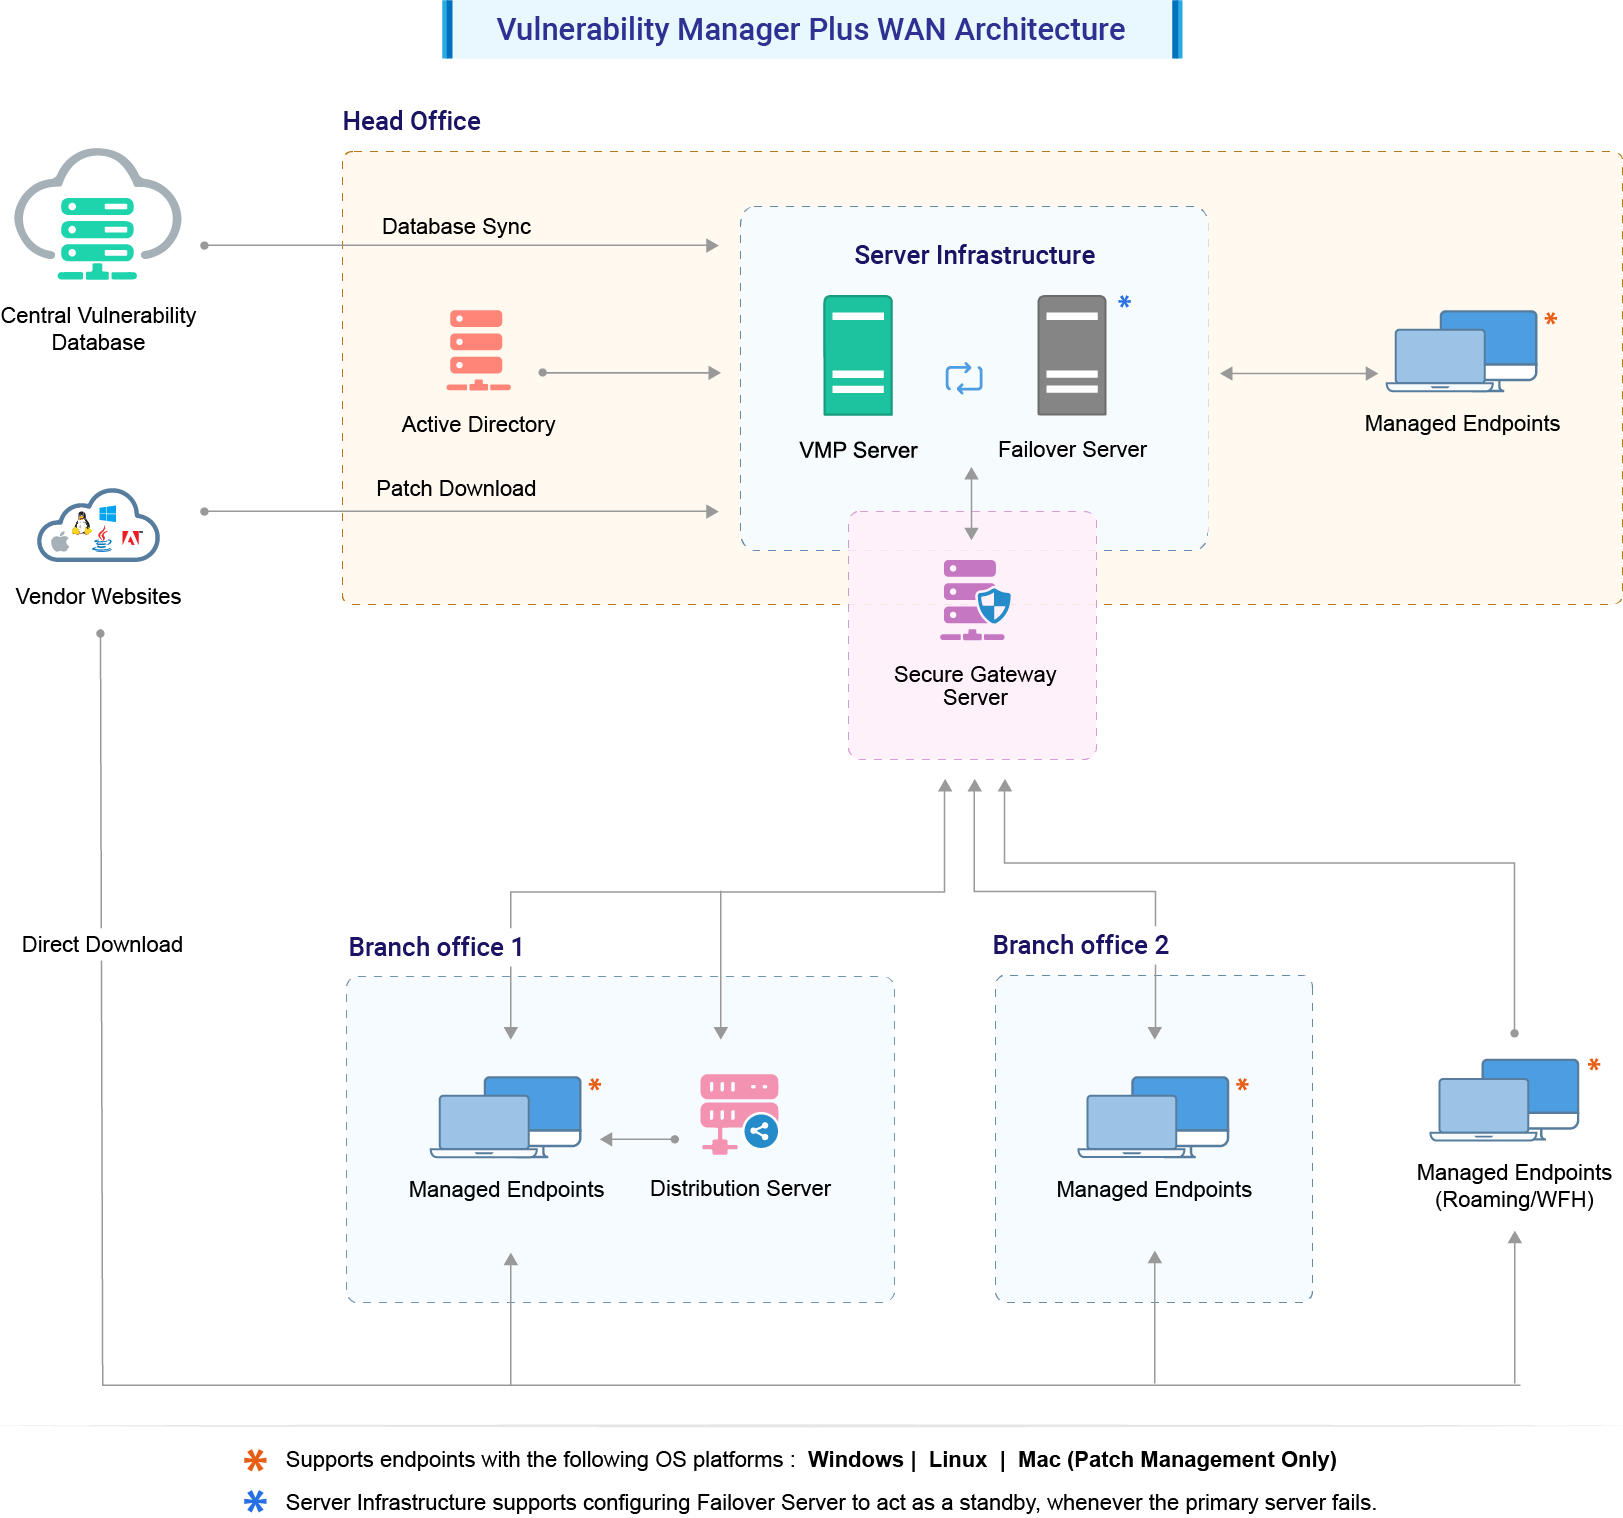
Vulnerability Management WAN Architecture ManageEngine Vulnerability Manager Plus is an Enterprise vulnerability management software that helps you scan, assess, prioritize and remediate vulnerabilities in your network endpoints. It comprises of features like vulnerability scanner and vulnerability assessment, automated patch management , security configuration management , zero-day ...

Learn how Vulnerability Manager Plus manages vulnerabilities across WAN environments using distribution servers, agents, and centralized patch management .
The CISO's Guide to SD

In this scenario, the controller vulnerability grants full visibility and control of the WAN network. This event underscores a fundamental truth in modern networking: a controller isn't just a management tool; it is the most sensitive part of the security perimeter and must be built on secure-by-design principles.
Palo Alto Networks Vulnerability Management The CISO's Guide to SD- WAN Controller Security: Why Architecture is Your Top Risk The modern Wide Area Network ( WAN ) securely connects users, devices, and applications scattered across branches, data centers, and multiple clouds.
Cisco SD
Understanding Cisco SD- WAN Architecture This video provides a solid overview of the vManage management plane and how it sits at the heart of the SD- WAN architecture , which is critical for understanding the scope of this vulnerability .
Cisco Catalyst SD- WAN architecture and control components (vManage, vSmart, vBond) Cisco Catalyst SD- WAN upgrade procedure Cisco TAC case management and admin-tech collection procedures

Comprehensive Strategies for Enhancing SD
The SD- WAN architecture in Figure 9 represents an advanced multi-site network design including comprehensive management and security mechanisms. We will go into detail on the configuration depicted below:
Implementing Secure WAN Architecture To ensure the protection of network infrastructure, implementing a secure WAN architecture is crucial. This involves designing and configuring the network in a way that minimizes vulnerabilities and maximizes security. Here are four key elements to consider when implementing a secure network architecture : 1.

Government of Canada Guideline on Vulnerability Management
Clear timelines for vulnerability remediation should be defined based on risk levels, ensuring timely mitigation of high-risk vulnerabilities and maintaining compliance with regulatory requirement. This work should be facilitated through ticketing, change management , configuration management and patch management tools.



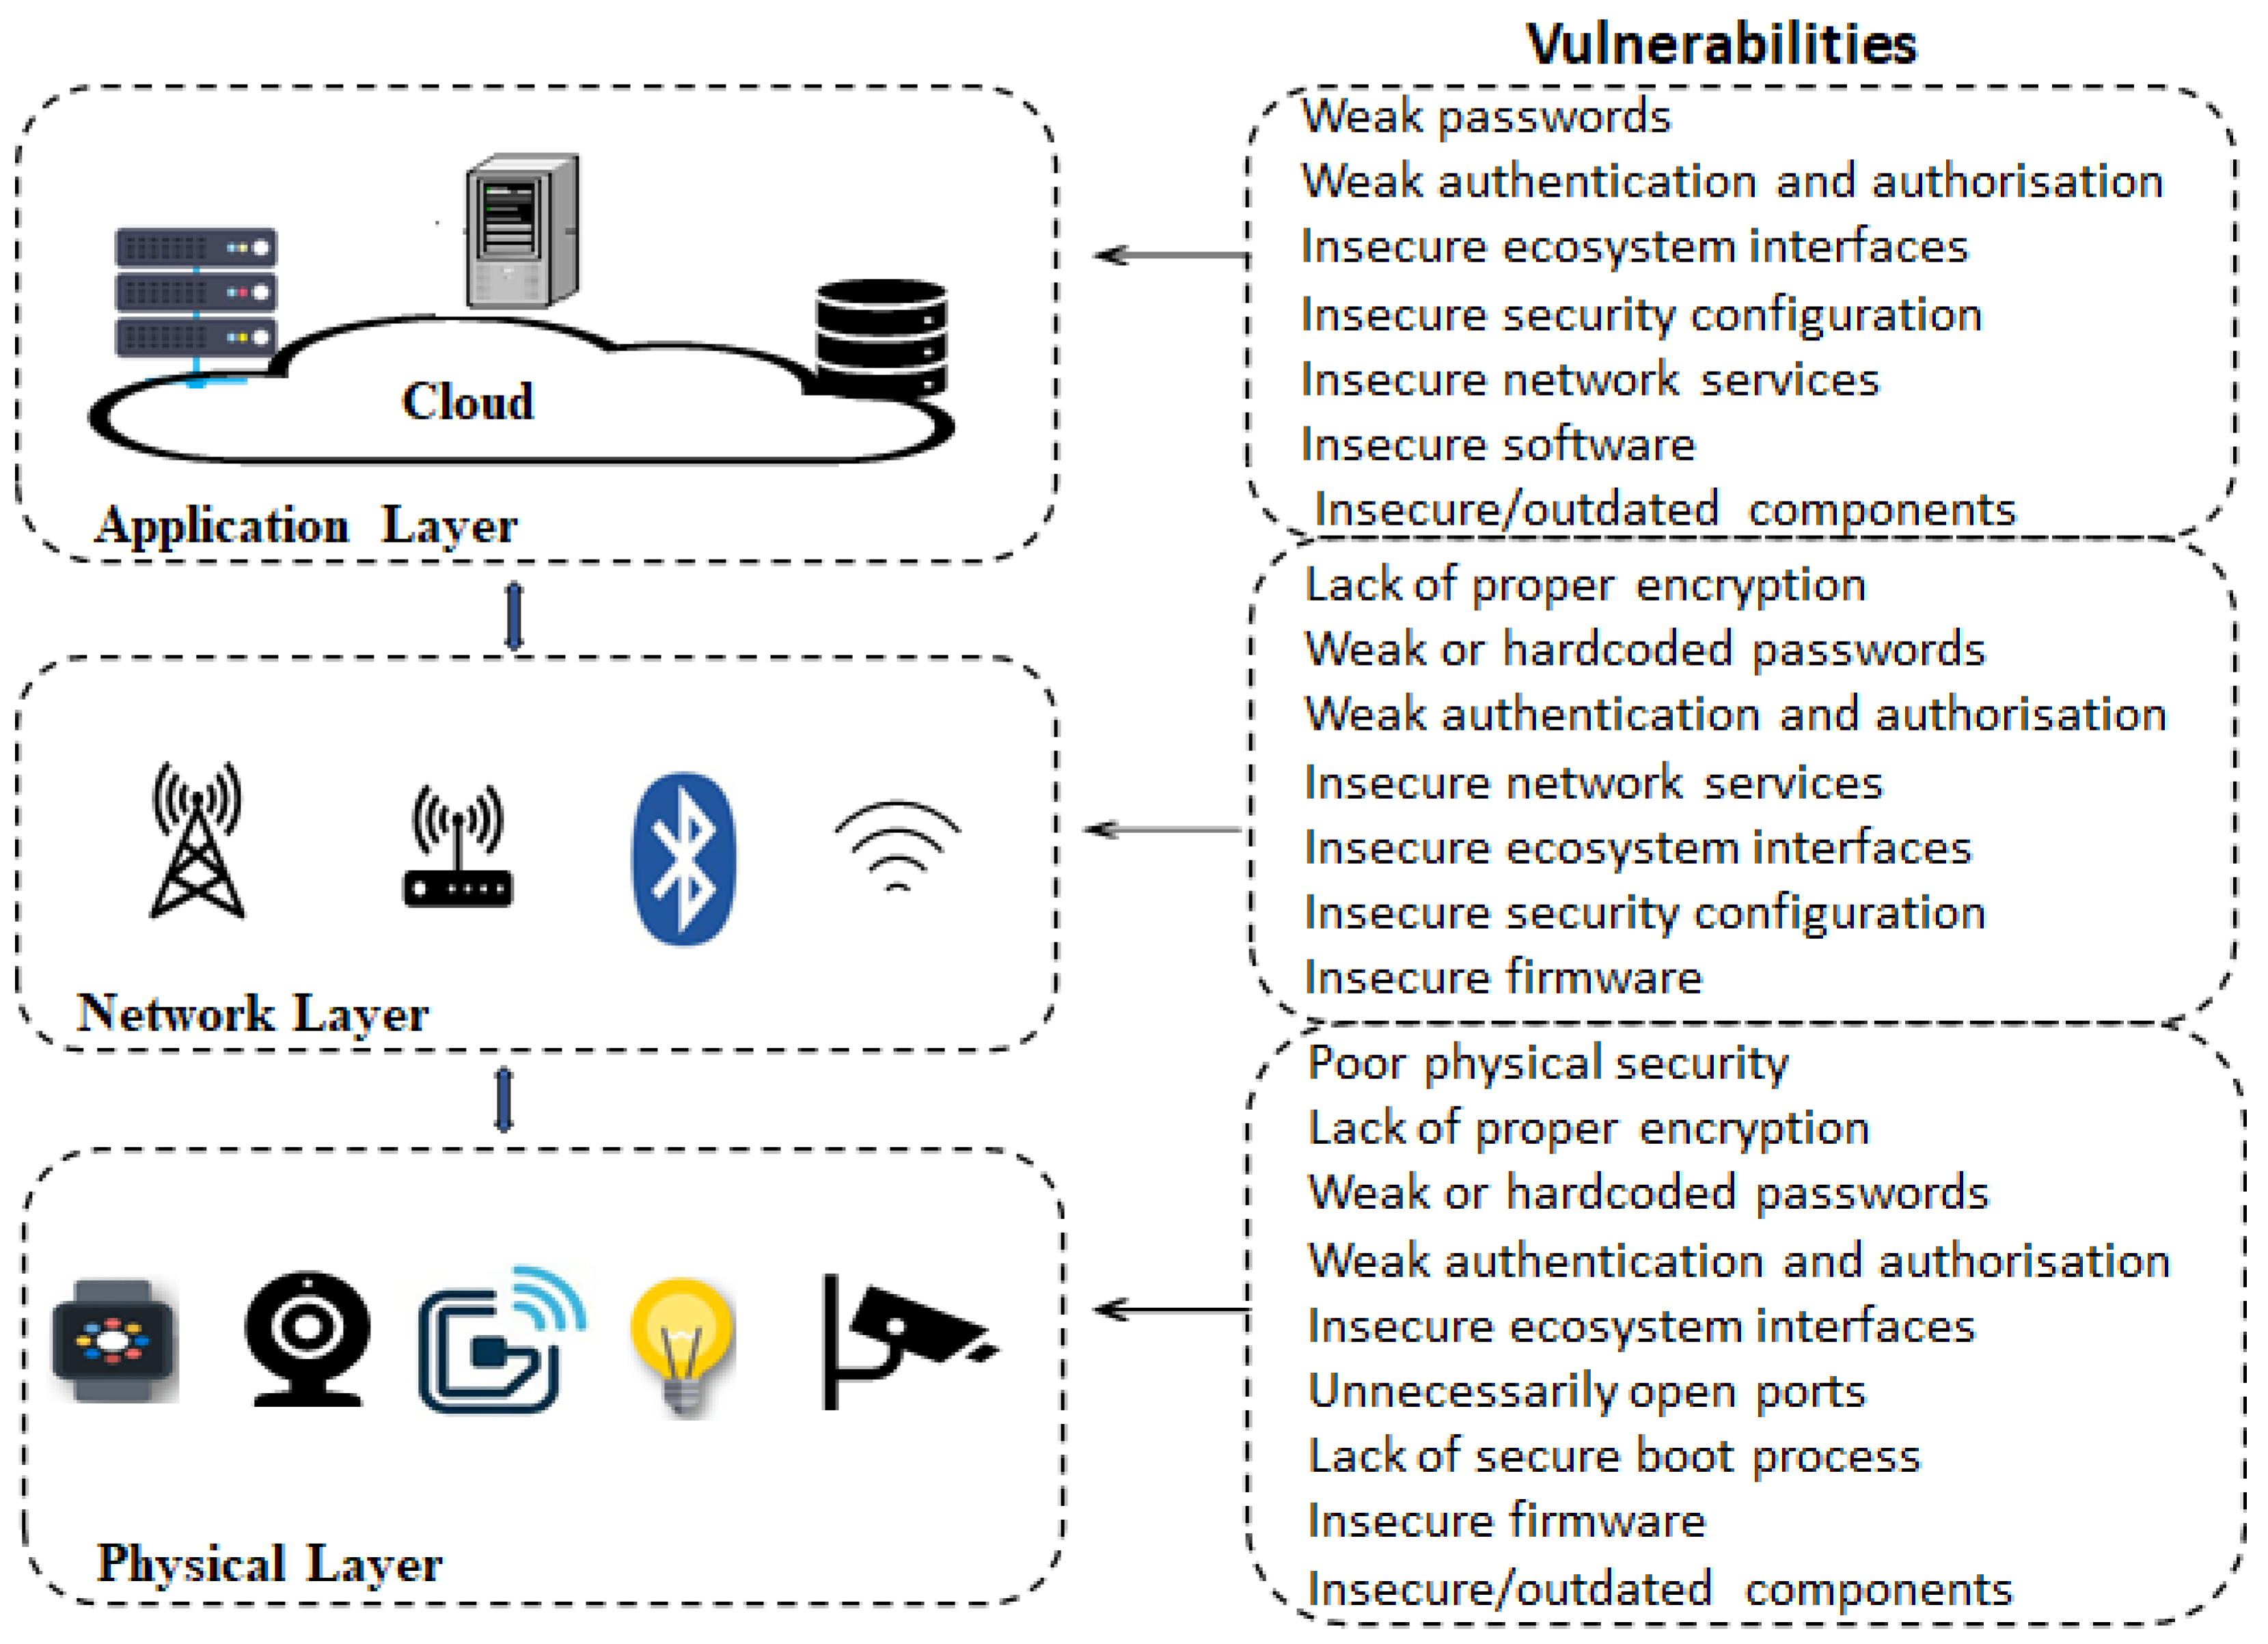
Additionally, this paper includes a systematic evaluation of selecting a risk management framework tailored to OT, which will be used to test multiple WAN security solutions and identify key variables to consider when choosing a network security solution to enhance the OT WAN infrastructure and bolster security for ICS and CPS.
Vulnerability Assessment tool
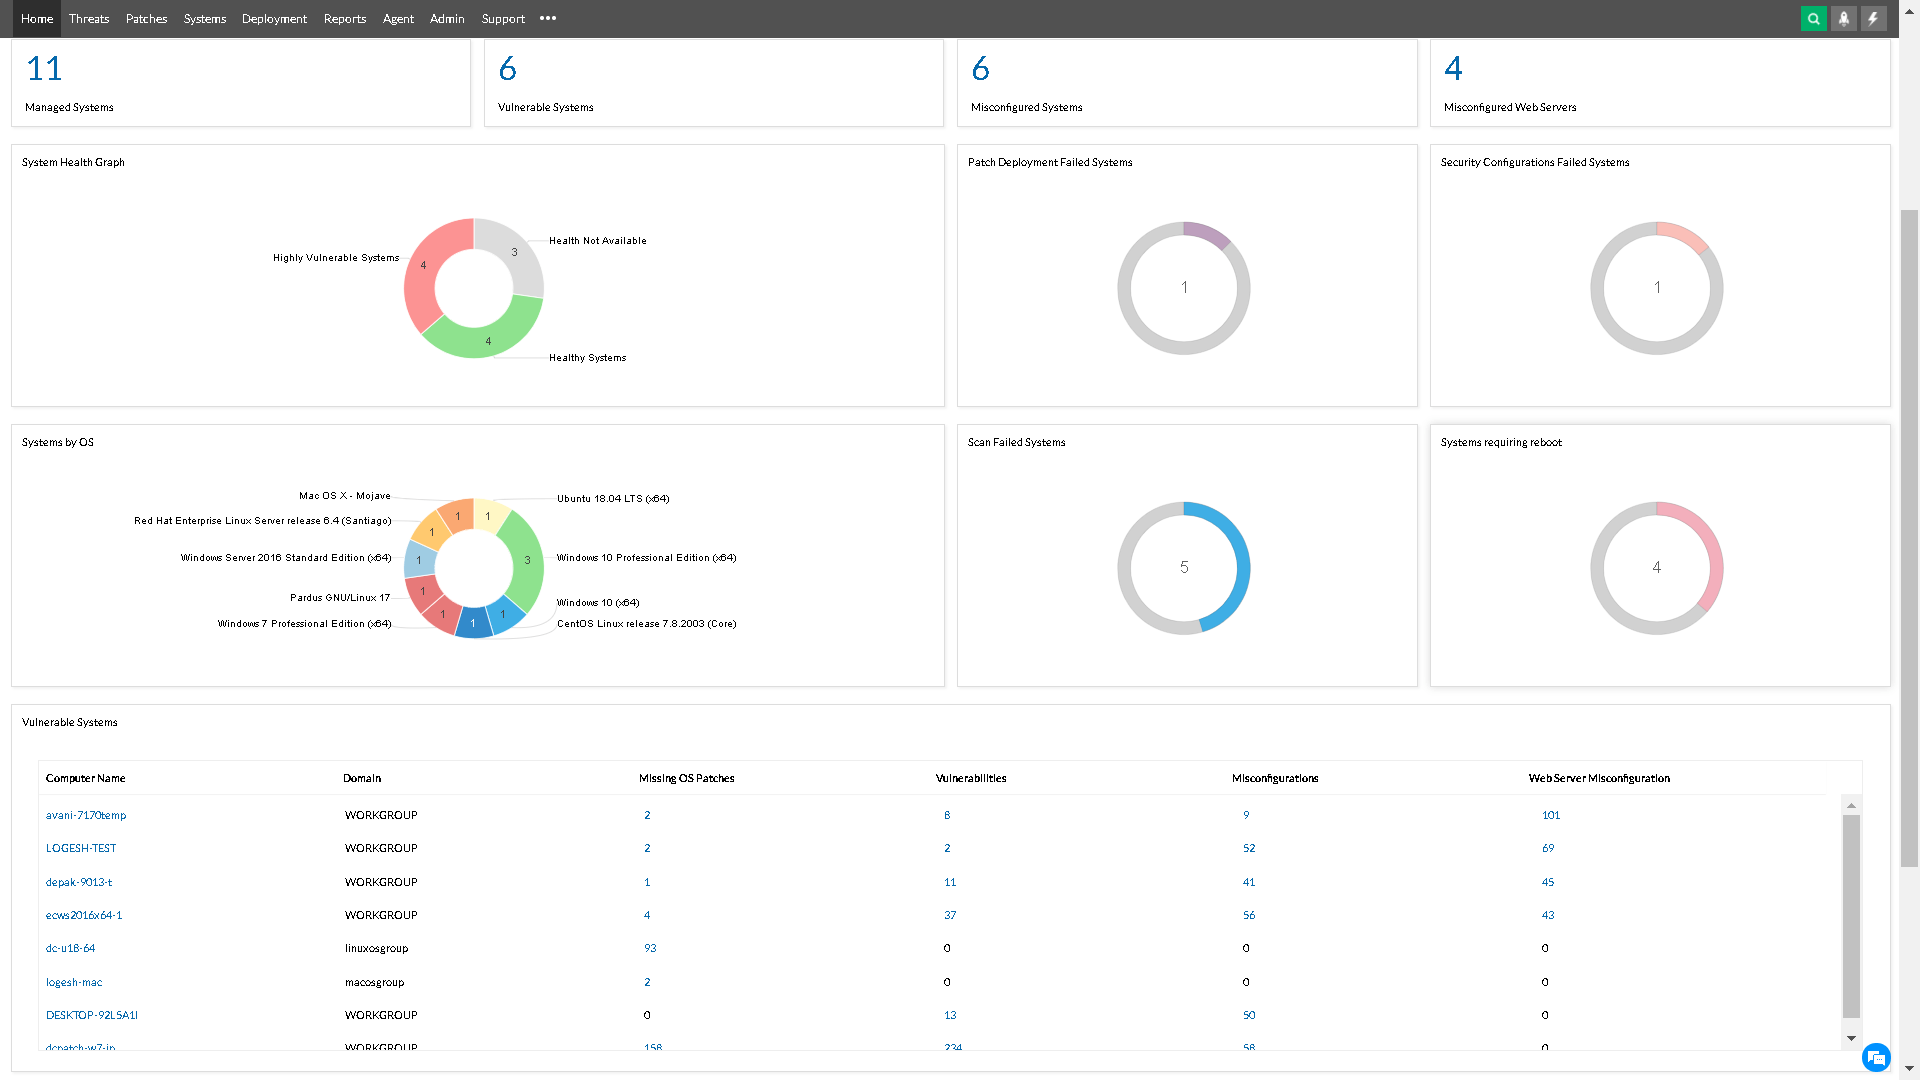
Assess vulnerabilities based on CVSS, severity, age, exploitability, asset criticality. Prioritize and remediate imminent and impactful risks with Vulnerability Manager Plus.