Access Control Policy
Access Control Access Control policies are just one part of the Firewall Threat Defense (FTD) feature set that organizations use to control network traffic. As packets ingress the firewall , many checks occur. For example, is the packet part of an existing connection, and does the packet require decryption or network address translation?
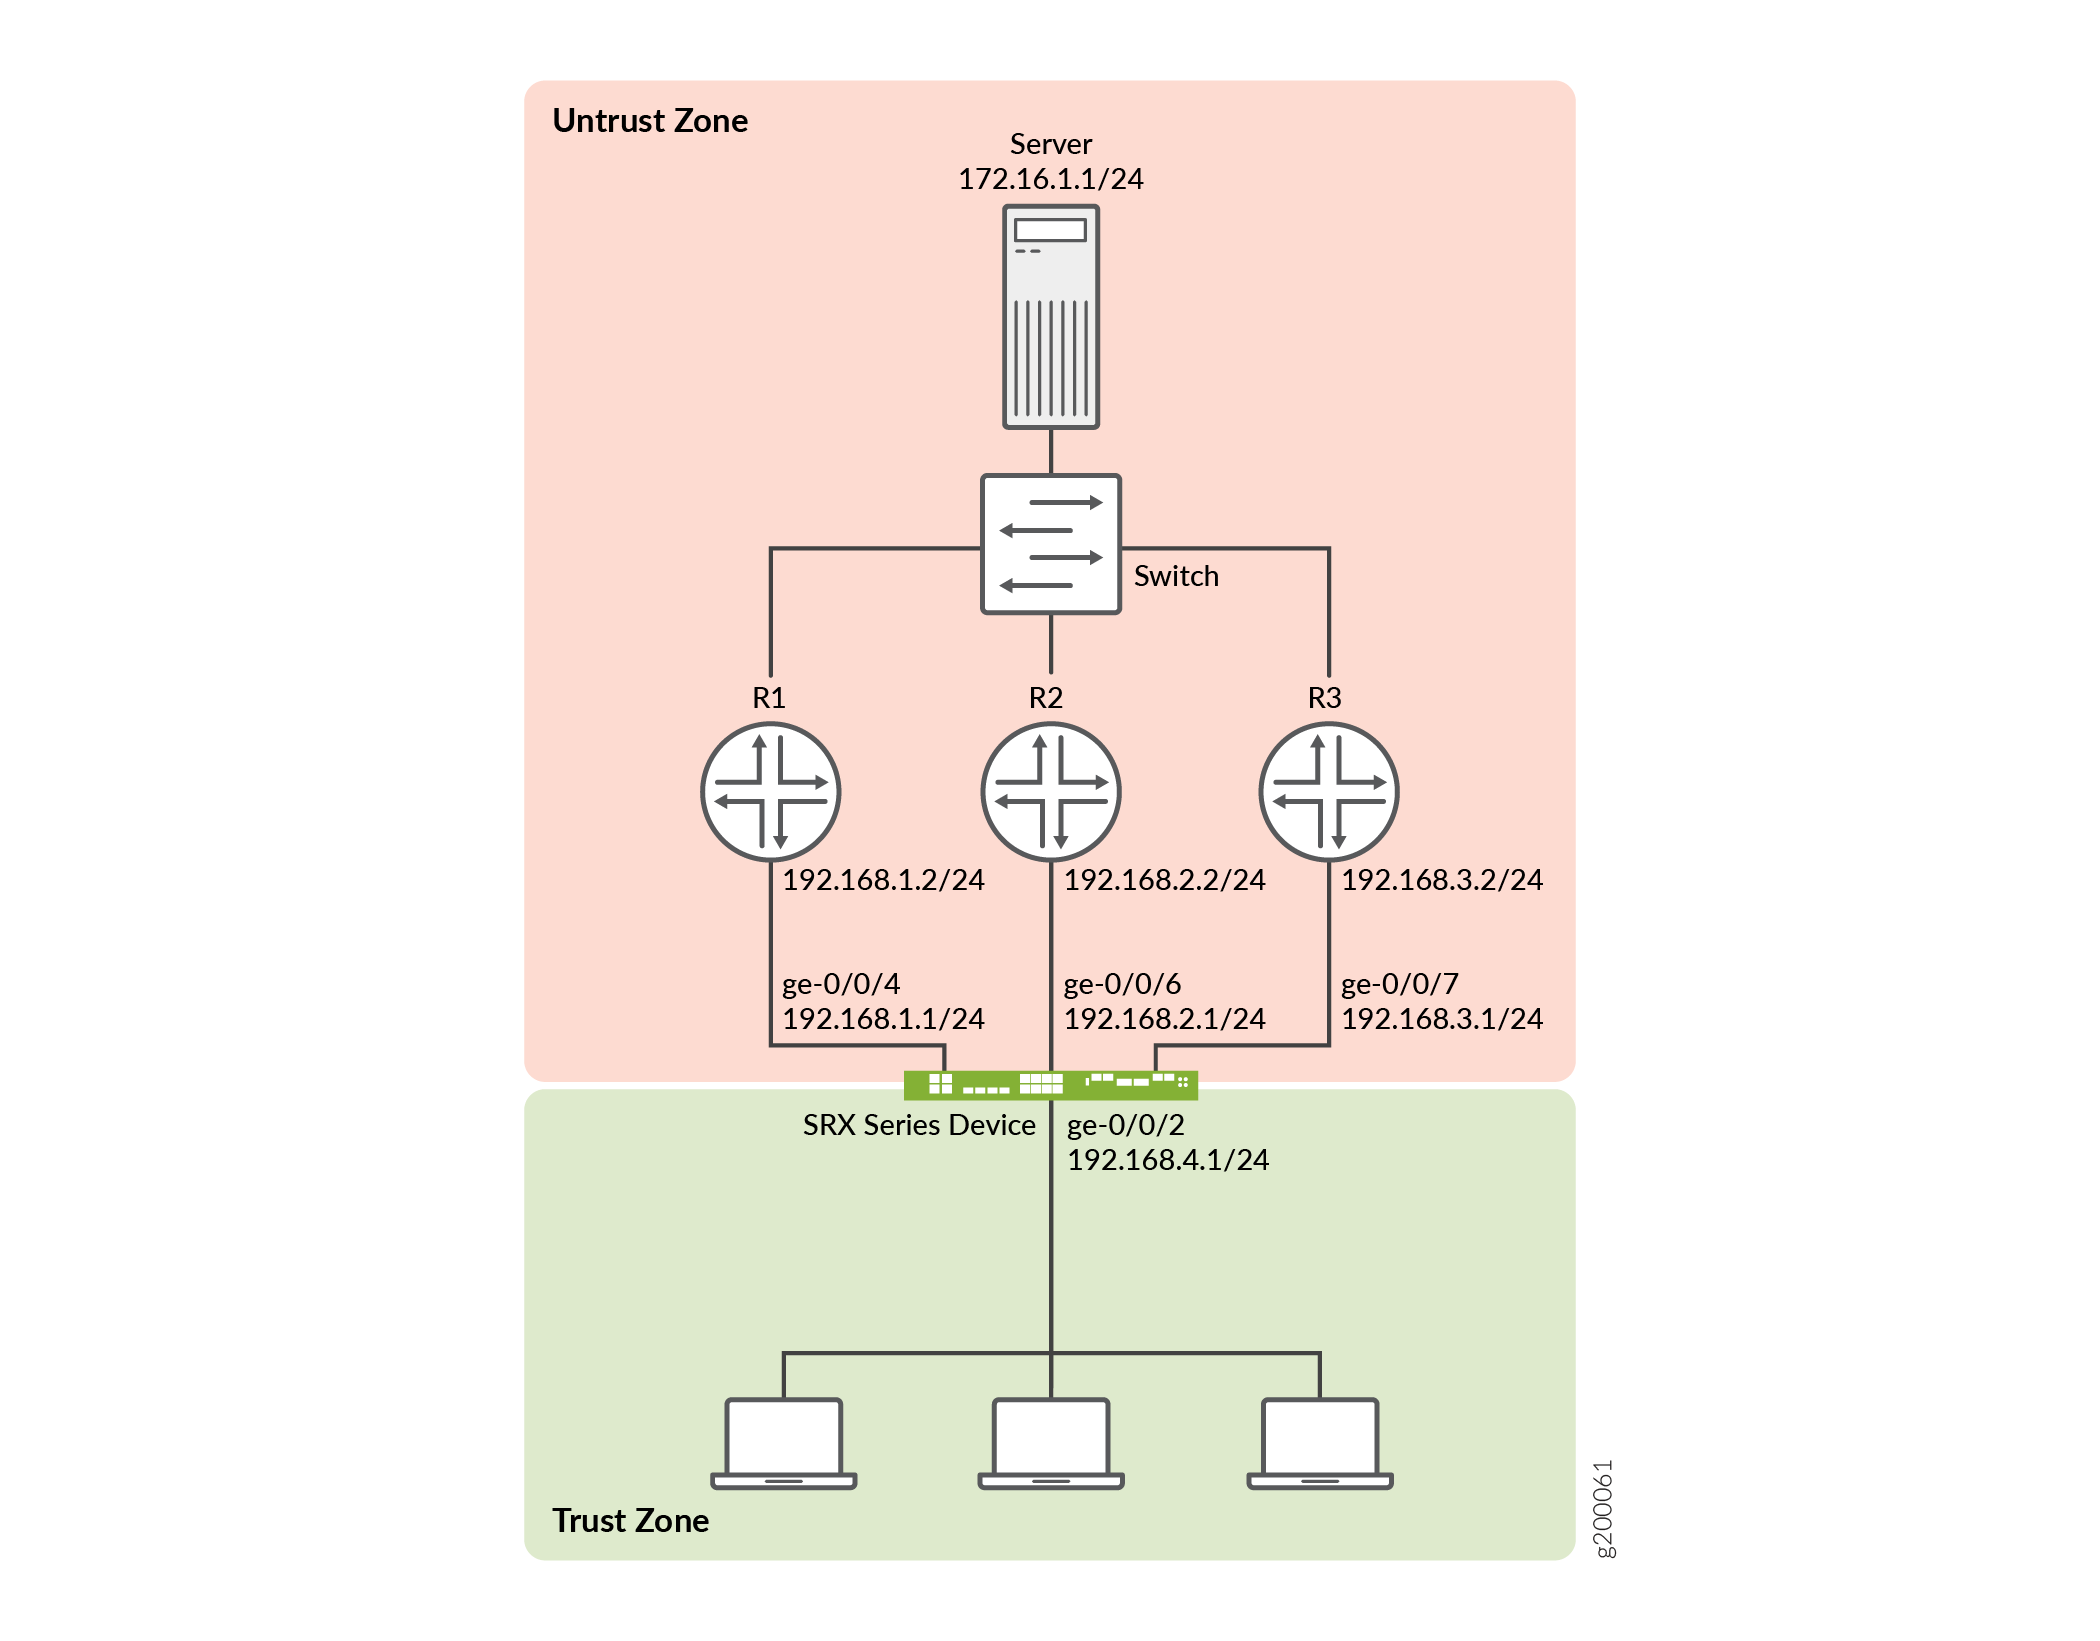
How to configure rules in the access control policy to control network access through the device. Access control is your basic firewall policy, and includes network and zone based control , application filtering, URL filtering, and IPS scanning.
Firewall Rules and Access Control Lists Tutorial
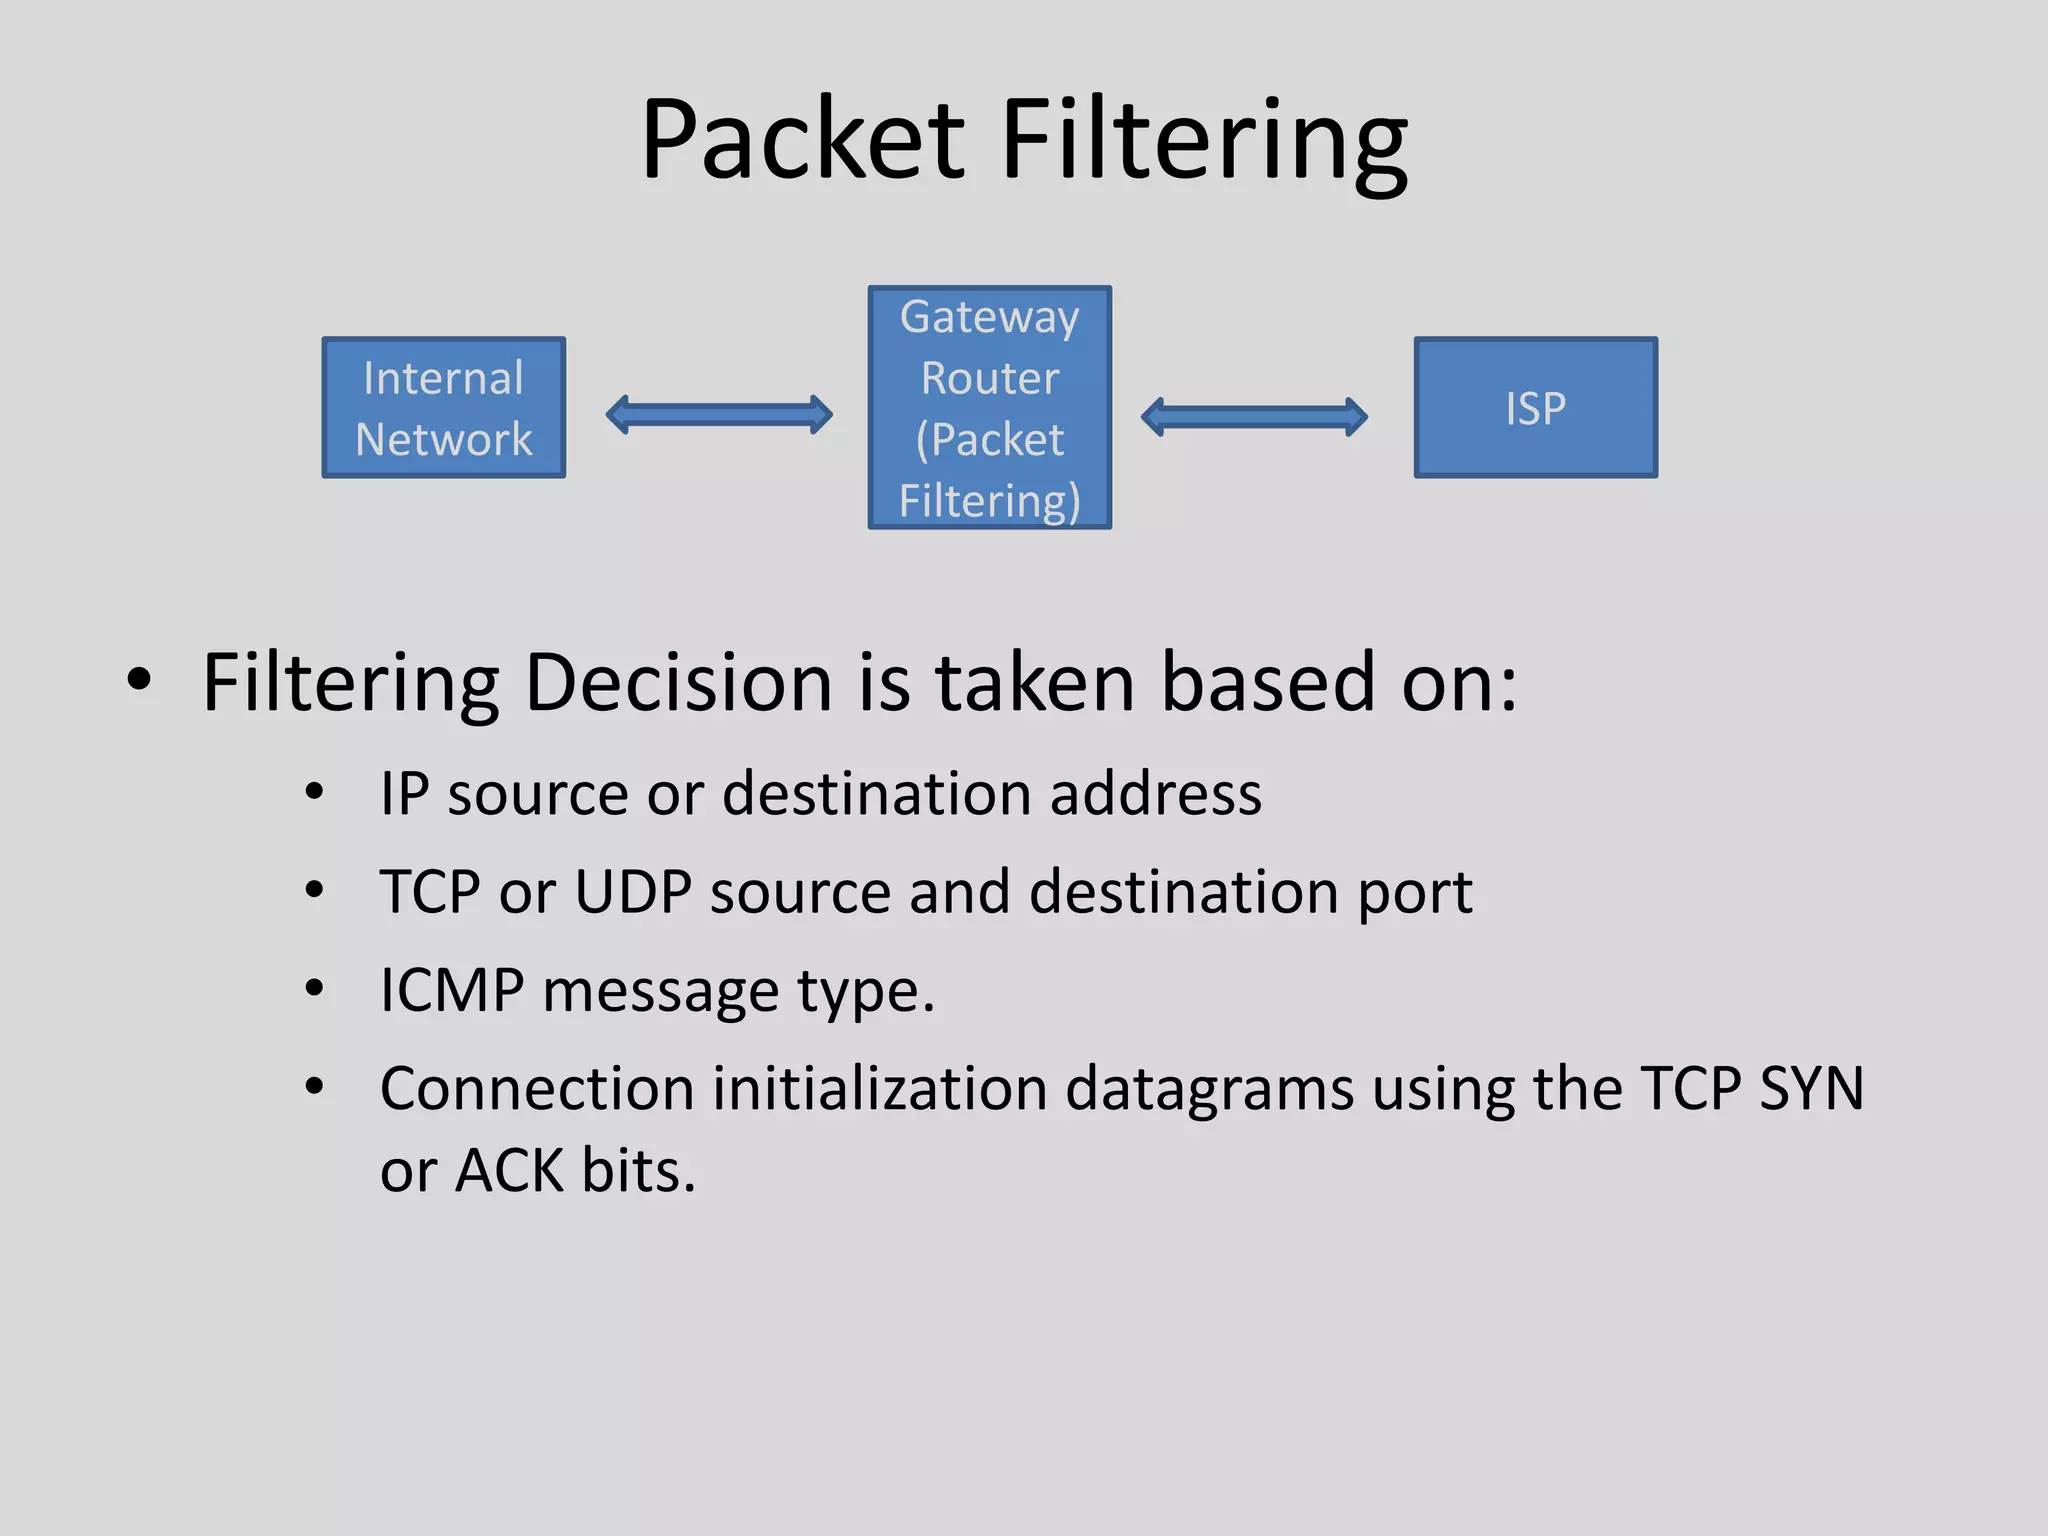
In the previous lesson, you learned that a firewall filters network traffic to protect internal systems from unauthorized access . It inspects packets moving between trusted and untrusted networks and decides which to allow or block based on a set of rules. A firewall enforces its filtering decisions through Access Control Lists (ACLs).
Firewalls and access control work hand-in-hand to secure your network: Threat Prevention: Firewalls block potential threats while access control ensures that only trusted users can access the network. Data Protection: Together, they create a safe environment for both the network and the information stored within it.

Difference between ACL and Firewall
While deploying security solutions in setups, administrators may be challenged with verdict on whether to consider ACL ( Access Control List) or use Firewall to secure the LAN Network setup. From a Bird's eye view, it may seem that ACL also filter the traffic (mostly LAN and WAN communication) like Firewalls do.
1. Introduction to Access Control and Firewall Technology Access control and firewall technology play a crucial role in securing networks and protecting sensitive information from unauthorized access . In today's digital age, where cyber threats are becoming increasingly sophisticated, it is...
ACL vs. Firewall
ACL vs. Firewall What's the Difference? ACL ( Access Control List) and Firewall are both security measures used to control and monitor network traffic. ACL is a set of rules that determine which packets are allowed or denied access to a network based on criteria such as source IP address, destination IP address, and port number.
Firewall Access Control involves setting rules that dictate which network traffic is allowed or blocked. These rules are based on criteria like source and destination IP addresses, ports, and protocols. Its primary function is to enforce security policies, preventing unauthorized access and protecting internal networks from external threats while enabling legitimate communication.

What Is Access Control Types, Models & Best Practices
What Is Access Control ? Access control is a security practice that determines who can view, use, or interact with resources in a given environment, and under what conditions. Most security programs depend on access control whether or not they've formally defined it. Every time a system checks whether a user has permission to open a file, query a database, or connect to a network, that's access ...



Access control is the process of authorizing users, groups, and machines to access objects on a network or computer. Learn more about access control systems.