Cybersecurity Compliance Made Easy: NIST Framework Hub
NIST Cybersecurity Framework compliance hub
NIST Cybersecurity Framework overview The NIST Cybersecurity Framework (CSF) is a non-certifiable standard for managing cyber security. It comprises security requirements in the form of policies, procedures, and technical controls. After implementing all the requirements from the framework , an organization can share an implementation report with partners and clients to demonstrate their ...

NIST Special Publication 800-53 Revision 5 ( NIST SP 800-53 Rev. 5) is a cybersecurity and compliance framework developed by the National Institute of Standards and Technology ( NIST ), an agency that's part of the U.S. Department of Commerce.
NIST Cybersecurity Frameworks Hub
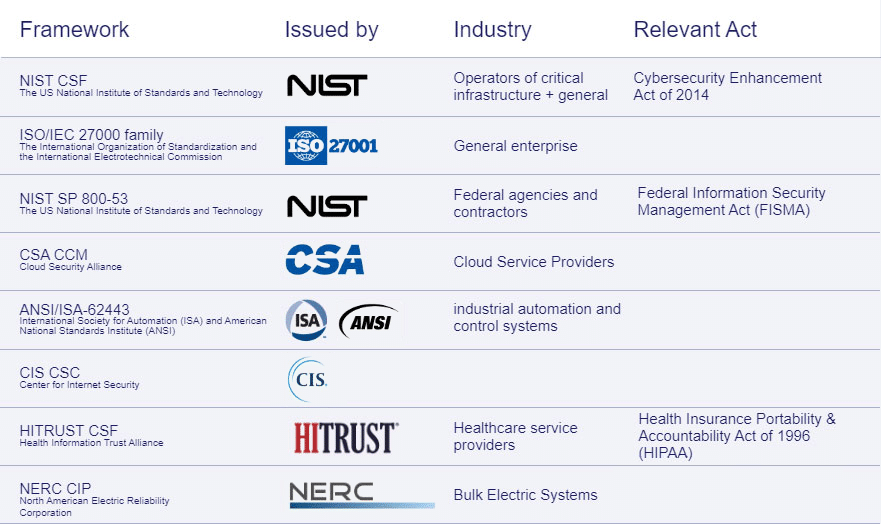
Delve into Cynomi's NIST Cybersecurity Frameworks Hub for essential resources on NIST standards, compliance guidelines, and strategies to fortify your cybersecurity measures.
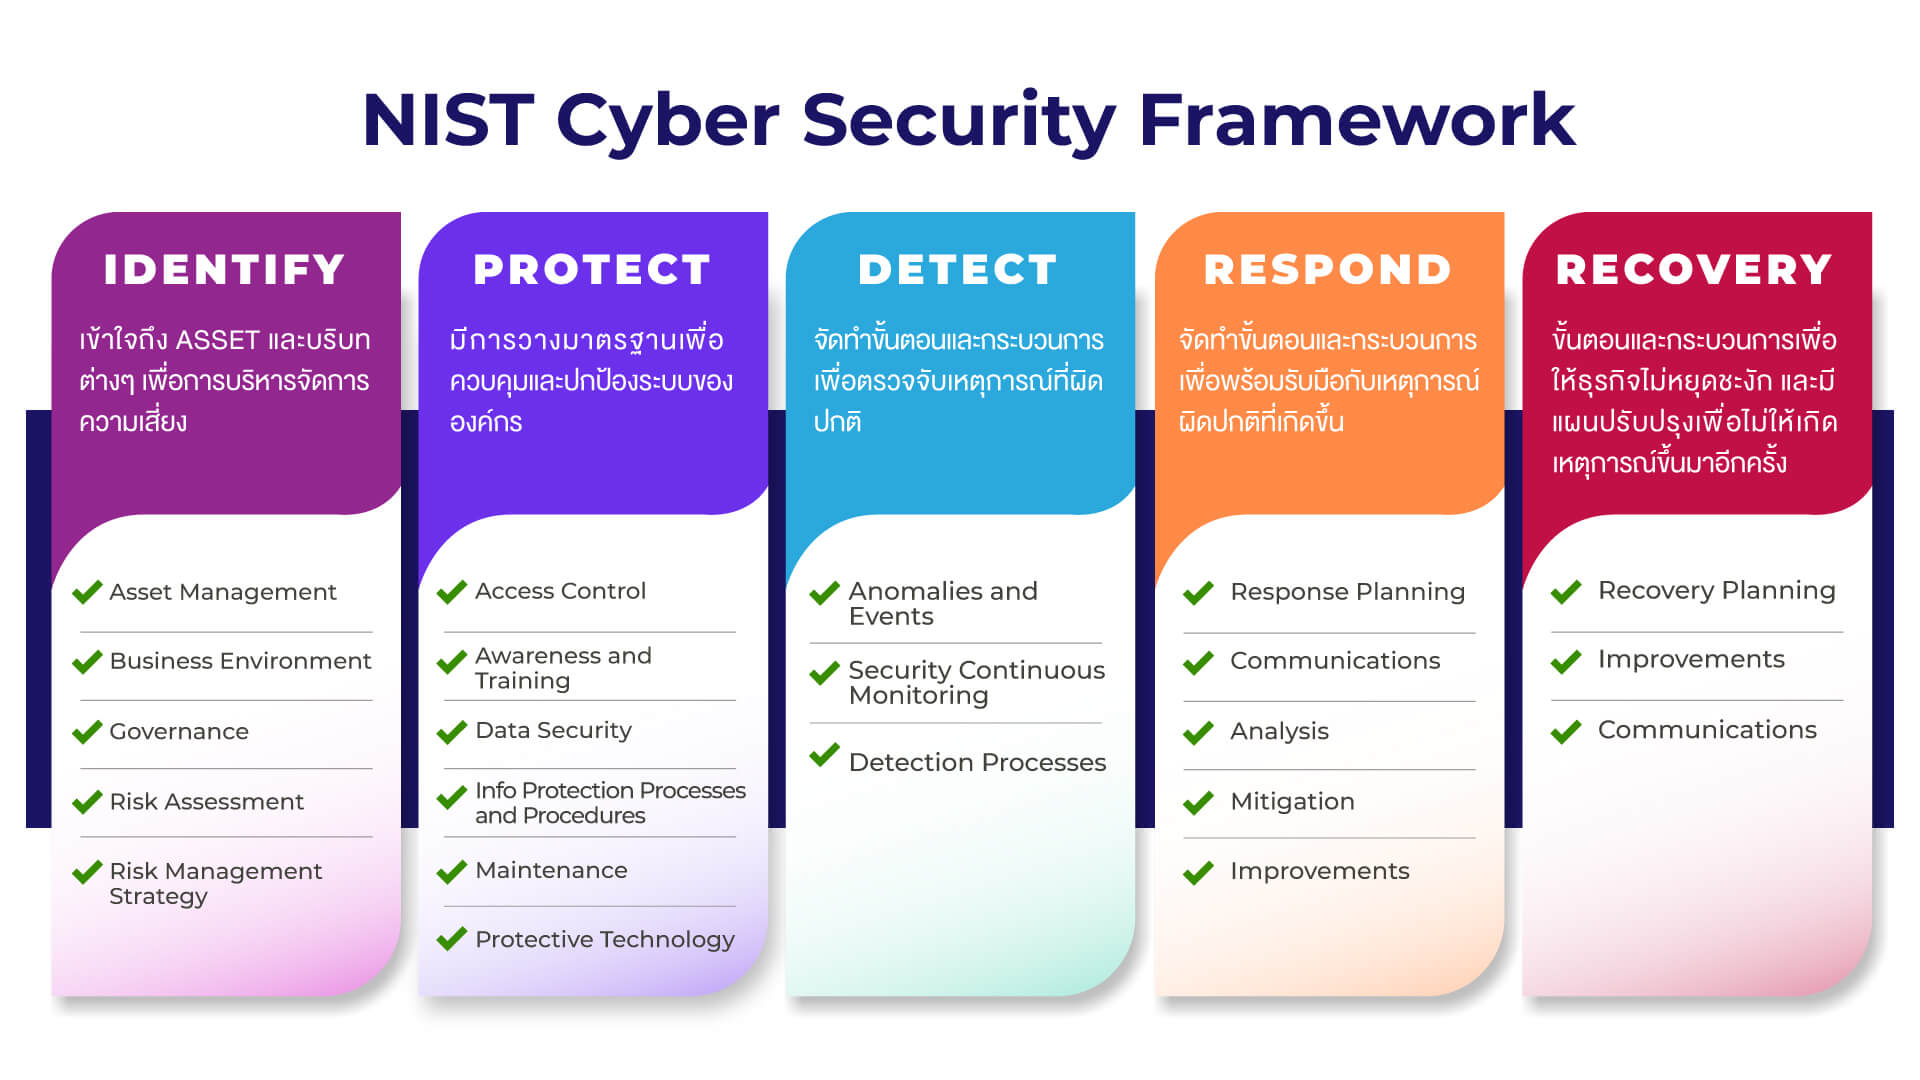
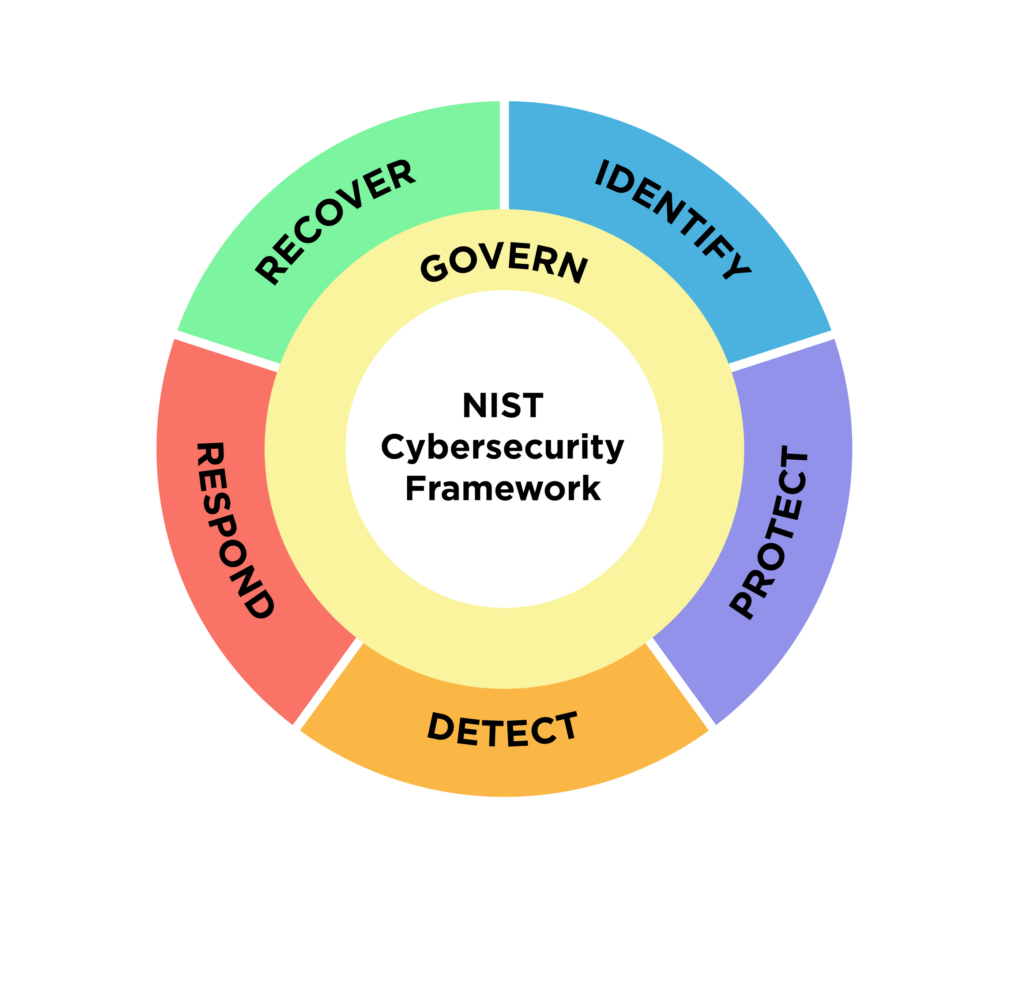
The National Institute of Standards and Technology ( NIST ) developed NIST CSF to give organizations a common cybersecurity language to work with. The NIST CSF meaning boils down to this: it's a voluntary, risk-based framework that helps organizations identify, protect, detect, respond to, and recover from cybersecurity incidents and events.
NIST Cybersecurity Framework (CSF)
NIST CSF overview The National Institute of Standards and Technology ( NIST ) Cybersecurity Framework (CSF) was published in February 2014 as guidance for critical infrastructure organizations to better understand, manage, and reduce their cybersecurity risks.
NIST compliance means aligning your cybersecurity program with standards developed by the National Institute of Standards and Technology ( NIST ). The NIST security framework is a risk-based model built around five core functions designed to address evolving threats and serves as a widely adopted framework for managing cybersecurity risk globally.

What is the NIST Cybersecurity Framework
The NIST Cybersecurity Framework isn't another compliance checkbox—it's the common language that helps security teams explain cyber risk to executives who don't speak tech. Since February 2024, CSF 2.0 organizes cybersecurity into six functions (Govern, Identify, Protect, Detect, Respond, Recover) that any organization can adapt, regardless of size. Unlike prescriptive standards that demand ...
This draft explains how to find, filter, and apply informative references using NIST tools. Review and submit comments here. The final version of NIST Cybersecurity Framework 2.0: Cybersecurity , Enterprise Risk Management, and Workforce Management Quick-Start Guide
The NIST Cybersecurity Framework (CSF) 2.0
The NIST Cybersecurity Framework (CSF) 2.0 provides guidance to industry, government agencies, and other organizations to manage cybersecurity risks. It offers a taxonomy of high-level cybersecurity outcomes that can be used by any organization — regardless of its size, sector, or maturity — to better understand, assess, prioritize, and ...



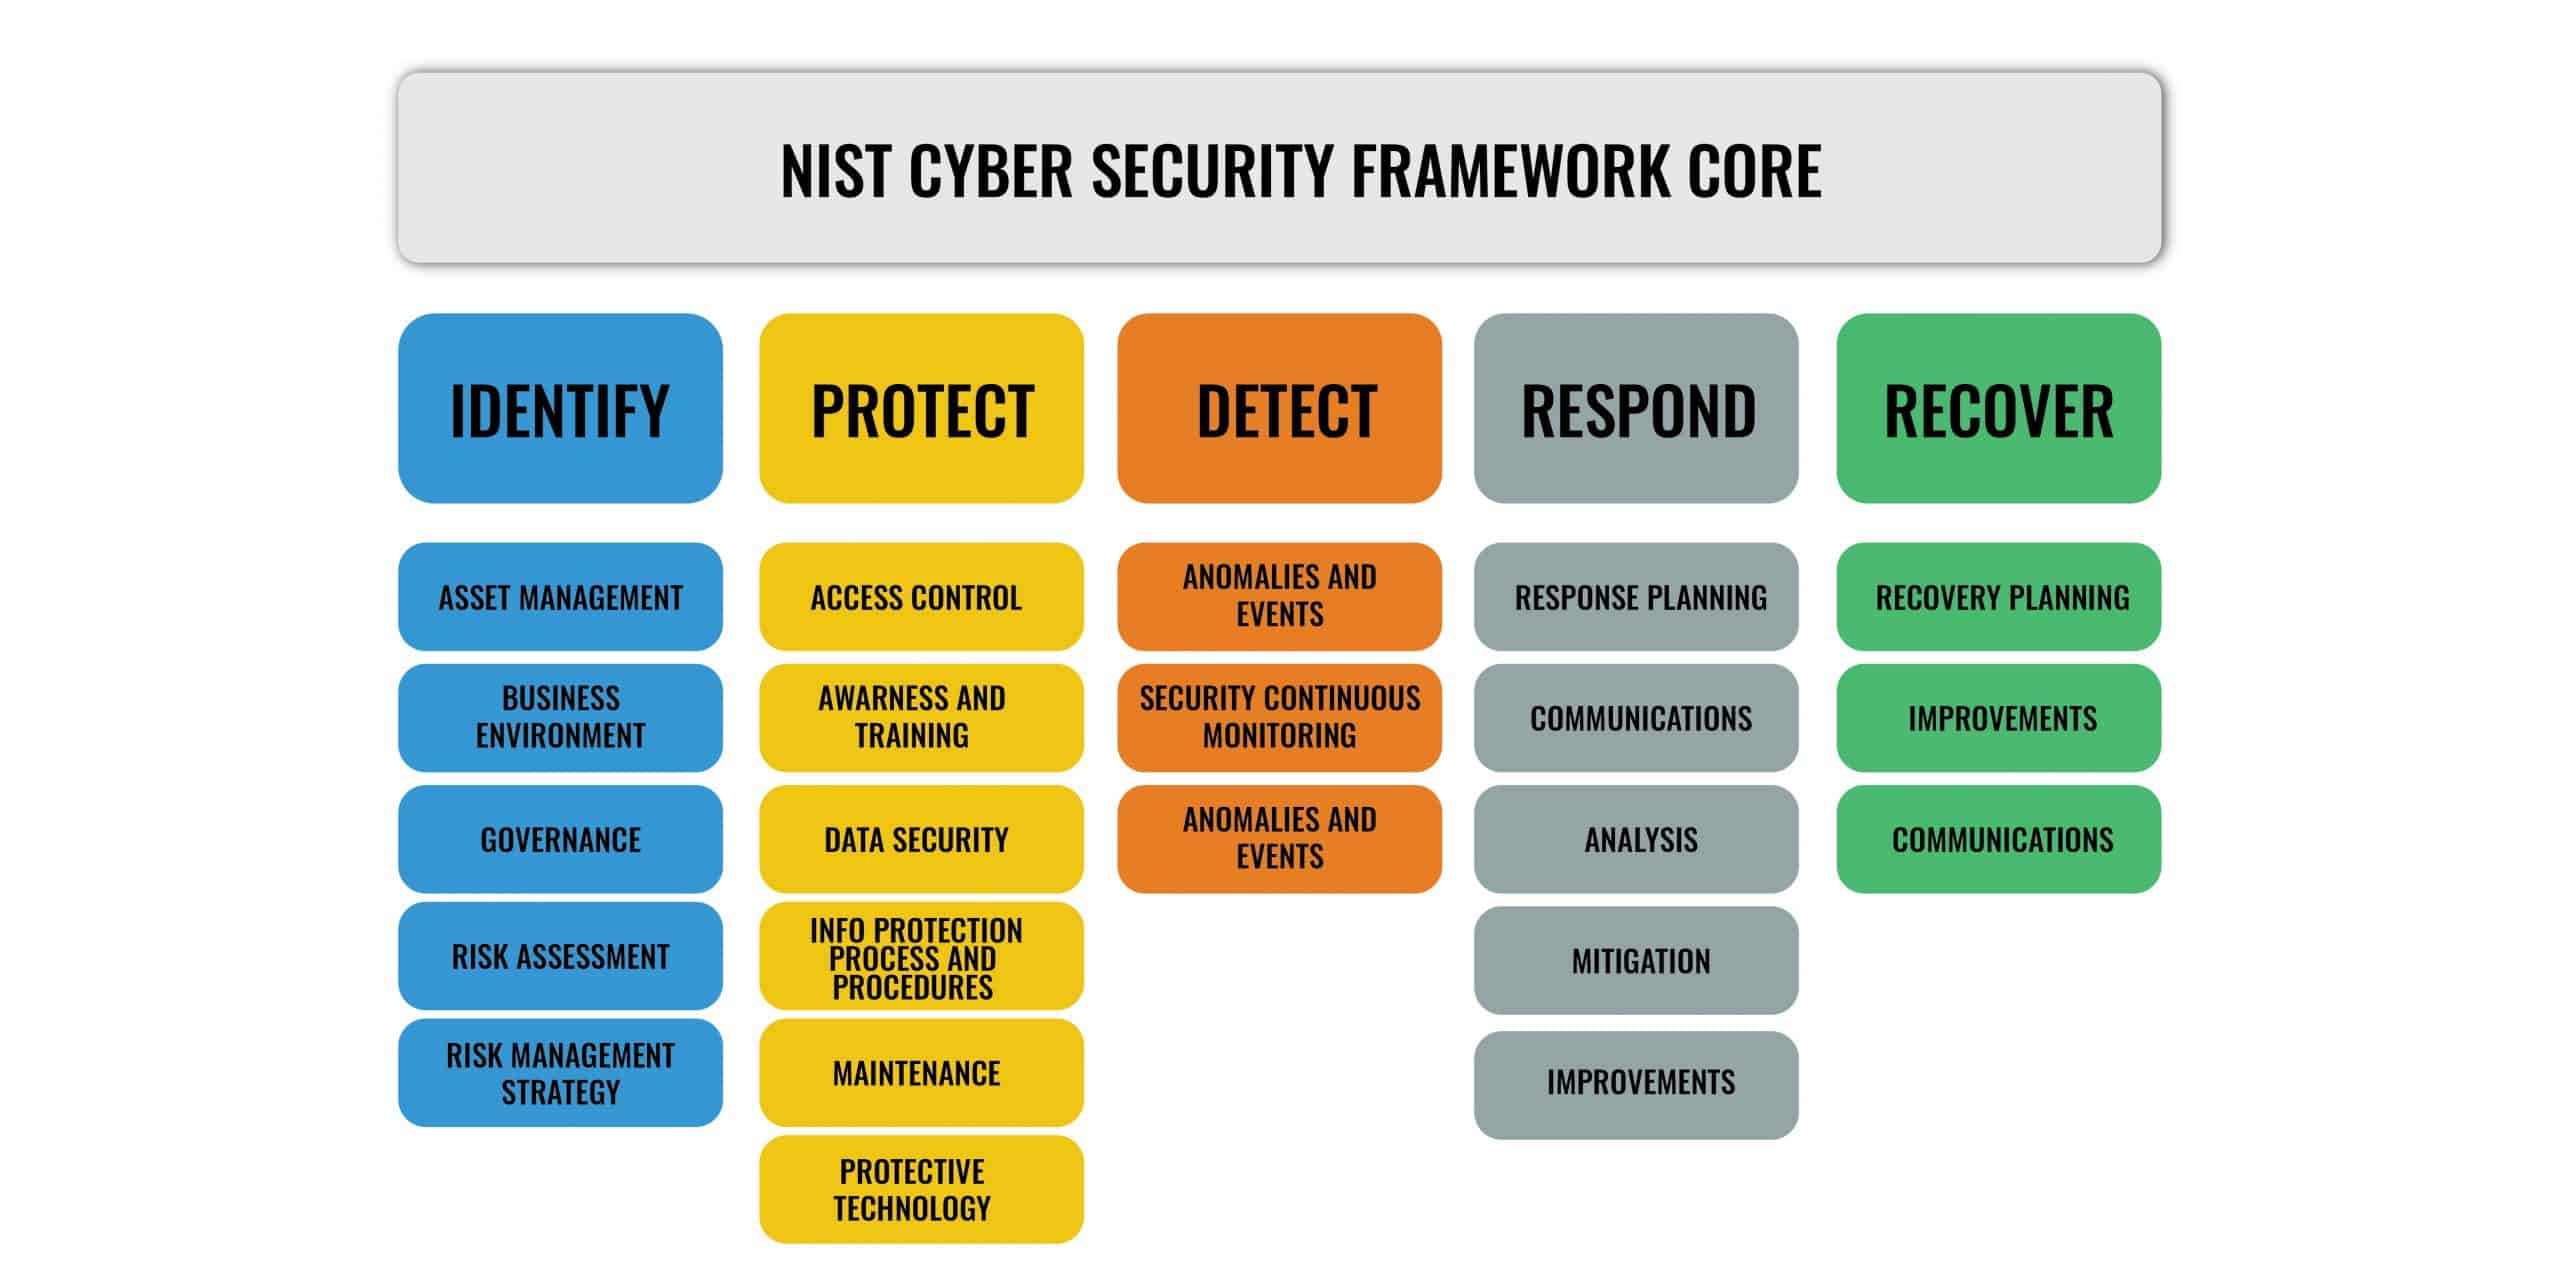
The NCSR question set represents the National Institute of Standards and Technology Cybersecurity Framework ( NIST CSF). This guide gives the correlation between 49 of the NIST CSF subcategories, and applicable policy and standard templates. A NIST subcategory is represented by text, such as "ID.AM-5." This represents the NIST function of Identify and the category of Asset Management. For ...