Enable Audit and Handle Events for Windows Server Malware Protection
By Janet · Apr 18, 2026
Windows Security Audit Events
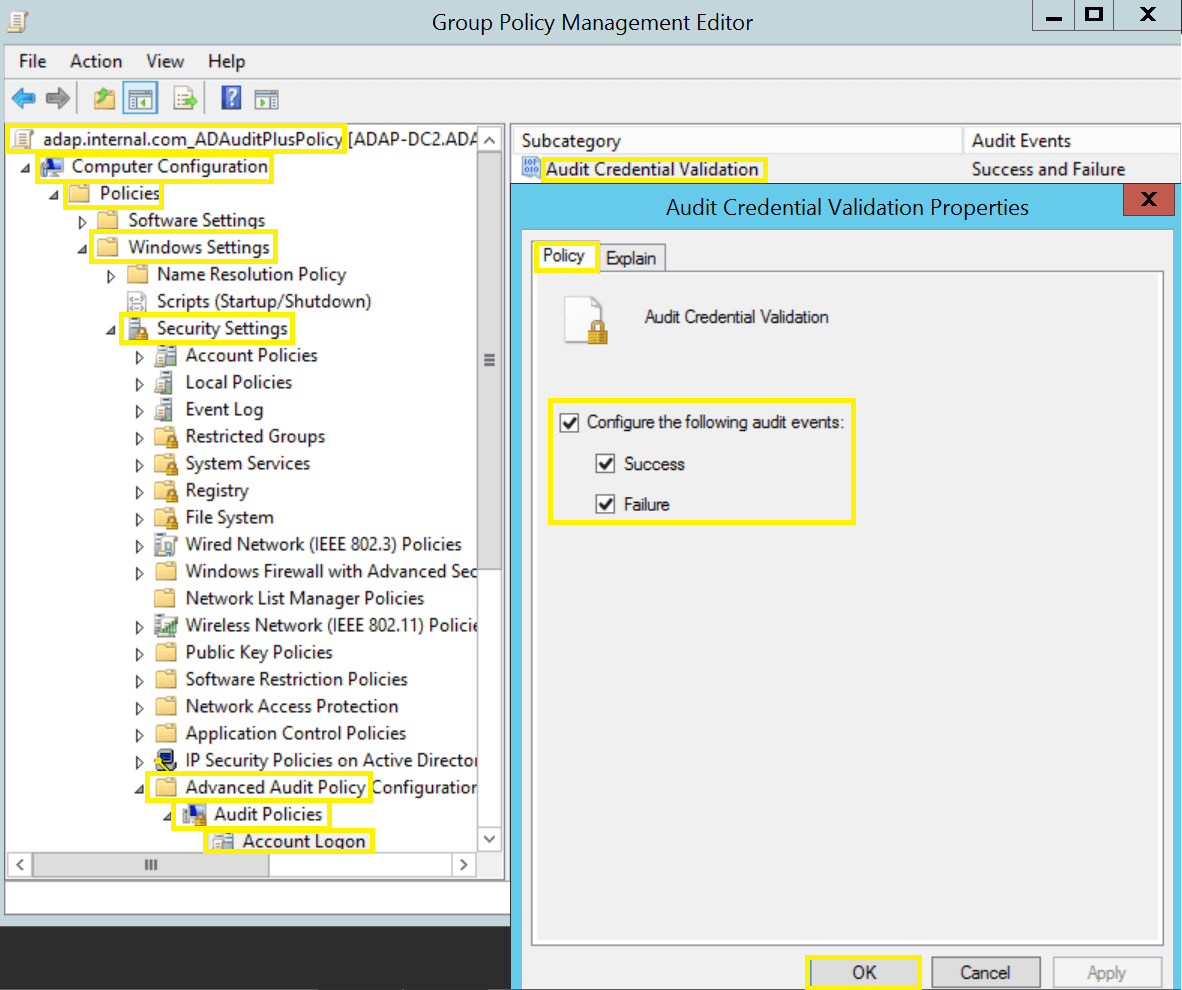
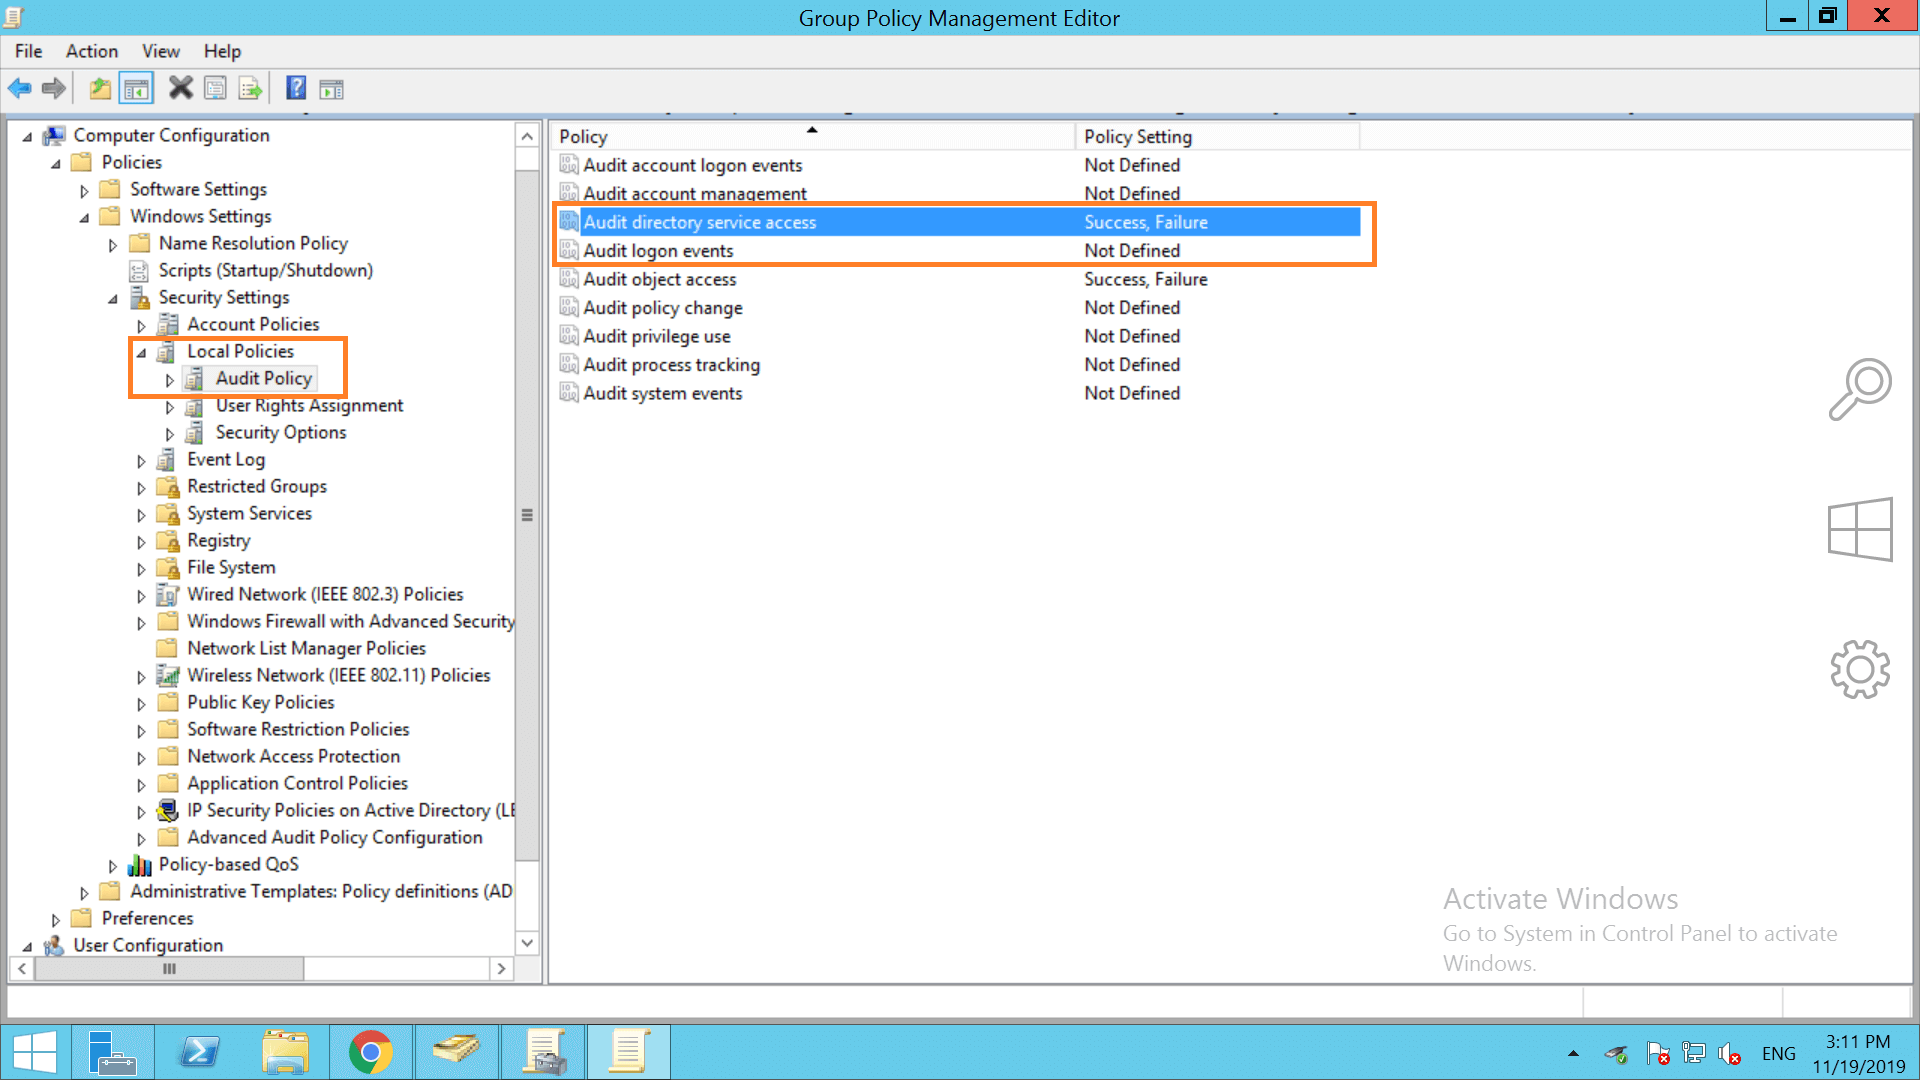
Image result for Configure audit policy manually | Windows server audit guide | ADAudit Plus
Enable Windows Security Audit Events : step-by-step setup for logon tracking, policy changes, and privileged account monitoring.
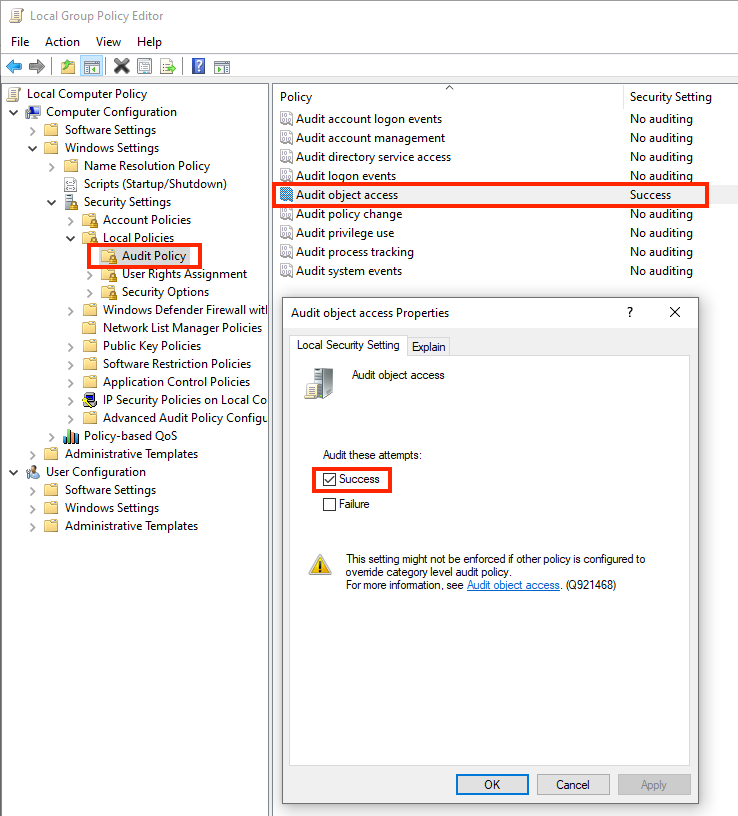
Image result for Configure Windows event auditing - Microsoft Defender for Identity | Microsoft Learn
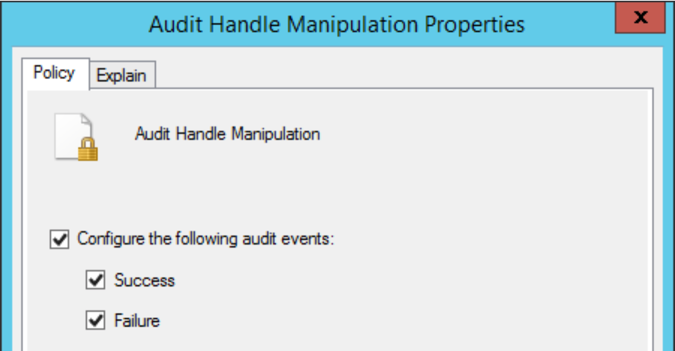
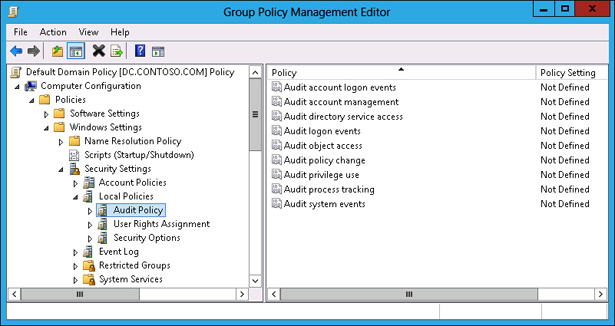
Windows Audit Policy is the built-in control mechanism for logging security events on a system. It allows administrators to fine-tune what gets recorded, expanding beyond default logs to capture critical activities like user logons, file access, process creation, and handle requests.
How to Monitor and Audit Your Windows Server for Security Events
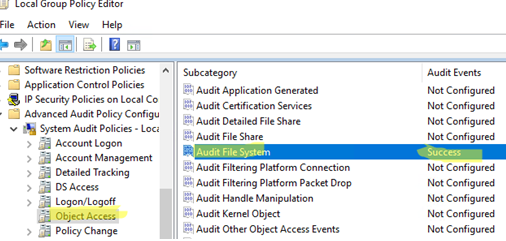
Image result for Manual config of audit policy | Windows file audit | ADAudit Plus
This article explores the essential elements of monitoring and auditing in Windows Server , offering valuable insights into the necessary tools and practices for recognizing and addressing security events . In doing so, it strengthens the digital defenses of our server environment.
Abstract This document describes the security audit policy settings available in Windows Server 2008 onwards , Windows 7 onwards, and audit events that they generate. These settings allow selecting only the behavior you want to monitor and excludes audit results for other behaviors.
Image result for Configure Windows event auditing - Microsoft Defender for Identity | Microsoft Learn
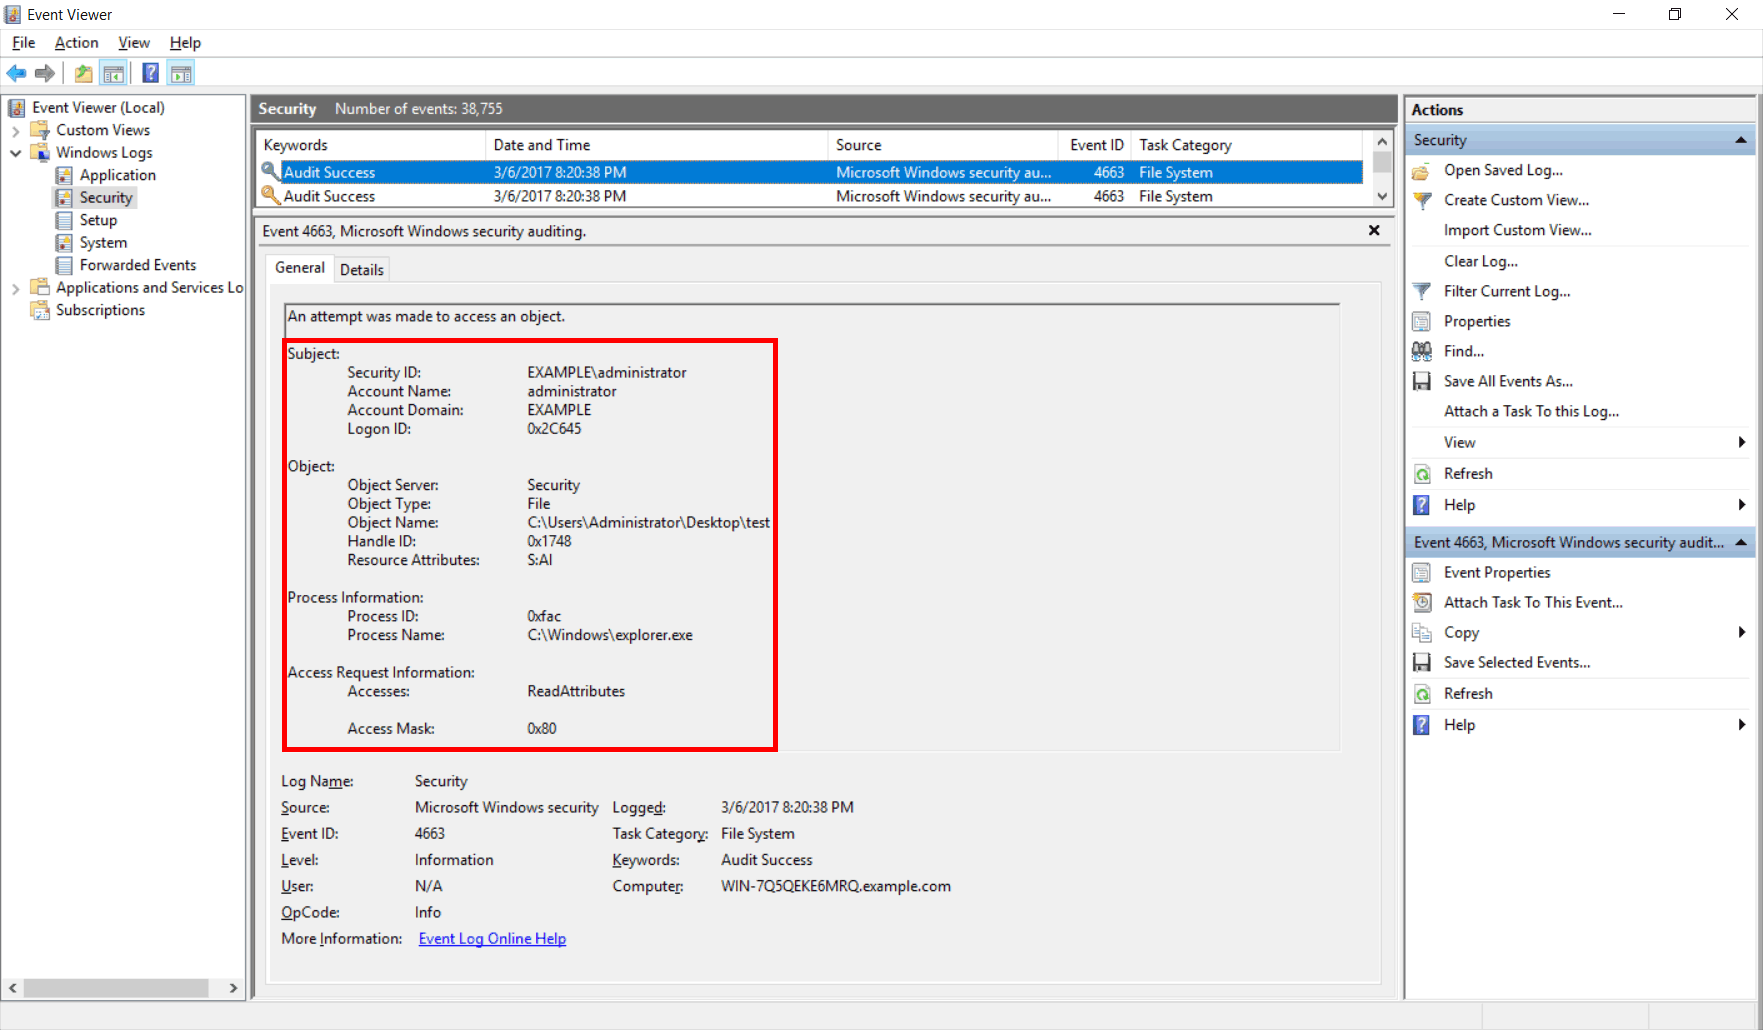
Chapter 2 Audit Policies and Event Viewer
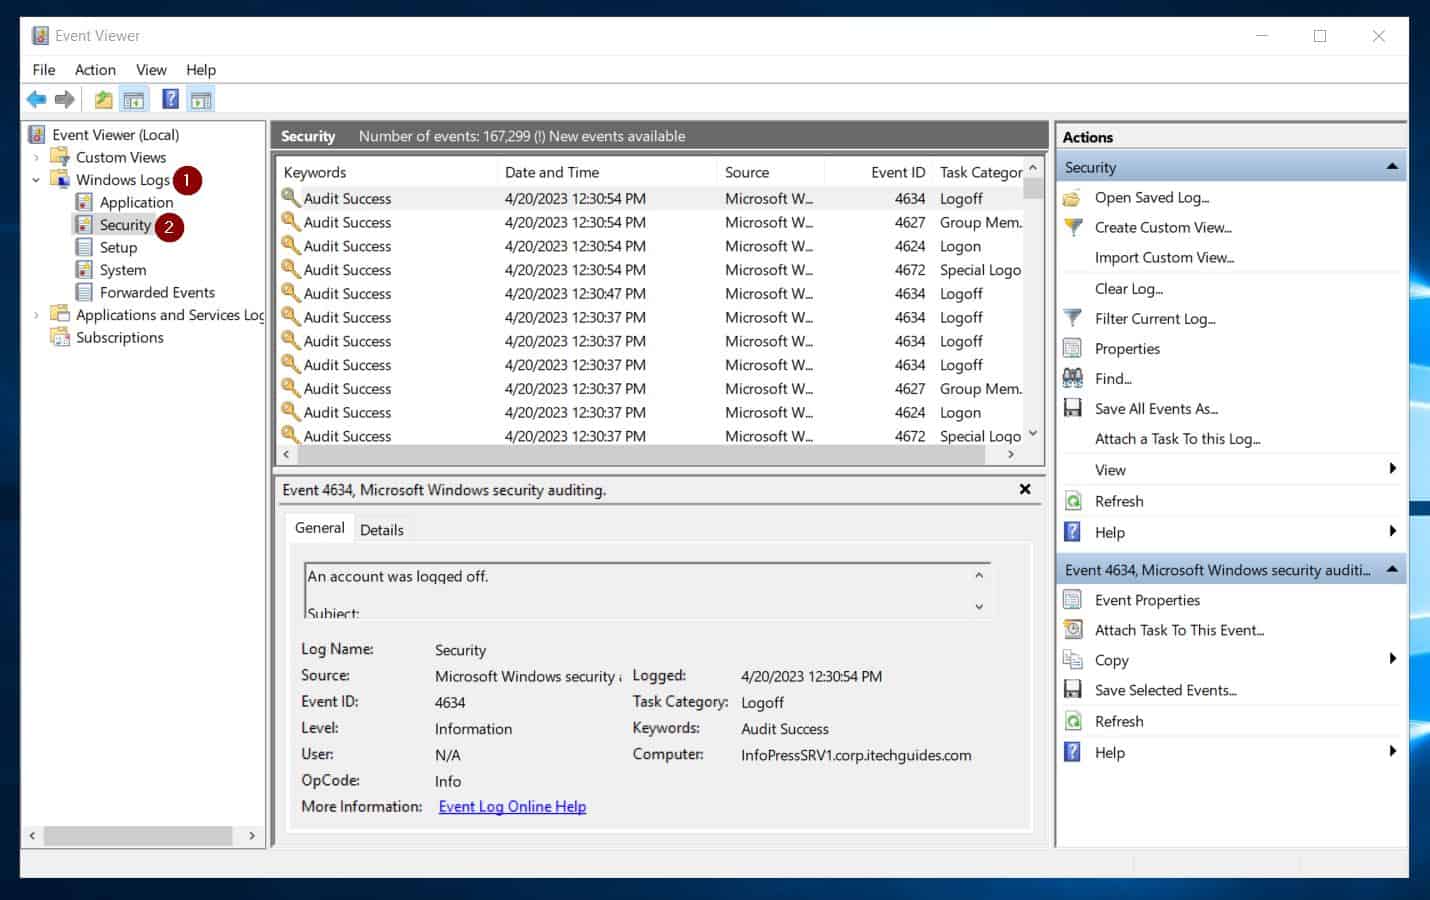
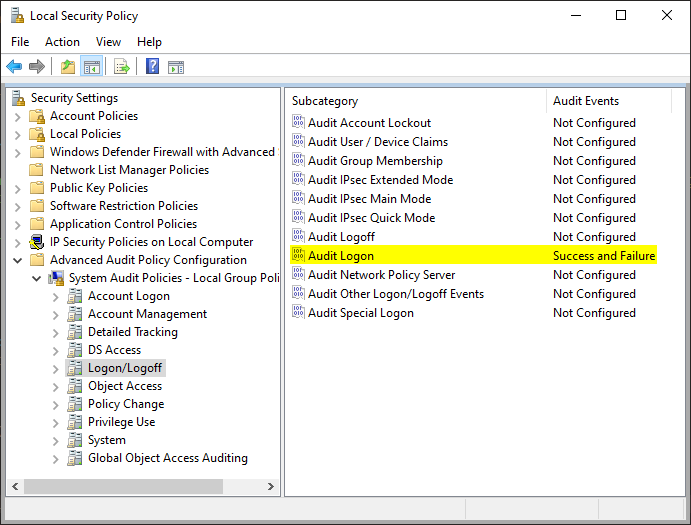
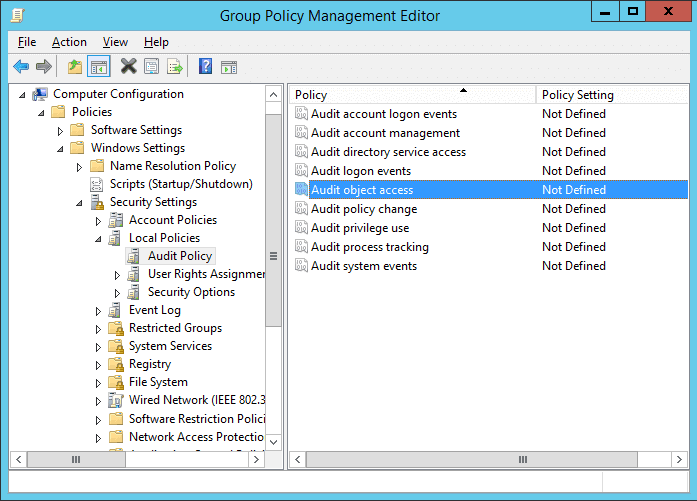
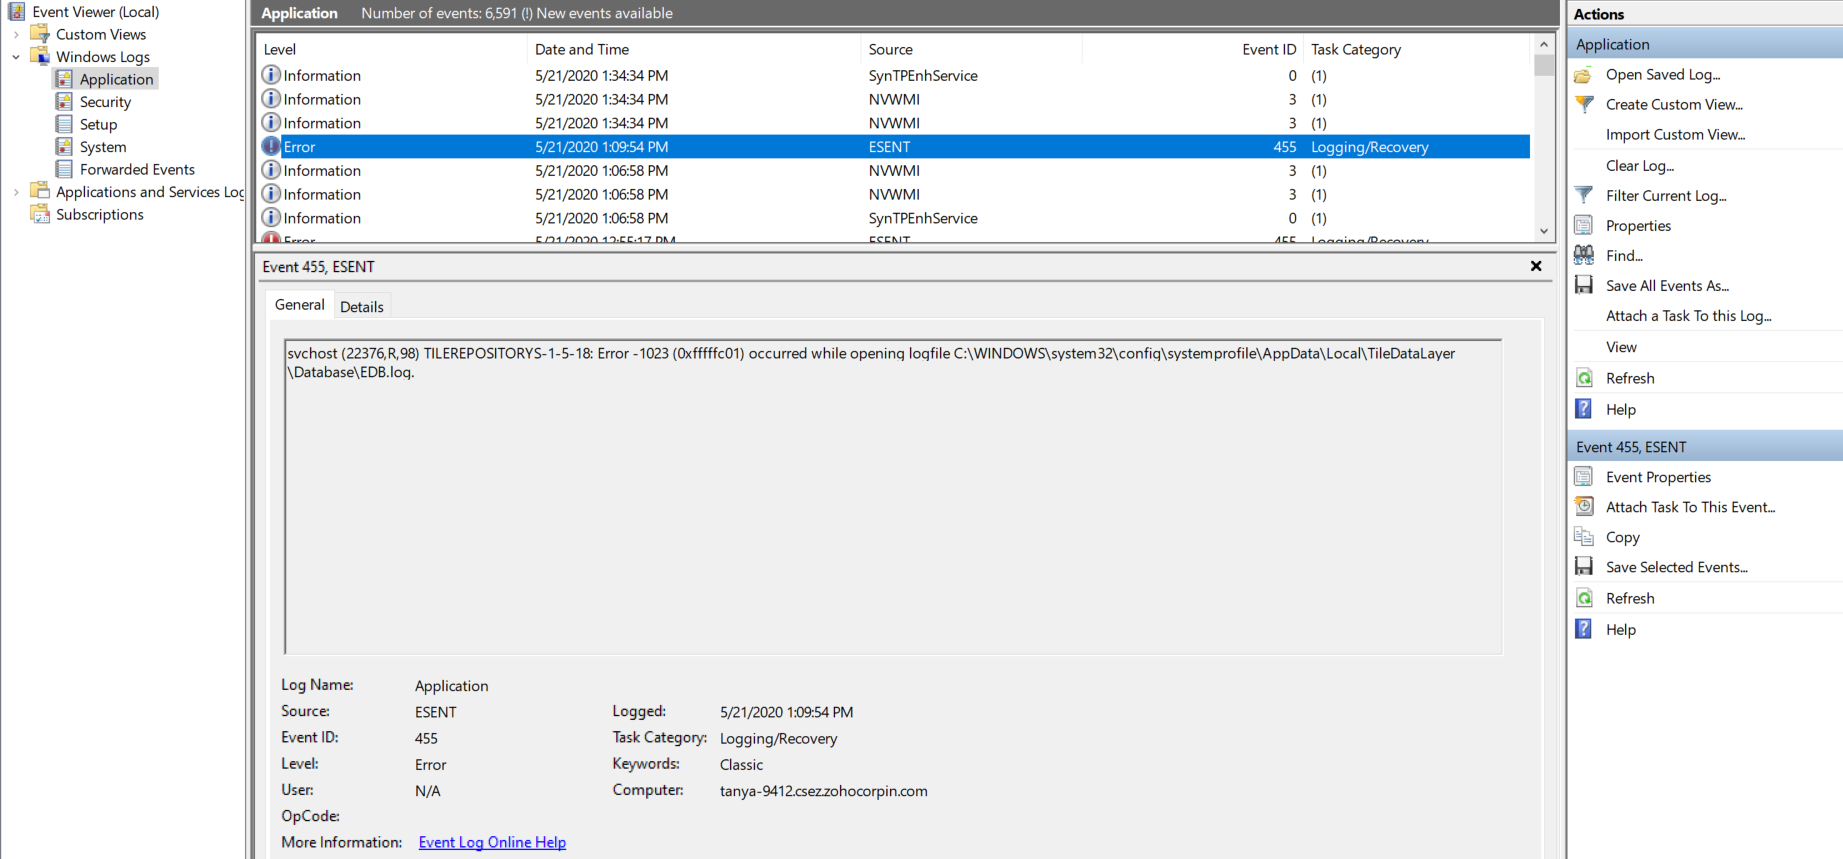
To prevent a lot of unwanted noise events from being dumped into your Security log you must configure audit policy at the subcategory level. Event Viewer is much improved compared to the version back in Windows Server 2003. You can now analyze the merged data from multiple logs in one view and take advantage of much more flexible filtering.
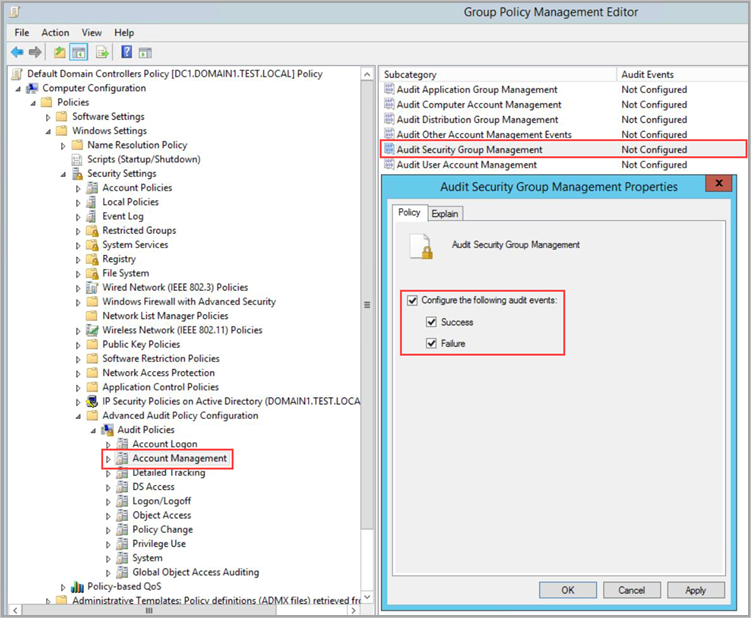
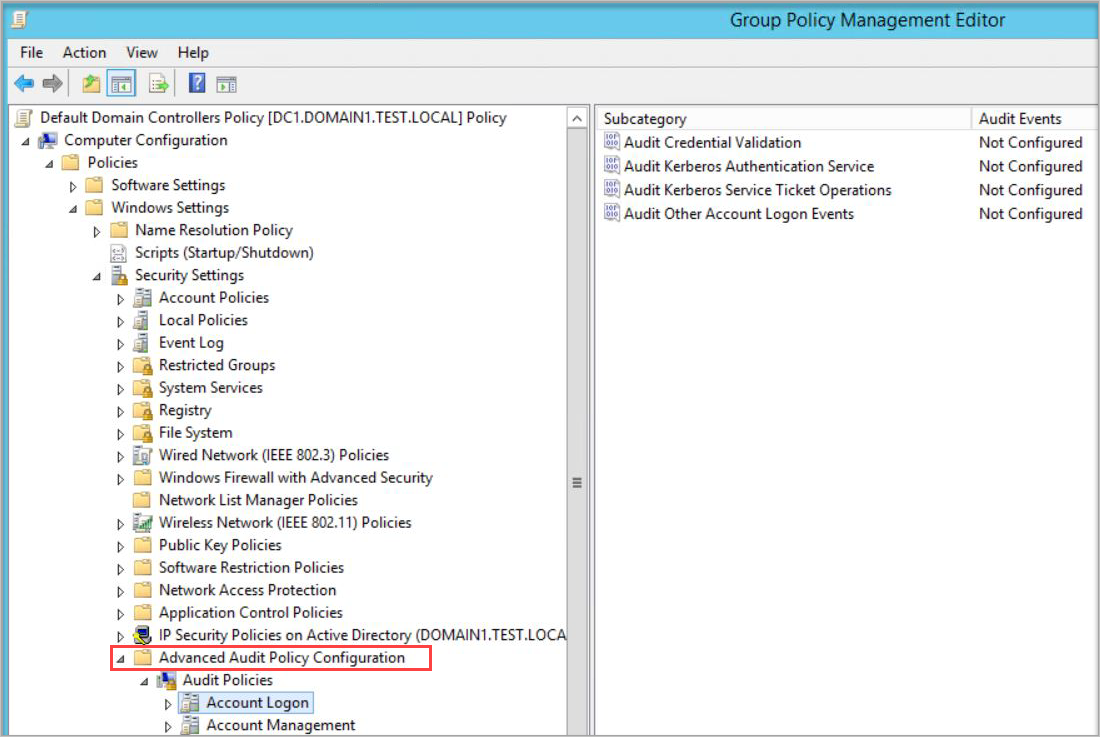
Configure Windows event auditing for Defender for Identity sensors. Learn automatic, manual, and PowerShell methods to enable required audit policies.
Image result for Windows Server Security Best Practices: Secure Your Windows Server Environment
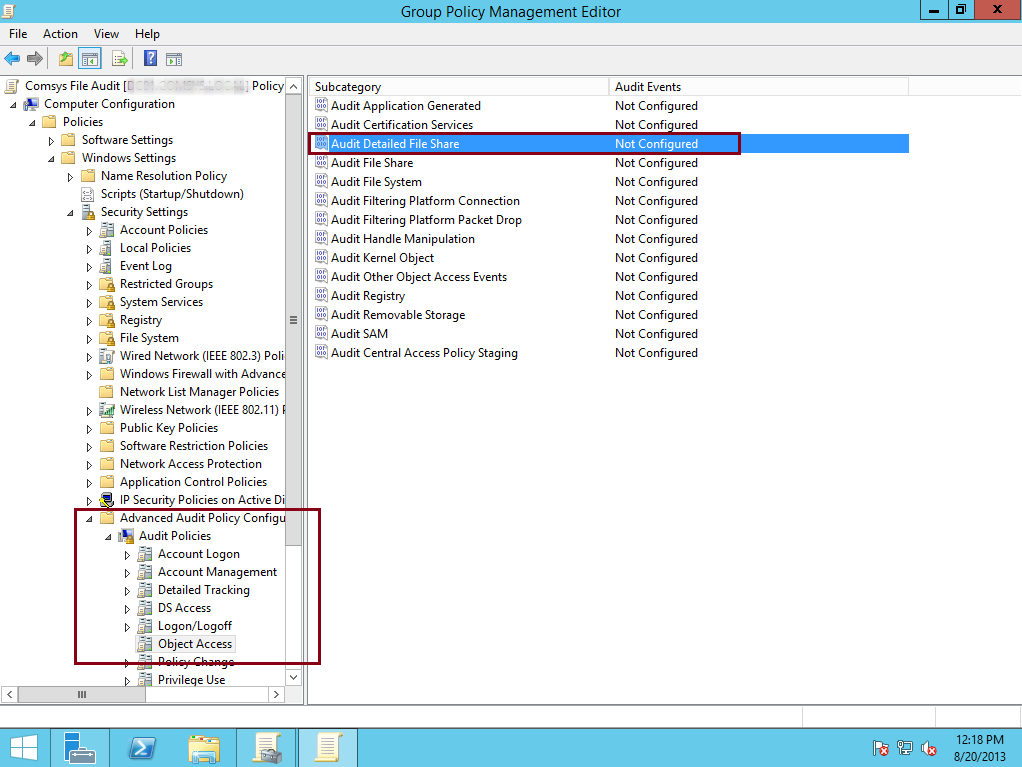
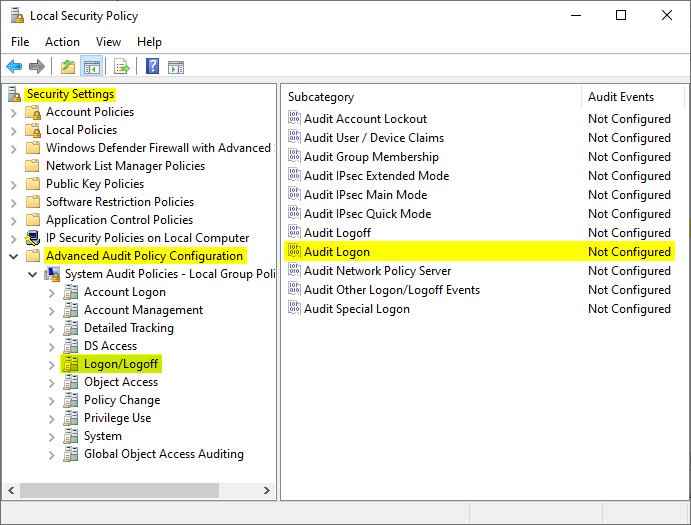
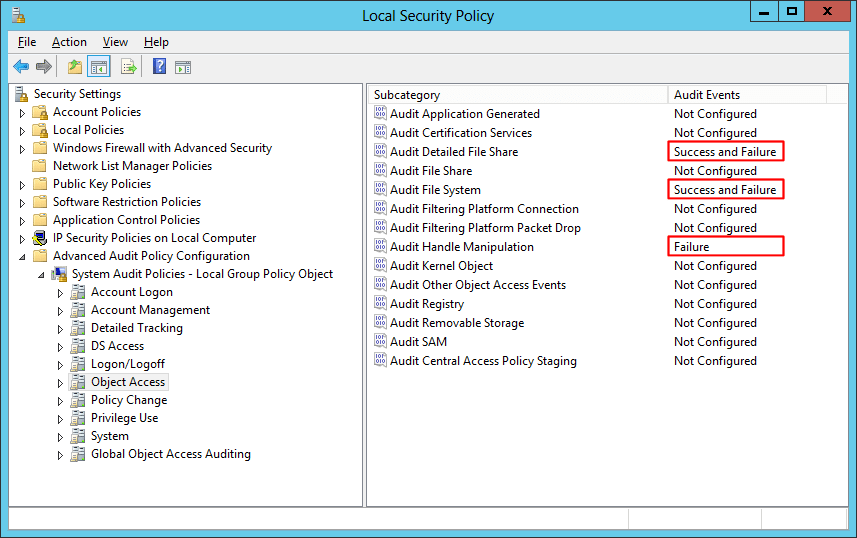
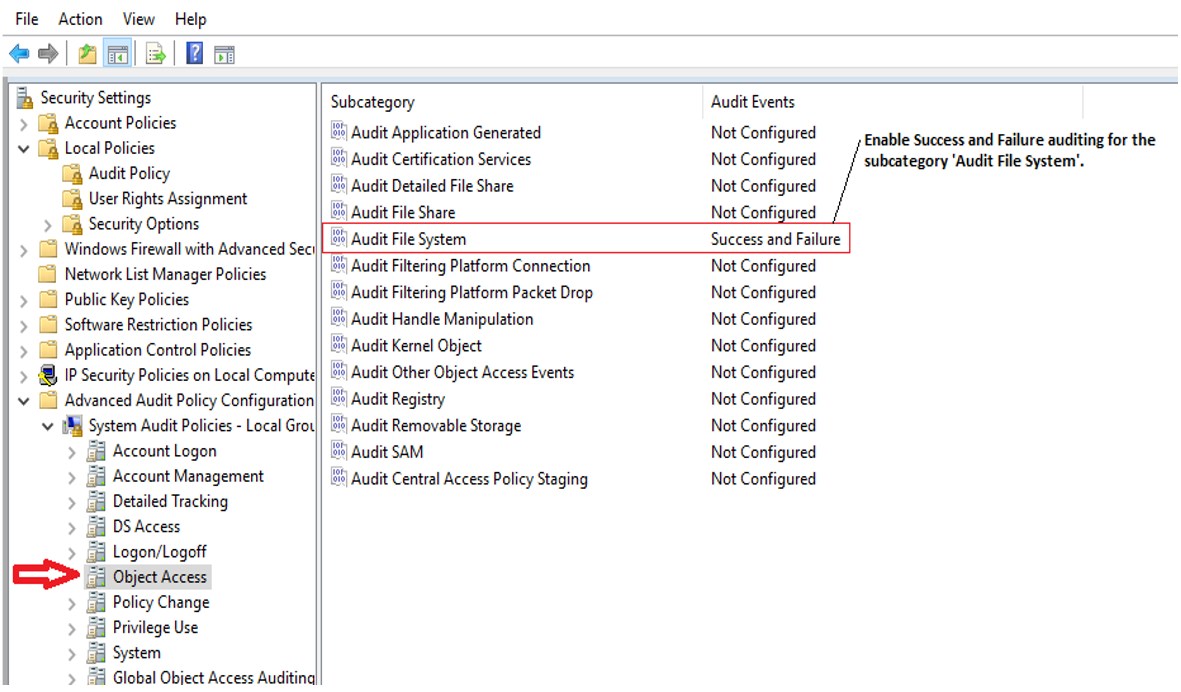
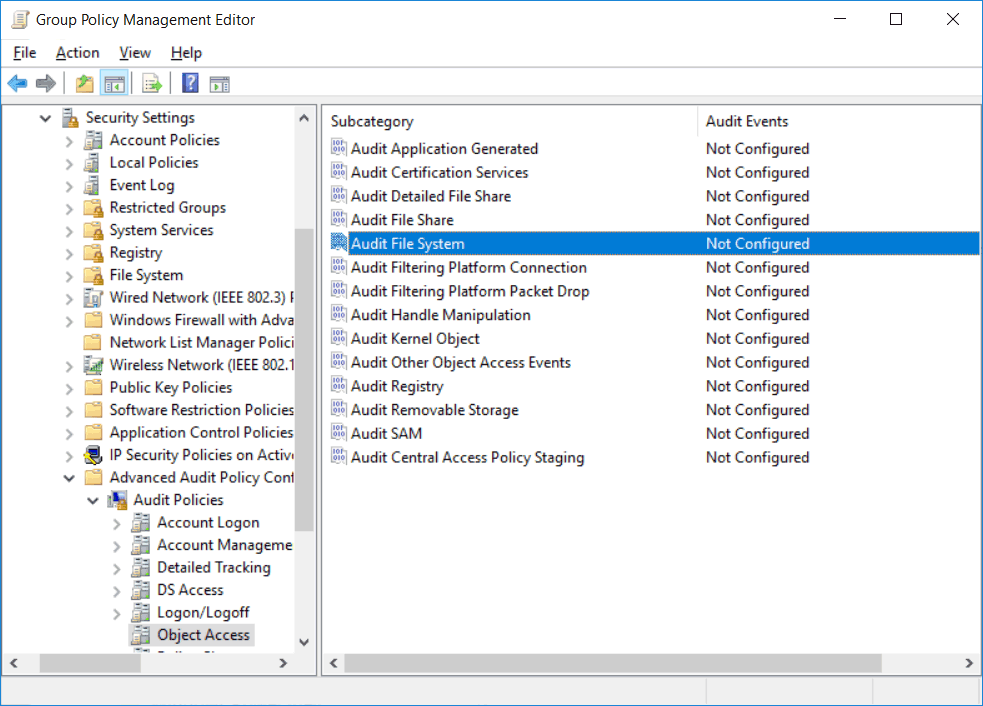
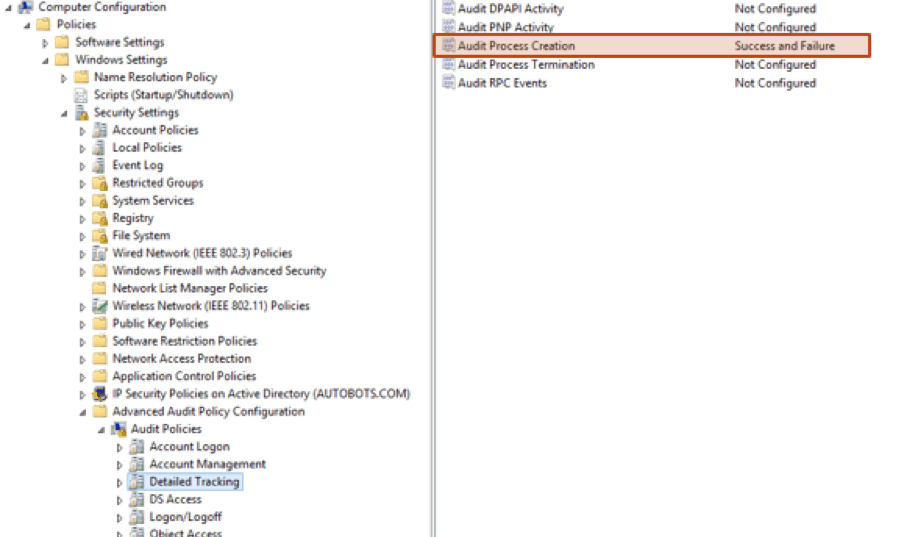
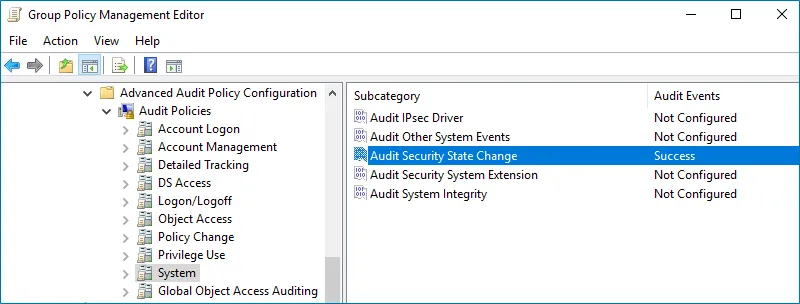
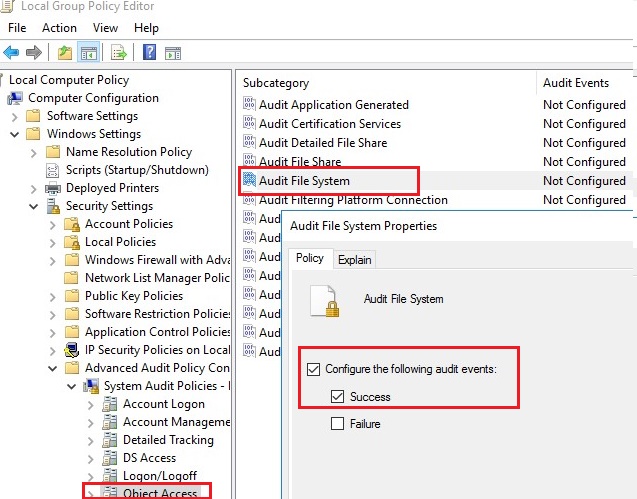
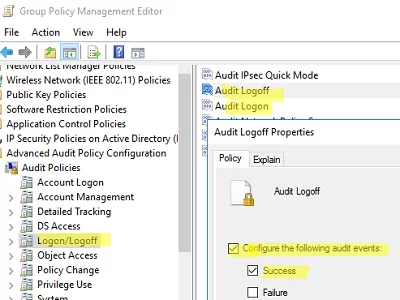
Advanced Audit Policy Configuration settings
The Advanced Audit Policy Configuration settings in Group Policy allows admins to specify which security events are audited on Windows systems for tracking activities, security monitoring, and incident detection.
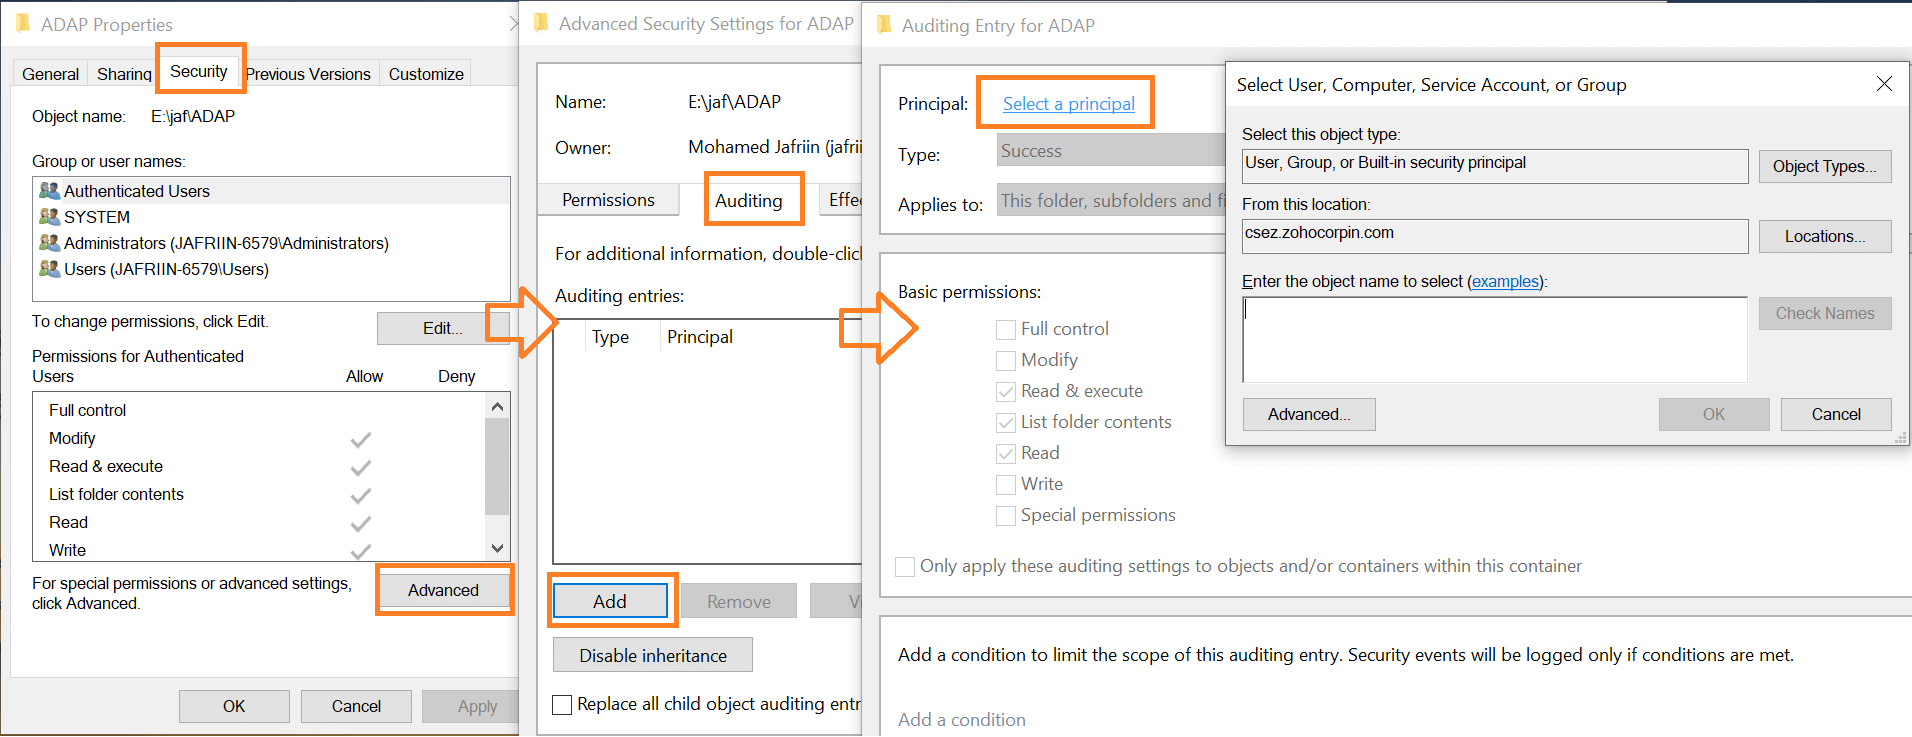
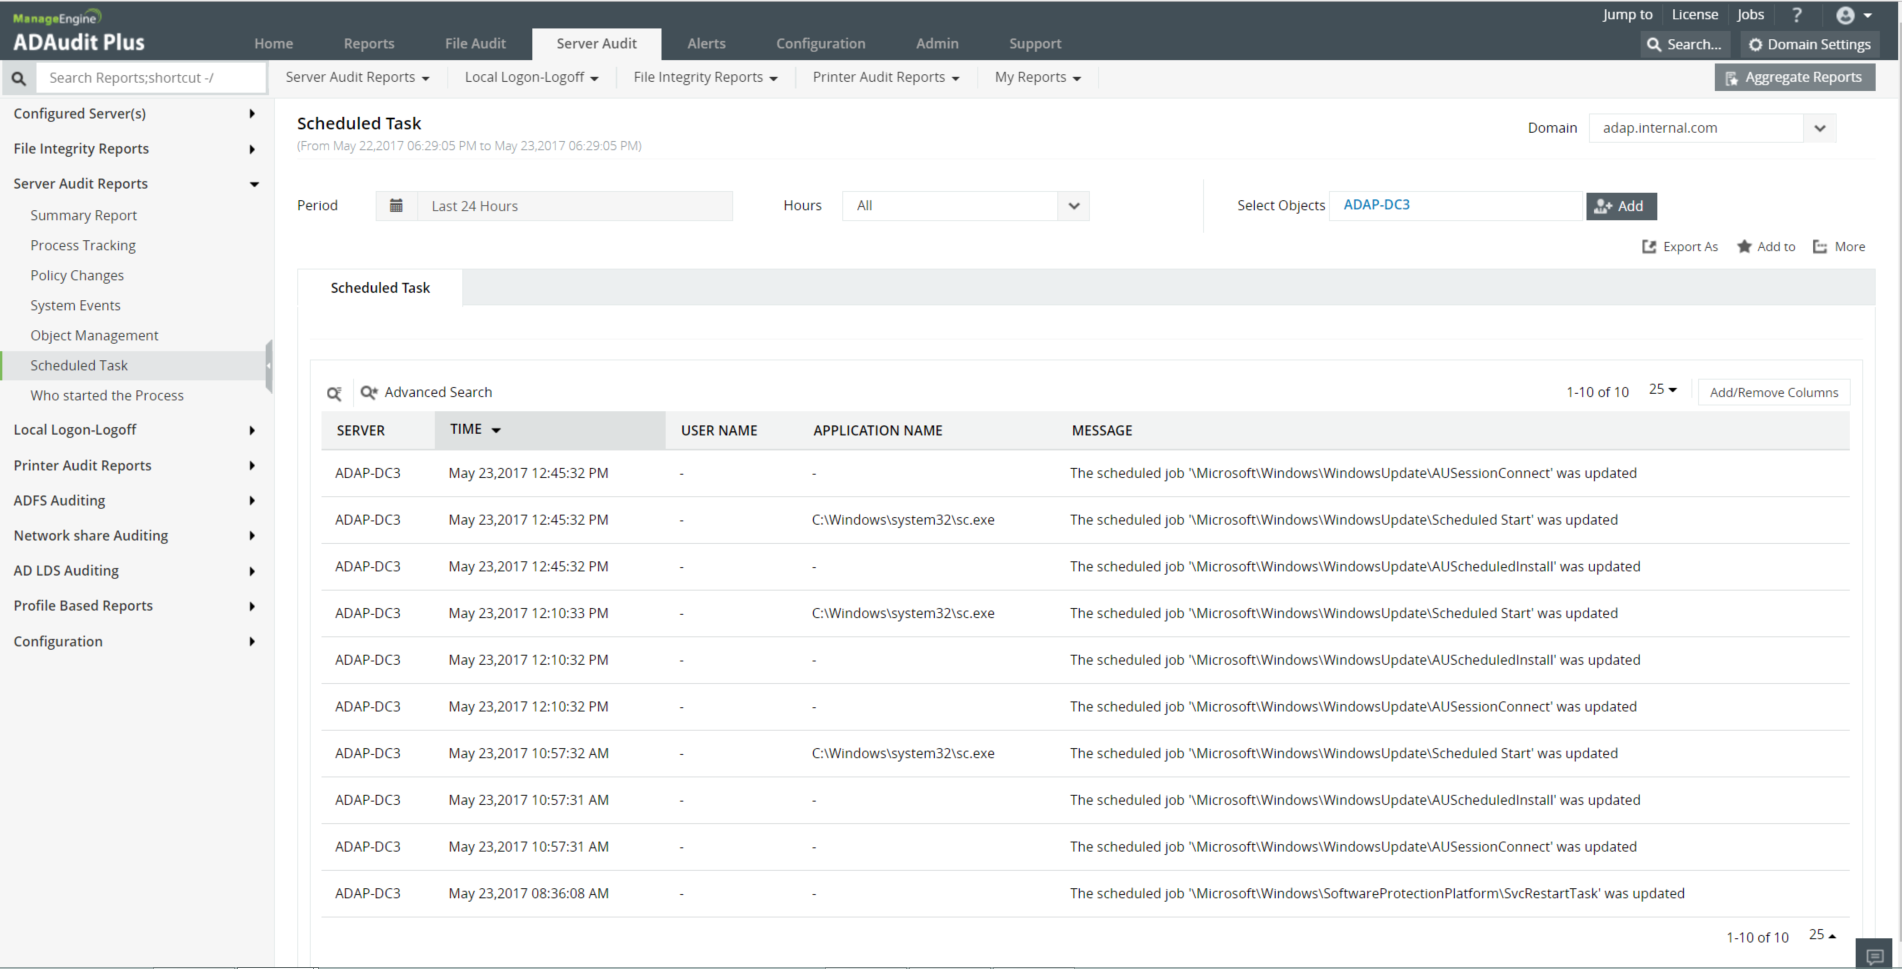
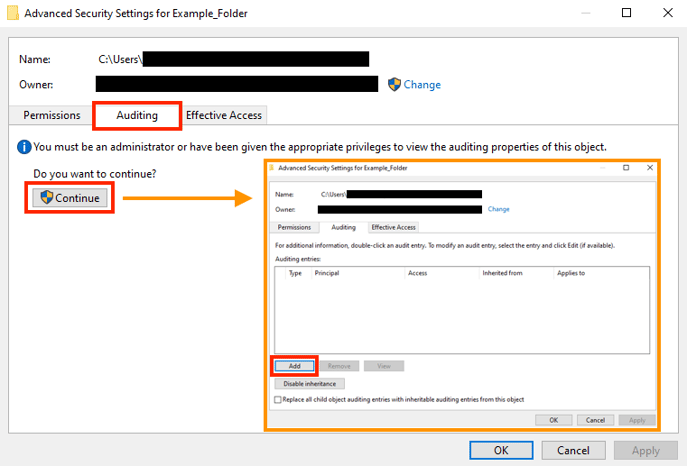
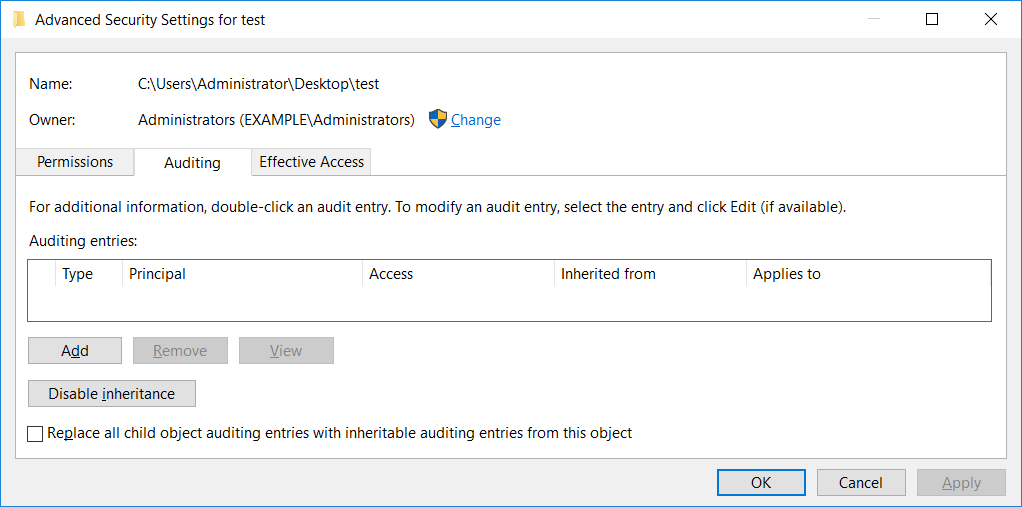
Configure and manage security audit settings (in addition to audit policies and advanced audit policies, you must also configure System Access Control Lists (SACLs) to enable auditing on directory objects and files/folders). For information on how to configure SACLs, visit our help document.
Image result for Manual config of audit policy | Windows file audit | ADAudit Plus
Detecting Windows Server Security Threats with Advanced Event Log Analyzers
Malware Infections Malware infections pose a significant threat to Windows servers , jeopardizing their security and functionality in several ways. Once infiltrated, malware can compromise the confidentiality, integrity, and availability of data and services hosted on the server .
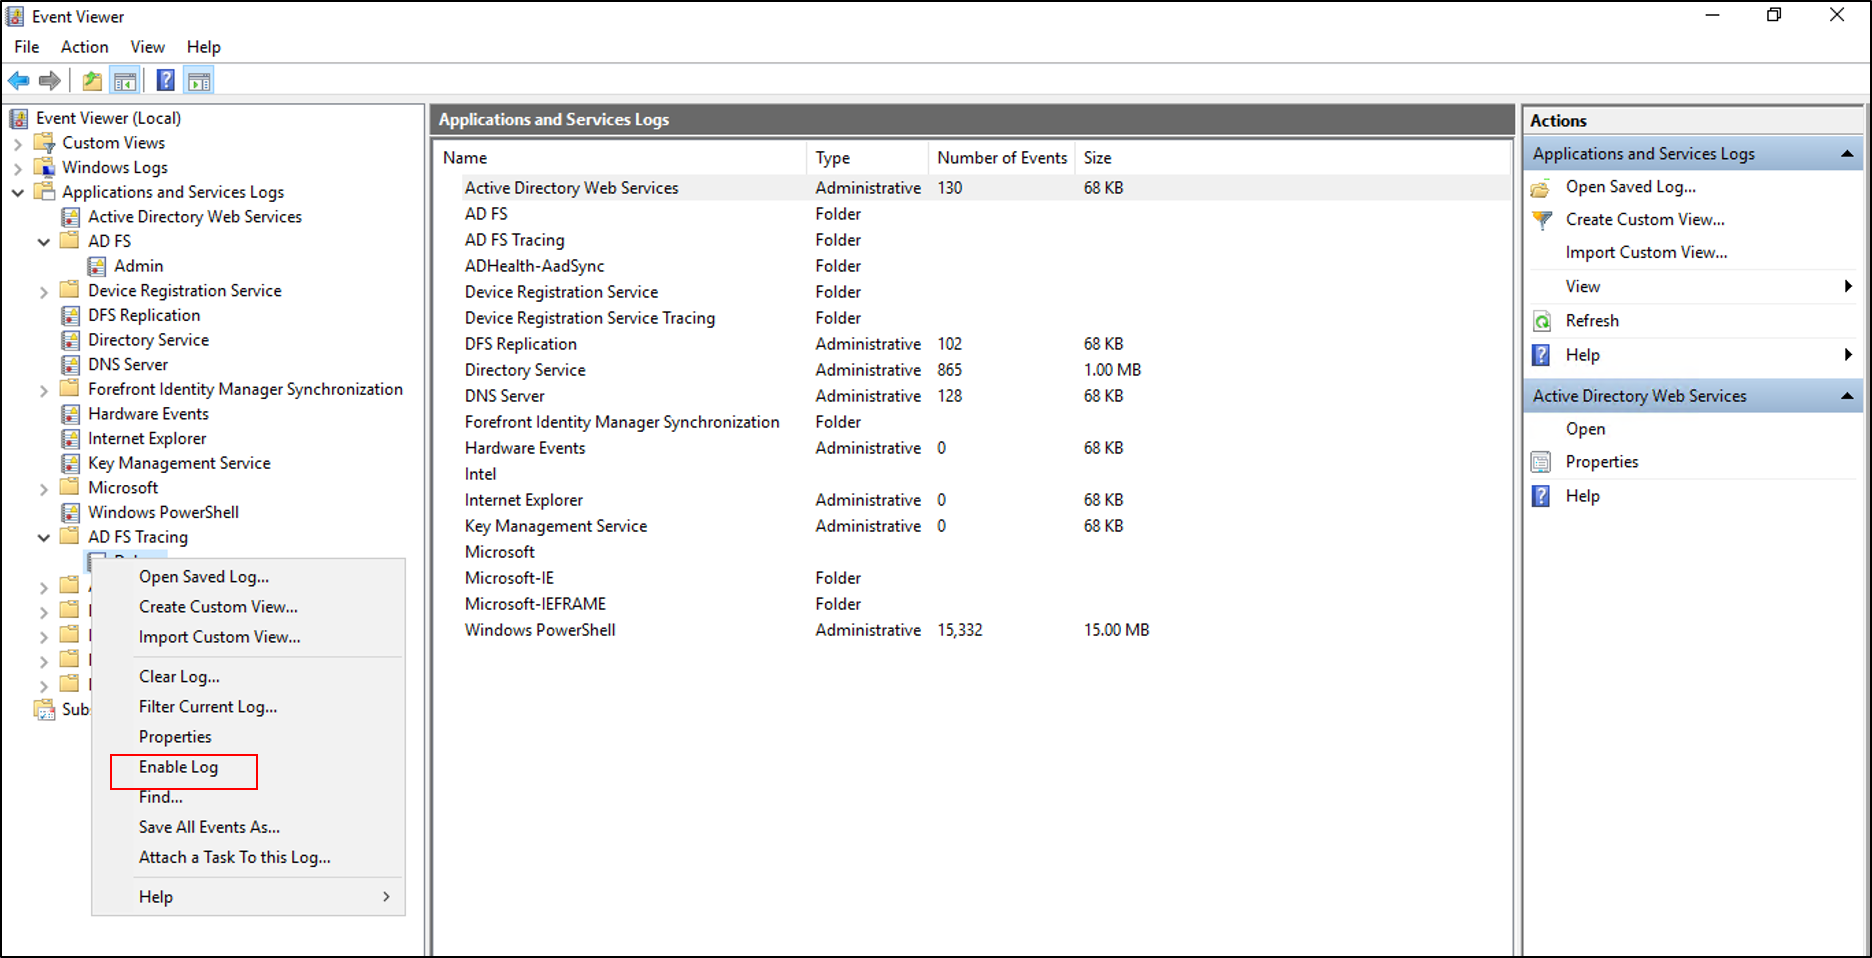
Image result for Manual config of audit policy | Windows file audit | ADAudit PlusImage result for Windows logging cheat sheet | PDFImage result for How to configure Microsoft Windows Server to log all failed and successful logon attempts. Edit ...Image result for How to configure Windows advanced audit policy | ADAudit PlusImage result for Configure File and Folder Access Auditing on Windows (GPO) | Windows OS HubImage result for Enabling the System Event Audit Log - Windows drivers | Microsoft LearnImage result for Configure File Access Auditing in Windows Server 2016 - RootUsersImage result for How To Detect File Changes in Windows Server | BlumiraImage result for How to enable audit policy in Windows Server 2012Image result for Audit Security Policy Implementation In Windows Environment at Kayla Olney blogImage result for Complete Guide to Windows File System Auditing - VaronisImage result for How to reduce the number of events generated in the Windows Security event log of the File ...Image result for How to Enable and Configure Audit Settings on Microsoft File server?Image result for Configure event log settings | Windows server audit guide | ADAudit PlusImage result for Troubleshoot Active Directory Federation Services with events and logging | Microsoft LearnImage result for security - Sources (protocols) for Audit Failures (Event ID 4625) in Windows Event Log - Server ...Image result for Configure File Access Auditing in Windows Server 2016 - RootUsersImage result for How to Enable Process Creation Events to Track Malware and Threat Activity - Security BoulevardImage result for Enable File Access Auditing in WindowsImage result for Enable DNS Logging and Diagnostics in Windows Server | Microsoft LearnImage result for Manual config of audit policy | Windows file audit | ADAudit PlusImage result for How to Audit File or Folder Deletion in Windows Server?Image result for Microsoft SQL Server Audit Log GuideImage result for How to enable auditing of Active Directory objects in Windows ServerImage result for Configure Global Object Access Auditing in Windows ServerImage result for Configure Advanced Audit Policies | Netwrix Product DocumentationImage result for Enhancing Security with Windows Server Access Auditing - WafaTech BlogsImage result for How to enable file and folder access auditing in Windows ServerImage result for How to audit the windows Event Log for deleted files using event filter in xPath form - Pat ...Image result for Top 10 Best Windows File Server Auditing Software Tools - 2026 | CloudSmallBusinessServiceImage result for How To Detect File Changes in Windows Server | BlumiraImage result for Windows 10 Event Logs And Log Files Guide - AVXVIImage result for New Audit Events added to the Windows 10 & Server 2016 security auditing | Security audit ...Image result for Automatic Windows event auditing configuration for Defender for Identity V3.x sensorImage result for How to Find Out Who Deleted a File on Windows | Windows OS HubImage result for Security Log & System Events Change Auditing in Windows Servers - ADAudit PlusImage result for Windows File Access MonitoringImage result for View Success and Failed Local Logon Attempts on Windows | Windows OS HubImage result for How To Detect File Changes in Windows Server | BlumiraImage result for Enable Audit Collection task. After you enable this service, all security events are sent to the ...Image result for Administering Windows Server 2012 R2: Monitoring and Auditing | Microsoft Press StoreImage result for The SMB protocol: All you need to know_smbprotocol-CSDN博客Image result for Auditing issues in Windows Server - Microsoft Q&AImage result for Configure File Access Auditing in Windows Server 2016 - RootUsers
Introduction Collecting Windows Event logs is crucial for maintaining a secure and well-monitored IT environment. Whether it's tracking user logins, monitoring changes to critical systems, or detecting potential security threats, Windows event logs provide the detailed visibility you need to understand what's happening across your network—especially on critical machines like Domain ...