How to Configure Network Address Translation (NAT)on pfSense software ...
As part of this approach, NAT configurations expose just a single IP address for a complete network to the outside world, thereby masking and bolstering the security of the entire internal network . Network address translation is often used in remote-access scenarios because it conserves addresses while boosting security.
For detecting WAN-type interfaces for use with NAT , pfSense software looks for the presence of a gateway selected on the interface configuration if it has a static IP address , or pfSense software assumes the interface is a WAN if it is a dynamic type such as PPPoE or DHCP.
What is the Default NAT Configuration on pfSense ? This section details the pfSense software's default NAT settings. Automatically create the optimal NAT configuration that can be found. This setup may not be suited to certain circumstances, and pfSense software allows for its complete modification through the web interface. This is in contrast to the majority of other open-source firewall ...
General Options Translation Misc Rule Information Configuring Outbound NAT Rules Outbound NAT Configuration Examples Disabling Outbound NAT Static Port Endpoint-independent Port Restricted Cone NAT Outbound NAT Outbound NAT , also known as Source NAT , controls how pfSense ® software will translate the source address and ports of traffic leaving ...

pfSense NAT
Outbound NAT - controlling source address translation for egress traffic, manual and hybrid modes, static port for VPN Related Sections pfSense Firewall - filtering rules, aliases, and security policy management Firewall Rules - rule creation, processing order, floating rules pfSense VPN - VPN tunnel configuration requiring correct NAT settings
This page documents the Network Address Translation ( NAT ) implementation in pfSense , including port forwarding (RDR), outbound NAT (SNAT), 1:1 NAT (Binat), and NPt. It explains how these NAT types wor
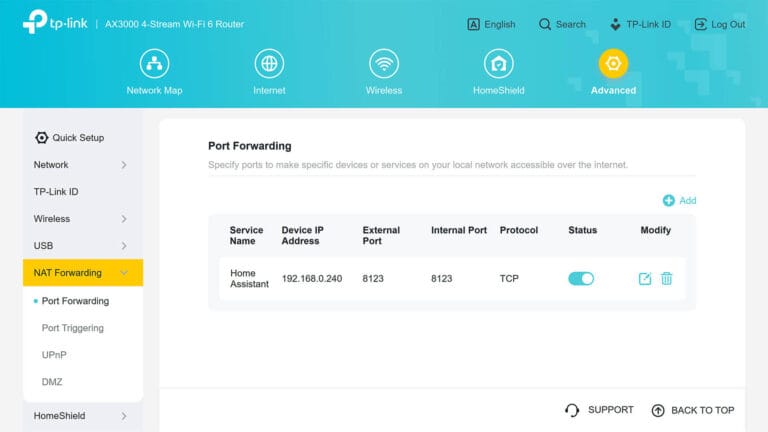
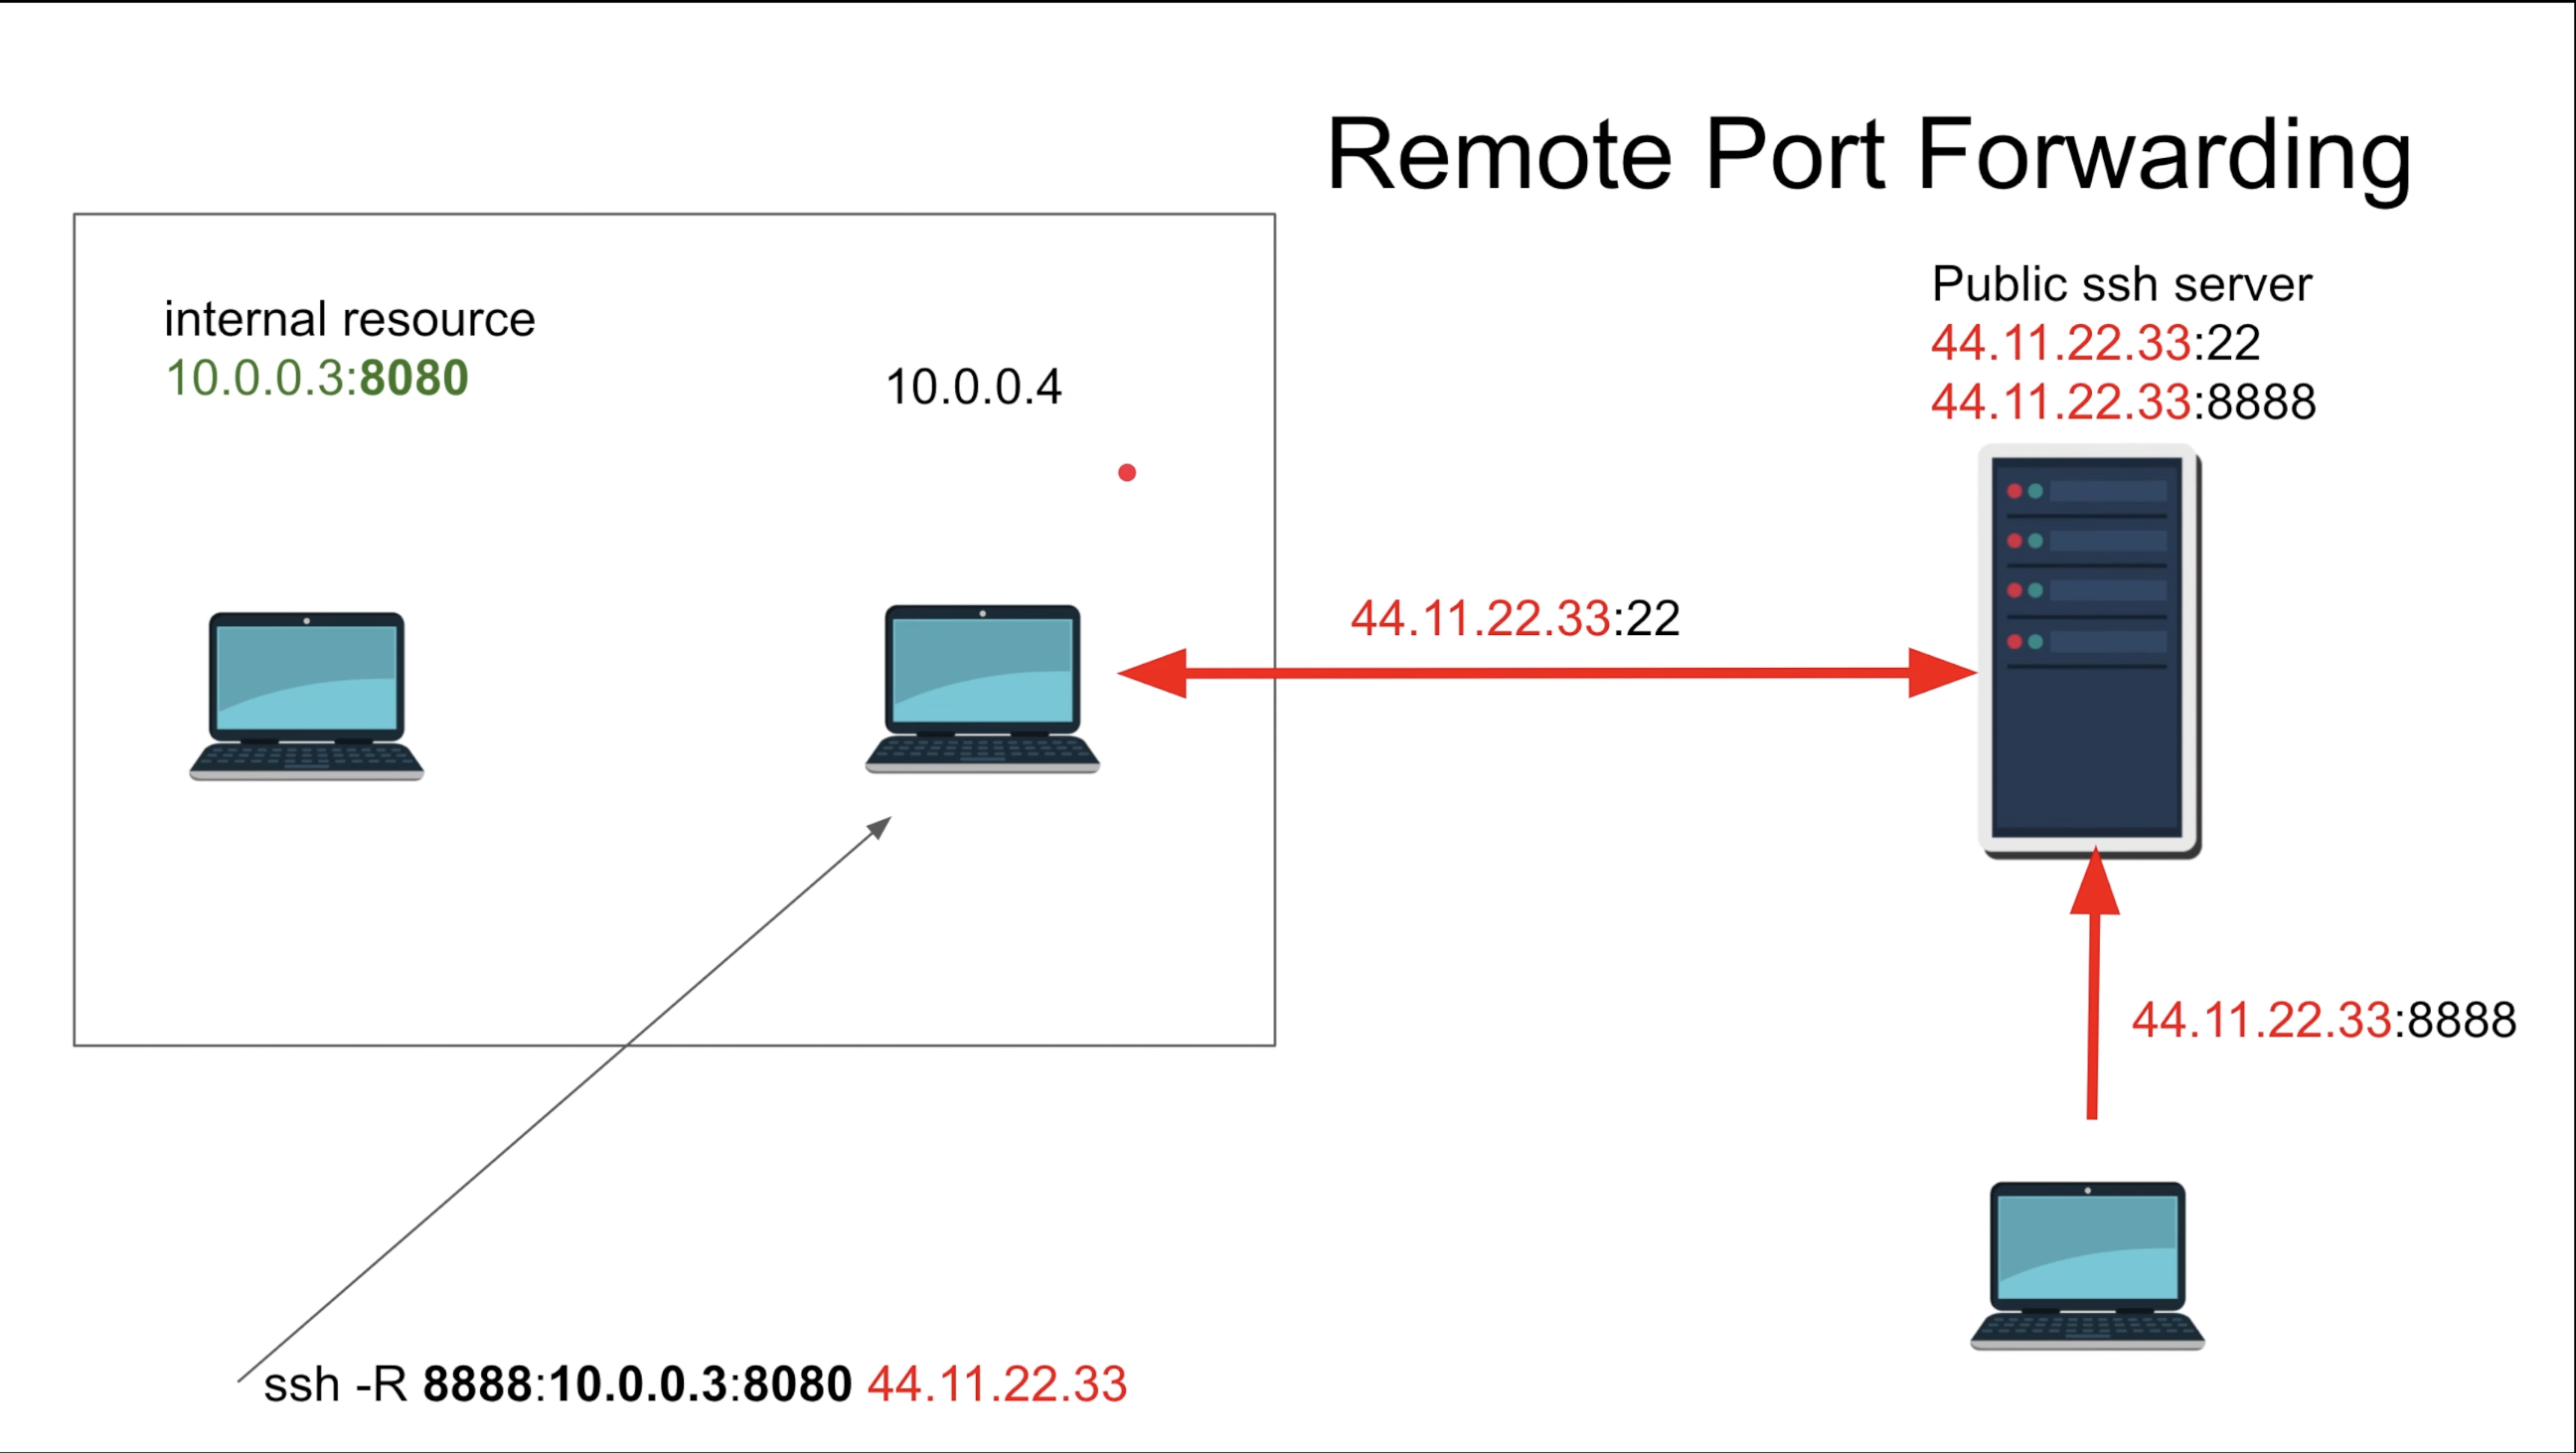
pfSense Port Forwarding

As we can see from the illustration, How To Configure Network Address Translation Nat On Pfsense Software has many fascinating aspects to explore.
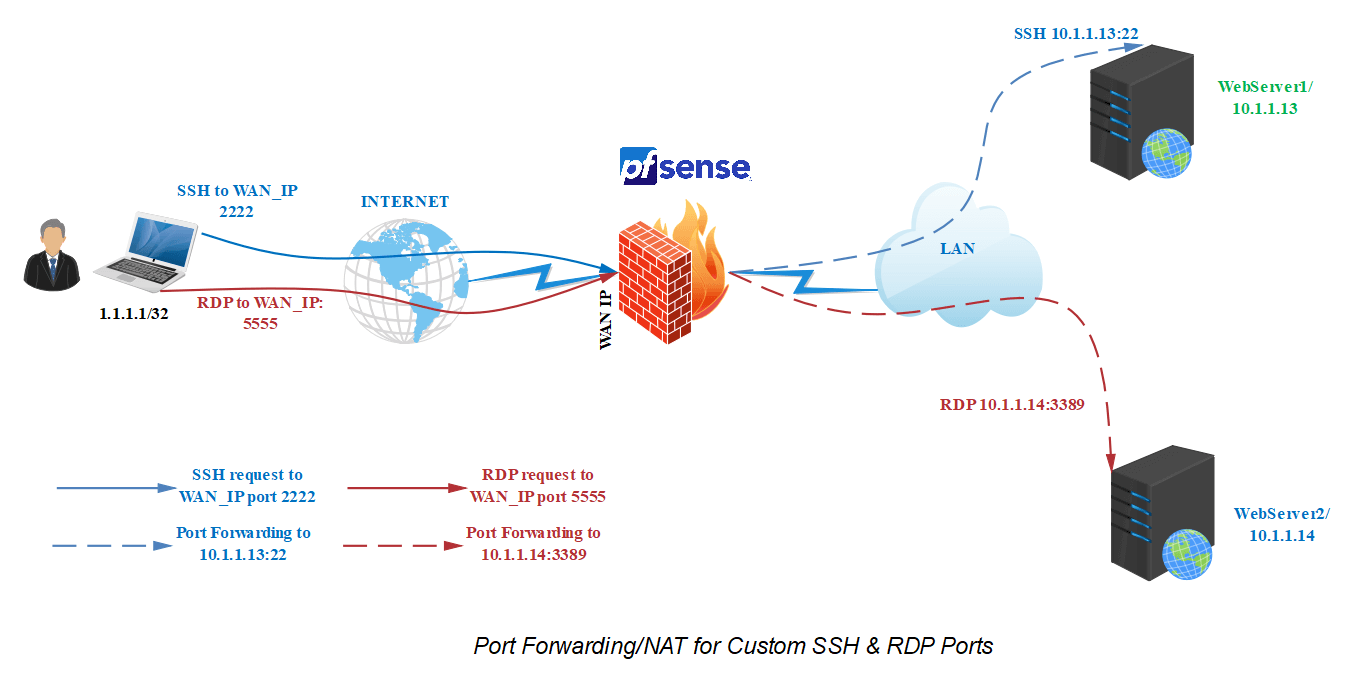
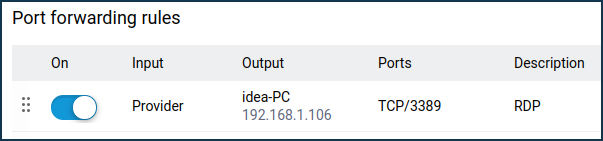
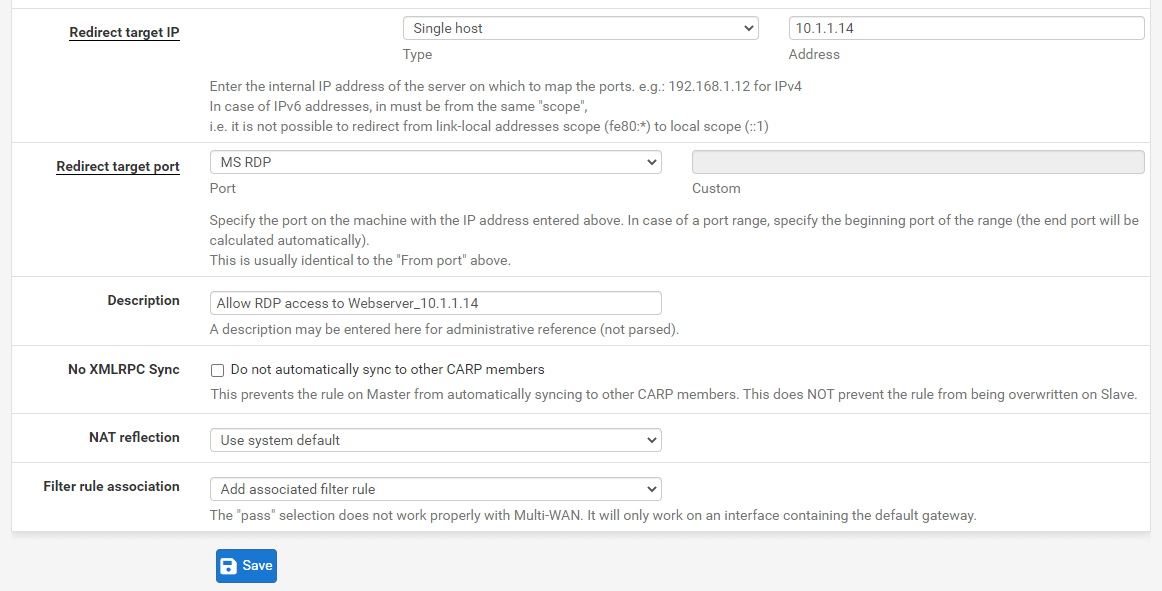
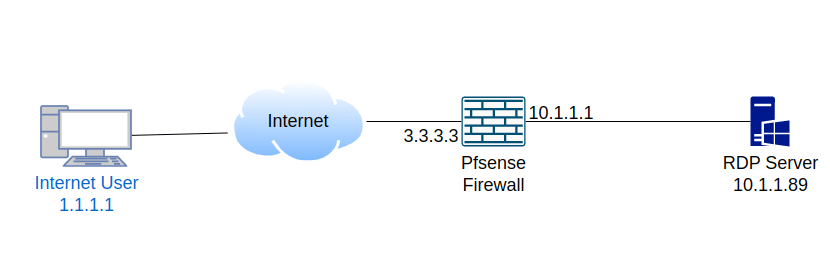
When a packet arrives on the WAN interface, pfSense consults the port forward rule table and, upon a match, rewrites the destination address to the IP of the internal server. This is a form of DNAT (Destination NAT ) - destination address translation .
pfSense Documentation ¶ The documentation, maintained with the help of the community, offers instructions on how to install, configure , and use pfSense ® software to protect your network .
How to Set Up NAT with pfSense
How to Set Up NAT with pfSense Learn how to configure outbound NAT , port forwarding, and 1:1 NAT on pfSense using the web interface.
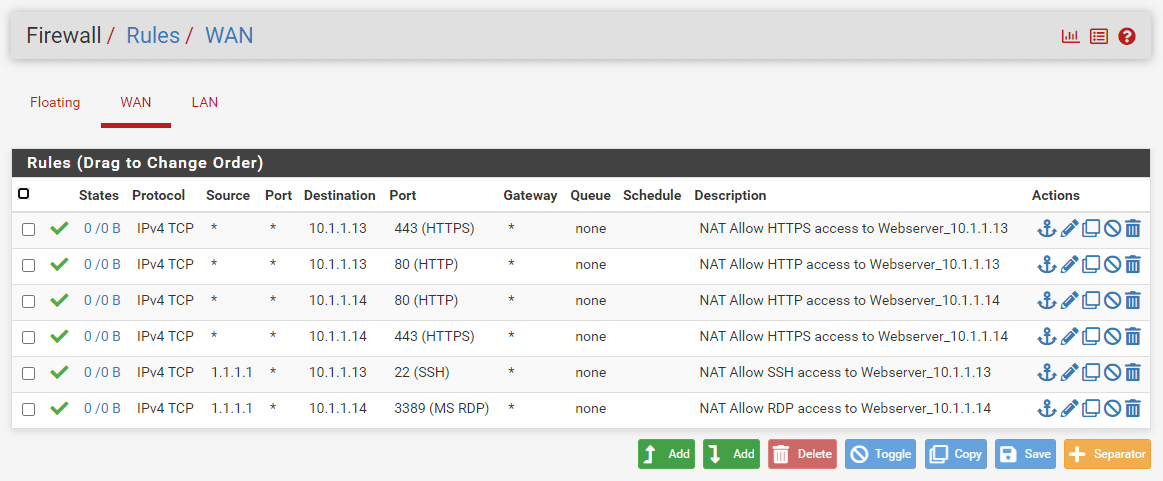
Step 6: Test the NAT Rule From an external device, attempt to access the forwarded service (e.g., open a web browser and enter your WAN IP followed by the port). Ensure that traffic is routed to the correct internal IP address and service. Additional Notes Firewall Rules: pfSense automatically creates a matching firewall rule for the NAT rule.