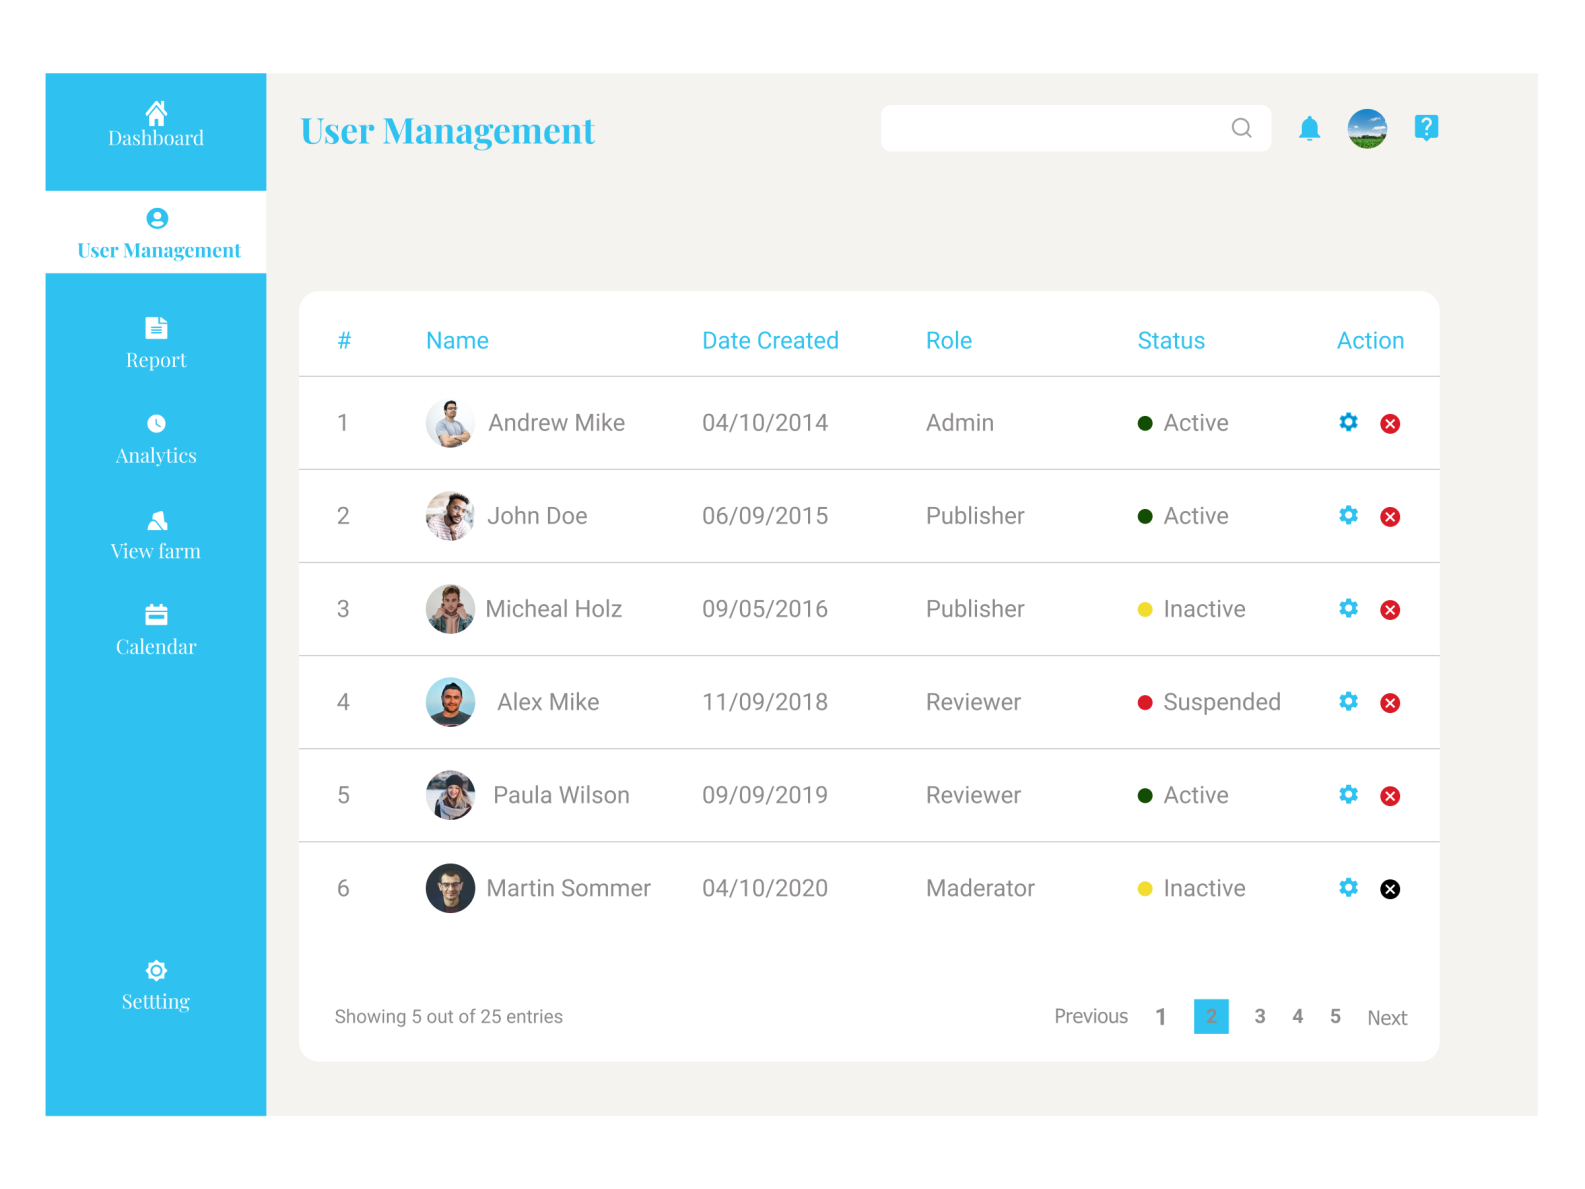
Designing a user management application requires more than just creating login forms and password resets. It demands a thoughtful architecture that balances security, scalability, and user experience. Whether you're building an internal admin panel or a customer-facing platform, the decisions made during the design phase will ripple through every layer of the system for years to come.
Core Principles of User Management Architecture
Every solid user management system starts with a clear separation of concerns. Authentication, authorization, profile management, and session handling should each live in their own logical boundaries. When these responsibilities bleed into one another, you end up with tangled code that becomes nearly impossible to audit or extend. A well-designed system treats each concern as a distinct service or module with well-defined interfaces.
Scalability must be considered from day one. Even if you're launching with a hundred users, the architecture should support millions without a complete rewrite. This means choosing the right database patterns, caching strategies, and session storage mechanisms early. Horizontal scaling, stateless authentication tokens, and asynchronous processing for non-critical operations like email notifications all contribute to a system that grows gracefully.

Authentication and Security Considerations
Password handling remains one of the most critical aspects of user management design. Hashing algorithms like bcrypt, scrypt, or Argon2 should be non-negotiable choices. Beyond passwords, multi-factor authentication (MFA) has moved from optional to essential. Time-based one-time passwords (TOTP), hardware security keys, and biometric verification each serve different threat models and user populations.
| Security Layer | Implementation | User Impact |
|---|---|---|
| Password Hashing | Argon2id with per-user salts | Transparent to users |
| Session Management | JWT with refresh token rotation | Seamless re-authentication |
| Rate Limiting | Sliding window per IP and user | Minimal for legitimate users |
| Audit Logging | Immutable append-only logs | No direct user impact |
Session management deserves special attention. JSON Web Tokens (JWTs) offer stateless scalability but introduce complexity around token revocation. Server-side sessions with Redis or similar stores simplify invalidation but add infrastructure dependencies. The right choice depends on your specific requirements around logout behavior, concurrent session limits, and distributed system architecture.
User Experience and Interface Design
The interface layer often determines whether users actually adopt your system. Registration flows should minimize friction while collecting necessary information. Progressive profiling—gathering additional user data over time rather than demanding everything upfront—significantly improves completion rates. Social login options reduce barriers but introduce dependencies on third-party providers and potential data sharing concerns.

Role-based access control (RBAC) and attribute-based access control (ABAC) provide different granularity for permissions. RBAC works well for stable organizational structures, while ABAC handles complex, context-dependent authorization rules. Most mature systems implement RBAC as the foundation with ABAC overlays for edge cases. The interface for managing these permissions must be intuitive enough for non-technical administrators to configure without engineering support.
Data Modeling and Storage Strategies
User data models evolve constantly. Schema design should accommodate this evolution without destructive migrations. Flexible document stores work well for profile data that varies across user types, while relational structures better serve authentication credentials and audit trails. Many production systems use polyglot persistence—different storage engines for different access patterns—rather than forcing everything into a single database technology.
- Separate authentication credentials from profile data to limit blast radius of breaches
- Implement soft deletes with retention policies for compliance requirements
- Design for GDPR/CCPA from the start rather than retrofitting later
- Plan for data portability and account merging scenarios
Operational Concerns and Monitoring
Production user management systems require comprehensive observability. Login success rates, password reset frequencies, and session anomalies should trigger alerts before users report issues. Audit logs must capture who accessed what resources when, with tamper-evident storage for compliance scenarios. Performance metrics around authentication latency directly impact user experience and should be tracked with the same rigor as business metrics.
Disaster recovery planning cannot be an afterthought. User data represents both a critical business asset and a significant liability. Backup strategies, geographic distribution, and recovery time objectives should be documented and tested regularly. The ability to restore service during partial outages while maintaining security boundaries separates amateur implementations from production-grade systems.
Building user management infrastructure is ultimately about trust. Users entrust their credentials and personal information to your system. Every design decision either reinforces or erodes that trust. The systems that endure are those that treat security and privacy as foundational requirements rather than features to be added later. Starting with strong architectural principles creates the foundation for everything that follows.